Best Managed Detection and Response (MDR) Software for Medium-Sized Businesses

How Many Managed Detection and Response (MDR) Software Products Does G2 Track?

Total Products under this Category: 149

Category Stats (Nov 2026)

  • Average Rating: 4.49/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.08%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Managed Detection and Response (MDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 9,500+ Authentic Reviews
  • 149+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

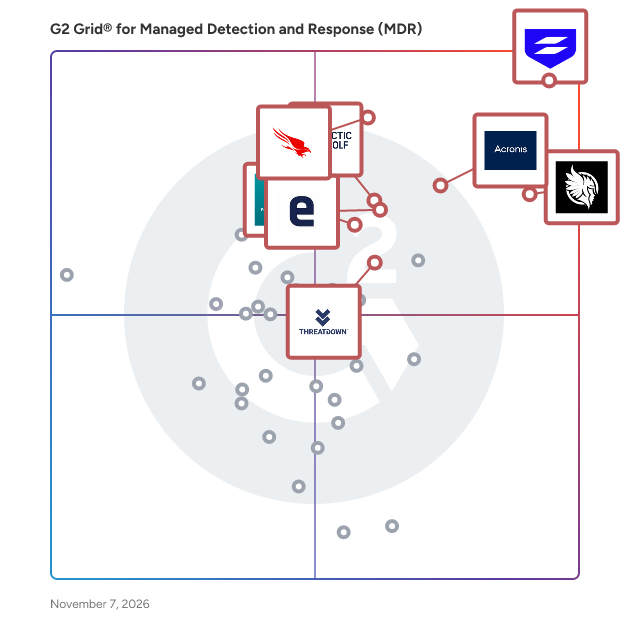
G2 Grid® for Managed Detection and Response (MDR) Software

G2 Grid® for Managed Detection and Response (MDR)  Software plotting products by satisfaction and market presence

Highlighted products: Sophos MDR, CrowdStrike Falcon Endpoint Protection Platform, Arctic Wolf, Huntress Managed EDR, Acronis Cyber Protect Cloud (now Acronis Cyber Platform), eSentire, ESET PROTECT, and ThreatDown.

Underlying data: [Grid® JSON](https://www.g2.com/categories/managed-detection-and-response-mdr/grids.json?focus%5B%5D=sophos-mdr&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=arctic-wolf&focus%5B%5D=huntress-managed-edr&focus%5B%5D=acronis-cyber-protect-cloud-now-acronis-cyber-platform&focus%5B%5D=esentire&focus%5B%5D=eset-protect&focus%5B%5D=threatdown&segment=mid-market)

Sophos MDR

Sophos Managed Detection and Response (MDR) is a fully managed service delivered by experts who detect and respond to cyberattacks targeting your computers, servers, networks, cloud workloads, email accounts, backups, and more. Our highly skilled security analysts stop advanced human-led attacks and take immediate action to neutralize threats before they can disrupt your business operations or compromise your sensitive data.

Average Rating: 4.7/5.0

Total Reviews: 691

How Do G2 Users Rate Sophos MDR?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.5/10 (Category avg: 9.1/10)
  • Automated remediation: 9.2/10 (Category avg: 8.7/10)
  • Automated investigation: 9.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Sophos MDR?

  • Seller: Sophos
  • Company Website:
  • Year Founded: 1985
  • HQ Location: Oxfordshire
  • LinkedIn® Page: www.linkedin.com
    5,550 employees on LinkedIn®
  • Ownership: LSE:SOPH

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Information Technology and Services, Manufacturing
  • Company Size: 63% Medium, 20% Large

What Do G2 Reviewers Say About Sophos MDR?

AI-generated summary from verified user reviews

Pros
  • Users value the proactive threat detection, benefiting from swift responses and expert analysis in real-time.
  • Users value the 24/7 monitoring and response of Sophos MDR, ensuring continuous cybersecurity without taxing internal resources.
  • Users find Sophos MDR to have exceptional ease of use, making security management seamless and efficient.
  • Users value the peace of mind provided by Sophos MDR's continuous monitoring and proactive threat detection.
  • Users appreciate the fast response times of Sophos MDR, which enhances monitoring and reduces internal workload.
Cons
  • Users feel that the high cost of Sophos MDR is a significant drawback compared to other services.
  • Users experience communication issues with Sophos MDR, including delays and unclear report functionalities impacting overall efficiency.
  • Users find the limited customization in Sophos MDR restricts their ability to fine-tune detection rules effectively.
  • Users often experience complexity of integration with Sophos MDR, hindering effective communication and alerting workflows.
  • Users find the poor reporting and overwhelming alert volume challenging, impacting their ability to manage incidents effectively.

What Are Recent G2 Reviews of Sophos MDR?

What Are G2 Users Discussing About Sophos MDR?

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 637

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.1/10 (Category avg: 9.1/10)
  • Automated remediation: 9.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.0/10 (Category avg: 8.9/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Security Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Large, 37% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the cloud-native architecture and effective features like workflow automation and asset management in CrowdStrike Falcon.
  • Users value the advanced threat detection capabilities of CrowdStrike Falcon, enhancing security and streamlining response efforts.
  • Users value the ease of use of CrowdStrike Falcon, benefiting from its lightweight agent and intuitive interface.
  • Users appreciate the robust security features of CrowdStrike Falcon, enhancing endpoint protection and system performance.
  • Users praise the superior detection capabilities of CrowdStrike Falcon, consistently delivering reliable and swift responses.
Cons
  • Users find that CrowdStrike Falcon's high licensing cost can be burdensome, particularly for smaller teams and organizations.
  • Users express frustration over the complexity of CrowdStrike Falcon's management console and its steep learning curve.
  • Users find the steep learning curve of CrowdStrike Falcon challenging due to its complex management console.
  • Users face limited functionality in adding hash values to CrowdStrike Falcon, which restricts monitoring capabilities.
  • Users express concern over the high pricing of CrowdStrike Falcon, especially for smaller organizations.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Arctic Wolf

Arctic Wolf® is the cybersecurity and AI company that ends cyber risk by transforming it into business resilience. Powered by the Aurora® Superintelligence Platform, Arctic Wolf delivers modern security operations built on proprietary AI and decades of real-world expertise to manage and mitigate cyber threats. The platform is built on the Swarm of Experts™, which coordinates specialized AI agents across core security operations functions. The Security Operations Graph™ connects real-world telemetry and customer context to every workflow. The AI Trust Engine™ validates outcomes and keeps human experts in the loop. Arctic Wolf serves businesses of all sizes looking to strengthen their cybersecurity posture. IT and security teams turn to Arctic Wolf to streamline operations, gain a clearer view of their security landscape, and build resilience against cyberattacks. Arctic Wolf's Aurora-branded solutions include Aurora® Managed Detection and Response (MDR), which provides 24x7 monitoring and rapid threat detection and response. Aurora® Attack Surface Management and Aurora® Vulnerability Management help organizations identify and remediate vulnerabilities to reduce their attack surface. Aurora® Endpoint Security safeguards devices against threats. Aurora® Security Awareness and Training helps employees reduce human error in cybersecurity. Aurora® Incident Response helps organizations respond when a security incident occurs. The Concierge Security® Team delivers personalized support, working closely with organizations to understand their unique challenges and build tailored strategies for stronger cyber resilience. By combining AI-driven automation with expert validated precision, Arctic Wolf helps organizations confidently manage cyber risk, so they can operate with control and the freedom to innovate.

Average Rating: 4.7/5.0

Total Reviews: 276

How Do G2 Users Rate Arctic Wolf?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Arctic Wolf?

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Hospital & Health Care, Information Technology and Services
  • Company Size: 71% Medium, 20% Large

What Do G2 Reviewers Say About Arctic Wolf?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the quick and proactive customer support from Arctic Wolf, enhancing their security management experience.
  • Users value Arctic Wolf's proactive threat detection, experiencing enhanced security and peace of mind through expert support.
  • Users commend Arctic Wolf for its hands-on and proactive security approach, acting as an extension of their team.
  • Users appreciate the ease of use of Arctic Wolf, highlighting its seamless onboarding and user-friendly platform.
  • Users value the proactive alerts from Arctic Wolf, enhancing security while freeing up time for critical tasks.
Cons
  • Users note the high cost of Arctic Wolf, which may be out of budget for some potential customers.
  • Users experience a significant number of false positives with Arctic Wolf, leading to increased investigation time and ticket generation.
  • Users experience a steep learning curve initially, though support during onboarding helps navigate the complexities.
  • Users face overwhelming cybersecurity risks with Arctic Wolf, resulting in many alerts and complex reports to manage.
  • Users face dashboard issues that require adjustment, but support is available to help navigate the complexities.

What Are Recent G2 Reviews of Arctic Wolf?

What Are G2 Users Discussing About Arctic Wolf?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Acronis Cyber Protect Cloud (now Acronis Cyber Platform)

Acronis delivers the world’s most complete cyber resilience platform, combining backup, disaster recovery, cybersecurity, RMM, and business operations tools into a single, natively integrated solution. Built specifically for Managed Service Providers (MSPs) and IT teams, Acronis simplifies operations with one agent, one console, and one license model. Automation, AI-driven insights, and multi-tenant management ensure that fewer technicians can manage more clients at lower cost. With predictable pricing and transparent billing, Acronis enables partners and IT teams to scale efficiently, comply with regulations, and deliver unmatched resilience. No other vendor delivers this level of integration, efficiency, and MSP alignment. Acronis Cyber Protect Cloud (now Acronis Cyber Platform) unites backup and next-generation, AI-based anti-malware, antivirus, and endpoint protection management in one solution. Integration and automation provide unmatched ease for service providers — reducing complexity while increasing productivity and decreasing operating costs. Acronis Cyber Platform is the single service provider solution that combines backup, anti-malware (including anti-virus, anti-ransomware, and anti-cryptojacking) and security and management capabilities such as vulnerability assessments, patch management, URL filtering and more. Now, service providers can eliminate complexity and make security a centerpiece of their offerings while increasing SLAs, decreasing churn, and generating more recurring revenue. Get upgraded security with integrated AI-based defenses that protect clients from modern threats, make smarter use of resources so your team can focus on clients, and earn new recurring revenue and higher margins that strengthen your business. Enriched with next-gen, full-stack anti-malware protection and comprehensive yet simple management tools, built on top of our industry-leading backup and data recovery solution, Acronis Cyber Platform simplifies onboarding, daily operations, and reporting, and combats advanced attacks with new use cases enabled by integration. Acronis Cyber Platform makes it easy to deliver the modern cyber protection your clients seek. Acronis is majority-owned by EQT.

Average Rating: 4.7/5.0

Total Reviews: 1,466

How Do G2 Users Rate Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 10.0/10 (Category avg: 9.1/10)
  • Automated remediation: 10.0/10 (Category avg: 8.7/10)
  • Automated investigation: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

  • Seller: Acronis
  • Company Website:
  • Year Founded: 2003
  • HQ Location: Schaffhausen
  • LinkedIn® Page: www.linkedin.com
    1,923 employees on LinkedIn®
  • Ownership: Acronis is majority-owned by EQT

Who Uses This Product?

  • Who Uses This: CEO, Director
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 69% Small, 27% Medium

What Do G2 Reviewers Say About Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Acronis Cyber Protect Cloud, enjoying centralized management of backups and protections.
  • Users appreciate the convenience of centralized backup management with Acronis Cyber Protect Cloud, streamlining tasks effectively.
  • Users value the ease of backup with Acronis Cyber Protect Cloud, appreciating its efficiency and straightforward training.
  • Users appreciate the easy management of backups and protection features in one console, enhancing efficiency and reliability.
  • Users value the comprehensive security offered by Acronis Cyber Protect Cloud, ensuring reliable data protection and quick recovery.
Cons
  • Users have noted a slow performance of Acronis Cyber Protect Cloud, particularly during peak usage and larger operations.
  • Users find the pricing relatively high, making it challenging to propose to customers in the African market.
  • Users find the setup and management complexity challenging, along with pricing that feels high compared to competitors.
  • Users often struggle with poor customer support, leading to confusion and frustration during setup and troubleshooting.
  • Users often face backup issues, including failures and unaccounted removals in the management portal, complicating their experience.

What Are Recent G2 Reviews of Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

What Are G2 Users Discussing About Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

Huntress Managed EDR

Huntress Managed EDR is a fully managed endpoint detection and response (EDR) solution that pairs continuous endpoint monitoring with a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) with limited in-house security staff, it monitors Windows, macOS, and Linux endpoints for malicious behavior, including ransomware, persistent footholds, and lateral movement, and pairs automated detection with expert threat hunters who validate and respond to incidents in real time. Huntress Managed EDR reduces attacker dwell time through rapid threat containment and remediation, giving lean IT and security teams enterprise-grade endpoint protection without the overhead of building an internal SOC.

Average Rating: 4.8/5.0

Total Reviews: 975

How Do G2 Users Rate Huntress Managed EDR?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.6/10 (Category avg: 9.1/10)
  • Automated remediation: 9.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.5/10 (Category avg: 8.9/10)

Who Is the Company Behind Huntress Managed EDR?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 78% Small, 18% Medium

What Do G2 Reviewers Say About Huntress Managed EDR?

AI-generated summary from verified user reviews

Pros
  • Users praise the responsive customer support of Huntress Managed EDR, valuing its clarity and effectiveness in assistance.
  • Users appreciate the ease of use of Huntress Managed EDR, highlighting its intuitive interface and seamless integration.
  • Users commend Huntress for its unmatched threat detection, enhancing security visibility and simplifying device management.
  • Users value the expert monitoring and effective protection of Huntress Managed EDR, appreciating its simplicity and reliability.
  • Users value the 24/7 continuous monitoring of Huntress Managed EDR, ensuring proactive cybersecurity management for their systems.
Cons
  • Users note that improvements are needed in the AV UI management and exception handling processes for Huntress EDR.
  • Users note the lack of customization limits control and requires proper setup for optimal usage.
  • Users find the reporting tools limited, making it challenging to demonstrate value to clients effectively.
  • Users express concern over the lack of detailed alerts from Huntress Managed EDR during critical investigations.
  • Users experience integration issues with Huntress, finding a gap between advertised features and actual performance.

What Are Recent G2 Reviews of Huntress Managed EDR?

What Are G2 Users Discussing About Huntress Managed EDR?

eSentire

eSentire is a leader in Controlled Autonomy SecOps, protecting thousands of organizations across 35+ industries around the world. Founded in 2001, the company’s Controlled Autonomy SecOps operating model pairs agentic AI operatives with engineered human-judgment controls, delivering expert-depth security outcomes at machine speed without ceding accountability to opaque automation. Powered by the unified agentic AI Atlas Platform, eSentire’s Atlas AI + 24/7 expert human SOC coverage delivers offensive capabilities that preempt exposures before attackers do, detect, and respond to stop threats in real time. For more information, visit esentire.com and follow @eSentire.

Average Rating: 4.6/5.0

Total Reviews: 284

How Do G2 Users Rate eSentire?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.1/10 (Category avg: 9.1/10)
  • Automated remediation: 8.6/10 (Category avg: 8.7/10)
  • Automated investigation: 8.9/10 (Category avg: 8.9/10)

Who Is the Company Behind eSentire?

  • Seller: eSentire
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Waterloo, Ontario
  • LinkedIn® Page: www.linkedin.com
    556 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, CTO
  • Top Industries: Financial Services, Legal Services
  • Company Size: 59% Medium, 23% Large

What Do G2 Reviewers Say About eSentire?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid response time of eSentire, enhancing their confidence in security management and threat resolution.
  • Users value the excellent customer support at eSentire, with quick responses and a human touch readily available.
  • Users find eSentire's managed SOC services vital for constant monitoring and operational security, especially after hours.
  • Users value eSentire's deep expertise and 24/7 support, providing reliable cybersecurity solutions tailored to their needs.
  • Users value the 24/7 continuous monitoring by eSentire, enabling quick responses to anomalies and ensuring peace of mind.
Cons
  • Users experience communication issues with eSentire, often feeling that clarity and support are lacking during interactions.
  • Users experience an inefficient alert system requiring internal validation, impacting overall usability and response times.
  • Users find the pricing of eSentire to be steep, limiting access to additional services or features.
  • Users face portal issues with eSentire, preferring direct email updates for ticket details rather than mandatory portal logins.
  • Users find poor reporting from eSentire problematic, citing infrequent reviews and a lack of actionable insights.

What Are Recent G2 Reviews of eSentire?

What Are G2 Users Discussing About eSentire?

ESET PROTECT

ESET PROTECT is an AI-native cybersecurity platform that combines next-generation prevention, detection, and response capabilities with AI-powered security technologies and 24/7 managed detection and response (MDR) services delivered by ESET security experts. A single, unified management console provides centralized visibility across security operations, helping organizations automate repetitive tasks and enabling security teams to focus on higher-priority activities. With exceptional detection accuracy and fewer false positives, the platform helps reduce alert noise and identify real threats faster. Designed to help organizations stay ahead of known and emerging threats, ESET PROTECT strengthens cyber resilience, improves operational efficiency, and supports compliance initiatives. Why Organizations Choose ESET PROTECT Reduce Security Burden with Expert-Led Protection Fill cybersecurity skill gaps with 24/7 managed detection and response (MDR) backed by ESET experts. Gain faster incident response, actionable threat intelligence, and access to a team of experienced threat hunters. Secure AI Workflows Without Slowing Innovation Adopt AI confidently while protecting your organization from emerging AI-related threats. Secure AI conversations from malicious responses and risky prompts, protect against AI agent attacks, and detect suspicious AI agent behavior. Confidence in Cybersecurity with ESET AI Technologies Benefit from AI-powered technologies built specifically for cybersecurity. ESET helps security teams prevent threats earlier, prioritize and respond faster, improve threat detection, reduce noise, and protect people, devices, data, and businesses across multiple perimeters. Strengthen Compliance Readiness Navigate growing compliance demands with confidence. Our endpoint protection solutions help you assess risk, automate compliance processes, and demonstrate adherence to regulatory, customer, and industry requirements. Support compliance with NIS2, DORA, GDPR, ISO 27001, and more through continuous monitoring, automated evidence collection, and actionable recommendations to strengthen your security and compliance posture.

Average Rating: 4.6/5.0

Total Reviews: 976

How Do G2 Users Rate ESET PROTECT?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.7/10 (Category avg: 9.1/10)
  • Automated remediation: 9.8/10 (Category avg: 8.7/10)
  • Automated investigation: 9.6/10 (Category avg: 8.9/10)

Who Is the Company Behind ESET PROTECT?

  • Seller: ESET
  • Company Website:
  • Year Founded: 1992
  • HQ Location: Bratislava, Slovak Republic
  • LinkedIn® Page: www.linkedin.com
    2,014 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Network Administrator
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 45% Small

What Do G2 Reviewers Say About ESET PROTECT?

AI-generated summary from verified user reviews

Pros
  • Users find ESET PROTECT's intuitive interface makes setup and ongoing management straightforward and efficient.
  • Users value ESET PROTECT for its robust protection against cyber threats, safeguarding sensitive data effectively.
  • Users praise the reliability of ESET PROTECT, valuing its thorough threat detection and ease of management.
  • Users value the robust security features of ESET PROTECT, ensuring comprehensive protection against cyber threats.
  • Users value the centralized management of ESET PROTECT, streamlining policy application across all endpoints effortlessly.
Cons
  • Users find the learning curve steep with ESET PROTECT, citing frustrations with outdated interfaces and difficult configurations.
  • Users find difficult configuration challenges with ESET PROTECT, complicating management and requiring considerable expertise to navigate.
  • Users find ESET PROTECT to have a not user-friendly interface, making navigation and configuration challenging, especially for newcomers.
  • Users find the lack of clarity in ESET PROTECT's interface and settings can be challenging to navigate effectively.
  • Users find difficult navigation in ESET PROTECT's interface, complicating the configuration and usage for first-time users.

What Are Recent G2 Reviews of ESET PROTECT?

What Are G2 Users Discussing About ESET PROTECT?

ThreatDown

AI has changed what businesses need to protect and how fast they need to respond. Ungoverned AI tools leak data through identities and API keys nobody's watching, while AI-driven attacks compress exploit windows from months to hours and generate the alert volume of dozens of attackers at once — a scale problem no team can staff its way out of. ThreatDown meets AI-scale risk with an AI-native platform built for more than the endpoint — one lightweight agent, one console, no tool sprawl. AI visibility flags every AI tool in use and blocks sensitive data before it reaches the model. ThreatDown ITDR monitors every identity, human and non-human, to catch compromise before attackers act. And Endpoint and email security stop attacks where they start - on the device and in the inbox. On top, ThreatDown MDR pairs AI-powered triage, with elite analysts who respond 24/7, detecting threats in a median of 5 minutes and containing them in 19. It's enterprise-grade protection at AI speed, without the headcount or complexity.

Average Rating: 4.6/5.0

Total Reviews: 1,049

How Do G2 Users Rate ThreatDown?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 9.1/10 (Category avg: 8.7/10)
  • Automated investigation: 9.1/10 (Category avg: 8.9/10)

Who Is the Company Behind ThreatDown?

  • Seller: ThreatDown
  • Company Website:
  • HQ Location: Santa Clara, US
  • LinkedIn® Page: www.linkedin.com
    164 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 48% Small, 41% Medium

What Do G2 Reviewers Say About ThreatDown?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of ThreatDown, especially for managing clients and deploying the product effectively.
  • Users appreciate the ease of use and streamlined admin console of ThreatDown, enhancing their overall experience.
  • Users praise the awesome security of ThreatDown, appreciating its great protection and proactive network monitoring.
  • Users value the efficient threat detection of ThreatDown, enhancing security management and peace of mind.
  • Users value the quick and effective customer support from ThreatDown, ensuring smooth resolution of any issues.
Cons
  • Users struggle with poor customer support, finding it difficult to reach assistance when needed for improvements.
  • Users find the lack of clarity in reporting customization and integrations frustrating, complicating their overall experience.
  • Users find the missing features in ThreatDown limiting, especially regarding policy application and language support.
  • Users report false positives blocking legitimate software, but issues are typically resolved quickly with support.
  • Users highlight the communication issues in ThreatDown, lacking direct message features for better user notifications and alerts.

What Are Recent G2 Reviews of ThreatDown?

What Are G2 Users Discussing About ThreatDown?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.3/10 (Category avg: 9.1/10)
  • Automated remediation: 9.4/10 (Category avg: 8.7/10)
  • Automated investigation: 9.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, enjoying its simple implementation and daily operation.
  • Users appreciate the responsive SOC team and improved dashboard features, enhancing control and reducing notification noise.
  • Users value the effective threat detection of Cynet, appreciating its responsiveness and improved dashboard features.
  • Users commend Cynet's responsive customer support, quickly resolving issues and enhancing the overall experience with the product.
  • Users commend Cynet for its robust security features, seamless implementation, and excellent support, enhancing overall cybersecurity management.
Cons
  • Users find limited customization options in dashboards and integrations, affecting their overall experience with Cynet.
  • Users note feature limitations in customization and integration options, which may hinder user experience and flexibility.
  • Users find a lack of customization in dashboards and features, limiting their ability to tailor the platform effectively.
  • Users experience limited features with Cynet, particularly in reporting options and third-party integrations.
  • Users note that some missing features hinder full integration and customization, impacting overall user experience.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

Huntress Managed ITDR

Huntress Managed ITDR is a fully managed identity threat detection and response (ITDR) solution that pairs continuous identity monitoring across Microsoft 365 and Google Workspace with a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) with limited in-house identity security expertise, it detects identity-based threats such as credential compromise, privilege escalation, and lateral movement, and pairs automated behavioral analysis with expert analysts who investigate and respond to identity incidents in real time. Huntress Managed ITDR reduces dwell time on compromised accounts through rapid detection and remediation, giving lean IT and security teams enterprise-grade identity protection without the overhead of building an in-house identity security team. Our enterprise-grade solution gives you continuous monitoring for identity-based threats, rapid detection of unauthorized access, location-based and VPN/tunnel/proxy anomalies, and fast response to suspicious activities like rogue applications, shadow workflows, and business email compromise (BEC) scams. By focusing on protecting user credentials and session tokens, Huntress keeps your organization's digital identities safe, even as attackers develop sneakier tactics.

Average Rating: 4.8/5.0

Total Reviews: 154

How Do G2 Users Rate Huntress Managed ITDR?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.6/10 (Category avg: 9.1/10)
  • Automated remediation: 9.7/10 (Category avg: 8.7/10)
  • Automated investigation: 9.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Huntress Managed ITDR?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 73% Small, 22% Medium

What Do G2 Reviewers Say About Huntress Managed ITDR?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring of Huntress Managed ITDR, enabling swift detection of identity-based threats and account anomalies.
  • Users value the quick threat detection and intervention of Huntress Managed ITDR, ensuring timely protection against account compromises.
  • Users value the rapid detection and intervention of Huntress Managed ITDR, ensuring prompt responses to account compromises.
  • Users appreciate the easy integrations of Huntress Managed ITDR, seamlessly fitting into existing systems and enhancing security.
  • Users praise the rapid and thorough customer support from Huntress, which enhances their overall experience significantly.
Cons
  • Users express concerns over inadequate detection of failed login attempts, hindering timely threat response and investigation efforts.
  • Users experience an inefficient alert system that delays detection, impacting response times to security threats.
  • Users desire more customization control in the management console for enhanced system granularity in settings.
  • Users experience portal issues with manual escalations and mismatched visuals, complicating their overall management experience.
  • Users find the interface clumsy and confusing, which complicates navigation and login approval processes.

What Are Recent G2 Reviews of Huntress Managed ITDR?

Zscaler Sec Ops

Red Canary provides managed detection and response (MDR), finding and stopping threats before business impact. You get a security operations platform and 24x7 service that proactively monitors for malicious and suspicious behaviors and responds to stop them from becoming serious security incidents. MDR services complement and enhance your SOC, operating as a trusted partner, offering the expertise, tools, and support needed to strengthen your overall security posture. The platform works using several key components: Your existing endpoint and cloud workload sensors/agents Alert collectors and integrations with your alert-generating security products Integrations with your cloud service providers, identity platforms, and SaaS applications Cloud-hosted collection, detection, and response platforms Our Cyber Incident Response Team (CIRT) Our Threat Hunting team The sensors already running on the endpoints and cloud workloads that make up your corporate and production environments collect detailed telemetry about what is happening in those systems. The telemetry and alerts from your cloud service provider, identity platforms, SaaS applications, and other security products are both sent to our cloud-hosted platform. This allows our CIRT to perform analysis of that data to identify and confirm suspicious activity and security incidents. The security orchestration and response capabilities can execute automations using playbooks on endpoints for response and remediation. Our unique combination of detection-as-code detection engineering, proactive threat hunting, and agentic AI uncovers critical threats deep within your environment before they cause harm. Our renowned in-house intelligence team provides tactical insights tailored to your unique environment, helping you understand the adversaries you face, their specific tactics, and how to stop them. Red Canary enables 10X faster response to threats, helping you slash your mean time to respond (MTTR) by detecting threats early, investigating with precision, and enabling rapid containment, both expert-led and automated. Red Canary helps get more value from your existing tech stack continuously analyzing data across identities, endpoint, and cloud.

Average Rating: 4.6/5.0

Total Reviews: 133

How Do G2 Users Rate Zscaler Sec Ops?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.7/10 (Category avg: 9.1/10)
  • Automated remediation: 8.8/10 (Category avg: 8.7/10)
  • Automated investigation: 8.8/10 (Category avg: 8.9/10)

Who Is the Company Behind Zscaler Sec Ops?

  • Seller: Zscaler
  • Company Website:
  • Year Founded: 2008
  • HQ Location: San Jose, California
  • LinkedIn® Page: www.linkedin.com
    9,150 employees on LinkedIn®
  • Ownership: NASDAQ:ZS

Who Uses This Product?

  • Who Uses This: Security Analyst, Security Engineer
  • Top Industries: Financial Services, Manufacturing
  • Company Size: 56% Large, 39% Medium

What Do G2 Reviewers Say About Zscaler Sec Ops?

AI-generated summary from verified user reviews

Pros
  • Users value the responsive and knowledgeable customer support from Red Canary, ensuring quick solutions and peace of mind.
  • Users feel reassured by the advanced threat detection capabilities of Zscaler Sec Ops, enhancing their organization's security posture.
  • Users value the reliable support from Red Canary, ensuring peace of mind with continuous monitoring and expert assistance.
  • Users value the efficiency of alert management with Red Canary, enjoying reduced manual workload and improved incident response.
  • Users appreciate the efficient automation and integrations of Red Canary, simplifying incident response and enhancing daily operations.
Cons
  • Users experience an inefficient alert system with slow response times and limited integration options, impacting security effectiveness.
  • Users express frustration over communication issues with Zscaler Sec Ops, affecting support and access clarity.
  • Users find the high costs of Zscaler Sec Ops a significant drawback, impacting overall value and accessibility.
  • Users find difficult navigation to be a challenge, requiring time to adapt to the system's interface.
  • Users face integration issues with Zscaler Sec Ops, finding compatibility with various systems lacking and challenging.

What Are Recent G2 Reviews of Zscaler Sec Ops?

What Are G2 Users Discussing About Zscaler Sec Ops?

Deepwatch

Deepwatch® delivers AI-Native MDR through the Deepwatch Guardian MDR Platform™, combining the Deepwatch Detection Engine, Threat Intelligence, the NEXA™ AI Ecosystem, and Expert Oversight to help organizations identify the threats that matter most and accelerate investigation, containment, and response. By integrating with existing security technologies without requiring rip-and-replace, Deepwatch helps organizations reduce risk, strengthen operational resilience, and respond with confidence. Deepwatch Awards and Recognition: - Forbes America’s Best Startup Employers: 2026, 2025, 2024, 2023, 2022 - Great Place to Work® Certified: 2025, 2024, 2023, 2022, 2021 - Cybersecurity Breakthrough Award: Managed Security Solution of the Year 2025 - CRN Security 100 - Top 20 Endpoint and Managed Security Companies 2025 - Cyber Defense Magazine - 12 Global Infosec Awards 2024 - LinkedIn Top 50 Startups 2023 - Military Times Best for Vets Employers 2024 - US Department of Labor Hire Vets Gold Award 2024 - InHerSight #1 Cyber Workplace for Women 2023 - Fortress Cybersecurity Award: 2023, 2022 - CISO Choice Awards: MSSP Winner: 2022, 2021, 2020 - Backed by premier investors with >$275 Million in growth capital from Goldman Sachs, Vista Equity Partners, Springcoast, Splunk Ventures, and ABS Capital - Splunk Global Partner - #1 Volume MDR/MSSP

Average Rating: 4.7/5.0

Total Reviews: 24

How Do G2 Users Rate Deepwatch?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.4/10 (Category avg: 9.1/10)
  • Automated remediation: 8.5/10 (Category avg: 8.7/10)
  • Automated investigation: 9.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Deepwatch?

  • Seller: Deepwatch
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Palo Alto, California, United States
  • LinkedIn® Page: www.linkedin.com
    228 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 46% Medium

What Do G2 Reviewers Say About Deepwatch?

AI-generated summary from verified user reviews

Pros
  • Users commend Deepwatch for their swift response time, ensuring quick resolutions and efficient handling of security events.
  • Users value the continuous monitoring by Deepwatch, enhancing security awareness and detection with top-notch responsiveness.
  • Users find implementation easy with Deepwatch due to smooth transitions and skilled support throughout the process.
  • Users appreciate Deepwatch's reliable service, which proactively addresses threats and ensures a smooth operational experience.
  • Users value the expert staff and responsive support from Deepwatch, enhancing their security operations significantly.
Cons
  • Users report communication issues with Deepwatch, affecting real-time collaboration and timely support for requests.
  • Users feel the limited integration options hinder Deepwatch's performance and complicate the overall user experience.
  • Users experience slow performance with Deepwatch, especially during complex searches and initial setup, hindering efficiency.
  • Users face deployment issues with Deepwatch, finding initial onboarding and component operations time-consuming and complicated.
  • Users find the difficult navigation in Deepwatch's Service Now integration less intuitive compared to alternatives like Jira.

What Are Recent G2 Reviews of Deepwatch?

Secureworks Taegis MDR

Secureworks® Taegis™ MDR is an industry-leading solution that harnesses the power of AI with human expertise to deliver 24/7 threat monitoring, detection, investigation, and response capabilities. By integrating security telemetry from hundreds of sources, customers can maximize their current security investments and see more, detect better, and respond faster. Delivered on top of the open Taegis XDR platform, the solution provides comprehensive coverage across the entire attack surface - endpoints, network, cloud, email, identity, OT and business applications – and customers have access to the same console as Secureworks security experts, who they are able to reach within 90 seconds through live chat.

Average Rating: 4.6/5.0

Total Reviews: 48

How Do G2 Users Rate Secureworks Taegis MDR?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.1/10 (Category avg: 9.1/10)
  • Automated remediation: 8.0/10 (Category avg: 8.7/10)
  • Automated investigation: 8.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Secureworks Taegis MDR?

  • Seller: Sophos
  • Year Founded: 1985
  • HQ Location: Oxfordshire
  • LinkedIn® Page: www.linkedin.com
    5,550 employees on LinkedIn®
  • Ownership: LSE:SOPH

Who Uses This Product?

  • Top Industries: Financial Services, Computer & Network Security
  • Company Size: 52% Medium, 38% Large

What Do G2 Reviewers Say About Secureworks Taegis MDR?

AI-generated summary from verified user reviews

Pros
  • Users praise the immediate response of Secureworks Taegis MDR, enhancing incident resolution and reducing team workload.
  • Users appreciate the 24/7 monitoring of Secureworks Taegis MDR, ensuring constant protection and quick incident resolution.
  • Users value the exceptional customer support from Secureworks Taegis MDR, enhancing their overall business security experience.
  • Users appreciate the dashboard usability of Secureworks Taegis MDR, enabling efficient use by non-technical staff.
  • Users value the easy integrations of Secureworks Taegis MDR, enabling seamless connectivity with other vendors like Microsoft.
Cons
  • Users find difficult navigation challenging, particularly with complex features and initial setup, requiring time and expertise.
  • Users note that implementation of new integrations can be slow, particularly for non-mainstream tools, affecting overall experience.
  • Users find integration issues with third-party tools challenging, complicating the overall experience and setup process.
  • Users find the learning curve steep, particularly in navigating advanced features and optimizing setup for alerts.
  • Users note the limited features of Secureworks Taegis MDR, which may lack some integrations with niche tools.

What Are Recent G2 Reviews of Secureworks Taegis MDR?

What Are G2 Users Discussing About Secureworks Taegis MDR?

Field Effect MDR

Field Effect delivers intelligence-grade managed detection and response for the AI era. Built on Federated Smart Compute™ and nation-state tradecraft, our holistic MDR platform uncovers weaknesses early, blocks attacks in real time, and reduces risk across the entire threat surface—endpoint, network, cloud, and more. With an 18-second median time to detect, Field Effect helps MSPs and overwhelmed IT teams outpace agentic attacks and achieve premium protection with the team they have.

Average Rating: 4.8/5.0

Total Reviews: 54

How Do G2 Users Rate Field Effect MDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 7.6/10 (Category avg: 8.7/10)
  • Automated investigation: 9.1/10 (Category avg: 8.9/10)

Who Is the Company Behind Field Effect MDR?

  • Seller: Field Effect
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Ottawa
  • LinkedIn® Page: www.linkedin.com
    149 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Small, 33% Medium

What Do G2 Reviewers Say About Field Effect MDR?

AI-generated summary from verified user reviews

Pros
  • Users commend the prompt and knowledgeable customer support, enhancing their experience with Field Effect MDR's reliable service.
  • Users find the ease of use of Field Effect MDR exceptional, enhancing their cybersecurity management experience effortlessly.
  • Users admire the high-quality alerts from Field Effect MDR that enhance response capabilities and reduce false positives.
  • Users value the effective threat detection of Field Effect MDR, ensuring continuous and comprehensive cybersecurity protection.
  • Users value the meaningful and actionable alerts from Field Effect MDR, enhancing their security response capabilities.
Cons
  • Users face alert issues with Field Effect MDR, requiring additional support for clarity and integration problems.
  • Users express frustration with the inefficient alert system, often overwhelmed by the high volume of alerts received.
  • Users find communication issues arise due to overly technical explanations and difficulties in navigating the support portal.
  • Users feel there is insufficient information on alerts, often needing support for more details during investigations.
  • Users find the learning curve steep for Field Effect MDR, requiring time to tune the platform effectively.

What Are Recent G2 Reviews of Field Effect MDR?

What Are G2 Users Discussing About Field Effect MDR?

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 5.0/5.0

Total Reviews: 83

How Do G2 Users Rate UnderDefense MAXI?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.8/10 (Category avg: 9.1/10)
  • Automated remediation: 9.5/10 (Category avg: 8.7/10)
  • Automated investigation: 9.9/10 (Category avg: 8.9/10)

Who Is the Company Behind UnderDefense MAXI?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Information Technology and Services, Marketing and Advertising
  • Company Size: 54% Small, 40% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users value the high visibility UnderDefense MAXI provides into security alerts, streamlining threat management and response.
  • Users commend the responsive and effective customer support of UnderDefense MAXI, enhancing their cybersecurity management and experience.
  • Users commend UnderDefense MAXI for its effective cybersecurity solutions, enhancing security management and response efficiency.
  • Users value the information accuracy provided by UnderDefense, which clarifies security issues and enhances response efficiency.
  • Users highlight the quick issue resolution by UnderDefense, improving security alert management and enhancing overall security operations.
Cons
  • Users feel a lack of automation features limits control over the dashboard for UnderDefense MAXI.
  • Users desire more control over the dashboard, seeking enhanced customization and automated update options with UnderDefense MAXI.
  • Users note that limited integration requires significant setup time to ensure proper tool configuration.
  • Users find the setup process challenging, requiring significant time and effort for proper tool integration.

What Are Recent G2 Reviews of UnderDefense MAXI?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated