Best Security Orchestration, Automation, and Response (SOAR) Software

How Many Security Orchestration, Automation, and Response (SOAR) Software Products Does G2 Track?

Total Products under this Category: 99

Category Stats (Sep 2026)

  • Average Rating: 4.54/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: ReliaQuest GreyMatter (+1.22%) - Among all products in this category, ReliaQuest GreyMatter recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Security Orchestration, Automation, and Response (SOAR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,700+ Authentic Reviews
  • 99+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

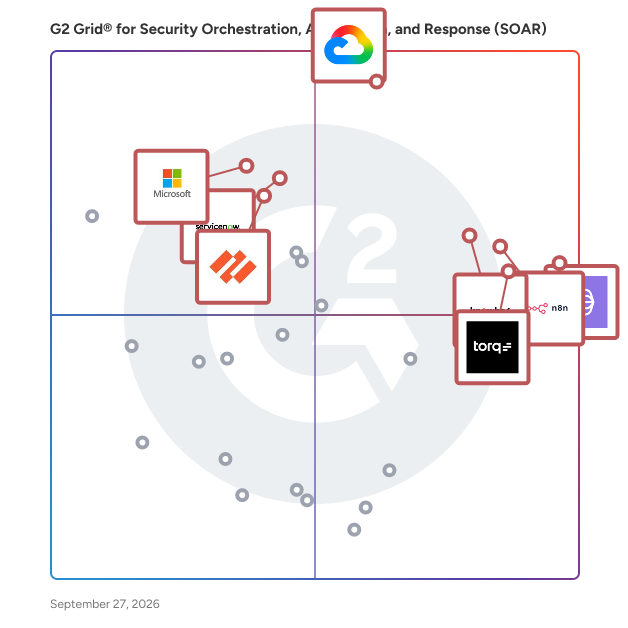
G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software

G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, Tines Stories, n8n, Torq AI SOC Platform, KnowBe4 PhishER/PhishER Plus, ServiceNow Security Operations, Microsoft Sentinel, and Palo Alto Cortex XSIAM.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-orchestration-automation-and-response-soar/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=tines-stories&focus%5B%5D=n8n&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=knowbe4-phisher-phisher-plus&focus%5B%5D=servicenow-security-operations&focus%5B%5D=microsoft-sentinel&focus%5B%5D=palo-alto-cortex-xsiam)

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 141

How Do G2 Users Rate Google Security Operations?

  • Automated Remediation: 9.9/10 (Category avg: 8.8/10)
  • Quality of Support: 8.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.1/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Student, Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 40% Small, 34% Medium

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation of Google Security Operations, enhancing efficiency in threat management.
  • Users value the high-level threat detection capabilities of Google Security Operations, enhancing their security response efficiency.
  • Users find Google Security Operations very easy to use, allowing for quick incident analysis and efficient responses.
  • Users value the comprehensive security of Google Security Operations for effectively detecting and responding to threats.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and providing a unified security view.
Cons
  • Users find the costly upkeep of Google Security Operations challenging, especially for large organizations.
  • Users often face a steep learning curve with Google Security Operations, especially if unfamiliar with Google Cloud services.
  • Users find the implementation and configuration complex, requiring more time and resources compared to other tools.
  • Users find the learning difficulty of Google Security Operations challenging due to its complex features and setup.
  • Users find limited customization in Google Security Operations hinders adaptability and user experience for specific security needs.

What Are Recent G2 Reviews of Google Security Operations?

Tines Stories

Tines is the intelligent workflow platform trusted by the world's most advanced organizations. Companies like Coinbase, Databricks, Mars, Reddit, and SAP use Tines to power their most important workflows. With Tines, they’ve built a secure, flexible foundation to operationalize AI agents and intelligent workflows, unlocking productivity, moving faster, and future-proofing how work gets done.

Average Rating: 4.7/5.0

Total Reviews: 424

How Do G2 Users Rate Tines Stories?

  • Automated Remediation: 9.3/10 (Category avg: 8.8/10)
  • Quality of Support: 9.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Tines Stories?

  • Seller: Tines
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Dublin, IE
  • LinkedIn® Page: www.linkedin.com
    619 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Medium, 35% Large

What Do G2 Reviewers Say About Tines Stories?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Tines, enabling seamless automation without any coding knowledge.
  • Users highlight the flexibility and ease of automation with Tines, making integration and workflow creation seamless.
  • Users commend Tines for its exceptional customer support, appreciating the team's responsiveness and proactive assistance.
  • Users highlight Tines for its ease of use and rapid implementation, significantly boosting team efficiency and automation capabilities.
  • Users value Tines for its time-saving automation capabilities, allowing teams to focus on more strategic activities efficiently.
Cons
  • Users note a steep learning curve with Tines, especially for newcomers to automation and orchestration tools.
  • Users find Tines lacking in missing features that can hinder initial onboarding and expectations for functionality.
  • Users note a lack of features in Tines, pointing out missing options and inconsistencies in functionality.
  • Users find the complexity of advanced features in Tines overwhelming, especially for teams lacking a clear strategy.
  • Users find Tines has a difficult learning curve, particularly for newcomers to automation and orchestration tools.

What Are Recent G2 Reviews of Tines Stories?

What Are G2 Users Discussing About Tines Stories?

n8n

n8n is a workflow automation platform built for technical teams operationalizing AI. Built for technical teams, it offers 500+ integrations, custom code flexibility, and self-hosting options. With 180k+ Github Stars and a thriving community, n8n enables teams to build production-ready automation workflows that bridge AI with real business processes.

Average Rating: 4.7/5.0

Total Reviews: 306

How Do G2 Users Rate n8n?

  • Automated Remediation: 8.2/10 (Category avg: 8.8/10)
  • Quality of Support: 8.1/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.5/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind n8n?

  • Seller: n8n GmbH
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Berlin, Berlin
  • Twitter: @n8n_io
    81,824 Twitter followers
  • LinkedIn® Page: linkedin.com
    1,275 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Founder
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 18% Medium

What Do G2 Reviewers Say About n8n?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of n8n, enjoying intuitive designs that simplify complex workflow automation.
  • Users value the flexible automation capabilities of n8n, enhancing productivity through easy and extensive workflow management.
  • Users appreciate the extensive integrations of n8n, enabling seamless connections between various tools within workflows.
  • Users value the intuitive visual editor of n8n, enabling easy creation of complex workflows and automations.
  • Users enjoy the efficient workflow management of n8n, streamlining tasks and enhancing productivity through automation.
Cons
  • Users note a significant learning curve with n8n, requiring time and tutorials to optimize workflows effectively.
  • Users find n8n's difficult learning curve challenging, especially for non-developers managing complex workflows effectively.
  • Users note the absence of essential features in self-hosted n8n, hindering functionality and ease of use.
  • Users struggle with the poor interface design of n8n, finding it unresponsive and difficult to navigate effectively.
  • Users find the limitations in debugging and handling large workflows a significant challenge when using n8n.

What Are Recent G2 Reviews of n8n?

What Are G2 Users Discussing About n8n?

Torq AI SOC Platform

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats. Working alongside your SecOps staff, the Torq platform integrates with your security stack to facilitate containment and remediation workflows.

Average Rating: 4.8/5.0

Total Reviews: 151

How Do G2 Users Rate Torq AI SOC Platform?

  • Automated Remediation: 9.2/10 (Category avg: 8.8/10)
  • Quality of Support: 9.6/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.4/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Torq AI SOC Platform?

  • Seller: torq
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @torq_io
    1,944 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    470 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Medium, 30% Small

What Do G2 Reviewers Say About Torq AI SOC Platform?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Torq AI SOC Platform, making it accessible for all skill levels.
  • Users value the efficiency of automated security workflows in Torq, enhancing both speed and effectiveness in threat management.
  • Users value the automation capabilities of Torq AI SOC Platform, enhancing efficiency and streamlining security workflows effectively.
  • Users appreciate the no-code automation capabilities of Torq, streamlining workflows and enhancing overall operational efficiency.
  • Users value the real-time threat detection of Torq AI SOC Platform, enhancing efficiency in responding to security incidents.
Cons
  • Users face a difficult learning curve with Torq AI SOC Platform, requiring significant training and support for effective use.
  • Users face a significant learning curve with Torq AI SOC Platform, requiring time and proper training for effective use.
  • Users note the missing features in Torq AI SOC Platform, especially regarding playbooks and incident management capabilities.
  • Users note that improvement is needed in grouping findings, vendor integration, and overall flexibility for better experience.
  • Users face poor interface design in Torq, including unresponsive buttons and a challenging debugging process.

What Are Recent G2 Reviews of Torq AI SOC Platform?

KnowBe4 PhishER/PhishER Plus

KnowBe4 PhishER Plus delivers automated incident response to eliminate SOC noise and remediate malicious emails across your organization simultaneously. It leverages AI to categorize reported messages across email and Microsoft Teams, automatically responding to reporters, flagging high-risk messages, and removing threats across all mailboxes. SOC teams can even flip malicious messages into training simulations to see who would have fallen victim. Customers report saving upwards of 99% of triage time, highly praising the platform's intuitive, user-friendly interface that transforms overwhelming manual workflows into fast, consistent actions. This layer of defense reviews threats slipping past other security layers, offering a single pane of glass view with leading third-party integrations like CrowdStrike, Webroot, and VirusTotal. PhishER Plus turns manual email triaging into a proactive, automated security posture.

Average Rating: 4.5/5.0

Total Reviews: 570

How Do G2 Users Rate KnowBe4 PhishER/PhishER Plus?

  • Automated Remediation: 8.7/10 (Category avg: 8.8/10)
  • Quality of Support: 9.2/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.9/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind KnowBe4 PhishER/PhishER Plus?

  • Seller: KnowBe4, Inc.
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Clearwater, FL
  • Twitter: @KnowBe4
    16,161 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,642 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Director of IT
  • Top Industries: Financial Services, Primary/Secondary Education
  • Company Size: 75% Medium, 13% Large

What Do G2 Reviewers Say About KnowBe4 PhishER/PhishER Plus?

AI-generated summary from verified user reviews

Pros
  • Users value the effective phishing tests and automation features of KnowBe4 PhishER, enhancing their security posture.
  • Users appreciate the email threat scoring feature of KnowBe4 PhishER, enabling proactive responses to potential threats.
  • Users value the automation capabilities of KnowBe4 PhishER, enhancing efficiency in identifying and managing phishing threats.
  • Users find KnowBe4 PhishER/PhishER Plus remarkably easy to use, enhancing efficiency in triaging and reporting spam emails.
  • Users appreciate the streamlined threat detection of KnowBe4 PhishER, making phishing email management effortless and efficient.
Cons
  • Users report issues with clean emails landing in the Junk Email folder, leading to troubleshooting difficulties and uncertainty.
  • Users experience frequent false positives, complicating automation and necessitating time-consuming manual reviews for accuracy.
  • Users experience ineffective email security with PhishER, as it fails to correctly filter phishing emails into the inbox.
  • Users find the learning curve intimidating for setup, requiring additional assistance for effective use of PhishER/PhishER Plus.
  • Users find the inefficient automation of PhishER frustrating, as it often misses campaigns and requires manual intervention.

What Are Recent G2 Reviews of KnowBe4 PhishER/PhishER Plus?

What Are G2 Users Discussing About KnowBe4 PhishER/PhishER Plus?

ServiceNow Security Operations

ServiceNow Security Operations is a sophisticated software solution designed to enhance threat and vulnerability management as well as incident response for organizations. By leveraging artificial intelligence, this platform empowers security teams to operate more efficiently and effectively, allowing for streamlined collaboration across IT, security, and risk management departments. The primary goal of ServiceNow Security Operations is to simplify complex security processes while minimizing risks associated with cybersecurity threats. Targeted at security teams within organizations of various sizes, ServiceNow Security Operations addresses the need for a cohesive approach to managing security incidents and vulnerabilities. It is particularly beneficial for organizations that utilize multiple security tools, as it integrates security and vulnerability data from these existing systems. This integration enables teams to respond to threats more rapidly by automating critical workflows and processes, thus reducing the manual effort traditionally required in incident response. The platform is suitable for both small businesses and large enterprises, making it a versatile choice for organizations looking to enhance their cybersecurity measures. Key features of ServiceNow Security Operations include intelligent workflows that automate routine tasks, allowing security professionals to focus on more strategic initiatives. The platform’s AI-driven capabilities facilitate the automatic correlation of threat intelligence from diverse sources, such as the MITRE ATT&CK framework. This feature enhances situational awareness and enables teams to prioritize threats effectively based on real-time data. Additionally, the ability to take action within other security or IT management tools from a centralized console streamlines operations, ensuring that teams can respond to incidents without unnecessary delays. This centralized approach not only improves efficiency but also fosters better communication among different departments involved in security management. Moreover, the use of digital security workflows and orchestration significantly accelerates tasks such as analysis, prioritization, and remediation. By automating these processes, organizations can improve their response times and enhance their overall cybersecurity posture. The integration of AI-driven automation within the ServiceNow AI Platform® further strengthens the platform's capabilities, enabling organizations to drive cyber resilience and reduce their exposure to potential threats. This proactive approach to cybersecurity ensures that organizations are not only reacting to incidents but are also prepared to prevent them. ServiceNow Security Operations stands out in the cybersecurity landscape by offering a comprehensive solution that addresses the complexities of modern cybersecurity challenges. By automating and simplifying threat and vulnerability management, it empowers security teams to respond more effectively, thereby enhancing the overall security framework of an organization. This makes it an essential tool for any organization looking to bolster its defenses against the ever-evolving landscape of cyber threats.

Average Rating: 4.3/5.0

Total Reviews: 80

How Do G2 Users Rate ServiceNow Security Operations?

  • Automated Remediation: 8.8/10 (Category avg: 8.8/10)
  • Quality of Support: 8.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.5/10 (Category avg: 8.8/10)

Who Is the Company Behind ServiceNow Security Operations?

  • Seller: ServiceNow
  • Company Website:
  • Year Founded: 2004
  • HQ Location: Santa Clara, CA
  • Twitter: @servicenow
    55,548 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    35,078 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 55% Large, 19% Medium

What Do G2 Reviewers Say About ServiceNow Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the remarkable integration capabilities of ServiceNow Security Operations, facilitating seamless management of security incidents.
  • Users value the seamless integration with third-party tools in ServiceNow Security Operations, enhancing productivity and workflow efficiency.
  • Users praise the seamless integration capabilities of ServiceNow Security Operations, enhancing efficiency and productivity in incident management.
  • Users appreciate the ease of use of ServiceNow Security Operations, facilitating efficient management of security incidents.
  • Users appreciate the end-to-end management of incidents in ServiceNow Security Operations, enhancing efficiency and integration.
Cons
  • Users find the difficult setup of ServiceNow Security Operations to be a significant barrier to effective implementation.
  • Users face integration issues with ServiceNow Security Operations, citing difficulties in setup and limited direct integrations.
  • Users feel the licensing issues with ServiceNow Security Operations limit playbook options, impacting remediation and increasing costs.
  • Users struggle with the complexity of building playbooks in ServiceNow Security Operations, highlighting a need for simplification.
  • Users face difficult customization when building playbooks in ServiceNow Security Operations, hindering their effectiveness and efficiency.

What Are Recent G2 Reviews of ServiceNow Security Operations?

What Are G2 Users Discussing About ServiceNow Security Operations?

Microsoft Sentinel

Microsoft Sentinel lets you see and stop threats before they cause harm, with SIEM reinvented for a modern world. Microsoft Sentinel is your birds-eye view across the enterprise. Put the cloud and large-scale intelligence from decades of Microsoft security experience to work. Make your threat detection and response smarter and faster with artificial intelligence (AI). Eliminate security infrastructure setup and maintenance, and elastically scale to meet your security needs—while reducing IT costs. With Microsoft Sentinel, you can: - Collect data at cloud scale—across all users, devices, applications, and infrastructure, both on-premises and in multiple clouds - Detect previously uncovered threats and minimize false positives using analytics and unparalleled threat intelligence from Microsoft - Investigate threats with AI and hunt suspicious activities at scale, tapping into decades of cybersecurity work at Microsoft -Respond to incidents rapidly with built-in orchestration and automation of common tasks

Average Rating: 4.4/5.0

Total Reviews: 275

How Do G2 Users Rate Microsoft Sentinel?

  • Automated Remediation: 8.7/10 (Category avg: 8.8/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Microsoft Sentinel?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Who Uses This: Security Analyst, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Large, 31% Medium

What Do G2 Reviewers Say About Microsoft Sentinel?

AI-generated summary from verified user reviews

Pros
  • Users value the advanced threat detection of Microsoft Sentinel, enhancing security and proactive threat management.
  • Users value the easy integrations of Microsoft Sentinel, facilitating quick setup and streamlined security processes.
  • Users value the seamless integration of Microsoft Sentinel with various third-party and Microsoft products, enhancing functionality and management.
  • Users commend the ease of use of Microsoft Sentinel, facilitating quick integration and a user-friendly experience.
Cons
  • Users express concern over the high costs of Microsoft Sentinel, especially as data ingestion increases.
  • Users face integration issues with Microsoft Sentinel, especially when connecting to legacy systems and third-party tools.
  • Users find the complexity of Microsoft Sentinel challenging, requiring extensive training and effort for effective use.

What Are Recent G2 Reviews of Microsoft Sentinel?

What Are G2 Users Discussing About Microsoft Sentinel?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.5/5.0

Total Reviews: 96

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Automated Remediation: 7.8/10 (Category avg: 8.8/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 7.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 40% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users value the best-in-class log management of Palo Alto Cortex XSIAM, benefiting from its effective alerting and integration features.
  • Users find the user-friendly dashboard of Palo Alto Cortex XSIAM essential for monitoring and understanding alerts effectively.
  • Users value the real-time monitoring capabilities of Palo Alto Cortex XSIAM, enhancing threat detection and response efficiency.
  • Users value the simple and user-friendly interface of Palo Alto Cortex XSIAM, making monitoring effortless.
  • Users value the good dashboard creation tools in Palo Alto Cortex XSIAM, enhancing ease of use and implementation.
Cons
  • Users note that Palo Alto Cortex XSIAM requires significant resources, impacting implementation time and increasing infrastructure costs.
  • Users find the complexity of implementation for Palo Alto Cortex XSIAM to be time-consuming and resource-intensive.
  • Users find the cost of Palo Alto Cortex XSIAM to be high, especially for smaller businesses.
  • Users face dashboard issues with XSIAM, finding it difficult to monitor assets and navigate the interface.
  • Users face difficult setup issues with Palo Alto Cortex XSIAM, requiring expertise and extensive time for initial implementation.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

Barracuda Incident Response

No email defense technology can protect against increasingly advanced email threats 100 percent of the time. Some advanced social engineering attacks like business email compromise will reach users’ mailboxes. And when they do, you need to respond quickly and accurately to minimize the scope and severity of damage. Barracuda Incident Response lets you respond to threats quickly and effectively, by automating investigative workflows and enabling direct removal of malicious emails

Average Rating: 4.5/5.0

Total Reviews: 16

How Do G2 Users Rate Barracuda Incident Response?

  • Automated Remediation: 9.2/10 (Category avg: 8.8/10)
  • Quality of Support: 9.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.6/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Barracuda Incident Response?

  • Seller: Barracuda
  • Year Founded: 2002
  • HQ Location: Campbell, CA
  • Twitter: @Barracuda
    15,239 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,327 employees on LinkedIn®
  • Ownership: Private

Who Uses This Product?

  • Company Size: 50% Medium, 25% Large

What Do G2 Reviewers Say About Barracuda Incident Response?

AI-generated summary from verified user reviews

Pros
  • Users value the instant threat removal capability of Barracuda Incident Response, enhancing email security effectively.
  • Users appreciate the email search and removal functionality in Barracuda Incident Response, enhancing data control easily.
  • Users value the instant threat removal capability of Barracuda Incident Response, preventing potential larger security issues.
  • Users value the comprehensive incident response capabilities of Barracuda, enhancing their cybersecurity protection effectively.
  • Users find Barracuda Incident Response to be an incredible tool for effective remediation and investigation in cybersecurity.
Cons
  • Users wish for blocking future emails across all gateway levels, as current limitations impact email management effectiveness.

What Are Recent G2 Reviews of Barracuda Incident Response?

What Are G2 Users Discussing About Barracuda Incident Response?

Palo Alto Networks Cortex XSOAR

Palo Alto Networks' Cortex XSOAR is a comprehensive Security Orchestration, Automation, and Response (SOAR) platform designed to streamline and enhance security operations. By integrating automation, case management, real-time collaboration, and threat intelligence management, Cortex XSOAR empowers security teams to respond to incidents more efficiently and effectively. Key Features and Functionality: - Process Standardization and Automation: Cortex XSOAR offers over 270 out-of-the-box playbooks, enabling the automation of numerous security use cases. These playbooks orchestrate response actions across more than 350 third-party products, facilitating seamless integration and operational consistency. - Security-Focused Case Management: The platform unifies alerts, incidents, and indicators from various sources into a single case management framework. This consolidation accelerates incident response by providing a comprehensive view of security events. - Real-Time Collaboration: Cortex XSOAR includes a Virtual War Room equipped with built-in ChatOps and a command-line interface. This feature allows security teams to collaborate in real time, execute commands across the entire product stack, and manage incidents more effectively. - Threat Intelligence Management: The platform aggregates disparate threat intelligence sources, customizes and scores feeds, and matches indicators against the organization's specific environment. This capability enables security teams to take informed actions swiftly. Primary Value and Problem Solving: Cortex XSOAR addresses the challenges faced by security teams, such as the overwhelming volume of alerts and the need for rapid incident response. By automating repetitive tasks and standardizing processes, the platform reduces the time spent on incidents by up to 90%, allowing analysts to focus on critical threats. The integration of threat intelligence management with SOAR capabilities ensures that organizations can operationalize threat feeds effectively, enhancing their overall security posture. Additionally, the platform's extensive integration ecosystem, with over 360 third-party integrations, enables organizations to orchestrate complex workflows across their existing security infrastructure without extensive custom development.

Average Rating: 4.6/5.0

Total Reviews: 28

How Do G2 Users Rate Palo Alto Networks Cortex XSOAR?

  • Automated Remediation: 9.0/10 (Category avg: 8.8/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.9/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Palo Alto Networks Cortex XSOAR?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 50% Large, 32% Medium

What Do G2 Reviewers Say About Palo Alto Networks Cortex XSOAR?

AI-generated summary from verified user reviews

Pros
  • Users value the powerful automation capabilities of Cortex XSOAR for enhancing incident response and threat detection.
  • Users appreciate the great UI of Palo Alto Networks Cortex XSOAR, enhancing data clarity and integration efficiency.
  • Users appreciate the clean and accurate data provided by Palo Alto Networks Cortex XSOAR, enhancing efficiency and safety.
  • Users value the powerful automation capabilities for incident response in Palo Alto Networks Cortex XSOAR.
  • Users appreciate the direct customer support from Palo Alto Networks Cortex XSOAR, enhancing their incident response experience.
Cons
  • Users find the learning curve steep, requiring significant time to become proficient with Cortex XSOAR.
  • Users desire more customization options for reporting, indicating limitations in the current capabilities of Cortex XSOAR.
  • Users find the logging issues in Cortex XSOAR frustrating, as readability is hindered by window size constraints.
  • Users find log management issues frustrating as data logs are hard to read quickly without opening new tabs.
  • Users feel that the reporting features lack customization, leading to a need for improvement in functionality.

What Are Recent G2 Reviews of Palo Alto Networks Cortex XSOAR?

What Are G2 Users Discussing About Palo Alto Networks Cortex XSOAR?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.6/10 (Category avg: 8.6/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

Proofpoint Threat Response

Proofpoint Threat Response takes the manual labor and guesswork out of incident response to help you resolve threats faster and more efficiently.

Average Rating: 4.6/5.0

Total Reviews: 17

How Do G2 Users Rate Proofpoint Threat Response?

  • Automated Remediation: 9.0/10 (Category avg: 8.8/10)
  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Proofpoint Threat Response?

  • Seller: Proofpoint
  • Year Founded: 2002
  • HQ Location: Sunnyvale, CA
  • Twitter: @proofpoint
    31,157 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5,261 employees on LinkedIn®
  • Ownership: NASDAQ: PFPT

Who Uses This Product?

  • Company Size: 56% Medium, 22% Large

What Do G2 Reviewers Say About Proofpoint Threat Response?

AI-generated summary from verified user reviews

Pros
  • Users value the automatic recall of suspicious emails in Proofpoint Threat Response for enhancing email security.
  • Users value the automated recall of suspicious emails, enhancing security and reducing potential threats effectively.
  • Users value the automatic recall of suspicious emails, enhancing their phishing prevention efforts significantly.
  • Users value the comprehensive security tools of Proofpoint Threat Response, enhancing their company's protection against threats.
  • Users appreciate the comprehensive threat detection tools of Proofpoint Threat Response, enhancing their company's security measures.
Cons
  • Users report experiencing multiple false positives with email management, leading to numerous recalls and replacements.
  • Users report frequent false positives with Proofpoint Threat Response, causing numerous email recalls and replacements.
  • Users note a steep learning curve with Proofpoint Threat Response, despite the availability of training and support.

What Are Recent G2 Reviews of Proofpoint Threat Response?

Sumo Logic

Sumo Logic, Inc. unifies and analyzes enterprise data, translating it into actionable insights through one AI-powered cloud-native log analytics platform. This single source of truth enables Dev, Sec and Ops teams to simplify complexity, collaborate efficiently and accelerate data-driven decisions that drive business value. Customers around the world rely on the Sumo Logic SaaS Log Analytics Platform for trusted insights to ensure application reliability, secure and protect against modern security threats, and gain insights into their cloud infrastructures. For more information, visit: SUMOLOGIC.COM

Average Rating: 4.3/5.0

Total Reviews: 405

How Do G2 Users Rate Sumo Logic?

  • Automated Remediation: 8.8/10 (Category avg: 8.8/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.4/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Sumo Logic?

  • Seller: Sumo Logic
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Redwood City, CA
  • Twitter: @SumoLogic
    6,542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    824 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 38% Large

What Do G2 Reviewers Say About Sumo Logic?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use in Sumo Logic, citing its simple query language and intuitive configurations.
  • Users value the ease of searching and configuring logs with Sumo Logic, enhancing their monitoring and tracing efficiency.
  • Users appreciate the Comprehensive Continuous Intelligence feature of Sumo Logic for transforming data into actionable insights quickly.
  • Users value the powerful visual insights and efficient log management capabilities of Sumo Logic for fast resolution.
  • Users value the real-time monitoring capabilities of Sumo Logic, enjoying swift insights and effective data management.
Cons
  • Users find Sumo Logic expensive, prompting concerns about whether its value justifies the high pricing.
  • Users find the difficult learning curve of Sumo Logic challenging, requiring significant time to become proficient.
  • Users face a steep learning curve with Sumo Logic, requiring significant time to master its features and query language.
  • Users face a steep learning curve with Sumo Logic, requiring significant time to master complex features and queries.
  • Users experience slow performance with Sumo Logic, facing delays in alerting and a cumbersome user interface.

What Are Recent G2 Reviews of Sumo Logic?

What Are G2 Users Discussing About Sumo Logic?

Splunk SOAR (Security Orchestration, Automation and Response)

Splunk SOAR provides security orchestration, automation and response capabilities that allow security analysts to work smarter by automating repetitive tasks; respond to security incidents faster with automated detection, investigation, and response; increase productivity, efficiency and accuracy; and strengthen defenses by connecting and coordinating complex workflows across their team and tools. Splunk SOAR also supports a broad range of security operations center (SOC) functions including event and case management, integrated threat intelligence, collaboration tools and reporting.

Average Rating: 4.4/5.0

Total Reviews: 39

How Do G2 Users Rate Splunk SOAR (Security Orchestration, Automation and Response)?

  • Automated Remediation: 8.6/10 (Category avg: 8.8/10)
  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.1/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Splunk SOAR (Security Orchestration, Automation and Response)?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Top Industries: Information Technology and Services, Consulting
  • Company Size: 43% Medium, 35% Large

What Do G2 Reviewers Say About Splunk SOAR (Security Orchestration, Automation and Response)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automation capabilities of Splunk SOAR, enabling efficient threat detection and response with minimal human error.
  • Users value the end-to-end security management of Splunk SOAR, enhancing incident response and threat detection efficiency.
  • Users appreciate the flexibility and integration capabilities of Splunk SOAR for tailoring security workflows to their needs.
  • Users commend the easy threat detection and analysis capabilities, enhancing security response with flexible workflows.
  • Users appreciate the ease of use in Splunk SOAR, benefiting from a user-friendly interface and seamless integrations.
Cons
  • Users find Splunk SOAR expensive, making it difficult for normal users to afford and implement effectively.
  • Users find the learning curve steep for Splunk SOAR, requiring extensive knowledge and training for effective use.
  • Users find the difficult learning curve of Splunk SOAR challenging, especially for beginners and new users of automation tools.
  • Users find the software's complexity challenging to navigate, particularly for beginners needing extensive training.
  • Users find the poor interface design of Splunk SOAR challenging, particularly for beginners navigating its features.

What Are Recent G2 Reviews of Splunk SOAR (Security Orchestration, Automation and Response)?

What Are G2 Users Discussing About Splunk SOAR (Security Orchestration, Automation and Response)?

Blink

Automate Everything Security in the Blink of AI Blink is a security workflow automation platform designed to make building, collaborating, and scaling all things security & beyond effortless using generative AI. Whether you prefer code, low-code, or no-code, Blink has got you covered. Easily drag and drop the actions you want into a workflow, leveraging the over 30,000 integrations available in the automation library, or use Blink Copilot to generate a workflow with a natural language prompt. Use Blink as an automation hub, where security teams go to quickly develop, collaborate, and automate their security ideas. Leverage the platform’s 10,000+ workflows that come out of the box to quickly build workflows for real-time remediation. Generate automation workflows for standalone use cases or build an end-to-end proactive automation strategy, streamlining security responses across your entire organization.

Average Rating: 4.7/5.0

Total Reviews: 19

How Do G2 Users Rate Blink?

  • Automated Remediation: 9.0/10 (Category avg: 8.8/10)
  • Quality of Support: 9.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.5/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Blink?

  • Seller: Blink Ops
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Austin, US
  • Twitter: @getBlinkOps
    706 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    126 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 63% Medium, 21% Large

What Do G2 Reviewers Say About Blink?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Blink, enabling quick setup and a satisfying overall experience.
  • Users value the powerful automation and strong support of Blink, leading to effective security outcomes quickly.
  • Users value the excellent customer support of Blink, enhancing their experience and ensuring product effectiveness.
  • Users appreciate the easy setup of Blink, enabling quick and seamless initiation with the software.
  • Users find Blink's seamless JavaScript integration and quick setup invaluable for efficient web project execution.
Cons
  • Users find Blink's limited extensibility problematic for large projects, affecting adaptability across different departments.
  • Users find Blink's limited extensibility problematic, particularly for large and complex projects, hindering productivity.

What Are Recent G2 Reviews of Blink?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024

Learn More About Security Orchestration, Automation, and Response (SOAR) Software

What is Security, Orchestration, Automation, and Response (SOAR) Software?

Security orchestration, automation, and response (SOAR) software helps coordinate, execute, and automate tasks between various IT workers and tools. SOAR tools allow organizations to respond quickly to cybersecurity attacks and observe, understand, and prevent future incidents.

SOAR software gives organizations a comprehensive view of their existing security systems while centralizing the security data. By automating security responses and reducing manual tasks, SOAR helps to generate a faster and more accurate response to security attacks. It also helps better coordinate and route incident response to the most appropriate IT worker in real time.

What Does SOAR Stand For?

SOAR stands for security orchestration, automation, and response. SOAR software significantly contributes to identifying potential future security threats.

What are the Common Features of Security, Orchestration, Automation, and Response (SOAR) Software?

Usually, a SOAR software offering operates under three primary software capabilities:

Threat and vulnerability management: Threat and vulnerability management examines key assets and prioritizes efforts to reduce risk. Working with other security teams, threat and vulnerability management helps prevent attacks by threat actors.

Security incident response: Security incident response addresses and manages the aftermath of a security breach, cyberattack, computer incident, or security incident. Security incident response is to handle the aftermath of a security breach in a way that limits damage, reduces recovery time, and reduces cost.

Security operations automation: Security operations automation is the technology that enables the automation and orchestration of security tasks. This can include both administrative duties and incident detection and response.

What are the Benefits of Security, Orchestration, Automation, and Response (SOAR) Software?

The benefits of using a SOAR tool are that it lessens the impact of security incidents and reduces the risk of legal liability. SOAR software helps companies’ security teams by enabling them to:

Maintain a central view: One of the benefits of SOAR software is that it gives security staff a central view and enables control of existing security systems while centralizing data collection to improve a company's security posture, operational efficiency, and productivity. 

Automate manual tasks: As with most software today, users are looking for help in terms of automation. SOAR software helps to manage and automate all aspects of a security incident lifecycle. This removes manual tasks, gives security staff more time to be productive, and allows them to focus on more mission-critical security tasks that do not require manual tasks.

Define incident and response procedures: SOAR software helps security systems define incident and response procedures. This helps to route security incidents to the correct security staff. SOAR can also prioritize and standardize the security response processes in a consistent, transparent, and documented way. 

Optimize incident response: Because SOAR software helps security staff define incident and response procedures, incident response is more accurate. This accuracy enables security systems and staff to have improved responses where they may have to contain, eradicate, or recover crucial data. 

Identify and assign incident severity levels: SOAR software helps to identify and assign incident severity levels. Severity levels in cybersecurity measure how severely a security incident impacts various parts of the organization. SOAR software automatically identifies and assigns severity levels, enabling the right security system and staff to respond appropriately. This means both can respond immediately to security incidents that may negatively affect an organization, such as networks, software, employee or customer data, etc.

Support collaboration and unstructured investigations: SOAR software supports collaboration and unstructured investigations in real time, helping route each security incident to the security system and security staff best suited to respond. Collaboration with other IT teams for tasks such as remediation or other departments such as legal is possible. 

Streamline operations: By using SOAR software, organizations can streamline security operations for threat and vulnerability management, security incident response, and security operations automation. SOAR software connects these security elements while integrating disparate security systems. SOAR software’s playbooks allow users to orchestrate, streamline and automate tasks. Playbooks also codify the process workflows that streamline the SOAR software functions.

Who Uses Security, Orchestration, Automation, and Response (SOAR) Software?

IT and cybersecurity staff: They use SOAR software to handle security alerts such as phishing, which includes looking for threat feed data from endpoints, failed user logins, logins from unusual locations, malicious VPN access attempts, and so on. It's also used to hunt for threats and respond to incidents from attached files for malware analysis, cloud-aware incident response, and automate data enrichment. Cybersecurity staff who assign incident severity and check other products for vulnerability scores also use SOAR platforms.

Challenges with Security, Orchestration, Automation, and Response (SOAR) software

There are a number of challenges with SOAR software that IT teams can encounter.

Skill gaps: While there is the misconception that SOAR software could replace security staff, the tool is meant to augment security teams, allowing them to work efficiently and effectively but not replacing them. However, there still may be a skills gap as the security team must be able to create detailed workflows of their processes.

Effective deployment: Another challenge of SOAR software is that it must be deployed to the enterprise but also connected to the other applications and technologies, which can be very complicated. An organization must also have staff with enough skills to deploy and maintain the platform. The applications and technologies used by the enterprise must also be able to support or be integrated into the SOAR software. One of SOAR software’s greatest strengths is to connect and orchestrate other technologies; however, if each technology is unable to be integrated, it hampers the benefits of deploying SOAR software.

How to Buy Security, Orchestration, Automation, and Response Software

Requirements Gathering (RFI/RFP) for Security, Orchestration, Automation, and Response (SOAR) Software

If an organization is just starting out and looking to purchase SOAR software, g2.com can help select the best one.

Most business pain points might be related to all of the manual work that must be completed. If the company is large and has a lot of networks, data, or devices in its organization, they may need to shop for a SOAR software that can grow with its organization. Users should think about the pain points in security to help create a checklist of criteria. Additionally, the buyer must determine the number of employees who will need to use the SOAR software and if they currently have the skills to administer it. 

Taking a holistic overview of the business and identifying pain points can help the team springboard into creating a checklist of criteria. The checklist serves as a detailed guide that includes both necessary and nice-to-have features, including budget, features, number of users, integrations, security staff skills, cloud or on-premises solutions, and more.

Depending on the scope of the deployment, it might be helpful to produce an RFI, a one-page list with a few bullet points describing what is needed from SOAR software.

Compare Security, Orchestration, Automation, and Response (SOAR) Software

Create a long list

Vendor evaluations are an essential part of the software buying process from meeting the business functionality needs to implementation. For ease of comparison, after all demos are complete, it helps to prepare a consistent list of questions regarding specific needs and concerns to ask each vendor.

Create a short list

From the long list of vendors, it is helpful to narrow down the list of vendors and come up with a shorter list of contenders, preferably no more than three to five. With this list in hand, businesses can produce a matrix to compare the features and pricing of the various solutions.

Conduct demos

To ensure the comparison is comprehensive, the user should demo each solution on the shortlist with the same use cases. This will allow the business to evaluate like for like and see how each vendor stacks up against the competition. 

Selection of Security, Orchestration, Automation, and Response (SOAR) Software

Choose a selection team

Before getting started, creating a winning team that will work together throughout the entire process, from identifying pain points to implementation, is crucial. The software selection team should consist of organization members with the right interest, skills, and time to participate in this process. A good starting point is to aim for three to five people who fill roles such as the main decision maker, project manager, process owner, system owner, or staffing subject matter expert, as well as a technical lead, head administrator, or security administrator. In smaller companies, the vendor selection team may be smaller, with fewer participants multitasking and taking on more responsibilities.

Compare notes

The selection team should compare notes and facts and figures which they noted during the process, such as costs, security capabilities, and alert and incident response times.

Negotiation

Just because something is written on a company’s pricing page does not mean it's final. It is crucial to open up a conversation regarding pricing and licensing. For example, the vendor may be willing to give a discount for multi-year contracts or for recommending the product to others.

Final decision

After this stage, and before going all in, it is recommended to roll out a test run or pilot program to test adoption with a small sample size of users. If the tool is well used and well received, the buyer can be confident that the selection was correct. If not, it might be time to go back to the drawing board.

What does Security, Orchestration, Automation, and Response (SOAR) Software cost?

SOAR is considered a long-term investment. This means there must be a careful evaluation of vendors, and the software should be tailored to each organization's specific requirements. Once a SOAR solution is purchased, deployed, and integrated into an organization’s security system, the cost could be high, which is why the evaluation stage of selecting SOAR software is so crucial. The notion of rip-and-replace cost can be high. The SOAR vendor chosen should continue to provide support for the SOAR solution with flexibility and open integration.

Return on Investment (ROI)

Organizations decide to purchase SOAR software with some type of return on investment (ROI). As they want to recoup the money spent on the software, it is critical to understand the costs that will be saved in terms of efficiency.

SOAR software saves security staff costs by eliminating manual tasks. For example, SOAR software automatically investigates the scenario of email phishing attacks which is very common, so this task can be very repetitive and consumes security staff time if it is done manually. A large enterprise used actual data from its SOAR software deployment and compared it to the cost of handling email phishing investigations automatically using SOAR software versus handling them manually. The enterprise found that the reduction in staff time required to handle phishing emails equated to savings of over $680,000 per year.