Best Managed Detection and Response (MDR) Software for Small Business

How Many Managed Detection and Response (MDR) Software Products Does G2 Track?

Total Products under this Category: 145

Category Stats (Oct 2026)

  • Average Rating: 4.49/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: October 22, 2026

How Does G2 Rank Managed Detection and Response (MDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 9,000+ Authentic Reviews
  • 145+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

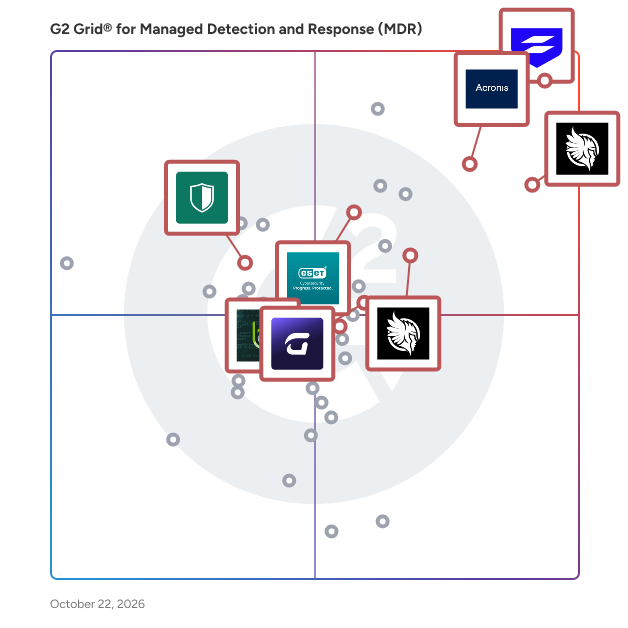
G2 Grid® for Managed Detection and Response (MDR) Software

G2 Grid® for Managed Detection and Response (MDR)  Software plotting products by satisfaction and market presence

Highlighted products: Huntress Managed EDR, Acronis Cyber Protect Cloud (now Acronis Cyber Platform), Sophos MDR, Huntress Managed ITDR, ESET PROTECT, Guardz, Kaseya MDR (formerly RocketCyber), and Blackpoint Cyber.

Underlying data: [Grid® JSON](https://www.g2.com/categories/managed-detection-and-response-mdr/grids.json?focus%5B%5D=huntress-managed-edr&focus%5B%5D=acronis-cyber-protect-cloud-now-acronis-cyber-platform&focus%5B%5D=sophos-mdr&focus%5B%5D=huntress-managed-itdr&focus%5B%5D=eset-protect&focus%5B%5D=guardz&focus%5B%5D=kaseya-mdr-formerly-rocketcyber&focus%5B%5D=blackpoint-cyber&segment=small-business)

Huntress Managed EDR

Huntress Managed EDR is a fully managed endpoint detection and response (EDR) solution that pairs continuous endpoint monitoring with a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) with limited in-house security staff, it monitors Windows, macOS, and Linux endpoints for malicious behavior, including ransomware, persistent footholds, and lateral movement, and pairs automated detection with expert threat hunters who validate and respond to incidents in real time. Huntress Managed EDR reduces attacker dwell time through rapid threat containment and remediation, giving lean IT and security teams enterprise-grade endpoint protection without the overhead of building an internal SOC.

Average Rating: 4.8/5.0

Total Reviews: 907

How Do G2 Users Rate Huntress Managed EDR?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.6/10 (Category avg: 9.1/10)
  • Automated remediation: 9.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.5/10 (Category avg: 8.9/10)

Who Is the Company Behind Huntress Managed EDR?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • Twitter: @HuntressLabs
    40,338 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 79% Small, 17% Medium

What Do G2 Reviewers Say About Huntress Managed EDR?

AI-generated summary from verified user reviews

Pros
  • Users praise the exceptional customer support from Huntress, ensuring smooth transitions and effective issue resolution for MSPs.
  • Users find Huntress Managed EDR incredibly easy to implement, ensuring a smooth transition and outstanding support throughout.
  • Users value the real-time threat detection of Huntress, enhancing security and minimizing false positives for effective response.
  • Users value the continuous monitoring of Huntress Managed EDR, ensuring swift threat identification and endpoint protection.
  • Users value the easy deployment of Huntress Managed EDR, simplifying setup and improving security coverage efficiently.
Cons
  • Users face alert issues with Huntress Managed EDR, including false positives and unclear notifications during updates.
  • Users suggest that improvements are needed for exception management and better visibility into AV scans and quarantined files.
  • Users are concerned about integration issues with various platforms, wishing for more compatibility beyond just Defender.
  • Users find the lack of customization in alerting and reporting limits the ability to tailor their experience effectively.
  • Users face limited Mac compatibility and deployment challenges, leading to frustration in mixed OS environments.

What Are Recent G2 Reviews of Huntress Managed EDR?

What Are G2 Users Discussing About Huntress Managed EDR?

Acronis Cyber Protect Cloud (now Acronis Cyber Platform)

Acronis delivers the world’s most complete cyber resilience platform, combining backup, disaster recovery, cybersecurity, RMM, and business operations tools into a single, natively integrated solution. Built specifically for Managed Service Providers (MSPs) and IT teams, Acronis simplifies operations with one agent, one console, and one license model. Automation, AI-driven insights, and multi-tenant management ensure that fewer technicians can manage more clients at lower cost. With predictable pricing and transparent billing, Acronis enables partners and IT teams to scale efficiently, comply with regulations, and deliver unmatched resilience. No other vendor delivers this level of integration, efficiency, and MSP alignment. Acronis Cyber Protect Cloud (now Acronis Cyber Platform) unites backup and next-generation, AI-based anti-malware, antivirus, and endpoint protection management in one solution. Integration and automation provide unmatched ease for service providers — reducing complexity while increasing productivity and decreasing operating costs. Acronis Cyber Platform is the single service provider solution that combines backup, anti-malware (including anti-virus, anti-ransomware, and anti-cryptojacking) and security and management capabilities such as vulnerability assessments, patch management, URL filtering and more. Now, service providers can eliminate complexity and make security a centerpiece of their offerings while increasing SLAs, decreasing churn, and generating more recurring revenue. Get upgraded security with integrated AI-based defenses that protect clients from modern threats, make smarter use of resources so your team can focus on clients, and earn new recurring revenue and higher margins that strengthen your business. Enriched with next-gen, full-stack anti-malware protection and comprehensive yet simple management tools, built on top of our industry-leading backup and data recovery solution, Acronis Cyber Platform simplifies onboarding, daily operations, and reporting, and combats advanced attacks with new use cases enabled by integration. Acronis Cyber Platform makes it easy to deliver the modern cyber protection your clients seek. Acronis is majority-owned by EQT.

Average Rating: 4.7/5.0

Total Reviews: 1,390

How Do G2 Users Rate Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 10.0/10 (Category avg: 9.1/10)
  • Automated remediation: 10.0/10 (Category avg: 8.7/10)
  • Automated investigation: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

  • Seller: Acronis
  • Company Website:
  • Year Founded: 2003
  • HQ Location: Schaffhausen
  • Twitter: @acronis
    94,498 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,923 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Director
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 68% Small, 28% Medium

What Do G2 Reviewers Say About Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Acronis Cyber Protect Cloud, making management and customization straightforward and efficient.
  • Users value the effective backup solutions of Acronis Cyber Protect Cloud for their simplicity and integration.
  • Users value the robust security features of Acronis Cyber Protect Cloud, ensuring safe data management and ransomware protection.
  • Users value the ease of backup management with Acronis Cyber Protect Cloud's all-in-one platform, simplifying their operations.
  • Users value the all-in-one platform of Acronis Cyber Protect Cloud, integrating backup, cybersecurity, and management seamlessly.
Cons
  • Users often experience slow performance with Acronis Cyber Protect Cloud, affecting the efficiency of backups and restores.
  • Users find Acronis Cyber Protect Cloud expensive compared to competitors, complicating their decision-making due to unclear pricing.
  • Users are frustrated with the poor customer support, especially due to unavailability on weekends during critical backup tests.
  • Users find the complexity of the interface and pricing confusing, which complicates their overall experience with Acronis Cyber Protect Cloud.
  • Users report backup issues with Acronis Cyber Protect Cloud, particularly concerning multiple export files and limited weekend support.

What Are Recent G2 Reviews of Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

What Are G2 Users Discussing About Acronis Cyber Protect Cloud (now Acronis Cyber Platform)?

Sophos MDR

Sophos Managed Detection and Response (MDR) is a fully managed service delivered by experts who detect and respond to cyberattacks targeting your computers, servers, networks, cloud workloads, email accounts, backups, and more. Our highly skilled security analysts stop advanced human-led attacks and take immediate action to neutralize threats before they can disrupt your business operations or compromise your sensitive data.

Average Rating: 4.7/5.0

Total Reviews: 582

How Do G2 Users Rate Sophos MDR?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.5/10 (Category avg: 9.1/10)
  • Automated remediation: 9.2/10 (Category avg: 8.7/10)
  • Automated investigation: 9.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Sophos MDR?

  • Seller: Sophos
  • Company Website:
  • Year Founded: 1985
  • HQ Location: Oxfordshire
  • Twitter: @Sophos
    36,759 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5,550 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Information Technology and Services, Manufacturing
  • Company Size: 63% Medium, 21% Large

What Do G2 Reviewers Say About Sophos MDR?

AI-generated summary from verified user reviews

Pros
  • Users commend the efficient threat detection of Sophos MDR, noting its quick responses and practical solutions.
  • Users value the 24/7 continuous monitoring of Sophos MDR, ensuring swift response to potential threats and enhancing security.
  • Users find Sophos MDR to be easy to use, enjoying its smooth management and seamless integration with existing systems.
  • Users value the 24/7 expert monitoring of Sophos MDR, providing unparalleled peace of mind against cyber threats.
  • Users appreciate the quick response time of Sophos MDR, enhancing incident management efficiency and reliability.
Cons
  • Users find Sophos MDR to be expensive, particularly challenging for smaller organizations with budget constraints.
  • Users highlight communication issues with Sophos MDR, noting slow response times and overwhelming alert volumes.
  • Users find the limited customization in alert handling restricts their ability to tailor responses effectively.
  • Users are concerned about the complexity of integration, particularly with external alerting platforms, affecting efficiency.
  • Users find the poor reporting issues in Sophos MDR frustrating due to complexity and lack of customization.

What Are Recent G2 Reviews of Sophos MDR?

What Are G2 Users Discussing About Sophos MDR?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Huntress Managed ITDR

Huntress Managed ITDR is a fully managed identity threat detection and response (ITDR) solution that pairs continuous identity monitoring across Microsoft 365 and Google Workspace with a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) with limited in-house identity security expertise, it detects identity-based threats such as credential compromise, privilege escalation, and lateral movement, and pairs automated behavioral analysis with expert analysts who investigate and respond to identity incidents in real time. Huntress Managed ITDR reduces dwell time on compromised accounts through rapid detection and remediation, giving lean IT and security teams enterprise-grade identity protection without the overhead of building an in-house identity security team. Our enterprise-grade solution gives you continuous monitoring for identity-based threats, rapid detection of unauthorized access, location-based and VPN/tunnel/proxy anomalies, and fast response to suspicious activities like rogue applications, shadow workflows, and business email compromise (BEC) scams. By focusing on protecting user credentials and session tokens, Huntress keeps your organization's digital identities safe, even as attackers develop sneakier tactics.

Average Rating: 4.8/5.0

Total Reviews: 117

How Do G2 Users Rate Huntress Managed ITDR?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.6/10 (Category avg: 9.1/10)
  • Automated remediation: 9.6/10 (Category avg: 8.7/10)
  • Automated investigation: 9.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Huntress Managed ITDR?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • Twitter: @HuntressLabs
    40,338 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 76% Small, 20% Medium

What Do G2 Reviewers Say About Huntress Managed ITDR?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring of Huntress Managed ITDR, enabling quick detection of threats without additional overhead.
  • Users value the clear visibility and actionable alerts Huntress Managed ITDR provides for identity-based threats.
  • Users appreciate the quick detection and thorough alerts of Huntress Managed ITDR, ensuring rapid incident intervention.
  • Users value the easy integrations of Huntress Managed ITDR, enhancing efficiency and security across multiple platforms.
  • Users praise the rapid and responsive customer support of Huntress Managed ITDR, enhancing overall satisfaction and efficiency.
Cons
  • Users report inadequate detection of failed login attempts, limiting proactive responses to security threats.
  • Users report an inefficient alert system, lacking crucial details and failing to detect key security threats promptly.
  • Users desire greater control and customization in the management console for enhanced functionality and flexibility.
  • Users face portal issues, including awkward escalations, mismatched visuals, and inadequate integration for issue resolution.
  • Users find the UI confusing, especially when navigating approvals and exceptions, leading to a clumsy experience.

What Are Recent G2 Reviews of Huntress Managed ITDR?

ESET PROTECT

ESET PROTECT is an AI-native cybersecurity platform that combines next-generation prevention, detection, and response capabilities with AI-powered security technologies and 24/7 managed detection and response (MDR) services delivered by ESET security experts. A single, unified management console provides centralized visibility across security operations, helping organizations automate repetitive tasks and enabling security teams to focus on higher-priority activities. With exceptional detection accuracy and fewer false positives, the platform helps reduce alert noise and identify real threats faster. Designed to help organizations stay ahead of known and emerging threats, ESET PROTECT strengthens cyber resilience, improves operational efficiency, and supports compliance initiatives. Why Organizations Choose ESET PROTECT Reduce Security Burden with Expert-Led Protection Fill cybersecurity skill gaps with 24/7 managed detection and response (MDR) backed by ESET experts. Gain faster incident response, actionable threat intelligence, and access to a team of experienced threat hunters. Secure AI Workflows Without Slowing Innovation Adopt AI confidently while protecting your organization from emerging AI-related threats. Secure AI conversations from malicious responses and risky prompts, protect against AI agent attacks, and detect suspicious AI agent behavior. Confidence in Cybersecurity with ESET AI Technologies Benefit from AI-powered technologies built specifically for cybersecurity. ESET helps security teams prevent threats earlier, prioritize and respond faster, improve threat detection, reduce noise, and protect people, devices, data, and businesses across multiple perimeters. Strengthen Compliance Readiness Navigate growing compliance demands with confidence. Our endpoint protection solutions help you assess risk, automate compliance processes, and demonstrate adherence to regulatory, customer, and industry requirements. Support compliance with NIS2, DORA, GDPR, ISO 27001, and more through continuous monitoring, automated evidence collection, and actionable recommendations to strengthen your security and compliance posture.

Average Rating: 4.6/5.0

Total Reviews: 965

How Do G2 Users Rate ESET PROTECT?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.7/10 (Category avg: 9.1/10)
  • Automated remediation: 9.8/10 (Category avg: 8.7/10)
  • Automated investigation: 9.6/10 (Category avg: 8.9/10)

Who Is the Company Behind ESET PROTECT?

  • Seller: ESET
  • Company Website:
  • Year Founded: 1992
  • HQ Location: Bratislava, Slovak Republic
  • Twitter: @ESET
    275,702 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,014 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Network Administrator
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 45% Small

What Do G2 Reviewers Say About ESET PROTECT?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the straightforward installation of ESET PROTECT, making it easy for anyone to get started.
  • Users commend ESET PROTECT for its robust ransomware protection, ensuring comprehensive security across multiple endpoints.
  • Users commend the reliability of ESET PROTECT, especially its strong protection against ransomware across multiple platforms.
  • Users value the great security of ESET PROTECT, ensuring computer safety with minimal impact on performance.
  • Users value the centralized management of ESET PROTECT, enabling effortless device oversight and enhanced threat detection.
Cons
  • Users find a learning curve with ESET PROTECT, as some features are complex and require expensive licenses.
  • Users find the difficult configuration process of ESET PROTECT time-consuming and sometimes overly complex for setup and management.
  • Users find the dashboard not user-friendly, citing excessive clicks for accessing necessary data and managing settings.
  • Users report a lack of clarity in policy management and task handling, complicating effective security oversight.
  • Users find difficult navigation in ESET PROTECT, requiring advanced skills and patience during implementation and setup.

What Are Recent G2 Reviews of ESET PROTECT?

What Are G2 Users Discussing About ESET PROTECT?

Guardz

Guardz is a unified cybersecurity platform specifically designed for Managed Service Providers (MSPs). This innovative solution consolidates essential security controls, identity threat detection and response (ITDR), endpoint protection (EDR), email security, user awareness training and phishing simulations, and Managed Detection and Response (MDR) into a single AI-native framework. The platform aims to enhance operational efficiency by streamlining security processes and providing a comprehensive approach to cybersecurity. Targeting MSPs, Guardz addresses the unique challenges these providers face in managing multiple security tools that often operate in silos. By adopting an identity-centric approach, Guardz connects various security vectors, effectively reducing the gaps that can leave organizations vulnerable. This layered and holistic view enables MSPs to respond to user risks in real time, ensuring that security measures are not only reactive but also proactive in safeguarding client environments. Key features of Guardz include its 24/7 AI and human-led Managed Detection and Response (MDR) services. The platform employs agentic AI to triage threats at machine speed, allowing for rapid identification and prioritization of potential security incidents. This automated triage process is complemented by expert analysts who validate findings, mitigate risks, and guide response actions. As a result, MSPs can offer scalable protection to their clients without the need to expand their workforce, making it a cost-effective solution for growing cybersecurity demands. Guardz stands out in the cybersecurity landscape by providing a unified platform that integrates various security functions into one cohesive system. This integration not only simplifies the management of security tools but also enhances the overall effectiveness of security measures. By leveraging AI-driven insights and human expertise, Guardz empowers MSPs to deliver robust cybersecurity solutions that adapt to the evolving threat landscape, ensuring their clients remain protected against emerging risks.

Average Rating: 4.6/5.0

Total Reviews: 125

How Do G2 Users Rate Guardz?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.0/10 (Category avg: 9.1/10)
  • Automated remediation: 8.9/10 (Category avg: 8.7/10)
  • Automated investigation: 8.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Guardz?

  • Seller: Guardz
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Tel Aviv, IL
  • Twitter: @GuardzCyber
    114 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    160 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 77% Small, 18% Medium

What Do G2 Reviewers Say About Guardz?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Guardz, highlighting its organized dashboard and straightforward integration.
  • Users value the robust security of Guardz, ensuring comprehensive protection for their systems and emails effortlessly.
  • Users value the efficient multi-tenant features of Guardz, enhancing operational workflow and client management.
  • Users appreciate the easy setup of Guardz, quickly deploying it for customers in about an hour.
  • Users value the effective threat detection capabilities of Guardz, enhancing overall cybersecurity for their clients.
Cons
  • Users find the limited features of Guardz restrict their workflow and hinder automation capabilities, needing more flexibility.
  • Users face integration issues with Guardz, finding alerts cumbersome and lacking essential API support for smoother operations.
  • Users note a significant lack of features in Guardz, limiting its effectiveness in mixed environments and advanced configurations.
  • Users find limited customization options in Guardz, impacting its adaptability for advanced configurations in mixed environments.
  • Users desire more transparency and clarity regarding the tools and methods used by Guardz for safety.

What Are Recent G2 Reviews of Guardz?

Kaseya MDR (formerly RocketCyber)

A complete rebuild of RocketCyber, it delivers more powerful protection in a simpler, more modern platform — with 24/7 AI-augmented, human-led threat detection and response across endpoints, firewalls and Microsoft 365, backed by a global SOC operating from Florida and Ireland. And unlike vendors that require you to rip and replace existing security tools, Kaseya MDR integrates with both Kaseya and third-party EDR solutions, so you can maintain protection regardless of your current environment. At the core of the platform is an AI-enhanced SOC, powered by Kaseya Intelligence, that handles machine-speed triage, noise reduction and event correlation before human analysts step in. Your team only sees validated threats that require attention, not hundreds of raw alerts to sort through manually. When action is needed, the SOC executes containment directly — device isolation, account lock, session revocation — without requiring internal intervention, with direct phone access to SOC analysts available when you need it.

Average Rating: 4.4/5.0

Total Reviews: 62

How Do G2 Users Rate Kaseya MDR (formerly RocketCyber)?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.7/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 8.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Kaseya MDR (formerly RocketCyber)?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • Twitter: @KaseyaCorp
    17,411 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 81% Small, 18% Medium

What Do G2 Reviewers Say About Kaseya MDR (formerly RocketCyber)?

AI-generated summary from verified user reviews

Pros
  • Users value the clear and understandable alerts from Kaseya MDR, enhancing resolution and system integration.
  • Users value the easy integrations of Kaseya MDR, enhancing overall functionality and user experience across systems.
  • Users find the 24/7 availability of Kaseya MDR invaluable for quick support during off-hours and emergencies.
  • Users value the clarity and detail of alerts from Kaseya MDR, making issue resolution easier and faster.
  • Users value the supportive customer support of Kaseya MDR, enhancing clarity and ease of use with alerts.
Cons
  • Users report experiencing far too many false positives, leading to questions about the product's overall effectiveness and value.
  • Users face challenges with inadequate detection while isolating the system, impacting its reliability and effectiveness.
  • Users criticize the limited integration with common security solutions, leading to numerous false positives and poor protection.

What Are Recent G2 Reviews of Kaseya MDR (formerly RocketCyber)?

Blackpoint Cyber

Blackpoint Cyber is the forerunner in the managed detection and response space, leveraging our proprietary ecosystem to help our partners fight back and win against cyberthreats. We have served the community since 2014 and proudly continue to safeguard businesses around the world. We believe that no one should go alone into the unfair fight. At Blackpoint, our team strives to provide unified, 24/7 detection to help you take out your adversaries before they can even see us coming.

Average Rating: 4.7/5.0

Total Reviews: 257

How Do G2 Users Rate Blackpoint Cyber?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.4/10 (Category avg: 9.1/10)
  • Automated remediation: 9.0/10 (Category avg: 8.7/10)
  • Automated investigation: 9.2/10 (Category avg: 8.9/10)

Who Is the Company Behind Blackpoint Cyber?

  • Seller: Blackpoint Cyber
  • Year Founded: 2014
  • HQ Location: Denver, Colorado, United States
  • Twitter: @blackpointus
    1,531 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    209 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: President, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 82% Small, 17% Medium

What Do G2 Reviewers Say About Blackpoint Cyber?

AI-generated summary from verified user reviews

Pros
  • Users praise the responsive customer support of Blackpoint Cyber, appreciating quick assistance and exceptional service quality.
  • Users value the fast threat detection of Blackpoint Cyber, appreciating quick SOC responses and effective remediation.
  • Users praise the quick and easy deployment of Blackpoint Cyber, enhancing their overall experience and efficiency.
  • Users find the setup process quick and easy, enhancing their overall experience with Blackpoint Cyber.
  • Users value the continuous monitoring of Blackpoint Cyber, praising its quick detection and effective incident response.
Cons
  • Users experience integration issues with Blackpoint Cyber, finding it lacking information and support for seamless connectivity.
  • Users find poor reporting capabilities limit effective asset management and hinder comprehensive client reviews for Blackpoint Cyber.
  • Users find Blackpoint Cyber expensive, making it difficult for some to justify the investment needed for coverage.
  • Users face portal issues with Compass One, citing clunky navigation and a lack of comprehensive features.
  • Users find the difficult navigation frustrating, citing confusion with portal and client settings.

What Are Recent G2 Reviews of Blackpoint Cyber?

What Are G2 Users Discussing About Blackpoint Cyber?

ThreatDown

AI has changed what businesses need to protect and how fast they need to respond. Ungoverned AI tools leak data through identities and API keys nobody's watching, while AI-driven attacks compress exploit windows from months to hours and generate the alert volume of dozens of attackers at once — a scale problem no team can staff its way out of. ThreatDown meets AI-scale risk with an AI-native platform built for more than the endpoint — one lightweight agent, one console, no tool sprawl. AI visibility flags every AI tool in use and blocks sensitive data before it reaches the model. ThreatDown ITDR monitors every identity, human and non-human, to catch compromise before attackers act. And Endpoint and email security stop attacks where they start - on the device and in the inbox. On top, ThreatDown MDR pairs AI-powered triage, with elite analysts who respond 24/7, detecting threats in a median of 5 minutes and containing them in 19. It's enterprise-grade protection at AI speed, without the headcount or complexity.

Average Rating: 4.6/5.0

Total Reviews: 1,046

How Do G2 Users Rate ThreatDown?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 9.1/10 (Category avg: 8.7/10)
  • Automated investigation: 9.1/10 (Category avg: 8.9/10)

Who Is the Company Behind ThreatDown?

  • Seller: ThreatDown
  • Company Website:
  • HQ Location: Santa Clara, US
  • LinkedIn® Page: www.linkedin.com
    164 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 48% Small, 41% Medium

What Do G2 Reviewers Say About ThreatDown?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use in deploying ThreatDown, making integration and implementation straightforward and efficient.
  • Users praise ThreatDown for its easy onboarding and integration, offering robust security with user-friendly tools and support.
  • Users value the enhanced security provided by ThreatDown, appreciating its effectiveness and minimal performance impact.
  • Users appreciate the effective threat detection of ThreatDown, making security straightforward and reliable over the years.
  • Users find the customer support of ThreatDown exceptional, noting prompt resolutions and helpful account management.
Cons
  • Users express concerns about poor customer support, citing difficulty in reaching help and needing more regular engagement.
  • Users find the lack of clarity in customization and integration processes frustrating, impacting overall user experience.
  • Users are frustrated by the significant lack of features in ThreatDown, diminishing its overall appeal and functionality.
  • Users experience false positives with ThreatDown, causing complications and confusion in managing software access effectively.
  • Users experience communication issues with ThreatDown, including sporadic device identification and slow support responses.

What Are Recent G2 Reviews of ThreatDown?

What Are G2 Users Discussing About ThreatDown?

Todyl Security Platform

Todyl is an AI-powered Cybersecurity and Assurance Platform for threat, risk, and compliance management delivered through a single agent and a single portal. Our platform defends against modern, advanced threats spanning identity, endpoint, network, cloud, SaaS, and more. We also simplify meeting and demonstrating extensive compliance and insurance requirements with centralized data collection and reporting, easy-to-use assessment tools, a built-in risk register, and dashboards to cut back on manual reporting and spreadsheet sprawl. Our platform delivers a layered approach to cybersecurity, spanning SASE, Micro-Segmentation (LZT), Endpoint Security, SIEM, MXDR, and GRC all delivered through the same agent, in a cloud native platform. It’s easy to implement as a cost effective, fully integrated single solution that can consolidate and simplify your security and compliance programs. You can also deploy individual modules to meet your current needs, with a simple toggle within the UI to add or trial new modules when you need them. And an integrated Assurance Marketplace helps you complete your security program with additional services like incident response and penetration testing, and streamlined access to cyber insurance providers.

Average Rating: 4.7/5.0

Total Reviews: 107

How Do G2 Users Rate Todyl Security Platform?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 8.6/10 (Category avg: 8.7/10)
  • Automated investigation: 8.8/10 (Category avg: 8.9/10)

Who Is the Company Behind Todyl Security Platform?

  • Seller: Todyl
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Denver, CO
  • LinkedIn® Page: www.linkedin.com
    120 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 76% Small, 7% Medium

What Do G2 Reviewers Say About Todyl Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Todyl, highlighting its intuitive interface and seamless integration capabilities.
  • Users highlight the responsive and accessible customer support of Todyl, enhancing their overall experience and efficiency.
  • Users praise the convenient deployment and comprehensive integration features of Todyl Security Platform for enhanced security.
  • Users value the comprehensive security offered by Todyl, appreciating its ease of installation and cost-effectiveness.
  • Users praise the deployment ease of Todyl, appreciating its intuitive interface and seamless integration across platforms.
Cons
  • Users find there are improvements needed in customization, integrations, and the steep learning curve for Todyl's platform.
  • Users report integration issues with Todyl, noting limited API capabilities and inconsistencies with third-party connections.
  • Users find the reporting options inadequate, lacking ease of access and integration for strategic reviews.
  • Users notice the limited features in Todyl, particularly in customization, API, and reporting capabilities.
  • Users find the reporting tools inadequate, making it hard to extract useful insights for strategic reviews.

What Are Recent G2 Reviews of Todyl Security Platform?

Arctic Wolf

Arctic Wolf® is the cybersecurity and AI company that ends cyber risk by transforming it into business resilience. Powered by the Aurora® Superintelligence Platform, Arctic Wolf delivers modern security operations built on proprietary AI and decades of real-world expertise to manage and mitigate cyber threats. The platform is built on the Swarm of Experts™, which coordinates specialized AI agents across core security operations functions. The Security Operations Graph™ connects real-world telemetry and customer context to every workflow. The AI Trust Engine™ validates outcomes and keeps human experts in the loop. Arctic Wolf serves businesses of all sizes looking to strengthen their cybersecurity posture. IT and security teams turn to Arctic Wolf to streamline operations, gain a clearer view of their security landscape, and build resilience against cyberattacks. Arctic Wolf's Aurora-branded solutions include Aurora® Managed Detection and Response (MDR), which provides 24x7 monitoring and rapid threat detection and response. Aurora® Attack Surface Management and Aurora® Vulnerability Management help organizations identify and remediate vulnerabilities to reduce their attack surface. Aurora® Endpoint Security safeguards devices against threats. Aurora® Security Awareness and Training helps employees reduce human error in cybersecurity. Aurora® Incident Response helps organizations respond when a security incident occurs. The Concierge Security® Team delivers personalized support, working closely with organizations to understand their unique challenges and build tailored strategies for stronger cyber resilience. By combining AI-driven automation with expert validated precision, Arctic Wolf helps organizations confidently manage cyber risk, so they can operate with control and the freedom to innovate.

Average Rating: 4.7/5.0

Total Reviews: 276

How Do G2 Users Rate Arctic Wolf?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Arctic Wolf?

  • Seller: Arctic Wolf Networks
  • Company Website:
  • Year Founded: 2012
  • HQ Location: Eden Prairie, MN
  • Twitter: @AWNetworks
    4,520 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,292 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Hospital & Health Care, Information Technology and Services
  • Company Size: 71% Medium, 20% Large

What Do G2 Reviewers Say About Arctic Wolf?

AI-generated summary from verified user reviews

Pros
  • Users commend Arctic Wolf for its responsive customer support, ensuring effective collaboration and timely assistance during security incidents.
  • Users value the proactive threat detection of Arctic Wolf, ensuring timely alerts and expert support for security incidents.
  • Users value Arctic Wolf's proactive security approach, providing peace of mind and seamless team integration for threat management.
  • Users appreciate the ease of use of Arctic Wolf, highlighting its user-friendly interface and smooth deployment.
  • Users value the fast notifications of events, enabling quick engagement and effective issue triage with professionals.
Cons
  • Users highlight the high cost of Arctic Wolf, wishing it was more affordable despite its effectiveness.
  • Users note the issue of false positives in alerts, requiring time-consuming investigations despite overall satisfaction.
  • Users experience a steep learning curve, requiring time and IT knowledge to navigate Arctic Wolf's features effectively.
  • Users feel overwhelmed by the amount of cybersecurity risks detailed in reports and seek better notification methods.
  • Users face dashboard issues with quirks and delays in resolving identified risks, though updates are frequent.

What Are Recent G2 Reviews of Arctic Wolf?

What Are G2 Users Discussing About Arctic Wolf?

Field Effect MDR

Field Effect delivers intelligence-grade managed detection and response for the AI era. Built on Federated Smart Compute™ and nation-state tradecraft, our holistic MDR platform uncovers weaknesses early, blocks attacks in real time, and reduces risk across the entire threat surface—endpoint, network, cloud, and more. With an 18-second median time to detect, Field Effect helps MSPs and overwhelmed IT teams outpace agentic attacks and achieve premium protection with the team they have.

Average Rating: 4.8/5.0

Total Reviews: 43

How Do G2 Users Rate Field Effect MDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.2/10 (Category avg: 9.1/10)
  • Automated remediation: 7.6/10 (Category avg: 8.7/10)
  • Automated investigation: 9.1/10 (Category avg: 8.9/10)

Who Is the Company Behind Field Effect MDR?

  • Seller: Field Effect
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Ottawa
  • Twitter: @fieldeffectsoft
    1,304 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    149 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 52% Small, 27% Medium

What Do G2 Reviewers Say About Field Effect MDR?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use in Field Effect MDR, particularly enjoying simple setup and deployment processes.
  • Users value the responsive and helpful customer support of Field Effect MDR, ensuring effective implementation and issue resolution.
  • Users appreciate the comprehensive alert notifications of Field Effect MDR, enabling timely identification of vulnerabilities and issues.
  • Users commend the top-notch security monitoring of Field Effect MDR, enhancing protection and response to potential threats.
  • Users commend the easy initial setup of Field Effect MDR, allowing for quick deployment and seamless integration.
Cons
  • Users find alert issues with Field Effect MDR, often needing additional support due to unclear notifications and false alarms.
  • Users find the inefficient alert system difficult to manage due to overwhelming volume and lack of detail.
  • Users find the learning curve steep, necessitating additional time for onboarding and user adaptation to the Field Effect MDR.
  • Users find the communication issues frustrating, often needing to simplify technical info for clients, leading to extra support requests.
  • Users experience integration issues with Field Effect MDR, leading to reporting challenges and account disruptions during system interactions.

What Are Recent G2 Reviews of Field Effect MDR?

What Are G2 Users Discussing About Field Effect MDR?

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 4.9/5.0

Total Reviews: 65

How Do G2 Users Rate UnderDefense MAXI?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.8/10 (Category avg: 9.1/10)
  • Automated remediation: 9.7/10 (Category avg: 8.7/10)
  • Automated investigation: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind UnderDefense MAXI?

  • Seller: UnderDefense
  • Year Founded: 2017
  • HQ Location: New York, NY
  • Twitter: @underdefense
    153 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    133 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Information Technology and Services, Marketing and Advertising
  • Company Size: 48% Small, 45% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the visibility provided by UnderDefense MAXI, allowing them to focus on relevant security alerts effectively.
  • Users commend UnderDefense MAXI for its outstanding customer support, ensuring rapid responses and clear guidance throughout their cybersecurity needs.
  • Users appreciate the expert cybersecurity support from UnderDefense MAXI, enhancing their security posture and alert management.
  • Users commend the accuracy of information provided by UnderDefense MAXI, enhancing their security management and decision-making.
  • Users value the exceptional issue resolution by UnderDefense, enhancing security management with quick and effective solutions.
Cons
  • Users desire more automation in UnderDefense MAXI, seeking greater control over the dashboard and updates.
  • Users desire more control over the dashboard and automated updates for a better experience with UnderDefense MAXI.
  • Users note the limited integration requiring extra setup time, which can be a hurdle for new users.
  • Users note the setup difficulty requiring time and effort to properly integrate tools before full functionality can be enjoyed.

What Are Recent G2 Reviews of UnderDefense MAXI?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.3/10 (Category avg: 9.1/10)
  • Automated remediation: 9.4/10 (Category avg: 8.7/10)
  • Automated investigation: 9.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, appreciating its straightforward yet comprehensive functionalities for effective protection.
  • Users value the unified platform of Cynet, which offers effective security through streamlined endpoint protection and detection.
  • Users praise Cynet for its effective threat detection and seamless monitoring, enhancing overall cybersecurity effortlessly.
  • Users commend Cynet for its exceptional customer support, ensuring a smooth and efficient deployment experience.
  • Users praise Cynet for its flawless threat monitoring and detection, enhancing overall cybersecurity effectiveness effortlessly.
Cons
  • Users find limited customization options in reporting and dashboards, affecting their ability to present necessary data.
  • Users find feature limitations in Cynet, with a desire for more customization options and broader integrations.
  • Users note a lack of customization in reports, wishing for more options to tailor data presentation.
  • Users note limited features, such as basic reporting and few third-party integrations, impacting customization and deeper controls.
  • Users note a lack of essential features like web filtering and security policies compared to other vendors.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

eSentire

eSentire is a leader in Controlled Autonomy SecOps, protecting thousands of organizations across 35+ industries around the world. Founded in 2001, the company’s Controlled Autonomy SecOps operating model pairs agentic AI operatives with engineered human-judgment controls, delivering expert-depth security outcomes at machine speed without ceding accountability to opaque automation. Powered by the unified agentic AI Atlas Platform, eSentire’s Atlas AI + 24/7 expert human SOC coverage delivers offensive capabilities that preempt exposures before attackers do, detect, and respond to stop threats in real time. For more information, visit esentire.com and follow @eSentire.

Average Rating: 4.6/5.0

Total Reviews: 284

How Do G2 Users Rate eSentire?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.1/10 (Category avg: 9.1/10)
  • Automated remediation: 8.6/10 (Category avg: 8.7/10)
  • Automated investigation: 8.9/10 (Category avg: 8.9/10)

Who Is the Company Behind eSentire?

  • Seller: eSentire
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Waterloo, Ontario
  • Twitter: @eSentire
    6,438 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    556 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, CTO
  • Top Industries: Financial Services, Legal Services
  • Company Size: 59% Medium, 23% Large

What Do G2 Reviewers Say About eSentire?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid response time of eSentire, enhancing their confidence in security management and threat resolution.
  • Users value the excellent customer support at eSentire, with quick responses and a human touch readily available.
  • Users find eSentire's managed SOC services vital for constant monitoring and operational security, especially after hours.
  • Users value eSentire's deep expertise and 24/7 support, providing reliable cybersecurity solutions tailored to their needs.
  • Users value the 24/7 continuous monitoring by eSentire, enabling quick responses to anomalies and ensuring peace of mind.
Cons
  • Users experience communication issues with eSentire, often feeling that clarity and support are lacking during interactions.
  • Users experience an inefficient alert system requiring internal validation, impacting overall usability and response times.
  • Users note that eSentire is expensive compared to alternatives, reflecting its premium support and expertise.
  • Users face portal issues with eSentire, preferring direct email updates for ticket details rather than mandatory portal logins.
  • Users find poor reporting from eSentire problematic, citing infrequent reviews and a lack of actionable insights.

What Are Recent G2 Reviews of eSentire?

What Are G2 Users Discussing About eSentire?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated