Best Incident Response Software for Small Business

How Many Incident Response Software Products Does G2 Track?

Total Products under this Category: 110

Category Stats (Nov 2026)

  • Average Rating: 4.48/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.08%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Incident Response Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,600+ Authentic Reviews
  • 110+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

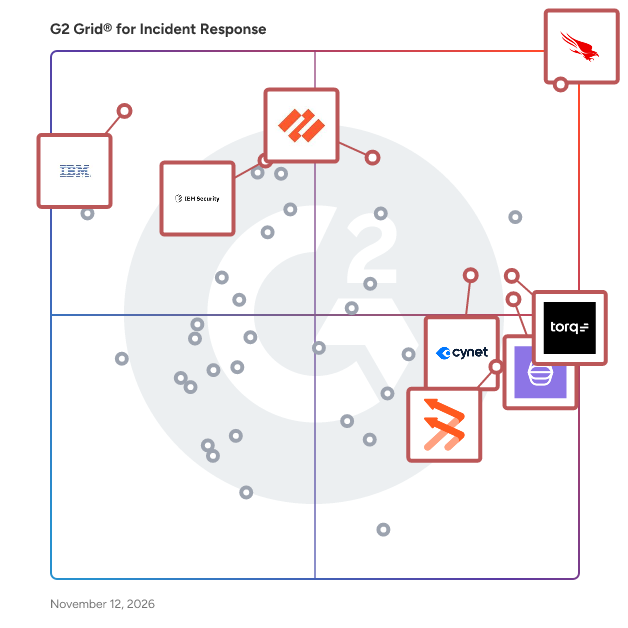
G2 Grid® for Incident Response Software

G2 Grid® for Incident Response Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Palo Alto Cortex XSIAM, Tines Stories, Torq AI SOC Platform, UnderDefense MAXI, IBM Concert platform, IBM QRadar SIEM, and Cynet.

Underlying data: [Grid® JSON](https://www.g2.com/categories/incident-response/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=tines-stories&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=underdefense-maxi&focus%5B%5D=ibm-concert-platform&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=cynet&segment=small-business)

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 654

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Threat Intelligence: 9.6/10 (Category avg: 8.9/10)
  • Quality of Support: 8.9/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.6/10 (Category avg: 8.5/10)
  • Incident Logs: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Security Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Large, 37% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the cloud-native architecture and effective features like workflow automation and asset management in CrowdStrike Falcon.
  • Users value the advanced threat detection capabilities of CrowdStrike Falcon, enhancing security and streamlining response efforts.
  • Users value the ease of use of CrowdStrike Falcon, benefiting from its lightweight agent and intuitive interface.
  • Users appreciate the robust security features of CrowdStrike Falcon, enhancing endpoint protection and system performance.
  • Users praise the superior detection capabilities of CrowdStrike Falcon, consistently delivering reliable and swift responses.
Cons
  • Users find that CrowdStrike Falcon's high licensing cost can be burdensome, particularly for smaller teams and organizations.
  • Users express frustration over the complexity of CrowdStrike Falcon's management console and its steep learning curve.
  • Users find the steep learning curve of CrowdStrike Falcon challenging due to its complex management console.
  • Users face limited functionality in adding hash values to CrowdStrike Falcon, which restricts monitoring capabilities.
  • Users express concern over the high pricing of CrowdStrike Falcon, especially for smaller organizations.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 111

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Threat Intelligence: 8.9/10 (Category avg: 8.9/10)
  • Quality of Support: 8.5/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.2/10 (Category avg: 8.5/10)
  • Incident Logs: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Palo Alto Cortex XSIAM, benefiting from its intuitive interface and seamless integration.
  • Users value the advanced threat detection capabilities of Palo Alto Cortex XSIAM, ensuring both known and unknown threats are managed effectively.
  • Users value the seamless integrations of Palo Alto Cortex XSIAM, enhancing overall functionality across various platforms.
  • Users value the unified console of Palo Alto Cortex XSIAM for simplifying security management across endpoints, network, and cloud.
  • Users value the single console integration, highlighting its ease of use and reliability for threat detection.
Cons
  • Users find the Cortex XSIAM to be very expensive compared to other solutions, impacting overall satisfaction.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM a challenge due to its complexity and setup.
  • Users find the complexity of the console overwhelming, requiring significant time and expertise to navigate effectively.
  • Users report integration issues with Palo Alto Cortex XSIAM, facing challenges with non-native equipment and log maintenance.
  • Users find the UX improvement of Palo Alto Cortex XSIAM lacking in customization and intuitive design for features.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

Tines Stories

Tines is the intelligent workflow platform trusted by the world's most advanced organizations. Companies like Coinbase, Databricks, Mars, Reddit, and SAP use Tines to power their most important workflows. With Tines, they’ve built a secure, flexible foundation to operationalize AI agents and intelligent workflows, unlocking productivity, moving faster, and future-proofing how work gets done.

Average Rating: 4.7/5.0

Total Reviews: 425

How Do G2 Users Rate Tines Stories?

  • Threat Intelligence: 8.8/10 (Category avg: 8.9/10)
  • Quality of Support: 9.5/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.6/10 (Category avg: 8.5/10)
  • Incident Logs: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Tines Stories?

  • Seller: Tines
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Dublin, IE
  • LinkedIn® Page: www.linkedin.com
    619 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, Software Engineer
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 39% Medium, 35% Large

What Do G2 Reviewers Say About Tines Stories?

AI-generated summary from verified user reviews

Pros
  • Users praise the intuitive ease of use of Tines Stories, facilitating quick workflow setup and management.
  • Users value the powerful automation capabilities of Tines, making complex workflows accessible and streamlined for all skill levels.
  • Users praise Tines for its responsive and helpful customer support, enhancing their overall experience with the tool.
  • Users love Tines for its amazing integrations and exceptional support, making automation accessible for all skill levels.
  • Users find Tines Stories to be a time-saving solution, enabling quick and efficient automation of tasks.
Cons
  • Users acknowledge a learning curve with Tines Stories, but find support alleviates challenges and enhances usability.
  • Users note missing features in Tines Stories, including limited JavaScript use and a need for improved ticketing functionality.
  • Users are frustrated by the lack of features in Tines Stories, particularly for scripting and ticketing functionalities.
  • Users find Tines Stories to have a steep learning curve, as creating structures can be intimidating without clear guidance.
  • Users find difficult learning curves in Tines Stories, especially with advanced functions and formulas requiring more accessible documentation.

What Are Recent G2 Reviews of Tines Stories?

What Are G2 Users Discussing About Tines Stories?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Torq AI SOC Platform

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats. Working alongside your SecOps staff, the Torq platform integrates with your security stack to facilitate containment and remediation workflows.

Average Rating: 4.8/5.0

Total Reviews: 166

How Do G2 Users Rate Torq AI SOC Platform?

  • Threat Intelligence: 9.1/10 (Category avg: 8.9/10)
  • Quality of Support: 9.5/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.2/10 (Category avg: 8.5/10)
  • Incident Logs: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Torq AI SOC Platform?

  • Seller: torq
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • LinkedIn® Page: www.linkedin.com
    470 employees on LinkedIn®
  • Total Revenue (USD mm): $21

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Medium, 30% Small

What Do G2 Reviewers Say About Torq AI SOC Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the user-friendly interface of Torq AI SOC Platform, enhancing their incident management and workflow efficiency.
  • Users value the strong security overview provided by Torq AI SOC Platform, enhancing incident tracking and vulnerability management.
  • Users appreciate the seamless automation of Torq AI SOC Platform, enhancing security and simplifying workflow management.
  • Users value the intuitive dashboards of Torq AI SOC Platform, centralizing incident views and enhancing security operations.
  • Users appreciate the comprehensive threat detection of Torq AI, delivering crucial insights and enhancing security across networks.
Cons
  • Users find the difficult learning curve challenging, requiring time and training to fully utilize Torq AI SOC Platform.
  • Users note a slight learning curve with the Torq AI SOC Platform, making it challenging for beginners to master.
  • Users feel the missing built-in playbooks hinder the ease of onboarding and overall management within the Torq AI SOC Platform.
  • Users suggest improvement needed in documentation and feature management for better usability of Torq AI SOC Platform.
  • Users experience poor interface design, with issues like unresponsive buttons and unintuitive navigation that hinder efficiency.

What Are Recent G2 Reviews of Torq AI SOC Platform?

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 4.9/5.0

Total Reviews: 79

How Do G2 Users Rate UnderDefense MAXI?

  • Threat Intelligence: 9.6/10 (Category avg: 8.9/10)
  • Quality of Support: 9.9/10 (Category avg: 8.8/10)
  • Incident Case Management: 9.4/10 (Category avg: 8.5/10)
  • Incident Logs: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind UnderDefense MAXI?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Marketing and Advertising, Information Technology and Services
  • Company Size: 52% Small, 42% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users value the high visibility UnderDefense MAXI provides into security alerts, streamlining threat management and response.
  • Users commend the responsive and effective customer support of UnderDefense MAXI, enhancing their cybersecurity management and experience.
  • Users commend UnderDefense MAXI for its effective cybersecurity solutions, enhancing security management and response efficiency.
  • Users value the information accuracy provided by UnderDefense, which clarifies security issues and enhances response efficiency.
  • Users highlight the quick issue resolution by UnderDefense, improving security alert management and enhancing overall security operations.
Cons
  • Users feel a lack of automation features limits control over the dashboard for UnderDefense MAXI.
  • Users desire more control over the dashboard, seeking enhanced customization and automated update options with UnderDefense MAXI.
  • Users note that limited integration requires significant setup time to ensure proper tool configuration.
  • Users find the setup process challenging, requiring significant time and effort for proper tool integration.

What Are Recent G2 Reviews of UnderDefense MAXI?

IBM Concert platform

IBM Concert® is an agentic IT Ops platform that creates an adaptable, unified operational layer across your environment. It connects signals, generates shared context, and coordinates action across teams and tools, so your entire system operates as one. With cross-domain intelligence, Concert helps you reduce risk, maintain business continuity, improve performance, and optimize cost across the stack. Powered by agentic AI, it surfaces what matters, prioritizes business impact, and orchestrates action through governed workflows. 

Average Rating: 4.1/5.0

Total Reviews: 36

How Do G2 Users Rate IBM Concert platform?

  • Quality of Support: 7.2/10 (Category avg: 8.8/10)

Who Is the Company Behind IBM Concert platform?

  • Seller: IBM
  • Company Website:
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Company Size: 39% Small, 33% Large

What Do G2 Reviewers Say About IBM Concert platform?

AI-generated summary from verified user reviews

Pros
  • Users find IBM Concert's ease of use remarkable, providing clear insights and a unified view that simplifies project management.
  • Users value the end-to-end visibility and AI-driven insights of IBM Concert, enhancing focus and reducing confusion in projects.
  • Users value the automation capabilities of IBM Concert, enhancing efficiency and streamlining issue management across applications.
  • Users find the easy setup of IBM Concert convenient, enabling quick integration and efficient management of IT operations.
  • Users value IBM Concert for its clear, actionable insights that streamline problem-solving and enhance IT operations efficiency.
Cons
  • Users experience a challenging learning difficulty with IBM Concert, especially in grasping advanced features and setup.
  • Users find the initial setup complex, requiring time to adapt and understand the platform effectively.
  • Users report a significant learning curve with IBM Concert, making it challenging to fully utilize its features.
  • Users notice integration issues with IBM Concert, finding the setup and onboarding process overly complex and needing improvement.
  • Users find the limited customization options for dashboards and reports hinder flexibility for their team needs.

What Are Recent G2 Reviews of IBM Concert platform?

IBM QRadar SIEM

Outsmart threats with an end-to-end award-winning security suite; proven to prevent, endure and recover from both known & unknown IT hazards faced by SoCs in the modern-day.

Average Rating: 4.4/5.0

Total Reviews: 286

How Do G2 Users Rate IBM QRadar SIEM?

  • Threat Intelligence: 8.4/10 (Category avg: 8.9/10)
  • Quality of Support: 8.3/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.3/10 (Category avg: 8.5/10)
  • Incident Logs: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind IBM QRadar SIEM?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM
  • Phone: 1-866-277-7488

Who Uses This Product?

  • Who Uses This: Security Engineer, SOC Analyst
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 52% Large, 29% Medium

What Do G2 Reviewers Say About IBM QRadar SIEM?

AI-generated summary from verified user reviews

Pros
  • Users value the intuitive user interface of IBM QRadar SIEM, enhancing ease of use for all experience levels.
  • Users appreciate the seamless integration capabilities of IBM QRadar SIEM, enhancing data management and reporting efficiency.
  • Users appreciate the user-friendly dashboard of IBM QRadar SIEM, enhancing ease of use and customization.
  • Users value the easy integrations of IBM QRadar SIEM, enhancing functionality with seamless API and SaaS connections.
  • Users appreciate the intuitive user interface of IBM QRadar SIEM, which simplifies navigation for less experienced users.
Cons
  • Users find the UI improvements unsatisfactory, noting limitations in features, search capabilities, and report building.
  • Users find the product expensive, especially when increasing EPS and managing costs for maintenance and features.
  • Users find the cost of implementing QRadar SIEM to be high, particularly for smaller organizations, affecting accessibility.
  • Users struggle with dashboard issues in QRadar, experiencing inefficiencies and limited functionality in the user interface.
  • Users find the initial setup time-consuming, requiring significant expertise and effort to customize for their needs.

What Are Recent G2 Reviews of IBM QRadar SIEM?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Threat Intelligence: 9.2/10 (Category avg: 8.9/10)
  • Quality of Support: 9.3/10 (Category avg: 8.8/10)
  • Incident Case Management: 9.0/10 (Category avg: 8.5/10)
  • Incident Logs: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, enjoying its simple implementation and daily operation.
  • Users appreciate the responsive SOC team and improved dashboard features, enhancing control and reducing notification noise.
  • Users value the effective threat detection of Cynet, appreciating its responsiveness and improved dashboard features.
  • Users commend Cynet's responsive customer support, quickly resolving issues and enhancing the overall experience with the product.
  • Users commend Cynet for its robust security features, seamless implementation, and excellent support, enhancing overall cybersecurity management.
Cons
  • Users find limited customization options in dashboards and integrations, affecting their overall experience with Cynet.
  • Users note feature limitations in customization and integration options, which may hinder user experience and flexibility.
  • Users find a lack of customization in dashboards and features, limiting their ability to tailor the platform effectively.
  • Users experience limited features with Cynet, particularly in reporting options and third-party integrations.
  • Users note that some missing features hinder full integration and customization, impacting overall user experience.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

KnowBe4 PhishER/PhishER Plus

KnowBe4 PhishER Plus delivers automated incident response to eliminate SOC noise and remediate malicious emails across your organization simultaneously. It leverages AI to categorize reported messages across email and Microsoft Teams, automatically responding to reporters, flagging high-risk messages, and removing threats across all mailboxes. SOC teams can even flip malicious messages into training simulations to see who would have fallen victim. Customers report saving upwards of 99% of triage time, highly praising the platform's intuitive, user-friendly interface that transforms overwhelming manual workflows into fast, consistent actions. This layer of defense reviews threats slipping past other security layers, offering a single pane of glass view with leading third-party integrations like CrowdStrike, Webroot, and VirusTotal. PhishER Plus turns manual email triaging into a proactive, automated security posture.

Average Rating: 4.6/5.0

Total Reviews: 573

How Do G2 Users Rate KnowBe4 PhishER/PhishER Plus?

  • Threat Intelligence: 8.5/10 (Category avg: 8.9/10)
  • Quality of Support: 9.2/10 (Category avg: 8.8/10)
  • Incident Case Management: 7.9/10 (Category avg: 8.5/10)
  • Incident Logs: 8.4/10 (Category avg: 8.8/10)

Who Is the Company Behind KnowBe4 PhishER/PhishER Plus?

  • Seller: KnowBe4, Inc.
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Clearwater, FL
  • LinkedIn® Page: www.linkedin.com
    2,655 employees on LinkedIn®
  • Ownership: NASDAQ: KNBE

Who Uses This Product?

  • Who Uses This: IT Manager, Director of IT
  • Top Industries: Financial Services, Primary/Secondary Education
  • Company Size: 75% Medium, 13% Large

What Do G2 Reviewers Say About KnowBe4 PhishER/PhishER Plus?

AI-generated summary from verified user reviews

Pros
  • Users love how KnowBe4 PhishER/PhishER Plus simplifies phishing email management, streamlining workflows and enhancing security efficiently.
  • Users value the automatic sorting and prioritization of suspicious emails, enhancing response efficiency and security.
  • Users appreciate the automation of KnowBe4 PhishER, which simplifies managing reported phishing emails effectively.
  • Users appreciate the enhanced security provided by KnowBe4 PhishER/PhishER Plus, simplifying phishing email management and response.
  • Users commend the ease of use of KnowBe4 PhishER/PhishER Plus, simplifying phishing email management and enhancing security effectively.
Cons
  • Users experience frequent false positives, leading to wasted time and complicating the automation process of threat detection.
  • Users find the ineffective email security concerning, as threats sometimes bypass filters and reach inboxes unaddressed.
  • Users desire greater email management granularity in PhishER, noting inconsistencies and delays in filtering reported emails.
  • Users experience a time-consuming learning curve when configuring PhishER/PhishER Plus to their specific needs.
  • Users find the setup difficult, requiring extensive reading and outside help, complicating the initial onboarding process.

What Are Recent G2 Reviews of KnowBe4 PhishER/PhishER Plus?

What Are G2 Users Discussing About KnowBe4 PhishER/PhishER Plus?

Wazuh

Wazuh is a free and open source security platform that unifies XDR and SIEM capabilities. It protects workloads across on-premises, virtualized, containerized, and cloud-based environments. Wazuh, with over 30 million downloads per year, has one of the largest open-source security communities in the world. Wazuh helps organizations of all sizes protect their data assets against security threats. Learn more about the project at wazuh.com

Average Rating: 4.5/5.0

Total Reviews: 70

How Do G2 Users Rate Wazuh?

  • Threat Intelligence: 8.7/10 (Category avg: 8.9/10)
  • Quality of Support: 8.4/10 (Category avg: 8.8/10)
  • Incident Case Management: 7.9/10 (Category avg: 8.5/10)
  • Incident Logs: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Wazuh?

Who Uses This Product?

  • Who Uses This: SOC Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Small, 40% Medium

What Do G2 Reviewers Say About Wazuh?

AI-generated summary from verified user reviews

Pros
  • Users find Wazuh's user-friendly interface and simple learning curve makes it ideal for small scale companies.
  • Users value the affordability of Wazuh, enjoying enterprise-level security without incurring high licensing costs.
  • Users value the visibility and control Wazuh offers, enhancing security event management across their infrastructure.
  • Users value the easy management of Wazuh, which simplifies operations and reduces costs effectively.
  • Users find Wazuh very easy to set up, appreciating the simple rollout process and preconfigured agents.
Cons
  • Users find the complex interface of Wazuh challenging, especially during initial setup and configuration adjustments.
  • Users find Wazuh's interface not user-friendly, struggling with complex configurations and a challenging learning curve.
  • Users often face complex implementation challenges with Wazuh that hinder effective deployment and usage.
  • Users encounter a steep learning curve with Wazuh, particularly during initial setup and configuration adjustments.
  • Users find the difficult setup of Wazuh challenging, particularly for newcomers managing configurations and tuning.

What Are Recent G2 Reviews of Wazuh?

What Are G2 Users Discussing About Wazuh?

Microsoft Sentinel

Microsoft Sentinel lets you see and stop threats before they cause harm, with SIEM reinvented for a modern world. Microsoft Sentinel is your birds-eye view across the enterprise. Put the cloud and large-scale intelligence from decades of Microsoft security experience to work. Make your threat detection and response smarter and faster with artificial intelligence (AI). Eliminate security infrastructure setup and maintenance, and elastically scale to meet your security needs—while reducing IT costs. With Microsoft Sentinel, you can: - Collect data at cloud scale—across all users, devices, applications, and infrastructure, both on-premises and in multiple clouds - Detect previously uncovered threats and minimize false positives using analytics and unparalleled threat intelligence from Microsoft - Investigate threats with AI and hunt suspicious activities at scale, tapping into decades of cybersecurity work at Microsoft -Respond to incidents rapidly with built-in orchestration and automation of common tasks

Average Rating: 4.4/5.0

Total Reviews: 275

How Do G2 Users Rate Microsoft Sentinel?

  • Quality of Support: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Microsoft Sentinel?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Who Uses This: Senior Software Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Large, 31% Medium

What Do G2 Reviewers Say About Microsoft Sentinel?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time monitoring of Microsoft Sentinel, gaining enhanced visibility and streamlined incident handling across their systems.
  • Users appreciate the effective alerting of Microsoft Sentinel, enhancing security through automated responses to unusual activities.
  • Users value the seamless dashboard usability of Microsoft Sentinel, enhancing their security management and threat response efficiency.
  • Users value the fast and secure threat response of Microsoft Sentinel, enhancing their security and alert management.
  • Users value the centralized data collection feature of Microsoft Sentinel, enhancing security analytics and threat visibility.
Cons
  • Users find the cloud dependency of Microsoft Sentinel challenging, making custom reporting and integration cumbersome.
  • Users find the complex configuration of Microsoft Sentinel challenging, often requiring extensive documentation and exploration.
  • Users find configuration issues in Microsoft Sentinel challenging, requiring time, effort, and technical expertise to navigate.
  • Users find the difficult setup of Microsoft Sentinel frustrating, often requiring extensive documentation exploration for configuration.
  • Users find the poor interface design of Microsoft Sentinel challenging, making navigation and understanding features difficult.

What Are Recent G2 Reviews of Microsoft Sentinel?

What Are G2 Users Discussing About Microsoft Sentinel?

SpinOne

SpinOne is an AI-powered SaaS data protection platform that combines automated backup and recovery, Data Leak and Loss Prevention (DLP), SaaS Security Posture Management (SSPM), ransomware protection, and continuous security monitoring to protect business-critical data across Google Workspace, Microsoft 365, Salesforce, and Slack. Recognized by Gartner in the Market Guide for SaaS Security Posture Management, SpinOne helps organizations secure, protect, recover, and govern SaaS data across their most critical cloud applications. Unlike traditional backup solutions or standalone security tools, SpinOne unifies SaaS backup, data recovery, Data Leak and Loss Prevention (DLP), SaaS Security Posture Management (SSPM), ransomware protection, and automated security controls in a single platform. Organizations use SpinOne to prevent data loss, reduce cyber risk, strengthen compliance, and improve business continuity. SpinOne provides automated Google Workspace backup and recovery for Gmail, Google Drive, Shared Drives, Calendar, Contacts, and Google Sites. IT teams can restore individual files, emails, folders, users, or complete accounts with point-in-time recovery to minimize downtime caused by accidental deletion, ransomware, insider threats, malicious applications, or operational errors. SpinOne also provides Microsoft 365 backup and recovery for Exchange Online, OneDrive, SharePoint, and Microsoft Teams. Across SaaS applications, SpinOne helps organizations maintain secure, recoverable, and compliant business data. Beyond backup and recovery, SpinOne protects SaaS environments with AI-powered Data Leak and Loss Prevention (DLP), helping organizations identify sensitive information, prevent unauthorized data exposure, reduce data leakage risks, and enforce security policies. SpinOne SaaS Security Posture Management (SSPM) continuously monitors SaaS environments, identifies security risks, detects misconfigurations, and helps automate remediation. Key capabilities include: Google Workspace backup and recovery Microsoft 365 backup and recovery SaaS backup and data protection Data Leak Prevention (DLP) Data Loss Prevention (DLP) SaaS Security Posture Management (SSPM) Ransomware detection and recovery Point-in-time recovery and granular restore Continuous SaaS security monitoring Sensitive data protection Compliance and audit readiness Business continuity and disaster recovery SpinOne has been recognized by Cyber Defense Magazine through multiple Global InfoSec Awards, including recognition for Secure SaaS Backup, Ransomware Protection for SaaS Data, SaaS/Cloud Security, Browser Security, and Data Security Posture Management categories. SpinOne helps organizations protect SaaS data throughout its lifecycle—from preventing data leaks and security risks to backing up critical information, detecting ransomware, and rapidly recovering after cyber incidents. Organizations choose SpinOne as a unified SaaS data protection platform to secure, back up, recover, and govern critical data across Google Workspace, Microsoft 365, Salesforce, and Slack.

Average Rating: 4.8/5.0

Total Reviews: 133

G2 Deal: Get $ 500 off SpinOne with this exclusive G2 deal!

SpinOne is an all-in-one, SaaS security platform that protects SaaS data for mission-critical SaaS applications. Start a 15-day free trial of SpinOne. When you're ready to purchase, add the promo code "SPINLOVER" to claim $ 500 off your first year of a main subscription purchase of SpinOne.

Price: $500 Off

View this exclusive G2 deal

How Do G2 Users Rate SpinOne?

  • Threat Intelligence: 9.2/10 (Category avg: 8.9/10)
  • Quality of Support: 9.6/10 (Category avg: 8.8/10)
  • Incident Case Management: 9.3/10 (Category avg: 8.5/10)
  • Incident Logs: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind SpinOne?

  • Seller: SpinAI
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Palo Alto, California
  • LinkedIn® Page: www.linkedin.com
    91 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, IT Director
  • Top Industries: Marketing and Advertising, Non-Profit Organization Management
  • Company Size: 51% Medium, 40% Small

What Do G2 Reviewers Say About SpinOne?

AI-generated summary from verified user reviews

Pros
  • Users love the user-friendly interface of SpinOne, making backup and restoration quick and easy.
  • Users commend SpinOne for its excellent customer support, highlighting their responsiveness and proactive assistance in backups and restorations.
  • Users love the ease of use and reliability of SpinOne for efficiently backing up Google Workspace data.
  • Users value the reliability and ease of use of SpinOne for secure Google Workspace backups and peace of mind.
  • Users value the reliable granular backups of SpinOne, appreciating its ease of use and excellent support.
Cons
  • Users face backup issues with limited management features and complications during large migrations, causing frustration.
  • Users find the per user license cost expensive, especially for large organizations or smaller budgets.
  • Users find the poor interface design of SpinOne hinders navigation and complicates complex tasks.
  • Users find pricing issues difficult, particularly for larger organizations needing full coverage or smaller ones with budget constraints.
  • Users experience lack of backup management tools, causing challenges in version control and space management during migrations.

What Are Recent G2 Reviews of SpinOne?

What Are G2 Users Discussing About SpinOne?

Sumo Logic

Sumo Logic, Inc. unifies and analyzes enterprise data, translating it into actionable insights through one AI-powered cloud-native log analytics platform. This single source of truth enables Dev, Sec and Ops teams to simplify complexity, collaborate efficiently and accelerate data-driven decisions that drive business value. Customers around the world rely on the Sumo Logic SaaS Log Analytics Platform for trusted insights to ensure application reliability, secure and protect against modern security threats, and gain insights into their cloud infrastructures. For more information, visit: SUMOLOGIC.COM

Average Rating: 4.4/5.0

Total Reviews: 413

How Do G2 Users Rate Sumo Logic?

  • Threat Intelligence: 7.7/10 (Category avg: 8.9/10)
  • Quality of Support: 8.6/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.1/10 (Category avg: 8.5/10)
  • Incident Logs: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Sumo Logic?

  • Seller: Sumo Logic
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Redwood City, CA
  • LinkedIn® Page: www.linkedin.com
    824 employees on LinkedIn®
  • Ownership: NASDAQ: SUMO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 38% Large

What Do G2 Reviewers Say About Sumo Logic?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use in Sumo Logic, enabling quick insights from data without complexity.
  • Users commend the powerful and accessible log management features of Sumo Logic, enhancing efficiency and visualization capabilities.
  • Users value the flexible analytics and powerful real-time features of Sumo Logic, enhancing collaboration and operational visibility.
  • Users value the real-time monitoring capabilities of Sumo Logic, enabling quick insights and effective data visualization.
  • Users value the powerful and accessible analytics of Sumo Logic, enhancing their data visualization and decision-making capabilities.
Cons
  • Users find the difficult learning curve of Sumo Logic challenging, especially transitioning from simpler tools.
  • Users face a steeper learning curve with Sumo Logic, especially when transitioning from tools like Splunk or Elastic.
  • Users note a steep learning curve with Sumo Logic that may challenge teams transitioning from other tools.
  • Users find Sumo Logic expensive, especially if data tiers are misconfigured, leading to unexpected high bills.
  • Users experience slow performance with Sumo Logic, facing delays and lag during queries, especially with large datasets.

What Are Recent G2 Reviews of Sumo Logic?

What Are G2 Users Discussing About Sumo Logic?

Splunk Enterprise Security

Splunk Enterprise Security (ES) is a data-centric, modern security information and event management (SIEM) solution that delivers data-driven insights for full breadth visibility into your security posture so you can protect your business and mitigate risk at scale. With unparalleled search and reporting, advanced analytics, integrated intelligence, and prepackaged security content, Splunk ES accelerates threat detection and investigation, letting you determine the scope of high-priority threats to your environment so you can quickly take action. Built on an open and scalable data platform, you can stay agile in the face of evolving threats and business needs. Our extensive ecosystem of Splunk, partner, and community-built integrations as well as flexible deployment options ensure your technology investments are working in tandem with Splunk ES whilst meeting you wherever you are on your cloud, multi-cloud, or hybrid journey.

Average Rating: 4.3/5.0

Total Reviews: 226

How Do G2 Users Rate Splunk Enterprise Security?

  • Threat Intelligence: 9.0/10 (Category avg: 8.9/10)
  • Quality of Support: 8.6/10 (Category avg: 8.8/10)
  • Incident Case Management: 7.5/10 (Category avg: 8.5/10)
  • Incident Logs: 8.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Splunk Enterprise Security?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Large, 30% Medium

What Do G2 Reviewers Say About Splunk Enterprise Security?

AI-generated summary from verified user reviews

Pros
  • Users value the powerful log analytics of Splunk Enterprise Security, enhancing their ability to analyze and correlate logs effectively.
  • Users benefit from the smart threat detection of Splunk Enterprise Security, enabling early identification of security issues.
  • Users value the extensive integration options of Splunk Enterprise Security, enhancing their existing Splunk investments and workflows.
  • Users value the versatility in data handling of Splunk Enterprise Security, enhancing insights and decision-making across domains.
  • Users appreciate the real-time monitoring capabilities of Splunk Enterprise Security, enhancing their cybersecurity responsiveness and decision-making.
Cons
  • Users find the complex setup of Splunk Enterprise Security time-consuming and challenging, impacting initial deployment effectiveness.
  • Users find the difficult learning curve of Splunk Enterprise Security challenging, especially for those new to data analysis.
  • Users often cite high costs at scale as a significant drawback, especially with growing data ingestion needs.
  • Users express concerns about poor customer support, highlighting the need for more responsive assistance and resources.
  • Users often face setup difficulties with Splunk Enterprise Security, requiring significant time and resources for configuration.

What Are Recent G2 Reviews of Splunk Enterprise Security?

What Are G2 Users Discussing About Splunk Enterprise Security?

CYREBRO

CYREBRO is an AI-native Managed Detection and Response solution, providing the core foundation and capabilities of a state-level Security Operations Center delivered through its cloud-based, interactive SOC Platform. CYREBRO rapidly detects, analyzes, investigates and responds to cyber threats, for businesses of all sizes.

Average Rating: 4.4/5.0

Total Reviews: 129

How Do G2 Users Rate CYREBRO?

  • Threat Intelligence: 8.6/10 (Category avg: 8.9/10)
  • Quality of Support: 8.3/10 (Category avg: 8.8/10)
  • Incident Case Management: 8.0/10 (Category avg: 8.5/10)
  • Incident Logs: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind CYREBRO?

  • Seller: CYREBRO
  • Year Founded: 2013
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 64% Medium, 25% Small

What Do G2 Reviewers Say About CYREBRO?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CYREBRO, enjoying straightforward navigation and quick access to critical investigations.
  • Users praise CYREBRO's highly responsive customer support, enhancing the overall experience and efficiency in issue resolution.
  • Users value the real-time alerts from CYREBRO, enhancing their ability to respond swiftly to cyber threats.
  • Users value the real-time alerts from CYREBRO, enhancing security and enabling quick, informed decision-making in threat management.
  • Users value the intuitive dashboard usability of CYREBRO for quick status visibility and efficient client monitoring.
Cons
  • Users report frequent update issues with CYREBRO, experiencing overwhelming alerts and integration difficulties during onboarding.
  • Users experience communication issues with CYREBRO, noting delays in support responses and vague initial ticket details.
  • Users experience poor customer support with delayed responses and vague details, impacting overall effectiveness and communication.
  • Users face dashboard issues with connectivity and limited features, complicating their overall experience with CYREBRO.
  • Users experience ineffective alerts due to overwhelming volume and vague details, impacting usability and clarity.

What Are Recent G2 Reviews of CYREBRO?

What Are G2 Users Discussing About CYREBRO?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated
Reviews & FAQs

Reviews Summary: The Best Incident Response Software for Small-Business Businesses

Thanks to 5136 Incident Response software reviews and associated data from users working for small-sized companies, at G2 we have some of the most definitive data on the best Incident Response software for the smaller space. We have identified 21 individual Incident Response products offering the features, pricing and support that Small-Business companies look for when comparing Incident Response software and solutions. These reviews are generated using the qualitative and quantitative feedback from G2 members working in small-sized companies and who have used these Incident Response software products.

When G2 reviewers submit their Incident Response software reviews, they often provide information on the type of company they work for and what market segment they belong to. We break these different market segments into three distinct groups:

  • Small Business Incident Response Software Reviews (< 50 employees)
  • smaller Incident Response Software Reviews (51-1,000 employees)
  • Enterprise Incident Response Software Reviews (1,001+ employees)

smaller businesses have their own unique requirements when it comes to Incident Response software compared to small or enterprise companies. That is why these individual small-sized company Incident Response software reviews are especially helpful when comparing product set up, ease of use and overall cost.

Below you will find FAQs and review snippets for Incident Response software products that work well in smaller environments. These reviews are written by real G2 users working for these Small-Business companies who have real-world experience with these Incident Response software products.

FAQs About Incident Response Software for Small-Business Businesses

Q. What are the best Incident Response software products for small-sized businesses, according to G2 reviewers?
  • CrowdStrike Falcon Endpoint Protection Platform - 4.7-stars, 30 reviews (11% from smaller reviewers)
  • Tines Stories - 4.6-stars, 45 reviews (28% from smaller reviewers)
  • Palo Alto Cortex XSIAM - 4.5-stars, 14 reviews (27% from smaller reviewers)
  • Torq AI SOC Platform - 4.9-stars, 28 reviews (29% from smaller reviewers)
  • UnderDefense MAXI - 5.0-stars, 15 reviews (45% from smaller reviewers)
Q. What are the least-liked Incident Response software products for professionals at small-sized companies, based on the overall G2 rating?
  • D3 Security - 4.2-stars, 15 reviews (24% from smaller reviewers)
  • SIRP - 4.5-stars, 10 reviews (45% from smaller reviewers)
  • LogRhythm SIEM - 4.2-stars, 17 reviews (18% from smaller reviewers)
  • Guardsix - 4.8-stars, 10 reviews (22% from smaller reviewers)
  • Rapid7 Next-Gen SIEM - 4.3-stars, 12 reviews (19% from smaller reviewers)
Q. What are the highest-rated Incident Response software tool features according to employees at Small-Business companies?
  • Encryption - 5.0-stars
  • Data Security - 5.0-stars
  • Data Visualization - 5.0-stars
Q. What are the features that are rated lowest by employees at Small-Business companies?
  • AI Text Summarization - 3.8-stars
  • AI Text Generation - 3.9-stars
  • System Isolation - 4.1-stars
Q. How many Incident Response software reviews are from users working in smaller companies?

516 out of all Incident Response software reviews on G2 are from users working in Small-Business companies (10%).

Here's What Reviewers Working at smaller Businesses Have to Say About Incident Response Software

What Small-Business Professionals Liked What Small-Business Professionals Disliked

LogRhythm SIEM: “LR SOAR is able to bring detection into action.”

Read Review

Datev: “Pretty much everything. The app to log in is super slow, Datev is complicated and old fashioned, the UX seems like from the 90s, there are no real integrations into other tools.”

Read Review

IBM QRadar SIEM: “Upgraded Technology and Support. SIEM, Digital Forensics, Cloud Security Monitoring and Analysis.”

Read Review

CYREBRO: “The platform still feels immature: some functionalities are limited or not well developed. The integrations with other tools are not as smooth as expected, and the customization of rules or reports is very basic. Sometimes, the analyses are superficial and require manual intervention to obtain real value.”

Read Review

CrowdStrike Falcon Endpoint Protection Platform: “Its strong real-time threat detection and response capabilities. It provides good visibility across endpoints, helps identify suspicious activity and makes it easier to investigate and respond to security incidents from centralized console.”

Read Review

Intezer: “Capping of the free tier. Some GUI issues”

Read Review

Recommendations To Others Problems Solved & Benefits

KnowBe4 PhishER/PhishER Plus: “Talking with a KnowBe4 rep definitely swayed us on the decision. They do a great job of demoing their products.”

Read Review

CrowdStrike Falcon Endpoint Protection Platform: “It helps us detect and respond to endpoint threats quickly by providing centralized visibility, which reduces the time we need to investigate and contain incidents.”

Read Review

Intezer: “Always do a PoC/PoV if one hasn't used it before.”

Read Review

Palo Alto Cortex XSIAM: “Cortex XSIAM is helping us address several challenges around security monitoring, alert fatigue, and incident response.<br><br>One of the biggest benefits for us is automated detection and investigation. XSIAM helps correlate related events and prioritize meaningful threats, reducing the volume of noise our security team needs to manually review. This allows us to focus more time on genuine incidents and threat hunting rather than repetitive alert investigation.”

Read Review

Microsoft Sentinel: “If you're a small team or a big organization, just go for it.”

Read Review

UnderDefense MAXI: “UnderDefense watches for suspicious activity around checkout and payment integrations across the client stores we run, including the ones hosted in completely different environments. Before, an odd pattern on one store could sit there until a client or a payment provider pointed it out. Now we hear about it first, with the relevant context already attached, so we can act on it the same day. It has also changed the conversation with our clients, since we can tell them their store is being watched around the clock and mean it.”

Read Review