Best Security Orchestration, Automation, and Response (SOAR) Software for Small Business

How Many Security Orchestration, Automation, and Response (SOAR) Software Products Does G2 Track?

Total Products under this Category: 98

Category Stats (Oct 2026)

  • Average Rating: 4.53/5 (↓0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: ServiceNow Security Operations (+0.44%) - Among all products in this category, ServiceNow Security Operations recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Security Orchestration, Automation, and Response (SOAR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,700+ Authentic Reviews
  • 98+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

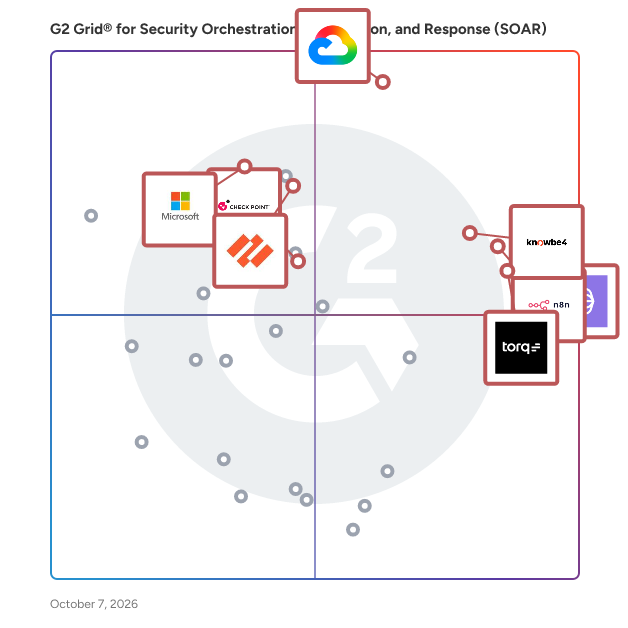
G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software

G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software plotting products by satisfaction and market presence

Highlighted products: n8n, Google Security Operations, Tines Stories, Palo Alto Cortex XSIAM, Torq AI SOC Platform, KnowBe4 PhishER/PhishER Plus, Check Point Infinity Platform, and Microsoft Sentinel.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-orchestration-automation-and-response-soar/grids.json?focus%5B%5D=n8n&focus%5B%5D=google-security-operations&focus%5B%5D=tines-stories&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=knowbe4-phisher-phisher-plus&focus%5B%5D=check-point-infinity-platform&focus%5B%5D=microsoft-sentinel&segment=small-business)

n8n

n8n is a workflow automation platform built for technical teams operationalizing AI. Built for technical teams, it offers 500+ integrations, custom code flexibility, and self-hosting options. With 180k+ Github Stars and a thriving community, n8n enables teams to build production-ready automation workflows that bridge AI with real business processes.

Average Rating: 4.7/5.0

Total Reviews: 307

How Do G2 Users Rate n8n?

  • Automated Remediation: 8.2/10 (Category avg: 8.7/10)
  • Quality of Support: 8.1/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.5/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind n8n?

  • Seller: n8n GmbH
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Berlin, Berlin
  • Twitter: @n8n_io
    81,824 Twitter followers
  • LinkedIn® Page: linkedin.com
    1,275 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Founder
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 18% Medium

What Do G2 Reviewers Say About n8n?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of n8n, enjoying intuitive designs that simplify complex workflow automation.
  • Users value the flexible automation capabilities of n8n, enhancing productivity through easy and extensive workflow management.
  • Users appreciate the extensive integrations of n8n, enabling seamless connections between various tools within workflows.
  • Users value the intuitive visual editor of n8n, enabling easy creation of complex workflows and automations.
  • Users enjoy the efficient workflow management of n8n, streamlining tasks and enhancing productivity through automation.
Cons
  • Users note a significant learning curve with n8n, requiring time and tutorials to optimize workflows effectively.
  • Users find n8n's difficult learning curve challenging, especially for non-developers managing complex workflows effectively.
  • Users note the absence of essential features in self-hosted n8n, hindering functionality and ease of use.
  • Users struggle with the poor interface design of n8n, finding it unresponsive and difficult to navigate effectively.
  • Users find the limitations in debugging and handling large workflows a significant challenge when using n8n.

What Are Recent G2 Reviews of n8n?

What Are G2 Users Discussing About n8n?

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 144

How Do G2 Users Rate Google Security Operations?

  • Automated Remediation: 9.9/10 (Category avg: 8.7/10)
  • Quality of Support: 8.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.1/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Student, Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Small, 33% Medium

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation of Google Security Operations, enhancing efficiency in threat management.
  • Users value the high-level threat detection capabilities of Google Security Operations, enhancing their security response efficiency.
  • Users find Google Security Operations very easy to use, allowing for quick incident analysis and efficient responses.
  • Users value the comprehensive security of Google Security Operations for effectively detecting and responding to threats.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and providing a unified security view.
Cons
  • Users find the costly upkeep of Google Security Operations challenging, especially for large organizations.
  • Users often face a steep learning curve with Google Security Operations, especially if unfamiliar with Google Cloud services.
  • Users find the implementation and configuration complex, requiring more time and resources compared to other tools.
  • Users find the learning difficulty of Google Security Operations challenging due to its complex features and setup.
  • Users find limited customization in Google Security Operations hinders adaptability and user experience for specific security needs.

What Are Recent G2 Reviews of Google Security Operations?

Tines Stories

Tines is the intelligent workflow platform trusted by the world's most advanced organizations. Companies like Coinbase, Databricks, Mars, Reddit, and SAP use Tines to power their most important workflows. With Tines, they’ve built a secure, flexible foundation to operationalize AI agents and intelligent workflows, unlocking productivity, moving faster, and future-proofing how work gets done.

Average Rating: 4.7/5.0

Total Reviews: 424

How Do G2 Users Rate Tines Stories?

  • Automated Remediation: 9.3/10 (Category avg: 8.7/10)
  • Quality of Support: 9.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Tines Stories?

  • Seller: Tines
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Dublin, IE
  • LinkedIn® Page: www.linkedin.com
    619 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Medium, 35% Large

What Do G2 Reviewers Say About Tines Stories?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Tines, enabling seamless automation without any coding knowledge.
  • Users highlight the flexibility and ease of automation with Tines, making integration and workflow creation seamless.
  • Users commend Tines for its exceptional customer support, appreciating the team's responsiveness and proactive assistance.
  • Users highlight Tines for its ease of use and rapid implementation, significantly boosting team efficiency and automation capabilities.
  • Users value Tines for its time-saving automation capabilities, allowing teams to focus on more strategic activities efficiently.
Cons
  • Users note a steep learning curve with Tines, especially for newcomers to automation and orchestration tools.
  • Users find Tines lacking in missing features that can hinder initial onboarding and expectations for functionality.
  • Users note a lack of features in Tines, pointing out missing options and inconsistencies in functionality.
  • Users find the complexity of advanced features in Tines overwhelming, especially for teams lacking a clear strategy.
  • Users find Tines has a difficult learning curve, particularly for newcomers to automation and orchestration tools.

What Are Recent G2 Reviews of Tines Stories?

What Are G2 Users Discussing About Tines Stories?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 103

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Automated Remediation: 7.6/10 (Category avg: 8.7/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 6.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 35% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users value the best-in-class log management of Palo Alto Cortex XSIAM, benefiting from its effective alerting and integration features.
  • Users find the user-friendly dashboard of Palo Alto Cortex XSIAM essential for monitoring and understanding alerts effectively.
  • Users value the real-time monitoring capabilities of Palo Alto Cortex XSIAM, enhancing threat detection and response efficiency.
  • Users value the simple and user-friendly interface of Palo Alto Cortex XSIAM, making monitoring effortless.
  • Users value the good dashboard creation tools in Palo Alto Cortex XSIAM, enhancing ease of use and implementation.
Cons
  • Users note that Palo Alto Cortex XSIAM requires significant resources, impacting implementation time and increasing infrastructure costs.
  • Users find the complexity of implementation for Palo Alto Cortex XSIAM to be time-consuming and resource-intensive.
  • Users find the cost of Palo Alto Cortex XSIAM to be high, especially for smaller businesses.
  • Users face dashboard issues with XSIAM, finding it difficult to monitor assets and navigate the interface.
  • Users face difficult setup issues with Palo Alto Cortex XSIAM, requiring expertise and extensive time for initial implementation.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

Torq AI SOC Platform

Torq is the AI SOC platform that combines agentic insights and automation so that enterprises can triage, investigate, and respond to actual risks, faster. Torq streamlines every step from alert through resolution. The platform analyzes your risk context to identify your biggest threats. Working alongside your SecOps staff, the Torq platform integrates with your security stack to facilitate containment and remediation workflows.

Average Rating: 4.8/5.0

Total Reviews: 151

How Do G2 Users Rate Torq AI SOC Platform?

  • Automated Remediation: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 9.6/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.4/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Torq AI SOC Platform?

  • Seller: torq
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @torq_io
    1,944 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    470 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Medium, 30% Small

What Do G2 Reviewers Say About Torq AI SOC Platform?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Torq AI SOC Platform, making it accessible for all skill levels.
  • Users value the efficiency of automated security workflows in Torq, enhancing both speed and effectiveness in threat management.
  • Users value the automation capabilities of Torq AI SOC Platform, enhancing efficiency and streamlining security workflows effectively.
  • Users appreciate the no-code automation capabilities of Torq, streamlining workflows and enhancing overall operational efficiency.
  • Users value the real-time threat detection of Torq AI SOC Platform, enhancing efficiency in responding to security incidents.
Cons
  • Users face a difficult learning curve with Torq AI SOC Platform, requiring significant training and support for effective use.
  • Users face a significant learning curve with Torq AI SOC Platform, requiring time and proper training for effective use.
  • Users note the missing features in Torq AI SOC Platform, especially regarding playbooks and incident management capabilities.
  • Users note that improvement is needed in grouping findings, vendor integration, and overall flexibility for better experience.
  • Users face poor interface design in Torq, including unresponsive buttons and a challenging debugging process.

What Are Recent G2 Reviews of Torq AI SOC Platform?

KnowBe4 PhishER/PhishER Plus

KnowBe4 PhishER Plus delivers automated incident response to eliminate SOC noise and remediate malicious emails across your organization simultaneously. It leverages AI to categorize reported messages across email and Microsoft Teams, automatically responding to reporters, flagging high-risk messages, and removing threats across all mailboxes. SOC teams can even flip malicious messages into training simulations to see who would have fallen victim. Customers report saving upwards of 99% of triage time, highly praising the platform's intuitive, user-friendly interface that transforms overwhelming manual workflows into fast, consistent actions. This layer of defense reviews threats slipping past other security layers, offering a single pane of glass view with leading third-party integrations like CrowdStrike, Webroot, and VirusTotal. PhishER Plus turns manual email triaging into a proactive, automated security posture.

Average Rating: 4.5/5.0

Total Reviews: 572

How Do G2 Users Rate KnowBe4 PhishER/PhishER Plus?

  • Automated Remediation: 8.7/10 (Category avg: 8.7/10)
  • Quality of Support: 9.2/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.9/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind KnowBe4 PhishER/PhishER Plus?

  • Seller: KnowBe4, Inc.
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Clearwater, FL
  • Twitter: @KnowBe4
    16,161 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,655 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Director of IT
  • Top Industries: Financial Services, Primary/Secondary Education
  • Company Size: 75% Medium, 13% Large

What Do G2 Reviewers Say About KnowBe4 PhishER/PhishER Plus?

AI-generated summary from verified user reviews

Pros
  • Users value the effective phishing tests and automation features of KnowBe4 PhishER, enhancing their security posture.
  • Users appreciate the email threat scoring feature of KnowBe4 PhishER, enabling proactive responses to potential threats.
  • Users value the automation capabilities of KnowBe4 PhishER, enhancing efficiency in identifying and managing phishing threats.
  • Users find KnowBe4 PhishER/PhishER Plus remarkably easy to use, enhancing efficiency in triaging and reporting spam emails.
  • Users appreciate the streamlined threat detection of KnowBe4 PhishER, making phishing email management effortless and efficient.
Cons
  • Users report issues with clean emails landing in the Junk Email folder, leading to troubleshooting difficulties and uncertainty.
  • Users experience frequent false positives, complicating automation and necessitating time-consuming manual reviews for accuracy.
  • Users experience ineffective email security with PhishER, as it fails to correctly filter phishing emails into the inbox.
  • Users find the learning curve intimidating for setup, requiring additional assistance for effective use of PhishER/PhishER Plus.
  • Users find the inefficient automation of PhishER frustrating, as it often misses campaigns and requires manual intervention.

What Are Recent G2 Reviews of KnowBe4 PhishER/PhishER Plus?

What Are G2 Users Discussing About KnowBe4 PhishER/PhishER Plus?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.6/10 (Category avg: 8.6/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

Microsoft Sentinel

Microsoft Sentinel lets you see and stop threats before they cause harm, with SIEM reinvented for a modern world. Microsoft Sentinel is your birds-eye view across the enterprise. Put the cloud and large-scale intelligence from decades of Microsoft security experience to work. Make your threat detection and response smarter and faster with artificial intelligence (AI). Eliminate security infrastructure setup and maintenance, and elastically scale to meet your security needs—while reducing IT costs. With Microsoft Sentinel, you can: - Collect data at cloud scale—across all users, devices, applications, and infrastructure, both on-premises and in multiple clouds - Detect previously uncovered threats and minimize false positives using analytics and unparalleled threat intelligence from Microsoft - Investigate threats with AI and hunt suspicious activities at scale, tapping into decades of cybersecurity work at Microsoft -Respond to incidents rapidly with built-in orchestration and automation of common tasks

Average Rating: 4.4/5.0

Total Reviews: 275

How Do G2 Users Rate Microsoft Sentinel?

  • Automated Remediation: 8.7/10 (Category avg: 8.7/10)
  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.3/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Microsoft Sentinel?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Who Uses This: Security Analyst, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Large, 31% Medium

What Do G2 Reviewers Say About Microsoft Sentinel?

AI-generated summary from verified user reviews

Pros
  • Users value the advanced threat detection of Microsoft Sentinel, enhancing security and proactive threat management.
  • Users value the easy integrations of Microsoft Sentinel, facilitating quick setup and streamlined security processes.
  • Users value the seamless integration of Microsoft Sentinel with various third-party and Microsoft products, enhancing functionality and management.
  • Users commend the ease of use of Microsoft Sentinel, facilitating quick integration and a user-friendly experience.
Cons
  • Users express concern over the high costs of Microsoft Sentinel, especially as data ingestion increases.
  • Users face integration issues with Microsoft Sentinel, especially when connecting to legacy systems and third-party tools.
  • Users find the complexity of Microsoft Sentinel challenging, requiring extensive training and effort for effective use.

What Are Recent G2 Reviews of Microsoft Sentinel?

What Are G2 Users Discussing About Microsoft Sentinel?

Swimlane

Swimlane automates the work security teams hate. As the leader in agentic AI security automation, Swimlane unifies operations across the SOC and beyond with its platform, Swimlane Turbine. The problem is real: over three million SecOps roles sit unfilled, and analysts drown in alerts while juggling 30+ disconnected tools, each with its own schema and quirks. Meanwhile, the average breach now costs $4.5 million. Swimlane closes that gap. Swimlane Hero AI, embedded within the Turbine platform, turns natural-language prompts into automated investigations and responses, cutting MTTR by 75%. Analysts trigger remediation with one click, backed by NIST-aligned case management. Turbine Canvas lets teams build playbooks and agents with no, low, or full code, so automation doesn't wait on a developer's calendar. The Swimlane Marketplace adds a growing library of agents, integrations, and playbooks, built on demand at no cost, ending vendor lock-in for good. Under the hood, Swimlane's Active Sensing Fabric ingests data at scale, pushing capability beyond traditional SOAR. Cloud-native architecture backs it up: one customer runs 25 million automated actions a day at 75,000 actions per minute. That's not a demo number. That's production. Analysts get customizable dashboards and AI-augmented reporting that turn raw activity into KPIs executives actually read, proving ROI without a translation layer. The market has taken notice. Independent evaluations against 15+ competitors all point the same direction: Swimlane leads. Inc. named it Best in Business. Customers at Northern Power, Toshiba, Weedmaps, and InComm Payments back that up, citing customizable playbooks, dashboards, and a professional services team that shows up when it counts. Swimlane doesn't just orchestrate security tasks. It gives every security function, from vulnerability management to compliance to business continuity, a way to move faster than the threats they're chasing.

Average Rating: 4.5/5.0

Total Reviews: 45

How Do G2 Users Rate Swimlane?

  • Automated Remediation: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 9.1/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.5/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Swimlane?

  • Seller: Swimlane
  • Year Founded: 2014
  • HQ Location: Boulder, US
  • Twitter: @swimlane
    1,628 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    271 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Medium, 31% Small

What Do G2 Reviewers Say About Swimlane?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Swimlane, appreciating its low-code automation and seamless integration capabilities.
  • Users appreciate the easy integrations of Swimlane, enhancing their playbooks with fast and robust connectivity options.
  • Users appreciate the personalization and robust integration features of Swimlane, enhancing usability and flexibility in security management.
  • Users value the seamless integrations of Swimlane, enhancing playbook creation and collaboration across various technologies.
  • Users value the flexibility of low-code automation in Swimlane, enabling extensive opportunities for security operations enhancements.
Cons
  • Users find Swimlane complex to set up and maintain, but support is timely and helpful in overcoming challenges.
  • Users find the learning curve steep initially with Swimlane, requiring time to become comfortable and proficient.
  • Users find the limited resources available for Swimlane challenging, particularly during initial deployment and playbook design.
  • Users report poor customer support, with slow responses and challenges in diagnosing upgrade issues.
  • Users find Swimlane's poor interface design cluttered and difficult to navigate, requiring a more modern refresh.

What Are Recent G2 Reviews of Swimlane?

What Are G2 Users Discussing About Swimlane?

CrowdSec

CrowdSec is an open-source security stack that detects aggressive behaviors and prevents them from accessing your systems. Its user-friendly design and ease of integration into your current security infrastructure offer a low technical entry barrier and a high-security gain. Once an unwanted behavior is detected, it is automatically blocked. The aggressive IP, scenario triggered and the timestamp is sent for curation, to avoid poisoning & false positives. If verified, this IP is then redistributed to all CrowdSec users running the same scenario. By sharing the threat they faced, all users are protecting each other.

Average Rating: 4.7/5.0

Total Reviews: 85

How Do G2 Users Rate CrowdSec?

  • Automated Remediation: 9.1/10 (Category avg: 8.7/10)
  • Quality of Support: 8.9/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.8/10 (Category avg: 8.6/10)
  • Workflow Automation: 7.8/10 (Category avg: 8.8/10)

Who Is the Company Behind CrowdSec?

  • Seller: CrowdSec
  • Year Founded: 2020
  • HQ Location: Paris, FR
  • Twitter: @Crowd_Security
    19,491 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 69% Small, 20% Medium

What Are Recent G2 Reviews of CrowdSec?

What Are G2 Users Discussing About CrowdSec?

D3 Security

D3 stands at the forefront of AI-powered security, providing real-time, autonomous SOC solutions that help organizations stay ahead of cyber threats. By merging autonomous investigation and triage with AI-guided remediation, D3 is delivering AI-powered, human-led cyber security solutions. Morpheus is D3 Security’s fully autonomous SOC solution that triages, investigates, and responds to every alert, 24/7. Morpheus covers 100% of your alerts — no exceptions — so your team never has to choose between chasing false positives or risking a breach. It triages 95% of alerts in under two minutes, integrating seamlessly with any SIEM, XDR, or security stack. Unlike traditional SOAR platforms, Morpheus doesn’t need endless playbook tuning; it can build response workflows on the fly, specific to your security stack. The result? Zero alert fatigue, fewer missed threats, and a dramatic boost in SOC efficiency, powered by a data privacy-friendly and SecOps-focused AI model.

Average Rating: 4.2/5.0

Total Reviews: 64

How Do G2 Users Rate D3 Security?

  • Automated Remediation: 8.3/10 (Category avg: 8.7/10)
  • Quality of Support: 9.0/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind D3 Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 49% Large, 41% Medium

What Are Recent G2 Reviews of D3 Security?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 187

How Do G2 Users Rate Intezer?

  • Automated Remediation: 9.2/10 (Category avg: 8.7/10)
  • Quality of Support: 8.6/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.8/10 (Category avg: 8.6/10)
  • Workflow Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Year Founded: 2015
  • HQ Location: New York
  • Twitter: @IntezerLabs
    10,170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 23% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Intezer, ensuring timely detection and blocking of malware.
  • Users value the effective malware detection and security features of Intezer that enhance system protection.
  • Users value Intezer for its effective malware detection and response capabilities, enhancing overall security and incident management.
  • Users value the high detection accuracy of Intezer, ensuring timely malware detection and enhanced system security.
  • Users appreciate the ease of use of Intezer, making malware detection and incident response straightforward and efficient.
Cons
  • Users feel the inability to control file visibility limits their privacy and management options in certain situations.
  • Users report complex interface issues with Intezer, making navigation challenging and less intuitive.
  • Users are concerned about limited file visibility control, which may impact their data privacy and access management.
  • Users find the difficult navigation of Intezer frustrating, with a less-than-ideal UI and small text affecting readability.
  • Users find the expensive pricing of Intezer problematic, especially with the limited free tier and some GUI issues.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated