Best Managed Detection and Response (MDR) Software for Small Business - Page 2

How Many Managed Detection and Response (MDR) Software Products Does G2 Track?

Total Products under this Category: 145

Category Stats (Oct 2026)

  • Average Rating: 4.49/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: October 22, 2026

How Does G2 Rank Managed Detection and Response (MDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 9,000+ Authentic Reviews
  • 145+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

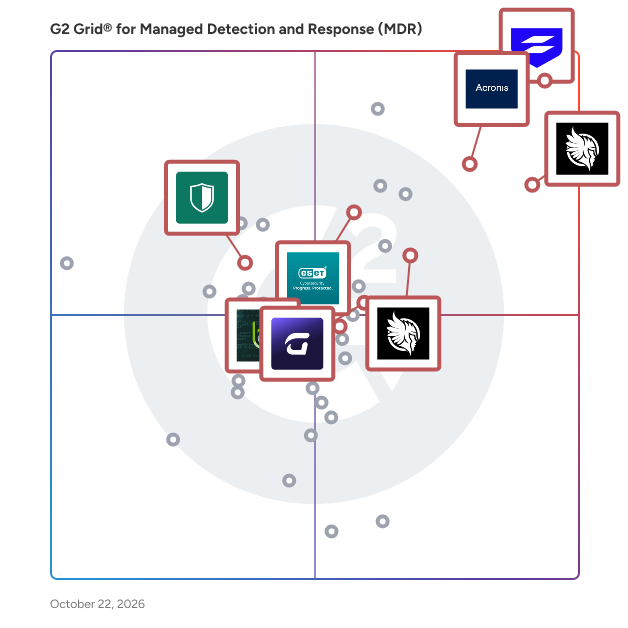
G2 Grid® for Managed Detection and Response (MDR) Software

G2 Grid® for Managed Detection and Response (MDR)  Software plotting products by satisfaction and market presence

Highlighted products: Huntress Managed EDR, Acronis Cyber Protect Cloud (now Acronis Cyber Platform), Sophos MDR, Huntress Managed ITDR, ESET PROTECT, Guardz, Kaseya MDR (formerly RocketCyber), and Blackpoint Cyber.

Underlying data: [Grid® JSON](https://www.g2.com/categories/managed-detection-and-response-mdr/grids.json?focus%5B%5D=huntress-managed-edr&focus%5B%5D=acronis-cyber-protect-cloud-now-acronis-cyber-platform&focus%5B%5D=sophos-mdr&focus%5B%5D=huntress-managed-itdr&focus%5B%5D=eset-protect&focus%5B%5D=guardz&focus%5B%5D=kaseya-mdr-formerly-rocketcyber&focus%5B%5D=blackpoint-cyber&segment=small-business)

LevelBlue MDR / MXDR

LevelBlue’s Managed Extended Detection and Response (MXDR) service delivers continuous, expert-driven protection across networks, endpoints, identities, cloud apps, and email. Backed by a 24/7 SOC, LevelBlue helps organizations rapidly realize value from existing technology investments while reducing cyber risk in complex hybrid environments. Our seasoned security engineers provide co-management for your XDR and SIEM, ensuring both are expertly managed and optimized to stay ahead of evolving threats. LevelBlue empowers your team with proprietary threat intelligence, flexible integration with existing technologies, and measurable outcomes—strengthening enterprise security and partnering with you to minimize cyber risk. Recent LevelBlue Acquisitions: - Alert Logic is a LevelBlue Co. - Trustwave is a LevelBlue Co. - Cybereason is a LevelBlue Co.

Average Rating: 4.5/5.0

Total Reviews: 247

How Do G2 Users Rate LevelBlue MDR / MXDR?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.7/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 8.2/10 (Category avg: 8.9/10)

Who Is the Company Behind LevelBlue MDR / MXDR?

Who Uses This Product?

  • Who Uses This: Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Medium, 36% Large

What Do G2 Reviewers Say About LevelBlue MDR / MXDR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the informative and easy-to-navigate dashboard of LevelBlue MDR / MXDR, enhancing their overall experience.
  • Users value the deployment ease of LevelBlue MDR/MXDR, appreciating its simple installation and user-friendly dashboard.
  • Users find the easy installation of LevelBlue MDR/MXDR straightforward, facilitating a smooth deployment experience.
  • Users value the ability to meet compliance requirements effectively with LevelBlue MDR / MXDR's robust SOC services.
  • Users value the complete visibility into incidents, enabling detailed tracking and understanding of each event.
Cons
  • Users find the difficult navigation of the vulnerability list and reporting process challenging and frustrating.
  • Users find the inefficient alert system somewhat cumbersome, needing improvements for better user experience and responsiveness.
  • Users find the poor reporting of LevelBlue MDR/MXDR frustrating, as it complicates access to essential information.

What Are Recent G2 Reviews of LevelBlue MDR / MXDR?

What Are G2 Users Discussing About LevelBlue MDR / MXDR?

Expel

Expel is the leading managed detection and response (MDR) provider trusted by some of the world’s most recognizable brands to expel their adversaries, minimize risk, and build security resilience. Expel’s 24x7x365 coverage spans the widest breadth of attack surfaces, including cloud, with 100% transparency. We combine world-class security practitioners and our AI-driven platform, Expel Workbench™, to ingest billions of events monthly and still achieve a 21-minute critical alert MTTR. Expel augments existing programs to help customers maximize their security investments and focus on building trust—with their customers, partners, and employees. Expel Managed Detection and Response delivers 24/7 decision support. We integrate with the tech you already have—across attack surfaces—to maximize your existing tech investments. Our platform automates analysis for your vendor alerts to filter out false positives. We’ll enrich the alerts that matter with context so we can resolve them with an average alert-to-fix of 21 minutes for critical alerts. Expel Threat Hunting provides peace of mind that your environment is secure and your defenses are optimized. Expel identifies attacks your automated detections missed, while providing insights that enable a stronger defensive strategy. You get clear guidance on how you can improve your defenses from a dedicated team of experts, without the strain on internal teams. Expel Vulnerability Prioritization accelerates your remediation process by letting you know exactly which vulnerabilities pose the greatest risk, with recommendations on next steps for immediate action. Expel Phishing takes complete ownership of your phishing inbox and provides remediation and guidance when threats enter via this critical attack vector. Unique data from your security technology helps Expel monitor and remove phishing emails from your inbox as well as protecting your entire environment from these attacks.

Average Rating: 4.6/5.0

Total Reviews: 74

How Do G2 Users Rate Expel?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.2/10 (Category avg: 9.1/10)
  • Automated remediation: 8.1/10 (Category avg: 8.7/10)
  • Automated investigation: 9.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Expel?

  • Seller: Expel
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Herndon, Virginia
  • Twitter: @ExpelSecurity
    12,791 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    476 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 51% Large, 35% Medium

What Do G2 Reviewers Say About Expel?

AI-generated summary from verified user reviews

Pros
  • Users find Expel to be effortless to use, facilitating seamless navigation and integration with comprehensive support.
  • Users value the easy integrations of Expel, enhancing connectivity within their security ecosystem effortlessly.
  • Users value the comprehensive security coverage of Expel, providing quick threat detection and seamless integration with existing systems.
  • Users value Expel for its rapid threat detection and response, ensuring swift identification and containment of security risks.
  • Users highlight the prompt and knowledgeable customer support of Expel, enhancing their overall security operations experience.
Cons
  • Users note the limited customization options in Expel, impacting alert specificity and overall reporting flexibility.
  • Users experience communication issues with Expel, noting delays in responses and confusion during the escalation process.
  • Users face challenges with the inefficient alert system, lacking customization and specificity in notifications for improved workflow.
  • Users experience limited integration across some tools with Expel, affecting investigation workflows and overall efficiency.
  • Users find Expel expensive, especially considering the additional time spent customizing reports for specific insights.

What Are Recent G2 Reviews of Expel?

What Are G2 Users Discussing About Expel?

Barracuda Managed XDR

Barracuda Managed XDR is the comprehensive next-generation cybersecurity solution that protects organizations of all sizes against today’s ever-evolving threat landscape. Barracuda Managed XDR is a fully managed service instantly augmenting an organization’s IT staff, identifying signals amidst noise, and reducing TTR from days to seconds. The solution features advanced AI-driven threat protection, SIEM, SOAR, and enterprise-grade threat intelligence from 11+ billion IOCs and hundreds of ML-enriched detection rules aligned to the MITRE ATT&CK framework. Ingesting trillions of events across endpoints, servers, identity, cloud, email, and firewalls, the cloud-native solution detects, responds to, and eliminates cyberthreats in real time across the attack lifecycle. An ‘open’ XDR solution, Barracuda Managed XDR integrates with an organization’s existing technology, ensuring a smooth deployment while enhancing security resilience and operational efficiency. Barracuda Managed XDR is powered by Barracuda’s 24/7/365 global SOC, featuring five specialized expert-level teams delivering best-in-class SLAs and proactive real-time threat detection and response.

Average Rating: 4.6/5.0

Total Reviews: 44

How Do G2 Users Rate Barracuda Managed XDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.6/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.2/10 (Category avg: 8.9/10)

Who Is the Company Behind Barracuda Managed XDR?

  • Seller: Barracuda
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Campbell, CA
  • Twitter: @Barracuda
    15,239 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,327 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Medium, 40% Small

What Do G2 Reviewers Say About Barracuda Managed XDR?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Barracuda Managed XDR, appreciating its straightforward setup and intuitive portal.
  • Users value the 24/7 monitoring of Barracuda Managed XDR, providing proactive security and peace of mind without added workload.
  • Users value the 24/7 security protection Barracuda Managed XDR provides, enhancing confidence and safeguarding endpoints effectively.
  • Users value the 24/7 proactive security of Barracuda Managed XDR, ensuring constant protection and peace of mind.
  • Users value the 24/7 proactive security alerts of Barracuda Managed XDR, enhancing confidence in threat detection and response.
Cons
  • Users desire a more customizable experience with Barracuda Managed XDR, especially in reporting and self-management options.
  • Users face a steep learning curve when setting up and navigating Barracuda Managed XDR's security features effectively.
  • Users find Barracuda Managed XDR to be not user-friendly, seeking greater customization and self-management options.
  • Users find the portal issues cumbersome, requiring multiple logins and dashboards for effective management of programs.
  • Users find the agent on endpoint devices limited, requiring portal logins to manage program permissions effectively.

What Are Recent G2 Reviews of Barracuda Managed XDR?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

CYREBRO

CYREBRO is an AI-native Managed Detection and Response solution, providing the core foundation and capabilities of a state-level Security Operations Center delivered through its cloud-based, interactive SOC Platform. CYREBRO rapidly detects, analyzes, investigates and responds to cyber threats, for businesses of all sizes.

Average Rating: 4.3/5.0

Total Reviews: 128

How Do G2 Users Rate CYREBRO?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.5/10 (Category avg: 9.1/10)
  • Automated remediation: 6.7/10 (Category avg: 8.7/10)
  • Automated investigation: 7.9/10 (Category avg: 8.9/10)

Who Is the Company Behind CYREBRO?

  • Seller: CYREBRO
  • Year Founded: 2013
  • HQ Location: Tel Aviv, IL
  • Twitter: @CYREBRO_IO
    307 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 64% Medium, 25% Small

What Do G2 Reviewers Say About CYREBRO?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CYREBRO, thanks to its intuitive UI and quick access to investigations.
  • Users value the responsive and knowledgeable customer support of CYREBRO, enhancing their overall experience and satisfaction.
  • Users value the dashboard usability of CYREBRO, benefiting from easy management and seamless incident response.
  • Users value the real-time alerts and actionable insights from CYREBRO, enhancing their security response and peace of mind.
  • Users value the real-time alerts from CYREBRO that enhance response time and simplify incident management effectively.
Cons
  • Users report experiencing update issues with alert management, leading to overwhelmed users and hindered onboarding processes.
  • Users face communication issues with Cyrebro support, experiencing slow response times and vague information that complicates problem resolution.
  • Users report poor customer support with slow response times and limited availability, impacting their overall experience.
  • Users often find ineffective alerts from CYREBRO, struggling with overwhelming volume and vague details requiring further support.
  • Users report an inefficient alert system, with overwhelming notifications and redundant alerts complicating their experience.

What Are Recent G2 Reviews of CYREBRO?

What Are G2 Users Discussing About CYREBRO?

Heimdal

Accommodate all your cybersecurity needs under one convenient roof with the Heimdal® Unified Cybersecurity Platform. Our cybersecurity solutions can be used as standalone products or integrated into one another as part of a cohesive and unified XDR platform. Whether you’re a reseller, distributor, MSSP, or an organization committed to bolstering your online security, we provide an array of cutting-edge products to make your mission smoother. Heimdal® is a fast-growing cybersecurity company focused on continuous technological innovation. Since its establishment in 2014 in Copenhagen, based on the winning idea of CTF World Champions, Heimdal has experienced spectacular growth by proactively building products that anticipate threatscape trends. The company offers a multi-layeredand unified security suite that combines threat prevention, patch and asset management, endpoint rights management, antivirus and mail security which together secure customers against cyberattacks and keep critical information and intellectual property safe. Heimdal has been recognized as a thought leader in the industry and has won multiple international awards both for its solutions and for its educational content creation. The Heimdal line of products currently consists of 10 products and 2 services. The former category encompasses DNS Security for Endpoints & Network, Patch & Asset Management, Privileged Access Management, Application Control, Next-Gen Endpoint Antivirus, Ransomware Encryption Protection, Email Security, Email Fraud Prevention, and Remote Desktop. The latter is represented by Endpoint Detection & Response, as well as eXtended Detection & Response, or EDR and XDR for short. Currently, Heimdal’s cybersecurity solutions are deployed in more than 45 countries and supported regionally from offices in 15+ countries, by 175+ highly qualified specialists. Heimdal is ISAE 3000 certified and secures more than 2 million endpoints for over 10,000 companies. The company supports its partners without concessions on the basis of predictability and scalability. The common goal is to create a sustainable ecosystem and a strategic partnership.

Average Rating: 4.4/5.0

Total Reviews: 81

How Do G2 Users Rate Heimdal?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 10.0/10 (Category avg: 9.1/10)
  • Automated remediation: 10.0/10 (Category avg: 8.7/10)
  • Automated investigation: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Heimdal?

  • Seller: Heimdal®
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • Twitter: @HeimdalSecurity
    5,086 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Construction
  • Company Size: 57% Medium, 30% Small

What Do G2 Reviewers Say About Heimdal?

AI-generated summary from verified user reviews

Pros
  • Users praise the easy setup of Heimdal, appreciating its straightforward installation and quick integration with their systems.
  • Users find that file transfer with Heimdal is seamless and reliable, enhancing overall productivity and ease of use.
  • Users commend Heimdal for its exceptional issue resolution support, providing quick and professional solutions exceeding expectations.
  • Users value the reliable patch management of Heimdal, delivering consistent performance without issues during monthly updates.
  • Users value the reliable security and user-friendly interface of Heimdal, enhancing overall satisfaction and support.
Cons
  • Users find the complex interface of Heimdal difficult to navigate, complicating their overall experience and functionality.
  • Users find the admin portal complex and illogical, making navigation frustrating and cumbersome for essential tasks.
  • Users find the customer support lacking during initial setup, which causes issues with product deployment and upgrades.
  • Users find the poor interface design of Heimdal difficult to navigate, complicating essential tasks and access.
  • Users experience restart issues with Heimdal, feeling unprotected after scans until the software is rebooted.

What Are Recent G2 Reviews of Heimdal?

Adlumin

Adlumin, an N-able Company, provides enterprise-grade cybersecurity for organizations of all sizes through its innovative Security Operations as a Service platform. With an agnostic approach, the Adlumin platform seamlessly integrates with existing tech stacks, and its flexible management options enable it to be self-managed by an internal team, or fully managed by Adlumin experts. The Adlumin platform stops cyber threats early with deep learning models tailored to each environment. It maximizes resource efficiency by optimizing existing technology and streamlining workflows across teams. Adlumin transforms risk into resilience by identifying and addressing vulnerabilities, while cybersecurity experts proactively uncover and neutralize threats before they can do damage. Adlumin empowers organizations to take control of their digital security making advanced protection accessible to all.

Average Rating: 4.7/5.0

Total Reviews: 65

How Do G2 Users Rate Adlumin?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.8/10 (Category avg: 9.1/10)
  • Automated remediation: 8.7/10 (Category avg: 8.7/10)
  • Automated investigation: 8.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Adlumin?

  • Seller: N-able
  • Company Website:
  • HQ Location: Morrisville, North Carolina
  • Twitter: @Nable
    15,859 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 56% Medium, 23% Small

What Do G2 Reviewers Say About Adlumin?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the detailed analytic reports of Adlumin, highlighting its reliability and user-friendly interface.
  • Users value the detailed analytic reports of Adlumin for their reliability and user-friendly interface.
  • Users appreciate the detailed analytic reports from Adlumin, enhancing reliability and ease of use.
  • Users praise the ease of management with Adlumin, appreciating its reliable and user-friendly interface.
  • Users praise the ease of use of Adlumin, highlighting its reliability and detail in analytic reports.
Cons
  • Users feel that the customer support for Adlumin is adequate but has room for improvement.

What Are Recent G2 Reviews of Adlumin?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated