Best Security Orchestration, Automation, and Response (SOAR) Software - Page 2

How Many Security Orchestration, Automation, and Response (SOAR) Software Products Does G2 Track?

Total Products under this Category: 99

Category Stats (Sep 2026)

  • Average Rating: 4.54/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: ReliaQuest GreyMatter (+1.22%) - Among all products in this category, ReliaQuest GreyMatter recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Security Orchestration, Automation, and Response (SOAR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,700+ Authentic Reviews
  • 99+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

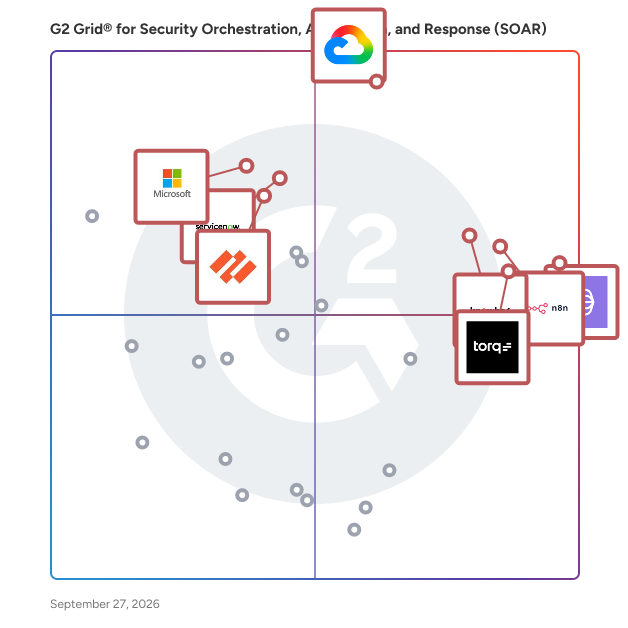
G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software

G2 Grid® for Security Orchestration, Automation, and Response (SOAR) Software plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, Tines Stories, n8n, Torq AI SOC Platform, KnowBe4 PhishER/PhishER Plus, ServiceNow Security Operations, Microsoft Sentinel, and Palo Alto Cortex XSIAM.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-orchestration-automation-and-response-soar/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=tines-stories&focus%5B%5D=n8n&focus%5B%5D=torq-ai-soc-platform&focus%5B%5D=knowbe4-phisher-phisher-plus&focus%5B%5D=servicenow-security-operations&focus%5B%5D=microsoft-sentinel&focus%5B%5D=palo-alto-cortex-xsiam)

IBM QRadar SOAR

IBM QRadar® SOAR is designed to help your security team respond to cyberthreats with confidence, automate with intelligence and collaborate with consistency. It guides your team in resolving incidents by codifying established incident response processes into dynamic playbooks. The open and agnostic platform helps accelerate and orchestrate their response by automating actions with intelligence and integrating with other security tools. IBM QRadar SOAR is available on AWS Marketplace.

Average Rating: 4.0/5.0

Total Reviews: 25

How Do G2 Users Rate IBM QRadar SOAR?

  • Automated Remediation: 7.5/10 (Category avg: 8.8/10)
  • Quality of Support: 7.9/10 (Category avg: 9.0/10)
  • Ease of Admin: 6.7/10 (Category avg: 8.6/10)
  • Workflow Automation: 7.4/10 (Category avg: 8.8/10)

Who Is the Company Behind IBM QRadar SOAR?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 72% Large, 21% Medium

What Do G2 Reviewers Say About IBM QRadar SOAR?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of IBM QRadar SOAR, appreciating its intuitive interface and seamless integration options.
  • Users value the automation capabilities of IBM QRadar SOAR, which significantly streamline security operations and reduce manual work.
  • Users value the seamless integrations with various tools, enhancing efficiency in security operations and workflows.
  • Users value the seamless integration capabilities of IBM QRadar SOAR, enhancing their security and workflow efficiency.
  • Users value the quick and effective customer support from IBM, enhancing their experience with QRadar SOAR.
Cons
  • Users face integration issues with IBM QRadar SOAR, experiencing difficulties in connecting applications and managing sophisticated transformations.
  • Users find the initial complexity of IBM QRadar SOAR challenging, making it hard to adapt to its features.
  • Users find the limited integration of IBM QRadar SOAR restrictive, hindering sophisticated implementations and transformations.
  • Users find that IBM QRadar SOAR has significant system limitations that hinder complex transformations and integration tasks.
  • Users often face bug issues with workflows, experiencing errors and occasional lagging that disrupts their productivity.

What Are Recent G2 Reviews of IBM QRadar SOAR?

Demisto

Demisto is a platform that provides automated and collaborative security solutions.

Average Rating: 4.5/5.0

Total Reviews: 15

How Do G2 Users Rate Demisto?

  • Automated Remediation: 10.0/10 (Category avg: 8.8/10)
  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.7/10 (Category avg: 8.6/10)
  • Workflow Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Demisto?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 53% Medium, 40% Small

What Are Recent G2 Reviews of Demisto?

SIRP

SIRP is an AI-native Autonomous SOC platform designed to evolve traditional Security Orchestration, Automation, and Response (SOAR) into governed, decision-driven security operations. Unlike legacy SOAR tools that rely on static playbooks and workflow automation, SIRP enables intelligent AI agents to analyze alerts, compute risk, execute response actions, and continuously learn from outcomes within defined policy boundaries. The platform combines contextual reasoning, real-time intelligence, and adaptive learning to reduce manual triage, minimize alert fatigue, and accelerate incident response while maintaining governance, auditability, and control. SIRP supports enterprise SOC teams and MSSPs seeking to operate at machine speed without sacrificing human oversight for high-impact decisions.

Average Rating: 4.7/5.0

Total Reviews: 22

How Do G2 Users Rate SIRP?

  • Automated Remediation: 9.2/10 (Category avg: 8.8/10)
  • Quality of Support: 9.8/10 (Category avg: 9.0/10)
  • Ease of Admin: 10.0/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind SIRP?

  • Seller: SIRP
  • Year Founded: 2017
  • HQ Location: Bethesda, Maryland
  • Twitter: @sirp_io
    74 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 41% Small, 37% Medium

What Do G2 Reviewers Say About SIRP?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the comprehensive automation features of SIRP, enhancing their security orchestration and incident management efficiency.
  • Users value the excellent customer support from SIRP, enhancing their overall experience with the product.
  • Users praise SIRP for its ease of use, making security automation and incident management seamless and efficient.
  • Users value the easy integrations offered by SIRP, enhancing their security automation and orchestration experience.
  • Users praise SIRP for its ease of use and excellent support, along with comprehensive security features and integrations.

What Are Recent G2 Reviews of SIRP?

Exabeam New-Scale Platform

The Exabeam New-Scale Security Operations Platform is built to help organizations detect, investigate, and respond to insider threats tied to both human users and non-human identities. It brings together behavioral analytics, automation, and AI-driven workflows to help security operations teams reduce risk and maintain operational integrity. The platform supports AI agent-powered threat detection, investigation, and response (TDIR) by automating high-friction tasks and applying behavioral context to every signal. By combining proactive risk identification with fast, guided response, the New-Scale Platform helps teams move from alert handling to informed decision-making. Designed for enterprise security operations teams, the New-Scale Platform supports organizations that need consistent visibility into internal risk without adding operational overhead. Analysts use behavioral analytics to understand what is normal for a user or agent, then quickly spot meaningful deviations. This approach is especially valuable in data-sensitive industries such as finance, healthcare, and technology, where internal misuse, compromised credentials, or agent misuse can create immediate business impact. At the core of the New-Scale Platform is advanced behavioral analytics. The platform analyzes activity patterns across identities, devices, and services to establish baselines of normal behavior. When activity deviates from those baselines, dynamic risk scoring helps security teams focus on the activity most likely to indicate misuse or compromise. This reduces alert noise and shortens the time it takes to understand what is happening and why. The New-Scale Platform also extends user and entity behavior analytics (UEBA) to non-human identities through Agent Behavior Analytics (ABA). ABA applies the same behavior-based approach as UEBA to service accounts, APIs, automation tools, and AI agents. By monitoring how agents typically interact with data and systems, the platform helps teams detect misuse, drift, or compromise that traditional controls often miss. Automation plays a central role in improving day-to-day operations. The New-Scale Platform automates investigation steps, enrichment, and response actions within TDIR workflows, allowing analysts to spend less time on repetitive tasks and more time validating risk and containing incidents. Behavioral context and AI-driven prioritization help teams address the most relevant threats first, improving response consistency without increasing workload. With the Exabeam New-Scale Platform, security teams can benchmark and prove the value of their security program against peers and measurable outcomes. Outcomes Navigator translates raw security data into business-relevant insights to demonstrate progress against the most strategic use cases, MITRE ATT&CK TTPs, and compliance initiatives. Together, user and entity behavior analytics (UEBA), Agent Behavior Analytics (ABA), and agent-powered automated TDIR workflows help security operations teams detect insider risk earlier, investigate faster, and respond with greater precision. The New-Scale Platform gives organizations a practical way to manage insider threats tied to people and agents, accelerate security operations, and prove security impact over time.

Average Rating: 4.6/5.0

Total Reviews: 15

How Do G2 Users Rate Exabeam New-Scale Platform?

  • Automated Remediation: 10.0/10 (Category avg: 8.8/10)
  • Quality of Support: 8.1/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.8/10 (Category avg: 8.6/10)
  • Workflow Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Exabeam New-Scale Platform?

  • Seller: Exabeam
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Broomfield, CO
  • Twitter: @exabeam
    5,374 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    785 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 56% Large, 31% Medium

What Do G2 Reviewers Say About Exabeam New-Scale Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Exabeam New-Scale Platform, benefiting from its seamless integrations and automation.
  • Users commend the detection accuracy of Exabeam New-Scale Platform, enhancing their ability to identify threats effectively.
  • Users appreciate the rich features and ease of integration offered by the Exabeam New-Scale Platform for security.
  • Users value the world-class UBEA features and comprehensive security tools of Exabeam New-Scale Platform.
  • Users value the automation capabilities of Exabeam, enhancing response efficiency and reducing manual investigation efforts.
Cons
  • Users find the complexity of the Exabeam New-Scale Platform challenging, especially during setup and configuration.
  • Users find the complex setup of Exabeam New-Scale Platform challenging, often requiring significant expertise for configuration.
  • Users find the difficult setup of Exabeam New-Scale Platform challenging, requiring significant expertise for effective management.
  • Users find the parsing issues in Exabeam New-Scale Platform challenging, impacting user-friendliness and efficiency.
  • Users find the software complexity of Exabeam New-Scale Platform challenging, requiring significant expertise for effective management.

What Are Recent G2 Reviews of Exabeam New-Scale Platform?

What Are G2 Users Discussing About Exabeam New-Scale Platform?

Shuffle

Shuffle is an open source automation platform for security professionals (SOAR). Run it locally: https://github.com/frikky/shuffle Try it out here: https://shuffler.io/register Join the community: https://discord.gg/B2CBzUm

Average Rating: 4.8/5.0

Total Reviews: 15

How Do G2 Users Rate Shuffle?

  • Automated Remediation: 9.5/10 (Category avg: 8.8/10)
  • Quality of Support: 9.4/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.4/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Shuffle?

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 67% Medium, 33% Small

What Are Recent G2 Reviews of Shuffle?

What Are G2 Users Discussing About Shuffle?

CrowdSec

CrowdSec is an open-source security stack that detects aggressive behaviors and prevents them from accessing your systems. Its user-friendly design and ease of integration into your current security infrastructure offer a low technical entry barrier and a high-security gain. Once an unwanted behavior is detected, it is automatically blocked. The aggressive IP, scenario triggered and the timestamp is sent for curation, to avoid poisoning & false positives. If verified, this IP is then redistributed to all CrowdSec users running the same scenario. By sharing the threat they faced, all users are protecting each other.

Average Rating: 4.7/5.0

Total Reviews: 85

How Do G2 Users Rate CrowdSec?

  • Automated Remediation: 9.1/10 (Category avg: 8.8/10)
  • Quality of Support: 8.9/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.8/10 (Category avg: 8.6/10)
  • Workflow Automation: 7.8/10 (Category avg: 8.8/10)

Who Is the Company Behind CrowdSec?

  • Seller: CrowdSec
  • Year Founded: 2020
  • HQ Location: Paris, FR
  • Twitter: @Crowd_Security
    19,491 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 69% Small, 20% Medium

What Are Recent G2 Reviews of CrowdSec?

What Are G2 Users Discussing About CrowdSec?

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Automated Remediation: 7.5/10 (Category avg: 8.8/10)
  • Quality of Support: 9.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 9.0/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • Twitter: @blumira
    1 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the easy setup of Blumira Automated Detection & Response, enabling quick integration and efficient use.
  • Users appreciate the responsive customer support of Blumira, finding it reliable and personal for their IT needs.
  • Users praise the setup ease of Blumira, appreciating its quick integration and automated alert features.
  • Users appreciate the reliable real-time alerting of Blumira, valuing its clarity and ease of use for all techs.
  • Users value the reliable real-time alerting of Blumira, appreciating its ease of use and helpful implementation.
Cons
  • Users find limited customization with detection filters, relying on support for creating necessary custom detections.
  • Users express concern over false positives that can disrupt business functions and lead to frustration with repeated alerts.
  • Users find Blumira's pricing expensive, citing inflexible models and insufficient features in lower tiers.
  • Users express frustration over false positives that waste time and complicate the overall experience with Blumira.
  • Users express concern over insufficient information, desiring better data accessibility and clearer deployment status.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

Swimlane

Swimlane automates the work security teams hate. As the leader in agentic AI security automation, Swimlane unifies operations across the SOC and beyond with its platform, Swimlane Turbine. The problem is real: over three million SecOps roles sit unfilled, and analysts drown in alerts while juggling 30+ disconnected tools, each with its own schema and quirks. Meanwhile, the average breach now costs $4.5 million. Swimlane closes that gap. Swimlane Hero AI, embedded within the Turbine platform, turns natural-language prompts into automated investigations and responses, cutting MTTR by 75%. Analysts trigger remediation with one click, backed by NIST-aligned case management. Turbine Canvas lets teams build playbooks and agents with no, low, or full code, so automation doesn't wait on a developer's calendar. The Swimlane Marketplace adds a growing library of agents, integrations, and playbooks, built on demand at no cost, ending vendor lock-in for good. Under the hood, Swimlane's Active Sensing Fabric ingests data at scale, pushing capability beyond traditional SOAR. Cloud-native architecture backs it up: one customer runs 25 million automated actions a day at 75,000 actions per minute. That's not a demo number. That's production. Analysts get customizable dashboards and AI-augmented reporting that turn raw activity into KPIs executives actually read, proving ROI without a translation layer. The market has taken notice. Independent evaluations against 15+ competitors all point the same direction: Swimlane leads. Inc. named it Best in Business. Customers at Northern Power, Toshiba, Weedmaps, and InComm Payments back that up, citing customizable playbooks, dashboards, and a professional services team that shows up when it counts. Swimlane doesn't just orchestrate security tasks. It gives every security function, from vulnerability management to compliance to business continuity, a way to move faster than the threats they're chasing.

Average Rating: 4.5/5.0

Total Reviews: 45

How Do G2 Users Rate Swimlane?

  • Automated Remediation: 9.2/10 (Category avg: 8.8/10)
  • Quality of Support: 9.1/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.5/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Swimlane?

  • Seller: Swimlane
  • Year Founded: 2014
  • HQ Location: Boulder, US
  • Twitter: @swimlane
    1,628 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    270 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Medium, 31% Small

What Do G2 Reviewers Say About Swimlane?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Swimlane, appreciating its low-code automation and seamless integration capabilities.
  • Users appreciate the easy integrations of Swimlane, enhancing their playbooks with fast and robust connectivity options.
  • Users appreciate the personalization and robust integration features of Swimlane, enhancing usability and flexibility in security management.
  • Users value the seamless integrations of Swimlane, enhancing playbook creation and collaboration across various technologies.
  • Users value the flexibility of low-code automation in Swimlane, enabling extensive opportunities for security operations enhancements.
Cons
  • Users find Swimlane complex to set up and maintain, but support is timely and helpful in overcoming challenges.
  • Users find the learning curve steep initially with Swimlane, requiring time to become comfortable and proficient.
  • Users find the limited resources available for Swimlane challenging, particularly during initial deployment and playbook design.
  • Users report poor customer support, with slow responses and challenges in diagnosing upgrade issues.
  • Users find Swimlane's poor interface design cluttered and difficult to navigate, requiring a more modern refresh.

What Are Recent G2 Reviews of Swimlane?

What Are G2 Users Discussing About Swimlane?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 187

How Do G2 Users Rate Intezer?

  • Automated Remediation: 9.2/10 (Category avg: 8.8/10)
  • Quality of Support: 8.6/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.8/10 (Category avg: 8.6/10)
  • Workflow Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Year Founded: 2015
  • HQ Location: New York
  • Twitter: @IntezerLabs
    10,170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    89 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 23% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Intezer, ensuring timely detection and blocking of malware.
  • Users value the effective malware detection and security features of Intezer that enhance system protection.
  • Users value Intezer for its effective malware detection and response capabilities, enhancing overall security and incident management.
  • Users value the high detection accuracy of Intezer, ensuring timely malware detection and enhanced system security.
  • Users appreciate the ease of use of Intezer, making malware detection and incident response straightforward and efficient.
Cons
  • Users feel the inability to control file visibility limits their privacy and management options in certain situations.
  • Users report complex interface issues with Intezer, making navigation challenging and less intuitive.
  • Users are concerned about limited file visibility control, which may impact their data privacy and access management.
  • Users find the difficult navigation of Intezer frustrating, with a less-than-ideal UI and small text affecting readability.
  • Users find the expensive pricing of Intezer problematic, especially with the limited free tier and some GUI issues.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

Guardsix

Guardsix is the sovereign security platform for lean European teams, bringing log management and audit-ready compliance to regulated industries, critical national infrastructure operators, and the Managed Security Service Providers (MSSPs) that serve them throughout Europe and beyond. Headquartered in Copenhagen, Denmark, Guardsix delivers sovereign-by-design security for organisations that carry real operational responsibility. The company employs several hundred cyber security specialists and keeps every organisation it serves in full control of their data, deployment, and operations. Guardsix provides a unified Command Centre platform combining: • Security Information and Event Management (SIEM) • Network Detection and Response (NDR) • Security Orchestration, Automation and Response (SOAR) • Fleet for enabling multi-tenant management • Governance for Healthcare internal risk compliance monitoring The platform is built to support European data sovereignty, regulatory compliance and operational control, with predictable node-based pricing and deployment options spanning on-premises, air-gapped, hybrid and cloud environments. Guardsix solutions help organisations: • Simplify audit readiness for regulations such as NIS2, DORA, and GDPR. • Support lean security teams with efficient log management and simplified workflows. • Scale security operations without increased complexity or ingestion-led pricing surprises. • Keep security data under European jurisdiction and control — where it lives, who operates it, and under whose laws. • Deploy on their own terms, on-prem and in infrastructure they control, keeping migration a real option at every renewal. • See clearly across their whole environment, with SIEM, NDR, SOAR, Fleet, and Governance in one sovereign platform rather than a stack of point tools. Guardsix maintains SOC 2 Type II attestation and designs its solutions in accordance with European data protection requirements. With a strong partner-first model, Guardsix works closely with regional MSSPs and service providers, combining sovereign-by-design security technology with European integrity and deployment flexibility.

Average Rating: 4.3/5.0

Total Reviews: 105

How Do G2 Users Rate Guardsix?

  • Automated Remediation: 8.5/10 (Category avg: 8.8/10)
  • Quality of Support: 9.0/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.0/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Guardsix?

  • Seller: guardsix
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Copenhagen, Capital Region
  • LinkedIn® Page: linkedin.com
    162 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Medium, 31% Small

What Do G2 Reviewers Say About Guardsix?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of Guardsix, simplifying administration and enhancing overall user experience.
  • Users appreciate the ease of use of Guardsix Log Management, making it simple and efficient for managing logs.
  • Users commend the excellent customer support of Logpoint, enhancing the overall experience and satisfaction with the product.
  • Users value the easy integrations of Logpoint, seamlessly unifying various telemetry types within their existing tech ecosystem.
  • Users value the efficiency of Logpoint, simplifying incident management and enhancing overall effectiveness in daily operations.
Cons
  • Users find the poor interface design challenging, making it difficult to navigate and utilize effectively.
  • Users find the UX improvement necessary as logs are poorly presented and the interface is slow and confusing.
  • Users find the interface complexity challenging, though improvements are expected in the near future.
  • Users find the confusing interface of Guardsix challenging and slow to navigate, impacting their overall experience.
  • Users feel there is an information deficiency about resource needs, leading to potential overuse and uncertainty in design.

What Are Recent G2 Reviews of Guardsix?

What Are G2 Users Discussing About Guardsix?

D3 Security

D3 stands at the forefront of AI-powered security, providing real-time, autonomous SOC solutions that help organizations stay ahead of cyber threats. By merging autonomous investigation and triage with AI-guided remediation, D3 is delivering AI-powered, human-led cyber security solutions. Morpheus is D3 Security’s fully autonomous SOC solution that triages, investigates, and responds to every alert, 24/7. Morpheus covers 100% of your alerts — no exceptions — so your team never has to choose between chasing false positives or risking a breach. It triages 95% of alerts in under two minutes, integrating seamlessly with any SIEM, XDR, or security stack. Unlike traditional SOAR platforms, Morpheus doesn’t need endless playbook tuning; it can build response workflows on the fly, specific to your security stack. The result? Zero alert fatigue, fewer missed threats, and a dramatic boost in SOC efficiency, powered by a data privacy-friendly and SecOps-focused AI model.

Average Rating: 4.2/5.0

Total Reviews: 64

How Do G2 Users Rate D3 Security?

  • Automated Remediation: 8.3/10 (Category avg: 8.8/10)
  • Quality of Support: 9.0/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.2/10 (Category avg: 8.6/10)
  • Workflow Automation: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind D3 Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 49% Large, 41% Medium

What Are Recent G2 Reviews of D3 Security?

DoControl

DoControl is a SaaS data security platform that helps organizations discover, understand, and protect sensitive data across business-critical applications like Google Workspace, Microsoft 365, Slack, Salesforce, and Box. DoControl gives security teams continuous visibility into where sensitive data lives, who and what has access to it, and how it’s being used - helping address risks from excessive permissions, external sharing, insider threats, third-party access, Shadow AI, and risky OAuth applications. Combining SaaS DLP, Data Access Governance, data classification, insider risk detection, and automated remediation, DoControl goes beyond alerting to actively reduce risk. Its agentless, API-driven platform uses identity and business context to detect risky activity and automatically enforce policies - revoking access, removing public sharing, quarantining sensitive data, and remediating exposure at scale - without proxies, endpoint agents, or disruption to users.

Average Rating: 4.7/5.0

Total Reviews: 55

How Do G2 Users Rate DoControl?

  • Quality of Support: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind DoControl?

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 53% Large, 47% Medium

What Do G2 Reviewers Say About DoControl?

AI-generated summary from verified user reviews

Pros
  • Users value the clear visibility into SaaS data, ensuring informed decision-making and improved security oversight.
  • Users value the clear visibility and continuous monitoring of DoControl, enhancing their ability to detect security flaws.
  • Users value the real-time monitoring capabilities of DoControl, enhancing visibility into SaaS data and user activities.
  • Users value the enhanced security monitoring of DoControl, enabling them to identify and address potential security flaws effectively.
  • Users value the robust access control feature of DoControl, enhancing security by monitoring cloud application activities effectively.
Cons
  • Users find the complexity of configurations challenging, particularly when dealing with policy management and user access settings.
  • Users find the difficult learning curve in onboarding and policy management interface challenging in DoControl.
  • Users find the policy management interface confusing, making it challenging to manage strict user access effectively.
  • Users find complex configuration time-consuming, limiting the effectiveness of the otherwise easy-to-create custom policies.
  • Users find configuration issues arise from limited options and the complexity of creating custom setups takes time.

What Are Recent G2 Reviews of DoControl?

IBM Cloud Pak for Security

IBM Cloud Pak for Security is a platform that helps you uncover hidden threats, make more informed risk-based decisions and prioritize your team’s time

Average Rating: 4.4/5.0

Total Reviews: 9

How Do G2 Users Rate IBM Cloud Pak for Security?

  • Automated Remediation: 8.9/10 (Category avg: 8.8/10)
  • Quality of Support: 9.2/10 (Category avg: 9.0/10)
  • Ease of Admin: 8.9/10 (Category avg: 8.6/10)
  • Workflow Automation: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind IBM Cloud Pak for Security?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Company Size: 40% Large, 30% Medium

What Are Recent G2 Reviews of IBM Cloud Pak for Security?

What Are G2 Users Discussing About IBM Cloud Pak for Security?

Microsoft Security Copilot

Empower your defenders to detect hidden patterns, harden defenses, and respond to incidents faster with generative AI

Average Rating: 4.3/5.0

Total Reviews: 12

How Do G2 Users Rate Microsoft Security Copilot?

  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Ease of Admin: 7.8/10 (Category avg: 8.6/10)

Who Is the Company Behind Microsoft Security Copilot?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 75% Large, 17% Medium

What Do G2 Reviewers Say About Microsoft Security Copilot?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Microsoft Security Copilot, enhancing security management through seamless integration and AI-driven insights.
  • Users appreciate the AI integration for threat detection, enhancing their ability to quickly identify and mitigate risks.
  • Users appreciate the AI-driven threat detection of Microsoft Security Copilot, making security management more efficient and effective.
  • Users value the AI-powered threat detection of Microsoft Security Copilot, enhancing their ability to identify and respond to risks.
  • Users highlight the automation of routine tasks by Microsoft Security Copilot, enhancing efficiency and accelerating incident response.
Cons
  • Users find complexity in Microsoft Security Copilot due to the need for careful input and extra double-checking.
  • Users find Microsoft Security Copilot to be expensive, suggesting it could be more cost effective for wider accessibility.
  • Users find the difficult learning curve of Microsoft Security Copilot challenging, especially for those inexperienced with AI tools.
  • Users face false positives that waste time and hinder workflow efficiency, complicating the use of Security Copilot.
  • Users are frustrated with the limited access of Microsoft Security Copilot, affecting overall usability and experience.

What Are Recent G2 Reviews of Microsoft Security Copilot?

NetWitness Platform

NetWitness is a comprehensive threat detection, investigation and response platform that combines visibility, analytics, insight, and automation into a single solution. It collects and analyzes data across all capture points (logs, packets, netflow, endpoint and IoT) and computing platforms (physical, virtual and cloud), enriching data with threat intelligence and business context.

Average Rating: 3.9/5.0

Total Reviews: 23

How Do G2 Users Rate NetWitness Platform?

  • Automated Remediation: 9.2/10 (Category avg: 8.8/10)
  • Quality of Support: 7.6/10 (Category avg: 9.0/10)
  • Ease of Admin: 7.4/10 (Category avg: 8.6/10)
  • Workflow Automation: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind NetWitness Platform?

  • Seller: NetWitness
  • Year Founded: 1997
  • HQ Location: Bedford, MA
  • Twitter: @Netwitness
    1,621 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    204 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 54% Large, 33% Medium

What Do G2 Reviewers Say About NetWitness Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized management of NetWitness Platform, which simplifies threat hunting across various data sources.
  • Users appreciate the centralized threat hunting capabilities of the NetWitness Platform, reducing tool sprawl and enhancing security efficiency.
  • Users value the packet capture and replay capabilities of NetWitness Platform for in-depth forensic investigations.
  • Users value the ability to capture full network packets for deep forensic investigation, enhancing their analytic capabilities.
  • Users appreciate the centralized view of the Management Console, simplifying threat hunting across diverse data sources.
Cons
  • Users find the complex implementation of NetWitness Platform challenging, needing expert skills for initial setup and upgrades.
  • Users face complexity in initial setup and upgrades with NetWitness Platform, requiring significant technical expertise and stability concerns.
  • Users face a complex setup for the NetWitness Platform, often needing extensive technical expertise for deployment and upgrades.
  • Users face deployment difficulties with the NetWitness Platform, often requiring advanced technical skills and experiencing upgrade instability.
  • Users find the expertise required for initial setup and upgrades complex, leading to deployment challenges.

What Are Recent G2 Reviews of NetWitness Platform?

What Are G2 Users Discussing About NetWitness Platform?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024