Best Managed Detection and Response (MDR) Software for Medium-Sized Businesses - Page 2

How Many Managed Detection and Response (MDR) Software Products Does G2 Track?

Total Products under this Category: 149

Category Stats (Nov 2026)

  • Average Rating: 4.49/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.08%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Managed Detection and Response (MDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 9,500+ Authentic Reviews
  • 149+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

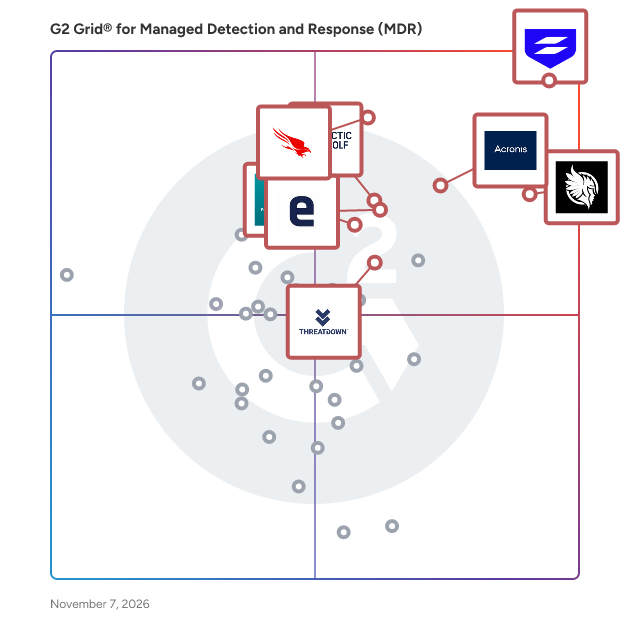
G2 Grid® for Managed Detection and Response (MDR) Software

G2 Grid® for Managed Detection and Response (MDR)  Software plotting products by satisfaction and market presence

Highlighted products: Sophos MDR, CrowdStrike Falcon Endpoint Protection Platform, Arctic Wolf, Huntress Managed EDR, Acronis Cyber Protect Cloud (now Acronis Cyber Platform), eSentire, ESET PROTECT, and ThreatDown.

Underlying data: [Grid® JSON](https://www.g2.com/categories/managed-detection-and-response-mdr/grids.json?focus%5B%5D=sophos-mdr&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=arctic-wolf&focus%5B%5D=huntress-managed-edr&focus%5B%5D=acronis-cyber-protect-cloud-now-acronis-cyber-platform&focus%5B%5D=esentire&focus%5B%5D=eset-protect&focus%5B%5D=threatdown&segment=mid-market)

Pondurance

Pondurance is the only provider of risk-based MDR services specifically engineered to eliminate breach risks. As a full-service provider of DFIR, MDR, and cybersecurity advisory and compliance services, Pondurance protects midmarket organizations from data breach risks before, during, and after its occurrence. Organizations entrusted with consumer protected health information (PHI) and personally identifiable information (PII) rely on Pondurance to provide a unified platform and trusted U.S.-based SOC service.

Average Rating: 4.6/5.0

Total Reviews: 23

How Do G2 Users Rate Pondurance?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.5/10 (Category avg: 9.1/10)
  • Automated remediation: 8.7/10 (Category avg: 8.7/10)
  • Automated investigation: 8.8/10 (Category avg: 8.9/10)

Who Is the Company Behind Pondurance?

  • Seller: Pondurance
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Indianapolis, US
  • LinkedIn® Page: www.linkedin.com
    105 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Hospital & Health Care
  • Company Size: 65% Medium, 22% Large

What Do G2 Reviewers Say About Pondurance?

AI-generated summary from verified user reviews

Pros
  • Users value Pondurance for its excellent response times, ensuring prompt follow-ups and effective issue resolution.
  • Users are impressed with Pondurance's proactive cybersecurity services and appreciate the dedicated support and responsiveness.
  • Users value the continuous monitoring provided by Pondurance, appreciating the thorough support and quick response times.
  • Users commend Pondurance for its proactive customer support, enhancing security through effective communication and prompt assistance.
  • Users value the real-time monitoring of Pondurance, appreciating prompt follow-ups on any arising issues.
Cons
  • Users experience occasional deployment issues with Pondurance, but find them to be infrequent and minor.

What Are Recent G2 Reviews of Pondurance?

Expel

Expel is the leading managed detection and response (MDR) provider trusted by some of the world’s most recognizable brands to expel their adversaries, minimize risk, and build security resilience. Expel’s 24x7x365 coverage spans the widest breadth of attack surfaces, including cloud, with 100% transparency. We combine world-class security practitioners and our AI-driven platform, Expel Workbench™, to ingest billions of events monthly and still achieve a 21-minute critical alert MTTR. Expel augments existing programs to help customers maximize their security investments and focus on building trust—with their customers, partners, and employees. Expel Managed Detection and Response delivers 24/7 decision support. We integrate with the tech you already have—across attack surfaces—to maximize your existing tech investments. Our platform automates analysis for your vendor alerts to filter out false positives. We’ll enrich the alerts that matter with context so we can resolve them with an average alert-to-fix of 21 minutes for critical alerts. Expel Threat Hunting provides peace of mind that your environment is secure and your defenses are optimized. Expel identifies attacks your automated detections missed, while providing insights that enable a stronger defensive strategy. You get clear guidance on how you can improve your defenses from a dedicated team of experts, without the strain on internal teams. Expel Vulnerability Prioritization accelerates your remediation process by letting you know exactly which vulnerabilities pose the greatest risk, with recommendations on next steps for immediate action. Expel Phishing takes complete ownership of your phishing inbox and provides remediation and guidance when threats enter via this critical attack vector. Unique data from your security technology helps Expel monitor and remove phishing emails from your inbox as well as protecting your entire environment from these attacks.

Average Rating: 4.6/5.0

Total Reviews: 74

How Do G2 Users Rate Expel?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.2/10 (Category avg: 9.1/10)
  • Automated remediation: 8.1/10 (Category avg: 8.7/10)
  • Automated investigation: 9.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Expel?

  • Seller: Expel
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Herndon, Virginia
  • LinkedIn® Page: www.linkedin.com
    476 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 51% Large, 35% Medium

What Do G2 Reviewers Say About Expel?

AI-generated summary from verified user reviews

Pros
  • Users highlight ease of use with Expel, appreciating its seamless setup and intuitive Workbench for daily operations.
  • Users value the high-fidelity detection and collaboration of Expel, enhancing security maturity and operational efficiency.
  • Users value Expel for its responsive and knowledgeable customer support, ensuring smooth operations and quick issue resolution.
  • Users value the easy integrations of Expel, making it simple to connect with various security tools effortlessly.
  • Users highlight the unwavering reliability of Expel, transforming security operations with transparency and expert support.
Cons
  • Users experience communication issues with Expel, desiring more timely responses and clearer escalation procedures for incidents.
  • Users note the limited customization in Expel, making it challenging to adapt alerts and processes to specific needs.
  • Users find the inefficient alert system lacks customization, hindering prioritization and complicating incident management processes.
  • Users encounter limited integration with certain tools, necessitating alternate workflows and hindering overall efficiency in investigations.
  • Users find Expel to be expensive due to time spent on customizing less flexible reporting features and alerts.

What Are Recent G2 Reviews of Expel?

What Are G2 Users Discussing About Expel?

CyberMaxx

CyberMaxx is a modern MDR leader, combining advanced AI threat detection with seasoned human expertise to deliver faster, smarter, and more holistic response. Our solution helps organizations enhance their cybersecurity posture through proactive threat detection and rapid incident response. With a focus on delivering comprehensive security services, CyberMaxx is tailored to meet the needs of businesses seeking to safeguard their digital assets against an ever-evolving landscape of cyber threats. The target audience for CyberMaxx includes mid-sized businesses that require robust security measures but may lack the internal resources or expertise to effectively manage cybersecurity threats. Organizations in various regulated sectors, including finance, healthcare, and municipalities, can benefit from CyberMaxx's offerings, which are designed to provide peace of mind through continuous monitoring and expert intervention. The service is particularly valuable for companies that prioritize security but want to avoid the complexities of managing multiple vendors or investing in additional technologies. One of the standout features of CyberMaxx is its “Big R Response,” which ensures 24/7/365 threat detection backed by a team of seasoned experts. The Threat Response Team operates within the Security Operations Center (SOC) to investigate potential threats immediately, assessing the full scope of any compromise and working diligently with clients until remediation is achieved. This level of responsiveness is crucial for minimizing the impact of security incidents and ensuring business continuity. CyberMaxx also distinguishes itself through its tech-enabled approach, which integrates existing best-in-class technologies without requiring clients to commit to specific vendors or make additional investments. This flexibility allows organizations to leverage their current infrastructure while benefiting from CyberMaxx’s expertise. Furthermore, the dedicated account resources provided by CyberMaxx act as an extension of the client’s team, delivering the equivalent of 3-5 full-time technical experts. This ensures that clients receive personalized support and guidance tailored to their unique security needs. In addition to its core MDR services, CyberMaxx offers a suite of Offensive Services, including Penetration Testing, Risk & Compliance Assessments, and Security Awareness Training. These services are designed to strengthen defenses against evolving threats, reinforcing the belief that proactive offense is essential for effective defense. With over 24 years of experience and a client base of more than 800 global customers, CyberMaxx brings unmatched security expertise and a commitment to partnership, making it a valuable ally in the fight against cyber threats.

Average Rating: 4.7/5.0

Total Reviews: 42

How Do G2 Users Rate CyberMaxx?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.8/10 (Category avg: 9.1/10)
  • Automated remediation: 9.6/10 (Category avg: 8.7/10)
  • Automated investigation: 9.4/10 (Category avg: 8.9/10)

Who Is the Company Behind CyberMaxx?

  • Seller: CyberMaxx
  • Company Website:
  • Year Founded: 2003
  • HQ Location: New York City, NY
  • LinkedIn® Page: linkedin.com
    223 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Hospital & Health Care
  • Company Size: 43% Medium, 40% Large

What Do G2 Reviewers Say About CyberMaxx?

AI-generated summary from verified user reviews

Pros
  • Users commend the exceptional SOC services of CyberMaxx, appreciating their proactive communication and rapid incident response.
  • Users value the clear and timely alert management from CyberMaxx that enhances operational efficiency and communication.
  • Users value the 24/7 continuous monitoring by CyberMaxx, ensuring quick response and proactive threat management.
  • Users highly value the clear and regular communication from CyberMaxx, enhancing collaboration and alleviating confusion.
  • Users value CyberMaxx for its immediate response, ensuring prompt handling of issues as they arise.
Cons
  • Users experience communication issues with CyberMaxx, leading to frustration and inadequate response to their concerns.
  • Users express frustration with the inefficient alert system that complicates communication and fails to meet expectations.

What Are Recent G2 Reviews of CyberMaxx?

What Are G2 Users Discussing About CyberMaxx?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Barracuda Managed XDR

Barracuda Managed XDR is the comprehensive next-generation cybersecurity solution that protects organizations of all sizes against today’s ever-evolving threat landscape. Barracuda Managed XDR is a fully managed service instantly augmenting an organization’s IT staff, identifying signals amidst noise, and reducing TTR from days to seconds. The solution features advanced AI-driven threat protection, SIEM, SOAR, and enterprise-grade threat intelligence from 11+ billion IOCs and hundreds of ML-enriched detection rules aligned to the MITRE ATT&CK framework. Ingesting trillions of events across endpoints, servers, identity, cloud, email, and firewalls, the cloud-native solution detects, responds to, and eliminates cyberthreats in real time across the attack lifecycle. An ‘open’ XDR solution, Barracuda Managed XDR integrates with an organization’s existing technology, ensuring a smooth deployment while enhancing security resilience and operational efficiency. Barracuda Managed XDR is powered by Barracuda’s 24/7/365 global SOC, featuring five specialized expert-level teams delivering best-in-class SLAs and proactive real-time threat detection and response.

Average Rating: 4.5/5.0

Total Reviews: 54

How Do G2 Users Rate Barracuda Managed XDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.6/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 9.2/10 (Category avg: 8.9/10)

Who Is the Company Behind Barracuda Managed XDR?

  • Seller: Barracuda
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Campbell, CA
  • LinkedIn® Page: www.linkedin.com
    2,327 employees on LinkedIn®
  • Ownership: Private

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 34% Small

What Do G2 Reviewers Say About Barracuda Managed XDR?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use and straightforward setup of Barracuda Managed XDR, enhancing overall security management.
  • Users appreciate the 24/7 proactive monitoring of Barracuda Managed XDR, enhancing security without overburdening tech teams.
  • Users value the 24/7 security and straightforward setup of Barracuda Managed XDR, enhancing protection effortlessly.
  • Users value the 24/7 security of Barracuda Managed XDR, ensuring proactive protection against cyber threats with minimal effort.
  • Users value the timely alerts from Barracuda Managed XDR, enhancing threat navigation and response efficiency.
Cons
  • Users find the lack of customization in Barracuda Managed XDR limits their ability to tailor reporting and management.
  • Users note a challenging learning curve with Barracuda Managed XDR, particularly during initial setup and feature navigation.
  • Users feel the interface is not user-friendly and desire more customization options, particularly for reporting and management.
  • Users find the portal issues cumbersome, requiring logins for endpoint management and complicating overall product handling.
  • Users find the agent on the endpoint device limited, requiring logins to the portal for program management.

What Are Recent G2 Reviews of Barracuda Managed XDR?

Kaseya MDR (formerly RocketCyber)

A complete rebuild of RocketCyber, it delivers more powerful protection in a simpler, more modern platform — with 24/7 AI-augmented, human-led threat detection and response across endpoints, firewalls and Microsoft 365, backed by a global SOC operating from Florida and Ireland. And unlike vendors that require you to rip and replace existing security tools, Kaseya MDR integrates with both Kaseya and third-party EDR solutions, so you can maintain protection regardless of your current environment. At the core of the platform is an AI-enhanced SOC, powered by Kaseya Intelligence, that handles machine-speed triage, noise reduction and event correlation before human analysts step in. Your team only sees validated threats that require attention, not hundreds of raw alerts to sort through manually. When action is needed, the SOC executes containment directly — device isolation, account lock, session revocation — without requiring internal intervention, with direct phone access to SOC analysts available when you need it.

Average Rating: 4.4/5.0

Total Reviews: 65

How Do G2 Users Rate Kaseya MDR (formerly RocketCyber)?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.7/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 8.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Kaseya MDR (formerly RocketCyber)?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 80% Small, 18% Medium

What Do G2 Reviewers Say About Kaseya MDR (formerly RocketCyber)?

AI-generated summary from verified user reviews

Pros
  • Users value the clear alerts and helpful recommendations from Kaseya MDR, enhancing their monitoring experience.
  • Users value the easy integrations of Kaseya MDR, appreciating the seamless connectivity with other systems and features.
  • Users value the 24/7 availability of Kaseya MDR for timely support, even during off-hours.
  • Users appreciate the clear and understandable alerts from Kaseya MDR, along with detailed reviews and helpful resolutions.
  • Users appreciate the supportive customer support of Kaseya MDR, providing clear alerts and helpful resolution steps.
Cons
  • Users find inadequate detection in Kaseya MDR, facing false positives and poor integration with popular security tools.
  • Users report numerous false positives and poor integration with popular security solutions, questioning Kaseya MDR's effectiveness.
  • Users find Kaseya MDR's limited integration with common security solutions reduces its overall effectiveness and protection.

What Are Recent G2 Reviews of Kaseya MDR (formerly RocketCyber)?

LevelBlue MDR / MXDR

LevelBlue’s Managed Extended Detection and Response (MXDR) service delivers continuous, expert-driven protection across networks, endpoints, identities, cloud apps, and email. Backed by a 24/7 SOC, LevelBlue helps organizations rapidly realize value from existing technology investments while reducing cyber risk in complex hybrid environments. Our seasoned security engineers provide co-management for your XDR and SIEM, ensuring both are expertly managed and optimized to stay ahead of evolving threats. LevelBlue empowers your team with proprietary threat intelligence, flexible integration with existing technologies, and measurable outcomes—strengthening enterprise security and partnering with you to minimize cyber risk. Recent LevelBlue Acquisitions: - Alert Logic is a LevelBlue Co. - Trustwave is a LevelBlue Co. - Cybereason is a LevelBlue Co.

Average Rating: 4.5/5.0

Total Reviews: 247

How Do G2 Users Rate LevelBlue MDR / MXDR?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.7/10 (Category avg: 9.1/10)
  • Automated remediation: 8.3/10 (Category avg: 8.7/10)
  • Automated investigation: 8.2/10 (Category avg: 8.9/10)

Who Is the Company Behind LevelBlue MDR / MXDR?

Who Uses This Product?

  • Who Uses This: Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Medium, 36% Large

What Do G2 Reviewers Say About LevelBlue MDR / MXDR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the informative and easy-to-navigate dashboard of LevelBlue MDR / MXDR, enhancing their overall experience.
  • Users value the deployment ease of LevelBlue MDR/MXDR, appreciating its simple installation and user-friendly dashboard.
  • Users find the easy installation of LevelBlue MDR/MXDR straightforward, facilitating a smooth deployment experience.
  • Users value the ability to meet compliance requirements effectively with LevelBlue MDR / MXDR's robust SOC services.
  • Users value the complete visibility into incidents, enabling detailed tracking and understanding of each event.
Cons
  • Users find the difficult navigation of the vulnerability list and reporting process challenging and frustrating.
  • Users find the inefficient alert system somewhat cumbersome, needing improvements for better user experience and responsiveness.
  • Users find the poor reporting of LevelBlue MDR/MXDR frustrating, as it complicates access to essential information.

What Are Recent G2 Reviews of LevelBlue MDR / MXDR?

What Are G2 Users Discussing About LevelBlue MDR / MXDR?

DefenseStorm

DefenseStorm is a comprehensive cybersecurity platform specifically designed for financial institutions, focusing on cyber risk assessment, governance, security, and fraud prevention. This integrated solution addresses the unique challenges that banks and other financial entities face in maintaining cyber risk readiness amidst a complex landscape of regulations and technological demands. The platform is tailored to meet the stringent requirements of the banking sector, making it a vital resource for organizations seeking to enhance their cybersecurity posture. DefenseStorm's intelligent data engine, known as GRID ACTIVE, plays a crucial role in this process by providing real-time access to critical threat data. This capability allows financial institutions to analyze and respond to potential threats swiftly, ensuring they remain vigilant against evolving cyber risks. Targeted at banks and financial service providers, DefenseStorm offers a range of use cases that are essential for maintaining compliance and safeguarding sensitive data. The platform not only helps institutions assess their current cyber risk levels but also provides governance tools that facilitate adherence to regulatory requirements. By integrating security measures with fraud detection capabilities, DefenseStorm enables organizations to create a robust defense against both internal and external threats. One of the standout features of DefenseStorm is its Cyber Threat Surveillance Operations (CTS Ops) team, which provides round-the-clock support. This managed service ensures that financial institutions have access to expert resources at all times, allowing them to leverage specialized knowledge and experience in combating cyber threats. The continuous monitoring and proactive threat management offered by the CTS Ops team enhance the overall security framework of the institution, providing peace of mind to stakeholders. Overall, DefenseStorm's unique focus on the banking sector, combined with its advanced data analytics and dedicated support services, positions it as a critical tool for financial institutions aiming to navigate the complexities of cybersecurity. By equipping organizations with the necessary tools and expertise, DefenseStorm helps them not only to meet regulatory obligations but also to foster a culture of security that is essential in today's digital landscape.

Average Rating: 4.8/5.0

Total Reviews: 30

How Do G2 Users Rate DefenseStorm?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.2/10 (Category avg: 9.1/10)
  • Automated remediation: 7.7/10 (Category avg: 8.7/10)
  • Automated investigation: 7.9/10 (Category avg: 8.9/10)

Who Is the Company Behind DefenseStorm?

  • Seller: DEFENSESTORM
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Alpharetta, Georgia
  • LinkedIn® Page: www.linkedin.com
    85 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Banking, Financial Services
  • Company Size: 80% Medium, 20% Small

What Do G2 Reviewers Say About DefenseStorm?

AI-generated summary from verified user reviews

Pros
  • Users commend the knowledgeable and helpful customer support of DefenseStorm, enhancing their cybersecurity experience significantly.
  • Users value the dedicated and knowledgeable team of DefenseStorm, enhancing security with 24/7 support and assistance.
  • Users find the ease of use of DefenseStorm makes implementing and monitoring cybersecurity effortless and efficient.
  • Users praise the knowledgeable and helpful staff of DefenseStorm, ensuring excellent support and seamless interactions.
  • Users value the 24/7 alert notifications from DefenseStorm, ensuring proactive responses to potential security issues.
Cons
  • Users face difficult navigation within DefenseStorm, making it hard to effectively utilize its features and dashboards.
  • Users suggest that training is required for effective use, with inadequate materials hindering user experience and reliance.
  • Users find the manual asset management process cumbersome and unreliable, despite appreciating other aspects of the product.
  • Users find executive reporting difficult due to complex dashboards, hindering effective interpretation for non-IT stakeholders.
  • Users find inadequate reporting in DefenseStorm, struggling to create clear executive summaries from complex dashboards.

What Are Recent G2 Reviews of DefenseStorm?

Guardz

Guardz is a unified cybersecurity platform specifically designed for Managed Service Providers (MSPs). This innovative solution consolidates essential security controls, identity threat detection and response (ITDR), endpoint protection (EDR), email security, user awareness training and phishing simulations, and Managed Detection and Response (MDR) into a single AI-native framework. The platform aims to enhance operational efficiency by streamlining security processes and providing a comprehensive approach to cybersecurity. Targeting MSPs, Guardz addresses the unique challenges these providers face in managing multiple security tools that often operate in silos. By adopting an identity-centric approach, Guardz connects various security vectors, effectively reducing the gaps that can leave organizations vulnerable. This layered and holistic view enables MSPs to respond to user risks in real time, ensuring that security measures are not only reactive but also proactive in safeguarding client environments. Key features of Guardz include its 24/7 AI and human-led Managed Detection and Response (MDR) services. The platform employs agentic AI to triage threats at machine speed, allowing for rapid identification and prioritization of potential security incidents. This automated triage process is complemented by expert analysts who validate findings, mitigate risks, and guide response actions. As a result, MSPs can offer scalable protection to their clients without the need to expand their workforce, making it a cost-effective solution for growing cybersecurity demands. Guardz stands out in the cybersecurity landscape by providing a unified platform that integrates various security functions into one cohesive system. This integration not only simplifies the management of security tools but also enhances the overall effectiveness of security measures. By leveraging AI-driven insights and human expertise, Guardz empowers MSPs to deliver robust cybersecurity solutions that adapt to the evolving threat landscape, ensuring their clients remain protected against emerging risks.

Average Rating: 4.6/5.0

Total Reviews: 126

How Do G2 Users Rate Guardz?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.0/10 (Category avg: 9.1/10)
  • Automated remediation: 8.9/10 (Category avg: 8.7/10)
  • Automated investigation: 8.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Guardz?

  • Seller: Guardz
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    160 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 78% Small, 18% Medium

What Do G2 Reviewers Say About Guardz?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Guardz, highlighting its straightforward navigation and centralized dashboard for managing security.
  • Users value the comprehensive security overview Guardz offers, seamlessly integrating threat detection and management across environments.
  • Users value the user-friendly dashboard and exceptional customer service of Guardz, enhancing their monitoring capabilities significantly.
  • Users highlight the easy setup of Guardz, allowing quick deployment and rapid access to security insights.
  • Users commend Guardz for its effective threat detection, ensuring security across client environments with minimal complexity.
Cons
  • Users note the limited features of Guardz when not using M365 or G-Suite, affecting functionality and depth.
  • Users experience integration issues with Guardz, as it lacks seamless connections with existing security tools.
  • Users note the lack of features for non-M365 or G-Suite clients, limiting essential functionalities like antivirus deployment.
  • Users note a lack of customization in Guardz, limiting flexibility in feature deployment and reporting options.
  • Users find the insufficient information in Guardz frustrating, as it complicates email management and user understanding.

What Are Recent G2 Reviews of Guardz?

Heimdal

Accommodate all your cybersecurity needs under one convenient roof with the Heimdal® Unified Cybersecurity Platform. Our cybersecurity solutions can be used as standalone products or integrated into one another as part of a cohesive and unified XDR platform. Whether you’re a reseller, distributor, MSSP, or an organization committed to bolstering your online security, we provide an array of cutting-edge products to make your mission smoother. Heimdal® is a fast-growing cybersecurity company focused on continuous technological innovation. Since its establishment in 2014 in Copenhagen, based on the winning idea of CTF World Champions, Heimdal has experienced spectacular growth by proactively building products that anticipate threatscape trends. The company offers a multi-layeredand unified security suite that combines threat prevention, patch and asset management, endpoint rights management, antivirus and mail security which together secure customers against cyberattacks and keep critical information and intellectual property safe. Heimdal has been recognized as a thought leader in the industry and has won multiple international awards both for its solutions and for its educational content creation. The Heimdal line of products currently consists of 10 products and 2 services. The former category encompasses DNS Security for Endpoints & Network, Patch & Asset Management, Privileged Access Management, Application Control, Next-Gen Endpoint Antivirus, Ransomware Encryption Protection, Email Security, Email Fraud Prevention, and Remote Desktop. The latter is represented by Endpoint Detection & Response, as well as eXtended Detection & Response, or EDR and XDR for short. Currently, Heimdal’s cybersecurity solutions are deployed in more than 45 countries and supported regionally from offices in 15+ countries, by 175+ highly qualified specialists. Heimdal is ISAE 3000 certified and secures more than 2 million endpoints for over 10,000 companies. The company supports its partners without concessions on the basis of predictability and scalability. The common goal is to create a sustainable ecosystem and a strategic partnership.

Average Rating: 4.5/5.0

Total Reviews: 85

How Do G2 Users Rate Heimdal?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 10.0/10 (Category avg: 9.1/10)
  • Automated remediation: 10.0/10 (Category avg: 8.7/10)
  • Automated investigation: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Heimdal?

  • Seller: Heimdal®
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Computer & Network Security, Construction
  • Company Size: 56% Medium, 29% Small

What Do G2 Reviewers Say About Heimdal?

AI-generated summary from verified user reviews

Pros
  • Users value the easy setup of Heimdal, enabling seamless deployment of tools across devices.
  • Users praise the seamless file transfer capabilities of Heimdal, enhancing efficiency and reliability across their systems.
  • Users praise Heimdal for its exceptional issue resolution and quick, professional support for effective problem-solving.
  • Users appreciate the reliable and effective patch management of Heimdal, ensuring smooth operation and timely updates.
  • Users value the reliable security solutions of Heimdal, enhanced by a user-friendly interface and excellent support.
Cons
  • Users find the interface complex, struggling with navigation and access to essential features in Heimdal.
  • Users find the admin portal complex and illogical, complicating navigation and access to essential features.
  • Users experience poor customer support initially, but find help improves over time with better product understanding.
  • Users find the poor interface design of Heimdal challenging, complicating navigation and access to essential features.
  • Users often face restart issues with Heimdal, leaving them feeling temporarily "unprotected" after scans.

What Are Recent G2 Reviews of Heimdal?

Blackpoint Cyber

Blackpoint Cyber is the forerunner in the managed detection and response space, leveraging our proprietary ecosystem to help our partners fight back and win against cyberthreats. We have served the community since 2014 and proudly continue to safeguard businesses around the world. We believe that no one should go alone into the unfair fight. At Blackpoint, our team strives to provide unified, 24/7 detection to help you take out your adversaries before they can even see us coming.

Average Rating: 4.7/5.0

Total Reviews: 257

How Do G2 Users Rate Blackpoint Cyber?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 9.4/10 (Category avg: 9.1/10)
  • Automated remediation: 9.0/10 (Category avg: 8.7/10)
  • Automated investigation: 9.2/10 (Category avg: 8.9/10)

Who Is the Company Behind Blackpoint Cyber?

Who Uses This Product?

  • Who Uses This: President, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 82% Small, 17% Medium

What Do G2 Reviewers Say About Blackpoint Cyber?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the quick and effective customer support from Blackpoint Cyber, enhancing their overall experience.
  • Users value the exceptional threat detection from Blackpoint Cyber, ensuring rapid response and effective remediation of security incidents.
  • Users find deployment quick and easy with Blackpoint Cyber, enhancing integration and overall user experience.
  • Users commend the quick and easy setup process of Blackpoint Cyber, enhancing their overall experience significantly.
  • Users value the responsiveness and support of the SOC team, praising their 24/7 protection and efficiency.
Cons
  • Users find the service expensive, making it less appealing for those seeking basic coverage or small scale solutions.
  • Users face integration issues with Blackpoint Cyber, lacking essential information and compatibility with other solutions.
  • Users find poor reporting capabilities hinder effective asset management and regulatory compliance across their client base.
  • Users find the portal issues challenging, as navigation is clunky and the UI lacks smoothness.
  • Users find the difficult navigation of Blackpoint Cyber challenging, complicating access to important information and settings.

What Are Recent G2 Reviews of Blackpoint Cyber?

What Are G2 Users Discussing About Blackpoint Cyber?

CYREBRO

CYREBRO is an AI-native Managed Detection and Response solution, providing the core foundation and capabilities of a state-level Security Operations Center delivered through its cloud-based, interactive SOC Platform. CYREBRO rapidly detects, analyzes, investigates and responds to cyber threats, for businesses of all sizes.

Average Rating: 4.4/5.0

Total Reviews: 129

How Do G2 Users Rate CYREBRO?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.5/10 (Category avg: 9.1/10)
  • Automated remediation: 6.7/10 (Category avg: 8.7/10)
  • Automated investigation: 7.9/10 (Category avg: 8.9/10)

Who Is the Company Behind CYREBRO?

  • Seller: CYREBRO
  • Year Founded: 2013
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 64% Medium, 25% Small

What Do G2 Reviewers Say About CYREBRO?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CYREBRO, enjoying straightforward navigation and quick access to critical investigations.
  • Users praise CYREBRO's highly responsive customer support, enhancing the overall experience and efficiency in issue resolution.
  • Users value the real-time alerts from CYREBRO, enhancing their ability to respond swiftly to cyber threats.
  • Users value the real-time alerts from CYREBRO, enhancing security and enabling quick, informed decision-making in threat management.
  • Users value the intuitive dashboard usability of CYREBRO for quick status visibility and efficient client monitoring.
Cons
  • Users report frequent update issues with CYREBRO, experiencing overwhelming alerts and integration difficulties during onboarding.
  • Users experience communication issues with CYREBRO, noting delays in support responses and vague initial ticket details.
  • Users experience poor customer support with delayed responses and vague details, impacting overall effectiveness and communication.
  • Users face dashboard issues with connectivity and limited features, complicating their overall experience with CYREBRO.
  • Users experience ineffective alerts due to overwhelming volume and vague details, impacting usability and clarity.

What Are Recent G2 Reviews of CYREBRO?

What Are G2 Users Discussing About CYREBRO?

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.3/10 (Category avg: 9.1/10)
  • Automated remediation: 5.4/10 (Category avg: 8.7/10)
  • Automated investigation: 6.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Blumira, facilitating quick detection and monitoring of security incidents.
  • Users value the outstanding customer support of Blumira, highlighting swift assistance and a seamless onboarding experience.
  • Users appreciate the easy implementation of Blumira Automated Detection & Response, enabling quick and efficient setup processes.
  • Users value the real-time alerting feature of Blumira, enhancing their security awareness and incident management.
  • Users value the real-time alerting of Blumira, as it effectively tracks security events in their MS 365 environment.
Cons
  • Users feel that the limited customization options hinder the product's potential and integration capabilities with other tools.
  • Users find the alert system's customization lacking, highlighting a need for improved log source comparisons and SIEM functionality.
  • Users find the pricing model expensive and inflexible, not meeting their budget or needs effectively.
  • Users find the faulty detection limitations frustrating, especially around custom rules and log visibility.
  • Users find the inefficient alert system lacking essential user details, complicating response strategies and false positive management.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

Adlumin

Adlumin, an N-able Company, provides enterprise-grade cybersecurity for organizations of all sizes through its innovative Security Operations as a Service platform. With an agnostic approach, the Adlumin platform seamlessly integrates with existing tech stacks, and its flexible management options enable it to be self-managed by an internal team, or fully managed by Adlumin experts. The Adlumin platform stops cyber threats early with deep learning models tailored to each environment. It maximizes resource efficiency by optimizing existing technology and streamlining workflows across teams. Adlumin transforms risk into resilience by identifying and addressing vulnerabilities, while cybersecurity experts proactively uncover and neutralize threats before they can do damage. Adlumin empowers organizations to take control of their digital security making advanced protection accessible to all.

Average Rating: 4.7/5.0

Total Reviews: 65

How Do G2 Users Rate Adlumin?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.3/10)
  • Proactive threat hunting: 8.8/10 (Category avg: 9.1/10)
  • Automated remediation: 8.7/10 (Category avg: 8.7/10)
  • Automated investigation: 8.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Adlumin?

  • Seller: N-able
  • Company Website:
  • HQ Location: Morrisville, North Carolina
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 56% Medium, 23% Small

What Do G2 Reviewers Say About Adlumin?

AI-generated summary from verified user reviews

Pros
  • Users value the detailed analytic reports from Adlumin, praising its reliability and ease of use.
  • Users value the detailed analytic reports from Adlumin, praising its reliability and user-friendly interface.
  • Users find Adlumin reliable and easy to use, particularly valuing the detailed analytic reports it provides.
  • Users appreciate the ease of management in Adlumin, finding it reliable and user-friendly for detailed reports.
  • Users find Adlumin's interface to be easy to use, with detailed analytics enhancing their experience.
Cons
  • Users feel that Adlumin's customer support could be better, indicating some room for improvement in service quality.

What Are Recent G2 Reviews of Adlumin?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated