Best Penetration Testing Tools

How Many Penetration Testing Tools Products Does G2 Track?

Total Products under this Category: 200

Category Stats (Nov 2026)

  • Average Rating: 4.64/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Penetration Testing Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 200+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

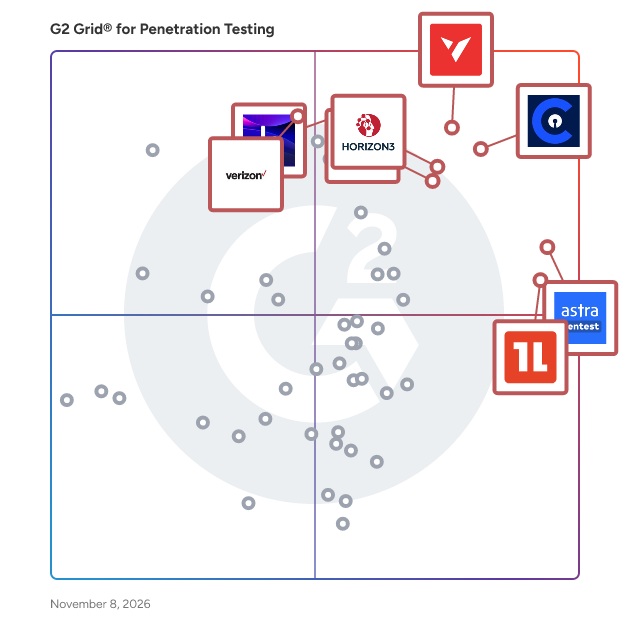
G2 Grid® for Penetration Testing Tools

G2 Grid® for Penetration Testing Tools plotting products by satisfaction and market presence

Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)

Cobalt

Cobalt is the pioneer in pentesting as a service (PTaaS) and a leader in continuous offensive security testing grounded in human expertise. The Cobalt Offensive Security Platform spans the full spectrum of offensive security, from targeted, human-led pentesting to high-frequency, AI-driven autonomous security testing. Only Cobalt brings together the four critical elements of modern offensive security: elite human expertise, a context-aware platform, AI-powered orchestration, and the industry's largest dataset of real-world pentest results. Thousands of customers and hundreds of partners rely on Cobalt and its global network of 500+ vetted security experts to continuously identify, prioritize, and remediate exploitable risk with the speed, flexibility, and precision today's organizations require.

Average Rating: 4.5/5.0

Total Reviews: 184

How Do G2 Users Rate Cobalt?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Cobalt?

  • Seller: Cobalt
  • Company Website:
  • Year Founded: 2013
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    597 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 52% Medium, 22% Small

What Do G2 Reviewers Say About Cobalt?

AI-generated summary from verified user reviews

Pros
  • Users value Cobalt's efficient pentesting process with organized dashboards and real-time collaboration, enhancing overall productivity.
  • Users value the quick and responsive customer support of Cobalt, enhancing their testing experience with excellent communication.
  • Users praise the ease of use of Cobalt, highlighting its friendly interface for non-technical resources.
  • Users value the excellent communication from Cobalt's support team, appreciating their responsiveness and timely updates.
  • Users value Cobalt’s real-time, detailed reporting, which provides immediate insights and a streamlined pentesting process.
Cons
  • Users find Cobalt to be expensive compared to competitors, raising concerns over its pricing structure and auto-renewal policy.
  • Users feel that Cobalt has a limited scope of audits, impacting efficiency and overall cybersecurity effectiveness.
  • Users find the lack of detail in test cases leads to confusion and a less satisfactory experience.
  • Users find Cobalt's pricing model confusing and prefer a more straightforward payment structure for services.
  • Users experience inaccuracy in audits, causing missed findings and inefficiencies in the pentesting process of Cobalt.

What Are Recent G2 Reviews of Cobalt?

What Are G2 Users Discussing About Cobalt?

vPenTest

Vonahi Security is building the future of offensive cybersecurity by delivering automated, high-quality penetration testing through its SaaS platform, vPenTest. Designed to replicate the tools, techniques, and methodologies of experienced consultants, vPenTest brings the benefits of manual network penetration testing into an easy-to-use, automated solution. Traditionally, penetration testing has been a manual, time consuming, and expensive process that many organizations only perform once or twice a year. This often leaves businesses exposed to emerging threats between assessments. vPenTest addresses this gap by offering fast, consistent, and on-demand testing that helps organizations evaluate their real-time cybersecurity risk more effectively. Powered by a proprietary framework that evolves through continuous research and real-world insights, vPenTest stays aligned with the latest attack techniques and industry best practices. The platform is backed by over 13 years of offensive security expertise, with the team holding certifications such as CISSP, OSCP, OSCE, CEH, and more. Their knowledge is built directly into the platform, ensuring each test is conducted with depth, consistency, and accuracy—without the delays or variability of manual testing.
 vPenTest enables organizations to run internal and external network penetration tests as often as needed monthly, quarterly, or prior to audits or insurance reviews. The automated reports provide actionable insights that make it easy to prioritize remediation and demonstrate progress toward compliance. Today, over 22,000 organizations rely on vPenTest to strengthen their security posture and reduce risk. This includes managed service providers, managed security service providers, financial institutions, compliance-driven organizations, and internal IT teams. Whether you're working to meet regulatory requirements, secure cyber insurance coverage, or proactively defend against evolving threats, vPenTest makes network penetration testing easy, affordable, and scalable.

Average Rating: 4.6/5.0

Total Reviews: 248

How Do G2 Users Rate vPenTest?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.0/10 (Category avg: 9.2/10)
  • Extensibility: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind vPenTest?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 69% Small, 24% Medium

What Do G2 Reviewers Say About vPenTest?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of vPenTest, noting its intuitive setup and clear, detailed results.
  • Users value the reporting quality of vPenTest for its comprehensive insights and compliance with stringent requirements.
  • Users commend vPenTest for its efficient penetration testing capabilities, allowing for rapid setup and user-friendly navigation.
  • Users find the setup process remarkably smooth, allowing for quick onboarding and immediate use without complications.
  • Users praise the ease of implementation of vPenTest, noting a smooth setup and seamless integration into workflows.
Cons
  • Users are frustrated by the limited scope of vPenTest, as it fails to address critical vulnerabilities effectively.
  • Users find the setup process complex, especially for multi-site configurations, creating challenges in deployment and integration.
  • Users note a lack of detail in vPenTest, making it difficult to understand results and streamline explanations.
  • Users express concerns about inadequate reporting, with repetitive findings and a need for more robust options.
  • Users find the monthly cost to be expensive, especially for small organizations with infrequent usage.

What Are Recent G2 Reviews of vPenTest?

Astra Pentest

Astra Security is a leading continuous penetration testing platform that combines AI-powered autonomous pentesting with certified expert-led assessments. Powered by Attack AI, trained on 6.8M+ security findings and insights from 5,000+ real-world pentests. Astra deploys intelligent agents that continuously discover, validate, prioritize, and help remediate vulnerabilities at scale. While AI handles speed and scale, Astra’s certified security experts focus on what automation alone cannot: complex business logic flaws, multi-step attack chains, advanced exploit paths, and emerging AI/LLM-specific threats. Built for modern engineering teams, Astra integrates directly into CI/CD workflows, enabling continuous security validation between releases instead of relying on outdated annual pentests. The platform delivers comprehensive Autonomous Pentest powered by AI agents, DAST vulnerability scanner and human-driven pentests across web apps, AI/LLMs, mobile apps, APIs, cloud infrastructure. Astra is CREST-accredited, CERT-IN empaneled, and a PCI ASV-certified vendor. Our team also led the development of the OWASP APTS framework, helping shape the industry standard for continuous security testing. Today, 1,500+ organizations across 70+ countries trust Astra Security, including Ford, Loom, CompTIA, Hitachi, HackerRank, and OLX.

Average Rating: 4.7/5.0

Total Reviews: 264

G2 Deal: For G2 users: 10% off across all pentest plans

Avail Astra Pentest at 10% off, our comprehensive pentest suite scans for 8000+ security tests including OWASP Top 10, SANS 25, known CVEs & security best practices. This offer is exclusive to G2 users!

Price: ~~$5999~~ → $5400

View this exclusive G2 deal

How Do G2 Users Rate Astra Pentest?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.0/10 (Category avg: 9.2/10)
  • Extensibility: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Astra Pentest?

  • Seller: ASTRA IT, Inc.
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Bengaluru, IN
  • LinkedIn® Page: www.linkedin.com
    154 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, CEO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 68% Small, 26% Medium

What Do G2 Reviewers Say About Astra Pentest?

AI-generated summary from verified user reviews

Pros
  • Users value the responsive customer support of Astra Pentest, facilitating a smooth and efficient penetration testing process.
  • Users appreciate Astra Pentest's thorough vulnerability detection, praising its clarity, responsiveness, and ease of management.
  • Users appreciate the ease of use of Astra Pentest, enjoying a smooth onboarding process and intuitive interface.
  • Users commend Astra Pentest for its thorough and responsive pentesting efficiency, simplifying vulnerability management with clear guidance.
  • Users value Astra Pentest's thorough vulnerability identification, enjoying clear findings and effective collaboration for easy remediation.
Cons
  • Users express frustration with poor customer support, highlighting delays and lack of transparency in tracking issues.
  • Users note a poor interface design in Astra Pentest, making usability and navigation more challenging than necessary.
  • Users often face slow performance issues, particularly with report speed and initial setup complications during pentesting.
  • Users note that the UX could be improved, particularly regarding the interface's intuitiveness and false positives during scans.
  • Users experience false positives with Astra Pentest, leading to additional clarification and verification time.

What Are Recent G2 Reviews of Astra Pentest?

What Are G2 Users Discussing About Astra Pentest?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

NodeZero from Horizon3

Horizon3's NodeZero® Proactive Security Platform shifts the advantage from attackers to defenders by helping organizations fight AI with AI. It autonomously tests defenses at machine speed, safely uncovering and prioritizing exploitable attack paths across on-premises and virtual infrastructure, cloud and hybrid environments, identity systems, Kubernetes, data infrastructure, APIs, and external assets. NodeZero reveals risks beyond known CVEs, including compromised credentials, exposed data, misconfigurations, weak controls, and risky policies. By safely chaining weaknesses as an attacker would, it shows what can be reached and the potential impact. Teams receive clear remediation guidance, then verify that fixes work, turning security testing into a continuous Hack, Fix, Verify, Repeat loop. Reports provide visibility into test actions, exploit chains, affected assets, and verified remediations, giving teams measurable proof of progress, audit-ready evidence, and greater confidence in their resilience.

Average Rating: 4.7/5.0

Total Reviews: 50

How Do G2 Users Rate NodeZero from Horizon3?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.7/10 (Category avg: 9.2/10)
  • Extensibility: 9.8/10 (Category avg: 8.8/10)

Who Is the Company Behind NodeZero from Horizon3?

  • Seller: Horizon3.ai
  • Company Website:
  • Year Founded: 2019
  • HQ Location: San Francisco, US
  • LinkedIn® Page: linkedin.com
    548 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 43% Medium, 27% Small

What Do G2 Reviewers Say About NodeZero from Horizon3?

AI-generated summary from verified user reviews

Pros
  • Users praise the intuitive vulnerability detection of NodeZero, facilitating easy integration and thorough cybersecurity assessments.
  • Users appreciate the intuitive communication of NodeZero, making it accessible and effective for both technical and nontechnical teams.
  • Users highlight the intuitive interface and thorough capabilities of NodeZero, making it essential for effective cybersecurity.
  • Users value the ease of implementation of NodeZero, finding it simple for both technical and nontechnical staff.
  • Users appreciate the easy integrations of NodeZero, enabling seamless implementation for both technical and non-technical staff.
Cons
  • Users note that the inadequate reporting in NodeZero makes it hard to identify specific machine outcomes.
  • Users find the lack of detailed reporting on machine success and failure a significant drawback of NodeZero.

What Are Recent G2 Reviews of NodeZero from Horizon3?

Oneleet

Oneleet is the all-in-one security and compliance platform that gets companies genuinely secure while achieving SOC 2, ISO 27001, HIPAA and other compliance certifications faster than traditional approaches. Unlike compliance platforms that focus on checkbox evidence collection, Oneleet implements real security first. Compliance follows automatically as a natural outcome of effective cybersecurity, not as a separate goal. Most companies face a false choice: painful but effective security, or painless but ineffective compliance theater. Traditional compliance platforms require juggling multiple vendors, managing fragmented tools, spending months with consultants, and doing manual evidence collection to achieve a certificate that doesn't actually make you secure. Oneleet consolidates what previously required half a dozen vendors into one integrated platform: penetration testing by real security experts (not just vulnerability scans), code scanning with SAST and DAST, cloud security posture management, attack surface monitoring, mobile device management, security training and awareness, policy generation and management, and continuous compliance monitoring. Because we build everything ourselves and control the entire stack, we deploy comprehensive security with a click. No blind spots. No integration gaps. No vendor sprawl. We guarantee audit outcomes because our standards are higher than auditors' standards. We use AI extensively but responsibly, automating threat modeling and risk assessments while keeping humans in the loop to ensure quality. Clients never see AI hallucinations. We take full responsibility for the entire security journey, from initial setup through audit completion and continuous monitoring. Companies achieve compliance readiness faster with Oneleet, not by doing less, but by making real security easier. We ship all the tools you would normally spend weeks or months setting up and adopting. Our customers regularly win deals they previously lost due to inadequate security postures. Oneleet is the fastest growing compliance company in the sector. A large number of Oneleet's newer clients come from platforms like Vanta and Drata. With Oneleet's all-in-one bundle pricing its ROI is significantly higher than that of Vanta, Drata and Delve. Companies that switch from Vanta, Drata, or Delve to Oneleet report faster audits, higher approval rates, and less manual effort. Vanta and Drata rely heavily on manual evidence collection and vendor integrations, creating delays and gaps. Delve emphasizes AI automation but often sacrifices accuracy—its generated outputs are frequently rejected or require manual fixes. Oneleet achieves both precision and speed by combining full-stack automation with expert oversight, producing the industry’s lowest audit-rejection rate and the fastest path to verified security. Oneleet serves SMBs and growth-stage companies that need compliance certifications to close enterprise deals, but want to be genuinely secure, not just certified on paper. Founded by professional penetration testers who spent over a decade breaching Fortune 500s and startups, we built Oneleet to end the disconnect between compliance and security.

Average Rating: 4.9/5.0

Total Reviews: 140

How Do G2 Users Rate Oneleet?

  • Performance and Reliability: 10.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Oneleet?

  • Seller: Oneleet
  • Year Founded: 2022
  • HQ Location: Atlanta, US
  • LinkedIn® Page: www.linkedin.com
    49 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Engineer
  • Top Industries: Computer Software, Medical Devices
  • Company Size: 16% Small, 11% Medium

What Do G2 Reviewers Say About Oneleet?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous security monitoring of Oneleet, enhancing compliance and reducing stress in audits.
  • Users value the compliance facilitation of Oneleet, enhancing documentation management for ISO 27001 certification during sales cycles.
  • Users find Oneleet's platform to have exceptional ease of use, simplifying compliance and providing clear support throughout.
  • Users value the quick and expert responses from Oneleet, feeling supported like having a senior colleague available.
  • Users value the effective compliance management capabilities of Oneleet, simplifying processes and ensuring thoroughness across multiple frameworks.
Cons
  • Users experience integration issues with Oneleet, affecting connections with various third-party applications.
  • Users find the limited customization options of Oneleet restrictive, desiring quicker integration rollouts.
  • Users find the limited integrations of Oneleet restrictive, missing out on essential connections for enhanced functionality.
  • Users find a lack of integration with smaller platforms, limiting Oneleet's overall effectiveness for their needs.
  • Users feel the lack of customization in reports limits their ability to tailor the product to their needs.

What Are Recent G2 Reviews of Oneleet?

Pentera

Pentera is the category leader for Automated Security Validation, allowing every organization to test with ease the integrity of all cybersecurity layers, unfolding true, current security exposures at any moment, at any scale. Thousands of security professionals and service providers around the world use Pentera to guide remediation and close security gaps before they are exploited. Its customers include Casey's General Stores, Emeria, LuLu International Exchange, IP Telecom PT, BrewDog, City National Bank, Schmitz Cargobull, and MBC Group. Pentera is backed by leading investors such as K1 Investment Management, Insight Partners, Blackstone, Evolution Equity Partners, and AWZ. Visit https://pentera.io for more information.

Average Rating: 4.6/5.0

Total Reviews: 195

How Do G2 Users Rate Pentera?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.7/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.7/10 (Category avg: 9.2/10)
  • Extensibility: 7.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Pentera?

  • Seller: Pentera
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    460 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Government Administration, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About Pentera?

AI-generated summary from verified user reviews

Pros
  • Users love the user-friendly UI of Pentera, which simplifies penetration testing and enhances overall efficiency.
  • Users value the effective vulnerability identification and remediation suggestions, enhancing their overall security posture.
  • Users appreciate the fully automated features of Pentera, noting its quick implementation and user-friendly interface.
  • Users value the responsive customer support of Pentera, enhancing overall satisfaction and efficiency in vulnerability management.
  • Users value the realistic testing capabilities of Pentera, enhancing company network security and response effectiveness.
Cons
  • Users find the reporting inadequate, lacking detail for enterprise-scale insights and missing multilingual support.
  • Users are disappointed with the lack of a robust RBAC system for effective user access control in Pentera.
  • Users desire improvements in handling false positives, but overall satisfaction remains high with current functionalities.
  • Users note that reporting lacks robustness, especially for enterprise-level insights and multilingual support.
  • Users express concerns about the missing features, such as insufficient vulnerabilities, limited RBAC, and lack of translation.

What Are Recent G2 Reviews of Pentera?

H1 Platform

HackerOne is a global leader in Continuous Threat Exposure Management (CTEM) and the only solution provider that pairs the simultaneous trust of the Fortune 500 and the world's largest community of security researchers to secure the AI-native enterprise. The H1 Platform unites agentic AI solutions with security researchers ingenuity to continuously discover, validate, prioritize, and remediate exposures across code, cloud, and AI systems. Through solutions like bug bounty, vulnerability disclosure, agentic pentesting, AI red teaming, and code security, HackerOne delivers measurable, continuous reduction of cyber risk for enterprises. Industry leaders, including Anthropic, Crypto.com, General Motors, Goldman Sachs, Lufthansa, Uber, UK Ministry of Defence, and the U.S. Department of Defense, trust HackerOne to safeguard their digital ecosystems. HackerOne was recognized in Gartner’s Emerging Tech Impact Radar: AI Cybersecurity Ecosystem report for its leadership in AI Security Testing.

Average Rating: 4.5/5.0

Total Reviews: 107

How Do G2 Users Rate H1 Platform?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.3/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind H1 Platform?

  • Seller: HackerOne
  • Company Website:
  • Year Founded: 2012
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    7,090 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Large, 34% Medium

What Do G2 Reviewers Say About H1 Platform?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of H1 Platform, making it simple to manage and track bounty programs effectively.
  • Users highlight the helpful customer service of HackerOne, ensuring effective assistance and smooth platform navigation.
  • Users value the seamless collaboration facilitated by H1 Platform, enhancing communication with security researchers and team members.
  • Users value the enhanced security protection of H1 Platform, facilitating proactive vulnerability management and team collaboration.
  • Users value the exceptional customer support of H1 Platform, enhancing their overall experience and program management.
Cons
  • Users find the complexity issues in triaging and credentials management to be a challenge, impacting overall efficiency.
  • Users note the expensive pricing of H1 Platform, which may challenge smaller organizations despite its value.
  • Users face time management challenges with inconsistent triage speed and quality, impacting overall efficiency on the H1 Platform.
  • Users experience poor customer support with long ticket resolutions and unresolved queries impacting their overall satisfaction.
  • Users find the poor interface design of H1 Platform confusing and difficult to navigate, often missing reports.

What Are Recent G2 Reviews of H1 Platform?

What Are G2 Users Discussing About H1 Platform?

Verizon Penetration Testing

Penetration testing is an important part of managing risk. It helps you probe for cyber vulnerabilities so you can put resources where theyre needed most. Assess your risks and measure the dangers, then use real-world scenarios to help you strengthen your security.

Average Rating: 4.6/5.0

Total Reviews: 15

How Do G2 Users Rate Verizon Penetration Testing?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.4/10 (Category avg: 9.2/10)
  • Extensibility: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Verizon Penetration Testing?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 58% Small, 21% Large

What Are Recent G2 Reviews of Verizon Penetration Testing?

What Are G2 Users Discussing About Verizon Penetration Testing?

Bugcrowd

Bugcrowd frees organizations with a low tolerance for risk from chronic talent shortages, noisy tools that breed false positives, and the fear of critical hidden or emerging vulnerabilities. Our SaaS platform provides access to the unlimited capacity and skills of the global ethical hacker/pentester community for deeper, proactive risk reduction and faster regulatory compliance. With 12+ years of experience and 1200+ customers in every industry (including OpenAI, National Australia Bank, Indeed, USAA, Twilio, and CISA), we know what long-term with crowdsourced security looks like.

Average Rating: 4.3/5.0

Total Reviews: 60

How Do G2 Users Rate Bugcrowd?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.5/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.2/10 (Category avg: 8.8/10)

Who Is the Company Behind Bugcrowd?

  • Seller: Bugcrowd
  • Year Founded: 2012
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    3,858 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 34% Large, 33% Small

What Do G2 Reviewers Say About Bugcrowd?

AI-generated summary from verified user reviews

Pros
  • Users value the high-quality reporting in Bugcrowd, enabling efficient tracking of vulnerabilities and enhanced security posture.
  • Users find Bugcrowd's platform to be easy to use, enhancing their efficiency and overall experience in vulnerability testing.
  • Users value the responsive customer support from Bugcrowd, enhancing their experience with timely assistance and solutions.
  • Users commend Bugcrowd for its consistent and transparent communication, enhancing the overall efficiency of their research experience.
  • Users value the diverse and skilled security research community in Bugcrowd, ensuring high-quality vulnerability findings.
Cons
  • Users express frustration with poor customer support, noting slow response times and inconsistent triaging processes.
  • Users experience slow performance in triage and report validation, leading to frustration and delays in updates.
  • Users experience slow response times and inconsistent triaging, which can lead to frustration and lack of clarity.
  • Users experience inadequate reporting with slow validations and delays, impacting timely resolutions and overall efficiency.
  • Users find the learning curve steep with Bugcrowd, making it challenging for beginners to navigate effectively.

What Are Recent G2 Reviews of Bugcrowd?

Burp Suite

Burp Suite is a complete ecosystem for web application and API security testing, combining two products: Burp Suite DAST - a best-of-breed, precision DAST solution that automates runtime testing, and Burp Suite Professional - the industry-standard toolkit for manual penetration testing. Developed by PortSwigger, more than 85,000 security professionals rely on Burp Suite to find, verify, and understand vulnerabilities across complex modern web applications. Burp Suite DAST is PortSwigger’s enterprise dynamic application security testing (DAST) solution, purpose-built for continuous, automated scanning of web applications and APIs. Unlike many DAST solutions, which are part of a wider AST offering, Burp Suite DAST is not a bolt-on tool - instead it’s precision-built from over 20 years of dynamic testing experience. Burp Suite DAST reveals the runtime issues that static analysis tools miss, such as authentication flaws, configuration drift, and chained vulnerabilities. Built on the same proprietary scanning engine that powers Burp Suite Professional, it delivers precise, low-noise results that security teams trust. Key capabilities of Burp Suite DAST include: Continuous, automated scanning of web applications and APIs, integration with CI/CD pipelines and vulnerability management tools, flexible deployment across cloud, and on-premise environments, shared scanning logic and configurations between automated and manual testing, accurate, low-noise detection informed by PortSwigger Research. Burp Suite Professional complements DAST with deep manual testing capability. It’s the industry-standard toolkit for penetration testers, consultants, and AppSec engineers who need complete insight and flexibility when validating or exploring vulnerabilities. Findings discovered by DAST can be investigated and verified in Burp Suite Professional, ensuring every result is accurate, contextual, and actionable. Together, Burp Suite DAST and Burp Suite Professional create a unified ecosystem that delivers automation at breadth and manual depth where it counts. Burp Suite is built for AppSec teams who need scalable, trustworthy coverage across web and API environments, enabling a seamless handoff between automated and manual testing.

Average Rating: 4.8/5.0

Total Reviews: 134

How Do G2 Users Rate Burp Suite?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.8/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Burp Suite?

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 41% Medium, 33% Small

What Do G2 Reviewers Say About Burp Suite?

AI-generated summary from verified user reviews

Pros
  • Users enjoy the user-friendly interface of Burp Suite, making navigation and analysis straightforward for all skill levels.
  • Users highlight the user-friendly interface of Burp Suite, making it easy to navigate and utilize effectively.
  • Users value the deep automation and manual testing capabilities of Burp Suite for effective security assessments.
  • Users appreciate the control and visibility Burp Suite offers, with powerful tools for effective web application testing.
  • Users praise Burp Suite for its clear, user-friendly interface that simplifies web application penetration testing for both beginners and experts.
Cons
  • Users find Burp Suite to be expensive, particularly for the professional version, which may limit accessibility for some users.
  • Users report slow performance with Burp Suite, particularly on lower-end systems during extensive scanning tasks.
  • Users find the steep learning curve of Burp Suite challenging, especially beginners navigating its complex features and tools.
  • Users find the steep learning curve in Burp Suite challenging, particularly for beginners adjusting to its complex setup.
  • Users find the limited customization in Burp Suite restricts exploration, especially for beginners and independent learners.

What Are Recent G2 Reviews of Burp Suite?

What Are G2 Users Discussing About Burp Suite?

NetSPI

NetSPI PTaaS is a type of penetration testing as a service (PTaaS) solution designed to help organizations identify and remediate vulnerabilities within their systems, applications, and networks. This service utilizes a combination of skilled professionals, established processes, and advanced AI technology to provide contextualized security outcomes in real time, all accessible through a unified platform. By addressing the limitations of traditional penetration testing methods, NetSPI PTaaS offers a more efficient and comprehensive approach to security assessments. This service is targeted at businesses of all sizes, from startups to large enterprises, making it particularly beneficial for security teams looking to enhance their vulnerability management strategies. NetSPI PTaaS caters to a variety of use cases, including application security assessments, infrastructure testing, and evaluations of emerging technologies such as artificial intelligence. With over 50 different types of penetration tests available, including traditional point in time testing and our continuous offerings, organizations can customize their security evaluations to meet specific needs, ensuring thorough coverage across all potential attack surfaces. A key feature of NetSPI PTaaS is its commitment to delivering real-time findings through a single platform. This capability allows security teams to receive immediate insights into vulnerabilities, enabling them to act swiftly to mitigate risks based on role and priority, managing testing in just a few clicks. The platform's integration capabilities enhance its usability, allowing organizations to seamlessly incorporate findings into their existing security workflows. This streamlined approach not only saves time but also ensures that remediation efforts are based on high-fidelity, manually validated findings, thus improving overall security effectiveness. The expertise of NetSPI's team of over 350 in-house security professionals is another significant differentiator. Their extensive experience and knowledge in the field of cybersecurity ensure that the testing methodologies employed are rigorous and consistent, uncovering vulnerabilities, exposures, and misconfigurations that may be overlooked by other solutions. This white-glove approach to penetration testing emphasizes the importance of manual validation, providing organizations with reliable and actionable insights that can significantly enhance their security posture. NetSPI PTaaS stands out in the realm of penetration testing services by combining expert human analysis with advanced AI technology, delivering timely and accurate results. This empowers organizations to strengthen their defenses against evolving cyber threats, ensuring that they remain resilient in an increasingly complex security landscape.

Average Rating: 4.9/5.0

Total Reviews: 19

How Do G2 Users Rate NetSPI?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.8/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 9.5/10 (Category avg: 8.8/10)

Who Is the Company Behind NetSPI?

  • Seller: NetSPI
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Minneapolis, MN
  • LinkedIn® Page: www.linkedin.com
    595 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 42% Medium, 37% Large

What Do G2 Reviewers Say About NetSPI?

AI-generated summary from verified user reviews

Pros
  • Users commend NetSPI for their expertise and professionalism, delivering effective engagement and excellent communication throughout the process.
  • Users commend the exceptional quality of the NetSPI team, appreciating their skills and effective communication throughout engagements.
  • Users value the effective communication with NetSPI, enjoying real-time updates and easy access to project history.
  • Users praise the ease of use of NetSPI, highlighting its intuitive interface and effective communication tools.
  • Users praise the outstanding service quality of NetSPI, highlighting their exceptional team and effective tools for engagement.
Cons
  • Users find that difficult navigation within NetSPI's interface hampers their overall experience and efficiency.
  • Users reported false positives in the NetSPI vulnerability report, causing confusion regarding affected devices.
  • Users find the vulnerability report unclear, as it lacks details on which devices are affected by vulnerabilities.
  • Users report a lack of detail in vulnerability reports, making it unclear which devices are affected.
  • Users noted a lack of information regarding vulnerabilities on specific devices in the NetSPI reports.

What Are Recent G2 Reviews of NetSPI?

YesWeHack

YesWeHack is a leading Offensive Security and Exposure Management platform delivering integrated, API-based solutions to secure organisations’ growing attack surfaces. Its human-in-the-loop model combines Bug Bounty (leveraging a global community of 160,000+ skilled ethical hackers), Agentic Pentest, Exposure Management, and unified Vulnerability Management to deliver agile, exhaustive security testing at scale. Customers include Louis Vuitton, Ferrero, the European Commission, Tencent and L’Oréal Groupe. ISO 27001-certified, CREST-accredited, and EU-hosted with full GDPR compliance.

Average Rating: 4.8/5.0

Total Reviews: 33

How Do G2 Users Rate YesWeHack?

  • Has the product been a good partner in doing business?: 9.9/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.9/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.4/10 (Category avg: 9.2/10)
  • Extensibility: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind YesWeHack?

  • Seller: YesWeHack
  • Year Founded: 2015
  • HQ Location: Paris, France
  • LinkedIn® Page: www.linkedin.com
    786 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 42% Large, 36% Small

What Do G2 Reviewers Say About YesWeHack?

AI-generated summary from verified user reviews

Pros
  • Users celebrate the user-friendly platform of YesWeHack, simplifying security processes while enhancing vulnerability detection.
  • Users commend the superb customer support of YesWeHack, noting their effectiveness and responsiveness in resolving issues promptly.
  • Users appreciate the excellent support team and user-friendly platform of YesWeHack, enhancing their security experience.
  • Users appreciate the high reporting quality of YesWeHack, enhancing trust and identifying vulnerabilities effectively.
  • Users value the high quality of the platform and the exceptional support from YesWeHack's dedicated teams.
Cons
  • Users find the pricing steep, which makes YesWeHack less accessible for smaller organizations.
  • Users find the poor interface design limits tracking capabilities, impacting overall user experience and satisfaction.
  • Users find the limited scope of YesWeHack inadequate for managing a high number of programs effectively.
  • Users note that the missing tracking features hinder YesWeHack's interface, though the team is responsive to feedback.
  • Users find the pricing steep for smaller organizations, limiting accessibility for a broader audience.

What Are Recent G2 Reviews of YesWeHack?

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 223

How Do G2 Users Rate Intruder?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.6/10 (Category avg: 9.2/10)
  • Extensibility: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users find Intruder's ease of use essential, appreciating its intuitive setup and minimal maintenance requirements.
  • Users value the easy setup and effective vulnerability detection of Intruder, enhancing their network security swiftly.
  • Users commend Intruder's responsive and friendly customer support, appreciating their fast and effective communication for assistance.
  • Users praise Intruder's intuitive user interface, which simplifies navigation and integrates seamlessly with existing tools.
  • Users appreciate the clarity and prioritisation of Intruder's vulnerability findings, enabling effective and meaningful action against risks.
Cons
  • Users find the expensive pricing a barrier for smaller implementations and prefer a more competitive option.
  • Users are frustrated with the slow scanning speed of Intruder, leading to missed vulnerabilities and increased manual work.
  • Users find licensing issues complicated, with unclear costs and separate application and infrastructure licenses adding to confusion.
  • Users report experiencing false positives with Intruder, leading to extra manual work and missed vulnerabilities.
  • Users find limited features in Intruder, particularly regarding licensing clarity and advanced reporting options.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

Synack

Synack is a continuous penetration testing platform that combines agentic AI with a global network of vetted security researchers to uncover real, exploitable vulnerabilities across the entire attack surface. Most organizations test only a fraction of what matters. Synack closes that coverage gap—using AI to scale discovery and human expertise to validate real risk. The platform enables enterprises to move from periodic testing to continuous security validation across web applications, APIs, cloud, and infrastructure—prioritizing findings based on what is actually exploitable, not just detected. Synack supports penetration testing, continuous security testing, vulnerability management, and attack surface management in dynamic, cloud-based, and hybrid environments. Founded by former NSA professionals, Synack supports enterprise and public sector organizations where security, compliance, and risk management are mission-critical.

Average Rating: 4.8/5.0

Total Reviews: 21

How Do G2 Users Rate Synack?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Synack?

  • Seller: NetSPI
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Minneapolis, MN
  • LinkedIn® Page: www.linkedin.com
    595 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 71% Large, 14% Medium

What Are Recent G2 Reviews of Synack?

What Are G2 Users Discussing About Synack?

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.5/5.0

Total Reviews: 272

How Do G2 Users Rate Aikido Security?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 10.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated March 5, 2025