Top Free Penetration Testing Tools

How Many Penetration Testing Tools Products Does G2 Track?

Total Products under this Category: 196

Category Stats (Nov 2026)

  • Average Rating: 4.64/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Penetration Testing Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 196+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

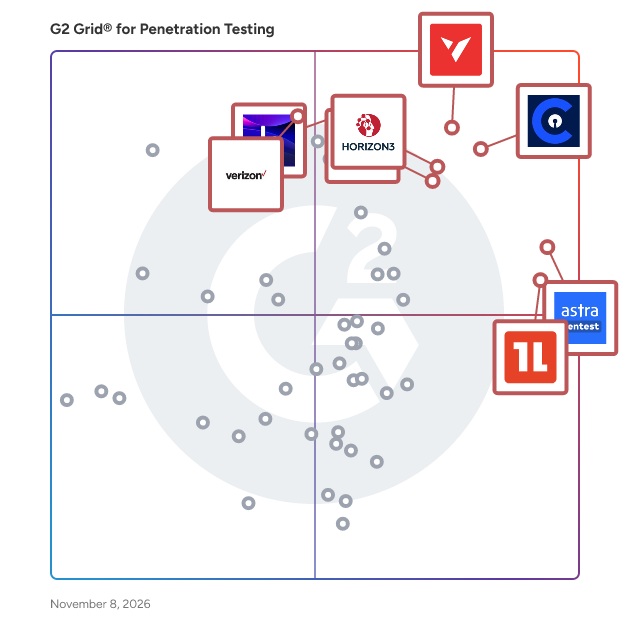
G2 Grid® for Penetration Testing Tools

G2 Grid® for Penetration Testing Tools plotting products by satisfaction and market presence

Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)

vPenTest

Vonahi Security is building the future of offensive cybersecurity by delivering automated, high-quality penetration testing through its SaaS platform, vPenTest. Designed to replicate the tools, techniques, and methodologies of experienced consultants, vPenTest brings the benefits of manual network penetration testing into an easy-to-use, automated solution. Traditionally, penetration testing has been a manual, time consuming, and expensive process that many organizations only perform once or twice a year. This often leaves businesses exposed to emerging threats between assessments. vPenTest addresses this gap by offering fast, consistent, and on-demand testing that helps organizations evaluate their real-time cybersecurity risk more effectively. Powered by a proprietary framework that evolves through continuous research and real-world insights, vPenTest stays aligned with the latest attack techniques and industry best practices. The platform is backed by over 13 years of offensive security expertise, with the team holding certifications such as CISSP, OSCP, OSCE, CEH, and more. Their knowledge is built directly into the platform, ensuring each test is conducted with depth, consistency, and accuracy—without the delays or variability of manual testing.
 vPenTest enables organizations to run internal and external network penetration tests as often as needed monthly, quarterly, or prior to audits or insurance reviews. The automated reports provide actionable insights that make it easy to prioritize remediation and demonstrate progress toward compliance. Today, over 22,000 organizations rely on vPenTest to strengthen their security posture and reduce risk. This includes managed service providers, managed security service providers, financial institutions, compliance-driven organizations, and internal IT teams. Whether you're working to meet regulatory requirements, secure cyber insurance coverage, or proactively defend against evolving threats, vPenTest makes network penetration testing easy, affordable, and scalable.

Average Rating: 4.6/5.0

Total Reviews: 248

How Do G2 Users Rate vPenTest?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.0/10 (Category avg: 9.2/10)
  • Extensibility: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind vPenTest?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 69% Small, 24% Medium

What Do G2 Reviewers Say About vPenTest?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of vPenTest, noting its intuitive setup and clear, detailed results.
  • Users value the reporting quality of vPenTest for its comprehensive insights and compliance with stringent requirements.
  • Users commend vPenTest for its efficient penetration testing capabilities, allowing for rapid setup and user-friendly navigation.
  • Users find the setup process remarkably smooth, allowing for quick onboarding and immediate use without complications.
  • Users praise the ease of implementation of vPenTest, noting a smooth setup and seamless integration into workflows.
Cons
  • Users are frustrated by the limited scope of vPenTest, as it fails to address critical vulnerabilities effectively.
  • Users find the setup process complex, especially for multi-site configurations, creating challenges in deployment and integration.
  • Users note a lack of detail in vPenTest, making it difficult to understand results and streamline explanations.
  • Users express concerns about inadequate reporting, with repetitive findings and a need for more robust options.
  • Users find the monthly cost to be expensive, especially for small organizations with infrequent usage.

What Are Recent G2 Reviews of vPenTest?

Astra Pentest

Astra Security is a leading continuous penetration testing platform that combines AI-powered autonomous pentesting with certified expert-led assessments. Powered by Attack AI, trained on 6.8M+ security findings and insights from 5,000+ real-world pentests. Astra deploys intelligent agents that continuously discover, validate, prioritize, and help remediate vulnerabilities at scale. While AI handles speed and scale, Astra’s certified security experts focus on what automation alone cannot: complex business logic flaws, multi-step attack chains, advanced exploit paths, and emerging AI/LLM-specific threats. Built for modern engineering teams, Astra integrates directly into CI/CD workflows, enabling continuous security validation between releases instead of relying on outdated annual pentests. The platform delivers comprehensive Autonomous Pentest powered by AI agents, DAST vulnerability scanner and human-driven pentests across web apps, AI/LLMs, mobile apps, APIs, cloud infrastructure. Astra is CREST-accredited, CERT-IN empaneled, and a PCI ASV-certified vendor. Our team also led the development of the OWASP APTS framework, helping shape the industry standard for continuous security testing. Today, 1,500+ organizations across 70+ countries trust Astra Security, including Ford, Loom, CompTIA, Hitachi, HackerRank, and OLX.

Average Rating: 4.7/5.0

Total Reviews: 264

G2 Deal: For G2 users: 10% off across all pentest plans

Avail Astra Pentest at 10% off, our comprehensive pentest suite scans for 8000+ security tests including OWASP Top 10, SANS 25, known CVEs & security best practices. This offer is exclusive to G2 users!

Price: ~~$5999~~ → $5400

View this exclusive G2 deal

How Do G2 Users Rate Astra Pentest?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.0/10 (Category avg: 9.2/10)
  • Extensibility: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Astra Pentest?

  • Seller: ASTRA IT, Inc.
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Bengaluru, IN
  • LinkedIn® Page: www.linkedin.com
    154 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, CEO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 68% Small, 26% Medium

What Do G2 Reviewers Say About Astra Pentest?

AI-generated summary from verified user reviews

Pros
  • Users value the responsive customer support of Astra Pentest, facilitating a smooth and efficient penetration testing process.
  • Users appreciate Astra Pentest's thorough vulnerability detection, praising its clarity, responsiveness, and ease of management.
  • Users appreciate the ease of use of Astra Pentest, enjoying a smooth onboarding process and intuitive interface.
  • Users commend Astra Pentest for its thorough and responsive pentesting efficiency, simplifying vulnerability management with clear guidance.
  • Users value Astra Pentest's thorough vulnerability identification, enjoying clear findings and effective collaboration for easy remediation.
Cons
  • Users express frustration with poor customer support, highlighting delays and lack of transparency in tracking issues.
  • Users note a poor interface design in Astra Pentest, making usability and navigation more challenging than necessary.
  • Users often face slow performance issues, particularly with report speed and initial setup complications during pentesting.
  • Users note that the UX could be improved, particularly regarding the interface's intuitiveness and false positives during scans.
  • Users experience false positives with Astra Pentest, leading to additional clarification and verification time.

What Are Recent G2 Reviews of Astra Pentest?

What Are G2 Users Discussing About Astra Pentest?

NodeZero from Horizon3

Horizon3's NodeZero® Proactive Security Platform shifts the advantage from attackers to defenders by helping organizations fight AI with AI. It autonomously tests defenses at machine speed, safely uncovering and prioritizing exploitable attack paths across on-premises and virtual infrastructure, cloud and hybrid environments, identity systems, Kubernetes, data infrastructure, APIs, and external assets. NodeZero reveals risks beyond known CVEs, including compromised credentials, exposed data, misconfigurations, weak controls, and risky policies. By safely chaining weaknesses as an attacker would, it shows what can be reached and the potential impact. Teams receive clear remediation guidance, then verify that fixes work, turning security testing into a continuous Hack, Fix, Verify, Repeat loop. Reports provide visibility into test actions, exploit chains, affected assets, and verified remediations, giving teams measurable proof of progress, audit-ready evidence, and greater confidence in their resilience.

Average Rating: 4.7/5.0

Total Reviews: 50

How Do G2 Users Rate NodeZero from Horizon3?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.7/10 (Category avg: 9.2/10)
  • Extensibility: 9.8/10 (Category avg: 8.8/10)

Who Is the Company Behind NodeZero from Horizon3?

  • Seller: Horizon3.ai
  • Company Website:
  • Year Founded: 2019
  • HQ Location: San Francisco, US
  • LinkedIn® Page: linkedin.com
    548 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 44% Medium, 26% Large

What Do G2 Reviewers Say About NodeZero from Horizon3?

AI-generated summary from verified user reviews

Pros
  • Users praise the intuitive vulnerability detection of NodeZero, facilitating easy integration and thorough cybersecurity assessments.
  • Users appreciate the intuitive communication of NodeZero, making it accessible and effective for both technical and nontechnical teams.
  • Users highlight the intuitive interface and thorough capabilities of NodeZero, making it essential for effective cybersecurity.
  • Users value the ease of implementation of NodeZero, finding it simple for both technical and nontechnical staff.
  • Users appreciate the easy integrations of NodeZero, enabling seamless implementation for both technical and non-technical staff.
Cons
  • Users note that the inadequate reporting in NodeZero makes it hard to identify specific machine outcomes.
  • Users find the lack of detailed reporting on machine success and failure a significant drawback of NodeZero.

What Are Recent G2 Reviews of NodeZero from Horizon3?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 223

How Do G2 Users Rate Intruder?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.6/10 (Category avg: 9.2/10)
  • Extensibility: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users find Intruder's ease of use essential, appreciating its intuitive setup and minimal maintenance requirements.
  • Users value the easy setup and effective vulnerability detection of Intruder, enhancing their network security swiftly.
  • Users commend Intruder's responsive and friendly customer support, appreciating their fast and effective communication for assistance.
  • Users praise Intruder's intuitive user interface, which simplifies navigation and integrates seamlessly with existing tools.
  • Users appreciate the clarity and prioritisation of Intruder's vulnerability findings, enabling effective and meaningful action against risks.
Cons
  • Users find the expensive pricing a barrier for smaller implementations and prefer a more competitive option.
  • Users are frustrated with the slow scanning speed of Intruder, leading to missed vulnerabilities and increased manual work.
  • Users find licensing issues complicated, with unclear costs and separate application and infrastructure licenses adding to confusion.
  • Users report experiencing false positives with Intruder, leading to extra manual work and missed vulnerabilities.
  • Users find limited features in Intruder, particularly regarding licensing clarity and advanced reporting options.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.5/5.0

Total Reviews: 272

How Do G2 Users Rate Aikido Security?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 10.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

Synack

Synack is a continuous penetration testing platform that combines agentic AI with a global network of vetted security researchers to uncover real, exploitable vulnerabilities across the entire attack surface. Most organizations test only a fraction of what matters. Synack closes that coverage gap—using AI to scale discovery and human expertise to validate real risk. The platform enables enterprises to move from periodic testing to continuous security validation across web applications, APIs, cloud, and infrastructure—prioritizing findings based on what is actually exploitable, not just detected. Synack supports penetration testing, continuous security testing, vulnerability management, and attack surface management in dynamic, cloud-based, and hybrid environments. Founded by former NSA professionals, Synack supports enterprise and public sector organizations where security, compliance, and risk management are mission-critical.

Average Rating: 4.8/5.0

Total Reviews: 21

How Do G2 Users Rate Synack?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Synack?

  • Seller: NetSPI
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Minneapolis, MN
  • LinkedIn® Page: www.linkedin.com
    595 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 71% Large, 14% Small

What Are Recent G2 Reviews of Synack?

What Are G2 Users Discussing About Synack?

Metasploit

Metasploit is a comprehensive penetration testing platform developed by Rapid7, designed to help security professionals identify, exploit, and validate vulnerabilities within their networks. By simulating real-world attacks, Metasploit enables organizations to assess their security posture and enhance their defenses against potential threats. Key Features and Functionality: - Extensive Exploit Library: Access to a vast, regularly updated database of over 1,500 exploits and 3,300 modules, allowing users to simulate a wide range of attack scenarios. - Automated Exploitation: Features like Smart Exploitation and automated credential brute-forcing streamline the penetration testing process, increasing efficiency and accuracy. - Post-Exploitation Modules: Over 330 post-exploitation modules enable testers to assess the impact of a successful breach and gather critical information from compromised systems. - Credential Testing: Ability to run brute-force attacks against more than 20 account types, including databases, web servers, and remote administration tools, to uncover weak or reused passwords. - Integration Capabilities: Seamless integration with other Rapid7 products, such as InsightVM and Nexpose, facilitates closed-loop vulnerability validation and remediation prioritization. Primary Value and Problem Solving: Metasploit empowers organizations to proactively identify and address security weaknesses before malicious actors can exploit them. By simulating real-world attacks, it provides valuable insights into potential vulnerabilities, enabling security teams to prioritize remediation efforts effectively. This proactive approach enhances overall security awareness, reduces the risk of breaches, and ensures compliance with industry standards and regulations.

Average Rating: 4.6/5.0

Total Reviews: 53

How Do G2 Users Rate Metasploit?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Metasploit?

  • Seller: Rapid7
  • Year Founded: 2000
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    8,746 employees on LinkedIn®
  • Ownership: NASDAQ:RPD
  • Total Revenue (USD mm): $411

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 47% Small, 40% Medium

What Do G2 Reviewers Say About Metasploit?

AI-generated summary from verified user reviews

Pros
  • Users value the pentesting efficiency of Metasploit, appreciating its extensive toolkit and versatile payload creation.
  • Users commend Metasploit for its expertise in payload creation, making it a top choice for hackers.
Cons
  • Users find the complex setup of Metasploit challenging and suggest that automation would improve usability.

What Are Recent G2 Reviews of Metasploit?

What Are G2 Users Discussing About Metasploit?

Pentest-Tools.com

Vulnerability detection | Autonomous pentesting | Human expertise Built by offensive security practitioners, Pentest-Tools.com gives security teams a unified place to test their defenses continuously, go deeper when needed, and prove what needs to be fixed. Pentest-Tools.com covers multiple classes of assets, from web applications to network and cloud infrastructures, with daily detection and exploitation updates. Experienced offensive security professionals, including our customers and our own services team, constantly battle-test it across numerous engagements. Their feedback helps us keep improving the product so it delivers: ✔️ a low false positive rate ✔️ rich evidence, including screenshots, attack replay, data snippets, and more ✔️ detailed, customizable reporting Behind all of this, our vulnerability research team proactively looks for new security issues in widely used software and explores attack techniques, using them to enrich our exploit database and vulnerability feed. Unlike vulnerability scanners that primarily stop at detection, or testing approaches built around a single level of depth, Pentest-Tools.com lets teams match testing depth to the situation. Security teams can: ✔️ control what gets tested, how & when with deterministic Scanning & Validation ✔️ investigate web apps on-demand with autonomous AI Pentests ✔️ bring in human-led Offensive Security Services when business context, independent attestation, or custom reporting matter. As the target or situation changes, internal security teams can move between these testing modes without changing vendors or breaking their workflow.

Average Rating: 4.8/5.0

Total Reviews: 110

How Do G2 Users Rate Pentest-Tools.com?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.9/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.2/10 (Category avg: 9.2/10)
  • Extensibility: 6.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Pentest-Tools.com?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 67% Small, 19% Medium

What Do G2 Reviewers Say About Pentest-Tools.com?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Pentest-Tools.com, appreciating its straightforward setup and user-friendly features.
  • Users value the automation of scans on Pentest-Tools.com, enabling efficient and reliable vulnerability management with minimal manual effort.
  • Users commend the exceptional customer support from Pentest-Tools.com, highlighting their responsiveness and willingness to assist.
  • Users value the efficiency of Pentest-Tools.com, appreciating its comprehensive and user-friendly penetration testing capabilities.
  • Users appreciate the easy scheduling features of Pentest-Tools.com, significantly streamlining their vulnerability management process.
Cons
  • Users face difficult customization in Pentest-Tools.com due to limited report editing and template options, hindering flexibility.
  • Users feel the limited features of Pentest-Tools.com hinder report customization and timely scan test reports.
  • Users note that slow scanning can hinder efficiency, complicating the user experience with Pentest-Tools.com.
  • Users find the manual work required for complex findings somewhat annoying, especially when dealing with numerous assets.
  • Users find the interface confusing, wishing for more intuitive navigation and better integration capabilities.

What Are Recent G2 Reviews of Pentest-Tools.com?

What Are G2 Users Discussing About Pentest-Tools.com?

Indusface WAS

Indusface WAS (Web Application Scanner) provides comprehensive managed dynamic application security testing (DAST) solution. It is a zero-touch, non-intrusive cloud-based solution that provides daily monitoring for web applications, checking for systems and application vulnerabilities, and malware. Indusface WAS with its automated scans & manual pentesting done by certified security experts ensures none of the OWASP Top10, business logic vulnerabilities, and malware go unnoticed. With zero false-positive guarantee and comprehensive reporting with remediation guidance, Indusface web app scanning ensures developers to quickly fix vulnerabilities seamlessly.

Average Rating: 4.6/5.0

Total Reviews: 64

How Do G2 Users Rate Indusface WAS?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.2/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Indusface WAS?

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Small, 37% Medium

What Do G2 Reviewers Say About Indusface WAS?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive vulnerability detection by Indusface WAS, benefiting from detailed insights and helpful remediation guidelines.
  • Users appreciate the comprehensive vulnerability identification offered by Indusface WAS, ensuring detailed insights and effective remediation.
  • Users commend the responsive customer support from Indusface, ensuring timely assistance during VAPT testing and queries.
  • Users value the scanning efficiency of Indusface WAS, benefiting from automated deep-dive security scans and detailed reports.
  • Users value the deep-dive security scans of Indusface WAS, which enhance security accreditation and vulnerability management.
Cons
  • Users note that Indusface WAS is expensive, particularly for development environment scans and SSL certificates.
  • Users find the interface confusing and suggest it needs to be more intuitive and up-to-date.
  • Users find the limited functionality in the free testing version restricts their ability to effectively scan development environments.
  • Users feel that limited pricing options for staging scans hinder effective testing before deployment in development environments.
  • Users find the interface design outdated and unintuitive, though improvements are reportedly in progress.

What Are Recent G2 Reviews of Indusface WAS?

What Are G2 Users Discussing About Indusface WAS?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

How Do G2 Users Rate Edgescan?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.5/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.5/10 (Category avg: 9.2/10)
  • Extensibility: 9.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, enjoying its user-friendly interface and convenient access to essential information.
  • Users value the near false positive free vulnerability scanning of Edgescan, making web application testing efficient and reliable.
  • Users highly value the fantastic customer support from Edgescan, enhancing their overall experience significantly.
  • Users value the validated, near false positive free vulnerability scanning of Edgescan, enhancing their testing experience significantly.
  • Users appreciate the user-friendly console of Edgescan, as it offers easy access and comprehensive functionality for managing vulnerabilities.
Cons
  • Users find the complex UI of Edgescan challenging, leading to inefficiencies and difficulties in task navigation.
  • Users find the limited customization for hosts and filtering frustrating, impacting their ability to adapt to changes.
  • Users find the poor interface design of Edgescan frustrating, hindering efficient navigation and task completion.
  • Users experience slow performance with Edgescan, as scans can take longer due to thorough validation processes.
  • Users find the user interface challenging to navigate, leading to delays and difficulty performing common tasks.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?

Invicti Web + API (formerly Acunetix)

Invicti Web + API (formerly Acunetix) is a dynamic application security testing (DAST) solution that helps security and development teams find and validate exploitable vulnerabilities across web applications and APIs. Built on the same Acunetix technology and expertise customers already know, Invicti Web + API combines fast, accurate scanning with proof-based validation, modern application coverage, and intelligent automation. With Invicti Web + API, teams can: - Discover and test vulnerabilities across websites, web applications, APIs, single-page applications, and modern JavaScript frameworks - Validate exploitable vulnerabilities with proof-based scanning to reduce false positives and manual verification - Test REST, SOAP, and GraphQL APIs, including complex and stateful application workflows - Integrate security testing into CI/CD, issue tracking, and development workflows so validated findings reach the teams responsible for remediation - Automate recurring application security testing across development and production environments Invicti Web + API serves as the foundation of Invicti’s solution portfolio, extending proven web and API security into the broader Invicti AppSec platform and its agentic pentesting capabilities.

Average Rating: 4.1/5.0

Total Reviews: 100

How Do G2 Users Rate Invicti Web + API (formerly Acunetix)?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.6/10 (Category avg: 9.2/10)
  • Extensibility: 7.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Invicti Web + API (formerly Acunetix)?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 40% Large, 34% Medium

What Do G2 Reviewers Say About Invicti Web + API (formerly Acunetix)?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid and precise vulnerability detection in Invicti Web + API, enhancing security for their applications.
  • Users commend the ease of use of Invicti Web + API, appreciating its intuitive interface and seamless integration.
  • Users appreciate the robust security features of Invicti Web + API, ensuring thorough protection for web applications.
  • Users appreciate the effective vulnerability identification capabilities of Invicti, enhancing web application security significantly.
  • Users value the accuracy of results from Invicti Web + API, ensuring reliable vulnerability assessments for web applications.
Cons
  • Users find the pricing of Invicti Web + API to be expensive, limiting accessibility for smaller teams and projects.
  • Users find the complexity in setup and configurations of Invicti Web + API challenging, especially for new users.
  • Users find the complex setup of Invicti Web + API challenging, especially for first-time configurations and integrations.
  • Users experience slow scanning that can hinder normal workflows and complicate the use of the tool.
  • Users find that difficult customization can hinder the integration of Invicti Web + API, requiring extensive technical knowledge.

What Are Recent G2 Reviews of Invicti Web + API (formerly Acunetix)?

What Are G2 Users Discussing About Invicti Web + API (formerly Acunetix)?

Titania Nipper InfraSight

Award-winning Risk-Based Vulnerability Management. Nipper InfraSight analyzes network device configurations in the way Advances Persistent Threat (APT) groups do, to identify misconfigurations that could create attack paths. This analysis offers unparalleled, pen-tester accuracy, finding critical vulnerabilities in firewalls, routers, switches that other tools simply cannot see. Our solutions then prioritize the biggest risks to your business and provide device-specific remediation guidance, right down to specific command line prompts.  By analyzing device configurations against key compliance standards and security frameworks (including STIGs/CIS Benchmarks/PCI DSS/CMMC/CORA/NIST SP 800-53), Nipper solutions tell you precisely which devices are at risk of failing, how significant that risk is, and how you can solve it, with auditor-ready reports. Whether your focus is taking pragmatic, risk-based security measures to minimize known vulnerabilities or ensuring compliance with industry security standards, Nipper solutions provide the targeted insights you need. No other security provider looks at the network in the same way. That’s why Nipper can uniquely provide the network configuration coverage that organizations urgently require. 30+ U.S. federal agencies and 800+ organizations globally trust Nipper solutions to deliver vulnerability analysis and compliance automation while supporting air-gapped environments, sovereign cloud requirements, and complex regulated infrastructures.

Average Rating: 4.3/5.0

Total Reviews: 33

How Do G2 Users Rate Titania Nipper InfraSight?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 10.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Titania Nipper InfraSight?

  • Seller: Titania
  • Company Website:
  • Year Founded: 2009
  • HQ Location: London, GB
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 39% Large, 24% Medium

What Do G2 Reviewers Say About Titania Nipper InfraSight?

AI-generated summary from verified user reviews

Pros
  • Users find the ease of use of Titania Nipper InfraSight exceptional, enabling straightforward assessments with clear documentation.
  • Users value the clear and actionable reporting of Titania Nipper InfraSight, enhancing their assessment accuracy and usability.
  • Users value the scanning efficiency of Titania Nipper InfraSight, enabling quick identification of vital system risks.
  • Users commend Titania Nipper for its effective vulnerability detection, providing actionable recommendations and enhancing network security.
  • Users value the clear and user-friendly interface of Titania Nipper InfraSight, making assessment straightforward and efficient.
Cons
  • Users find the licensing issues challenging, specifically with device limits and the model based on quantity.
  • Users often experience false positives, leading to confusion with inaccurate findings and device vulnerability reports.
  • Users find the lack of cloud support frustrating, especially with inaccuracies in scanning recommendations for specific devices.
  • Users face limited compatibility with devices, leading to the inconvenience of maintaining multiple software versions.
  • Users face a limited scope of device support, requiring maintenance of older versions and encountering auditing challenges.

What Are Recent G2 Reviews of Titania Nipper InfraSight?

What Are G2 Users Discussing About Titania Nipper InfraSight?

Cyver Core

Cyver Core is a pentest collaboration and management platform to digitize, automate, and optimize manual work for pentest firms, while enabling Pentest-as-a-Service delivery. Cyver Core offers pentest report automation, branded client portals, pentest management, team management, and more.

Average Rating: 4.7/5.0

Total Reviews: 20

How Do G2 Users Rate Cyver Core?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 7.9/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Cyver Core?

  • Seller: Cyver
  • Year Founded: 2020
  • HQ Location: Amsterdam, NL
  • LinkedIn® Page: www.linkedin.com
    10 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 75% Small, 20% Medium

What Do G2 Reviewers Say About Cyver Core?

AI-generated summary from verified user reviews

Pros
  • Users are impressed with the high efficiency and automation in managing pentesting workflows through Cyver Core.
  • Users value the streamlined reporting quality of Cyver Core, enhancing efficiency and client communication throughout the process.
  • Users appreciate the seamless communication of Cyver Core, enhancing collaboration and streamlining the workflow efficiently.
  • Users value the fast and helpful customer support of Cyver Core, enhancing their overall experience and engagement.
  • Users appreciate the robust cybersecurity features of Cyver Core, enhancing pentesting efficiency and customer experience.
Cons
  • Users find the limited customization of Cyver Core restricting, particularly with fixed roles and predefined options.
  • Users have reported technical issues such as stability problems and occasional slowness that affect usability.
  • Users experience poor documentation, leading to non-intuitive UI/UX and occasional bugs despite quick fixes.
  • Users find poor interface design in Cyver Core, with some UI/UX areas being non-intuitive and causing confusion.
  • Users report experiencing slow performance at times, which can hinder their overall experience with Cyver Core.

What Are Recent G2 Reviews of Cyver Core?

What Are G2 Users Discussing About Cyver Core?

APPCHECK

Uncover your full attack surface, test it constantly, act with confidence. AppCheck helps organisations reduce cyber risk, meet compliance requirements and keep pace with evolving threats. Our platform delivers continuous security testing across your attack surface with the depth of a manual penetration test, uncovering vulnerabilities unique to your systems across web applications, APIs and infrastructure. Born from a UK-based penetration testing organisation, AppCheck combines over 20 years of testing expertise with a first-principles approach to security testing. Developed and supported by experienced penetration testers, the platform goes beyond known vulnerability signatures, analysing application behaviour to identify weaknesses that conventional scanning approaches can miss. Using multiple proprietary crawling engines, AppCheck tests modern and traditional technologies, including Single Page Applications (SPAs), APIs and complex authentication flows such as SSO, 2FA and TOTP. Discover: Gain visibility across your attack surface, including forgotten assets and third-party exposure. Assess: Find and validate vulnerabilities with the depth and rigour of a manual penetration test. Take action: Prioritise real-world risk and focus resources on what needs fixing first. Organisations can conduct unlimited security assessments across web applications, SPAs, APIs, cloud services and network infrastructure, covering both internal and external assets. With support for production and UAT environments, AppCheck also helps development teams shift security testing left through integrations with CI/CD pipelines and build tools, including Azure DevOps, GitHub, Jenkins, TeamCity, CircleCI, Bamboo and GitLab CI/CD. This enables automated security testing throughout development, helping teams identify vulnerabilities as changes are introduced. With unlimited scans and users per licence, teams can test continuously without additional charges for each scan, backed by direct UK-based support from security specialists. AppCheck is proud to be a CVE Numbering Authority (CNA), contributing to global vulnerability research.

Average Rating: 4.7/5.0

Total Reviews: 68

How Do G2 Users Rate APPCHECK?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.3/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.5/10 (Category avg: 9.2/10)
  • Extensibility: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind APPCHECK?

  • Seller: APPCHECK
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Leeds, GB
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 49% Medium, 31% Small

What Do G2 Reviewers Say About APPCHECK?

AI-generated summary from verified user reviews

Pros
  • Users commend the thorough and reliable vulnerability detection of AppCheck, enhancing security in their applications effectively.
  • Users find the ease of use of AppCheck remarkable, praising its user-friendly interface and responsive support.
  • Users value the excellent pricing and functionality of AppCheck, along with its reliable and intuitive vulnerability scanning.
  • Users find Pentest efficiency remarkable with AppCheck, leading to significant cost savings and streamlined vulnerability detection.
  • Users value the automated scanning feature of AppCheck, enhancing efficiency and streamlining vulnerability management across multiple apps.
Cons
  • Users find the poor customer support frustrating, needing to raise tickets for simple adjustments to the scan list.
  • Users suggest that UX improvements in scoring, customization, and integrations could enhance the AppCheck experience.
  • Users find the API issues frustrating, as endpoint changes require a service request and delays functionality.
  • Users find difficult customization in AppCheck's reporting features, needing more flexibility for contextual adjustments.
  • Users experience a notable difficult learning curve with Appcheck, which may hinder initial ease of use.

What Are Recent G2 Reviews of APPCHECK?

Black Duck Polaris Platform

Black Duck builds trust in software by enabling organizations to manage application security, quality, and compliance risks at the speed their business demands. Black Duck solutions help developers to secure code as fast as they write it, development and DevSecOps teams to automate testing within development pipelines without compromising velocity, and security teams to proactively manage risk and focus remediation efforts on what matters most. With Black Duck, organizations can transform the way they build and deliver software, aligning people, processes, and technology to intelligently address software risks across their portfolio and at all stages of the application lifecycle.

Average Rating: 4.2/5.0

Total Reviews: 103

How Do G2 Users Rate Black Duck Polaris Platform?

  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 6.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Black Duck Polaris Platform?

  • Seller: Black Duck
  • Year Founded: 2024
  • HQ Location: Burlington, US
  • LinkedIn® Page: www.linkedin.com
    1,317 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Large, 32% Medium

What Do G2 Reviewers Say About Black Duck Polaris Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the accuracy of findings in Black Duck Polaris, especially its powerful engine for identifying open source issues.
  • Users praise the powerful open source issue identification by Black Duck Polaris, benefiting from extensive Black Duck Knowledge.
Cons
  • Users note that the platform requires huge resource constraints for on-prem deployment, impacting its usability.

What Are Recent G2 Reviews of Black Duck Polaris Platform?

What Are G2 Users Discussing About Black Duck Polaris Platform?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated March 5, 2025