Best Static Application Security Testing (SAST) Software

How Many Static Application Security Testing (SAST) Software Products Does G2 Track?

Total Products under this Category: 144

Category Stats (Nov 2026)

  • Average Rating: 4.54/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Endor Labs (+0.46%) - Among all products in this category, Endor Labs recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Static Application Security Testing (SAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,700+ Authentic Reviews
  • 144+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

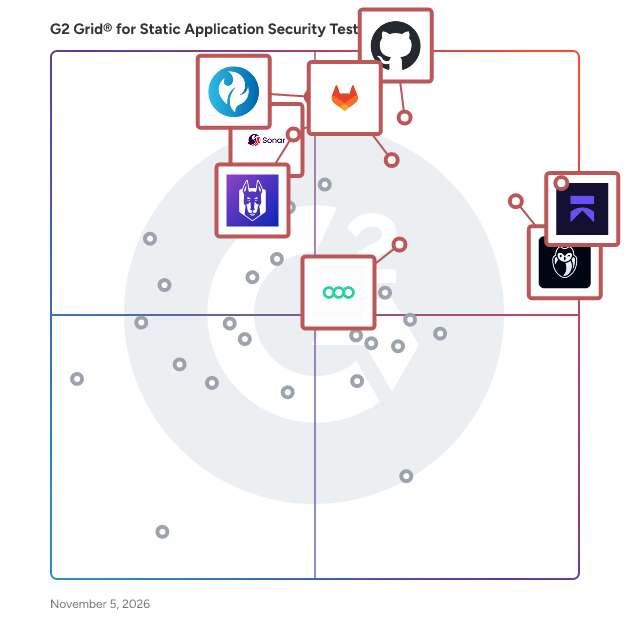
G2 Grid® for Static Application Security Testing (SAST) Software

G2 Grid® for Static Application Security Testing (SAST) Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, GitGuardian, GitHub, GitLab, SonarQube, HCL AppScan, Snyk, and Semgrep.

Underlying data: [Grid® JSON](https://www.g2.com/categories/static-application-security-testing-sast/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=gitguardian&focus%5B%5D=github&focus%5B%5D=gitlab&focus%5B%5D=sonarqube&focus%5B%5D=hcl-appscan&focus%5B%5D=snyk&focus%5B%5D=semgrep)

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.5/5.0

Total Reviews: 272

How Do G2 Users Rate Aikido Security?

  • Test Automation: 8.6/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.1/10)
  • Quality of Support: 9.3/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

GitGuardian

GitGuardian is the credential layer security platform for securing the secrets that let code, machines, and AI agents access systems and act as trusted identities. API keys, tokens, passwords, and other secrets carry real access. When they leak, attackers do not need to break in, they can log in. The scale of the problem keeps growing: 28.6 million new secrets were exposed on public GitHub in 2025, a 34% year-over-year increase and the largest jump on record. GitGuardian finds the secrets that matter across an organization's entire secrets surface, inside and outside the perimeter. Internal Secrets Monitoring detects hardcoded credentials across private repositories, CI/CD pipelines, container images, cloud configs, and collaboration tools like Slack, Jira, Confluence, and Google Drive, using 550+ detectors with live validity checks that confirm each secret is active before it hits your queue. Public Secrets Monitoring scans public GitHub (1B+ commits per year) and DockerHub in real time for corporate secrets exposed online. Developer Endpoint Protection extends coverage to the developer machine itself: config files, shell history, MCP configs, and files persisted by AI coding agents like Claude Code, Cursor, and Copilot. AI Hooks add runtime guardrails inside the agents, checking prompts before they are sent. For every secret it finds, GitGuardian reveals context and blast radius. NHI Governance supplies that identity layer, discovering every machine identity across repos, CI/CD, cloud, and collaboration tools, attributing ownership, scoring risk, helping configure rotation policies, and surfacing continuous compliance evidence for PCI-DSS v4.0, NYDFS, DORA, NIS 2, and NIST 800-53. The detection surfaces find what's leaking. The identity layer connects each leak back to who owns it and what it accesses. One closed loop, from a developer's laptop to public GitHub. Honeytokens alert teams the moment an attacker uses a decoy credential. Backed by a $50M Series C raised in February 2026 (Insight Partners, Quadrille Capital) and trusted by 600K+ developers, GitGuardian is the #1 most-installed security app on the GitHub Marketplace. Enterprises including ING, BASF, Datadog, Bouygues Telecom, Euronext, and Orange Business rely on the platform.

Average Rating: 4.8/5.0

Total Reviews: 304

How Do G2 Users Rate GitGuardian?

  • Test Automation: 8.4/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.1/10)
  • Quality of Support: 9.1/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 9.0/10 (Category avg: 8.5/10)

Who Is the Company Behind GitGuardian?

  • Seller: GitGuardian
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Paris, Île-de-France
  • LinkedIn® Page: www.linkedin.com
    208 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Software Developer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 85% Small, 12% Medium

What Do G2 Reviewers Say About GitGuardian?

AI-generated summary from verified user reviews

Pros
  • Users value the instant alert notifications from GitGuardian, enabling quick detection and remediation of sensitive data issues.
  • Users value the real-time secret detection of GitGuardian, enhancing security seamlessly within their development workflows.
  • Users value the fast and accurate vulnerability detection of GitGuardian, which ensures code safety effortlessly.
  • Users value the easy Git integration of GitGuardian, enhancing security without disrupting their coding workflow.
  • Users commend GitGuardian for its high accuracy in secret detection, enhancing security without disrupting their workflow.
Cons
  • Users experience false positives with GitGuardian, necessitating manual reviews and slowing down the workflow.
  • Users find the inefficient notifications overwhelming due to volume, false positives, and cluttered incident navigation.
  • Users note the limited customization options in GitGuardian, which can affect alert management and overall configuration.
  • Users find the confusing interface complicates navigation and increases manual filtering time for multiple incident alerts.
  • Users find the difficulty for beginners in navigating alerts overwhelming, impacting their ability to assess real threats effectively.

What Are Recent G2 Reviews of GitGuardian?

What Are G2 Users Discussing About GitGuardian?

GitHub

GitHub is where the world builds software. Millions of individuals, organizations and businesses around the world use GitHub to discover, share, and contribute software. Developers at startups to Fortune 50 companies use GitHub, every step of the way.

Average Rating: 4.7/5.0

Total Reviews: 2,362

How Do G2 Users Rate GitHub?

  • Test Automation: 8.6/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.1/10)
  • Quality of Support: 8.7/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.4/10 (Category avg: 8.5/10)

Who Is the Company Behind GitHub?

  • Seller: GitHub
  • Year Founded: 2008
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    6,653 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 47% Small, 31% Medium

What Do G2 Reviewers Say About GitHub?

AI-generated summary from verified user reviews

Pros
  • Users love the user-friendly interface of GitHub, enjoying seamless collaboration and efficient project management.
  • Users value the ease of use of GitHub, praising its intuitive interface and seamless collaboration features.
  • Users value the efficient team collaboration GitHub offers, streamlining workflows and enhancing project management.
  • Users value the smooth collaboration on GitHub, appreciating its all-in-one platform for managing projects and code.
  • Users appreciate how GitHub offers integrated version control, enhancing collaboration and workflow efficiency in development projects.
Cons
  • Users find the complexity of GitHub's features challenging, especially for new team members adapting to advanced workflows.
  • Users find the steep learning curve challenging, especially for advanced features and managing complex repositories.
  • Users find the difficulty for beginners in mastering advanced features and git commands to be quite challenging.
  • Users find the learning difficulty challenging, especially with advanced features and complex workflows for newcomers.
  • Users find the steep learning curve for advanced features challenging, especially for beginners navigating Git commands and workflows.

What Are Recent G2 Reviews of GitHub?

What Are G2 Users Discussing About GitHub?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

GitLab

GitLab is the most comprehensive AI-Powered DevSecOps platform that enables software innovation by empowering development, security, and operations teams to build better software, faster. With GitLab, teams can create, deliver, and manage code quickly and continuously instead of managing disparate tools and scripts. GitLab helps your teams across the complete DevSecOps lifecycle, from developing, securing, and deploying software. What makes us truly different? - Flexibility: Consume as a service or manage your own deployment - Cloud-Agnostic: Deploy anywhere with no vendor lock-in - No rip and replace: Scale to a platform approach at your own pace

Average Rating: 4.5/5.0

Total Reviews: 886

How Do G2 Users Rate GitLab?

  • Test Automation: 9.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.1/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.9/10 (Category avg: 8.5/10)

Who Is the Company Behind GitLab?

  • Seller: GitLab Inc.
  • Year Founded: 2014
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    3,431 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 37% Medium, 37% Small

What Do G2 Reviewers Say About GitLab?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of GitLab, enjoying its intuitive interface and smooth integration with tools.
  • Users appreciate the user-friendly interface and powerful integration features that streamline their development workflows in GitLab.
  • Users appreciate the integrated CI/CD feature of GitLab, which enhances their workflow and collaboration efficiency.
  • Users value the integrated CI/CD feature in GitLab, enabling seamless workflows and efficient code deployment.
  • Users value the seamless integrations in GitLab, enhancing productivity and aligning well with current development workflows.
Cons
  • Users find the complexity of the setup and interface can hinder their overall experience with GitLab.
  • Users find the difficult learning curve challenging, especially when adapting to unique project structures and numerous features.
  • Users find the interface confusing, with hidden settings and a cluttered design affecting usability and accessibility.
  • Users find the complex user interface of GitLab challenging, particularly with large projects, affecting usability and performance.
  • Users find the learning curve steep, especially when adapting to GitLab's diverse features and project structures.

What Are Recent G2 Reviews of GitLab?

What Are G2 Users Discussing About GitLab?

SonarQube

Sonar, the industry standard for code verification and automated code review, helps reduce outages, improve security, and lower risks associated with AI and agentic coding. As an independent verification platform, Sonar enables organizations to securely develop at the speed of AI. Sonar is the foundation for high-performance software engineering, analyzing over 750 billion lines of code daily to ensure applications are secure, reliable, and maintainable. Rooted in the open source community, Sonar is trusted by 7M+ developers globally, including teams at ServiceNow, Booking.com, Deutsche Bank, AstraZeneca, and Ford Motor Company.

Average Rating: 4.4/5.0

Total Reviews: 159

How Do G2 Users Rate SonarQube?

  • Test Automation: 6.5/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.1/10)
  • Quality of Support: 8.2/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 6.9/10 (Category avg: 8.5/10)

Who Is the Company Behind SonarQube?

  • Seller: Sonar
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Geneva, Switzerland
  • LinkedIn® Page: www.linkedin.com
    1,041 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 41% Large, 40% Medium

What Do G2 Reviewers Say About SonarQube?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the high-quality code analysis of SonarQube, which ensures cleaner, more reliable, and maintainable code.
  • Users appreciate the effective code quality management of SonarQube, enhancing prioritization and integration in development workflows.
  • Users appreciate the effective issue identification in SonarQube, enabling prioritization of new findings and maintaining code quality.
  • Users appreciate the ease of use of SonarQube, especially for simple integration and effective code quality management.
  • Users appreciate the easy integrations of SonarQube, seamlessly enhancing their CI/CD workflows and code quality management.
Cons
  • Users report encountering software bugs in SonarQube, leading to frustration with false positives and complex configurations.
  • Users find configuration complex in SonarQube, especially with large projects, leading to a time-consuming setup process.
  • Users struggle with the high rate of false positives, requiring extra time for manual review and adjustments.
  • Users find SonarQube's complexity in configuration and setup to be a challenging aspect, especially with large projects.
  • Users find the initial setup complex, especially for larger projects, requiring time for configuration and rule tuning.

What Are Recent G2 Reviews of SonarQube?

What Are G2 Users Discussing About SonarQube?

HCL AppScan

HCL AppScan is a comprehensive suite of market-leading application security testing solutions (SAST, DAST, IAST, SCA, API), available on-premises and on-cloud. These powerful DevSecOps tools pinpoint application vulnerabilities, allowing for quick remediation in every phase of the software development lifecycle. Fast and Accurate Scanning for Secure DevOps Developers and DevOps teams can quickly and accurately scan code, applications, and APIs for security vulnerabilities while applications are being developed. This allows companies to fix issues at the earliest stages of the software development lifecycle, when it is least costly to the business. Focus on the Fix Continuous monitoring with IAST, along with auto issue correlation with DAST and SAST scan results allows DevOps teams to group and prioritize findings for faster, more streamlined remediation. Enterprise Management for Security Teams Centralized, easy-to-use dashboards provide visibility and oversight of all security scanning and remediation, and allow users to set scan parameters and compliance policies.

Average Rating: 4.2/5.0

Total Reviews: 125

How Do G2 Users Rate HCL AppScan?

  • Test Automation: 8.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.6/10 (Category avg: 8.5/10)

Who Is the Company Behind HCL AppScan?

  • Seller: HCL Technologies
  • Company Website:
  • Year Founded: 1999
  • HQ Location: Noida, Uttar Pradesh
  • LinkedIn® Page: www.linkedin.com
    258,955 employees on LinkedIn®
  • Ownership: NSE - National Stock Exchange of India

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 50% Large, 26% Medium

What Are Recent G2 Reviews of HCL AppScan?

What Are G2 Users Discussing About HCL AppScan?

Snyk

Snyk (pronounced sneak) is a developer security platform for securing custom code, open source dependencies, containers, and cloud infrastructure all from a single platform. Snyk’s developer security solutions enable modern applications to be built securely, empowering developers to own and build security for the whole application, from code & open source to containers & cloud infrastructure. Secure while you code in your IDE: find issues quickly using the scanner, fix issues easily with remediation advice, verify the updated code. Integrate your source code repositories to secure applications: integrate a repository to find issues, prioritize with context, fix & merge. Secure your containers as you build, throughout the SDLC: start fixing containers as soon as your write a Dockerfile, continuously monitor container images throughout their lifecycle, and prioritize with context. Secure build and deployment pipelines: Integrate natively with your CI/CD tool, configure your rules, find & fix issues in your application, and monitor your applications. Secure your apps quickly with Snyk’s vulnerability scanning and automated fixes - Try for Free!

Average Rating: 4.5/5.0

Total Reviews: 136

How Do G2 Users Rate Snyk?

  • Test Automation: 7.8/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.1/10)
  • Quality of Support: 8.6/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 6.2/10 (Category avg: 8.5/10)

Who Is the Company Behind Snyk?

  • Seller: Snyk
  • HQ Location: Boston, Massachusetts
  • LinkedIn® Page: www.linkedin.com
    1,764 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 45% Medium, 35% Small

What Do G2 Reviewers Say About Snyk?

AI-generated summary from verified user reviews

Pros
  • Users appreciate Snyk's vulnerability detection, which enables timely identification and remediation of security issues.
  • Users value Snyk for its rapid vulnerability identification, significantly enhancing code security and DevOps efficiency.
  • Users value Snyk's easy integration setup, enhancing workflow and efficiency in vulnerability management within CI/CD pipelines.
  • Users find Snyk's easy setup with GitHub highly beneficial for seamless integration and vulnerability management.
  • Users appreciate the intuitive GUI and robust organizational features of Snyk, streamlining vulnerability management and reporting.
Cons
  • Users experience false positives from Snyk, leading to confusion and delays in their workflow.
  • Users find the poor interface design of Snyk inconvenient and seek better integration and usability.
  • Users express concerns over high pricing, especially for full feature access, though they see long-term value.
  • Users face scanning issues with false positives, slow scans, and lack of integration affecting workflow efficiency.
  • Users experience false positives and slow scans with Snyk, complicating integration and reducing effectiveness in detecting issues.

What Are Recent G2 Reviews of Snyk?

What Are G2 Users Discussing About Snyk?

Semgrep

Semgrep is a modern static analysis (SAST), software composition analysis (SCA), and secrets detection platform designed for both developers and security teams. It combines fast, deterministic analysis with context-aware AI that triages findings like a senior security engineer. The AI Assistant helps reduce false positives, prioritize meaningful results, and offers clear remediation guidance. Its “Memories” feature learns from past decisions to further reduce triage noise over time. Semgrep also supports deep analysis of transitive dependencies, not just direct ones, helping teams surface and address hidden risks in their supply chain. It integrates well into modern development workflows and is easy to customize across environments.

Average Rating: 4.6/5.0

Total Reviews: 56

How Do G2 Users Rate Semgrep?

  • Test Automation: 9.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.8/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 7.5/10 (Category avg: 8.5/10)

Who Is the Company Behind Semgrep?

  • Seller: Semgrep
  • Year Founded: 2017
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    265 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 45% Large, 43% Medium

What Do G2 Reviewers Say About Semgrep?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Semgrep, enabled by its intuitive syntax and smooth integration with CI/CD.
  • Users appreciate the flexibility and speed of Semgrep in enforcing coding standards and catching vulnerabilities effectively.
  • Users appreciate the effective vulnerability detection of Semgrep, facilitating quick identification and resolution of security issues.
  • Users appreciate the scanning efficiency of Semgrep, benefiting from rapid scans and streamlined CI/CD integration.
  • Users value Semgrep for its effective security vulnerability detection, enabling quick resolutions without hindering development speed.
Cons
  • Users find Semgrep not user-friendly due to a steep learning curve and complex initial setup requirements.
  • Users find the limited features of Semgrep restrict its usability and complicate effective vulnerability management.
  • Users find the difficult learning curve for Semgrep daunting, especially for creating advanced rules and setups.
  • Users express concerns about the lack of guidance in creating custom rules, complicating effective use of Semgrep.
  • Users note a steep learning curve for Semgrep's rule syntax, making it challenging for newcomers to master.

What Are Recent G2 Reviews of Semgrep?

Checkmarx

Checkmarx exists so the world can innovate faster than it ever has and still trust what it builds. That purpose starts with closing the Risk Gap — the widening distance between how fast software gets created and how fast risk can be understood and removed. As AI compresses the software development lifecycle from months to minutes, the old model of shipping code with known vulnerabilities and racing to patch it before attackers strike no longer works. Checkmarx's foundation: decades of deterministic threat intelligence and trillions of lines of code scanned each year. The Checkmarx One platform gives enterprises comprehensive application security, built to capture risk, eliminate vulnerabilities, and unify governance. Checkmarx Fusion now pairs that foundation with Claude-powered AI reasoning, unifying both engines to lead the category in detection accuracy. From there, the Checkmarx Assist family — Developer Assist, Triage Assist, and Remediation Assist — prevents vulnerabilities at the point of creation, prioritizes findings by real-world attackability, and generates review-ready fixes, so nothing sits in backlog waiting on a human to catch up. Checkmarx keeps detection and remediation independent. Instead of having the same system that writes the code grade its own work, security teams get oversight they can trust. This is the promise at the center of the mission: developers and agents never have to become security experts, and security leaders never have to take security on faith so enterprises can innovate at machine speed without ever trading speed for certainty.

Average Rating: 4.2/5.0

Total Reviews: 46

How Do G2 Users Rate Checkmarx?

  • Test Automation: 8.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.4/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 6.7/10 (Category avg: 8.5/10)

Who Is the Company Behind Checkmarx?

  • Seller: Checkmarx
  • Company Website:
  • Year Founded: 2006
  • HQ Location: Paramus, NJ
  • LinkedIn® Page: www.linkedin.com
    997 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 56% Large, 22% Medium

What Do G2 Reviewers Say About Checkmarx?

AI-generated summary from verified user reviews

Pros
  • Users find Checkmarx easy to implement into existing repositories, appreciating its user-friendly interface and comprehensive features.
  • Users appreciate the intuitive user interface of Checkmarx, making security reviews straightforward and user-friendly.
  • Users value the accuracy of results from Checkmarx, noting its effective code review and user-friendly interface.
  • Users appreciate the automation of security reviews in Checkmarx, praising its ease of implementation and user-friendly interface.
  • Users commend Checkmarx for its excellent customer support, consistently available to assist with any issues that arise.
Cons
  • Users experience a high number of false positives with Checkmarx, especially when analyzing Kotlin based projects.
  • Users are frustrated with Checkmarx's poor feature support for Kotlin, leading to numerous false positives in scans.
  • Users note a significant issue with false positives in Kotlin support, affecting their experience when using Checkmarx.
  • Users feel that the poor navigation in Checkmarx hinders their ability to efficiently use the dashboards.

What Are Recent G2 Reviews of Checkmarx?

What Are G2 Users Discussing About Checkmarx?

DryRun Security

Security leaders face a paradox: ship faster and enable agentic development while staying secure and keeping developers productive. DryRun Security resolves this by securing every pull request and repo with a high-precision, automated security engineer review right where developers and their agents build. DryRun Security is the industry’s most accurate agentic code security intelligence platform. Powered by its proprietary Contextual Security Analysis (CSA) engine, DryRun Security delivers the AI moment for security teams in an AI-native developer world. Traditional static application security testing (SAST) floods teams with alerts, misses higher-order risk, and burns time in triage. DryRun Security goes beyond SAST with contextual analysis that prioritizes what is exploitable and impactful in your codebase, then helps engineers remediate fast. Instead of “find everything and hope someone sorts it out,” DryRun Security delivers code security intelligence that is ready to act on. DryRun Security puts a security engineer directly into developer workflows. In pull requests, the Code Review Agent reviews changes in context, explains risk in plain language, and guides fixes where developers already work. In repos, the DeepScan Agent produces focused, human-grade findings for the issues that actually matter, without weeks of manual review before major milestones. The Custom Policy Agent enforces guardrails with Natural Language Code Policies, so you can standardize security and compliance requirements across teams without brittle rule sets. Codebase Insights allows leaders to ask questions of their entire codebase like "Are we exposed to this new vulnerability" and have confidence in minutes. DryRun Security also integrates with AI coding workflows, so remediation happens with the precision of a security engineer working at machine speed. Teams connect DryRun Security insights and guidance into Claude, Cursor, OpenAI Codex, and Windsurf, helping developers and their agents fix issues with contextual, security-engineered direction tied to the PR and codebase. What DryRun Security delivers (beyond SAST) • Automated secure code review in every pull request with high-signal findings and low noise • Contextual Security Analysis that catches common vulnerabilities and deeper multi-dependency and logic risks • Automated remediation guidance that helps engineers fix faster, with explanations and next steps • Secrets analysis identifies genuine hardcoded secrets and suppresses the usual false alarms • Policy enforcement in PRs using Natural Language Code Policies for consistent guardrails across repos • Codebase intelligence and reporting for AppSec visibility, prioritization, and audit-ready evidence DryRun Security supports most code environments, languages, and frameworks, including: • GitHub, GitLab • C#, Golang, Elixir, JavaScript, TypeScript, Python, Ruby, Java, Kotlin, PHP, Swift, HTML • Infrastructure as Code (Terraform, YAML) • And more

Average Rating: 4.9/5.0

Total Reviews: 23

How Do G2 Users Rate DryRun Security?

  • Test Automation: 10.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.1/10)
  • Quality of Support: 10.0/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind DryRun Security?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Computer Software
  • Company Size: 43% Small, 30% Medium

What Do G2 Reviewers Say About DryRun Security?

AI-generated summary from verified user reviews

Pros
  • Users value the context-aware security insights of DryRun Security, enabling effective vulnerability mitigation during code reviews.
  • Users value the context-aware vulnerability detection of DryRun Security, which reduces false positives and enhances trust with developers.
  • Users value the contextual intelligence of DryRun Security, enhancing code security and early issue detection in development.
  • Users value the accuracy of DryRun Security, as it reduces false positives and enhances code security insights.
  • Users value the easy setup of DryRun Security, enabling quick integration and automated scanning for better security.
Cons
  • Users experience slow performance in the management portal, with noticeable lag during UI interactions and loading times.
  • Users find the slow speed of the management portal frustrating, impacting their overall experience and efficiency.
  • Users note a need for better UX focus in DryRun Security to enhance developer engagement and workflow integration.
  • Users desire more customization options for tuning analyzers to enhance their experience with DryRun Security.
  • Users believe there are workflow issues that could be improved to enhance overall developer experience and adoption.

What Are Recent G2 Reviews of DryRun Security?

OX Security

OX rewires your security program for the Mythos Age: the era where AI writes the code, chains the exploits, and moves faster than human-built defenses can track. OX is an AI Native Application Protection Platform (AINAPP) unifying security from Prompt to Runtime. It moves your control surface upstream to the prompt, preventing and governing risk at the source instead of chasing it downstream in runtime. OX Mind and OX AI Context Lake connect AI-user governance, code security, cloud and runtime enforcement, and agentic pentesting into one system that shares context across the entire Agentic Development Lifecycle (ADLC), replacing fragmented point tools with a single platform. The platform runs on four connected pillars: OX VibeSec: Prevents unsafe AI decisions at the point of creation and governs every AI user in the organization, not just developers using coding assistants. Full visibility into which agents, MCPs, skills, and packages run, with what permissions, against what data. OX Code: Separates exploitable risk from theoretical noise using evidence from your actual deployment, threat model, and threat intelligence. OX Cloud: Prevents misconfigurations and enforces runtime boundaries that code and agents cannot cross, watching what actually runs in production. OX Agentic Pentester: Continuously simulates adversarial agent behavior to prove exploit paths back to their exact source, feeding what it finds back into OX VibeSec to sharpen governance. OX connects to your existing stack and traces every finding back to its origin (the prompt, the AI user, or the endpoint that created it), then fixes issues at the source rather than flagging them after the fact. For new deployments, OX consolidates governance, code security, cloud enforcement, and pentesting into one platform. For existing stacks, OX layers governance on top and makes current tools smarter through continuous learning, so the same issue never gets created twice. Visit https://ox.security for more information.

Average Rating: 4.8/5.0

Total Reviews: 51

How Do G2 Users Rate OX Security?

  • Test Automation: 7.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.1/10)
  • Quality of Support: 9.6/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 7.7/10 (Category avg: 8.5/10)

Who Is the Company Behind OX Security?

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 25% Large

What Do G2 Reviewers Say About OX Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the seamless integration and comprehensive features of OX Security, enhancing efficiency and issue management.
  • Users appreciate the ease of use of OX Security, highlighting its user-friendly interface and quick setup.
  • Users commend the great support team from OX Security, enhancing their overall experience and success.
  • Users value the seamless integration with existing tools, enhancing security without disrupting workflows or creating bottlenecks.
  • Users value the comprehensive security capabilities of OX Security, enhancing their organization's security posture effectively.
Cons
  • Users experience integration issues with OX Security, citing incomplete documentation and limited functionality in certain areas.
  • Users note the missing features in OX Security, impacting usability and integration with certain platforms and systems.
  • Users find OX Security's complexity overwhelming, with a steep learning curve and inadequate documentation frustrating the experience.
  • Users find the inadequate reporting in OX Security limits their ability to showcase security progress effectively.
  • Users note the limited cloud integration with tools like Azure DevOps, affecting ease of use and accessibility.

What Are Recent G2 Reviews of OX Security?

Arnica

Arnica is a comprehensive application security posture management (ASPM) platform that protects developers, source code, and products throughout the software development lifecycle. The platform provides real-time application security scanning with 100% coverage across the software supply chain, addressing risks in Static Application Security Testing (SAST), Software Composition Analysis (SCA), Infrastructure as Code (IaC), hardcoded secrets detection, and more. At its core, Arnica offers AI-native security governance that takes control of AI-generated code through advanced AI SAST scanning and agentic rules enforcement. The platform automatically injects centrally-controlled security requirements into AI coding agents like Copilot, Cursor, and Claude at the point of code generation, ensuring every line of AI-written code is secure by default before vulnerabilities reach production. This approach addresses 92% of risks before they ever reach production environments. Arnica's pipelineless architecture provides automatic coverage for every repository without requiring CI/CD pipeline integrations or IDE deployments. The platform scans every code change at the feature branch level, delivering developer-native workflows that keep teams focused on building features rather than chasing security issues. Risk prioritization is enhanced through OWASP Top 10, CVSS, EPSS, and KEV scoring, combined with organizational context to surface the most critical vulnerabilities. The platform excels in developer experience by delivering security findings directly within existing workflows through Slack, Microsoft Teams, pull request comments, and automated ticket management in Jira and Azure DevOps Boards. AI-powered mitigation suggestions provide context-aware, automated fixes that align with organizational coding standards, significantly reducing mean-time-to-remediation. Key security capabilities include real-time secrets detection with automatic validation and mitigation, comprehensive container scanning that maps vulnerabilities directly to source code, and intelligent dependency management with automated SCA upgrades. The platform maintains SOC 2 Type 2 compliance and ISO 27001 certification, ensuring enterprise-grade security standards. Arnica's unique value proposition lies in its ability to scale security across entire organizations while maintaining development velocity, providing complete visibility into code risks, and enabling proactive security measures that prevent vulnerabilities from reaching production environments.

Average Rating: 4.4/5.0

Total Reviews: 36

How Do G2 Users Rate Arnica?

  • Test Automation: 10.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.1/10)
  • Quality of Support: 8.8/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Arnica?

  • Seller: Arnica
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Alpharetta, Georgia
  • LinkedIn® Page: www.linkedin.com
    64 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Retail
  • Company Size: 62% Large, 22% Medium

What Do G2 Reviewers Say About Arnica?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the accuracy of findings from Arnica, effectively managing elevated privileges and reducing security risks.
  • Users value the actionable recommendations from Arnica, simplifying the removal of unused elevated privileges for enhanced security.
  • Users love the easy setup and administration of Arnica, saving time while meeting their needs effectively.
  • Users love the easy setup of Arnica, appreciating the quick and efficient administration process.
  • Users value Arnica for its ability to effectively remediate over-provisioning and enhance security without developer input.
Cons
  • Users note the limited access to features in Arnica for smaller teams not on GitHub Enterprise.

What Are Recent G2 Reviews of Arnica?

What Are G2 Users Discussing About Arnica?

OpenText Static Application Security Testing

OpenText™ Static Application Security Testing (SAST) is a comprehensive solution designed to identify and remediate security vulnerabilities within an application's source code during the early stages of development. By analyzing code from the "inside out," SAST provides immediate feedback to developers, enabling them to address security issues promptly and effectively. Key Features and Functionality: - Extensive Language Support: Supports over 33 programming languages and more than 1,400 vulnerability categories, ensuring broad applicability across various development environments. - Integration with Development Tools: Seamlessly integrates with popular Integrated Development Environments (IDEs) such as Eclipse, Visual Studio, and JetBrains, as well as Continuous Integration/Continuous Deployment (CI/CD) tools like Jenkins and Bamboo, facilitating a smooth incorporation into existing workflows. - Scalable Deployment Options: Offers flexible deployment models, including on-premises, cloud-based, and Software as a Service (SaaS) solutions, allowing organizations to choose the setup that best fits their needs. - Advanced Analysis Capabilities: Utilizes multiple algorithms and an expansive knowledge base of secure coding rules to perform thorough code analysis, pinpointing the root causes of vulnerabilities and providing detailed remediation guidance. Primary Value and Problem Solved: OpenText SAST empowers organizations to proactively manage application security by detecting and addressing vulnerabilities early in the Software Development Life Cycle (SDLC). This proactive approach reduces the risk of security breaches, minimizes the cost and effort associated with late-stage remediation, and enhances the overall security posture of applications. By integrating security testing into the development process, OpenText SAST helps developers create more secure code, leading to robust and reliable software products.

Average Rating: 4.5/5.0

Total Reviews: 21

How Do G2 Users Rate OpenText Static Application Security Testing?

  • Test Automation: 8.7/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.1/10)
  • Quality of Support: 8.7/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 7.0/10 (Category avg: 8.5/10)

Who Is the Company Behind OpenText Static Application Security Testing?

  • Seller: OpenText
  • Year Founded: 1991
  • HQ Location: Waterloo, ON
  • LinkedIn® Page: www.linkedin.com
    22,835 employees on LinkedIn®
  • Ownership: NASDAQ:OTEX
  • Phone: +1-519-888-7111

Who Uses This Product?

  • Top Industries: Financial Services, Banking
  • Company Size: 50% Large, 29% Small

What Do G2 Reviewers Say About OpenText Static Application Security Testing?

AI-generated summary from verified user reviews

Pros
  • Users value the easy integrations of OpenText Static Application Security Testing, enhancing workflow with various third-party tools.
  • Users value the extensive integration capabilities of OpenText Static Application Security Testing with various third-party tools.
  • Users value the extensive integration support of OpenText Static Application Security Testing with numerous languages and third-party tools.
Cons
  • Users dislike the false positives generated, but can manage them using the ignore feature in scans.

What Are Recent G2 Reviews of OpenText Static Application Security Testing?

What Are G2 Users Discussing About OpenText Static Application Security Testing?

Black Duck Polaris Platform

Black Duck builds trust in software by enabling organizations to manage application security, quality, and compliance risks at the speed their business demands. Black Duck solutions help developers to secure code as fast as they write it, development and DevSecOps teams to automate testing within development pipelines without compromising velocity, and security teams to proactively manage risk and focus remediation efforts on what matters most. With Black Duck, organizations can transform the way they build and deliver software, aligning people, processes, and technology to intelligently address software risks across their portfolio and at all stages of the application lifecycle.

Average Rating: 4.2/5.0

Total Reviews: 103

How Do G2 Users Rate Black Duck Polaris Platform?

  • Test Automation: 8.1/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.1/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.6/10 (Category avg: 8.5/10)

Who Is the Company Behind Black Duck Polaris Platform?

  • Seller: Black Duck
  • Year Founded: 2024
  • HQ Location: Burlington, US
  • LinkedIn® Page: www.linkedin.com
    1,317 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 53% Large, 32% Medium

What Do G2 Reviewers Say About Black Duck Polaris Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the accuracy of findings in Black Duck Polaris, especially its powerful engine for identifying open source issues.
  • Users praise the powerful open source issue identification by Black Duck Polaris, benefiting from extensive Black Duck Knowledge.
Cons
  • Users note that the platform requires huge resource constraints for on-prem deployment, impacting its usability.

What Are Recent G2 Reviews of Black Duck Polaris Platform?

What Are G2 Users Discussing About Black Duck Polaris Platform?

Kiuwan Code Security & Insights

Fast, Flexible Code Security! Kiuwan is a robust, end-to-end application security platform that integrates seamlessly into your development process. Our toolset includes Static Application Security Testing (SAST), Software Composition Analysis (SCA), Software Governance and Code Quality, empowering your team to quickly identify and remediate vulnerabilities. By integrating seamlessly into your CI/CD pipeline, Kiuwan enables early detection and remediation of security issues. Kiuwan supports strict compliance with industry standards including OWASP, CWE, MISRA, NIST, PCI DSS, and CERT, among others. Top features: ✅ Extensive language support: Over 30 programming languages. ✅ Detailed action plans: Prioritize remediation with tailored action plans. ✅ Code Security: Seamless Static Application Security Testing (SAST) integration. ✅ Insights: On-demand or continuous scanning Software Composition Analysis (SCA) to help reduce third-party threats. ✅ One-click Software Bill of Materials (SBOM) generation. Kiuwan is now part of Sembi - a global portfolio of market-leading software brands focused on software quality, security, and developer productivity. Code Smarter. Secure Faster. Ship Sooner

Average Rating: 4.5/5.0

Total Reviews: 29

How Do G2 Users Rate Kiuwan Code Security & Insights?

  • Test Automation: 9.4/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.1/10)
  • Quality of Support: 8.9/10 (Category avg: 9.2/10)
  • Source-Code Scanning: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Kiuwan Code Security & Insights?

  • Seller: Sembi
  • Company Website:
  • Year Founded: 2023
  • HQ Location: Austin, US
  • LinkedIn® Page: www.linkedin.com
    114 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Banking
  • Company Size: 41% Large, 35% Medium

What Do G2 Reviewers Say About Kiuwan Code Security & Insights?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of the results from Kiuwan, significantly enhancing their coding security measures.
  • Users appreciate the accuracy of findings from Kiuwan, ensuring reliable insights from code scans and reports.
  • Users praise the efficient customer support of Kiuwan, consistently resolving problems and enhancing user satisfaction.
  • Users value the user-friendly interface of Kiuwan Code Security & Insights, enhancing their overall experience and satisfaction.
  • Users appreciate the user-friendly automation testing of Kiuwan, enhancing their experience with efficient code scans and reporting.

What Are Recent G2 Reviews of Kiuwan Code Security & Insights?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024