Best Dynamic Application Security Testing (DAST) Software

How Many Dynamic Application Security Testing (DAST) Software Products Does G2 Track?

Total Products under this Category: 98

Category Stats (Sep 2026)

  • Average Rating: 4.58/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: AppSentinels (+0.89%) - Among all products in this category, AppSentinels recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Dynamic Application Security Testing (DAST) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,200+ Authentic Reviews
  • 98+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

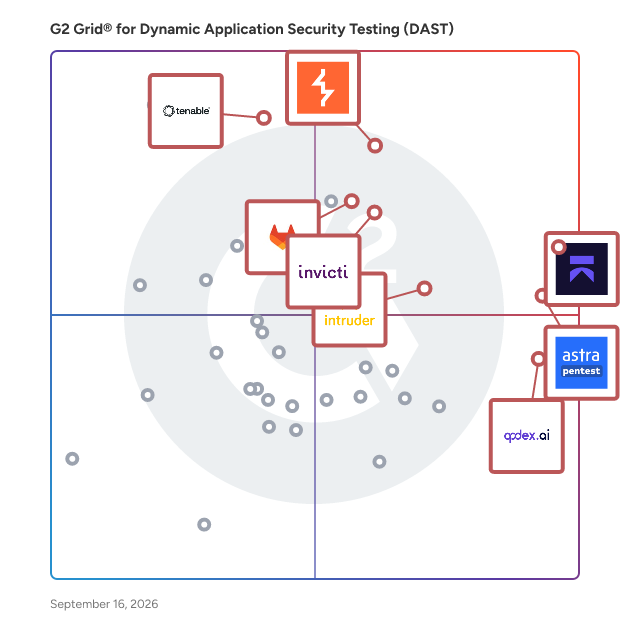
G2 Grid® for Dynamic Application Security Testing (DAST) Software

G2 Grid® for Dynamic Application Security Testing (DAST) Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, Astra Pentest, Burp Suite, Qodex.ai, Invicti, GitLab, Tenable Nessus, and Intruder.

Underlying data: [Grid® JSON](https://www.g2.com/categories/dynamic-application-security-testing-dast/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=astra-pentest&focus%5B%5D=burp-suite&focus%5B%5D=qodex-ai&focus%5B%5D=invicti&focus%5B%5D=gitlab&focus%5B%5D=tenable-nessus&focus%5B%5D=intruder)

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.6/5.0

Total Reviews: 262

How Do G2 Users Rate Aikido Security?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • API / Integrations: 8.3/10 (Category avg: 8.7/10)
  • Detection Rate: 10.0/10 (Category avg: 8.8/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • Twitter: @AikidoSecurity
    11,770 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 79% Small, 14% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

Astra Pentest

Astra Security is a leading continuous penetration testing platform that combines AI-powered autonomous pentesting with certified expert-led assessments. Powered by Attack AI, trained on 6.8M+ security findings and insights from 5,000+ real-world pentests. Astra deploys intelligent agents that continuously discover, validate, prioritize, and help remediate vulnerabilities at scale. While AI handles speed and scale, Astra’s certified security experts focus on what automation alone cannot: complex business logic flaws, multi-step attack chains, advanced exploit paths, and emerging AI/LLM-specific threats. Built for modern engineering teams, Astra integrates directly into CI/CD workflows, enabling continuous security validation between releases instead of relying on outdated annual pentests. The platform delivers comprehensive Autonomous Pentest powered by AI agents, DAST vulnerability scanner and human-driven pentests across web apps, AI/LLMs, mobile apps, APIs, cloud infrastructure. Astra is CREST-accredited, CERT-IN empaneled, and a PCI ASV-certified vendor. Our team also led the development of the OWASP APTS framework, helping shape the industry standard for continuous security testing. Today, 1,500+ organizations across 70+ countries trust Astra Security, including Ford, Loom, CompTIA, Hitachi, HackerRank, and OLX.

Average Rating: 4.6/5.0

Total Reviews: 238

G2 Deal: For G2 users: 10% off across all pentest plans

Avail Astra Pentest at 10% off, our comprehensive pentest suite scans for 8000+ security tests including OWASP Top 10, SANS 25, known CVEs & security best practices. This offer is exclusive to G2 users!

Price: ~~$5999~~ → $5400

View this exclusive G2 deal

How Do G2 Users Rate Astra Pentest?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • API / Integrations: 8.3/10 (Category avg: 8.7/10)
  • Detection Rate: 8.9/10 (Category avg: 8.8/10)
  • Test Automation: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Astra Pentest?

  • Seller: ASTRA IT, Inc.
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Bengaluru, IN
  • Twitter: @getastra
    694 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    154 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, CEO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 66% Small, 28% Medium

What Do G2 Reviewers Say About Astra Pentest?

AI-generated summary from verified user reviews

Pros
  • Users commend Astra Pentest's excellent customer support, noting their responsiveness and flexibility throughout the process.
  • Users praise the comprehensive vulnerability detection of Astra Pentest, which simplifies tracking and prioritizing security issues.
  • Users appreciate the user-friendly interface of Astra Pentest, enhancing their experience with clear and efficient vulnerability management.
  • Users commend Astra Pentest for its efficient scanning and penetration testing, enhancing security preparedness and team responsiveness.
  • Users value the vulnerability identification of Astra Pentest, enhancing confidence in security and business growth.
Cons
  • Users report poor customer support with Astra Pentest, noting slow email responses and lack of instant messaging options.
  • Users find the poor interface design of Astra Pentest frustrating, leading to confusion and difficulties in usage.
  • Users report slow performance with Astra Pentest, citing delays in results and instability during use.
  • Users find the UI challenging, particularly with note-taking and clarity on rescan needs during pentests.
  • Users face a lack of information with Astra Pentest, as documentation and updates are often insufficient or slow to arrive.

What Are Recent G2 Reviews of Astra Pentest?

What Are G2 Users Discussing About Astra Pentest?

Burp Suite

Burp Suite is a complete ecosystem for web application and API security testing, combining two products: Burp Suite DAST - a best-of-breed, precision DAST solution that automates runtime testing, and Burp Suite Professional - the industry-standard toolkit for manual penetration testing. Developed by PortSwigger, more than 85,000 security professionals rely on Burp Suite to find, verify, and understand vulnerabilities across complex modern web applications. Burp Suite DAST is PortSwigger’s enterprise dynamic application security testing (DAST) solution, purpose-built for continuous, automated scanning of web applications and APIs. Unlike many DAST solutions, which are part of a wider AST offering, Burp Suite DAST is not a bolt-on tool - instead it’s precision-built from over 20 years of dynamic testing experience. Burp Suite DAST reveals the runtime issues that static analysis tools miss, such as authentication flaws, configuration drift, and chained vulnerabilities. Built on the same proprietary scanning engine that powers Burp Suite Professional, it delivers precise, low-noise results that security teams trust. Key capabilities of Burp Suite DAST include: Continuous, automated scanning of web applications and APIs, integration with CI/CD pipelines and vulnerability management tools, flexible deployment across cloud, and on-premise environments, shared scanning logic and configurations between automated and manual testing, accurate, low-noise detection informed by PortSwigger Research. Burp Suite Professional complements DAST with deep manual testing capability. It’s the industry-standard toolkit for penetration testers, consultants, and AppSec engineers who need complete insight and flexibility when validating or exploring vulnerabilities. Findings discovered by DAST can be investigated and verified in Burp Suite Professional, ensuring every result is accurate, contextual, and actionable. Together, Burp Suite DAST and Burp Suite Professional create a unified ecosystem that delivers automation at breadth and manual depth where it counts. Burp Suite is built for AppSec teams who need scalable, trustworthy coverage across web and API environments, enabling a seamless handoff between automated and manual testing.

Average Rating: 4.8/5.0

Total Reviews: 126

How Do G2 Users Rate Burp Suite?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • API / Integrations: 8.3/10 (Category avg: 8.7/10)
  • Detection Rate: 7.2/10 (Category avg: 8.8/10)
  • Test Automation: 7.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Burp Suite?

  • Seller: PortSwigger
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Knutsford, GB
  • Twitter: @Burp_Suite
    138,186 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    345 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 41% Medium, 31% Small

What Do G2 Reviewers Say About Burp Suite?

AI-generated summary from verified user reviews

Pros
  • Users enjoy the user-friendly interface of Burp Suite, making navigation and analysis straightforward for all skill levels.
  • Users highlight the user-friendly interface of Burp Suite, making it easy to navigate and utilize effectively.
  • Users value the deep automation and manual testing capabilities of Burp Suite for effective security assessments.
  • Users appreciate the control and visibility Burp Suite offers, with powerful tools for effective web application testing.
  • Users praise Burp Suite for its clear, user-friendly interface that simplifies web application penetration testing for both beginners and experts.
Cons
  • Users find Burp Suite to be expensive, particularly for the professional version, which may limit accessibility for some users.
  • Users report slow performance with Burp Suite, particularly on lower-end systems during extensive scanning tasks.
  • Users find the steep learning curve of Burp Suite challenging, especially beginners navigating its complex features and tools.
  • Users find the steep learning curve in Burp Suite challenging, particularly for beginners adjusting to its complex setup.
  • Users find the limited customization in Burp Suite restricts exploration, especially for beginners and independent learners.

What Are Recent G2 Reviews of Burp Suite?

What Are G2 Users Discussing About Burp Suite?

Qodex.ai

Qodex is a continuous testing platform that runs your test scenarios against your real app on every pull request and deploy, then shows you exactly what broke with the failing request, response, and screenshot.

Average Rating: 4.9/5.0

Total Reviews: 60

How Do G2 Users Rate Qodex.ai?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • API / Integrations: 8.3/10 (Category avg: 8.7/10)
  • Detection Rate: 8.3/10 (Category avg: 8.8/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Qodex.ai?

  • Seller: QodexAI
  • Company Website:
  • Year Founded: 2023
  • HQ Location: San Francisco, California
  • LinkedIn® Page: linkedin.com
    13 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 75% Small, 20% Medium

What Do G2 Reviewers Say About Qodex.ai?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of Qodex.ai, enabling quick learning and efficient API testing for all skill levels.
  • Users appreciate the automation of testing in Qodex.ai, greatly reducing testing time and enhancing reliability.
  • Users value the easy interface for writing test cases, streamlining the testing process and enhancing efficiency.
  • Users appreciate the testing efficiency of Qodex.ai, streamlining the testing process and reducing shipment time significantly.
  • Users appreciate the effortless automation of Qodex.ai, which streamlines API testing and enhances team productivity.
Cons
  • Users note that the slow loading of the UI can hinder their experience and requires improvement.
  • Users find the poor documentation hampers their ability to fully utilize Qodex.ai's advanced features effectively.
  • Users report slow performance with Qodex.ai, noting delays in UI loading and chatbot response times.
  • Users report bug issues including repeated test cases, and suggest improvements in bug classification and accuracy.
  • Users report bugs related to test cases and suggest improvements for prioritizing and flagging issues effectively.

What Are Recent G2 Reviews of Qodex.ai?

Invicti

Invicti (formerly known as Netsparker) is an enterprise application and API security testing platform that helps organizations secure thousands of web applications and APIs at scale while dramatically reducing the risk of attack. Combining advanced DAST and IAST capabilities in a single platform, Invicti enables security teams to continuously identify, prioritize, and remediate vulnerabilities across complex modern environments with confidence and automation. With Invicti, security teams can: - Automate application security testing workflows and save hundreds of hours every month - Discover and secure all web applications and APIs, including forgotten, unmanaged, and shadow assets - Deliver actionable, developer-friendly feedback that helps teams remediate vulnerabilities faster and build more secure code over time - Reduce false positives with proof-based scanning technology that validates exploitable vulnerabilities - Scale application security programs across large enterprises without slowing development teams - Integrate security seamlessly into existing DevSecOps and CI/CD workflows Built for organizations with the most demanding security requirements, Invicti empowers teams to confidently secure their entire attack surface with accuracy, scalability, and automation.

Average Rating: 4.5/5.0

Total Reviews: 69

How Do G2 Users Rate Invicti?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • API / Integrations: 8.2/10 (Category avg: 8.7/10)
  • Detection Rate: 8.6/10 (Category avg: 8.8/10)
  • Test Automation: 8.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Invicti?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • Twitter: @InvictiSecurity
    2,557 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Large, 29% Medium

What Do G2 Reviewers Say About Invicti?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Invicti, facilitating quick setup and effective vulnerability scanning in their workflow.
  • Users value the quick and easy scanning technology of Invicti, enhancing workflow efficiency and accuracy in vulnerability detection.
  • Users value the simplicity and integration of Invicti, enhancing security measures through user-friendly report generation and detailed views.
  • Users value the easy-to-read and well-formatted reports from Invicti, enhancing efficiency and supporting ISO certification needs.
  • Users value the high accuracy and ease of use in Invicti's vulnerability detection, effectively identifying true issues.
Cons
  • Users find the customer support lacking, often experiencing slow responses and inadequate technical assistance.
  • Users experience slow performance during scans and setups, impacting overall efficiency and satisfaction.
  • Users experience slow scanning issues with Invicti, often leading to frustrating delays during the scanning process.
  • Users face API scanning issues with Invicti, limiting its effectiveness for their specific needs despite decent support.
  • Users find the complex setup of Invicti challenging initially, hindering their ability to quickly navigate configurations.

What Are Recent G2 Reviews of Invicti?

What Are G2 Users Discussing About Invicti?

GitLab

GitLab is the most comprehensive AI-Powered DevSecOps platform that enables software innovation by empowering development, security, and operations teams to build better software, faster. With GitLab, teams can create, deliver, and manage code quickly and continuously instead of managing disparate tools and scripts. GitLab helps your teams across the complete DevSecOps lifecycle, from developing, securing, and deploying software. What makes us truly different? - Flexibility: Consume as a service or manage your own deployment - Cloud-Agnostic: Deploy anywhere with no vendor lock-in - No rip and replace: Scale to a platform approach at your own pace

Average Rating: 4.5/5.0

Total Reviews: 885

How Do G2 Users Rate GitLab?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)
  • API / Integrations: 9.2/10 (Category avg: 8.7/10)
  • Detection Rate: 9.0/10 (Category avg: 8.8/10)
  • Test Automation: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind GitLab?

  • Seller: GitLab Inc.
  • Year Founded: 2014
  • HQ Location: San Francisco, California
  • Twitter: @gitlab
    171,534 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,431 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 37% Medium, 37% Small

What Do G2 Reviewers Say About GitLab?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use in GitLab, enjoying its all-in-one DevOps capabilities and intuitive interface.
  • Users value the all-encompassing features of GitLab, which enhance collaboration and streamline the DevOps workflow.
  • Users love the seamless CI/CD integration of GitLab, simplifying automation and collaboration in DevOps workflows.
  • Users value the seamless integrations in GitLab, resulting in efficient workflows and streamlined management across multiple functions.
  • Users praise the seamless CI/CD integration in GitLab, enhancing automation and collaboration within their DevOps workflow.
Cons
  • Users find the complexity of GitLab's setup and management to be a significant barrier to efficient use.
  • Users find the difficult learning curve of GitLab challenging due to its complex interface and YAML syntax.
  • Users find the interface confusing due to clutter and slow performance with large repositories, complicating their navigation.
  • Users find the complex user interface challenging, especially with slow performance and difficulties in navigation and management.
  • Users find the learning curve steep, particularly for those new to DevOps and managing extensive features.

What Are Recent G2 Reviews of GitLab?

What Are G2 Users Discussing About GitLab?

Tenable Nessus

Built for security practitioners, by security professionals, Nessus products by Tenable are the de-facto industry standard for vulnerability assessment. Nessus performs point-in-time assessments to help security professionals quickly and easily identify and fix vulnerabilities, including software flaws, missing patches, malware, and misconfigurations - across a variety of operating systems, devices, and applications. With features such as pre-built policies and templates, customizable reporting, group “snooze” functionality, and real-time updates, Nessus is designed to make vulnerability assessment simple, easy, and intuitive. The result: less time and effort to assess, prioritize, and remediate issues.

Average Rating: 4.5/5.0

Total Reviews: 293

How Do G2 Users Rate Tenable Nessus?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)

Who Is the Company Behind Tenable Nessus?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Who Uses This: Security Engineer, Network Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 33% Large

What Do G2 Reviewers Say About Tenable Nessus?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the extensive vulnerability identification capabilities of Tenable Nessus, enhancing their security risk management efforts.
  • Users value the comprehensive vulnerability detection in Tenable Nessus, enhancing their ability to manage security risks effectively.
  • Users praise the automated scanning of Tenable Nessus for its thoroughness and comprehensive vulnerability reporting.
  • Users value the ease of use of Tenable Nessus, appreciating its simple setup and user-friendly interface.
  • Users value the extensive reporting and automation capabilities of Tenable Nessus for better asset scanning.
Cons
  • Users note that slow scanning can take 2-3 days and may disrupt production environments due to high resource usage.
  • Users highlight the high costs of maintaining Tenable Nessus, which can be a barrier for many organizations.
  • Users find the limited features of Tenable Nessus restrictive, especially regarding host capacity and mobile app testing.
  • Users find the complexity of licensing and features in Tenable Nessus challenging, impacting overall usability and resource management.
  • Users report that false positives from Nessus can create additional workload and complicate vulnerability management processes.

What Are Recent G2 Reviews of Tenable Nessus?

What Are G2 Users Discussing About Tenable Nessus?

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 219

How Do G2 Users Rate Intruder?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • API / Integrations: 8.9/10 (Category avg: 8.7/10)
  • Detection Rate: 9.5/10 (Category avg: 8.8/10)
  • Test Automation: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • Twitter: @intruder_io
    979 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Intruder, with quick setup and intuitive system design enhancing their experience.
  • Users value the clarity and prioritization of Intruder's findings, enabling effective risk management and actionable insights.
  • Users value the quick and efficient customer support from Intruder, enhancing their overall scanning experience.
  • Users appreciate the intuitive interface of Intruder, finding it easy to set up and navigate.
  • Users value the efficient vulnerability identification from Intruder, enhancing their cybersecurity management effortlessly.
Cons
  • Users find the product expensive due to high costs for add-ons and fees per endpoint scanned.
  • Users find the slow scanning process frustrating, leading to inefficiencies and missed vulnerabilities during security assessments.
  • Users find licensing issues challenging, particularly regarding costs and constraints that affect system configurations.
  • Users experience false positives which can obscure the detection of critical vulnerabilities in security monitoring.
  • Users find the limited features of Intruder less accommodating for specific reporting and customization needs.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

Harness Platform

Simplify your developer experience with the world's first AI-augmented software delivery platform. Upgrade your software delivery with Harness' innovative CI/CD, Feature Flags, Infrastructure as Code Management, and Chaos Engineering tools. We are a software delivery platform that helps developers and infrastructure engineers build and ship code for cloud and on-premise projects. We automate the continuous integration and continuous delivery (CI/CD) process to help teams build faster, ship more frequently, and improve quality, efficiency, and governance. We help companies in four key areas: Number one, we accelerate innovation through DevOps modernization. We provide an approach for software delivery that automates processes, reduces manual interventions, consolidates tools, and accelerates time-to-market for new products, features, and fixes. Number two, we improve developer experience. We give you the ability to attract, retain, and onboard high-caliber engineering talent while fostering a culture of continuous innovation and improvement. Number three, we secure software delivery. We give you the ability to integrate security into every phase of the SDLC. And last but not least is, we optimize cloud costs. We give you the ability to eliminate waste and to ensure that appropriate cloud resources are allocated at the right place at the right time.

Average Rating: 4.6/5.0

Total Reviews: 328

How Do G2 Users Rate Harness Platform?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Detection Rate: 10.0/10 (Category avg: 8.8/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Harness Platform?

  • Seller: Harness
  • Company Website:
  • Year Founded: 2018
  • HQ Location: San Francisco
  • Twitter: @HarnessWealth
    1,389 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,832 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Computer Software, Financial Services
  • Company Size: 41% Large, 40% Medium

What Do G2 Reviewers Say About Harness Platform?

AI-generated summary from verified user reviews

Pros
  • Users find the ease of use of Harness Platform essential for streamlining their development projects effectively.
  • Users highlight the easy integration and comprehensive documentation of Harness Platform, streamlining project implementation and feature management.
  • Users value the ease of managing feature flags across environments, enhancing flexibility and control in deployment.
  • Users appreciate the easy setup of Harness Platform, allowing quick implementation of feature flags and A/B testing.
  • Users find the easy integrations in Harness Platform enhance their workflow and improve productivity significantly.
Cons
  • Users note the missing features in Harness Platform, particularly regarding multiple filters and flexibility compared to other tools.
  • Users find the activation and deactivation clarity lacking, causing confusion in managing feature flags effectively.
  • Users express frustration over limited features, including SDK options and difficulties with traffic splitting and flag management.
  • Users note a steep learning curve with Harness Platform, requiring time to master its extensive features and tools.
  • Users criticize the poor UI of Harness Platform, finding it difficult to manage feature flags effectively.

What Are Recent G2 Reviews of Harness Platform?

What Are G2 Users Discussing About Harness Platform?

HCL AppScan

HCL AppScan is a comprehensive suite of market-leading application security testing solutions (SAST, DAST, IAST, SCA, API), available on-premises and on-cloud. These powerful DevSecOps tools pinpoint application vulnerabilities, allowing for quick remediation in every phase of the software development lifecycle. Fast and Accurate Scanning for Secure DevOps Developers and DevOps teams can quickly and accurately scan code, applications, and APIs for security vulnerabilities while applications are being developed. This allows companies to fix issues at the earliest stages of the software development lifecycle, when it is least costly to the business. Focus on the Fix Continuous monitoring with IAST, along with auto issue correlation with DAST and SAST scan results allows DevOps teams to group and prioritize findings for faster, more streamlined remediation. Enterprise Management for Security Teams Centralized, easy-to-use dashboards provide visibility and oversight of all security scanning and remediation, and allow users to set scan parameters and compliance policies.

Average Rating: 4.1/5.0

Total Reviews: 87

How Do G2 Users Rate HCL AppScan?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • API / Integrations: 8.3/10 (Category avg: 8.7/10)
  • Detection Rate: 8.3/10 (Category avg: 8.8/10)
  • Test Automation: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind HCL AppScan?

  • Seller: HCL Technologies
  • Company Website:
  • Year Founded: 1999
  • HQ Location: Noida, Uttar Pradesh
  • Twitter: @hcltech
    425,043 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    258,955 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 53% Large, 27% Small

What Are Recent G2 Reviews of HCL AppScan?

What Are G2 Users Discussing About HCL AppScan?

Checkmarx

Checkmarx offers leading application security solutions that help organizations safeguard software development while enhancing efficiency and reducing costs. At the center is Checkmarx Fusion, the highest-fidelity scanning architecture in the industry. Most scanners force a choice: catch more, or get buried in noise and miss what matters. Fusion ends that trade-off — deterministic precision and frontier AI coverage fused into one verified result, with the Findings Analysis Engine validating and deduplicating every finding before a developer sees it. The result is an F1 score of 0.64 today by using the Checkmarx NG SAST vs. an industry average of ~0.20, and an astonishing market leading F1 score of 0.74 with Checkmarx Fusion. The Checkmarx One platform stands out in the realm of enterprise-grade security, offering comprehensive protection that addresses the complexities of modern software development, including legacy systems and AI-generated code. By scanning trillions of lines of code annually, Checkmarx enables companies to significantly lower their vulnerability density, ensuring a robust defense against potential threats. The platform is particularly beneficial for software development teams, security professionals, and organizations that prioritize secure coding practices. Checkmarx One provides essential tools to mitigate risks associated with both traditional and emerging programming languages. Its innovative architecture, powered by autonomous security agents and AI-native intelligence, allows organizations to integrate security seamlessly into their development workflows, thereby accelerating development velocity without compromising on safety. Key features of Checkmarx One include Triage Assist, which employs an autonomous AI agent to prioritize vulnerabilities based on real-world exploitability and contextual risk. This feature empowers teams to concentrate their efforts on the most critical issues rather than getting bogged down by static severity scores. Additionally, Remediation Assist generates review-ready fixes for validated vulnerabilities prior to code merges, streamlining the secure delivery process and minimizing the manual overhead typically associated with remediation tasks. Developer Assist is another notable feature, acting as a standalone security agent that identifies risks during the coding process. By providing safe, explainable, and verified fixes directly within the integrated development environment (IDE), it supports developers in maintaining a stable and rapid development pace. Furthermore, the platform includes AI Supply Chain Security, which offers centralized governance and visibility for AI components embedded in applications, ensuring that hidden AI assets are discovered and managed effectively. Lastly, Checkmarx One incorporates advanced analysis engines such as NG SAST and DAST for AI, which enhance security measures across various environments. The AI SAST feature expands detection capabilities to cover emerging and unsupported programming languages, while the DAST for AI strengthens runtime protection in continuous integration and deployment (CI/CD) settings. Together, these features position Checkmarx One as a comprehensive solution for organizations looking to fortify their software development lifecycle against evolving threats.

Average Rating: 4.2/5.0

Total Reviews: 45

How Do G2 Users Rate Checkmarx?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • API / Integrations: 9.2/10 (Category avg: 8.7/10)
  • Detection Rate: 7.5/10 (Category avg: 8.8/10)
  • Test Automation: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Checkmarx?

  • Seller: Checkmarx
  • Company Website:
  • Year Founded: 2006
  • HQ Location: Paramus, NJ
  • Twitter: @Checkmarx
    7,284 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    997 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 57% Large, 22% Medium

What Do G2 Reviewers Say About Checkmarx?

AI-generated summary from verified user reviews

Pros
  • Users value the easy implementation of Checkmarx into existing repositories, enhancing their security review processes effortlessly.
  • Users praise the intuitive user interface of Checkmarx, making security reviews and integrations straightforward and user-friendly.
  • Users value the accuracy of results in Checkmarx, finding it effective for automated security reviews.
  • Users appreciate the automation testing capabilities of Checkmarx, making security reviews efficient and user-friendly.
  • Users praise the responsive customer support of Checkmarx, consistently providing help when challenges arise.
Cons
  • Users experience a significant number of false positives with Checkmarx, particularly for Kotlin projects, leading to frustration.
  • Users face challenges with limited support for Kotlin, experiencing many false positives compared to other languages like Java or Javascript.
  • Users experience missing features in Checkmarx, particularly with Kotlin support, leading to numerous false positives.
  • Users find the navigation poor in Checkmarx, citing issues with dashboard layout and display clarity.

What Are Recent G2 Reviews of Checkmarx?

What Are G2 Users Discussing About Checkmarx?

Cobalt

Cobalt is the pioneer in pentesting as a service (PTaaS) and a leader in continuous offensive security testing grounded in human expertise. The Cobalt Offensive Security Platform spans the full spectrum of offensive security, from targeted, human-led pentesting to high-frequency, AI-driven autonomous security testing. Only Cobalt brings together the four critical elements of modern offensive security: elite human expertise, a context-aware platform, AI-powered orchestration, and the industry's largest dataset of real-world pentest results. Thousands of customers and hundreds of partners rely on Cobalt and its global network of 500+ vetted security experts to continuously identify, prioritize, and remediate exploitable risk with the speed, flexibility, and precision today's organizations require.

Average Rating: 4.5/5.0

Total Reviews: 179

How Do G2 Users Rate Cobalt?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • API / Integrations: 8.6/10 (Category avg: 8.7/10)
  • Detection Rate: 8.6/10 (Category avg: 8.8/10)
  • Test Automation: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Cobalt?

  • Seller: Cobalt
  • Company Website:
  • Year Founded: 2013
  • HQ Location: San Francisco, California
  • Twitter: @cobalt_io
    8,462 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    597 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Security Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 52% Medium, 23% Small

What Do G2 Reviewers Say About Cobalt?

AI-generated summary from verified user reviews

Pros
  • Users value the immediate reports and seamless experience provided by Cobalt during quick external pentests.
  • Users greatly appreciate Cobalt's exceptional customer support, making troubleshooting smooth and efficient with expert assistance readily available.
  • Users praise the ease of use of Cobalt, appreciating its seamless setup and effective reporting capabilities.
  • Users praise Cobalt for its strong communication throughout the process, ensuring transparency and collaboration with pentesters.
  • Users praise the immediate reporting quality of Cobalt, enhancing ease and efficiency in external pentests.
Cons
  • Users find Cobalt to be expensive, especially for small organizations and when integrating with existing systems.
  • Users find Cobalt's limited scope inadequately addresses critical testing needs, resulting in superficial evaluations and missed vulnerabilities.
  • Users find the lack of detail in instructions hampers effective testing, leading to confusion during setup.
  • Users find pricing issues with Cobalt, noting confusion and the desire for clearer models and fewer upcharges.
  • Users often face inaccuracies in audit scoping that hinder efficiency and lead to repeated issues in reports.

What Are Recent G2 Reviews of Cobalt?

What Are G2 Users Discussing About Cobalt?

Pynt - API Security Testing

Pynt is an innovative API Security Testing platform exposing verified API threats through simulated attacks. Hundreds of companies rely on Pynt to continuously monitor, classify and attack poorly secured APIs, before hackers do.

Average Rating: 4.8/5.0

Total Reviews: 44

How Do G2 Users Rate Pynt - API Security Testing?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • API / Integrations: 9.5/10 (Category avg: 8.7/10)
  • Detection Rate: 9.3/10 (Category avg: 8.8/10)
  • Test Automation: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind Pynt - API Security Testing?

  • Seller: Pynt
  • Year Founded: 2022
  • HQ Location: Tel Aviv, IL
  • Twitter: @pynt_io
    361 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    13 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Computer & Network Security
  • Company Size: 57% Small, 23% Large

What Do G2 Reviewers Say About Pynt - API Security Testing?

AI-generated summary from verified user reviews

Pros
  • Users value the flawless execution of vulnerability detection in Pynt, making security tests effortless and efficient.
  • Users value Pynt for its impressive security capabilities, quickly identifying and addressing critical vulnerabilities in API testing.
  • Users value the seamless integration of Pynt for API security, simplifying the process of securing APIs during development.
  • Users love Pynt for its easy integrations, streamlining API security testing with minimal effort and maximum efficiency.
  • Users appreciate the automation of API security testing with Pynt, enhancing efficiency and integrating seamlessly into workflows.
Cons
  • Users often find the complex setup challenging initially, impacting the integration experience with Pynt.
  • Users find the setup complexity challenging, especially for beginners, leading to potential conflicts and a less user-friendly experience.
  • Users find Pynt's limited features lacking, particularly in reporting and dashboard capabilities for managing multiple APIs.
  • Users find the poor interface design of Pynt frustrating, suggesting it needs significant improvements for better usability.
  • Users find the user interface needs significant improvement, which affects their overall experience with Pynt.

What Are Recent G2 Reviews of Pynt - API Security Testing?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

How Do G2 Users Rate Edgescan?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • API / Integrations: 8.0/10 (Category avg: 8.7/10)
  • Detection Rate: 9.2/10 (Category avg: 8.8/10)
  • Test Automation: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • Twitter: @edgescan
    2,256 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    90 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, highlighting its intuitive interface and straightforward navigation.
  • Users value the automated vulnerability detection features of Edgescan for efficient risk assessment and remediation support.
  • Users value the excellent customer support from Edgescan, noting their responsiveness and proactivity in addressing queries.
  • Users value the detailed vulnerability identification from Edgescan, enabling effective risk management and threat mitigation strategies.
  • Users value Edgescan for its intuitive interface and comprehensive functionality that streamlines security assessments and support.
Cons
  • Users find the complex UI of Edgescan challenging, often requiring guidance to navigate key functions effectively.
  • Users find limited customization options frustrating, particularly with filtering systems and administrative functionalities.
  • Users find the poor interface design of Edgescan challenging, causing navigation and task completion difficulties.
  • Users experience slow performance with Edgescan as manual reviews lead to longer scan completion times.
  • Users find the user interface challenging and unintuitive, leading to difficulties in navigation and task completion.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?

BugDazz API Scanner

BugDazz API Security Scanner by SecureLayer7 is a comprehensive tool designed to automatically detect vulnerabilities, misconfigurations, and security gaps in API endpoints, aiding security teams in protecting digital assets against increasing API-related threats and potential exploits. It offers real-time scanning capabilities, enabling the automatic detection of vulnerabilities as they arise. It supports authentication and access control management, allowing for the management of API controls within a single platform. BugDazz assists in achieving compliance by accelerating the generation of reports for standards such as PCI DSS and HIPAA. It integrates seamlessly with existing CI/CD pipelines, facilitating the acceleration of product rollouts. The scanner goes beyond standard OWASP Top 10 vulnerabilities, providing comprehensive protection against critical API security risks.

Average Rating: 4.9/5.0

Total Reviews: 11

How Do G2 Users Rate BugDazz API Scanner?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • API / Integrations: 10.0/10 (Category avg: 8.7/10)
  • Detection Rate: 9.3/10 (Category avg: 8.8/10)
  • Test Automation: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind BugDazz API Scanner?

  • Seller: SecureLayer7
  • Year Founded: 2012
  • HQ Location: Pune, Maharshtra
  • Twitter: @SecureLayer7
    2,522 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    122 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 91% Small, 9% Medium

What Do G2 Reviewers Say About BugDazz API Scanner?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of results from BugDazz API Scanner, enhancing collaboration and efficiency in workflow processes.
  • Users love the smooth integration with CI/CD pipelines, enabling efficient and timely security scans without delays.
  • Users value the seamless CI/CD integration of BugDazz API Scanner, enhancing efficiency without slowing down builds.
  • Users appreciate the ease of use of BugDazz API Scanner, facilitating quick integration and reliable results.
  • Users value the fast and accurate scans of BugDazz, seamlessly integrating into CI/CD workflows with minimal friction.
Cons
  • Users find documentation lacking, particularly in infrastructure guidance and clarity for Jerkins integration.
  • Users acknowledge a difficult learning curve with BugDazz API Scanner, requiring time to optimize scan configurations effectively.
  • Users suggest that the lack of guidance in documentation hinders effective usage of BugDazz API Scanner.
  • Users find the lack of detailed information in BugDazz API Scanner's documentation limiting for infrastructure-specific guidance.
  • Users note a learning curve in optimizing scans for various scenarios, but find it manageable overall.

What Are Recent G2 Reviews of BugDazz API Scanner?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024

Learn More About Dynamic Application Security Testing (DAST) Software

What is Dynamic Application Security Testing (DAST) Software?

Dynamic application security testing (DAST) is one of the many technology groupings of security testing solutions. DAST is a form of black-box security testing, meaning it simulates realistic threats and attacks. This differs from other forms of testing such as static application security testing (SAST), a white-box testing methodology used to examine the source code of an application.

DAST includes a number of testing components that operate while an application is running. Security professionals simulate real-world functionality through testing the application for vulnerabilities and then evaluate the effects on application performance. The methodology is often used to find issues near the end of the software development lifecycle. These issues may be tougher to fix than early flaws and bugs are, but those flaws pose a larger threat to critical components of an application.

DAST can also be thought of as a methodology. It’s a different approach than traditional security testing because once a test is completed, there are still tests to be done. It involves periodic inspections as updates are pushed live or changes are made before release. While a penetration test or code scan might serve as a one-off test for specific vulnerabilities or bugs, dynamic testing can be performed continually throughout the lifecycle of an application.

Key Benefits of Dynamic Application Security Testing (DAST) Software

  • Simulate realistic attacks and threats
  • Discover vulnerabilities not found in source code
  • Flexible and customizable testing options
  • Comprehensive assessment and scalable testing

Why Use Dynamic Application Security Testing (DAST) Software?

There are a number of testing solutions necessary for an all-encompassing approach to security testing and vulnerability discovery. Most start in the early stages of software development and help programmers discover bugs in the code and issues with the underlying framework or design. These tests require access to source code and are often used during development and quality assurance (QA) processes.

While early testing solutions approach testing from the standpoint of the developer, DAST approaches testing from the standpoint of a hacker. These tools simulate real threats to a functional, running application. Security professionals can simulate common attacks such as SQL injection and cross-site scripting or customize tests to threats specific to their product. These tools offer a highly customizable solution for testing during the later stages of development and while applications are deployed.

Flexibility — Users can schedule tests as they please or perform them continuously throughout an application’s or website’s lifecycle. Security professionals can modify environments to simulate their resources and infrastructure to ensure a realistic test and evaluation. They’re often scalable, as well, to see if increased traffic or usage would affect vulnerabilities and protection.

Industries with more specific threats may require more specific testing. Security professionals may identify a threat specific to the health care industry or financial sector and alter tests to simulate the threats most common to them. If performed correctly, these tools offer some of the most realistic and customizable solutions to the threats present in real-world situations.

Comprehensiveness — Threats are continuously evolving and expanding, making the ability to simulate multiple tests more necessary. DAST offers a versatile approach to testing, wherein security professionals can simulate and analyze each threat or attack type individually. These tests deliver comprehensive feedback and actionable insights that security and development teams use to remediate any issues, flaws, and vulnerabilities.

These tools will first perform an initial crawl, or examination, of applications and websites from a third-party perspective. They interact with applications using HTTP, allowing the tools to examine applications built with any programming language or on any framework. The tool will then test for misconfigurations, which expose a greater attack surface than internal vulnerabilities. Additional tests can be run, depending on the solution, but all the results and discoveries can be stored for actionable remediation.

Continuous assessment — Agile teams and other companies relying on frequent updates to applications should use DAST products with continuous assessment capabilities. SAST tools will provide more direct solutions for issues related to continuous integration processes, but DAST tools will provide a better view of how updates and changes will be seen from an outside perspective. Each new update may pose a new threat or unveil a new vulnerability; it is therefore crucial to continue testing even after applications have been completed and deployed.

Unlike SAST, DAST also requires less access to potentially sensitive source code within the application. DAST approaches the situation from an outside perspective as simulated threats attempt to gain access to vulnerable systems or sensitive information. This can make it easier to perform tests continuously without requiring individuals to access source code or other internal systems.

What are the Common Features of Dynamic Application Security Testing (DAST) Software?

Standard functionality is included in most dynamic application security testing (DAST) solutions:

Compliance testing — Compliance testing gives users the ability to test for various requirements from regulatory bodies. This can help ensure information is stored securely and protected from hackers.

Test automation — Test automation is the feature powering continuous testing processes. This functionality operates by running prescripted tests as frequently as required without the need for hands-on or manual testing.

Manual testing — Manual testing gives the user complete control over individual tests. These features allow users to perform hands-on live simulations and penetration tests.

Command-line tools — The command-line interface (CLI) is the language interpreter of a computer. CLI capabilities will allow security testers to simulate threats directly from the terminal host system and input command sequences.

Static code analysis — Static code analysis and static security testing is used to test from the inside out. These tools help security professionals examine application source code for security flaws without executing it.

Issue tracking — Issue tracking helps security professionals and developers document flaws or vulnerabilities as they are discovered. Proper documentation will make it easier to organize the actionable insights provided by the DAST tool.

Reporting and analytics — Reporting capabilities are important to DAST tools because they provide the information necessary to remediate any recently discovered vulnerabilities. Reporting and analytics features can also give teams a better idea of how attacks may affect application availability and performance.

Extensibility — Many applications offer the ability to expand functionality through the use of integrations, APIs, and plugins. These extensible components provide the ability to extend the platform beyond its native feature set to include additional features and functionalities.


Potential Issues with Dynamic Application Security Testing (DAST) Software

Testing coverage — While DAST technologies have come a long way, DAST tools alone are unable to discover the majority of vulnerabilities. This is why most experts suggest pairing them with SAST solutions. Combining the two can decrease the rate at which false positives occur. They can also be used to simplify the continuous testing process for agile teams. While no tool will detect every vulnerability, DAST may be less efficient than other testing tools if used alone.

Late-stage issues — DAST tools will require code to be compiled for each individual test because they rely on simulated functionality to test responses. This can be a roadblock for agile teams constantly integrating new code into an application. Reports are usually static and result from single tests. For agile teams, those reports can become outdated and lose value very quickly. This is just one more reason DAST tools should be used as a component of an all-encompassing security testing stack rather than a standalone solution.

Testing capabilities — Because DAST tools do not access an application's underlying source code, there are a number of flaws DAST tools will be unable to detect. For example, DAST tools are most effective at simulating reflection, or call-and-response, attacks where they can simulate an input and receive a response. They are not, however, highly effective in discovering smaller vulnerabilities or flaws in areas of the application that are rarely touched by users. These issues, as well as vulnerabilities in the original source code, will need to be addressed by additional security testing technologies.