Best Vulnerability Scanner Software

How Many Vulnerability Scanner Software Products Does G2 Track?

Total Products under this Category: 238

Category Stats (Sep 2026)

  • Average Rating: 4.59/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+0.97%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Vulnerability Scanner Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 7,900+ Authentic Reviews
  • 238+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

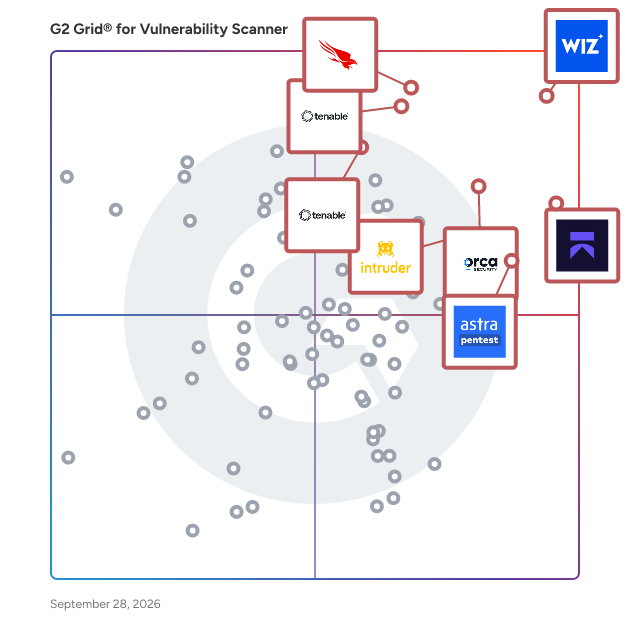
G2 Grid® for Vulnerability Scanner Software

G2 Grid® for Vulnerability Scanner Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, CrowdStrike Falcon Cloud Security, Tenable Nessus, Orca Security, Astra Pentest, Intruder, and Tenable Vulnerability Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vulnerability-scanner/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=tenable-nessus&focus%5B%5D=orca-security&focus%5B%5D=astra-pentest&focus%5B%5D=intruder&focus%5B%5D=tenable-vulnerability-management)

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 841

How Do G2 Users Rate Wiz?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Detection Rate: 8.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Wiz?

  • Seller: Wiz
  • Company Website:
  • Year Founded: 2020
  • HQ Location: New York, US
  • Twitter: @wiz_io
    24,733 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,147 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CISO, Security Engineer
  • Top Industries: Financial Services, Computer Software
  • Company Size: 53% Large, 39% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users value the robust APIs and user-friendly UI, appreciating ongoing improvements and a wealth of insightful issues.
  • Users value the continuous enhancement of security features by Wiz, appreciating the support and innovation in their tool.
  • Users appreciate the ease of use of Wiz, benefiting from its user-friendly interface and seamless integration.
  • Users value the comprehensive visibility Wiz provides, enhancing security and prioritizing essential aspects of their cloud environment.
  • Users appreciate the easy setup of Wiz, enabling a quick and seamless integration into their workflows.
Cons
  • Users find a significant learning curve in mastering Wiz's extensive features, which can hinder initial usage.
  • Users find the feature limitations of Wiz frustrating, especially with complex management and reporting challenges.
  • Users note that improvement is needed for laggy query responses and better dashboard reporting capabilities.
  • Users identify improvements needed in dashboard reporting and feature streamlining for better usability and budgeting.
  • Users find the interface overwhelming initially, facing a steep learning curve and complex licensing issues.

What Are Recent G2 Reviews of Wiz?

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.6/5.0

Total Reviews: 265

How Do G2 Users Rate Aikido Security?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 9.0/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.1/10 (Category avg: 8.5/10)

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • Twitter: @AikidoSecurity
    11,770 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 216

How Do G2 Users Rate CrowdStrike Falcon Cloud Security?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Detection Rate: 8.6/10 (Category avg: 9.0/10)
  • Automated Scans: 9.7/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.2/10 (Category avg: 8.5/10)

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 48% Large, 33% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

Tenable Nessus

Built for security practitioners, by security professionals, Nessus products by Tenable are the de-facto industry standard for vulnerability assessment. Nessus performs point-in-time assessments to help security professionals quickly and easily identify and fix vulnerabilities, including software flaws, missing patches, malware, and misconfigurations - across a variety of operating systems, devices, and applications. With features such as pre-built policies and templates, customizable reporting, group “snooze” functionality, and real-time updates, Nessus is designed to make vulnerability assessment simple, easy, and intuitive. The result: less time and effort to assess, prioritize, and remediate issues.

Average Rating: 4.5/5.0

Total Reviews: 296

How Do G2 Users Rate Tenable Nessus?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Detection Rate: 8.9/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.4/10 (Category avg: 8.5/10)

Who Is the Company Behind Tenable Nessus?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Who Uses This: Security Engineer, Network Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 33% Large

What Do G2 Reviewers Say About Tenable Nessus?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the extensive vulnerability identification capabilities of Tenable Nessus, enhancing their security risk management efforts.
  • Users value the comprehensive vulnerability detection in Tenable Nessus, enhancing their ability to manage security risks effectively.
  • Users praise the automated scanning of Tenable Nessus for its thoroughness and comprehensive vulnerability reporting.
  • Users value the ease of use of Tenable Nessus, appreciating its simple setup and user-friendly interface.
  • Users value the extensive reporting and automation capabilities of Tenable Nessus for better asset scanning.
Cons
  • Users note that slow scanning can take 2-3 days and may disrupt production environments due to high resource usage.
  • Users highlight the high costs of maintaining Tenable Nessus, which can be a barrier for many organizations.
  • Users find the limited features of Tenable Nessus restrictive, especially regarding host capacity and mobile app testing.
  • Users find the complexity of licensing and features in Tenable Nessus challenging, impacting overall usability and resource management.
  • Users report that false positives from Nessus can create additional workload and complicate vulnerability management processes.

What Are Recent G2 Reviews of Tenable Nessus?

What Are G2 Users Discussing About Tenable Nessus?

Orca Security

The Orca Cloud Security Platform identifies, prioritizes, and remediates risks and compliance issues in workloads, configurations, and identities across your cloud estate spanning AWS, Azure, Google Cloud, Kubernetes, Alibaba Cloud, and Oracle Cloud. Orca offers the industry’s most comprehensive cloud security solution in a single platform — eliminating the need to deploy and maintain multiple point solutions. Orca is agentless-first, and connects to your environment in minutes using Orca’s patented SideScanning™ technology that provides deep and wide visibility into your cloud environment, without requiring agents. In addition, Orca can integrate with third-party agents for runtime visibility and protection for critical workloads. Orca is at the forefront of leveraging Generative AI for simplified investigations and accelerated remediation – reducing required skill levels and saving cloud security, DevOps, and development teams time and effort, while significantly improving security outcomes. As a Cloud Native Application Protection Platform (CNAPP), Orca consolidates many point solutions in one platform, including: CSPM, CWPP, CIEM, Vulnerability Management, Container and Kubernetes Security, DSPM, API Security, CDR, Multi-cloud Compliance, Shift Left Security, and AI-SPM.

Average Rating: 4.7/5.0

Total Reviews: 312

How Do G2 Users Rate Orca Security?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Detection Rate: 8.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Orca Security?

  • Seller: Orca Security
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Portland, Oregon
  • Twitter: @orcasec
    4,835 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    523 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, CISO
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 53% Large, 36% Medium

What Do G2 Reviewers Say About Orca Security?

AI-generated summary from verified user reviews

Pros
  • Users highly value the ease of use of Orca Security, enabling quick setup and intuitive navigation.
  • Users value the great visibility provided by Orca Security, enabling effective vulnerability management and prioritization of alerts.
  • Users value the agentless feature and intuitive interface of Orca Security, enhancing their security management experience.
  • Users praise the visibility provided by Orca Security, gaining comprehensive insights into their cloud environment effortlessly.
  • Users praise Orca Security for its comprehensive security features, offering great visibility and ease of implementation.
Cons
  • Users express concerns about security vulnerabilities, especially regarding API security and detection of vulnerable packages.
  • Users experience dashboard issues like clutter, slow performance, and quirks that hinder efficient navigation and usability.
  • Users face challenges with delayed detection of vulnerabilities, impacting timely response and troubleshooting efforts in Orca Security.
  • Users report many false positives, complicating the assessment of actual vulnerabilities in Orca Security.
  • Users note that the reporting capabilities and customization options of Orca Security need significant improvement.

What Are Recent G2 Reviews of Orca Security?

What Are G2 Users Discussing About Orca Security?

Astra Pentest

Astra Security is a leading continuous penetration testing platform that combines AI-powered autonomous pentesting with certified expert-led assessments. Powered by Attack AI, trained on 6.8M+ security findings and insights from 5,000+ real-world pentests. Astra deploys intelligent agents that continuously discover, validate, prioritize, and help remediate vulnerabilities at scale. While AI handles speed and scale, Astra’s certified security experts focus on what automation alone cannot: complex business logic flaws, multi-step attack chains, advanced exploit paths, and emerging AI/LLM-specific threats. Built for modern engineering teams, Astra integrates directly into CI/CD workflows, enabling continuous security validation between releases instead of relying on outdated annual pentests. The platform delivers comprehensive Autonomous Pentest powered by AI agents, DAST vulnerability scanner and human-driven pentests across web apps, AI/LLMs, mobile apps, APIs, cloud infrastructure. Astra is CREST-accredited, CERT-IN empaneled, and a PCI ASV-certified vendor. Our team also led the development of the OWASP APTS framework, helping shape the industry standard for continuous security testing. Today, 1,500+ organizations across 70+ countries trust Astra Security, including Ford, Loom, CompTIA, Hitachi, HackerRank, and OLX.

Average Rating: 4.6/5.0

Total Reviews: 243

G2 Deal: For G2 users: 10% off across all pentest plans

Avail Astra Pentest at 10% off, our comprehensive pentest suite scans for 8000+ security tests including OWASP Top 10, SANS 25, known CVEs & security best practices. This offer is exclusive to G2 users!

Price: ~~$5999~~ → $5400

View this exclusive G2 deal

How Do G2 Users Rate Astra Pentest?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 8.7/10 (Category avg: 9.0/10)
  • Automated Scans: 8.9/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.7/10 (Category avg: 8.5/10)

Who Is the Company Behind Astra Pentest?

  • Seller: ASTRA IT, Inc.
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Bengaluru, IN
  • Twitter: @getastra
    694 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    154 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, CEO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 66% Small, 28% Medium

What Do G2 Reviewers Say About Astra Pentest?

AI-generated summary from verified user reviews

Pros
  • Users commend Astra Pentest's excellent customer support, noting their responsiveness and flexibility throughout the process.
  • Users praise the comprehensive vulnerability detection of Astra Pentest, which simplifies tracking and prioritizing security issues.
  • Users appreciate the user-friendly interface of Astra Pentest, enhancing their experience with clear and efficient vulnerability management.
  • Users commend Astra Pentest for its efficient scanning and penetration testing, enhancing security preparedness and team responsiveness.
  • Users value the vulnerability identification of Astra Pentest, enhancing confidence in security and business growth.
Cons
  • Users report poor customer support with Astra Pentest, noting slow email responses and lack of instant messaging options.
  • Users find the poor interface design of Astra Pentest frustrating, leading to confusion and difficulties in usage.
  • Users report slow performance with Astra Pentest, citing delays in results and instability during use.
  • Users find the UI challenging, particularly with note-taking and clarity on rescan needs during pentests.
  • Users face a lack of information with Astra Pentest, as documentation and updates are often insufficient or slow to arrive.

What Are Recent G2 Reviews of Astra Pentest?

What Are G2 Users Discussing About Astra Pentest?

Intruder

Intruder's continuous exposure management platform helps security, IT, and engineering teams stop breaches before they start. By unifying AI penetration testing, attack surface monitoring, cloud security, and vulnerability management in one intuitive platform, Intruder gives stretched teams an always-on security source of truth. Our approach focuses on continuous automated scanning using expertise and agentic solutions to ensure that the findings we deliver are accurate, prioritized by real-world risk, and ready to act on. Founded in 2015 by Chris Wallis, a former ethical hacker turned corporate blue teamer, Intruder is now protecting over 3,000 companies worldwide. Intruder has been awarded multiple accolades, was selected for GCHQ’s Cyber Accelerator, included on Deloitte’s Tech Fast 50 2023 list as the fastest-growing cybersecurity company in the UK and was named in G2’s 2026 Best Software Awards.

Average Rating: 4.8/5.0

Total Reviews: 220

How Do G2 Users Rate Intruder?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 9.3/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.5/10 (Category avg: 8.5/10)

Who Is the Company Behind Intruder?

  • Seller: Intruder
  • Company Website:
  • Year Founded: 2015
  • HQ Location: London
  • Twitter: @intruder_io
    979 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, Director
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Small, 37% Medium

What Do G2 Reviewers Say About Intruder?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Intruder, with quick setup and intuitive system design enhancing their experience.
  • Users value the clarity and prioritization of Intruder's findings, enabling effective risk management and actionable insights.
  • Users value the quick and efficient customer support from Intruder, enhancing their overall scanning experience.
  • Users appreciate the intuitive interface of Intruder, finding it easy to set up and navigate.
  • Users value the efficient vulnerability identification from Intruder, enhancing their cybersecurity management effortlessly.
Cons
  • Users find the product expensive due to high costs for add-ons and fees per endpoint scanned.
  • Users find the slow scanning process frustrating, leading to inefficiencies and missed vulnerabilities during security assessments.
  • Users find licensing issues challenging, particularly regarding costs and constraints that affect system configurations.
  • Users experience false positives which can obscure the detection of critical vulnerabilities in security monitoring.
  • Users find the limited features of Intruder less accommodating for specific reporting and customization needs.

What Are Recent G2 Reviews of Intruder?

What Are G2 Users Discussing About Intruder?

Tenable Vulnerability Management

Tenable Vulnerability Management provides a risk-based approach to identifying, prioritizing, and remediating vulnerabilities across your entire attack surface. Powered by Nessus technology and AI-driven analytics, it goes beyond CVSS scores to assess exploitability, asset criticality, and business impact—so you can focus on what matters most. With continuous visibility, automated scanning, and real-time risk insights, security teams can quickly expose and close critical vulnerabilities before they’re exploited. Advanced asset identification ensures accurate tracking in dynamic environments, while intuitive dashboards, comprehensive reporting, and seamless third-party integrations help streamline workflows. As a cloud-based solution, Tenable Vulnerability Management scales with your organization, empowering security teams to maximize efficiency, reduce risk, and improve resilience against evolving threats.

Average Rating: 4.5/5.0

Total Reviews: 124

How Do G2 Users Rate Tenable Vulnerability Management?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Detection Rate: 9.0/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Tenable Vulnerability Management?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 52% Large, 35% Medium

What Do G2 Reviewers Say About Tenable Vulnerability Management?

AI-generated summary from verified user reviews

Pros
  • Users value the user-friendly interface of Tenable Vulnerability Management, facilitating easy prioritization and action on vulnerabilities.
  • Users value the scanning efficiency of Tenable Vulnerability Management, enhancing their ability to prioritize and manage vulnerabilities effectively.
  • Users value the robust scanning and reporting features of Tenable Vulnerability Management, enhancing vulnerability management efficiency.
  • Users appreciate the efficient automated scanning capabilities of Tenable, enhancing their vulnerability management process significantly.
  • Users value the effective vulnerability identification that helps prioritize remediation efforts efficiently within their environments.
Cons
  • Users find the high costs of Tenable Vulnerability Management prohibitive, especially for organizations with tight budgets.
  • Users find the reporting capabilities inadequate, leading to a need for external data processing for better insights.
  • Users find the reporting capabilities limited, often requiring external processing for better data refinement and insights.
  • Users find the pricing issues of Tenable Vulnerability Management to be complex and potentially prohibitive for budget-conscious organizations.
  • Users find the complexity of Tenable Vulnerability Management to be challenging, affecting usability and management efficiency.

What Are Recent G2 Reviews of Tenable Vulnerability Management?

What Are G2 Users Discussing About Tenable Vulnerability Management?

Burp Suite

Burp Suite is a complete ecosystem for web application and API security testing, combining two products: Burp Suite DAST - a best-of-breed, precision DAST solution that automates runtime testing, and Burp Suite Professional - the industry-standard toolkit for manual penetration testing. Developed by PortSwigger, more than 85,000 security professionals rely on Burp Suite to find, verify, and understand vulnerabilities across complex modern web applications. Burp Suite DAST is PortSwigger’s enterprise dynamic application security testing (DAST) solution, purpose-built for continuous, automated scanning of web applications and APIs. Unlike many DAST solutions, which are part of a wider AST offering, Burp Suite DAST is not a bolt-on tool - instead it’s precision-built from over 20 years of dynamic testing experience. Burp Suite DAST reveals the runtime issues that static analysis tools miss, such as authentication flaws, configuration drift, and chained vulnerabilities. Built on the same proprietary scanning engine that powers Burp Suite Professional, it delivers precise, low-noise results that security teams trust. Key capabilities of Burp Suite DAST include: Continuous, automated scanning of web applications and APIs, integration with CI/CD pipelines and vulnerability management tools, flexible deployment across cloud, and on-premise environments, shared scanning logic and configurations between automated and manual testing, accurate, low-noise detection informed by PortSwigger Research. Burp Suite Professional complements DAST with deep manual testing capability. It’s the industry-standard toolkit for penetration testers, consultants, and AppSec engineers who need complete insight and flexibility when validating or exploring vulnerabilities. Findings discovered by DAST can be investigated and verified in Burp Suite Professional, ensuring every result is accurate, contextual, and actionable. Together, Burp Suite DAST and Burp Suite Professional create a unified ecosystem that delivers automation at breadth and manual depth where it counts. Burp Suite is built for AppSec teams who need scalable, trustworthy coverage across web and API environments, enabling a seamless handoff between automated and manual testing.

Average Rating: 4.8/5.0

Total Reviews: 126

How Do G2 Users Rate Burp Suite?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 8.6/10 (Category avg: 9.0/10)
  • Automated Scans: 8.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Burp Suite?

  • Seller: PortSwigger
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Knutsford, GB
  • Twitter: @Burp_Suite
    138,186 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    345 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 31% Small

What Do G2 Reviewers Say About Burp Suite?

AI-generated summary from verified user reviews

Pros
  • Users enjoy the user-friendly interface of Burp Suite, making navigation and analysis straightforward for all skill levels.
  • Users highlight the user-friendly interface of Burp Suite, making it easy to navigate and utilize effectively.
  • Users value the deep automation and manual testing capabilities of Burp Suite for effective security assessments.
  • Users appreciate the control and visibility Burp Suite offers, with powerful tools for effective web application testing.
  • Users praise Burp Suite for its clear, user-friendly interface that simplifies web application penetration testing for both beginners and experts.
Cons
  • Users find Burp Suite to be expensive, particularly for the professional version, which may limit accessibility for some users.
  • Users report slow performance with Burp Suite, particularly on lower-end systems during extensive scanning tasks.
  • Users find the steep learning curve of Burp Suite challenging, especially beginners navigating its complex features and tools.
  • Users find the steep learning curve in Burp Suite challenging, particularly for beginners adjusting to its complex setup.
  • Users find the limited customization in Burp Suite restricts exploration, especially for beginners and independent learners.

What Are Recent G2 Reviews of Burp Suite?

What Are G2 Users Discussing About Burp Suite?

Sysdig Secure

Sysdig Secure is the real-time cloud-native application protection platform (CNAPP) trusted by organizations of all sizes around the world.. Built by the creators of Falco and Wireshark, Sysdig uniquely delivers runtime-powered visibility and agentic AI to stop cloud attacks instantly, not after the damage is done. With Sysdig, you can: - Stop threats in 2 seconds and respond in minutes - Cut vulnerability noise by 95% with runtime prioritization - Detect real risk instantly across workloads, identities, and misconfigurations - Close permissions gaps in under 2 minutes Sysdig Secure consolidates CSPM, CWPP, CIEM, vulnerability management, and threat detection into a single open, real-time platform. Unlike other CNAPPs, Sysdig connects signals across runtime, identity, and posture to eliminate blind spots, reduce tool sprawl, and accelerate innovation without compromise. No guesswork. No black boxes. Just cloud security, the right way. Learn more at https://sysdig.com

Average Rating: 4.8/5.0

Total Reviews: 110

How Do G2 Users Rate Sysdig Secure?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 9.5/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.5/10 (Category avg: 8.5/10)

Who Is the Company Behind Sysdig Secure?

  • Seller: Sysdig
  • Company Website:
  • Year Founded: 2013
  • HQ Location: San Francisco, California
  • Twitter: @Sysdig
    10,284 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    562 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 47% Large, 40% Medium

What Do G2 Reviewers Say About Sysdig Secure?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Sysdig Secure, providing real-time threat detection and vulnerability insights.
  • Users value the real-time threat detection capabilities of Sysdig Secure, enhancing their security for cloud-native environments.
  • Users appreciate the real-time vulnerability detection of Sysdig Secure, aiding in effective risk prioritization and threat management.
  • Users value the real-time threat detection of Sysdig Secure, enhancing security for cloud-native applications and environments.
  • Users value the comprehensive visibility provided by Sysdig Secure, enhancing security and compliance across environments.
Cons
  • Users face feature limitations with Sysdig Secure, including outdated documentation and challenging integration processes.
  • Users find the complexity during initial setup a challenge, especially for those lacking technical expertise.
  • Users find missing features like runtime detection and tracing hinder sysdig's usability and integration with organizational systems.
  • Users note the difficult learning curve for Sysdig Secure, making it challenging for those unfamiliar with DevSecOps.
  • Users find the initial setup and configuration complex, leading to challenges in utilizing Sysdig Secure effectively.

What Are Recent G2 Reviews of Sysdig Secure?

What Are G2 Users Discussing About Sysdig Secure?

SentinelOne Singularity Endpoint

SentinelOne® Singularity™ Endpoint is an autonomous endpoint security platform that stops threats in real-time. It unifies endpoint protection (EPP), endpoint detection and response (EDR), and autonomous remediation to stop ransomware, zero-day exploits, supply chain attacks, and fileless malware. Singularity Endpoint protects workstations, mobile devices, servers, and cloud workloads across SaaS, on-premises, hybrid, and air-gapped environments. Behavioral and static AI detection models stop known and unknown threats by identifying how threats behave, not just what they look like. SentinelOne catches what signatures miss, without waiting on updates. Storyline® automatically correlates telemetry into one visual attack story, and patented one-click rollback restores systems to a trusted state in seconds. The result is stronger protection with fewer incidents and less operational overhead: lower dwell time, fewer false positives, and faster response. With Purple AI™, teams accelerate triage, threat hunting, and investigation. From alert to verdict without manual investigation. Purple AI's Agentic Investigation runs the analysis, surfaces the evidence, and tells your team exactly what to do next. The same SentinelOne agent that protects endpoints also defends every identity behind them. Detect credential abuse, shrink your attack surface, and contain identity threats from one console. Seamless integration of endpoint, identity, cloud, and third-party telemetry eliminates blind spots. Built AI-native from day one, Singularity Endpoint delivers best-in-industry coverage across Windows, macOS, Linux, and mobile operating systems, including legacy OSes. Trusted by more than 11,500 customers, SentinelOne is a six-time Gartner® Magic Quadrant™ Leader for Endpoint Protection.

Average Rating: 4.7/5.0

Total Reviews: 205

How Do G2 Users Rate SentinelOne Singularity Endpoint?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • Detection Rate: 9.5/10 (Category avg: 9.0/10)
  • Automated Scans: 8.7/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.6/10 (Category avg: 8.5/10)

Who Is the Company Behind SentinelOne Singularity Endpoint?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,571 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 45% Medium, 36% Large

What Do G2 Reviewers Say About SentinelOne Singularity Endpoint?

AI-generated summary from verified user reviews

Pros
  • Users value the tool efficiency of SentinelOne Singularity Endpoint, appreciating its user-friendly interface and effective threat detection.
  • Users find the ease of integration with Nable RMM and setup straightforward for daily operations.
  • Users praise the exceptional malware protection of SentinelOne, effectively stopping threats before they can cause harm.
  • Users find SentinelOne Singularity Endpoint to be a highly useful tool for incident notification and investigation.
  • Users appreciate the quick alerts and feature-rich capabilities of SentinelOne, enhancing security management and support.
Cons
  • Users face update issues with SentinelOne Singularity, leading to login problems and cumbersome agent management.
  • Users find the difficult learning curve of SentinelOne Singularity Endpoint challenging, especially for beginners navigating its features.
  • Users find the frequent updates challenging, as rapid changes lead to login issues and a steep learning curve.
  • Users report challenges with agent removal issues impacting application functionality and requiring improvement in uninstallation processes.
  • Users report ineffective alerts that hinder troubleshooting and prevent them from addressing application issues effectively.

What Are Recent G2 Reviews of SentinelOne Singularity Endpoint?

What Are G2 Users Discussing About SentinelOne Singularity Endpoint?

SentinelOne Singularity Cloud Security

Singularity Cloud Security is SentinelOne’s comprehensive, cloud-native application protection platform (CNAPP). It combines the best of agentless insights with AI-powered threat protection, to secure and protect your multi-cloud infrastructure, services, and containers from build time to runtime. SentinelOne’s CNAPP applies an attacker’s mindset to help security practitioners better prioritize their remediation tasks with evidence-backed Verified Exploit Paths™. The efficient and scalable runtime protection, proven over 5 years and trusted by many of the world’s leading cloud enterprises, harnesses local, autonomous AI engines to detect and thwart runtime threats in real-time. CNAPP data and workload telemetry is recorded to SentinelOne’s unified security lake, for easy access and investigation.

Average Rating: 4.9/5.0

Total Reviews: 122

How Do G2 Users Rate SentinelOne Singularity Cloud Security?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.2/10)
  • Detection Rate: 9.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.8/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.9/10 (Category avg: 8.5/10)

Who Is the Company Behind SentinelOne Singularity Cloud Security?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,571 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About SentinelOne Singularity Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the real-time threat alerts of SentinelOne Singularity Cloud Security, enhancing proactive protection against vulnerabilities.
  • Users appreciate the intuitive and user-friendly interface of SentinelOne Singularity, enhancing security management for everyone.
  • Users value the automated vulnerability detection of PingSafe, enabling proactive security and swift threat identification.
  • Users praise PingSafe for its comprehensive cloud security solutions that enhance threat detection and proactive risk management.
  • Users value the strong visibility and protection offered by SentinelOne Singularity Cloud Security, enhancing their operational efficiency.
Cons
  • Users note the complexity of configuring SentinelOne Singularity Cloud Security, requiring time and experience for effective use.
  • Users find that ineffective alerts require tuning, complicating setup and alignment with organizational workflows.
  • Users find the complex setup of SentinelOne Singularity Cloud Security can be time-consuming and challenging to navigate.
  • Users find the difficult configuration of SentinelOne Singularity Cloud Security can complicate setup and usage experience.
  • Users feel the UI of SentinelOne Singularity is clunky, making the platform harder to navigate and set up.

What Are Recent G2 Reviews of SentinelOne Singularity Cloud Security?

Pentera

Pentera is the category leader for Automated Security Validation, allowing every organization to test with ease the integrity of all cybersecurity layers, unfolding true, current security exposures at any moment, at any scale. Thousands of security professionals and service providers around the world use Pentera to guide remediation and close security gaps before they are exploited. Its customers include Casey's General Stores, Emeria, LuLu International Exchange, IP Telecom PT, BrewDog, City National Bank, Schmitz Cargobull, and MBC Group. Pentera is backed by leading investors such as K1 Investment Management, Insight Partners, Blackstone, Evolution Equity Partners, and AWZ. Visit https://pentera.io for more information.

Average Rating: 4.6/5.0

Total Reviews: 186

How Do G2 Users Rate Pentera?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 8.4/10 (Category avg: 9.0/10)
  • Automated Scans: 9.1/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Pentera?

  • Seller: Pentera
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Boston, MA
  • Twitter: @penterasec
    3,291 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    460 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Government Administration, Banking
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About Pentera?

AI-generated summary from verified user reviews

Pros
  • Users find Pentera's ease of use exceptional, thanks to its automation, customizable scenarios, and simple interface.
  • Users value the effective vulnerability scanning and remediation capabilities of Pentera, enhancing overall security posture.
  • Users value the automation capabilities of Pentera, enhancing their security testing and validation processes efficiently.
  • Users value the responsive customer support from Pentera, enhancing their experience and facilitating smooth operations.
  • Users value the realistic attack simulations offered by Pentera, enhancing their security posture through continuous validation.
Cons
  • Users find the reporting inadequate, suggesting it requires improvement for better enterprise-level insights.
  • Users express concern about the lack of a robust RBAC system, limiting proper access control and user rights management.
  • Users desire improvement in handling false positives, though overall satisfaction with Pentera remains high.
  • Users note the limited reporting capabilities of Pentera, especially for enterprise-level assessments and lacking Spanish translation.
  • Users are concerned about the missing features in Pentera, including updates on vulnerabilities and insufficient RBAC options.

What Are Recent G2 Reviews of Pentera?

Qualys WAS

Qualys WAS is Qualys's platform for end-to-end web application scanning.

Average Rating: 4.5/5.0

Total Reviews: 20

How Do G2 Users Rate Qualys WAS?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Detection Rate: 9.1/10 (Category avg: 9.0/10)
  • Automated Scans: 9.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.2/10 (Category avg: 8.5/10)

Who Is the Company Behind Qualys WAS?

  • Seller: Qualys
  • Year Founded: 1999
  • HQ Location: Foster City, CA
  • Twitter: @qualys
    34,248 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,637 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 33% Large

What Are Recent G2 Reviews of Qualys WAS?

What Are G2 Users Discussing About Qualys WAS?

Amazon Inspector

Amazon Inspector is an automated vulnerability management service that continuously scans AWS workloads—including Amazon EC2 instances, container images in Amazon ECR, AWS Lambda functions, and code repositories—for software vulnerabilities and unintended network exposure. By integrating seamlessly with AWS environments, it provides real-time detection and prioritization of security issues, enabling organizations to enhance their security posture efficiently. Key Features and Functionality: - Automated Discovery and Continuous Scanning: Automatically identifies and assesses AWS resources for vulnerabilities and network exposures, ensuring comprehensive coverage without manual intervention. - Contextualized Risk Scoring: Generates risk scores by correlating vulnerability data with environmental factors such as network accessibility and exploitability, aiding in the prioritization of remediation efforts. - Integration with AWS Services: Seamlessly integrates with AWS Security Hub and Amazon EventBridge, facilitating automated workflows and centralized management of security findings. - Support for Multiple Resource Types: Extends vulnerability management to various AWS services, including EC2 instances, container images, Lambda functions, and code repositories, providing a unified security assessment across the cloud environment. - Agentless Scanning for EC2 Instances: Offers continuous monitoring of EC2 instances for software vulnerabilities without the need for installing additional agents, simplifying deployment and maintenance. Primary Value and Problem Solved: Amazon Inspector addresses the critical need for continuous and automated vulnerability management within AWS environments. By providing real-time detection and prioritization of security issues, it enables organizations to proactively identify and remediate vulnerabilities, reducing the risk of security breaches and ensuring compliance with industry standards. Its integration with existing AWS services and support for various resource types streamline security operations, allowing teams to focus on strategic initiatives while maintaining a robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 25

How Do G2 Users Rate Amazon Inspector?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Amazon Inspector?

  • Seller: Amazon Web Services (AWS)
  • Year Founded: 2006
  • HQ Location: Seattle, WA
  • Twitter: @awscloud
    2,232,483 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    147,094 employees on LinkedIn®
  • Ownership: NASDAQ: AMZN

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 41% Small, 33% Medium

What Do G2 Reviewers Say About Amazon Inspector?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the security alerts provided by Amazon Inspector, enhancing their ability to respond to vulnerabilities effectively.
  • Users commend the excellent customer support from AWS, enhancing their experience and helping with security management.
  • Users value the centralized management capabilities of Amazon Inspector, enhancing monitoring and compliance across their environment.
  • Users value the collaborative capabilities of Amazon Inspector, enhancing their security monitoring and compliance efforts effectively.
  • Users commend the automated security issue detection of Amazon Inspector, appreciating its ease of setup and guidance.
Cons
  • Users find the complexity of Amazon Inspector's configuration can hinder effective security implementation without proper training.
  • Users find complexity issues with Amazon Inspector, as advanced knowledge is required for effective configuration and security.
  • Users feel the learning curve for Amazon Inspector is steep, requiring well-trained admins for effective use.
  • Users find Amazon Inspector has limited features, making it challenging to address specific security needs effectively.
  • Users find Amazon Inspector not user-friendly, requiring advanced knowledge for proper configuration and security management.

What Are Recent G2 Reviews of Amazon Inspector?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated April 10, 2026

Learn More About Vulnerability Scanner Software

What is Vulnerability Scanner Software?

Vulnerability scanners are used to examine applications, networks, and environments for security flaws and misconfigurations. These tools run a variety of dynamic security tests to identify security threats along an application or network’s attack surface. Scans can be used for anything from an application penetration test to a compliance scan. Depending on the specific objectives a user has, they can customize the vulnerability scanner to test for specific issues or requirements.

Companies can configure these tests to their unique environment. Companies that handle lots of personal or financial data may scan to ensure every transaction or datastore is encrypted from the public. They could also test their web applications against specific threats like SQL injection or cross-site scripting (XSS) attacks. The highly-customizable nature of vulnerability scanners provides users with tailor-made solutions for application and network security examination.

Many of these tools offer continuous scanning and testing for nonstop protection and monitoring. Whatever administrators set as a priority will be tested periodically and inform employees of issues or incidents. Continuous monitoring makes it much easier to discover vulnerabilities before they become an issue and drastically reduce the amount of time a vulnerability takes to remediate.

Top vulnerability scanner software with CVE remediation guidance typically combines automated scanning with prioritized fix recommendations that map findings to severity scores, exposure paths, and patch availability. Based on G2 reviews, security teams evaluate vulnerability scanner software by comparing CVE remediation depth, false positive rates, and how quickly the platform integrates into existing CI/CD pipelines and cloud environments.

Key Benefits of Vulnerability Scanner Software

  • Scan networks and applications for security flaws
  • Diagnose, track, and remediate vulnerabilities
  • Identify and resolve misconfigurations
  • Perform ad hoc security tests

Why Use Vulnerability Scanner Software?

Applications and networks are only beneficial to a business if they operate smoothly and securely. Vulnerability scanners are a useful tool to view internal systems and applications from the perspective of the attacker. These tools allow for dynamic testing while applications operate. This helps security teams take a step beyond patches and code analysis to evaluate security posture while the application, network, or instance actually runs.

Application security— Cloud, web, and desktop applications all require security, but operate differently. While many vulnerability scanners support testing for all kinds of applications, vulnerability scanners often support a few application types, but not others. Still, they will all examine the application itself, as well as the paths a user needs to access it. For example, if a vulnerability scanner is used on a web application, the tool will take into account the various attack vectors a hacker might take. This includes a site’s navigation, regional access, privileges, and other factors decided by the user. From there, the scanner will output reports on specific vulnerabilities, compliance issues, and other operational flaws.

Networks — While software applications are often the most obvious use cases for vulnerability scanners, network vulnerability scanners are also quite common. These tools take into account the network itself, as well as computers, servers, mobile devices and any other asset accessing a network. This helps businesses identify vulnerable devices and abnormal behaviors within a network to identify and remediate issues as well as improve their network's security posture. Many even provide visual tools for mapping networks and their associated assets to simplify the management and prioritization of vulnerabilities requiring remediation.

Cloud environments — Not to be confused with cloud-based solutions delivered in a SaaS model, cloud vulnerability scanners examine cloud services, cloud computing environments, and integrated connections. Like network vulnerability scanners, cloud environments require an examination on a few levels. Cloud assets come in many forms including devices, domains, and instances; but all must be accounted for and scanned. In a properly secured cloud computing environment, integrations and API connections, assets, and environments must all be mapped, configurations must be monitored, and requirements must be enforced.

Based on G2 reviews, vulnerability scanner platforms generating VLAN audit reports are evaluated primarily by security teams running segmented enterprise networks where compliance frameworks (PCI, HIPAA, SOC 2, ISO 27001) require documented scans across each network zone. Reviewers point to audit-ready compliance reporting, granular scan scope by IP range and network segment, and exportable evidence formats as the features that determine whether the platform shortens the audit prep cycle or adds another step to it.

What are the Common Features of Vulnerability Scanner Software?

Vulnerability scanners can provide a wide range of features, but here are a few of the most common found in the market.

Network mapping — Network mapping features provide a visual representation of network assets including endpoints, servers, and mobile devices to intuitively demonstrate an entire network’s components.

Web inspection — Web inspection features are used to assess the security of a web application in the context of its availability. This includes site navigation, taxonomies, scripts, and other web-based operations that may impact a hacker’s abilities.

Defect tracking — Defect and issue tracking functionality helps users discover and document vulnerabilities and track them to their source through the resolution process.

Interactive scanning — Interactive scanning or interactive application security testing features allow a user to be directly involved in the scanning process, watch tests in real time, and perform ad hoc tests.

Perimeter scanning — Perimeter scanning will analyze assets connected to a network or cloud environment for vulnerabilities.

Black box testing — Black box scanning refers to tests conducted from the hacker’s perspective. Black box scanning examines functional applications externally for vulnerabilities like SQL injection or XSS.

Continuous monitoring — Continuous monitoring allows users to set it and forget it. They enable scanners to run all the time as they alert users of new vulnerabilities.

Compliance monitoring — Compliance-related monitoring features are used to monitor data quality and send alerts based on violations or misuse.

Asset discovery — Asset discovery features unveil applications in use and trends associated with asset traffic, access, and usage.

Logging and reporting — Log documentation and reporting provides required reports to manage operations. It provides adequate logging to troubleshoot and support auditing.

Threat intelligence — Threat intelligence features integrate with or store information related to common threats and how to resolve them once incidents occur.

Risk analysis — Risk scoring and risk analysis features identify, score, and prioritize security risks, vulnerabilities, and compliance impacts of attacks and breaches.

Extensibility — Extensibility and integration features provide the ability to extend the platform or product to include additional features and functionalities.

Based on G2 reviews, the most trusted vulnerability scanner platforms in 2026 for security teams lead on CVE remediation guidance and easy setup onboarding, with reviewers describing time-to-first-scan in hours rather than weeks. SOC and AppSec teams point to clear remediation steps, severity scoring, and actionable findings as the features that distinguish platforms they actively use from ones that produce noise. Vulnerability scanner solutions with easy setup onboarding are highlighted in recent reviews for delivering full environment visibility on day one through agentless, API-driven architectures, with documentation that reduces the engineering lift typically associated with rolling out vulnerability scanning.

Many vulnerability scanner tools will also offer the following features: 

Potential Issues with Vulnerability Scanner Software

False positives — False positives are one of the most common issues with security tools. They indicate a tool is not running efficiently and introduce lots of unnecessary labor. Users should examine figures related to specific products and their accuracy before purchasing a solution.

Integrations — Integrations can make an application or product do virtually anything, but only if the integration is supported. If a specific solution must be integrated or a specific data source is highly relevant, be sure it’s compatible with the vulnerability scanner before making that decision.

Scalability — Scalability is always important, especially for growing teams. Cloud and SaaS-based solutions are traditionally the most scalable, but desktop and open source tools may be as well. Scalability will be important for teams considering collaborative use, concurrent use, and multi-application and environment scanning.