Best Extended Detection and Response (XDR) Platforms - Page 2

How Many Extended Detection and Response (XDR) Platforms Products Does G2 Track?

Total Products under this Category: 113

Category Stats (Nov 2026)

  • Average Rating: 4.55/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.95%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Extended Detection and Response (XDR) Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,900+ Authentic Reviews
  • 113+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

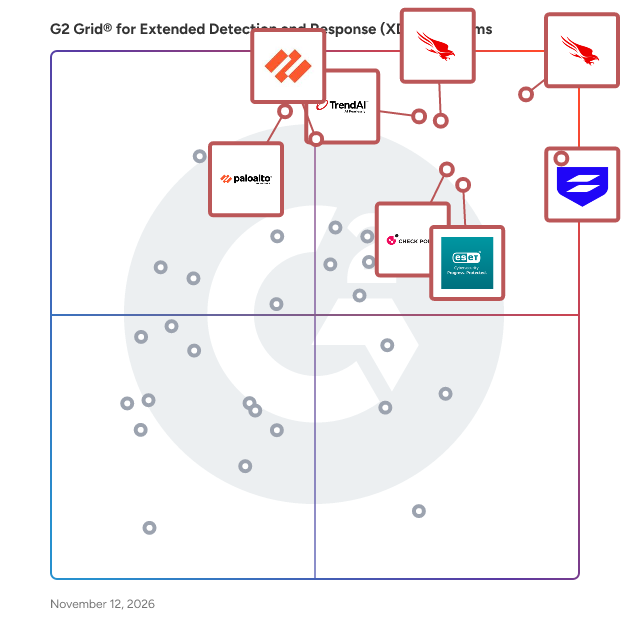
G2 Grid® for Extended Detection and Response (XDR) Platforms

G2 Grid® for Extended Detection and Response (XDR) Platforms plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.

Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)

aiXDR-PMAX

Seceon delivers an AI driven XDR and operational threat management platform that unifies next generation SIEM, SOAR, NDR, UEBA, ITDR, endpoint protection, and cloud security in a single platform. A single agent design ingests and correlates telemetry across endpoint, network, identity, cloud, and OT and ICS sources in real time. Behavioral baselines, network anomaly detection, threat intelligence correlation, and natural language threat hunting support the identification of advanced threats. Identity protection supports multiple identity platforms and network monitoring supports OT and ICS environments. Automated response and compliance ready logging support security operations and incident response through platform consolidation.

Average Rating: 4.9/5.0

Total Reviews: 24

How Do G2 Users Rate aiXDR-PMAX?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.8/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.6/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind aiXDR-PMAX?

  • Seller: Seceon
  • Year Founded: 2015
  • HQ Location: Westford, Massachusetts, United States
  • LinkedIn® Page: www.linkedin.com
    174 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 48% Medium, 36% Small

What Are Recent G2 Reviews of aiXDR-PMAX?

Bitdefender GravityZone XDR

Bitdefender Business Solutions Group is the business cybersecurity division of Bitdefender, delivering GravityZone — a unified platform that consolidates endpoint protection (EPP), endpoint detection and response (EDR), extended detection and response (XDR), and managed detection and response (MDR) into a single agent and console. Bitdefender GravityZone serves mid-market organizations with lean IT and security teams, protecting endpoints, identities, email, network, and cloud workloads. Effortless Security. Unmatched Protection For more information, visit https://www.bitdefender.com/en-us/business/.

Average Rating: 4.2/5.0

Total Reviews: 113

How Do G2 Users Rate Bitdefender GravityZone XDR?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.2/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Bitdefender GravityZone XDR?

  • Seller: Bitdefender
  • Year Founded: 2001
  • HQ Location: Bucuresti, Romania
  • LinkedIn® Page: www.linkedin.com
    2,344 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 54% Small, 38% Medium

What Do G2 Reviewers Say About Bitdefender GravityZone XDR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the easy installation and maintenance of Bitdefender GravityZone XDR, simplifying security management significantly.
  • Users find Bitdefender GravityZone XDR's ease of use refreshing, with simple installation and straightforward policy maintenance.
  • Users praise the excellent customer support of Bitdefender GravityZone XDR, enhancing their overall experience and satisfaction.
  • Users value the efficiency of Bitdefender GravityZone XDR, praising its easy installation and smooth management experience.
  • Users appreciate the excellent security and threat detection provided by Bitdefender GravityZone XDR, enhancing their protection against risks.
Cons
  • Users find Bitdefender GravityZone XDR not user-friendly due to its complex interface and challenging navigation.
  • Users find the complex interface of Bitdefender GravityZone XDR challenging, impacting navigation and overall ease of use.
  • Users find the complexity of setup and management challenging, particularly for non-technical individuals and during updates.
  • Users find the configuration issues challenging, especially beginners, adding time and complexity to setup and management.
  • Users find the difficult configuration of Bitdefender GravityZone XDR challenging, especially for non-technical individuals.

What Are Recent G2 Reviews of Bitdefender GravityZone XDR?

What Are G2 Users Discussing About Bitdefender GravityZone XDR?

Todyl Security Platform

Todyl is an AI-powered Cybersecurity and Assurance Platform for threat, risk, and compliance management delivered through a single agent and a single portal. Our platform defends against modern, advanced threats spanning identity, endpoint, network, cloud, SaaS, and more. We also simplify meeting and demonstrating extensive compliance and insurance requirements with centralized data collection and reporting, easy-to-use assessment tools, a built-in risk register, and dashboards to cut back on manual reporting and spreadsheet sprawl. Our platform delivers a layered approach to cybersecurity, spanning SASE, Micro-Segmentation (LZT), Endpoint Security, SIEM, MXDR, and GRC all delivered through the same agent, in a cloud native platform. It’s easy to implement as a cost effective, fully integrated single solution that can consolidate and simplify your security and compliance programs. You can also deploy individual modules to meet your current needs, with a simple toggle within the UI to add or trial new modules when you need them. And an integrated Assurance Marketplace helps you complete your security program with additional services like incident response and penetration testing, and streamlined access to cyber insurance providers.

Average Rating: 4.7/5.0

Total Reviews: 107

How Do G2 Users Rate Todyl Security Platform?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 7.5/10 (Category avg: 8.8/10)

Who Is the Company Behind Todyl Security Platform?

  • Seller: Todyl
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Denver, CO
  • LinkedIn® Page: www.linkedin.com
    120 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 76% Small, 7% Medium

What Do G2 Reviewers Say About Todyl Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Todyl Security Platform, citing simple deployment and management for all skill levels.
  • Users commend the exceptional customer support from Todyl, particularly the rapid response and insightful analysis from the MXDR team.
  • Users value the feature-rich nature of Todyl Security Platform, enhancing security with extensive tools and integrations.
  • Users value Todyl's comprehensive security integration, which provides robust protection in a unified, easy-to-manage platform.
  • Users find Todyl Security Platform's deployment ease exceptional, allowing quick onboarding and effortless client management.
Cons
  • Users express the need for improvements in user guidance and complex configurations to enhance their experience with Todyl.
  • Users experience integration issues with Todyl, facing challenges in agent health visibility and complex configurations.
  • Users express concerns about inadequate reporting, limiting visibility on Agent Health and event details within the Todyl Platform.
  • Users note the limited features in Todyl's reporting and customization options, impacting their overall security management experience.
  • Users report poor reporting features in Todyl, restricting effective monitoring and customization for security insights.

What Are Recent G2 Reviews of Todyl Security Platform?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Elastic Security

Modernize your SOC with AI Security is a data problem. Your team needs to detect, investigate, and respond to threats quickly. Elastic Security unifies next-gen SIEM and XDR with native automation, with AI built into every step. Built on Elasticsearch, the open-source search platform trusted by millions, Elastic provides complete visibility across your environment. Our data mesh architecture streamlines analysis to raise team productivity and reduce attacker dwell time. Bolster your defenses - Detect threats faster by analyzing data from across your attack surface - Stop attacks with the industry's best-rated XDR protection - Close the loop faster with Elastic Workflows, blending scripted automation with agentic AI reasoning - Get more accurate AI assistance, grounded in your data using Elasticsearch's leading relevance capabilities With Elastic Security, your SOC team can use generative AI to distill alerts, automate repetitive tasks, and get tailored guidance, all with your choice of LLM and full transparency into reasoning and sources. SOC leaders choose Elastic Security when they need a unified, open platform ready to run on any cloud, on-prem, or air-gapped.

Average Rating: 4.4/5.0

Total Reviews: 38

How Do G2 Users Rate Elastic Security?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.4/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Elastic Security?

  • Seller: Elastic
  • Company Website:
  • Year Founded: 2012
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    10,457 employees on LinkedIn®
  • Ownership: NYSE: ESTC

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 46% Medium, 46% Small

What Do G2 Reviewers Say About Elastic Security?

AI-generated summary from verified user reviews

Pros
  • Users value the seamless integrations of Elastic Security, enhancing efficiency in monitoring and responding to security threats.
  • Users appreciate the ease of use of Elastic Security, enabling efficient investigations and seamless dashboard creation.
  • Users value the powerful detection capabilities of Elastic Security, enjoying advanced features and ease of use.
  • Users appreciate the easy integrations of Elastic Security, enhancing their security monitoring and investigation capabilities effortlessly.
  • Users value the efficiency improvements of Elastic Security, facilitating faster investigations and streamlined incident management.
Cons
  • Users struggle with the steep learning curve and high administrative overhead, making Elastic Security challenging for new teams.
  • Users note the complex implementation of Elastic Security, highlighting challenges with learning curves and administrative overhead.
  • Users experience significant complexity with Elastic Security, requiring extensive maintenance and a steep learning curve.
  • Users find the complex setup of Elastic Security daunting, particularly due to the steep learning curve and administrative overhead.
  • Users face significant integration issues with inconsistent field matching, complicating threat intelligence correlation and analysis.

What Are Recent G2 Reviews of Elastic Security?

Field Effect MDR

Field Effect delivers intelligence-grade managed detection and response for the AI era. Built on Federated Smart Compute™ and nation-state tradecraft, our holistic MDR platform uncovers weaknesses early, blocks attacks in real time, and reduces risk across the entire threat surface—endpoint, network, cloud, and more. With an 18-second median time to detect, Field Effect helps MSPs and overwhelmed IT teams outpace agentic attacks and achieve premium protection with the team they have.

Average Rating: 4.8/5.0

Total Reviews: 54

How Do G2 Users Rate Field Effect MDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.3/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.7/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Field Effect MDR?

  • Seller: Field Effect
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Ottawa
  • LinkedIn® Page: www.linkedin.com
    149 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Small, 33% Medium

What Do G2 Reviewers Say About Field Effect MDR?

AI-generated summary from verified user reviews

Pros
  • Users commend the prompt and knowledgeable customer support, enhancing their experience with Field Effect MDR's reliable service.
  • Users find the ease of use of Field Effect MDR exceptional, enhancing their cybersecurity management experience effortlessly.
  • Users admire the high-quality alerts from Field Effect MDR that enhance response capabilities and reduce false positives.
  • Users value the effective threat detection of Field Effect MDR, ensuring continuous and comprehensive cybersecurity protection.
  • Users value the meaningful and actionable alerts from Field Effect MDR, enhancing their security response capabilities.
Cons
  • Users face alert issues with Field Effect MDR, requiring additional support for clarity and integration problems.
  • Users express frustration with the inefficient alert system, often overwhelmed by the high volume of alerts received.
  • Users find communication issues arise due to overly technical explanations and difficulties in navigating the support portal.
  • Users feel there is insufficient information on alerts, often needing support for more details during investigations.
  • Users find the learning curve steep for Field Effect MDR, requiring time to tune the platform effectively.

What Are Recent G2 Reviews of Field Effect MDR?

What Are G2 Users Discussing About Field Effect MDR?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 48

How Do G2 Users Rate Darktrace / HYBRID NETWORK?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®
  • Ownership: LON: DARK

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 61% Medium, 29% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users value the robust monitoring capabilities of Darktrace, enhancing visibility and confidence in network security.
  • Users appreciate the self-learning AI technology of Darktrace, enhancing security with real-time monitoring and automated responses.
  • Users commend the rapid and accurate threat detection of Darktrace, ensuring confidence and effective protection from cyber threats.
  • Users appreciate the responsive customer support of Darktrace, enhancing their learning and experience with the platform.
  • Users commend the autonomous AI capabilities of Darktrace for its proactive and effective threat detection and response.
Cons
  • Users face a significant initial learning curve with Darktrace, requiring extensive time investment for proper tuning and validation.
  • Users find Darktrace / HYBRID NETWORK to be expensive, especially for smaller organizations with limited security budgets.
  • Users often face alert issues during the learning phase, needing significant time and effort to manage false positives.
  • Users report that the complex setup of Darktrace requires significant engineering skills and ongoing management efforts.
  • Some users experience false positives, necessitating IT intervention to restore services and improve detection capabilities.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

ReliaQuest GreyMatter

ReliaQuest’s agentic AI security operations platform, GreyMatter, allows security teams to detect threats at the source, contain them in under 5 minutes, and eliminate Tier 1 and Tier 2 work for faster investigation and response. GreyMatter orchestrates 6 agentic AI personas with 200+ agent skills and 400+ AI tools to exponentially scale security operations and help organizations predict what's next.

Average Rating: 4.7/5.0

Total Reviews: 20

How Do G2 Users Rate ReliaQuest GreyMatter?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.4/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind ReliaQuest GreyMatter?

  • Seller: ReliaQuest
  • Company Website:
  • Year Founded: 2007
  • HQ Location: Tampa, Florida, United States
  • LinkedIn® Page: www.linkedin.com
    1,106 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Consumer Services
  • Company Size: 40% Medium, 25% Small

What Do G2 Reviewers Say About ReliaQuest GreyMatter?

AI-generated summary from verified user reviews

Pros
  • Users value the exceptional visibility provided by ReliaQuest GreyMatter, enhancing security management across multiple environments effortlessly.
  • Users value the centralized management of ReliaQuest GreyMatter, enhancing security operations and streamlining incident response.
  • Users praise the exceptional customer support of ReliaQuest GreyMatter, noting responsiveness and helpful guidance in security management.
  • Users value the ease of use of ReliaQuest GreyMatter, enhancing efficiency through seamless integration and streamlined operations.
  • Users appreciate the easy integrations of ReliaQuest GreyMatter, significantly streamlining investigations and enhancing overall security visibility.
Cons
  • Users experience alert delays, clunky interfaces, and slow report loading, suggesting the need for improved UX design.
  • Users find the complexity of configurations and features requires significant time to fine-tune for desired outcomes.
  • Users experience inefficient alert systems due to delays, duplicates, and slow report loading, requiring additional fine-tuning.
  • Users experience a learning curve with advanced automation workflows, though support resources help ease the process.
  • Users experience login issues with ReliaQuest GreyMatter's Android app, citing a clunky sign-in process as frustrating.

What Are Recent G2 Reviews of ReliaQuest GreyMatter?

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 4.9/5.0

Total Reviews: 78

How Do G2 Users Rate UnderDefense MAXI?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)

Who Is the Company Behind UnderDefense MAXI?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Marketing and Advertising, Information Technology and Services
  • Company Size: 51% Small, 43% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users value the high visibility UnderDefense MAXI provides into security alerts, streamlining threat management and response.
  • Users commend the responsive and effective customer support of UnderDefense MAXI, enhancing their cybersecurity management and experience.
  • Users commend UnderDefense MAXI for its effective cybersecurity solutions, enhancing security management and response efficiency.
  • Users value the information accuracy provided by UnderDefense, which clarifies security issues and enhances response efficiency.
  • Users highlight the quick issue resolution by UnderDefense, improving security alert management and enhancing overall security operations.
Cons
  • Users feel a lack of automation features limits control over the dashboard for UnderDefense MAXI.
  • Users desire more control over the dashboard, seeking enhanced customization and automated update options with UnderDefense MAXI.
  • Users note that limited integration requires significant setup time to ensure proper tool configuration.
  • Users find the setup process challenging, requiring significant time and effort for proper tool integration.

What Are Recent G2 Reviews of UnderDefense MAXI?

Cisco SecureX

Cisco SecureX is the broadest, most integrated security platform that connects the breadth of Cisco's integrated security portfolio and the customer's infrastructure for a consistent experience.

Average Rating: 4.3/5.0

Total Reviews: 12

How Do G2 Users Rate Cisco SecureX?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.3/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Cisco SecureX?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Company Size: 58% Large, 25% Medium

What Do G2 Reviewers Say About Cisco SecureX?

AI-generated summary from verified user reviews

Pros
  • Users find Cisco SecureX to be easy to use, providing a seamless and bug-free cloud security experience.
  • Users praise the cloud security solutions of Cisco SecureX, highlighting its ease of use and effective access control.
  • Users value the centralized management of Cisco SecureX, streamlining security operations and improving incident response efficiency.
  • Users value the intuitive dashboard of Cisco SecureX, enhancing threat visibility and streamlining incident response efficiency.
  • Users value the easy integrations of Cisco SecureX, allowing for streamlined workflows across various security tools effortlessly.
Cons
  • Users find the complex implementation of Cisco SecureX challenging, especially when integrating with other tools and features.
  • Users find Cisco SecureX to be expensive, as it slightly exceeds many budgets for security software.
  • Users face integration issues with Cisco SecureX, finding the initial setup complex, especially with third-party tools.
  • Users report experiencing slow performance, especially during high data processing, impacting workflow efficiency at crucial times.
  • Users express concerns about the training issues requiring team involvement for every new update of Cisco SecureX.

What Are Recent G2 Reviews of Cisco SecureX?

What Are G2 Users Discussing About Cisco SecureX?

NetWitness Platform

NetWitness is a comprehensive threat detection, investigation and response platform that combines visibility, analytics, insight, and automation into a single solution. It collects and analyzes data across all capture points (logs, packets, netflow, endpoint and IoT) and computing platforms (physical, virtual and cloud), enriching data with threat intelligence and business context.

Average Rating: 3.9/5.0

Total Reviews: 23

How Do G2 Users Rate NetWitness Platform?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind NetWitness Platform?

Who Uses This Product?

  • Company Size: 54% Large, 33% Medium

What Do G2 Reviewers Say About NetWitness Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the network packet capture feature of NetWitness for effective forensic investigations and threat hunting.
  • Users appreciate the centralized threat detection capabilities of NetWitness Platform, enhancing efficiency in threat hunting across various data sources.
  • Users value the centralized view provided by NetWitness Platform, simplifying threat hunting across various data sources.
  • Users value the centralized threat hunting capabilities of NetWitness Platform, streamlining their cybersecurity efforts effectively.
  • Users value the full network packet capture capability of NetWitness, enhancing deep forensic investigation significantly.
Cons
  • Users find the complex implementation of NetWitness Platform challenging, needing extensive technical expertise for setup and upgrades.
  • Users find the complexity of initial deployment and upgrades challenging, requiring significant technical expertise and causing instability.
  • Users find the initial setup complex, often needing advanced expertise, which can hinder deployment and upgrades.
  • Users face complex deployment difficulties with the NetWitness Platform, needing substantial expertise for initial setup and upgrades.
  • Users face complex initial setup and deployment challenges, often needing significant expertise for effective use.

What Are Recent G2 Reviews of NetWitness Platform?

What Are G2 Users Discussing About NetWitness Platform?

ExtraHop

ExtraHop is the cybersecurity partner enterprises trust to reveal cyber risk and build business resilience. The ExtraHop RevealX platform for network detection and response and network performance management uniquely delivers the instant visibility and unparalleled decryption capabilities organizations need to expose the cyber risks and performance issues that other tools can’t see. When organizations have full network transparency with ExtraHop, they can investigate smarter, stop threats faster, and keep operations running. RevealX deploys on premises or in the cloud. It addresses the following use cases: - Ransomware - Zero trust - Software supply chain attacks - Lateral movement and C2 communication - Security hygiene - Network and Application Performance Management - IDS - Forensics and more A few of our differentiators: Continuous and on-demand PCAP: Full packet processing is superior to NetFlow and yields higher quality detections. Strategic decryption across a variety of protocols, including SSL/TLS, MS-RPC, WinRM, and SMBv3, gives you better visibility into early-stage threats hiding in encrypted traffic as they attempt to move laterally across your network. Protocol coverage: RevealX decodes more than 70 network protocols. Cloud-scale machine learning: Rather than relying on limited "on-box" compute power for analysis and detections, RevealX uses sophisticated cloud-hosted and cloud-scale machine learning workloads to identify suspicious behavior in real time and create high-fidelity alerts. ExtraHop was named a Leader in The Forrester Wave™: Network Analysis and Visibility, Q2 2023. Key Technology Integration and Go-to-Market Partners: CrowdStrike: RevealX integrates with CrowdStrike Falcon® LogScale, Falcon Insight XDR, Falcon Threat Graph, and Falcon Intelligence. Splunk SOAR AWS Google Cloud Security Founded in 2007, ExtraHop is privately held and headquartered in Seattle, Wash. To learn more, visit www.extrahop.com.

Average Rating: 4.6/5.0

Total Reviews: 68

How Do G2 Users Rate ExtraHop?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.6/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind ExtraHop?

Who Uses This Product?

  • Top Industries: Hospital & Health Care, Transportation/Trucking/Railroad
  • Company Size: 69% Large, 26% Medium

What Do G2 Reviewers Say About ExtraHop?

AI-generated summary from verified user reviews

Pros
  • Users value the all-in-one solution of ExtraHop, ensuring complete network visibility and excellent customer support.
  • Users value comprehensive monitoring with ExtraHop, enjoying complete visibility and anomaly detection across their network traffic.
  • Users value the easy deployment of ExtraHop, simplifying setup on both physical and virtual networks.
  • Users appreciate the responsive support from ExtraHop's knowledgeable Customer Success teams, enhancing overall satisfaction and experience.

What Are Recent G2 Reviews of ExtraHop?

What Are G2 Users Discussing About ExtraHop?

Carbon Black Cloud

The Carbon Black Cloud security platform helps you strengthen and unify security tools to see more and stop more. Carbon Black unifies visibility across your endpoints, networks, and containers to enable you to stop threats targeting your organization with speed and confidence. Carbon Black protects against the full spectrum of modern cyber-attacks, including emerging threats and ransomware. Top SOC teams, IR firms and MSSPs have adopted Carbon Black as a core component of their prevention, detection, and response capability stack. Carbon Black is available via MSSP or directly.

Average Rating: 4.1/5.0

Total Reviews: 38

How Do G2 Users Rate Carbon Black Cloud?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Carbon Black Cloud?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA
  • Phone: +1 800 225-5224

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 56% Medium, 33% Large

What Do G2 Reviewers Say About Carbon Black Cloud?

AI-generated summary from verified user reviews

Pros
  • Users find the ease of use in Carbon Black Cloud to be exceptional, enhancing overall management and interface interaction.
  • Users value the advanced antivirus protection of Carbon Black Cloud, ensuring 24/7 security against various threats.
  • Users appreciate the advanced AI-powered security of Carbon Black Cloud, providing affordable 24/7 protection effortlessly.
  • Users value the easy installation and strong protection offered by Carbon Black Cloud for their digital infrastructure.
  • Users praise the easy installation of Carbon Black Cloud, appreciating its quick setup and robust protection.
Cons
  • Users report agent removal issues with VMware Carbon Black Cloud, causing disruptions during critical tasks like exams.
  • Users face significant compatibility issues as the tool needs extensive customization and lacks integration with Microsoft OS.
  • Users find complex implementation challenging, particularly in creating global blocks and whitelists without individual policy updates.
  • Users face complex installation issues with VMware Carbon Black Cloud, leading to interruptions during critical tasks like exams.
  • Users find it challenging to manage configuration issues, especially when needing global blocks or whitelists.

What Are Recent G2 Reviews of Carbon Black Cloud?

What Are G2 Users Discussing About Carbon Black Cloud?

Open Threat Management (OTM) Platform

Seceon Open Threat Management Platform is a software designed for cybersecurity threat detection and response. The software integrates security monitoring, threat intelligence, and automated response capabilities to help organizations identify and mitigate cyber threats in real time. It ingests data from multiple sources, including network traffic, endpoints, and cloud environments, and applies machine learning and analytics to detect anomalies and threats. Through automation, the software streamlines incident response processes, supports compliance requirements, and assists security teams in reducing the time to detect and remediate security incidents. Seceon Open Threat Management Platform addresses the business problem of manual and fragmented security monitoring by offering a unified view and AI-driven analysis for proactive threat management.

Average Rating: 4.5/5.0

Total Reviews: 18

How Do G2 Users Rate Open Threat Management (OTM) Platform?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.6/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Open Threat Management (OTM) Platform?

  • Seller: Seceon
  • Year Founded: 2015
  • HQ Location: Westford, Massachusetts, United States
  • LinkedIn® Page: www.linkedin.com
    174 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 48% Medium, 33% Small

What Do G2 Reviewers Say About Open Threat Management (OTM) Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the comprehensive visibility provided by OTM, simplifying threat detection and enhancing response capabilities effectively.
  • Users appreciate the comprehensive visibility provided by the Open Threat Management Platform, streamlining threat detection and response.
  • Users appreciate the comprehensive visibility of the OTM Platform, facilitating quick and automated threat detection and response.
  • Users appreciate the comprehensive visibility of the OTM Platform, enhancing threat detection and response efficiency.
  • Users appreciate the user-friendly dashboard of the OTM Platform, enabling quick threat detection and streamlined workflows.
Cons
  • Users experience a steep learning curve with Seceon OTM, which can hinder new users from fully utilizing its features.
  • Users find the complex implementation of the OTM Platform challenging due to high resource requirements and a steep learning curve.
  • Users feel there is limited customization in Seceon OTM, impacting dashboard and report flexibility for security teams.
  • Users face poor customer support, often finding it less responsive than expected during critical integration issues.
  • Users experience slow performance with the OTM Platform, noting lags during alert analysis that hinder efficiency.

What Are Recent G2 Reviews of Open Threat Management (OTM) Platform?

What Are G2 Users Discussing About Open Threat Management (OTM) Platform?

Heimdal

Accommodate all your cybersecurity needs under one convenient roof with the Heimdal® Unified Cybersecurity Platform. Our cybersecurity solutions can be used as standalone products or integrated into one another as part of a cohesive and unified XDR platform. Whether you’re a reseller, distributor, MSSP, or an organization committed to bolstering your online security, we provide an array of cutting-edge products to make your mission smoother. Heimdal® is a fast-growing cybersecurity company focused on continuous technological innovation. Since its establishment in 2014 in Copenhagen, based on the winning idea of CTF World Champions, Heimdal has experienced spectacular growth by proactively building products that anticipate threatscape trends. The company offers a multi-layeredand unified security suite that combines threat prevention, patch and asset management, endpoint rights management, antivirus and mail security which together secure customers against cyberattacks and keep critical information and intellectual property safe. Heimdal has been recognized as a thought leader in the industry and has won multiple international awards both for its solutions and for its educational content creation. The Heimdal line of products currently consists of 10 products and 2 services. The former category encompasses DNS Security for Endpoints & Network, Patch & Asset Management, Privileged Access Management, Application Control, Next-Gen Endpoint Antivirus, Ransomware Encryption Protection, Email Security, Email Fraud Prevention, and Remote Desktop. The latter is represented by Endpoint Detection & Response, as well as eXtended Detection & Response, or EDR and XDR for short. Currently, Heimdal’s cybersecurity solutions are deployed in more than 45 countries and supported regionally from offices in 15+ countries, by 175+ highly qualified specialists. Heimdal is ISAE 3000 certified and secures more than 2 million endpoints for over 10,000 companies. The company supports its partners without concessions on the basis of predictability and scalability. The common goal is to create a sustainable ecosystem and a strategic partnership.

Average Rating: 4.5/5.0

Total Reviews: 85

How Do G2 Users Rate Heimdal?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)

Who Is the Company Behind Heimdal?

  • Seller: Heimdal®
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Computer & Network Security, Construction
  • Company Size: 56% Medium, 29% Small

What Do G2 Reviewers Say About Heimdal?

AI-generated summary from verified user reviews

Pros
  • Users value the easy setup of Heimdal, enabling seamless deployment of tools across devices.
  • Users praise the seamless file transfer capabilities of Heimdal, enhancing efficiency and reliability across their systems.
  • Users praise Heimdal for its exceptional issue resolution and quick, professional support for effective problem-solving.
  • Users appreciate the reliable and effective patch management of Heimdal, ensuring smooth operation and timely updates.
  • Users value the reliable security solutions of Heimdal, enhanced by a user-friendly interface and excellent support.
Cons
  • Users find the interface complex, struggling with navigation and access to essential features in Heimdal.
  • Users find the admin portal complex and illogical, complicating navigation and access to essential features.
  • Users experience poor customer support initially, but find help improves over time with better product understanding.
  • Users find the poor interface design of Heimdal challenging, complicating navigation and access to essential features.
  • Users often face restart issues with Heimdal, leaving them feeling temporarily "unprotected" after scans.

What Are Recent G2 Reviews of Heimdal?

Vectra AI Platform

The Vectra AI Platform helps security teams detect and stop real attacks that evade traditional security controls across network, identity, cloud, and SaaS environments. It provides real-time visibility into how attackers move through hybrid and multi-cloud environments, enabling teams to understand attack activity early and respond before incidents escalate. By correlating attacker behavior across the full attack lifecycle, the platform reduces alert noise and surfaces high-confidence threats that matter most. Analysts spend less time triaging isolated alerts and more time investigating complete attack stories with the context needed to take decisive action. Vectra AI unifies detection, investigation, and coordinated response across identity, endpoint, and network controls. Its approach is aligned with real-world defensive techniques, reflected in the highest number of vendor references in MITRE D3FEND and recognition as a Leader in the 2025 Gartner® Magic Quadrant™ for Network Detection and Response. Organizations worldwide rely on Vectra AI to detect attacks others miss and demonstrate measurable improvements in security operations.

Average Rating: 4.3/5.0

Total Reviews: 20

How Do G2 Users Rate Vectra AI Platform?

  • Has the product been a good partner in doing business?: 8.1/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Vectra AI Platform?

  • Seller: Vectra AI
  • Year Founded: 2011
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    669 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 75% Large, 15% Medium

What Do G2 Reviewers Say About Vectra AI Platform?

AI-generated summary from verified user reviews

Pros
  • Users find the ease of understanding Vectra AI Platform offers makes it simple to learn and use effectively.
  • Users find Vectra AI Platform to be easy to work with, benefiting from its clear learning methods.

What Are Recent G2 Reviews of Vectra AI Platform?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024