Best Cloud Detection and Response (CDR) Software

How Many Cloud Detection and Response (CDR) Software Products Does G2 Track?

Total Products under this Category: 44

Category Stats (Nov 2026)

  • Average Rating: 4.58/5 (↓0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: UnderDefense MAXI (+0.43%) - Among all products in this category, UnderDefense MAXI recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Cloud Detection and Response (CDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,600+ Authentic Reviews
  • 44+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

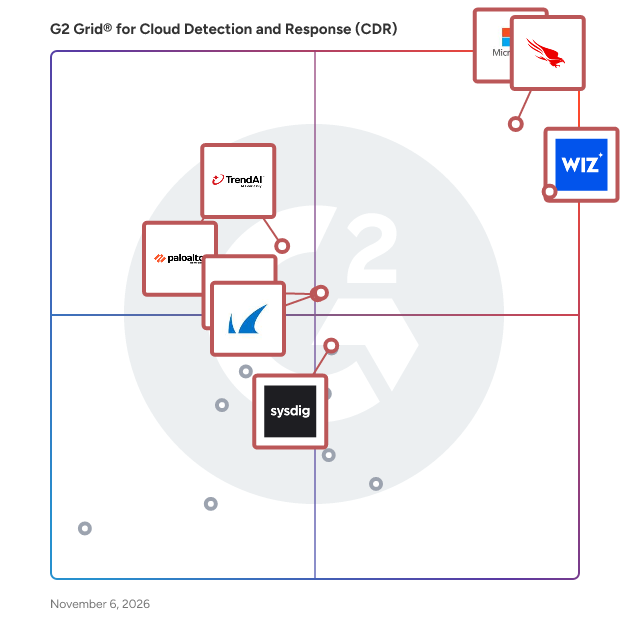
G2 Grid® for Cloud Detection and Response (CDR) Software

G2 Grid® for Cloud Detection and Response (CDR) Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security, Wiz, Cortex Cloud, TrendAI Vision One, Barracuda Managed XDR, Arctic Wolf, and Sysdig Secure.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-detection-and-response-cdr/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=wiz-wiz&focus%5B%5D=cortex-cloud&focus%5B%5D=trendai-vision-one&focus%5B%5D=barracuda-managed-xdr&focus%5B%5D=arctic-wolf&focus%5B%5D=sysdig-sysdig-secure)

Microsoft Defender for Cloud

Microsoft Defender for Cloud is a cloud native application protection platform for multicloud and hybrid environments with comprehensive security across the full lifecycle, from development to runtime.

Average Rating: 4.4/5.0

Total Reviews: 432

How Do G2 Users Rate Microsoft Defender for Cloud?

  • Ease of Admin: 8.7/10 (Category avg: 8.9/10)
  • Ease of Use: 8.7/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.3/10)
  • Quality of Support: 8.5/10 (Category avg: 9.2/10)

Who Is the Company Behind Microsoft Defender for Cloud?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Who Uses This: Saas Consultant, Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Medium, 35% Large

What Do G2 Reviewers Say About Microsoft Defender for Cloud?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the proactive security of Microsoft Defender for Cloud, ensuring peace of mind against potential threats and malware.
  • Users emphasize the comprehensive security of Microsoft Defender for Cloud, appreciating its proactive threat protection and ease of use.
  • Users appreciate the ease of use and real-time threat notifications of Microsoft Defender for Cloud, enhancing workflow efficiency.
  • Users appreciate the real-time vulnerability detection of Microsoft Defender for Cloud, enhancing their security and workflow efficiency.
  • Users value the real-time threat detection of Microsoft Defender for Cloud, ensuring robust security and peace of mind.
Cons
  • Users find the pricing complexity and overwhelming features of Microsoft Defender for Cloud challenging to navigate effectively.
  • Users note that the pricing can be expensive, especially for small to medium businesses, causing potential budgeting issues.
  • Users express frustration with delayed detection of threats, complicating their security management and response efforts.
  • Users experience false positive alerts with Microsoft Defender for Cloud, complicating the detection of real threats.
  • Users express frustration over the complex licensing structure of Microsoft Defender for Cloud, leading to confusion and unexpected costs.

What Are Recent G2 Reviews of Microsoft Defender for Cloud?

What Are G2 Users Discussing About Microsoft Defender for Cloud?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 240

How Do G2 Users Rate CrowdStrike Falcon Cloud Security?

  • Ease of Admin: 8.9/10 (Category avg: 8.9/10)
  • Ease of Use: 8.7/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.3/10)
  • Quality of Support: 8.9/10 (Category avg: 9.2/10)

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 51% Large, 31% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 922

How Do G2 Users Rate Wiz?

  • Ease of Admin: 9.0/10 (Category avg: 8.9/10)
  • Ease of Use: 8.8/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Quality of Support: 9.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Wiz?

  • Seller: Google
  • Company Website:
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Security Engineer, CISO
  • Top Industries: Financial Services, Computer Software
  • Company Size: 54% Large, 37% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users value the robust APIs and user-friendly UI, appreciating ongoing improvements and a wealth of insightful issues.
  • Users value the continuous enhancement of security features by Wiz, appreciating the support and innovation in their tool.
  • Users appreciate the ease of use of Wiz, benefiting from its user-friendly interface and seamless integration.
  • Users value the comprehensive visibility Wiz provides, enhancing security and prioritizing essential aspects of their cloud environment.
  • Users appreciate the easy setup of Wiz, enabling a quick and seamless integration into their workflows.
Cons
  • Users note that improvement is needed for laggy query responses and better dashboard reporting capabilities.
  • Users find the feature limitations of Wiz frustrating, especially with complex management and reporting challenges.
  • Users find a significant learning curve in mastering Wiz's extensive features, which can hinder initial usage.
  • Users identify improvements needed in dashboard reporting and feature streamlining for better usability and budgeting.
  • Users find the interface overwhelming initially, facing a steep learning curve and complex licensing issues.

What Are Recent G2 Reviews of Wiz?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

TrendAI Vision One

TrendAI Vision One is a cloud-native security operations platform, serving cloud, hybrid, and on-premises environments. It combines ASM and XDR in a single console to effectively manage cyber risk across your organization. The platform provides powerful risk insights, earlier threat detection, and automated risk and threat response options. Utilize the platform’s predictive machine learning and advanced security analytics for a broader perspective and advanced context. TrendAI Vision One integrates with its own expansive protection platform portfolio and industry-leading global threat intelligence, in addition to a broad ecosystem of purpose-built and API-driven third-party integrations.

Average Rating: 4.7/5.0

Total Reviews: 247

How Do G2 Users Rate TrendAI Vision One?

  • Ease of Admin: 8.7/10 (Category avg: 8.9/10)
  • Ease of Use: 8.6/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.3/10)
  • Quality of Support: 8.7/10 (Category avg: 9.2/10)

Who Is the Company Behind TrendAI Vision One?

  • Seller: TrendAI
  • Company Website:
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About TrendAI Vision One?

AI-generated summary from verified user reviews

Pros
  • Users value the unified visibility of TrendAI Vision One, enhancing security operations and reducing alert fatigue effectively.
  • Users commend the unified visibility of TrendAI Vision One, enhancing security operations through effective threat detection and response.
  • Users appreciate the ease of use of TrendAI Vision One, enjoying its intuitive dashboard and seamless navigation.
  • Users appreciate the unified visibility of TrendAI Vision One, enhancing security operations across multiple platforms seamlessly.
  • Users value the powerful threat detection capabilities of TrendAI Vision One, enhancing security response and visibility.
Cons
  • Users find the complex interface of TrendAI Vision One overwhelming, affecting navigation and usability significantly.
  • Users report integration issues with TrendAI Vision One, leading to complexities with setup and third-party tools.
  • Users report a challenging learning curve with TrendAI Vision One, making onboarding difficult for new teams.
  • Users note the high cost of TrendAI Vision One compared to similar products, impacting overall value perception.
  • Users note the limited features of TrendAI Vision One, especially in reporting and dynamic dashboard capabilities.

What Are Recent G2 Reviews of TrendAI Vision One?

What Are G2 Users Discussing About TrendAI Vision One?

Cortex Cloud

Cortex Cloud by Palo Alto Networks, the next version of Prisma Cloud, understands a unified security approach is essential for effectively addressing AppSec, CloudSec, and SecOps. Connecting cloud security and SOC workflows enables teams to achieve holistic visibility, trace risk across the lifecycle, and correlate real-time threat activity with development and runtime contexts. Cortex Cloud is a unified platform built on three core pillars: data integration, AI-driven intelligence, and automation. Now you can safeguard applications, data, and infrastructure across multicloud and hybrid environments with a unified data model that consolidates telemetry from code, runtime, identity, and endpoints, all into a single data source. Empower teams with precise, AI-powered insights and 2200+ machine learning models to identify and stop zero-day threats with real-time advanced threat detection and response. And automate with 1000+ prebuilt playbooks across your cloud stack to reduce manual workloads, accelerate remediations, and cut response times tenfold. Cortex Cloud delivers more than tools—it transforms how organizations secure their cloud environments.

Average Rating: 4.1/5.0

Total Reviews: 126

How Do G2 Users Rate Cortex Cloud?

  • Ease of Admin: 8.0/10 (Category avg: 8.9/10)
  • Ease of Use: 7.8/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 8.0/10 (Category avg: 9.3/10)
  • Quality of Support: 8.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Cortex Cloud?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 32% Medium

What Do G2 Reviewers Say About Cortex Cloud?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Cortex Cloud, promoting faster performance monitoring and streamlined decision-making.
  • Users appreciate the centralized data and analytics of Cortex Cloud, enhancing efficiency and decision-making across security operations.
  • Users appreciate the centralized security management of Cortex Cloud, streamlining workload management and enhancing operational efficiency.
  • Users appreciate the centralized visibility of Cortex Cloud, enhancing data monitoring and facilitating better decision-making.
  • Users value the seamless integration of Cortex Cloud, enhancing efficiency in managing resources across different environments.
Cons
  • Users note the expensive pricing of Cortex Cloud, making it less accessible for smaller teams or businesses.
  • Users find the difficult learning curve of Cortex Cloud can slow down adoption for new teams and users.
  • Users find the steep learning curve of Cortex Cloud challenging, especially for those unfamiliar with its advanced features.
  • Users express concerns over high and unclear pricing, which complicates budgeting and can escalate with scaling needs.
  • Users experience a complex setup with Cortex Cloud, often struggling with intuitive navigation and steep learning curves.

What Are Recent G2 Reviews of Cortex Cloud?

Barracuda Managed XDR

Barracuda Managed XDR is the comprehensive next-generation cybersecurity solution that protects organizations of all sizes against today’s ever-evolving threat landscape. Barracuda Managed XDR is a fully managed service instantly augmenting an organization’s IT staff, identifying signals amidst noise, and reducing TTR from days to seconds. The solution features advanced AI-driven threat protection, SIEM, SOAR, and enterprise-grade threat intelligence from 11+ billion IOCs and hundreds of ML-enriched detection rules aligned to the MITRE ATT&CK framework. Ingesting trillions of events across endpoints, servers, identity, cloud, email, and firewalls, the cloud-native solution detects, responds to, and eliminates cyberthreats in real time across the attack lifecycle. An ‘open’ XDR solution, Barracuda Managed XDR integrates with an organization’s existing technology, ensuring a smooth deployment while enhancing security resilience and operational efficiency. Barracuda Managed XDR is powered by Barracuda’s 24/7/365 global SOC, featuring five specialized expert-level teams delivering best-in-class SLAs and proactive real-time threat detection and response.

Average Rating: 4.5/5.0

Total Reviews: 53

How Do G2 Users Rate Barracuda Managed XDR?

  • Ease of Admin: 8.6/10 (Category avg: 8.9/10)
  • Ease of Use: 8.8/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Quality of Support: 9.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Barracuda Managed XDR?

  • Seller: Barracuda
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Campbell, CA
  • LinkedIn® Page: www.linkedin.com
    2,327 employees on LinkedIn®
  • Ownership: Private

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 50% Medium, 34% Small

What Do G2 Reviewers Say About Barracuda Managed XDR?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use and straightforward setup of Barracuda Managed XDR, enhancing overall security management.
  • Users appreciate the 24/7 proactive monitoring of Barracuda Managed XDR, enhancing security without overburdening tech teams.
  • Users value the 24/7 security and straightforward setup of Barracuda Managed XDR, enhancing protection effortlessly.
  • Users value the 24/7 security of Barracuda Managed XDR, ensuring proactive protection against cyber threats with minimal effort.
  • Users value the timely alerts from Barracuda Managed XDR, enhancing threat navigation and response efficiency.
Cons
  • Users find the lack of customization in Barracuda Managed XDR limits their ability to tailor reporting and management.
  • Users note a challenging learning curve with Barracuda Managed XDR, particularly during initial setup and feature navigation.
  • Users feel the interface is not user-friendly and desire more customization options, particularly for reporting and management.
  • Users find the portal issues cumbersome, requiring logins for endpoint management and complicating overall product handling.
  • Users find the agent on the endpoint device limited, requiring logins to the portal for program management.

What Are Recent G2 Reviews of Barracuda Managed XDR?

Arctic Wolf

Arctic Wolf® is the cybersecurity and AI company that ends cyber risk by transforming it into business resilience. Powered by the Aurora® Superintelligence Platform, Arctic Wolf delivers modern security operations built on proprietary AI and decades of real-world expertise to manage and mitigate cyber threats. The platform is built on the Swarm of Experts™, which coordinates specialized AI agents across core security operations functions. The Security Operations Graph™ connects real-world telemetry and customer context to every workflow. The AI Trust Engine™ validates outcomes and keeps human experts in the loop. Arctic Wolf serves businesses of all sizes looking to strengthen their cybersecurity posture. IT and security teams turn to Arctic Wolf to streamline operations, gain a clearer view of their security landscape, and build resilience against cyberattacks. Arctic Wolf's Aurora-branded solutions include Aurora® Managed Detection and Response (MDR), which provides 24x7 monitoring and rapid threat detection and response. Aurora® Attack Surface Management and Aurora® Vulnerability Management help organizations identify and remediate vulnerabilities to reduce their attack surface. Aurora® Endpoint Security safeguards devices against threats. Aurora® Security Awareness and Training helps employees reduce human error in cybersecurity. Aurora® Incident Response helps organizations respond when a security incident occurs. The Concierge Security® Team delivers personalized support, working closely with organizations to understand their unique challenges and build tailored strategies for stronger cyber resilience. By combining AI-driven automation with expert validated precision, Arctic Wolf helps organizations confidently manage cyber risk, so they can operate with control and the freedom to innovate.

Average Rating: 4.7/5.0

Total Reviews: 276

How Do G2 Users Rate Arctic Wolf?

  • Ease of Admin: 9.1/10 (Category avg: 8.9/10)
  • Ease of Use: 9.2/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.3/10)
  • Quality of Support: 9.4/10 (Category avg: 9.2/10)

Who Is the Company Behind Arctic Wolf?

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Hospital & Health Care, Information Technology and Services
  • Company Size: 71% Medium, 20% Large

What Do G2 Reviewers Say About Arctic Wolf?

AI-generated summary from verified user reviews

Pros
  • Users commend Arctic Wolf for its responsive customer support, ensuring effective collaboration and timely assistance during security incidents.
  • Users value the proactive threat detection of Arctic Wolf, ensuring timely alerts and expert support for security incidents.
  • Users value Arctic Wolf's proactive security approach, providing peace of mind and seamless team integration for threat management.
  • Users appreciate the ease of use of Arctic Wolf, highlighting its user-friendly interface and smooth deployment.
  • Users value the fast notifications of events, enabling quick engagement and effective issue triage with professionals.
Cons
  • Users highlight the high cost of Arctic Wolf, wishing it was more affordable despite its effectiveness.
  • Users note the issue of false positives in alerts, requiring time-consuming investigations despite overall satisfaction.
  • Users experience a steep learning curve, requiring time and IT knowledge to navigate Arctic Wolf's features effectively.
  • Users feel overwhelmed by the amount of cybersecurity risks detailed in reports and seek better notification methods.
  • Users face dashboard issues with quirks and delays in resolving identified risks, though updates are frequent.

What Are Recent G2 Reviews of Arctic Wolf?

What Are G2 Users Discussing About Arctic Wolf?

Sysdig Secure

Sysdig Secure is the real-time cloud-native application protection platform (CNAPP) trusted by organizations of all sizes around the world.. Built by the creators of Falco and Wireshark, Sysdig uniquely delivers runtime-powered visibility and agentic AI to stop cloud attacks instantly, not after the damage is done. With Sysdig, you can: - Stop threats in 2 seconds and respond in minutes - Cut vulnerability noise by 95% with runtime prioritization - Detect real risk instantly across workloads, identities, and misconfigurations - Close permissions gaps in under 2 minutes Sysdig Secure consolidates CSPM, CWPP, CIEM, vulnerability management, and threat detection into a single open, real-time platform. Unlike other CNAPPs, Sysdig connects signals across runtime, identity, and posture to eliminate blind spots, reduce tool sprawl, and accelerate innovation without compromise. No guesswork. No black boxes. Just cloud security, the right way. Learn more at https://sysdig.com

Average Rating: 4.8/5.0

Total Reviews: 110

How Do G2 Users Rate Sysdig Secure?

  • Ease of Admin: 9.3/10 (Category avg: 8.9/10)
  • Ease of Use: 9.3/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.3/10)
  • Quality of Support: 9.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Sysdig Secure?

  • Seller: Sysdig
  • Company Website:
  • Year Founded: 2013
  • HQ Location: San Francisco, California
  • LinkedIn® Page: www.linkedin.com
    556 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 47% Large, 40% Medium

What Do G2 Reviewers Say About Sysdig Secure?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Sysdig Secure, ensuring real-time protection for cloud-native environments.
  • Users value the in-depth runtime threat detection in Sysdig Secure, ensuring quick responses to potential vulnerabilities.
  • Users value the in-depth runtime threat detection of Sysdig Secure, ensuring robust security for VM workloads and Kubernetes.
  • Users value the in-depth runtime threat detection of Sysdig Secure, ensuring swift response to potential security breaches.
  • Users value the impressive UI and comprehensive features of Sysdig Secure, enhancing security and compliance efforts.
Cons
  • Users encounter feature limitations with Sysdig Secure, impacting vulnerability assessments and KSPM functionalities.
  • Users find the initial setup too complex, seeking a more streamlined and simplified configuration process for Sysdig Secure.
  • Users find the missing features in Sysdig Secure, like on-demand vulnerability assessment, limiting their experience.
  • Users find the difficult learning curve of Sysdig Secure challenging, complicating deployment and integration processes.
  • Users find the initial setup complexity of Sysdig Secure to be a significant drawback in their experience.

What Are Recent G2 Reviews of Sysdig Secure?

What Are G2 Users Discussing About Sysdig Secure?

Orca Security

The Orca Cloud Security Platform identifies, prioritizes, and remediates risks and compliance issues in workloads, configurations, and identities across your cloud estate spanning AWS, Azure, Google Cloud, Kubernetes, Alibaba Cloud, and Oracle Cloud. Orca offers the industry’s most comprehensive cloud security solution in a single platform — eliminating the need to deploy and maintain multiple point solutions. Orca is agentless-first, and connects to your environment in minutes using Orca’s patented SideScanning™ technology that provides deep and wide visibility into your cloud environment, without requiring agents. In addition, Orca can integrate with third-party agents for runtime visibility and protection for critical workloads. Orca is at the forefront of leveraging Generative AI for simplified investigations and accelerated remediation – reducing required skill levels and saving cloud security, DevOps, and development teams time and effort, while significantly improving security outcomes. As a Cloud Native Application Protection Platform (CNAPP), Orca consolidates many point solutions in one platform, including: CSPM, CWPP, CIEM, Vulnerability Management, Container and Kubernetes Security, DSPM, API Security, CDR, Multi-cloud Compliance, Shift Left Security, and AI-SPM.

Average Rating: 4.7/5.0

Total Reviews: 314

How Do G2 Users Rate Orca Security?

  • Ease of Admin: 9.0/10 (Category avg: 8.9/10)
  • Ease of Use: 9.2/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.3/10)
  • Quality of Support: 9.1/10 (Category avg: 9.2/10)

Who Is the Company Behind Orca Security?

  • Seller: Orca Security
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Portland, Oregon
  • LinkedIn® Page: www.linkedin.com
    523 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, Senior Security Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 54% Large, 36% Medium

What Do G2 Reviewers Say About Orca Security?

AI-generated summary from verified user reviews

Pros
  • Users highly value the ease of use of Orca Security, enabling quick setup and intuitive navigation.
  • Users value the agentless feature and intuitive interface of Orca Security, enhancing their security management experience.
  • Users commend Orca Security for its comprehensive cloud security capabilities, providing valuable insights and a seamless experience.
  • Users appreciate the user-friendly interface of Orca Security, finding it easy to navigate and understand.
  • Users praise the visibility provided by Orca Security, gaining comprehensive insights into their cloud environment effortlessly.
Cons
  • Users note that the reporting capabilities and customization options of Orca Security need significant improvement.
  • Users find feature limitations in Orca Security, highlighting issues with vulnerability reporting and asset scan capabilities.
  • Users experience limited features in Orca Security, hindering functionality and complicating tasks like report generation.
  • Users face missing features in Orca Security, including limited compliance modules and export functionality challenges.
  • Users experience ineffective alerts from Orca Security, leading to confusion and alert fatigue due to overloaded information.

What Are Recent G2 Reviews of Orca Security?

What Are G2 Users Discussing About Orca Security?

Cortex XDR

Cortex XDR is the industry’s first extended detection and response platform that stops modern attacks by integrating data from any source. With Cortex XDR, you can harness the power of AI, analytics and rich data to detect stealthy threats. Your SOC team can cut through the noise and focus on what matters most with intelligent alert grouping and incident scoring. Cross-data insights accelerate investigations, so you can streamline incident response and recovery. Cortex XDR delivers peace of mind with best-in-class endpoint protection that achieved the highest combined protection and detection scores in the MITRE ATT&CK® round 3 evaluation. The Cortex XDR platform collects and analyzes all data, so you can gain complete visibility and holistic protection to secure what’s next.

Average Rating: 4.5/5.0

Total Reviews: 89

How Do G2 Users Rate Cortex XDR?

  • Ease of Admin: 8.5/10 (Category avg: 8.9/10)
  • Ease of Use: 8.4/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.3/10)
  • Quality of Support: 8.7/10 (Category avg: 9.2/10)

Who Is the Company Behind Cortex XDR?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 40% Medium, 39% Large

What Do G2 Reviewers Say About Cortex XDR?

AI-generated summary from verified user reviews

Pros
  • Users praise the ease of use of Cortex XDR, highlighting its simple interface and excellent manageability.
  • Users value the rapid and accurate threat detection in Cortex XDR, enhancing their security and efficiency.
  • Users value the unified detection and response capability of Cortex XDR for efficient threat investigation.
  • Users value the intelligent alert system of Cortex XDR, which minimizes unnecessary notifications and enhances focus.
  • Users value the advanced AI technology in Cortex XDR, which delivers relevant alerts without overwhelming notifications.
Cons
  • Users experience a performance impact on lower-end systems with the Cortex XDR agent installed, complicating usability.
  • Users face compatibility issues with Cortex XDR, as it restricts core functionalities of the operating system.
  • Users find the complexity of Cortex XDR challenging due to its steep learning curve and management demands.
  • Users find the complex management of Cortex XDR challenging, especially when customizing detections and tuning policies.
  • Users find the difficult learning curve of Cortex XDR challenging, especially when tuning policies and customizing detections.

What Are Recent G2 Reviews of Cortex XDR?

What Are G2 Users Discussing About Cortex XDR?

Blackpoint Cyber

Blackpoint Cyber is the forerunner in the managed detection and response space, leveraging our proprietary ecosystem to help our partners fight back and win against cyberthreats. We have served the community since 2014 and proudly continue to safeguard businesses around the world. We believe that no one should go alone into the unfair fight. At Blackpoint, our team strives to provide unified, 24/7 detection to help you take out your adversaries before they can even see us coming.

Average Rating: 4.7/5.0

Total Reviews: 257

How Do G2 Users Rate Blackpoint Cyber?

  • Ease of Admin: 9.2/10 (Category avg: 8.9/10)
  • Ease of Use: 9.2/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Quality of Support: 9.6/10 (Category avg: 9.2/10)

Who Is the Company Behind Blackpoint Cyber?

Who Uses This Product?

  • Who Uses This: President, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 82% Small, 17% Medium

What Do G2 Reviewers Say About Blackpoint Cyber?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the quick and effective customer support from Blackpoint Cyber, enhancing their overall experience.
  • Users value the exceptional threat detection from Blackpoint Cyber, ensuring rapid response and effective remediation of security incidents.
  • Users find deployment quick and easy with Blackpoint Cyber, enhancing integration and overall user experience.
  • Users commend the quick and easy setup process of Blackpoint Cyber, enhancing their overall experience significantly.
  • Users value the responsiveness and support of the SOC team, praising their 24/7 protection and efficiency.
Cons
  • Users find the service expensive, making it less appealing for those seeking basic coverage or small scale solutions.
  • Users face integration issues with Blackpoint Cyber, lacking essential information and compatibility with other solutions.
  • Users find poor reporting capabilities hinder effective asset management and regulatory compliance across their client base.
  • Users find the portal issues challenging, as navigation is clunky and the UI lacks smoothness.
  • Users find the difficult navigation of Blackpoint Cyber challenging, complicating access to important information and settings.

What Are Recent G2 Reviews of Blackpoint Cyber?

What Are G2 Users Discussing About Blackpoint Cyber?

SaaS Alerts

​​SaaS Alerts is a automated cybersecurity platform to detect and automate the remediation of SaaS security threats. The platform provides unified, continuous monitoring of core business SaaS applications to protect against data theft and malicious actors, including Microsoft 365, Google Workspace, Salesforce, Slack, Dropbox, Okta, Duo and more. SaaS Alerts uses machine learning pattern detection to identify breaches, create instant alerts, and lock affected accounts, providing you with valuable time to respond before further damage can occur. It also enables you to terminate dangerous end-user file sharing activities and automate essential security tasks, enhancing efficiency and overall security.

Average Rating: 4.4/5.0

Total Reviews: 35

How Do G2 Users Rate SaaS Alerts?

  • Ease of Admin: 8.9/10 (Category avg: 8.9/10)
  • Ease of Use: 7.9/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Quality of Support: 9.1/10 (Category avg: 9.2/10)

Who Is the Company Behind SaaS Alerts?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 86% Small, 14% Medium

What Do G2 Reviewers Say About SaaS Alerts?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time alerts from SaaS Alerts, enhancing security monitoring and improving response times to unusual activities.
  • Users praise the ease of use of SaaS Alerts, appreciating its intuitive interface and straightforward navigation.
  • Users appreciate the real-time alert notifications from SaaS Alerts, enhancing confidence in monitoring user activity effectively.
  • Users appreciate the easy setup and regular innovative features that enhance the overall SaaS Alerts experience.
  • Users find the reporting capabilities of SaaS Alerts invaluable for identifying security vulnerabilities effortlessly.
Cons
  • Users find the ineffective alerts lead to wasted time on non-urgent issues, highlighting a need for better filtering.
  • Users find the inefficient alert system requires extra time for investigating notifications, disrupting workflow and productivity.
  • Users note false positives initially, but the system improves as it learns to filter them effectively.
  • Users find the inadequate filtering capabilities of SaaS Alerts lead to unnecessary time spent on non-urgent issues.
  • Users find the inefficient filtering of SaaS Alerts often leads to unnecessary time spent on non-actionable alerts.

What Are Recent G2 Reviews of SaaS Alerts?

UnderDefense MAXI

UnderDefense is an Agentic AI SOC & Compliance Automation platform trusted by 200+ enterprises in the US and EU. It works on top of the security stack you already own — no rip-and-replace, no added headcount — so your team spends its time on decisions, not triage. ◆ 10+ years of operations with zero ransomware incidents ◆ 250+ integrations across any SIEM, EDR, or cloud stack ◆ 24/7 IR team available whenever you need urgent support WHAT WE OFFER AGENTIC AI SOC UnderDefense Agentic AI SOC works on top of your existing security stack, turning every security team into a machine-speed defense unit without tool replacement or headcount expansion. It takes over the investigative routine that pulls your team away from strategic decisions: enrichment, correlation, triage. ▸ Investigation at Machine Speed: Agentic AI SOC accesses tools, enriches data, and performs deep cross-environment investigations at machine speed. It correlates, triages, and forms conclusions, offloading all repetitive work from your team. ▸ 2 Minutes Per Alert: Complete SIEM queries, threat intel checks, and cross-system correlations in 2 minutes. Every step fully observable and auditable. ▸ Human at Every Decision Point: The platform verifies suspicious activity with end-users via Slack or Teams, then routes containment decisions to your team or our 24/7 IR experts. COMPLIANCE AUTOMATION Stop chasing spreadsheets. UnderDefense MAXI Compliance AI automatically collects continuous evidence across ISO 27001, SOC 2, PCI DSS, GDPR, and HIPAA, and publishes your live posture through a shareable Trust Center link. ▸ 40% audit-ready in the first 40 minutes ▸ 2X faster time-to-compliance vs. traditional audit ▸ 24/7 continuous monitoring — posture always current, not point-in-time WHY WE ARE BETTER ✓ No rip-and-replace: Works with your current SIEM (Splunk, Sentinel, Chronicle, QRadar, Elastic), EDR, and cloud tools. Logs stay in your data lake. ✓ True Multi-Environment Coverage: Comprehensive visibility across on-premises, cloud (AWS, GCP, Azure), SaaS, network, identity, and OT/SCADA environments. ✓ The Only Agentic AI SOC with on-prem deployment: Full AI SOC inside your own infrastructure. No telemetry leaving your environment. Air-gapped available. ✓ Right-Sized for Any Enterprise: Detection engineering and support tailored to your organization, not a one-size-fits-all template. Start your free trial at underdefense.com

Average Rating: 5.0/5.0

Total Reviews: 82

How Do G2 Users Rate UnderDefense MAXI?

  • Ease of Admin: 9.6/10 (Category avg: 8.9/10)
  • Ease of Use: 9.8/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Quality of Support: 9.9/10 (Category avg: 9.2/10)

Who Is the Company Behind UnderDefense MAXI?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Information Technology and Services, Marketing and Advertising
  • Company Size: 54% Small, 40% Medium

What Do G2 Reviewers Say About UnderDefense MAXI?

AI-generated summary from verified user reviews

Pros
  • Users value the high visibility UnderDefense MAXI provides into security alerts, streamlining threat management and response.
  • Users commend the responsive and effective customer support of UnderDefense MAXI, enhancing their cybersecurity management and experience.
  • Users commend UnderDefense MAXI for its effective cybersecurity solutions, enhancing security management and response efficiency.
  • Users value the information accuracy provided by UnderDefense, which clarifies security issues and enhances response efficiency.
  • Users highlight the quick issue resolution by UnderDefense, improving security alert management and enhancing overall security operations.
Cons
  • Users feel a lack of automation features limits control over the dashboard for UnderDefense MAXI.
  • Users desire more control over the dashboard, seeking enhanced customization and automated update options with UnderDefense MAXI.
  • Users note that limited integration requires significant setup time to ensure proper tool configuration.
  • Users find the setup process challenging, requiring significant time and effort for proper tool integration.

What Are Recent G2 Reviews of UnderDefense MAXI?

Upwind

Upwind is the runtime-first cloud security platform that secures your deployments, configurations, and applications by providing real-time visibility from the inside out. We’ve built a unified fabric that maps your environment as it runs - revealing what’s truly at risk, what’s actively happening, and how to respond quickly and effectively. With Upwind, security, dev, and ops teams move faster, stay focused, and fix risks that matter most.

Average Rating: 4.9/5.0

Total Reviews: 10

How Do G2 Users Rate Upwind?

  • Ease of Admin: 9.5/10 (Category avg: 8.9/10)
  • Ease of Use: 9.0/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Upwind?

  • Seller: Upwind
  • Company Website:
  • Year Founded: 2022
  • HQ Location: San Francisco, California, United States
  • LinkedIn® Page: www.linkedin.com
    537 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Medium, 30% Large

What Do G2 Reviewers Say About Upwind?

AI-generated summary from verified user reviews

Pros
  • Users find Upwind to be very easy to use, appreciating its quick support and real-time functionality.
  • Users appreciate Upwind for its excellent visibility, enhancing risk posture and simplifying threat identification.
  • Users praise the quick and responsive customer support of Upwind, enhancing overall satisfaction and experience.
  • Users commend the real-time detection efficiency of Upwind, enabling swift threat identification and resolution.
  • Users commend the implementation ease of Upwind, highlighting its smooth integration into AWS environments.
Cons
  • Users find that the alert overload from numerous vulnerability findings can be quickly overwhelming and distracting.
  • Users note compliance issues with Upwind, particularly regarding NIST and GDPR reporting requirements.
  • Users face challenges with bulk alert resolution in Upwind, limiting effective data management capabilities.
  • Users find the data overload from numerous vulnerability findings to be overwhelming and difficult to manage.
  • Users face challenges with false positives, leading to difficulties in alert management and resolution.

What Are Recent G2 Reviews of Upwind?

Vectra AI Platform

The Vectra AI Platform helps security teams detect and stop real attacks that evade traditional security controls across network, identity, cloud, and SaaS environments. It provides real-time visibility into how attackers move through hybrid and multi-cloud environments, enabling teams to understand attack activity early and respond before incidents escalate. By correlating attacker behavior across the full attack lifecycle, the platform reduces alert noise and surfaces high-confidence threats that matter most. Analysts spend less time triaging isolated alerts and more time investigating complete attack stories with the context needed to take decisive action. Vectra AI unifies detection, investigation, and coordinated response across identity, endpoint, and network controls. Its approach is aligned with real-world defensive techniques, reflected in the highest number of vendor references in MITRE D3FEND and recognition as a Leader in the 2025 Gartner® Magic Quadrant™ for Network Detection and Response. Organizations worldwide rely on Vectra AI to detect attacks others miss and demonstrate measurable improvements in security operations.

Average Rating: 4.3/5.0

Total Reviews: 20

How Do G2 Users Rate Vectra AI Platform?

  • Ease of Admin: 8.1/10 (Category avg: 8.9/10)
  • Ease of Use: 8.4/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 8.1/10 (Category avg: 9.3/10)
  • Quality of Support: 8.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Vectra AI Platform?

  • Seller: Vectra AI
  • Year Founded: 2011
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    669 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 75% Large, 15% Medium

What Do G2 Reviewers Say About Vectra AI Platform?

AI-generated summary from verified user reviews

Pros
  • Users find the ease of understanding Vectra AI Platform offers makes it simple to learn and use effectively.
  • Users find Vectra AI Platform to be easy to work with, benefiting from its clear learning methods.

What Are Recent G2 Reviews of Vectra AI Platform?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024

Learn More About Cloud Detection and Response (CDR) Software

Cloud Detection and Response (CDR) FAQs

Most Popular FAQs

Which Cloud Detection and Response (CDR) has the best reviews?

Based on verified user ratings and review sentiment across this category, these CDR platforms stand out for overall satisfaction, usability, and security value:

  • Wiz - A cloud-native security platform known for agentless visibility, strong risk prioritization, and broad coverage across complex cloud environments.
  • Sysdig Secure - A runtime-focused cloud security platform highly rated for container visibility, threat detection depth, and strong support for Kubernetes-heavy environments.
  • Trend Vision One - An extended detection and response platform recognized for unifying cloud threat visibility with broader security operations workflows.
  • Upwind - A newer cloud security platform earning strong marks for investigation speed, runtime context, and clear prioritization of active cloud risks.
What is cloud detection and response (CDR) security?

Cloud Detection and Response (CDR) security is a category of software designed to detect, investigate, and respond to threats across cloud infrastructure, workloads, identities, and applications. Unlike traditional security tools that focus primarily on endpoints or network perimeters, CDR platforms are built to understand the dynamic nature of cloud environments, where assets change rapidly, and attack surfaces are highly distributed. These tools help security teams correlate suspicious activity, identify exposed resources, prioritize exploitable risks, and accelerate incident response using cloud-specific context. In practice, organizations use CDR software to reduce alert noise, improve visibility across multi-cloud estates, and shorten the time between threat detection and remediation.

Which CDR software offers the fastest response times?

The CDR tools that feel fastest in practice are typically the ones that combine strong alert prioritization with investigation workflows that are easy to act on:

  • Upwind - A cloud detection platform designed to surface runtime threats quickly and help security teams move from alert to action with minimal investigation overhead.
  • Blackpoint Cyber - A managed security platform frequently praised for responsiveness, fast triage, and operational support that reduces burden on internal teams.
  • Barracuda Managed XDR - A managed detection and response solution suited to teams that want guided response workflows and faster escalation support.
  • Trend Vision One - A broad security operations platform that helps teams detect and investigate threats quickly across cloud and adjacent environments.
Which CDR solution offers AI-powered threat analysis?

AI-powered cloud detection tools are increasingly valued for helping analysts reduce noise, identify meaningful attack paths, and prioritize incidents more effectively. The following platforms stand out in that area:

  • Cortex Cloud - A cloud security platform built to connect analytics, automation, and threat context for faster triage and investigation.
  • CrowdStrike Falcon Cloud Security - A cloud security offering that combines strong detection logic with broader telemetry and threat intelligence across environments.
  • Vectra AI Platform - An AI-driven detection platform built to identify attacker behavior patterns and surface higher-confidence threats for security teams.
  • Wiz - A cloud-native platform that uses contextual analysis and attack path mapping to help teams prioritize the risks most likely to matter.
What is CDR vs EDR?

CDR and EDR solve related but distinct security problems. EDR, or Endpoint Detection and Response, is built to monitor and protect endpoints such as laptops, servers, and workstations by identifying suspicious behavior at the device level. CDR, or Cloud Detection and Response, is designed to protect cloud infrastructure, workloads, identities, and services by detecting threats inside cloud environments. While EDR focuses on endpoint telemetry and device-based attack activity, CDR provides visibility into cloud-native risks such as exposed resources, identity misuse, runtime anomalies, and lateral movement across cloud assets. Organizations with hybrid environments often use both, with EDR covering devices and CDR covering cloud operations.

Small Business FAQs

What is the most affordable Cloud Detection and Response (CDR) for SMBs?

For small and mid-sized businesses, affordable CDR software typically means balancing meaningful cloud visibility with a manageable total cost of ownership.

  • ARMO Platform - A cloud-native security platform that appeals to smaller teams looking for strong Kubernetes and cloud workload visibility without a heavyweight implementation model.
  • Microsoft Defender for Cloud - A pragmatic option for SMBs already operating in Microsoft environments that want native cloud security coverage with familiar administrative controls.
  • SaaS Alerts - A lightweight monitoring and alerting solution suited to smaller teams that need visibility into suspicious activity without adopting a full enterprise security stack.
  • Barracuda Managed XDR - A managed security option that can reduce staffing pressure for SMBs that need faster detection and guided response support.
What is the best Cloud Detection and Response (CDR) for startups?

Startups need CDR software for small businesses that can be implemented quickly, supports lean security teams, and scales as cloud environments become more complex. 

  • Blackpoint Cyber - A strong fit for startups that want responsive support and practical threat response without building a large internal SOC.
  • ARMO Platform - A cloud-native platform that suits startups running containerized workloads and looking for fast deployment with modern architecture support.
  • Sonrai Security - A cloud security platform focused on identity and permissions risk, making it useful for startups trying to secure fast-growing cloud estates.
  • Orca Security - A cloud security platform that helps startups gain rapid visibility into risks without introducing extensive operational overhead.
Which Cloud Detection and Response (CDR) is the most user-friendly for startups?

Ease of use is a major priority for startup teams that do not have time for lengthy onboarding or complex administration. Among the products reviewed in this category, these platforms stand out for usability and approachability:

  • Blackpoint Cyber - Frequently recognized for a straightforward operating model and strong customer support that helps teams get value quickly.
  • Microsoft Defender for Cloud - A good fit for startups that want a familiar interface and manageable controls inside an existing Microsoft ecosystem.
  • Sysdig Secure - A strong option for startups with containerized environments that need deep visibility without sacrificing day-to-day usability.
  • Barracuda Managed XDR - A practical choice for lean teams that want cloud threat coverage supported by a managed service model.
What is the best CDR software for small security teams?

Small security teams typically need software that reduces manual correlation work, limits alert fatigue, and helps analysts move quickly without deep platform specialization. These options stand out for that use case:

  • SaaS Alerts - A lightweight option for smaller teams that want targeted alerting and easier oversight of suspicious cloud-related activity.
  • Blackpoint Cyber - A strong fit for teams that want fast response support and less operational burden on internal staff.
  • Microsoft Defender for Cloud - A sensible choice for small teams already committed to Microsoft cloud infrastructure and security tooling.
  • ARMO Platform - A cloud-native option that helps smaller teams get clear visibility into workloads and risks without a large deployment footprint.
What CDR tools are best for cloud-native startups running containers?

Startups running containerized infrastructure need CDR tools that understand runtime behavior, Kubernetes environments, and fast-changing cloud workloads. These products are especially well aligned to that operating model:

  • Sysdig Secure - Built for container and Kubernetes security with strong runtime detection and investigation capabilities.
  • ARMO Platform - Designed for modern cloud-native environments with a focus on container visibility and workload protection.
  • Upwind - A strong option for startups that want runtime context and fast threat prioritization across dynamic cloud workloads.
  • Orca Security - A practical fit for fast-moving teams that need broad cloud risk visibility with less deployment overhead.

Enterprise FAQs

What is the best-rated Cloud Detection and Response (CDR) for tech enterprises?

Technology enterprises require CDR platforms that can scale across large cloud estates, support complex workflows, and deliver meaningful context to security teams. 

  • Wiz - A leading enterprise cloud security platform known for broad visibility, agentless deployment, and strong prioritization across large environments.
  • CrowdStrike Falcon Cloud Security - A strong fit for enterprises that want cloud threat detection connected to a broader security operations ecosystem.
  • Trend Vision One - A unified security operations platform valued by enterprises seeking cloud detection alongside extended detection and response coverage.
  • Cortex Cloud - A strong option for enterprise teams that want cloud threat analysis connected to automation and larger SecOps workflows.
What is the most reliable Cloud Detection and Response (CDR) tool for enterprises?

Enterprise buyers consistently prioritize platform stability, detection accuracy, and operational reliability at scale. These products stand out most clearly on those criteria:

  • Wiz - Frequently recognized for dependable cloud visibility, consistent prioritization, and strong operational fit across complex environments.
  • Arctic Wolf - A security operations platform well suited to enterprises that value reliability, guided response, and managed support.
  • ReliaQuest GreyMatter - A strong enterprise option for organizations that need coordinated detection and response across multiple security tools.
  • Cortex XDR - A mature detection and response platform valued for stability, visibility, and strong fit within larger enterprise SOC programs.
What is the best-reviewed Cloud Detection and Response (CDR) for enterprise app integration?

Integration depth matters significantly for enterprise buyers that need CDR software to connect with broader cloud, security, and IT workflows. These products stand out for integration potential and ecosystem fit:

  • CrowdStrike Falcon Cloud Security - A strong choice for enterprises that want cloud threat detection closely integrated with endpoint, identity, and SOC workflows.
  • Microsoft Defender for Cloud - A practical enterprise option for organizations already standardized on Microsoft infrastructure and security tooling.
  • Cortex Cloud - Well-suited to enterprises that want cloud detection workflows tied into broader Palo Alto Networks security operations tooling.
  • Open XDR Security Operations Platform - A good fit for enterprises looking to integrate cloud detections into a wider cross-platform response environment.
What is the best enterprise CDR for managed security teams?

Organizations operating hybrid internal-and-managed security models need CDR platforms that support visibility, escalation, and response coordination without creating workflow friction. These platforms are especially relevant for that use case:

  • Arctic Wolf - A managed security platform built for enterprises that want cloud threat detection supported by expert guidance and ongoing monitoring.
  • ReliaQuest GreyMatter - A strong fit for enterprises that need to unify data, workflows, and response actions across a broad security stack.
  • Barracuda Managed XDR - A practical option for enterprises looking for faster response and external expertise without building everything internally.
  • Blackpoint Cyber - A useful choice for enterprises that value responsive managed support and streamlined threat handling.
What is the best enterprise CDR with AI-powered threat prioritization?

AI-assisted prioritization is increasingly important for enterprise cloud security teams managing high alert volume across distributed environments. These platforms stand out for helping analysts focus on the threats most likely to matter:

  • Wiz - Uses contextual analysis and attack path mapping to help enterprise teams prioritize the most actionable cloud risks.
  • Vectra AI Platform - Built around AI-driven detection logic that helps identify attacker behavior across complex environments.
  • CrowdStrike Falcon Cloud Security - A strong enterprise platform for teams that want cloud threat analysis backed by a mature detection ecosystem.
  • Cortex Cloud - Connects analytics and automation to help large security teams reduce noise and accelerate response decisions.

Last updated on April 23, 2026