Best Application Security Posture Management (ASPM) Software

How Many Application Security Posture Management (ASPM) Software Products Does G2 Track?

Total Products under this Category: 50

Category Stats (Nov 2026)

  • Average Rating: 4.53/5 (↓0.02 vs Oct 2026) The average rating of products in this category, based on all submitted ratings

Last updated: November 01, 2026

How Does G2 Rank Application Security Posture Management (ASPM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,300+ Authentic Reviews
  • 50+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

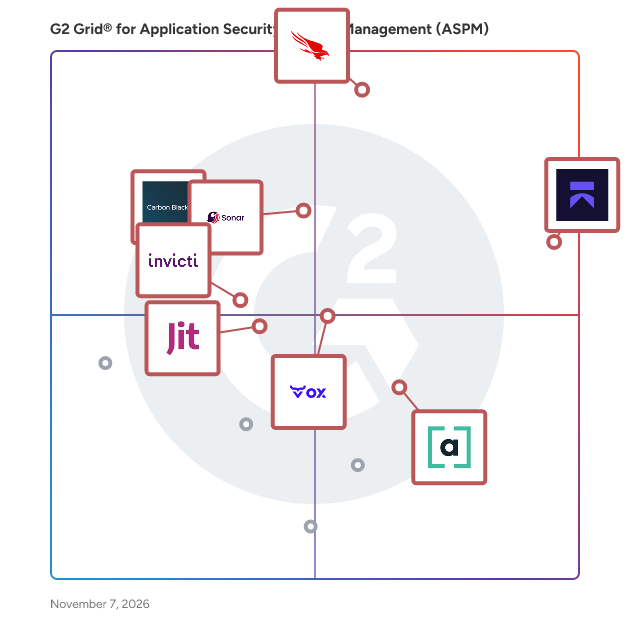
G2 Grid® for Application Security Posture Management (ASPM) Software

G2 Grid® for Application Security Posture Management (ASPM) Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, CrowdStrike Falcon Cloud Security, SonarQube, OX Security, Arnica, Invicti, Jit, and Carbon Black App Control.

Underlying data: [Grid® JSON](https://www.g2.com/categories/application-security-posture-management-aspm/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=sonarqube&focus%5B%5D=ox-security&focus%5B%5D=arnica&focus%5B%5D=invicti&focus%5B%5D=jit&focus%5B%5D=carbon-black-app-control)

Aikido Security

Aikido Security is the developer-first security platform that unifies code, cloud, protection, and attack testing in one suite of best-in-class products. Built by developers for developers, Aikido helps teams of any size ship secure software faster, automate protection, and simulate real-world attacks with AI-driven precision. The platform’s proprietary AI cuts noise by 95%, delivers one-click fixes, and saves developers 10+ hours per week. Aikido Intel proactively uncovers vulnerabilities in open source packages before disclosure, helping secure more than 50,000 organizations worldwide, including Revolut, Niantic, Visma, Montblanc, and GoCardless.

Average Rating: 4.5/5.0

Total Reviews: 272

Who Is the Company Behind Aikido Security?

  • Seller: Aikido Security
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Ghent, Belgium
  • LinkedIn® Page: www.linkedin.com
    320 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Founder, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 78% Small, 15% Medium

What Do G2 Reviewers Say About Aikido Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Aikido Security, thanks to its clear insights and seamless integration.
  • Users appreciate Aikido Security's robust security capabilities, providing a comprehensive and seamless integration in their workflow.
  • Users value the intuitive dashboard of Aikido Security, which simplifies security issue identification and management.
  • Users value the easy integrations of Aikido Security, enhancing workflows with seamless connections to existing GitLab repositories.
  • Users find Aikido's easy setup highly efficient, enabling quick implementation and immediate usability for security assessments.
Cons
  • Users note the lack of advanced features in Aikido Security, such as dark mode and in-depth analysis options.
  • Users find the pricing structure expensive for micro businesses, making upgrades difficult to justify.
  • Users note the limited features of Aikido Security, wishing for more customization and advanced options.
  • Users find the pricing issues challenging, especially for micro businesses, due to the steep upgrade costs.
  • Users feel Aikido Security is lacking features like advanced reporting and deeper compliance analysis compared to competitors.

What Are Recent G2 Reviews of Aikido Security?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 242

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Large, 31% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

SonarQube

Sonar, the industry standard for code verification and automated code review, helps reduce outages, improve security, and lower risks associated with AI and agentic coding. As an independent verification platform, Sonar enables organizations to securely develop at the speed of AI. Sonar is the foundation for high-performance software engineering, analyzing over 750 billion lines of code daily to ensure applications are secure, reliable, and maintainable. Rooted in the open source community, Sonar is trusted by 7M+ developers globally, including teams at ServiceNow, Booking.com, Deutsche Bank, AstraZeneca, and Ford Motor Company.

Average Rating: 4.4/5.0

Total Reviews: 161

Who Is the Company Behind SonarQube?

  • Seller: Sonar
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Geneva, Switzerland
  • LinkedIn® Page: www.linkedin.com
    1,041 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Large, 40% Medium

What Do G2 Reviewers Say About SonarQube?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the high-quality code analysis from SonarQube, ensuring cleaner, more reliable, and maintainable code.
  • Users appreciate SonarQube's separation of new and old code, enhancing prioritization of findings and improving overall code quality.
  • Users appreciate the effective issue identification of SonarQube, which enhances code quality and facilitates timely resolutions.
  • Users appreciate the ease of use of SonarQube, highlighting its simple setup and seamless CI/CD integration.
  • Users appreciate the easy integrations of SonarQube with CI/CD workflows, enhancing overall code quality and efficiency.
Cons
  • Users often face software bugs in SonarQube, leading to confusion with false positives and complex error messages.
  • Users find the complex configuration of SonarQube challenging, especially with initial setup and rule tuning in large projects.
  • Users report experiencing false positives that necessitate extra time for manual review and adjustments.
  • Users find the configuration complexity of SonarQube challenging, particularly with large projects and excessive warnings.
  • Users find the initial setup and configuration complex, especially for large projects, requiring time and careful tuning.

What Are Recent G2 Reviews of SonarQube?

What Are G2 Users Discussing About SonarQube?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

OX Security

OX rewires your security program for the Mythos Age: the era where AI writes the code, chains the exploits, and moves faster than human-built defenses can track. OX is an AI Native Application Protection Platform (AINAPP) unifying security from Prompt to Runtime. It moves your control surface upstream to the prompt, preventing and governing risk at the source instead of chasing it downstream in runtime. OX Mind and OX AI Context Lake connect AI-user governance, code security, cloud and runtime enforcement, and agentic pentesting into one system that shares context across the entire Agentic Development Lifecycle (ADLC), replacing fragmented point tools with a single platform. The platform runs on four connected pillars: OX VibeSec: Prevents unsafe AI decisions at the point of creation and governs every AI user in the organization, not just developers using coding assistants. Full visibility into which agents, MCPs, skills, and packages run, with what permissions, against what data. OX Code: Separates exploitable risk from theoretical noise using evidence from your actual deployment, threat model, and threat intelligence. OX Cloud: Prevents misconfigurations and enforces runtime boundaries that code and agents cannot cross, watching what actually runs in production. OX Agentic Pentester: Continuously simulates adversarial agent behavior to prove exploit paths back to their exact source, feeding what it finds back into OX VibeSec to sharpen governance. OX connects to your existing stack and traces every finding back to its origin (the prompt, the AI user, or the endpoint that created it), then fixes issues at the source rather than flagging them after the fact. For new deployments, OX consolidates governance, code security, cloud enforcement, and pentesting into one platform. For existing stacks, OX layers governance on top and makes current tools smarter through continuous learning, so the same issue never gets created twice. Visit https://ox.security for more information.

Average Rating: 4.8/5.0

Total Reviews: 51

Who Is the Company Behind OX Security?

Who Uses This Product?

  • Who Uses This: Security Engineer
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 25% Large

What Do G2 Reviewers Say About OX Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the seamless integration and comprehensive features of OX Security, enhancing efficiency and issue management.
  • Users appreciate the ease of use of OX Security, highlighting its user-friendly interface and quick setup.
  • Users commend the great support team from OX Security, enhancing their overall experience and success.
  • Users value the seamless integration with existing tools, enhancing security without disrupting workflows or creating bottlenecks.
  • Users value the comprehensive security capabilities of OX Security, enhancing their organization's security posture effectively.
Cons
  • Users experience integration issues with OX Security, citing incomplete documentation and limited functionality in certain areas.
  • Users note the missing features in OX Security, impacting usability and integration with certain platforms and systems.
  • Users find OX Security's complexity overwhelming, with a steep learning curve and inadequate documentation frustrating the experience.
  • Users find the inadequate reporting in OX Security limits their ability to showcase security progress effectively.
  • Users note the limited cloud integration with tools like Azure DevOps, affecting ease of use and accessibility.

What Are Recent G2 Reviews of OX Security?

Arnica

Arnica is a comprehensive application security posture management (ASPM) platform that protects developers, source code, and products throughout the software development lifecycle. The platform provides real-time application security scanning with 100% coverage across the software supply chain, addressing risks in Static Application Security Testing (SAST), Software Composition Analysis (SCA), Infrastructure as Code (IaC), hardcoded secrets detection, and more. At its core, Arnica offers AI-native security governance that takes control of AI-generated code through advanced AI SAST scanning and agentic rules enforcement. The platform automatically injects centrally-controlled security requirements into AI coding agents like Copilot, Cursor, and Claude at the point of code generation, ensuring every line of AI-written code is secure by default before vulnerabilities reach production. This approach addresses 92% of risks before they ever reach production environments. Arnica's pipelineless architecture provides automatic coverage for every repository without requiring CI/CD pipeline integrations or IDE deployments. The platform scans every code change at the feature branch level, delivering developer-native workflows that keep teams focused on building features rather than chasing security issues. Risk prioritization is enhanced through OWASP Top 10, CVSS, EPSS, and KEV scoring, combined with organizational context to surface the most critical vulnerabilities. The platform excels in developer experience by delivering security findings directly within existing workflows through Slack, Microsoft Teams, pull request comments, and automated ticket management in Jira and Azure DevOps Boards. AI-powered mitigation suggestions provide context-aware, automated fixes that align with organizational coding standards, significantly reducing mean-time-to-remediation. Key security capabilities include real-time secrets detection with automatic validation and mitigation, comprehensive container scanning that maps vulnerabilities directly to source code, and intelligent dependency management with automated SCA upgrades. The platform maintains SOC 2 Type 2 compliance and ISO 27001 certification, ensuring enterprise-grade security standards. Arnica's unique value proposition lies in its ability to scale security across entire organizations while maintaining development velocity, providing complete visibility into code risks, and enabling proactive security measures that prevent vulnerabilities from reaching production environments.

Average Rating: 4.4/5.0

Total Reviews: 36

Who Is the Company Behind Arnica?

  • Seller: Arnica
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Alpharetta, Georgia
  • LinkedIn® Page: www.linkedin.com
    64 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Retail
  • Company Size: 62% Large, 22% Medium

What Do G2 Reviewers Say About Arnica?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the accuracy of findings from Arnica, effectively managing elevated privileges and reducing security risks.
  • Users value the actionable recommendations from Arnica, simplifying the removal of unused elevated privileges for enhanced security.
  • Users love the easy setup and administration of Arnica, saving time while meeting their needs effectively.
  • Users love the easy setup of Arnica, appreciating the quick and efficient administration process.
  • Users value Arnica for its ability to effectively remediate over-provisioning and enhance security without developer input.
Cons
  • Users note the limited access to features in Arnica for smaller teams not on GitHub Enterprise.

What Are Recent G2 Reviews of Arnica?

What Are G2 Users Discussing About Arnica?

Invicti

Invicti (formerly known as Netsparker) is an enterprise application and API security testing platform that helps organizations secure thousands of web applications and APIs at scale while dramatically reducing the risk of attack. Combining advanced DAST and IAST capabilities in a single platform, Invicti enables security teams to continuously identify, prioritize, and remediate vulnerabilities across complex modern environments with confidence and automation. With Invicti, security teams can: - Automate application security testing workflows and save hundreds of hours every month - Discover and secure all web applications and APIs, including forgotten, unmanaged, and shadow assets - Deliver actionable, developer-friendly feedback that helps teams remediate vulnerabilities faster and build more secure code over time - Reduce false positives with proof-based scanning technology that validates exploitable vulnerabilities - Scale application security programs across large enterprises without slowing development teams - Integrate security seamlessly into existing DevSecOps and CI/CD workflows Built for organizations with the most demanding security requirements, Invicti empowers teams to confidently secure their entire attack surface with accuracy, scalability, and automation.

Average Rating: 4.5/5.0

Total Reviews: 69

Who Is the Company Behind Invicti?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 46% Large, 29% Medium

What Do G2 Reviewers Say About Invicti?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Invicti, highlighting its quick setup and straightforward report generation.
  • Users value the effective scanning technology of Invicti, enabling accurate identification of vulnerabilities and streamlined workflows.
  • Users value the accuracy and integration capabilities of Invicti, enhancing efficiency and simplifying reporting processes.
  • Users appreciate the well-formatted and easy-to-read reports from Invicti, simplifying certification processes significantly.
  • Users value the super accurate vulnerability detection of Invicti, enhancing their security workflows efficiently.
Cons
  • Users find the customer support inadequate, struggling with timely responses and effective solutions to issues.
  • Users experience slow performance during scans and setup, which affects their overall satisfaction with Invicti.
  • Users experience slow scanning issues with Invicti, affecting efficiency despite good support and solid performance once set up.
  • Users face API scanning issues with Invicti, limiting its effectiveness for their specific needs despite good support.
  • Users find the complex setup to be overwhelming initially, impacting the ease of using Invicti effectively.

What Are Recent G2 Reviews of Invicti?

What Are G2 Users Discussing About Invicti?

Jit

Jit is redefining application security by introducing the first Agentic AppSec Platform, seamlessly blending human expertise with AI-driven automation. Designed for modern development teams, Jit empowers organizations to proactively manage security risks across the entire software development lifecycle.​ AI-Powered Agents Jit's AI Agents, such as SERA (Security Evaluation and Remediation Agent) and COTA (Communication, Ops, and Ticketing Agent), collaborate with your teams to automate vulnerability triage, risk assessment, and remediation processes, significantly reducing manual workloads. ​ Comprehensive Security Scanning Achieve full-stack security coverage with integrated scanners for SAST, DAST, SCA, IaC, CSPM, and more. Jit's platform ensures continuous monitoring and immediate feedback on code changes, facilitating rapid identification and resolution of security issues. ​ Developer-Centric Experience With integrations into popular IDEs and CI/CD pipelines, Jit provides developers with contextual security insights directly within their workflows, promoting a shift-left approach without disrupting productivity. ​ Agentic AI for AppSec Teams Risk-Based Prioritization Utilizing the Model Context Protocol (MCP), Jit evaluates vulnerabilities in the context of runtime environments, business impact, and compliance requirements, enabling teams to focus on the most critical risks. ​ Seamless Integrations Jit integrates with a wide array of tools, including GitHub, GitLab, AWS, Azure, GCP, Jira, Slack, and more, ensuring that security processes are embedded within your existing technology stack. ​

Average Rating: 4.5/5.0

Total Reviews: 43

Who Is the Company Behind Jit?

  • Seller: jit
  • Year Founded: 2021
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    161 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 44% Medium, 42% Small

What Do G2 Reviewers Say About Jit?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automated and lightweight security controls of Jit, enhancing workflows without adding complexity.
  • Users praise the easy integrations of Jit, which streamline security management within existing development workflows effortlessly.
  • Users value the ease of use of Jit, enjoying seamless integration and simplified management within their workflows.
  • Users value the efficiency of Jit, streamlining workflows and reducing excess with lightweight, automated security controls.
  • Users appreciate the seamless integration support of Jit, enhancing their development workflow without added complexity.
Cons
  • Users face integration issues with Jit, as it lacks comprehensive support for all enterprise environments and tools.
  • Users find the limited features of Jit hinder integrations and onboarding, affecting complex environments and documentation quality.
  • Users experience limited integration capabilities with Jit, particularly for advanced configurations and third-party tools.
  • Users frequently find the documentation lacking, particularly for advanced configurations and integrations with third-party tools.
  • Users find the complexity of Jit overwhelming, particularly with advanced integrations and configuration for beginners.

What Are Recent G2 Reviews of Jit?

Carbon Black App Control

With the rise of security threats and malware, organizations need technologies to combat these risks. Unplanned downtime and performance degradation from security breaches impact productivity and reputation. As IT and security shift to the cloud, it's crucial to stay vigilant about security gaps. Many companies still rely on air-gapped servers or outdated operating systems (EOL OS) for critical systems and data storage. Carbon Black App Control offers proactive security for data centers, AWS, Azure, GCP, or hosted private clouds. App Control ensures trusted software runs, monitors file integrity, controls devices, protects memory and registry keys on Windows.

Average Rating: 4.6/5.0

Total Reviews: 44

Who Is the Company Behind Carbon Black App Control?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA
  • Phone: +1 800 225-5224

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 64% Large, 33% Medium

What Do G2 Reviewers Say About Carbon Black App Control?

AI-generated summary from verified user reviews

Pros
  • Users praise the awesome customer support of Carbon Black App Control, enhancing security and compliance effortlessly.
  • Users appreciate the ease of use in Carbon Black App Control, enhancing security and confidence in system management.
  • Users appreciate the easy implementation of Carbon Black App Control, enhancing security and compliance effortlessly.
  • Users appreciate the easy integrations of Carbon Black App Control, enhancing security and simplifying implementation.
  • Users value the easy implementation and strong security of Carbon Black App Control, enhancing compliance and trust in critical systems.
Cons
  • Users feel the pricing may be too expensive for smaller organizations despite its excellent security value.
  • Users have experienced false positives, but manual whitelisting helps mitigate this issue effectively.
  • Users experience high CPU usage with Carbon Black App Control, impacting performance and leading to unnecessary alerts.
  • Users often face high memory utilization with Carbon Black, leading to performance concerns and false alerts.
  • Users experience slow performance due to high CPU and memory usage, leading to frustration with the software's responsiveness.

What Are Recent G2 Reviews of Carbon Black App Control?

What Are G2 Users Discussing About Carbon Black App Control?

APPCHECK

Uncover your full attack surface, test it constantly, act with confidence. AppCheck helps organisations reduce cyber risk, meet compliance requirements and keep pace with evolving threats. Our platform delivers continuous security testing across your attack surface with the depth of a manual penetration test, uncovering vulnerabilities unique to your systems across web applications, APIs and infrastructure. Born from a UK-based penetration testing organisation, AppCheck combines over 20 years of testing expertise with a first-principles approach to security testing. Developed and supported by experienced penetration testers, the platform goes beyond known vulnerability signatures, analysing application behaviour to identify weaknesses that conventional scanning approaches can miss. Using multiple proprietary crawling engines, AppCheck tests modern and traditional technologies, including Single Page Applications (SPAs), APIs and complex authentication flows such as SSO, 2FA and TOTP. Discover: Gain visibility across your attack surface, including forgotten assets and third-party exposure. Assess: Find and validate vulnerabilities with the depth and rigour of a manual penetration test. Take action: Prioritise real-world risk and focus resources on what needs fixing first. Organisations can conduct unlimited security assessments across web applications, SPAs, APIs, cloud services and network infrastructure, covering both internal and external assets. With support for production and UAT environments, AppCheck also helps development teams shift security testing left through integrations with CI/CD pipelines and build tools, including Azure DevOps, GitHub, Jenkins, TeamCity, CircleCI, Bamboo and GitLab CI/CD. This enables automated security testing throughout development, helping teams identify vulnerabilities as changes are introduced. With unlimited scans and users per licence, teams can test continuously without additional charges for each scan, backed by direct UK-based support from security specialists. AppCheck is proud to be a CVE Numbering Authority (CNA), contributing to global vulnerability research.

Average Rating: 4.7/5.0

Total Reviews: 68

Who Is the Company Behind APPCHECK?

  • Seller: APPCHECK
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Leeds, GB
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 49% Medium, 31% Small

What Do G2 Reviewers Say About APPCHECK?

AI-generated summary from verified user reviews

Pros
  • Users commend the thorough and reliable vulnerability detection of AppCheck, enhancing security in their applications effectively.
  • Users find the ease of use of AppCheck remarkable, praising its user-friendly interface and responsive support.
  • Users value the excellent pricing and functionality of AppCheck, along with its reliable and intuitive vulnerability scanning.
  • Users find Pentest efficiency remarkable with AppCheck, leading to significant cost savings and streamlined vulnerability detection.
  • Users value the automated scanning feature of AppCheck, enhancing efficiency and streamlining vulnerability management across multiple apps.
Cons
  • Users find the poor customer support frustrating, needing to raise tickets for simple adjustments to the scan list.
  • Users suggest that UX improvements in scoring, customization, and integrations could enhance the AppCheck experience.
  • Users find the API issues frustrating, as endpoint changes require a service request and delays functionality.
  • Users find difficult customization in AppCheck's reporting features, needing more flexibility for contextual adjustments.
  • Users experience a notable difficult learning curve with Appcheck, which may hinder initial ease of use.

What Are Recent G2 Reviews of APPCHECK?

Strobes Security

Strobes is an AI-driven exposure management platform designed to help organizations streamline their security operations by unifying various security methodologies, including Attack Surface Management (ASM), Application Security Posture Management (ASPM), Risk-Based Vulnerability Management (RBVM), and Penetration Testing as a Service (PTaaS). This comprehensive solution provides users with a holistic view of their security posture, enabling them to identify, assess, and respond to potential risks and vulnerabilities effectively. Targeted primarily at security teams and IT professionals, Strobes caters to organizations of all sizes that require a robust approach to managing their security exposure. The platform is particularly beneficial for those who need to navigate the complexities of modern security environments, where multiple tools and processes can lead to fragmented insights. By consolidating various security functions into a single workflow, Strobes empowers users to make informed decisions based on a complete understanding of their risk landscape. One of the key features of Strobes is its extensive integration capabilities, boasting over 120 integrations with existing security tools and systems. This allows organizations to pull findings from disparate sources into a single view, enriching data with contextual information that enhances the relevance of insights. The platform's advanced correlation capabilities help identify relationships between different vulnerabilities and risks, enabling security teams to prioritize their remediation efforts effectively. The user-friendly dashboards in Strobes serve as a central hub for monitoring security activities, encompassing everything from asset discovery and vulnerability insights to Service Level Agreement (SLA) tracking and ticketing. This comprehensive visibility supports continuous prioritization and fix validation, allowing teams to address the most critical issues first. By automating triage processes, Strobes ensures that real risks and exposures are highlighted, facilitating a more efficient response to potential threats. Overall, Strobes stands out in the exposure management landscape by providing a cohesive and intelligent approach to security management. Its ability to unify various methodologies, coupled with powerful automation and integration features, positions it as a valuable tool for organizations seeking to enhance their security posture and effectively manage their exposure to risks.

Average Rating: 4.5/5.0

Total Reviews: 44

Who Is the Company Behind Strobes Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 42% Medium, 33% Large

What Do G2 Reviewers Say About Strobes Security?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid vulnerability assessments that enhance security fixes significantly, boosting efficiency and prioritization.
  • Users appreciate the rapid vulnerability assessments and prioritized remediation that enhance their security processes significantly.
  • Users value the thorough security measures of Strobes Security, impressed by its attention to detail in vulnerability management.
  • Users value the responsive customer support of Strobes Security, enhancing the experience with timely and effective assistance.
  • Users find Strobes Security exceptionally easy to use, enjoying quick setup and intuitive dashboards for efficient workflows.
Cons
  • Users express dissatisfaction with the inadequate reporting in Strobes Security, citing lack of transparency and customization options.
  • Users find the limited customization options in Strobes Security hinder initial workflow setup and usability improvements.
  • Users find Strobes Security's poor usability challenging initially, with a steep learning curve and complex dashboard navigation.
  • Users find the reporting issues in Strobes Security limit transparency and hinder customization for effective analysis.
  • Users find the user interface complex, making initial customization and workflow setup a challenging experience.

What Are Recent G2 Reviews of Strobes Security?

DefectDojo

DefectDojo unifies and automates vulnerability management, enabling security teams to focus on strategic, data-driven analysis. We help teams reduce time spent on manual tracking and consolidate vulnerabilities from existing tools for seamless vulnerability management.

Average Rating: 4.6/5.0

Total Reviews: 11

Who Is the Company Behind DefectDojo?

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 64% Medium, 36% Small

What Are Recent G2 Reviews of DefectDojo?

What Are G2 Users Discussing About DefectDojo?

ActiveState

ActiveState provides the world's largest library of secure open source: 79 million (Java, Javascript, Python, R, Go, etc.) vetted components across all major language ecosystems, including transitive dependencies and OS-level libraries—built from source to ensure every component is verified, vulnerability-free, and continuously updated. Software teams improve security posture while accelerating development velocity. We deliver five critical outcomes. Counter Supply Chain Risks at Their Source Significantly reduce the possibility of inheriting malicious code from pre-built binaries. Replace risky, unvetted public components with secure, verifiable packages built directly from source. Gain provenance over your artifacts, ensuring bad actors and malware never reach your environment. - Protection from compromised package ecosystems and build systems - Mitigate high-profile malware attacks such as the npm Shai-Hulud attack and other future threats Continuous Remediation for Your Open Source Inventory Shift from reactive patching to proactive immunity. Maintain a hardened security posture with safe-by-default open source and continuous remediation across your inventory. ActiveState artifacts reduce your attack surface and evolve to help close vulnerabilities before they become incidents. - Up to 99% reduction in CVEs compared to community open source artifacts - Achieve up to 90% reduction in MTTR for future vulnerabilities Apply Frictionless Security Policies Embed governance directly into developer workflows without impeding engineering or adding costly CI/CD bloat. ActiveState solutions slot seamlessly into existing tools and AI coding assistants, transforming security policy from a blocker into an enabler that reduces open source approval workflows from weeks and days to just hours and minutes. - Reduce open source approval workflows from weeks and days to hours and minutes Audit Ready Compliance, Always Achieve continuous compliance with instant, granular visibility into components, licenses, and dependencies across your organization. ActiveState delivers comprehensive SBOMs and metadata by default, ensuring you can meet complex standards and minimizing the scramble of audit preparation. - Full visibility into your open source usage, including transitive and OS level dependencies Reclaim Developer Velocity and Focus Minimize high-value engineering hours on dependency conflicts, environment setup, research and remediation. ActiveState components and artifacts are fully managed to ensure they are always up to date and safe to use so your team can focus entirely on shipping revenue-generating features. - Free up 4-8 developer hours per CVE - 68% reduction in scanner noise from false positives

Average Rating: 4.1/5.0

Total Reviews: 32

Who Is the Company Behind ActiveState?

  • Seller: ActiveState
  • Company Website:
  • Year Founded: 1997
  • HQ Location: Vancouver, BC
  • LinkedIn® Page: www.linkedin.com
    70 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Computer & Network Security
  • Company Size: 51% Small, 29% Medium

What Are Recent G2 Reviews of ActiveState?

What Are G2 Users Discussing About ActiveState?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, enjoying its user-friendly interface and convenient access to essential information.
  • Users value the near false positive free vulnerability scanning of Edgescan, making web application testing efficient and reliable.
  • Users highly value the fantastic customer support from Edgescan, enhancing their overall experience significantly.
  • Users value the validated, near false positive free vulnerability scanning of Edgescan, enhancing their testing experience significantly.
  • Users appreciate the user-friendly console of Edgescan, as it offers easy access and comprehensive functionality for managing vulnerabilities.
Cons
  • Users find the complex UI of Edgescan challenging, leading to inefficiencies and difficulties in task navigation.
  • Users find the limited customization for hosts and filtering frustrating, impacting their ability to adapt to changes.
  • Users find the poor interface design of Edgescan frustrating, hindering efficient navigation and task completion.
  • Users experience slow performance with Edgescan, as scans can take longer due to thorough validation processes.
  • Users find the user interface challenging to navigate, leading to delays and difficulty performing common tasks.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?

Mend.io

Modern risk doesn't live in one layer, it lives between them. Mend.io is built for every risk, across AI and AppSec, securing the code layer, the AI layer, and the interactions between them. From discovery and red teaming to guardrails and runtime protection, Mend.io delivers continuous protection across the entire AI application lifecycle. Mend.io solutions include: 1. Mend AI secures the layer where modern risk actually lives—the interaction between code and AI. It continuously discovers AI components (agents, prompts, models), tests real behavioral risk through automated red teaming, and enforces in-app runtime guardrails for one continuous control system for the AI lifecycle. 2. Mend AppSec secures the modern code layer by continuously discovering and prioritizing risk across code, libraries, containers, and dependencies, giving teams the clarity they need to reduce exposure and ship secure software faster. 3. Mend Renovate secures the foundation of every codebase by automatically updating dependencies, rating the likelihood each update will succeed without breaking changes, and grouping them by confidence level so teams can resolve them faster.

Average Rating: 4.3/5.0

Total Reviews: 117

Who Is the Company Behind Mend.io?

  • Seller: Mend
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, Massachusetts
  • LinkedIn® Page: www.linkedin.com
    259 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 36% Small, 33% Large

What Do G2 Reviewers Say About Mend.io?

AI-generated summary from verified user reviews

Pros
  • Users highlight the scanning efficiency of Mend.io, enabling seamless integration and effective source code analysis.
  • Users appreciate the ease of use of Mend.io, finding it helpful and easy to integrate into their workflow.
  • Users value the easy integrations with source code repositories, making security management efficient and straightforward.
  • Users praise Mend.io for its quick and accurate scanning capabilities, enhancing efficiency across various platforms.
  • Users value the automated vulnerability detection in Mend.io, enabling quick identification and resolution of critical issues.
Cons
  • Users face integration issues, finding it challenging to connect with on-premise tools and experiencing configuration problems.
  • Users find the limited features of Mend.io challenging, requiring workarounds for integration and specific use cases.
  • Users find missing features in Mend.io, struggling with integration and needing additional functionality for their workflows.
  • Users report complex implementation with numerous issues, including false positives and difficult integration processes.
  • Users find the interface confusing due to navigating between different portals for SAST and SCA products.

What Are Recent G2 Reviews of Mend.io?

What Are G2 Users Discussing About Mend.io?

Flyingduck

Flyingduck is a Comprehensive Code security Intelligence platform that identifies and remediates security vulnerabilities in the code base. Key modules are SBOM Compliance, SCA, SAST, Secrets Analysis. We also identify Business Logic Issues in the code such as OTP Bypass, Transaction Manipulation type issues with our Deep Logic Analysis AI engine.

Average Rating: 5.0/5.0

Total Reviews: 5

Who Is the Company Behind Flyingduck?

  • Seller: Flyingduck
  • Year Founded: 2024
  • HQ Location: Hyderabad, IN
  • LinkedIn® Page: www.linkedin.com
    17 employees on LinkedIn®
  • Ownership: Sarat Lingamallu
  • Phone: +919550681242

Who Uses This Product?

  • Company Size: 60% Medium, 20% Small

What Are Recent G2 Reviews of Flyingduck?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024