Best User and Entity Behavior Analytics (UEBA) Software for Small Business

How Many User and Entity Behavior Analytics (UEBA) Software Products Does G2 Track?

Total Products under this Category: 59

Category Stats (Nov 2026)

  • Average Rating: 4.36/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Incydr (+0.44%) - Among all products in this category, Incydr recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank User and Entity Behavior Analytics (UEBA) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,000+ Authentic Reviews
  • 59+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

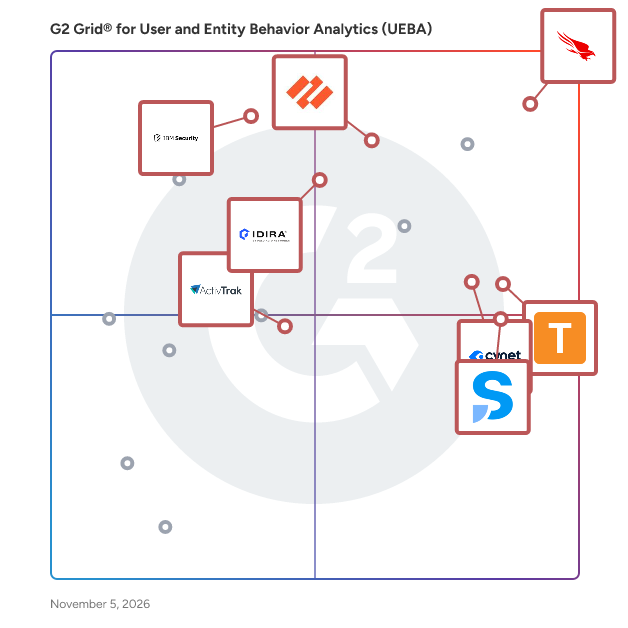
G2 Grid® for User and Entity Behavior Analytics (UEBA) Software

G2 Grid® for User and Entity Behavior Analytics (UEBA) Software plotting products by satisfaction and market presence

Highlighted products: Palo Alto Cortex XSIAM, IBM QRadar SIEM, Safetica, CrowdStrike Falcon Endpoint Protection Platform, Teramind, ActivTrak, Cynet, and Idira Identity Security Platform.

Underlying data: [Grid® JSON](https://www.g2.com/categories/user-and-entity-behavior-analytics-ueba/grids.json?focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=safetica&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=teramind&focus%5B%5D=activtrak&focus%5B%5D=cynet&focus%5B%5D=idira-identity-security-platform&segment=small-business)

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 107

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.0/10)
  • Ease of Use: 8.6/10 (Category avg: 8.8/10)
  • Continuous Analysis: 8.9/10 (Category avg: 9.0/10)
  • Anomaly Detection: 9.2/10 (Category avg: 8.9/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 35% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users find Palo Alto Cortex XSIAM to be easy to understand and user-friendly, enhancing their security product integration experience.
  • Users value the effective threat detection capabilities of Palo Alto Cortex XSIAM, identifying both known and unknown risks.
  • Users value the easy integrations with multiple systems, enhancing the functionality and efficiency of Palo Alto Cortex XSIAM.
  • Users value the rapid incident response capabilities of Palo Alto Cortex XSIAM, enhancing overall cybersecurity effectiveness.
  • Users appreciate the intuitive dashboard and easy threat detection features of Cortex XSIAM, enhancing overall security management.
Cons
  • Users find the cost of Palo Alto Cortex XSIAM to be prohibitively expensive, affecting its overall value and accessibility.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM challenging, especially for non-technical users.
  • Users find the complexity of Palo Alto Cortex XSIAM overwhelming, requiring significant time and expertise to effectively manage.
  • Users face significant integration issues with Palo Alto Cortex XSIAM, affecting overall usability and performance negatively.
  • Users face significant UX challenges with Palo Alto Cortex XSIAM, citing a less intuitive interface and limited customization.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

IBM QRadar SIEM

Outsmart threats with an end-to-end award-winning security suite; proven to prevent, endure and recover from both known & unknown IT hazards faced by SoCs in the modern-day.

Average Rating: 4.4/5.0

Total Reviews: 285

How Do G2 Users Rate IBM QRadar SIEM?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.0/10)
  • Ease of Use: 8.4/10 (Category avg: 8.8/10)
  • Continuous Analysis: 8.3/10 (Category avg: 9.0/10)
  • Anomaly Detection: 8.2/10 (Category avg: 8.9/10)

Who Is the Company Behind IBM QRadar SIEM?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Who Uses This: SOC Analyst, Security Engineer
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 52% Large, 29% Medium

What Do G2 Reviewers Say About IBM QRadar SIEM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of IBM QRadar SIEM, facilitating effective threat management and investigation.
  • Users appreciate the flexible integration capabilities of IBM QRadar SIEM, enhancing log management across diverse sources.
  • Users value the advanced threat detection and centralized log management features of IBM QRadar SIEM for enhanced security.
  • Users appreciate the easy integrations of IBM QRadar SIEM, enhancing its functionality with various platforms seamlessly.
  • Users appreciate the user-friendly interface of IBM QRadar SIEM, making it accessible for both tech and non-tech users.
Cons
  • Users find the UX improvements lacking, struggling with limited features and an unfriendly interface in QRadar SIEM.
  • Users find IBM QRadar SIEM expensive, particularly small and mid-sized companies struggling with the overall cost.
  • Users find the high cost of IBM QRadar SIEM challenging, particularly for smaller organizations needing comprehensive support.
  • Users face dashboard issues with IBM QRadar SIEM, lacking customization, usability, and integration for optimal performance.
  • Users find the time-consuming nature of QRadar SIEM frustrating, especially with complicated queries and log fetching delays.

What Are Recent G2 Reviews of IBM QRadar SIEM?

Safetica

Safetica’s Intelligent Data Security protects sensitive data where teams work. Our AI-powered platform unifies data protection, discovery, compliance, insider risk management, and AI Protection into a single solution. Using powerful AI, Safetica delivers contextual awareness that reduces false positives and stops real threats without disrupting productivity. With Safetica, security teams can maintain visibility and control over sensitive data, including how it is used and shared through AI, stay ahead of insider risks, maintain compliance, and secure sensitive cloud-based data. ✔️ Data Protection: Classify, monitor and control sensitive data across devices and clouds in real time. ✔️ Insider Risk and User Behavior: Spot risky behavior, detect intent, and stop insider threats to stay ahead of the careless handling of sensitive data, compromised user accounts and malicious user activity. ✔️ Compliance and Data Discovery: Prove compliance with audit-ready reporting for data in use, in motion, and at rest. ✔️ Cloud Security: Extend protection policies to cloud-based workloads — maintaining visibility, detecting risk, and enforcing mitigation across Microsoft 365, Google Drive, and hybrid work environments. Safetica is available as a SaaS solution (Safetica Intelligent Data Security Platform) and On-Premises (Safetica On-Prem). Safetica covers the following data security solutions: ✅ Data Loss Prevention: Discover, classify, and protect sensitive data through visibility, continuous monitoring, and real-time awareness alerts defending against data loss, empowering users, and to support regulatory compliance. ✅ AI Protection: Provides visibility into AI activity to protect sensitive data before it reaches AI tools. It includes DLP controls to protect sensitive data from ChatGPT, Claude, and Microsoft Copilot, while enabling productive AI use. ✅ Insider Risk Management: Enhance the protection of sensitive data from insider threats with real-time detection of anomalous behavior while also gaining insight into employee productivity. ✅ Cloud Data Protection: Continuously protect valuable data across Microsoft 365 and Google Drive by extending existing protection policies —ensuring secure access, responsible sharing, and visibility into cloud-based workloads across devices and hybrid environments. ✅ AI-Powered Contextual Defense: Access an intelligent, adaptive layer of protection that learns typical user behavior to detect anomalies and proactively mitigate insider threats with real-time detection, risk scoring, and dynamic response. ✅ Data Discovery and Classification: Discover and classify sensitive data using content and contextual analysis —giving you the insight to identify risks, reduce exposure, and enforce compliance. Safetica’s AI Data Classification discovers sensitive data manual rules may miss by analyzing files and proposing ready-to-use classifications that help identify gaps and expand classification coverage. ✅ Reporting and Administration: Safetica’s centralized console delivers clear, actionable insights—serving as a single source of truth for reviewing threats, enforcing policies, and investigating incidents. ✅ Device Control: Prevent unauthorized data access and reduce the risk of data loss by monitoring, controlling, and securing external devices connected to USB and peripheral ports across endpoints. ✅ User Activity and Workspace Audit: Protect sensitive data and reduce organizational risk by detecting both malicious and unintentional user activity —ensuring security, compliance, and visibility across your entire environment. ✅ Regulatory Compliance: Ensure data privacy and effortlessly maintain local and international compliance standards including GDPR, HIPAA, SOX, PCI-DSS, GLBA, ISO/IEC 27001, SOC2 or CCPA.

Average Rating: 4.6/5.0

Total Reviews: 194

How Do G2 Users Rate Safetica?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Ease of Use: 9.0/10 (Category avg: 8.8/10)
  • Continuous Analysis: 9.0/10 (Category avg: 9.0/10)
  • Anomaly Detection: 8.7/10 (Category avg: 8.9/10)

Who Is the Company Behind Safetica?

  • Seller: Safetica
  • Company Website:
  • Year Founded: 2011
  • HQ Location: San Jose, California, United States
  • Twitter: @Safetica
    664 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    130 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 38% Small

What Do G2 Reviewers Say About Safetica?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Safetica, highlighting its intuitive interface and simple setup process.
  • Users value the strong security features of Safetica, enhancing data protection and web security for remote work.
  • Users value Safetica for its effective data protection, ensuring web security and reducing data breach risks effortlessly.
  • Users commend the comprehensive DLP features of Safetica, enhancing security and simplifying user activity monitoring.
  • Users value the intuitive and clear interface of Safetica, enhancing ease of use and implementation across networks.
Cons
  • Users report slow performance issues with Safetica, including delays with applications and interactions with other software.
  • Users find the complexity of advanced configurations and setup processes to be overwhelming and tedious.
  • Users face integration issues with Antimalware and Mac/Linux devices, limiting Safetica's compatibility in diverse environments.
  • Users express concern over limited compatibility with Linux and Mac, affecting overall usability and support.
  • Users experience limited features with Safetica, facing challenges in file labeling and report customization options.

What Are Recent G2 Reviews of Safetica?

What Are G2 Users Discussing About Safetica?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 553

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Ease of Use: 9.0/10 (Category avg: 8.8/10)
  • Continuous Analysis: 9.2/10 (Category avg: 9.0/10)
  • Anomaly Detection: 9.1/10 (Category avg: 8.9/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Large, 40% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the lightweight performance and powerful threat detection of CrowdStrike Falcon, enhancing security without slowing down systems.
  • Users commend the effective threat detection capabilities of CrowdStrike Falcon, ensuring robust security without system slowdowns.
  • Users appreciate the ease of use of CrowdStrike Falcon, benefiting from its lightweight impact and efficient incident management.
  • Users appreciate the advanced real-time threat protection of CrowdStrike Falcon, ensuring efficient security without system performance issues.
  • Users praise the exceptional threat detection of CrowdStrike Falcon, noting its effectiveness against both known and unknown threats.
Cons
  • Users find the cost prohibitive for smaller organizations, especially with additional modules increasing overall expenses.
  • Users find the complexity of the user interface and additional costs challenging, complicating their overall experience.
  • Users face a steep learning curve with CrowdStrike’s query language, making transitions from other platforms challenging.
  • Users find the limited features challenging, especially concerning cost and technical accessibility for smaller businesses.
  • Users find that pricing can be a barrier for smaller organizations, complicating access to advanced features.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Teramind

Teramind is a unified workforce intelligence and cybersecurity platform designed to help organizations gain comprehensive visibility into employee activity, data movement, and insider risk across various environments, including endpoints, cloud applications, and networks. This platform integrates user activity monitoring, data loss prevention, and behavioral analytics to assist security teams in detecting insider threats, preventing data breaches, and investigating security incidents, all while supporting productivity optimization, AI governance, and compliance requirements. The platform is particularly beneficial for organizations that require a robust solution for monitoring and managing employee behavior and data security. It serves a diverse range of industries, including financial services, healthcare, government, manufacturing, and technology, where safeguarding sensitive information and mitigating insider risks are paramount. Teramind addresses various use cases, such as preventing intellectual property theft by departing employees, detecting compromised credentials, monitoring privileged user access, and enforcing acceptable use policies. Additionally, it aids organizations in demonstrating compliance with regulations like GDPR, HIPAA, and PCI-DSS. Teramind offers real-time data capture and alerting capabilities across desktop applications, web browsers, LLMs, AI Agents, email, file transfers, and cloud services. Security teams can leverage the platform to identify anomalous user behavior, enforce data protection policies, and respond to potential insider threats proactively. The software captures detailed audit trails, which include session recordings, screenshots, keystroke logging, application usage, and network activity, providing essential forensic evidence for security investigations and compliance audits. The architecture of Teramind supports various deployment options, including cloud-based SaaS, on-premises installations, and hybrid configurations, allowing organizations to choose a setup that best fits their operational needs. The platform seamlessly integrates with Security Information and Event Management (SIEM) systems, identity providers, and security orchestration tools, ensuring it fits well within existing security operations workflows. Notable features include AI-powered anomaly detection, natural language query reports, customizable alerting rules, and automated response actions that can block risky activities in real-time based on policy violations, enhancing the overall security posture of the organization.

Average Rating: 4.6/5.0

Total Reviews: 178

How Do G2 Users Rate Teramind?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.0/10)
  • Ease of Use: 8.9/10 (Category avg: 8.8/10)
  • Continuous Analysis: 9.1/10 (Category avg: 9.0/10)
  • Anomaly Detection: 8.6/10 (Category avg: 8.9/10)

Who Is the Company Behind Teramind?

  • Seller: Teramind
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Aventura, FL
  • Twitter: @teramindco
    883 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    218 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Small, 44% Medium

What Do G2 Reviewers Say About Teramind?

AI-generated summary from verified user reviews

Pros
  • Users highlight the solid and responsive customer support from Teramind, enhancing their overall experience significantly.
  • Users value the intuitive interface and comprehensive monitoring of Teramind for effective tracking and security enhancement.
  • Users find Teramind's intuitive interface and support team make it easy to operate and monitor effectively.
  • Users value the ease of monitoring remote employees with Teramind, enhancing transparency and user privacy effectively.
  • Users value the intuitive interface and comprehensive monitoring of Teramind for effective user activity analysis.
Cons
  • Users find Teramind's complex user interface challenging, complicating setup and daily management for new administrators.
  • Users face challenges with the difficult setup of Teramind, which complicates navigation and initial configuration.
  • Users find the limited dashboards in Teramind inadequate, hindering effective monitoring and insights for their needs.
  • Users find the difficult navigation of Teramind challenging, particularly for new administrators during setup and management.
  • Users note inadequate monitoring capabilities, particularly in real-time app tracking and flexible report optimization.

What Are Recent G2 Reviews of Teramind?

What Are G2 Users Discussing About Teramind?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.0/10)
  • Ease of Use: 9.1/10 (Category avg: 8.8/10)
  • Continuous Analysis: 9.5/10 (Category avg: 9.0/10)
  • Anomaly Detection: 9.4/10 (Category avg: 8.9/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, appreciating its straightforward yet comprehensive functionalities for effective protection.
  • Users value the unified platform of Cynet, which offers effective security through streamlined endpoint protection and detection.
  • Users praise Cynet for its effective threat detection and seamless monitoring, enhancing overall cybersecurity effortlessly.
  • Users commend Cynet for its exceptional customer support, ensuring a smooth and efficient deployment experience.
  • Users praise Cynet for its flawless threat monitoring and detection, enhancing overall cybersecurity effectiveness effortlessly.
Cons
  • Users find limited customization options in reporting and dashboards, affecting their ability to present necessary data.
  • Users find feature limitations in Cynet, with a desire for more customization options and broader integrations.
  • Users note a lack of customization in reports, wishing for more options to tailor data presentation.
  • Users note limited features, such as basic reporting and few third-party integrations, impacting customization and deeper controls.
  • Users note a lack of essential features like web filtering and security policies compared to other vendors.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

ActivTrak

ActivTrak provides the Work Intelligence organizations need to understand how work changes in the AI era. As the system of record for work, its award-winning platform captures behavioral data across people, tools and AI agents, and the workflows that connect them — enabling leaders to measure impact, optimize productivity and improve operational performance. The platform also powers research through the ActivTrak Productivity Lab. Built on a privacy-first data foundation, ActivTrak is trusted by more than 9,500 organizations worldwide and recognized by Deloitte’s Technology Fast 500, Inc. 5000, TrustRadius and G2 for delivering measurable ROI and stronger business outcomes. The company is backed by Elsewhere Partners, Sapphire Ventures and Francisco Partners. Learn more at www.activtrak.com.

Average Rating: 4.3/5.0

Total Reviews: 334

How Do G2 Users Rate ActivTrak?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.0/10)
  • Ease of Use: 8.4/10 (Category avg: 8.8/10)
  • Continuous Analysis: 8.8/10 (Category avg: 9.0/10)
  • Anomaly Detection: 8.1/10 (Category avg: 8.9/10)

Who Is the Company Behind ActivTrak?

  • Seller: Birch Grove Software, Inc.
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Austin, TX
  • Twitter: @activtrak
    5,821 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    184 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Operations Manager
  • Top Industries: Information Technology and Services, Hospital & Health Care
  • Company Size: 52% Small, 43% Medium

What Do G2 Reviewers Say About ActivTrak?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of ActivTrak, finding it intuitive for tracking team performance effortlessly.
  • Users value ActivTrak for its clear visibility into employee productivity, enhancing accountability and facilitating efficient coaching.
  • Users value the real-time employee monitoring of ActivTrak, enabling them to track productivity and activity effectively.
  • Users value the clear visibility into team productivity and efficient performance tracking provided by ActivTrak.
  • Users appreciate the visibility into team productivity provided by ActivTrak, enabling efficient tracking and coaching.
Cons
  • Users find ActivTrak's complexity overwhelming, as navigating detailed data and reports can be time-consuming and challenging.
  • Users find ActivTrak's insufficient detail overwhelming, making it challenging to extract useful insights from collected data.
  • Users find ActivTrak has limited features, impacting usability and flexibility, especially for smaller teams.
  • Users find the interface not user-friendly, struggling with navigation and lacking effective customer support for issues.
  • Users find difficult navigation in ActivTrak, struggling with an overwhelming interface and inconsistencies in information access.

What Are Recent G2 Reviews of ActivTrak?

What Are G2 Users Discussing About ActivTrak?

Idira Identity Security Platform

The Idira Identity Security Platform is the industry leading, next-generation platform that secures all identities for the AI enterprise. Built on CyberArk's 25 years of identity security leadership and Palo Alto Networks' platformization strategy, Idira eliminates the fragmentation between traditional identity solutions attackers have exploited for decades. Idira secures human, machine and agentic identities, without slowing down the business.

Average Rating: 4.5/5.0

Total Reviews: 248

How Do G2 Users Rate Idira Identity Security Platform?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.0/10)
  • Ease of Use: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Idira Identity Security Platform?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 53% Large, 37% Medium

What Are Recent G2 Reviews of Idira Identity Security Platform?

What Are G2 Users Discussing About Idira Identity Security Platform?

Microsoft Defender for Identity

Microsoft Defender for Identity enables you to integrate Microsoft Defender for Identity with Defender for Endpoint, for an even more complete threat protection solution. While Defender for Identity monitors the traffic on your domain controllers, Defender for Endpoint monitors your endpoints, together providing a single interface from which you can protect your environment.

Average Rating: 4.3/5.0

Total Reviews: 93

How Do G2 Users Rate Microsoft Defender for Identity?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.0/10)
  • Ease of Use: 8.1/10 (Category avg: 8.8/10)
  • Continuous Analysis: 8.2/10 (Category avg: 9.0/10)
  • Anomaly Detection: 8.3/10 (Category avg: 8.9/10)

Who Is the Company Behind Microsoft Defender for Identity?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Large, 32% Small

What Are Recent G2 Reviews of Microsoft Defender for Identity?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated