Best Risk-Based Vulnerability Management Software - Page 10

How Many Risk-Based Vulnerability Management Software Products Does G2 Track?

Total Products under this Category: 212

Category Stats (Sep 2026)

  • Average Rating: 4.49/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Ethiack (+0.86%) - Among all products in this category, Ethiack recorded the largest rating increase compared to last month

Last updated: September 01, 2026

How Does G2 Rank Risk-Based Vulnerability Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,300+ Authentic Reviews
  • 212+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

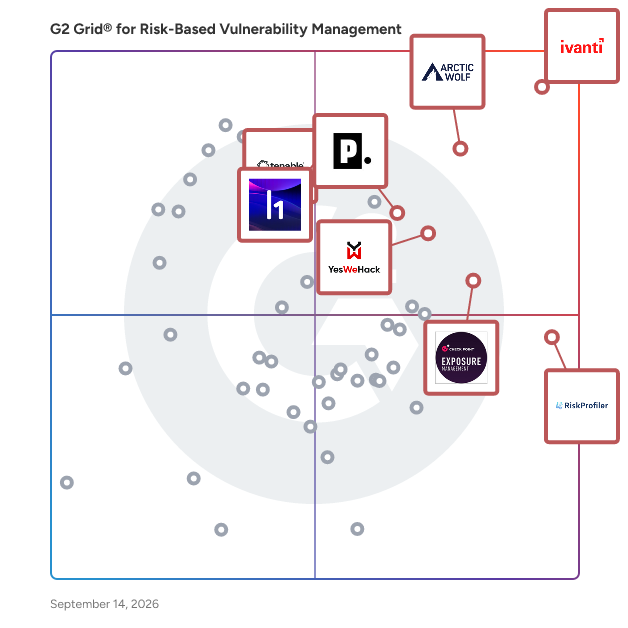
G2 Grid® for Risk-Based Vulnerability Management Software

G2 Grid® for Risk-Based Vulnerability Management Software plotting products by satisfaction and market presence

Highlighted products: Ivanti Neurons for Unified Endpoint Management, Arctic Wolf, Tenable Vulnerability Management, RiskProfiler - External Threat Exposure Management, YesWeHack, Pentera, Check Point Exposure Management, and H1 Platform.

Underlying data: [Grid® JSON](https://www.g2.com/categories/risk-based-vulnerability-management/grids.json?focus%5B%5D=ivanti-neurons-for-unified-endpoint-management&focus%5B%5D=arctic-wolf&focus%5B%5D=tenable-vulnerability-management&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=yeswehack&focus%5B%5D=pentera&focus%5B%5D=check-point-exposure-management&focus%5B%5D=h1-platform)

cloudDFN cDFN WatchTower

cDFN WatchTower is a CAASM (Cyber Asset Attack Surface Management) solution that integrates risk-based vulnerability management, external attack surface monitoring, dark web surveillance, vendor risk management, and compliance oversight into a single platform. It empowers organizations to proactively identify and address vulnerabilities, secure external assets, monitor potential threats on the dark web, and ensure compliance with industry standards. By consolidating these critical functions, businesses can reduce security gaps, streamline risk management, and enhance overall cybersecurity posture.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind cloudDFN cDFN WatchTower?

  • Seller: cloudDFN
  • Year Founded: 2019
  • HQ Location: Thane, IN
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About cloudDFN cDFN WatchTower?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the speedy dark web scans of cDFN WatchTower, enhancing security against credential leaks.
  • Users find the quick dark web scan of cloudDFN cDFN WatchTower invaluable for monitoring credential leaks.
  • Users value the quick dark web scans of cDFN WatchTower, assisting in effective monitoring of credential leaks.
  • Users value the quick dark web scan feature of cDFN WatchTower for effective credential leak monitoring.
  • Users appreciate the fast response time of cDFN WatchTower for quick dark web scans and credential monitoring.
Cons
  • Users find the complex navigation of cloudDFN cDFN WatchTower challenging, especially when exploring various modules initially.
  • Users note that the UI can be improved, making it challenging to navigate between different modules initially.
  • Users find difficult navigation challenging at first, indicating that the UI could use significant improvement.
  • Users find the navigation difficult at first, suggesting improvements to enhance the overall user experience.
  • Users find that the UI could be improved, with navigation between modules being challenging initially.

What Are Recent G2 Reviews of cloudDFN cDFN WatchTower?

Cogent Security

Cogent Security builds an AI and machine learning-based cybersecurity platform to enhance threat detection and response, and provides streamlined security workflows that allow faster risk reduction and free up critical resources.

Who Is the Company Behind Cogent Security?

Conviso

The Conviso Platform is a complete Application Security Posture Management (ASPM) solution that centralizes visibility, correlation, and prioritization of vulnerabilities across the software development lifecycle. It integrates with your existing SAST, DAST, SCA, IaC, and CI/CD tools, automates triage, and provides a unified view of risk — helping security and development teams work together to reduce complexity and strengthen AppSec maturity.

Who Is the Company Behind Conviso?

Covail Vulnerability Management

The Covail Vulnerability Management Solution provides you with an easy-to-understand and easy-to-use method of mitigating cyber-attacks through network assessments, vulnerability tracking, risk prioritization, and actionable reporting.

Who Is the Company Behind Covail Vulnerability Management?

  • Seller: Covail
  • Year Founded: 2014
  • HQ Location: Columbus, US
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

CSH Vulnerability Management Platform

CSH Vulnerability Management Platform is a comprehensive SaaS solution that helps system administrators and security professionals with the tools they need to identify, prioritize, and mitigate vulnerabilities across their infrastructure. Designed with a risk-based approach, our platform enables users to focus on the most critical security issues first, ensuring that resources are allocated efficiently to protect valuable assets. Our solution gathers in-depth information on vulnerabilities, installed software, and potentially insecure configurations using both agent-based and agentless approaches. With data collected from your infrastructure, our multi-user, unified dashboard provides a centralized view of all findings, allowing your team to assess and address vulnerabilities in real time. The dashboard’s intuitive layout makes it easy for users of any experience level to navigate and collaborate effectively, supporting both individual and team workflows. For enhanced security, CSH Vulnerability Management Platform also offers automated external port and vulnerability scans, configurable to recur at intervals that best suit your organization’s needs. These proactive scans help to identify potential exposures on your network perimeter, alerting you to any new or recurring vulnerabilities that may pose a risk to your environment. With flexible, scalable licensing options, you can purchase the exact number of licenses you need for your current infrastructure and expand as your organization grows. The CSH Vulnerability Management Platform seamlessly integrates into existing workflows, offering robust reporting features, customizable alerts, and support for third-party tools. By providing timely, actionable insights and a holistic view of your security posture, CSH Vulnerability Management Platform helps your team stay a step ahead in the rapidly evolving landscape of cybersecurity threats.

Who Is the Company Behind CSH Vulnerability Management Platform?

CVETodo

CVETodo is a CVE database and vulnerability management platform. Every CVE arrives analysed — AI analyst deep dives, remediation priority scoring, exploit and patch status — and everything you run gets matched against it: an open-source agent for servers, an agentless appliance inventory for firewalls and VPN gateways, and version-confirmed findings that roll up into remediation reports benchmarked against PCI DSS, Cyber Essentials, or Essential Eight.

Who Is the Company Behind CVETodo?

Cybellum Security Suite

Cybellum empowers automotive OEMs and suppliers to identify and remediate security risks at scale, throughout the entire vehicle life cycle. Our agentless solution scans embedded software components without needing access to their source code, exposing all cyber vulnerabilities. Manufacturers can then take immediate actions and eliminate any cyber risk in the development and production process, before any harm is done, while continuously monitor for emerging threats impacting vehicles on the road. Cybellum already partners with 10 leading OEMs and Tier-1 suppliers worldwide.

Who Is the Company Behind Cybellum Security Suite?

  • Seller: Cybellum
  • Year Founded: 2016
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    45 employees on LinkedIn®

Darktrace / CLOUD

Darktrace / CLOUD is a Cloud-Native Application Protection Platform (CNAPP) with advanced real-time Cloud Detection and Response (CDR) to protect runtime environments from active threats. It secures modern hybrid and multi-cloud environments by combining posture management, runtime threat detection, cloud-native response, and automated cloud investigations in a single AI-driven platform. As organizations scale across AWS, Azure, Google Cloud, SaaS, containers, and serverless architectures, static posture checks and alert-heavy tools are no longer enough. Darktrace / CLOUD continuously understands how your cloud environment behaves and automatically stops threats as they unfold. 1. Stop Active Cloud Threats in Real Time with AI-Driven CDR Darktrace delivers true Cloud Detection and Response in live production environments. Its Self-Learning AI monitors identity behavior, workload activity, and network connections to detect the most subtle indicators of account compromise, privilege escalation, insider threats, ransomware, and novel attacks. When real threats emerge, it can take precise, proportionate action to contain them immediately, minimizing business disruption. 2. Maintain Continuous Cloud Visibility, Posture Assurance, and Risk Reduction Darktrace combines continuous cloud monitoring with Cloud Security Posture Management (CSPM) capabilities to dynamically map architecture, identities (human and non-human), services, containers, and configurations. It identifies misconfigurations, vulnerabilities, toxic combinations of privileges, and exploitable attack paths, not just static compliance gaps. This ensures organizations maintain real-time visibility and awareness of risk as cloud environments evolve. 3. Accelerate Incident Response with Automated Cloud Investigations at Scale Darktrace integrates with any detection source and your existing security stack to perform automated investigations at cloud speed and scale. When suspicious activity is detected, Darktrace automatically collects and analyzes forensic evidence across logs, configurations, disk, memory, and ephemeral workloads. Full attacker timelines are generated in minutes, enabling rapid root-cause analysis, confident remediation, and audit-ready evidence without manual data gathering. While many CNAPP solutions focus primarily on posture or fragmented point capabilities, Darktrace / CLOUD unifies prevention, real-time detection, response, and automated investigation in one continuous AI-driven workflow, delivering protection that adapts as fast as the cloud itself. AI-Driven Automation from Detection to Investigation Self-Learning AI detects known, unknown, and novel threats while autonomous response and automated investigations dramatically reduce analyst workload and stop threats automatically. Unmatched Cloud Coverage with Breadth and Depth Darktrace unifies CSPM, identity analytics, runtime CDR, and forensic depth across IaaS, PaaS, SaaS, containers, and serverless environments to deliver protection at cloud speed and scale. True Hybrid, Cross-Domain Protection The platform correlates live activity across cloud, SaaS, on-premises, and network environments to uncover and contain lateral, cross-domain attacks. Flexible Deployment for Enterprise Reality With agentless API integrations and optional agent-based telemetry, Darktrace supports SaaS, hosted, and on-prem deployments, delivering rapid time-to-value while meeting regulatory and operational requirements.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Darktrace / CLOUD?

  • Seller: Darktrace
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • Twitter: @Darktrace
    18,177 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Darktrace / CLOUD?

Derive

Derive is the cybersecurity risk and operations platform that helps teams quantify risk, prioritize actions, and prove impact. Built on our Peer Risk Benchmarks – the most complete real-world dataset of cyber losses – Derive shows which risks matter most, what actions reduce loss, and where to invest next. The platform replaces legacy GRC tools with three integrated modules: Risk: Quantify and prioritize risk in dollars using real-world data Governance: Centralize controls, owners, assets, and frameworks Operations: Built-in workflows for user reviews, third-party and AI risk, IR/BC/DR, and more Unlike static tools or compliance checklists, Derive is dynamic. Risk updates in real time as your team acts. Every task is ranked by measurable risk reduction – so you know exactly what to do next.

Who Is the Company Behind Derive?

  • Seller: Derive
  • Year Founded: 2023
  • HQ Location: Richmond, US
  • LinkedIn® Page: linkedin.com
    3 employees on LinkedIn®

DragonSoft DVM

Vulnerability assessment software with network scanning, vulnerabilities evaluation, risk assessment, reporting and remediation.

Who Is the Company Behind DragonSoft DVM?

EcoTrust

Who Is the Company Behind EcoTrust?

  • Seller: EcoTrust
  • Year Founded: 2019
  • HQ Location: São Paulo, BR
  • LinkedIn® Page: www.linkedin.com
    13 employees on LinkedIn®

Empirical Security

Empirical Security builds a cybersecurity platform to deliver AI-driven vulnerability management by modeling both global and enterprise-specific threat landscapes, enabling security teams in enterprises to reduce alert noise, prioritize critical threats, and make data-informed decisions.

Who Is the Company Behind Empirical Security?

Eracent SBOM-HQ

SBOM-HQ™ - from Eracent SBOM-HQ™ provides a well-rounded set of data, reporting and analysis features that help organizations minimize risks and comply with cyber mandates and directives. While SBOM-HQ™ provides value to in-house and commercial application development teams, it is also unique in its approach to meeting the requirements of organizations that purchase or subscribe to software from numerous publishers. These “software consumers” will have to manage dozens, hundreds, or even thousands of SBOMs for products that they use, and this is impractical or impossible to do one SBOM at a time. SBOM-HQ™ is based around a centralized, single-source repository of libraries, components, and other related data from SBOMs. It dramatically reduces response time when a vulnerability is reported since it eliminates the need to review SBOMs individually. How does SBOM-HQ™ work? Customers upload their SBOM files via the user interface. During this straightforward process, users can assign related information that can be used to support reporting, filters, data access, and more. This information includes Publisher, Line of Business, Application Component, and more. SBOM-HQ™ “deconstructs” each uploaded SBOM and records the software product to which the SBOM belongs and all the SBOM’s content. This results in an index of components and libraries mapped to products. If a vulnerability is reported by NIST or another organization, customers get an immediate report of every product in use in their organization that includes the affected component or library. SBOM-HQ™ is continuously monitored and updated, and it leverages vulnerability data from NIST and other trusted global sources. It uses this data to display risk scores, levels of criticality, and more. SBOM-HQ™ also provides visibility into license types for each component and library, reducing the risk of unknowingly using a library that has excessive restrictions when less risky options are available. The system offers version tracking – the version in use, newer available versions, and version history – as well as lifecycle dates that support obsolescence management. The dedicated open source library within Eracent’s IT-Pedia® product data library provides a solid foundation for SBOM-HQ™’s analysis and reporting. Who can benefit from using SBOM-HQ? SBOM-HQ is designed to support all teams engaged in the use and operation of software. DevOps – SBOM-HQ integrates into CI/CD to generate and enrich SBOMs with real time risk data, ensuring secure and compliant releases. Procurement – SBOM-HQ equips procurement teams with SBOM-driven insights into software quality and licensing risks, enabling smarter vendor selection and safer software purchases. CyberSec teams – SBOM-HQ evaluates cyber security aspects of purchased software and monitors new vulnerabilities that appear. ITOps – SBOM-HQ exposes software weaknesses and helps mitigate the risks. Legal and Licensing teams – SBOM-HQ delivers clear visibility into open source licenses, flags conflicts early, and provides audit-ready compliance reports. Why SBOM-HQ? SBOM-HQ is designed to support software buyers and users, not just software publishers. While most SBOM solutions stop at the software development life cycle, SBOM-HQ goes further. It empowers software consumers to continuously monitor not only what they build, but also what they buy - from design and procurement, through integration, all the way to production in their own data centers. With SBOM-HQ, transparency extends beyond development, delivering visibility and control across the entire software supply chain. To learn more about SBOM-HQ™, register for a free trial at sbomhq.com or contact Eracent today!

Who Is the Company Behind Eracent SBOM-HQ?

  • Seller: Eracent
  • Year Founded: 2000
  • HQ Location: Riegelsville, Pennsylvania
  • Twitter: @eracent
    141 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    69 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024