Best Network Sandboxing Software

How Many Network Sandboxing Software Products Does G2 Track?

Total Products under this Category: 16

Category Stats (Oct 2026)

  • Average Rating: 4.45/5 The average rating of products in this category, based on all submitted ratings

Last updated: October 13, 2026

How Does G2 Rank Network Sandboxing Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 900+ Authentic Reviews
  • 16+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

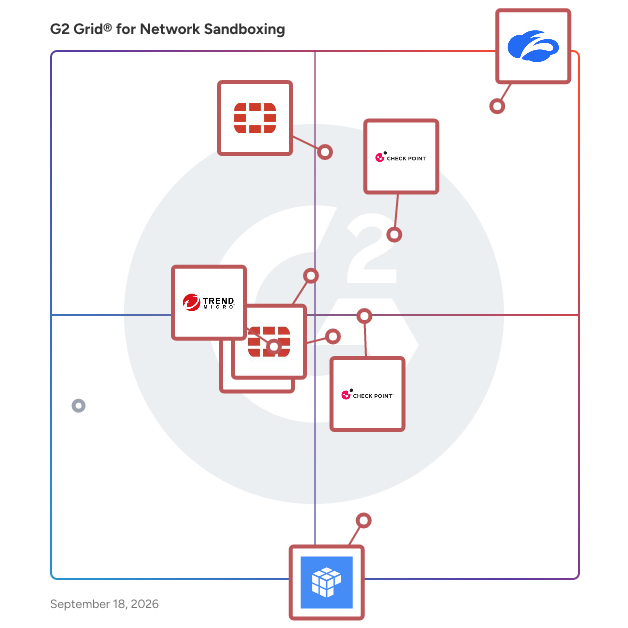
G2 Grid® for Network Sandboxing Software

G2 Grid® for Network Sandboxing Software plotting products by satisfaction and market presence

Highlighted products: Zscaler Internet Access, FortiSandbox, Check Point Infinity Platform, Check Point SandBlast Advanced Network Threat Prevention, FortiGuard Labs Outbreak Alerts, Kaspersky Next Optimum, Deep Discovery Inspector, and Intezer.

Underlying data: [Grid® JSON](https://www.g2.com/categories/network-sandboxing/grids.json?focus%5B%5D=zscaler-internet-access&focus%5B%5D=fortisandbox&focus%5B%5D=check-point-infinity-platform&focus%5B%5D=check-point-sandblast-advanced-network-threat-prevention&focus%5B%5D=fortiguard-labs-outbreak-alerts&focus%5B%5D=kaspersky-next-optimum&focus%5B%5D=trend-micro-deep-discovery-inspector&focus%5B%5D=intezer-intezer)

Zscaler Internet Access

Zscaler Internet Access™ (ZIA) is the world’s leading cloud-native secure access solution that protects users, devices, and data by securing all internet traffic, regardless of location. Leveraging cloud native, AI-powered cyberthreat protection and zero trust access to the internet and SaaS apps, ZIA ensures fast, direct, and secure connections to the internet and SaaS applications, eliminating the need for traditional on-premises security hardware. With ZIA, you can optimize internet security and user experience while aligning with Zero Trust principles through Zscaler Internet Access. ZIA's advanced features like Secure Web Gateways, DNS Security, Cloud Access Security Broker (CASB), Data Loss Prevention (DLP), Secure Enterprise Browsing, and Cloud Sandboxing provide comprehensive protection against advanced threats such as malware, ransomware, and phishing while safeguarding sensitive corporate data. It combines robust threat prevention with granular policy enforcement to ensure secure, seamless access for users across remote, branch, or hybrid environments. With ZIA, organizations can embrace cloud transformation while leveraging simplified management, reduced complexity, and consistent security across global teams. Key Features and Benefits: • Prevent cyberthreats and data loss with AI: Protect your organization against advanced threats with a suite of AI-powered cyberthreat and data protection services, enriched by real-time updates sourced from 500 trillion daily threat signals from the world’s largest security cloud. • Get an unmatched user experience: Get the world’s fastest internet and SaaS experience—up to 40% faster than legacy security architectures—to boost productivity and increase business agility. • Reduce costs and complexity: Realize 139% ROI with Zscaler by replacing 90% of your costly, complex, and slow appliances with a fully cloud-native zero trust platform. • Secure your hybrid workforce: Empower employees, customers, and third parties to securely access web apps and cloud services from anywhere, on any device—with a great digital experience. • Unify SecOps and NetOps Efforts: Drive faster, more collaborative security outcomes with shared tooling like real-time traffic insights, API-first integrations, and granular RBAC. • Achieve Total Data and Content Sovereignty: Enforce compliance for secure and localized access without performance tradeoffs using Egress NAT, geolocalized content, and in-country data logging. • Secure AI in Your Environment: Enable the secure use of Microsoft Copilot and other AI applications. • Protect Developer Environments at Scale: Automate SSL/TLS inspection for 30+ developer tools while sandboxing code and unknown or large files with instant AI-verdicts—all without slowing innovation. Zscaler Internet Access is trusted by organizations worldwide to ensure secure, reliable, and fast internet connectivity that supports both modern workflows and digital transformation initiatives."

Average Rating: 4.4/5.0

Total Reviews: 303

How Do G2 Users Rate Zscaler Internet Access?

  • Malware Probability Scores: 8.6/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.0/10 (Category avg: 9.4/10)
  • Sandbox: 8.9/10 (Category avg: 9.3/10)

Who Is the Company Behind Zscaler Internet Access?

  • Seller: Zscaler
  • Company Website:
  • Year Founded: 2008
  • HQ Location: San Jose, California
  • Twitter: @zscaler
    17,676 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    9,150 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Technical Support Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 54% Large, 27% Medium

What Do G2 Reviewers Say About Zscaler Internet Access?

AI-generated summary from verified user reviews

Pros
  • Users value the seamless security of Zscaler Internet Access, providing robust protection without compromising performance or user experience.
  • Users value the comprehensive internet security of Zscaler Internet Access, appreciating its effective threat prevention and user-friendly approach.
  • Users value the robust security capabilities of Zscaler Internet Access, ensuring safe browsing without added complexity.
  • Users find Zscaler Internet Access to be an excellent cloud proxy solution, praised for its ease of deployment and configuration.
  • Users value the seamless and robust email security of Zscaler Internet Access, ensuring protection without added complexity.
Cons
  • Users report slow performance with Zscaler Internet Access during peak hours, affecting connection speeds and productivity.
  • Users find the complex implementation challenging, especially for new admins, leading to potential web traffic access issues.
  • Users find complex configuration challenging, especially new admins, leading to potential web traffic access issues.
  • Users experience connection issues, including slow speeds, drops, and difficulties accessing certain websites or VPNs.
  • Users face challenging setup and slow internet speeds with Zscaler Internet Access, impacting user experience during peak times.

What Are Recent G2 Reviews of Zscaler Internet Access?

What Are G2 Users Discussing About Zscaler Internet Access?

FortiSandbox

Fortinet’s top-rated FortiSandbox provides the on-site intelligence that enables the Fortinet Security Fabric to address the fast moving and more targeted threats across a broad attack surface. Specifically, it delivers real-time intelligence through the automated detection and response to previously unknown malware. Broad Coverage of the Attack Surface with Security Fabric – applies advanced inspection across the top attack vectors of network, email, web infrastructure and even individual endpoints Automated Zero-day, Detection and Mitigation - Native integration and open APIs enable the exchange of objects from, and return of intelligence to, Fortinet and third-party vendor products for immediate threat response Certified and Top Rated - Constantly undergoes rigorous, real-world independent testing and consistently earns top marks such as ICSA ATD Certification and NSS Labs Recommendation for Breach Detection and Prevention.

Average Rating: 4.5/5.0

Total Reviews: 22

How Do G2 Users Rate FortiSandbox?

  • Malware Probability Scores: 8.6/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.2/10 (Category avg: 9.4/10)
  • Sandbox: 9.5/10 (Category avg: 9.3/10)

Who Is the Company Behind FortiSandbox?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 58% Medium, 29% Small

What Are Recent G2 Reviews of FortiSandbox?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Malware Probability Scores: 8.7/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.2/10 (Category avg: 9.4/10)
  • Sandbox: 8.8/10 (Category avg: 9.3/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Check Point SandBlast Advanced Network Threat Prevention

Check Point SandBlast Advanced Network Threat Prevention is a comprehensive security solution designed to protect organizations from sophisticated cyber threats, including zero-day attacks and advanced malware. By integrating real-time threat intelligence with advanced AI technologies, SandBlast delivers proactive defense mechanisms that prevent unknown cyber threats while maintaining seamless business operations. Key Features and Functionality: - Zero-Day Threat Prevention: Utilizes powerful threat intelligence and AI-based engines to detect and block previously unknown cyber threats before they can infiltrate the network. - Threat Emulation and Extraction: Employs CPU-level inspection and threat emulation to analyze suspicious files in a virtualized environment, identifying and mitigating potential threats without impacting network performance. - Streamlined Security Management: Offers single-click setup with out-of-the-box security policy profiles optimized for various business needs, reducing administrative overhead and ensuring up-to-date protection. - Seamless Productivity: Delivers a prevention-first strategy that does not compromise user experience, allowing uninterrupted business operations even when dealing with suspicious files. Primary Value and User Solutions: SandBlast Advanced Network Threat Prevention addresses the critical need for organizations to defend against evolving cyber threats without disrupting daily operations. By providing real-time threat intelligence, automated response mechanisms, and seamless integration with existing network infrastructure, SandBlast enhances security posture, minimizes security incidents, and ensures robust defense against malware, ransomware, and advanced persistent threats. Its intuitive management and comprehensive threat protection enable security teams to maintain high levels of protection with reduced complexity and administrative effort.

Average Rating: 4.4/5.0

Total Reviews: 17

How Do G2 Users Rate Check Point SandBlast Advanced Network Threat Prevention?

  • Malware Probability Scores: 7.9/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.3/10 (Category avg: 9.4/10)
  • Sandbox: 9.5/10 (Category avg: 9.3/10)

Who Is the Company Behind Check Point SandBlast Advanced Network Threat Prevention?

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 67% Medium, 28% Large

What Do G2 Reviewers Say About Check Point SandBlast Advanced Network Threat Prevention?

AI-generated summary from verified user reviews

Pros
  • Users find Check Point SandBlast to be easy to use and integrate, enhancing their overall experience with its simplicity.
  • Users value the easy integrations with Check Point SandBlast, enhancing functionality and overall user experience.
  • Users value the ease of use and unique detection features of Check Point SandBlast for seamless integration.
  • Users appreciate the installation ease of Check Point SandBlast, noting its simplicity and fast integration with other tools.
  • Users value the seamless integrations within the Check Point ecosystem, enhancing efficiency and decision-making speed.
Cons
  • Users find the cost intimidating, and it may also lead to CPU stress during operation.
  • Users find the high cost of Check Point SandBlast Advanced Network Threat Prevention to be quite intimidating.
  • Users find the high resource usage of Check Point SandBlast can strain their CPU and increase costs.
  • Users face incomplete information due to limitations in static analytics on MacOs and file size restrictions.
  • Users face limited features in Check Point SandBlast, particularly with static analytics and file size restrictions.

What Are Recent G2 Reviews of Check Point SandBlast Advanced Network Threat Prevention?

What Are G2 Users Discussing About Check Point SandBlast Advanced Network Threat Prevention?

FortiGuard Labs Outbreak Alerts

The FortiGuard team develops effective countermeasures to protect more than 320,000 Fortinet customers around the world. These countermeasures include up-to-the-minute threat intelligence, delivered as a subscription service for Fortinet security products

Average Rating: 4.2/5.0

Total Reviews: 12

How Do G2 Users Rate FortiGuard Labs Outbreak Alerts?

  • Malware Probability Scores: 9.2/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.4/10 (Category avg: 9.4/10)
  • Sandbox: 8.8/10 (Category avg: 9.3/10)

Who Is the Company Behind FortiGuard Labs Outbreak Alerts?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Who Uses This Product?

  • Company Size: 69% Medium, 15% Large

What Do G2 Reviewers Say About FortiGuard Labs Outbreak Alerts?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the proactive approach to zero-day malware through quick patch releases for FortiGate devices.
  • Users value the proactive ransomware protection provided by FortiGuard Labs, ensuring timely defenses against evolving threats.
  • Users appreciate the proactive detection of threats provided by FortiGuard Labs Outbreak Alerts, enhancing security measures effectively.
  • Users value the timely software updates that effectively address zero-day malware and enhance security continuously.
Cons
  • Users express concern over the lack of timely updates for firmware exploits and recategorization requests.
  • Users express frustration with the poor customer support, noting delays in addressing firmware exploits and recategorization requests.
  • Users experience poor detection performance as firmware exploits take time to address and recategorization requests go unnoticed.
  • Users report delays in addressing firmware exploits and bugs, impacting the overall effectiveness of FortiGuard Labs Outbreak Alerts.

What Are Recent G2 Reviews of FortiGuard Labs Outbreak Alerts?

Kaspersky Next Optimum

Kaspersky Next Optimum is the ideal choice for small and mid-sized businesses with lean cybersecurity teams. The offering is uniting in itself with strong endpoint protection, essential detection and response capabilities (EDR), and a seamless upgrade to XDR and MXDR for sophisticated cybersecurity. Layers of Kaspersky Next Optimum: • Kaspersky Next EDR Foundations – Powerful ML-based EPP, flexible security controls and EDR root cause analysis tools equip you with the most straightforward way to build a strong foundation for your cybersecurity. • Kaspersky Next EDR Optimum – Combines strong endpoint protection with enhanced controls, patch and encryption management, training for IT staff, cloud security and more – all boosted by essential EDR functionality to help you deflect attacks rapidly, with minimal demand on your resources. • Kaspersky Next XDR Optimum – In addition to exceptional EPP and automatic response capabilities that help identify, analyze and neutralize evasive threats, the solution gives you affordable, user-friendly detection and response tools that go beyond endpoints, as well as access to our online learning platform to raise the security awareness of your employees. • Kaspersky Next MXDR Optimum – Get expert-managed protection against sophisticated threats, delivered by Kaspersky’s globally renowned SOC experts with 24/7 infrastructure monitoring – while keeping essential XDR capabilities in-house.

Average Rating: 4.3/5.0

Total Reviews: 196

How Do G2 Users Rate Kaspersky Next Optimum?

  • Malware Probability Scores: 8.6/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.0/10 (Category avg: 9.4/10)
  • Sandbox: 9.0/10 (Category avg: 9.3/10)

Who Is the Company Behind Kaspersky Next Optimum?

  • Seller: Kaspersky
  • Year Founded: 1997
  • HQ Location: Moscow
  • Twitter: @kasperskylabind
    1,291 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    4,616 employees on LinkedIn®
  • Phone: 1-866-328-5700

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Medium, 33% Small

What Do G2 Reviewers Say About Kaspersky Next Optimum?

AI-generated summary from verified user reviews

Pros
  • Users value the central blocking mechanism of Kaspersky Next Optimum for its effective policy management and ease of use.
  • Users appreciate the ease of use of Kaspersky Next Optimum, finding the interface appealing and intuitive for security management.
  • Users appreciate Kaspersky's strong threat intelligence capabilities, providing robust protection for networks against cyber threats.
  • Users value the comprehensive protection Kaspersky offers for both small and large business networks against cyber threats.
  • Users value the advanced threat detection capabilities of Kaspersky Next Optimum, ensuring robust security for their organization.
Cons
  • Users report high resource usage with Kaspersky Next Optimum, leading to significant CPU and memory strain on servers.
  • Users experience slow performance with Kaspersky Next Optimum, especially during scans and while managing multiple endpoints.
  • Users face compatibility issues, including performance slowdowns and challenges with installation and integration across devices.
  • Users experience a complex setup for Kaspersky, particularly with licensing challenges and performance slowdowns affecting security.
  • Users face challenges with difficult configuration, particularly in licensing and setup for multiple locations.

What Are Recent G2 Reviews of Kaspersky Next Optimum?

What Are G2 Users Discussing About Kaspersky Next Optimum?

Deep Discovery Inspector

Deep Discovery Analyzer Extend the value of your security investments with custom sandboxing

Average Rating: 4.2/5.0

Total Reviews: 10

How Do G2 Users Rate Deep Discovery Inspector?

  • Malware Probability Scores: 8.8/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 8.8/10)
  • Malware Evaluation: 8.8/10 (Category avg: 9.4/10)
  • Sandbox: 8.3/10 (Category avg: 9.3/10)

Who Is the Company Behind Deep Discovery Inspector?

  • Seller: TrendAI
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY
  • Total Revenue (USD mm): $1,515

Who Uses This Product?

  • Company Size: 50% Medium, 30% Large

What Are Recent G2 Reviews of Deep Discovery Inspector?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 187

How Do G2 Users Rate Intezer?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Year Founded: 2015
  • HQ Location: New York
  • Twitter: @IntezerLabs
    10,170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 23% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Intezer, ensuring timely detection and blocking of malware.
  • Users value the effective malware detection and security features of Intezer that enhance system protection.
  • Users value Intezer for its effective malware detection and response capabilities, enhancing overall security and incident management.
  • Users value the high detection accuracy of Intezer, ensuring timely malware detection and enhanced system security.
  • Users appreciate the ease of use of Intezer, making malware detection and incident response straightforward and efficient.
Cons
  • Users feel the inability to control file visibility limits their privacy and management options in certain situations.
  • Users report complex interface issues with Intezer, making navigation challenging and less intuitive.
  • Users are concerned about limited file visibility control, which may impact their data privacy and access management.
  • Users find the difficult navigation of Intezer frustrating, with a less-than-ideal UI and small text affecting readability.
  • Users find the expensive pricing of Intezer problematic, especially with the limited free tier and some GUI issues.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

Symantec Content Analysis and Sandboxing

Detect and block advanced threats that elude traditional analysis with multiple-layer inspection and customizable sandboxing

Average Rating: 4.6/5.0

Total Reviews: 29

How Do G2 Users Rate Symantec Content Analysis and Sandboxing?

  • Malware Probability Scores: 10.0/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.4/10)
  • Sandbox: 10.0/10 (Category avg: 9.3/10)

Who Is the Company Behind Symantec Content Analysis and Sandboxing?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • Twitter: @broadcom
    63,909 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 37% Medium, 37% Large

What Are Recent G2 Reviews of Symantec Content Analysis and Sandboxing?

MetaDefender Managed File Transfer™ (MFT)

MetaDefender Managed File Transfer™ (MFT) is OPSWAT’s security-focused managed file transfer solution that unifies automation, usability, and compliance into a single, trusted platform. Secure file analysis is embedded directly into the solution, leveraging AI-based malware detection to deliver a premium MFT experience for both IT and OT environments. This approach provides adaptive zero-day protection by combining real-time file analysis with predictive AI that evaluates file structure and anticipates malicious behavior prior to execution, without detonation. Whether evaluating secure file transfer solutions, exploring MFT automation for workflow efficiency, or seeking MFT compliance to meet stringent standards, OPSWAT's secure MFT solution delivers comprehensive protection with industry-standard protocols and industry-leading file security technologies. With centralized governance, intuitive workflows, and real-time visibility across all security domains, MetaDefender Managed File Transfer simplifies compliance readiness through detailed audit trails, extensive reporting, and policy enforcement aligned with zero-trust architecture. It ensures business continuity by keeping secure file transfers reliable, uninterrupted, and protected from emerging threats while integrating seamlessly with OPSWAT’s ecosystem – including optical diodes, endpoint protection, portable media security, and kiosks – to enable secure, automated workflows

Average Rating: 4.8/5.0

Total Reviews: 41

How Do G2 Users Rate MetaDefender Managed File Transfer™ (MFT)?

  • Malware Probability Scores: 9.2/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.4/10)
  • Sandbox: 10.0/10 (Category avg: 9.3/10)

Who Is the Company Behind MetaDefender Managed File Transfer™ (MFT)?

  • Seller: OPSWAT
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Tampa, Florida
  • Twitter: @OPSWAT
    7,257 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,185 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 39% Large

What Do G2 Reviewers Say About MetaDefender Managed File Transfer™ (MFT)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the enhanced security provided by MetaDefender MFT through advanced threat detection and automated file scanning.
  • Users appreciate the secure transfer capabilities of MetaDefender MFT, enjoying seamless and automated file movement with robust security.
  • Users are impressed by the reliability of MetaDefender MFT, ensuring secure and efficient file transfers every time.
  • Users value the easy file transfer capabilities of MetaDefender MFT, facilitating secure sharing and workflow automation effortlessly.
  • Users value the enhanced compliance standards of MetaDefender MFT, ensuring secure and verified file transfers with detailed monitoring.
Cons
  • Users find the initial setup complexity of MetaDefender MFT challenging, especially for new users with advanced configuration needs.
  • Users face integration issues with MetaDefender MFT, making setup and management challenging, especially for smaller teams.
  • Users find the difficult learning curve for setup and configuration of MetaDefender MFT challenging, especially for new users.
  • Users note the high licensing costs of MetaDefender MFT make it challenging for smaller teams to adopt effectively.
  • Users suggest that more transparent pricing options would benefit smaller teams with lower transfer volumes.

What Are Recent G2 Reviews of MetaDefender Managed File Transfer™ (MFT)?

Trend Micro Deep Discovery

Deep Discovery Inspector is available as a physical or virtual network appliance. It's designed to quickly detect advanced malware that typically bypasses traditional security defenses and exfiltrates sensitive data. Specialized detection engines and custom sandbox analysis detect and prevent breaches.

Average Rating: 4.3/5.0

Total Reviews: 16

How Do G2 Users Rate Trend Micro Deep Discovery?

  • Malware Probability Scores: 8.9/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.4/10)
  • Sandbox: 8.9/10 (Category avg: 9.3/10)

Who Is the Company Behind Trend Micro Deep Discovery?

  • Seller: TrendAI
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY
  • Total Revenue (USD mm): $1,515

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 41% Medium, 35% Large

What Are Recent G2 Reviews of Trend Micro Deep Discovery?

AhnLab MDS

AhnLab MDS is a sandbox solution that provides advanced threat detection, analysis, and response capabilities without compromising end-user systems. Why AhnLab MDS • Advanced Threat Detection The multi-engine of AhnLab MDS is the backbone of its unrivaled file analysis technology, applying the most suitable analysis technique aligned with the characteristics of each file. It runs files in an isolated environment (sandbox) and performs a comprehensive analysis of behavior, file/process creation, network traffic, and URL access to determine the maliciousness of files. • No Execution Until Proven Safe AhnLab MDS never lets suspicious files executed in the end-user system. Once unanalyzed files are detected, it instantly holds execution, triggers analysis, and performs response measures, including file removal and system quarantine if a file is convicted of being malicious. • AI-Powered Email Security AhnLab MDS determines the maliciousness of email by extracting the email data and implementing AI-assisted analysis. This results in laser-accurate detection of phishing emails that might evade policy-based detection. Key Features • Cutting-Edge Sandbox Analysis In the sandbox constructed within the high-performance appliance, AhnLab MDS analyzes every executable and non-executable files as well as covert techniques hidden behind files. It accelerates users to outpace modern cyber threats without compromising end-user systems. • Reversing Anti-VM Some modern malware is equipped with anti-VM features, which freezes its operation once sandbox environments are detected. AhnLab MDS, always a few steps ahead of the latest cyber threats, reverses the anti-VM feature by disabling malware to scan the sandbox and evade detection. • Network Scanning When analyzing files, AhnLab MDS granularly detects and blocks malicious network traffic based on extensive signatures and YARA rules to tackle techniques of advanced persistent threats (APTs) such as C2 server connections. • Extensive Third-Party Integration AhnLab MDS is compatible with a variety of third-party products spanning SSL/TLS decryption and spam filtering solutions. This extends its range of file aggregation, detection, and analysis to deliver reinforced threat response capabilities. • Intelligence-Driven Defense AhnLab MDS actualizes “intelligence-driven defense” by deeply integrating with our native products and services. Our threat intelligence platform, AhnLab TIP, feeds additional insights on files, URLs, and Ips to AhnLab MDS, and industry-leading experts of ASEC step in to deliver the full-scale file analysis service. • Central Monitoring & Log Management The intuitive AhnLab MDS dashboard offers exceptional visibility into the threat detection and analysis status and central management of logs and events generated by products deployed across the organization.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate AhnLab MDS?

  • Malware Evaluation: 10.0/10 (Category avg: 9.4/10)

Who Is the Company Behind AhnLab MDS?

  • Seller: AhnLab
  • Year Founded: 1995
  • HQ Location: Seongnam-si, KR
  • Twitter: @AhnLab_SecuInfo
    2,971 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    691 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of AhnLab MDS?

Hillstone Cloud Sandbox

Cloud Sandbox delivers a unique, advanced threat detection platform that can emulate the execution environment and analyze all activities related to malicious files, identify advanced threats and collaborate with existing solutions to provide rapid remediation.

Average Rating: 4.0/5.0

Total Reviews: 1

How Do G2 Users Rate Hillstone Cloud Sandbox?

  • Malware Probability Scores: 10.0/10 (Category avg: 9.0/10)
  • Has the product been a good partner in doing business?: 6.7/10 (Category avg: 8.8/10)
  • Malware Evaluation: 8.3/10 (Category avg: 9.4/10)
  • Sandbox: 10.0/10 (Category avg: 9.3/10)

Who Is the Company Behind Hillstone Cloud Sandbox?

  • Seller: Hillstone Networks
  • Year Founded: 2006
  • HQ Location: Santa Clara, US
  • Twitter: @Hillstone_Net
    10,037 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    369 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Hillstone Cloud Sandbox?

What Are G2 Users Discussing About Hillstone Cloud Sandbox?

Software Defined Labs (SDL)

Virtual appliance that simplifies management, automation, and orchestration of network and lab resources.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Software Defined Labs (SDL)?

  • Malware Probability Scores: 10.0/10 (Category avg: 9.0/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.4/10)
  • Sandbox: 10.0/10 (Category avg: 9.3/10)

Who Is the Company Behind Software Defined Labs (SDL)?

  • Seller: Tokalabs
  • Year Founded: 2015
  • HQ Location: San Jose, US
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Software Defined Labs (SDL)?

C-Prot Endpoint Security

With a user-friendly interface, cloud or on-prem based management options and a central control panel, you can easily manage all your endpoint devices (Computer, Mobile Device, Smart TV) from one place.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind C-Prot Endpoint Security?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of C-Prot Endpoint Security?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024