Best Software Composition Analysis Tools - Page 3

How Many Software Composition Analysis Tools Products Does G2 Track?

Total Products under this Category: 75

Category Stats (Sep 2026)

  • Average Rating: 4.49/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Black Duck Polaris Platform (+2.92%) - Among all products in this category, Black Duck Polaris Platform recorded the largest rating increase compared to last month

Last updated: September 01, 2026

How Does G2 Rank Software Composition Analysis Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,600+ Authentic Reviews
  • 75+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

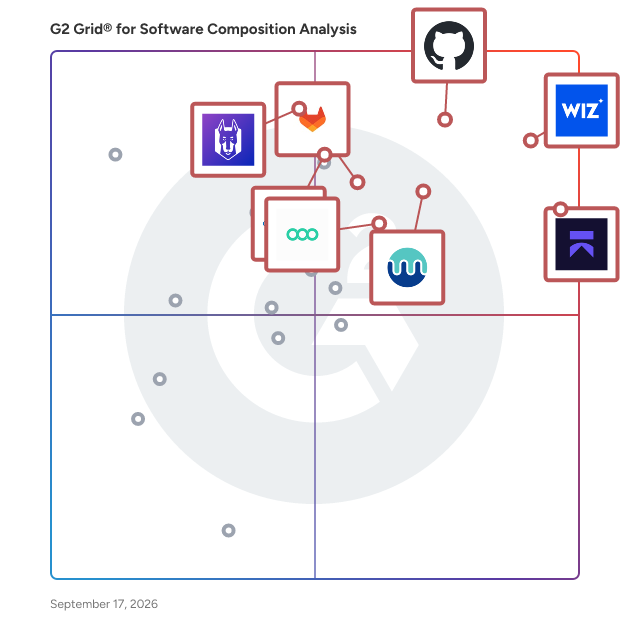
G2 Grid® for Software Composition Analysis Tools

G2 Grid® for Software Composition Analysis Tools plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, GitHub, Mend.io, Snyk, GitLab, DigiCert ONE, and Semgrep.

Underlying data: [Grid® JSON](https://www.g2.com/categories/software-composition-analysis/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=github&focus%5B%5D=mend-io&focus%5B%5D=snyk&focus%5B%5D=gitlab&focus%5B%5D=digicert-one&focus%5B%5D=semgrep)

Finite State

Finite State empowers device OEMs to ship securely while enabling engineering teams to move at the speed of AI, immediately transforming product artifacts into audit-ready assurance through a single automated workflow. Leveraging deep binary analysis and AI-native execution, the platform unifies code, compiled components, and firmware in minutes—connecting security design with deployed software. By continuously generating SBOMs, VEX, and signed compliance packages, Finite State enables connected device companies across industries such as medical devices and automotive to meet evolving regulations, including the EU Cyber Resilience Act (CRA), and deliver continuous compliance at speed. Learn more at https://finitestate.io/

Average Rating: 4.3/5.0

Total Reviews: 12

How Do G2 Users Rate Finite State?

  • Quality of Support: 9.2/10 (Category avg: 9.0/10)
  • Language Support: 10.0/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 8.3/10 (Category avg: 8.7/10)
  • Integration: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Finite State?

  • Seller: Finite State
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Columbus, Ohio, United States
  • Twitter: @FiniteStateInc
    670 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    78 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 25% Medium

What Are Recent G2 Reviews of Finite State?

GuardRails

GuardRails is an end-to-end security platform that makes AppSec easier for both security and development teams. We scan, detect, and provide real-time guidance to fix vulnerabilities early. Trusted by hundreds of teams around the world to build safer apps, GuardRails integrates seamlessly into the developers’ workflow, quietly scans as they code, and shows how to fix security issues on the spot via Just-in-Time training. GuardRails commits to keeping the noise low and only reporting high-impact vulnerabilities that are relevant to your organization. GuardRails helps organizations shift security everywhere and build a strong DevSecOps pipeline, so they can go faster to market without risking security.

Average Rating: 4.3/5.0

Total Reviews: 29

How Do G2 Users Rate GuardRails?

  • Quality of Support: 8.5/10 (Category avg: 9.0/10)
  • Language Support: 9.2/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Integration: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind GuardRails?

  • Seller: GuardRails
  • Year Founded: 2017
  • HQ Location: Singapore, Singapore
  • Twitter: @guardrailsio
    1,553 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 52% Small, 48% Medium

What Do G2 Reviewers Say About GuardRails?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of GuardRails, ensuring efficient code scans and vulnerability management in DevSecOps.
  • Users value the vulnerability detection capabilities of GuardRails, enhancing security with automated, comprehensive code scans.
  • Users find GuardRails easy to use, offering integrated feedback on security issues directly within their development environment.
  • Users value the error reduction capabilities of GuardRails, enabling early detection and swift resolution of security issues.
  • Users value the effective threat detection of GuardRails, ensuring secure code and timely vulnerability alerts during development.
Cons
  • Users note missing features in GuardRails, such as limited developer support and lack of report generation capabilities.
  • Users find time management challenging with GuardRails due to insufficient resources and requirement for constant supervision.
  • Users face bug issues with GuardRails, resulting in frequent bottlenecks and complications during code pushing.
  • Users face challenges with dashboard issues, including insufficient report generation and syncing difficulties for new users.
  • Users report false positives in GuardRails, which can complicate the vulnerability management process despite a helpful dashboard.

What Are Recent G2 Reviews of GuardRails?

Vigiles

Vigiles is a best-in-class vulnerability monitoring and remediation tool that combines a curated CVE database, continuous security feed based on your SBOM, powerful filtering, and easy triage tools so you don’t get blindsided by vulnerabilities.

Average Rating: 4.2/5.0

Total Reviews: 6

How Do G2 Users Rate Vigiles?

  • Quality of Support: 8.8/10 (Category avg: 9.0/10)
  • Language Support: 8.9/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 8.9/10 (Category avg: 8.7/10)
  • Integration: 7.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Vigiles?

  • Seller: Timesys
  • Year Founded: 1996
  • HQ Location: Pittsburgh, US
  • Twitter: @Timesys
    540 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    52 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 83% Small, 17% Large

What Are Recent G2 Reviews of Vigiles?

ZeroPath

ZeroPath (YC S24) is the first AI-native application security platform that fundamentally reimagines how organizations find and fix vulnerabilities. Unlike deterministic SAST tools that bolt AI onto legacy rule engines, ZeroPath was built from the ground up to combine large language models with advanced program analysis (AST, data flow, taint tracking) by Ex-Tesla Red Team and Google Security engineers. ZeroPath's core differentiation is detecting critical vulnerabilities that pattern-matching SAST fundamentally cannot find. It catches IDORs, authorization bypasses, race conditions, and authentication bugs by reasoning about application behavior and developer intent. This capability achieved a 92% alert reduction when triaging findings from legacy tools. ZeroPath is best suited for enterprises and startups that want a complete appsec experience with: AI-powered SAST across 16+ languages, SCA with exploitability analysis (90% noise reduction by determining if dependency CVEs are actually reachable in your code), secrets detection with validation, IaC scanning for Terraform/CloudFormation/Kubernetes, and natural language security policies. Context-aware autopatch generation fixes 70% of vulnerabilities automatically with framework-specific patches that match your coding standards. To keep the developer experience seamless, ZeroPath integrates into existing workflows with zero configuration. It provides Sub-60-second PR scans on GitHub, GitLab, Bitbucket, and Azure DevOps to provide instant security feedback without blocking development. Developers receive clear explanations, one-click fixes, and can refine patches using natural language commands directly in PR comments. The platform automatically attributes vulnerabilities to responsible developers and syncs bidirectionally with Jira, Linear, and more. Overall, less noise, along with the breadth of integrations, has already made security teams faster in triaging and finding real vulnerabilities. Having been security engineers ourselves, we also understand how important visibility is for the evaluations. ZeroPath users get executive dashboards with real-time MTTR tracking, automated compliance reporting for SOC2 and ISO27001, and risk-based prioritization using CVSS 4.0 scoring. The platform provides complete visibility across organizational repositories, including security models, authentication patterns, and filtering logic, without manual configuration. Our research team dogfeeds our own technology and has discovered CVE-2025-61928 (critical account takeover in better-auth with 300k+ weekly downloads), identified 170+ verified bugs in curl, found 7 vulnerabilities in django-allauth enabling account impersonation, and discovered 0-days in production systems at Netflix, Hulu, and Salesforce. Currently trusted by 750+ companies running 200k+ scans monthly, ZeroPath delivers what security-conscious engineering teams need: more real vulnerabilities, dramatically less noise, and automated fixes that actually work.

Average Rating: 4.5/5.0

Total Reviews: 11

How Do G2 Users Rate ZeroPath?

  • Quality of Support: 9.4/10 (Category avg: 9.0/10)
  • Integration: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind ZeroPath?

  • Seller: ZeroPath
  • Company Website:
  • Year Founded: 2024
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 36% Small, 27% Medium

What Do G2 Reviewers Say About ZeroPath?

AI-generated summary from verified user reviews

Pros
  • Users value the high accuracy of ZeroPath, effectively identifying real security issues with minimal false alarms.
  • Users value the accuracy of findings from ZeroPath, as it effectively identifies real security issues with minimal false alarms.
  • Users commend ZeroPath for its high accuracy in security detection, minimizing false alarms and enhancing issue resolution.
  • Users commend ZeroPath for its highly accurate vulnerability detection, minimizing false alarms and enhancing security efforts.
  • Users commend ZeroPath for its accurate vulnerability identification, significantly reducing false alarms and enhancing security efforts.
Cons
  • Users report bug issues with ZeroPath, but the support team addresses them quickly and effectively.
  • Users experience some bugs with ZeroPath, but the support team quickly resolves them to improve functionality.
  • Users face some software bugs in ZeroPath, though the team is responsive in resolving them quickly.
  • Users feel that the pricing structure of ZeroPath is not currently suitable for their organization's budget.
  • Users experience bugs in the dashboard, though the ZeroPath team swiftly addresses these problems.
What Are Recent G2 Reviews of ZeroPath?

Debricked

Debricked's SCA-tool allows you to manage your open source in an easy, smart and efficient manner. Automatically find, fix and prevent vulnerabilities, avoid non compliant licenses and evaluate the health of your dependencies - all in one tool. Security - Your developers shouldn't have to be security experts in order to write secure code. Debricked helps your developers automate open source security in their own pipelines and generate fixes with a button click. License Compliance - Make open source compliance a non issue by automating the prevention of non compliant licenses. Set customizable pipeline rules and make sure to be ready for launch year round. Community Health - Help your developers make informed decisions when choosing what open source to use. Search for name or functionality and easily compare similar projects side by side on a set of health metrics.

Average Rating: 4.8/5.0

Total Reviews: 5

How Do G2 Users Rate Debricked?

  • Quality of Support: 9.4/10 (Category avg: 9.0/10)
  • Language Support: 6.7/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 8.3/10 (Category avg: 8.7/10)
  • Integration: 9.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Debricked?

  • Seller: Debricked
  • Year Founded: 2018
  • HQ Location: Malmö, SE
  • Twitter: @debrickedab
    473 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 40% Medium

What Are Recent G2 Reviews of Debricked?

rezilion

Rezilion's software attack surface management platform automatically secures the software you deliver to customers, giving teams time back to build. Rezilion works across your stack, helping you to know what software is in your environment, what is vulnerable, and what is actually exploitable, so you can focus on what matters and remediate automatically. KEY FEATURES: - Dynamic SBOM Create an instant inventory of all the software components in your environment - Vulnerability Validation Know which of your software vulnerabilities are exploitable, and which are not, through runtime analysis - Vulnerability Remediation Cluster vulnerabilities to eliminate multiple problems at once and automatically execute remediation work to save teams time. WITH REZILION, ACHIEVE: - 85% reduction in patching work after filtering out unexplainable vulnerabilities - 24/7 Continuous monitoring of your software attack surface -600% Faster time to remediate when you focus on what matters and patch automatically - 360-degree visibility across your entire DevSecOps stack -- not just in silos

Average Rating: 4.4/5.0

Total Reviews: 11

How Do G2 Users Rate rezilion?

  • Quality of Support: 9.3/10 (Category avg: 9.0/10)
  • Language Support: 8.9/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 8.9/10 (Category avg: 8.7/10)
  • Integration: 7.2/10 (Category avg: 8.8/10)

Who Is the Company Behind rezilion?

  • Seller: rezilion
  • Year Founded: 2018
  • HQ Location: Be'er Sheva, Israel
  • Twitter: @rezilion_
    198 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 45% Medium, 36% Large

What Are Recent G2 Reviews of rezilion?

Sonatype Nexus Repository

World’s #1 Repository Manager with Free and Pro versions - Single source of truth for all of your components, binaries, and build artifacts. - Efficiently distribute parts and containers to developers. - Used by more than 5 million developers globally. Centralize Give your teams a single source of truth for every component they use. Store Optimize build performance and reliability by caching proxies of remote repositories. Adapt Deliver universal coverage for all major package types and formats Scale Install on an unlimited amount of servers for an unlimited amount of users. Universal Support for all Popular Build Tools Store and distribute Maven/Java, npm, NuGet, Helm, Docker, P2, OBR, APT, GO, R, Conan components and more. Manage components from dev through delivery: binaries, containers, assemblies, and finished goods. Awesome support for the Java Virtual Machine (JVM) ecosystem, including Gradle, Ant, Maven, and Ivy. Compatible with popular tools like Eclipse, IntelliJ, Hudson, Jenkins, Puppet, Chef, Docker, and more. Enterprise Control of Binaries and Build Artifacts Deliver innovation 24x7x365 with high availability. A single source of truth for components used across your entire software development lifecycle including QA, staging, and operations. Easily integrate with existing user and access provisioning systems including LDAP, Atlassian Crowd, and more. SAML/SSO authentication for enhanced security and single sign-on experience. See the Health of Your Software Supply Chain Repository Health Check (RHC) provides up-to-date component intelligence, so your teams make informed decisions early on. View components in need of remediation, prioritized by the severity of vulnerability. Easily avoid known security and license issues for Maven/Java, npm, NuGet, and PyPI components. Modern Features for Continuous Innovation Deploy directly to a desired repository with your choice of build or deployment tool or directly via HTTP. Stage and manage releases with dedicated security and automated rule validation. Enhanced staging provides streamlined oversight and approval of workflows for release candidates. Share binaries, snapshots and releases between groups of developers or post a collection of related, staged artifacts which can be easily tested, promoted, or discarded.

Average Rating: 4.5/5.0

Total Reviews: 21

How Do G2 Users Rate Sonatype Nexus Repository?

  • Quality of Support: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Sonatype Nexus Repository?

  • Seller: Sonatype
  • Year Founded: 2008
  • HQ Location: Fulton, US
  • Twitter: @sonatype
    10,589 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    567 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 43% Large, 39% Medium

What Are Recent G2 Reviews of Sonatype Nexus Repository?

What Are G2 Users Discussing About Sonatype Nexus Repository?

Dependency-Track

Dependency-Track is an intelligent Supply Chain Component Analysis platform that allows organizations to identify and reduce risk from the use of third-party and open source components. Dependency-Track takes a unique and highly beneficial approach by leveraging the capabilities of Software Bill of Materials (SBOM). This approach provides capabilities that traditional Software Composition Analysis (SCA) solutions cannot achieve. Dependency-Track monitors component usage across all versions of every application in its portfolio in order to proactively identify risk across an organization. The platform has an API-first design and is ideal for use in Continuous Integration (CI) and Continuous Delivery (CD) environments.

Average Rating: 4.3/5.0

Total Reviews: 4

How Do G2 Users Rate Dependency-Track?

  • Quality of Support: 6.7/10 (Category avg: 9.0/10)
  • Language Support: 9.2/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 7.5/10 (Category avg: 8.7/10)
  • Integration: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Dependency-Track?

  • Seller: OWASP
  • Year Founded: 2001
  • HQ Location: Wakefield, US
  • Twitter: @DependencyTrack
    1,436 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    686 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 75% Large, 25% Medium

What Do G2 Reviewers Say About Dependency-Track?

AI-generated summary from verified user reviews

Pros
  • Users value the neat UI and seamless integration of Dependency-Track, enhancing their overall experience and efficiency.
  • Users appreciate the neat UI and illustrative dashboards of Dependency-Track, enhancing usability and integration ease.
  • Users value the neat UI and integration ease of Dependency-Track, enhancing their risk management experience effectively.
  • Users love the neat UI with side nav bars and illustrative dashboards, enhancing their overall experience and integration.
Cons
  • Users find the limited cloud integration frustrating, relying on copy-pasting for collaboration instead.

What Are Recent G2 Reviews of Dependency-Track?

What Are G2 Users Discussing About Dependency-Track?

Kiuwan Code Security & Insights

Fast, Flexible Code Security! Kiuwan is a robust, end-to-end application security platform that integrates seamlessly into your development process. Our toolset includes Static Application Security Testing (SAST), Software Composition Analysis (SCA), Software Governance and Code Quality, empowering your team to quickly identify and remediate vulnerabilities. By integrating seamlessly into your CI/CD pipeline, Kiuwan enables early detection and remediation of security issues. Kiuwan supports strict compliance with industry standards including OWASP, CWE, MISRA, NIST, PCI DSS, and CERT, among others. Top features: ✅ Extensive language support: Over 30 programming languages. ✅ Detailed action plans: Prioritize remediation with tailored action plans. ✅ Code Security: Seamless Static Application Security Testing (SAST) integration. ✅ Insights: On-demand or continuous scanning Software Composition Analysis (SCA) to help reduce third-party threats. ✅ One-click Software Bill of Materials (SBOM) generation. Kiuwan is now part of Sembi - a global portfolio of market-leading software brands focused on software quality, security, and developer productivity. Code Smarter. Secure Faster. Ship Sooner

Average Rating: 4.5/5.0

Total Reviews: 29

How Do G2 Users Rate Kiuwan Code Security & Insights?

  • Quality of Support: 8.9/10 (Category avg: 9.0/10)

Who Is the Company Behind Kiuwan Code Security & Insights?

  • Seller: Sembi
  • Company Website:
  • Year Founded: 2023
  • HQ Location: Austin, US
  • LinkedIn® Page: www.linkedin.com
    114 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Banking
  • Company Size: 41% Large, 35% Medium

What Do G2 Reviewers Say About Kiuwan Code Security & Insights?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the accuracy of the results from Kiuwan Code Security & Insights, enhancing their overall experience.
  • Users value the accuracy of findings from Kiuwan, enhancing their satisfaction with code security and reporting.
  • Users commend the efficient customer support of Kiuwan, ensuring timely assistance and strong satisfaction overall.
  • Users appreciate the user-friendly interface of Kiuwan Code Security & Insights, making it very easy to navigate.
  • Users appreciate the user-friendly interface of Kiuwan Code Security & Insights, enhancing ease of use for dashboards.

What Are Recent G2 Reviews of Kiuwan Code Security & Insights?

IriusRisk

We make secure design the standard, scalable practice for all digital teams. IriusRisk makes secure design fast, reliable and accessible, even to non-security users, thanks to our automated and AI-augmented Threat Modeling Solution.

Average Rating: 4.7/5.0

Total Reviews: 3

How Do G2 Users Rate IriusRisk?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)
  • Language Support: 5.0/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 6.7/10 (Category avg: 8.7/10)
  • Integration: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind IriusRisk?

  • Seller: IriusRisk
  • HQ Location: Huesca, Aragon, Spain
  • Twitter: @IriusRisk
    1,666 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    181 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 33% Large, 33% Medium

What Do G2 Reviewers Say About IriusRisk?

AI-generated summary from verified user reviews

Pros
  • Users value the threat library of IriusRisk, finding it highly beneficial for risk management and analysis.
Cons
  • Users face challenges due to the limited cloud integration, which restricts their ability to fully leverage the tool.

What Are Recent G2 Reviews of IriusRisk?

Sonatype Lifecycle

Continuously secure your software supply chain with Sonatype Nexus Lifecycle, a software composition analysis (SCA) solution. Nexus Lifecycle helps development, security, and compliance teams reduce open source risk without slowing delivery. It detects vulnerable or non-compliant components early, provides clear remediation guidance, and enforces the same policies from development through CI/CD and release - powered by Sonatype Nexus Intelligence. Choose safer components up front: A Chrome extension and IDE integrations surface vulnerability, license, and quality insights as developers browse public repositories or add dependencies. Fix issues fast where work happens: In Eclipse, IntelliJ, and Visual Studio, developers can see exactly what's wrong and upgrade to an approved version with a click - no guesswork. Automate remediation in source control: Integrations with GitHub, GitLab, and Atlassian Bitbucket can comment on pull/merge requests and identify the specific dependency change that introduces risk, along with recommended versions to resolve it. You can also generate automated pull requests to update components that violate policy. Enforce open source policies across the SDLC: Create security, license, and architectural policies tailored by application type, team, or organization, then apply them consistently in developer tools, CI/CD, and repositories to prevent risky components from reaching production. Generate SBOMs in minutes: Produce accurate Software Bills of Materials (SBOMs) per application to understand what components and transitive dependencies are in use and verify compliance. Prove progress with reporting: Track trends like Mean Time to Resolution (MTTR) and violation reduction over time to demonstrate measurable risk reduction to stakeholders. Nexus Lifecycle integrates with common developer, CI/CD, and repository tools including Nexus Repository, Artifactory, Jira, Jenkins, Azure DevOps, and more.

Average Rating: 4.2/5.0

Total Reviews: 3

How Do G2 Users Rate Sonatype Lifecycle?

  • Quality of Support: 7.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Sonatype Lifecycle?

  • Seller: Sonatype
  • Year Founded: 2008
  • HQ Location: Fulton, US
  • Twitter: @sonatype
    10,589 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    567 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 75% Large, 25% Medium

What Are Recent G2 Reviews of Sonatype Lifecycle?

Veracode Application Security Platform

Veracode helps companies that innovate through software deliver secure code on time. Unlike on-premise solutions that are hard to scale and focused on finding rather than fixing, Veracode comprises a unique combination of SaaS technology and on-demand expertise that enables DevSecOps through integration with your pipeline,empower developers to fix security defects, and scales your program through best practices to achieve your desired outcomes. Veracode covers your all your AppSec needs in one solution through a combination of five analysis types available for 24 programming languages, 77 frameworks, and application types as varied as microservices, mainframe and mobile apps.

Average Rating: 3.8/5.0

Total Reviews: 25

How Do G2 Users Rate Veracode Application Security Platform?

  • Quality of Support: 8.0/10 (Category avg: 9.0/10)
  • Language Support: 10.0/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Integration: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Veracode Application Security Platform?

  • Seller: VERACODE
  • Year Founded: 2006
  • HQ Location: Burlington, MA
  • Twitter: @Veracode
    21,950 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    500 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 69% Large, 31% Medium

What Do G2 Reviewers Say About Veracode Application Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the effective security vulnerability identification offered by Veracode, enhancing overall application safety and code integrity.
  • Users find Veracode's vulnerability detection excellent for identifying security issues and ensuring high application security standards.
  • Users value the automated scanning of Veracode, streamlining security checks and enhancing code quality effortlessly.
  • Users value the effective detection of security vulnerabilities, enabling robust protection and streamlined development processes.
  • Users appreciate the ease of integration with GitHub and CI/CD pipelines, streamlining their development process effectively.
Cons
  • Users find Veracode to be expensive, with high costs, complex licensing, and unfulfilled feature delivery.
  • Users face a lack of information due to mismatches in documentation and delayed notifications during uploads.
  • Users express concerns over licensing issues, including rising costs, complex models, and unequal feature availability.
  • Users report poor customer support with pushy account executives and difficulties in resolving issues efficiently.
  • Users express concerns about pricing issues, with rising costs and a complex licensing model affecting value perception.

What Are Recent G2 Reviews of Veracode Application Security Platform?

What Are G2 Users Discussing About Veracode Application Security Platform?

Xygeni

Xygeni: AI-Native ASPM for the Software Supply Chain Xygeni is an AI-native ASPM (Application Security Posture Management) platform that unifies native and third-party security findings into one prioritized view. Its own detection engines cover SAST, SCA, DAST, Secrets, IaC, Container, CI/CD, and Build Security, and it also ingests results from tools like Snyk, Veracode, and Checkmarx so teams don't have to abandon what they've already invested in. Every finding, regardless of source, gets scored by exploitability, reachability, and business impact through Xygeni's Dynamic Funnels, which is what drives its reported 90% cut in alert noise. Two AI systems sit underneath the platform. CoreAI acts as a correlation and reporting layer for security leaders, turning scattered findings into a single risk narrative. DevAI works earlier, inside the developer's IDE and AI coding assistants, catching problems in both human-written and AI-generated code and proposing fixes before a pull request is even opened. On the supply chain side, Xygeni's MEW engine (Malware Early Warning) is built to catch malicious open-source packages the moment they hit a public registry, ahead of when a formal malware signature would normally exist. Shield takes that enforcement to the developer's own machine, blocking unauthorized package downloads at the OS level before they reach disk. Xygeni also runs a dedicated Code Quality engine across ten languages, ranking maintainability and complexity issues alongside security findings in the same console, so a team can see when the messiest file is also the riskiest one. The platform connects to GitHub, GitLab, Bitbucket, Jenkins, and Azure DevOps, and deploys as SaaS, on-premises, or fully air-gapped. Xygeni was named Hot Company in ASPM and in GenAI Application Security at the 2026 Global InfoSec Awards.

Average Rating: 4.6/5.0

Total Reviews: 4

How Do G2 Users Rate Xygeni?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)
  • Language Support: 8.3/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Integration: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Xygeni?

  • Seller: Xygeni Security
  • Year Founded: 2021
  • HQ Location: Madrid, ES
  • Twitter: @xygeni
    178 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    30 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 40% Medium

What Do G2 Reviewers Say About Xygeni?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the comprehensive security features of Xygeni, fostering a secure development environment without hindering productivity.
  • Users value the effective prioritization of security issues in Xygeni, allowing teams to focus on critical threats quickly.
  • Users value the effective risk management of Xygeni, enhancing security without hindering software development processes.
  • Users appreciate the robust security features of Xygeni, enhancing their development process while ensuring compliance and risk management.
  • Users value the seamless CI/CD integration of Xygeni, enabling early vulnerability detection without impacting release schedules.
Cons
  • Users face difficult setup issues with Xygeni, especially when dealing with certain edge cases requiring manual adjustments.
  • Users find the learning curve challenging for newcomers despite a generally intuitive platform, requiring familiarity with AppSec practices.

What Are Recent G2 Reviews of Xygeni?

Bytesafe

Bytesafe is a platform for end-to-end software supply chain security - a firewall for your dependencies. The platform consists of: - Dependency Firewall - Package Management - Software Composition Analysis - License Compliance

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate Bytesafe?

  • Quality of Support: 10.0/10 (Category avg: 9.0/10)
  • Language Support: 6.7/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 8.3/10 (Category avg: 8.7/10)
  • Integration: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind Bytesafe?

  • Seller: Bytesafe
  • Year Founded: 2018
  • HQ Location: Stockholm, SE
  • Twitter: @bytesafedev
    479 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Bytesafe?

What Are G2 Users Discussing About Bytesafe?

FossID

FossID is a Software Composition Analysis (SCA) suite designed to give organizations clear, defensible insight into the software they build and ship. It helps teams understand exactly what third-party, open source, and commercial code exists in their products so they can manage license compliance, intellectual property risk, and security with confidence. Agentic SCA by FossID brings software supply chain integrity into the moment of code creation for continuous, real-time license and security compliance so you can move at AI-speed and eliminate reactive code rework. FossID is ideal for organizations that value accuracy, transparency, and control over their software supply chain. It is widely used by manufacturers of embedded systems and software-driven products in industries such as automotive, aerospace, medical devices, industrial automation, electronics, and telecom, where regulatory requirements and long product lifecycles demand a higher standard of software governance. FossID is also trusted by legal, compliance, and GRC teams that need reliable, auditable results, as well as by acquirers and investors conducting technical due diligence. FossID analyzes real source code rather than relying solely on declared dependencies. FossID identifies reused components and code snippets with high precision, detecting fragments as small as six lines of code. This approach delivers more accurate results in complex, mixed codebases, including legacy systems, embedded software, and environments influenced by AI-assisted development. Key differentiators include deep snippet-level detection that remains effective even when code has been modified or reformatted, a 200M+ component open source knowledge base covering more than 2,500 licenses, and strong identification of license and copyright obligations. FossID is deployed in a way that ensures that source code never leaves the organization, a critical requirement for security- and IP-sensitive teams. FossID supports software supply chain integrity across the entire development and release lifecycle. Engineers use it early to identify and resolve issues before code is merged. Legal and compliance teams rely on it to validate policy compliance, manage license obligations and produce accurate SBOMs. Governance, Risk, and Compliance leaders use FossID to demonstrate software supply chain transparency, reduce audit risk, and support regulatory compliance initiatives, including the EU Cyber Resilience Act. The primary value of FossID is confidence. Confidence in what is inside your software, confidence in your compliance posture, and confidence that your teams can move forward efficiently without introducing unnecessary risk.

Average Rating: 4.0/5.0

Total Reviews: 2

How Do G2 Users Rate FossID?

  • Quality of Support: 7.5/10 (Category avg: 9.0/10)
  • Language Support: 8.3/10 (Category avg: 8.5/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Integration: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind FossID?

  • Seller: FossID
  • Company Website:
  • Year Founded: 2016
  • Twitter: @FOSSID_AB
    137 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 50% Medium

What Are Recent G2 Reviews of FossID?

Adam Crivello
AC
Researched and written by Adam Crivello
Updated October 3, 2024