Best Extended Detection and Response (XDR) Platforms - Page 3

How Many Extended Detection and Response (XDR) Platforms Products Does G2 Track?

Total Products under this Category: 113

Category Stats (Nov 2026)

  • Average Rating: 4.55/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.95%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Extended Detection and Response (XDR) Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,900+ Authentic Reviews
  • 113+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

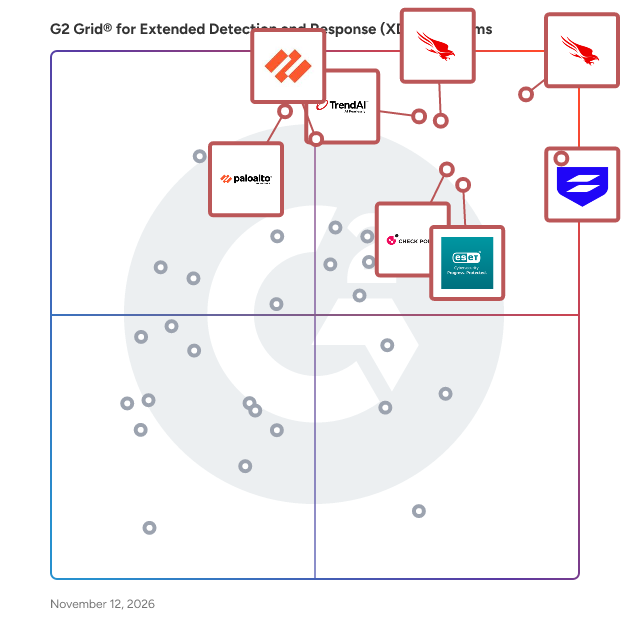
G2 Grid® for Extended Detection and Response (XDR) Platforms

G2 Grid® for Extended Detection and Response (XDR) Platforms plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.

Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.5/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Blumira, facilitating quick detection and monitoring of security incidents.
  • Users value the outstanding customer support of Blumira, highlighting swift assistance and a seamless onboarding experience.
  • Users appreciate the easy implementation of Blumira Automated Detection & Response, enabling quick and efficient setup processes.
  • Users value the real-time alerting feature of Blumira, enhancing their security awareness and incident management.
  • Users value the real-time alerting of Blumira, as it effectively tracks security events in their MS 365 environment.
Cons
  • Users feel that the limited customization options hinder the product's potential and integration capabilities with other tools.
  • Users find the alert system's customization lacking, highlighting a need for improved log source comparisons and SIEM functionality.
  • Users find the pricing model expensive and inflexible, not meeting their budget or needs effectively.
  • Users find the faulty detection limitations frustrating, especially around custom rules and log visibility.
  • Users find the inefficient alert system lacking essential user details, complicating response strategies and false positive management.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

Eye Security

Eye Security delivers one integrated solution for threat detection, incident response and cyber insurance. Most vendors sell you separate tools. Eye Security combines what companies typically buy separately into a single system of protection. Continuous monitoring happens through a 24/7 European SOC. When threats appear, Eye Security's team investigates, contains the damage, and guides you through recovery. Protection goes beyond detection: it means having cybersecurity experts who act, not just alerts you have to interpret. The Managed Detection and Response (MDR) service uses AI-accelerated threat detection combined with human expertise. This approach catches threats that automated tools alone miss, while keeping response times fast. Cyber insurance rounds out the approach, covering costs that even strong detection and response can't prevent. Together, detection, response and insurance create comprehensive cybersecurity coverage designed for real-world incidents. Eye Security is built for small and mid-sized companies in Europe that need professional cybersecurity without the overhead of an in-house security team. You get enterprise-grade threat detection and incident response capabilities without managing a large security operations center yourself. The service handles the complexity of modern cybersecurity so you can focus on running your business. One solution. One system of protection.

Average Rating: 4.1/5.0

Total Reviews: 14

How Do G2 Users Rate Eye Security?

  • Has the product been a good partner in doing business?: 8.1/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 7.5/10 (Category avg: 9.2/10)

Who Is the Company Behind Eye Security?

  • Seller: Eye Security
  • Company Website:
  • Year Founded: 2020
  • HQ Location: Den Haag, NL
  • LinkedIn® Page: www.linkedin.com
    273 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 29% Large

What Are Recent G2 Reviews of Eye Security?

LogRhythm SIEM

Rapidly deploy LogRhythm SIEM, the leading self-hosted SIEM, to secure your organization with powerful detections, synchronized threat intelligence, automated workflows, and achieve faster, more accurate threat detection, investigation, and response (TDIR).

Average Rating: 4.2/5.0

Total Reviews: 137

How Do G2 Users Rate LogRhythm SIEM?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)

Who Is the Company Behind LogRhythm SIEM?

  • Seller: Exabeam
  • Year Founded: 2013
  • HQ Location: Broomfield, CO
  • LinkedIn® Page: www.linkedin.com
    785 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Information Security Analyst, Cyber Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 40% Large, 40% Medium

What Are Recent G2 Reviews of LogRhythm SIEM?

What Are G2 Users Discussing About LogRhythm SIEM?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Adlumin

Adlumin, an N-able Company, provides enterprise-grade cybersecurity for organizations of all sizes through its innovative Security Operations as a Service platform. With an agnostic approach, the Adlumin platform seamlessly integrates with existing tech stacks, and its flexible management options enable it to be self-managed by an internal team, or fully managed by Adlumin experts. The Adlumin platform stops cyber threats early with deep learning models tailored to each environment. It maximizes resource efficiency by optimizing existing technology and streamlining workflows across teams. Adlumin transforms risk into resilience by identifying and addressing vulnerabilities, while cybersecurity experts proactively uncover and neutralize threats before they can do damage. Adlumin empowers organizations to take control of their digital security making advanced protection accessible to all.

Average Rating: 4.7/5.0

Total Reviews: 65

How Do G2 Users Rate Adlumin?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.2/10)
  • Unified Visibility: 6.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 7.5/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 6.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Adlumin?

  • Seller: N-able
  • Company Website:
  • HQ Location: Morrisville, North Carolina
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 56% Medium, 23% Small

What Do G2 Reviewers Say About Adlumin?

AI-generated summary from verified user reviews

Pros
  • Users value the detailed analytic reports from Adlumin, praising its reliability and ease of use.
  • Users value the detailed analytic reports from Adlumin, praising its reliability and user-friendly interface.
  • Users find Adlumin reliable and easy to use, particularly valuing the detailed analytic reports it provides.
  • Users appreciate the ease of management in Adlumin, finding it reliable and user-friendly for detailed reports.
  • Users find Adlumin's interface to be easy to use, with detailed analytics enhancing their experience.
Cons
  • Users feel that Adlumin's customer support could be better, indicating some room for improvement in service quality.

What Are Recent G2 Reviews of Adlumin?

B1 Platform by CloudCover

A network security platform, years in the making, leveraging mathematics to continuously learn, predict, and defend against attacks.

Average Rating: 4.6/5.0

Total Reviews: 43

How Do G2 Users Rate B1 Platform by CloudCover?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 7.6/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.2/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 7.3/10 (Category avg: 8.8/10)

Who Is the Company Behind B1 Platform by CloudCover?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 39% Medium, 39% Small

What Are Recent G2 Reviews of B1 Platform by CloudCover?

What Are G2 Users Discussing About B1 Platform by CloudCover?

SentinelOne Singularity XDR

SentinelOne Singularity XDR is an advanced cybersecurity platform that delivers autonomous prevention, detection, and response across endpoints, cloud workloads, and identity infrastructures. Leveraging artificial intelligence and machine learning, it provides real-time threat detection and automated remediation, ensuring comprehensive protection against a wide range of cyber threats. Key Features and Functionality: - Autonomous Threat Detection and Response: Utilizes AI-driven behavioral analysis to identify and neutralize threats without human intervention. - Comprehensive Coverage: Protects endpoints, cloud workloads, and identity infrastructures, offering a unified security solution. - Real-Time Visibility: Provides continuous monitoring and insights into the security posture of the entire IT environment. - Automated Remediation: Executes swift and precise responses to detected threats, minimizing potential damage. - Scalability: Designed to adapt to organizations of various sizes, ensuring effective protection as businesses grow. Primary Value and Problem Solved: Singularity XDR addresses the challenge of managing complex and evolving cyber threats by offering an integrated, AI-powered security platform. It reduces the need for manual intervention, enhances operational efficiency, and provides organizations with the tools to proactively defend against sophisticated attacks, thereby safeguarding critical assets and data.

Average Rating: 4.7/5.0

Total Reviews: 9

How Do G2 Users Rate SentinelOne Singularity XDR?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.5/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.7/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind SentinelOne Singularity XDR?

  • Seller: SentinelOne
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Company Size: 78% Medium, 11% Small

What Do G2 Reviewers Say About SentinelOne Singularity XDR?

AI-generated summary from verified user reviews

Pros
  • Users highly value the AI-powered monitoring of SentinelOne, enhancing threat detection and response across their environments.
  • Users value the AI-powered threat detection of SentinelOne Singularity XDR, enhancing security with automated and efficient responses.
  • Users appreciate the storyline-based alerting of SentinelOne Singularity XDR, making threat response clear and efficient.
  • Users value the automated threat detection and response of SentinelOne Singularity XDR, enhancing security efficiency and confidence.
  • Users value the seamless third-party integrations of SentinelOne Singularity XDR for streamlined, efficient security management.
Cons
  • Users express concern over the high pricing of SentinelOne Singularity XDR, which may challenge budget-conscious organizations.
  • Users find the documentation confusing, which complicates the setup and utilization of SentinelOne Singularity XDR.
  • Users experience false positives, leading to added administrative work while fine-tuning policies and managing alerts.
  • Users find the learning curve steep for advanced features and dashboards, needing dedicated training for effective use.
  • Users note that the setup process is complex and challenging, especially in large or diverse environments.

What Are Recent G2 Reviews of SentinelOne Singularity XDR?

WithSecure Elements Extended Detection and Response (XDR)

WithSecure Elements Extended Detection and Response (XDR) is a unified solution, designed to protect modern IT estates. It minimizes the impact of attacks by using automated and advanced preventative controls that keep incident volumes and lower-level attacks at bay. AI-powered tooling enables fast detection, investigation, and response to threats. Luminen GenAI assistant is automatically included with Elements XDR, further empowering your analyst. Secure your digital environment: - Endpoints (laptops and workstations, mobiles, servers) - Digital identities and their user credentials (Microsoft Entra ID) - Cloud resources (Microsoft Azure) - Emails and cloud-based collaboration services (Microsoft 365 including Exchange, SharePoint sites, OneDrive, and Microsoft Teams)

Average Rating: 4.4/5.0

Total Reviews: 117

How Do G2 Users Rate WithSecure Elements Extended Detection and Response (XDR)?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.3/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind WithSecure Elements Extended Detection and Response (XDR)?

  • Seller: WithSecure
  • Year Founded: 1988
  • HQ Location: Helsinki, Finland
  • LinkedIn® Page: www.linkedin.com
    1,780 employees on LinkedIn®
  • Ownership: FSOYF
  • Total Revenue (USD mm): $220

Who Uses This Product?

  • Company Size: 45% Medium, 40% Small

What Do G2 Reviewers Say About WithSecure Elements Extended Detection and Response (XDR)?

AI-generated summary from verified user reviews

Pros
  • Users value the user-friendly cloud console of WithSecure Elements XDR, making management and monitoring effortless.
  • Users praise the efficiency of WithSecure Elements XDR, ensuring smooth performance and reliable security without slowdowns.
  • Users value the effective alerting of WithSecure XDR, enabling quick identification of network vulnerabilities and weaknesses.
  • Users value the user-friendly cloud console of WithSecure Elements XDR, making endpoint management effortless and efficient.
  • Users value the easy management of WithSecure Elements XDR, thanks to its user-friendly cloud console for monitoring.
Cons
  • Users find WithSecure Elements XDR to be not user-friendly, citing a confusing interface and slow updates.
  • Users experience frequent and repetitive alerts, which can disrupt workflows and impact overall satisfaction with the tool.
  • Users experience console issues with slow updates, repetitive alerts, and a need for a modern interface.
  • Users experience delay issues with slow updates across devices and alerts that can be overly repetitive.
  • Users report issues with false positives, wishing for a more intelligent system to accurately learn accepted behaviors.

What Are Recent G2 Reviews of WithSecure Elements Extended Detection and Response (XDR)?

What Are G2 Users Discussing About WithSecure Elements Extended Detection and Response (XDR)?

Cybereason Defense Platform

Cybereason automatically detects malicious activity and presents it in an intuitive way. It deploys easily with minimal organizational impact and provides end-to-end context of an attack campaign. Most organizations deploy Cybereason and start detecting attacks within 24 to 48 hours.

Average Rating: 4.4/5.0

Total Reviews: 18

How Do G2 Users Rate Cybereason Defense Platform?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind Cybereason Defense Platform?

  • Seller: Cybereason
  • Year Founded: 2012
  • HQ Location: La Jolla, San Diego, US
  • LinkedIn® Page: www.linkedin.com
    448 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 61% Large, 22% Small

What Do G2 Reviewers Say About Cybereason Defense Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the great security options of Cybereason, benefiting from swift detection of malicious activity.
  • Users value the ease of use of the Cybereason Defense Platform, streamlining setup and enhancing security effortlessly.
  • Users commend the exceptional security options offered by the Cybereason Defense Platform, ensuring swift threat detection and protection.
  • Users value the seamless detection of malicious activity through Cybereason’s automated hunting engine and AI capabilities.
  • Users value the AI-driven threat detection of Cybereason, which swiftly identifies and mitigates malicious activities across endpoints.
Cons
  • Users note the need for enhanced user interface and better custom detection features to improve overall experience.
  • Users experience lack of clarity in after-sales support, making business interactions challenging and less effective.
  • Users feel the limited customization options hinder the effectiveness of the Cybereason Defense Platform's tailored defenses.
  • Users highlight the need for enhanced features in the Cybereason Defense Platform's custom detection rules for better usability.
  • Users find the poor customer support of Cybereason Defense Platform makes business interactions challenging and frustrating.

What Are Recent G2 Reviews of Cybereason Defense Platform?

What Are G2 Users Discussing About Cybereason Defense Platform?

Wirespeed

Lighting-fast automated detection & response (ADR) that helps stop threats in seconds. Wirespeed Automated Detection & Response uses automation to analyze alerts in milliseconds and contain threats before they can spread, only escalating critical cases that require your expertise. It’s an evolution of MDR designed to stand up to today’s machine-speed threats. It’s deployable in a few clicks and works seamlessly with your existing security stack.

Average Rating: 5.0/5.0

Total Reviews: 11

How Do G2 Users Rate Wirespeed?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Wirespeed?

Who Uses This Product?

  • Company Size: 55% Medium, 45% Small

What Do G2 Reviewers Say About Wirespeed?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring of Wirespeed, ensuring proactive threat detection and rapid alerts around the clock.
  • Users love the easy integrations of Wirespeed, facilitating quick setups for efficient threat monitoring and alerts.
  • Users highlight the exceptional ease of use of Wirespeed, benefiting from seamless integration and intuitive features.
  • Users love the immediate and actionable alert management of Wirespeed, enhancing their response to potential threats effortlessly.
  • Users praise the exceptional customer support of Wirespeed, highlighting fast responses and expert assistance throughout implementation.

What Are Recent G2 Reviews of Wirespeed?

Open XDR Security Operations Platform

The Stellar Cyber Open XDR platform delivers comprehensive, unified security without complexity, empowering lean security teams of any skill to successfully secure their environments. With Stellar Cyber, organizations reduce risk with early and precise identification and remediation of threats while slashing costs, retaining investments in existing tools, and improving analyst productivity, delivering an 8x improvement in MTTD and a 20x improvement in MTTR. The company is based in Silicon Valley. For more information, visit stellarcyber.ai.

Average Rating: 4.9/5.0

Total Reviews: 8

How Do G2 Users Rate Open XDR Security Operations Platform?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.7/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Open XDR Security Operations Platform?

  • Seller: STELLAR CYBER
  • Year Founded: 2017
  • HQ Location: San Jose, California, United States
  • LinkedIn® Page: www.linkedin.com
    150 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 25% Large

What Do G2 Reviewers Say About Open XDR Security Operations Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the seamless integrations of Open XDR, enhancing efficiency by unifying different security vendors' tools in one platform.
  • Users appreciate the easy integrations of Open XDR, enhancing threat detection without overhauling existing security systems.
  • Users value the comprehensive visibility provided by Open XDR, enabling a unified view of all security data sources.
  • Users value the effective threat detection capabilities of Open XDR, enhancing accuracy and reducing alert fatigue significantly.
  • Users appreciate the AI automation in Open XDR, enhancing threat detection speed and reducing alert fatigue significantly.
Cons
  • Users find the integration issues time-consuming, especially when connecting multiple tools or newly emerging solutions.
  • Users experience alerting issues that complicate operations, creating challenges with notifications and bulk assignments.
  • Users encounter troublesome alert management issues in Open XDR, leading to inefficiencies and increased workload during assignments.
  • Users face false positives that complicate alert management, creating unnecessary noise and impacting analyst efficiency.
  • Users face an inefficient alert system plagued by bugs, causing troubles with alerts during bulk assignments.

What Are Recent G2 Reviews of Open XDR Security Operations Platform?

Qomplx

QOMPLX is a leading provider of identity-focused cybersecurity software solutions. Our technology continually monitors user activity across all points of access, including cloud and on-premise systems, to prevent harm to your network, detect suspicious behavior and anomalies, and provide contextualized recommendations to improve your overall cybersecurity. The QOMPLX data platform provides real-time alerts and visualizations for rapid response and to allow for a proactive stance against malicious actors. It also enables the capture and store of identity data for future analysis, allowing organizations to detect and respond to emerging threats in a timely and effective manner. Additionally, our platform provides comprehensive reporting, audit trails, and a secure environment for identity management. With QOMPLX solutions, organizations can protect their digital environment from identity-related threats and ensure business continuity by utilizing: • Threat Detection and Response (ITDR) Prevent, detect and respond to identity threats in real-time • Managed Solutions Cost effective managed cybersecurity including Managed ITDR, Managed Extended Detection and Response (XDR), and Managed Detection and Response (MDR) • Attack Surface Monitoring (ASM) Discover cyber vulnerabilities and the size of your attack surface

Average Rating: 4.5/5.0

Total Reviews: 11

How Do G2 Users Rate Qomplx?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Unified Visibility: 9.2/10 (Category avg: 9.1/10)
  • Threat Hunting: 9.6/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Qomplx?

  • Seller: QOMPLX
  • Year Founded: 2015
  • HQ Location: Tysons, Virginia
  • LinkedIn® Page: www.linkedin.com
    22 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 55% Medium, 27% Large

What Are Recent G2 Reviews of Qomplx?

Symantec Storage Protection

Scalable, high-performance malware detection and prevention for cloud services, NAS devices, AWS S3 buckets, and SharePoint servers

Average Rating: 4.0/5.0

Total Reviews: 6

How Do G2 Users Rate Symantec Storage Protection?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Unified Visibility: 6.7/10 (Category avg: 9.1/10)
  • Threat Hunting: 5.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Symantec Storage Protection?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA
  • Phone: +1 800 225-5224

Who Uses This Product?

  • Company Size: 67% Small, 33% Large

What Do G2 Reviewers Say About Symantec Storage Protection?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the detection efficiency of Symantec Storage Protection, effectively preventing malware with a user-friendly setup.
  • Users find the ease of use of Symantec Storage Protection makes setup and operation straightforward and efficient.
  • Users find the setup ease of Symantec Storage Protection helpful, appreciating its straightforward and user-friendly installation process.
Cons
  • Users find the upgrade process time-consuming, which can lead to frustration during implementation of Symantec Storage Protection.

What Are Recent G2 Reviews of Symantec Storage Protection?

What Are G2 Users Discussing About Symantec Storage Protection?

Secureworks Taegis XDR

Taegis XDR is a cloud-native extended detection and response security platform that consolidates best-of-breed security components into a holistic ecosystem to provide proactive protection against complex cyber-attacks. Built on 20+ years of industry-leading security expertise, the solution is differentiated by our advanced analytics, integrated threat visibility and community-applied intelligence.

Average Rating: 4.0/5.0

Total Reviews: 6

How Do G2 Users Rate Secureworks Taegis XDR?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.8/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Secureworks Taegis XDR?

  • Seller: Sophos
  • Year Founded: 1985
  • HQ Location: Oxfordshire
  • LinkedIn® Page: www.linkedin.com
    5,550 employees on LinkedIn®
  • Ownership: LSE:SOPH

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Do G2 Reviewers Say About Secureworks Taegis XDR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the fantastic network security integration and effective alerting for monitored endpoints with Secureworks Taegis XDR.
  • Users value the superior threat detection of Secureworks Taegis XDR, enhancing network security and incident response.
  • Users value the real-time alerts from Secureworks Taegis XDR for enhanced security monitoring and awareness.
  • Users value the network alerts from Secureworks Taegis XDR, especially with monitored endpoints enhancing security awareness.
  • Users value the comprehensive attack surface coverage of Secureworks Taegis XDR, enhancing their overall security posture.
Cons
  • Users find the pricing to be substantial, making it a costly choice for their security needs.
  • Users experience false positives occasionally, leading to confusion and undermining confidence in the system's accuracy.
  • Users find the interface not intuitive, making navigation cumbersome and affecting overall user experience.

What Are Recent G2 Reviews of Secureworks Taegis XDR?

Cylerian Unified Cybersecurity Platform

Cylerian is the Intelligence Engineering Platform for the modern SOC, designed to bridge the gap between Security, Observability, and Operations. Traditional security operations are bogged down by fragmented tools—separate agents for EDR, SIEM, and RMM that don’t talk to each other. Cylerian solves this by providing a unified cloud-native platform that orchestrates the entire lifecycle of an incident, from detection to remediation. Built on a high-performance, AI-native architecture, Cylerian empowers security teams to: See Everything: Achieve ultimate observability with a unified data fabric that ingests logs, flows, and telemetry across endpoints, cloud, and networks. Act Instantly: Move beyond passive alerting. Cylerian’s agent provides the "hands" to fix what it finds, enabling automated patching, software deployment, and threat remediation without complex scripting. Simplify Operations: Replace costly, disjointed stacks (SIEM + EDR + RMM + SOAR) with one cohesive solution. Whether you are an MSP looking to scale efficiently or an enterprise seeking robust cyber resilience, Cylerian delivers enterprise-grade security and compliance tools (like File Integrity Monitoring and Compliance Tracking) with the ease of use of a modern SaaS platform.

Average Rating: 5.0/5.0

Total Reviews: 4

How Do G2 Users Rate Cylerian Unified Cybersecurity Platform?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Cylerian Unified Cybersecurity Platform?

  • Seller: Cylerian
  • Year Founded: 2018
  • HQ Location: Jersey City, US
  • LinkedIn® Page: www.linkedin.com
    17 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Do G2 Reviewers Say About Cylerian Unified Cybersecurity Platform?

AI-generated summary from verified user reviews

Pros
  • Users love the seamless integrations of Cylerian, enhancing functionality across all their applications effortlessly.
  • Users are impressed by the remediation automation in Cylerian, enhancing their cybersecurity processes effortlessly.
  • Users praise the comprehensive risk management capabilities of Cylerian, with daily use highlighting its extensive functionalities.
  • Users are impressed by the comprehensive vulnerability detection capabilities of Cylerian, enhancing their cybersecurity efficiency.
Cons
  • Users find the learning curve steep, requiring more training and resources to fully utilize the platform.
  • Users find the training issues challenging due to the platform's complexity and the need for additional resources.

What Are Recent G2 Reviews of Cylerian Unified Cybersecurity Platform?

Singularity AI SIEM

Secure your entire organization with the industry's fastest AI-powered open platform for all your data and workflows—built on the SentinelOne Singularity™ Data Lake. Singularity AI SIEM is designed for the autonomous SOC, empowering your security operations center to operate at peak efficiency. By leveraging AI and automation, our SIEM solution enables you to: Detect and respond to threats faster Improve overall security posture Reduce false positives and noise Allocate resources more effectively

Average Rating: 4.5/5.0

Total Reviews: 6

How Do G2 Users Rate Singularity AI SIEM?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Singularity AI SIEM?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Company Size: 50% Medium, 33% Small

What Do G2 Reviewers Say About Singularity AI SIEM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the sophisticated AI-powered capabilities of Singularity AI SIEM, enhancing their threat detection and response efficiency.
  • Users value the attentive customer support of Singularity AI SIEM, enhancing their overall experience and effectiveness.
  • Users value the high detection accuracy of Singularity AI SIEM, enhancing their ability to swiftly address security threats.
  • Users value the user-friendly interface of Singularity AI SIEM, making threat management accessible for all skill levels.
  • Users appreciate the efficiency of Singularity AI SIEM, enabling faster threat identification and response than traditional tools.
Cons
  • Users find the initial setup complex, which may lead to a steeper learning curve for effective use.
  • Users find the complex setup of Singularity AI SIEM to be a significant hurdle during initial implementation.
  • Users are concerned about the high cost of Singularity AI SIEM, impacting its accessibility and overall value.
  • Users note the high cost and complex setup of Singularity AI SIEM, impacting user accessibility and experience.
  • Users note the limited features of Singularity AI SIEM, which may hinder its overall effectiveness compared to competitors.

What Are Recent G2 Reviews of Singularity AI SIEM?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024