Best Attack Surface Management Software - Page 2

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 189

Category Stats (Sep 2026)

  • Average Rating: 4.6/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+2.02%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,900+ Authentic Reviews
  • 189+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

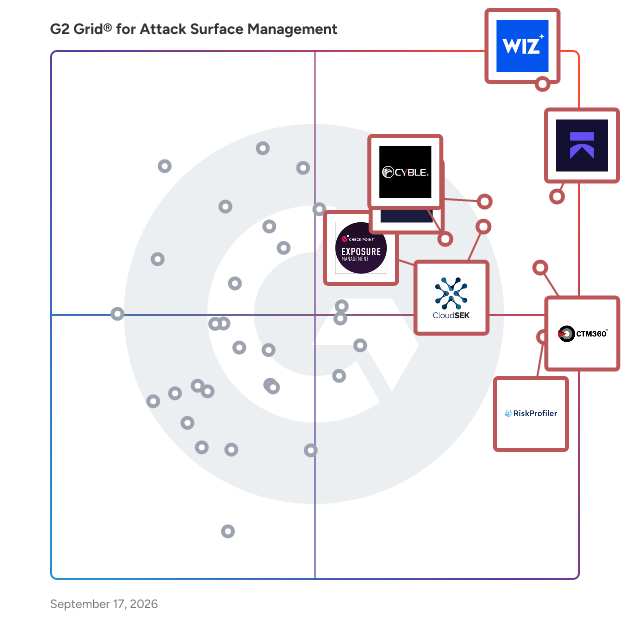
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

Pentera

Pentera is the category leader for Automated Security Validation, allowing every organization to test with ease the integrity of all cybersecurity layers, unfolding true, current security exposures at any moment, at any scale. Thousands of security professionals and service providers around the world use Pentera to guide remediation and close security gaps before they are exploited. Its customers include Casey's General Stores, Emeria, LuLu International Exchange, IP Telecom PT, BrewDog, City National Bank, Schmitz Cargobull, and MBC Group. Pentera is backed by leading investors such as K1 Investment Management, Insight Partners, Blackstone, Evolution Equity Partners, and AWZ. Visit https://pentera.io for more information.

Average Rating: 4.6/5.0

Total Reviews: 186

How Do G2 Users Rate Pentera?

  • Vulnerability Intelligence: 8.3/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 7.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 7.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Pentera?

  • Seller: Pentera
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Boston, MA
  • Twitter: @penterasec
    3,291 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    460 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Government Administration, Banking
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About Pentera?

AI-generated summary from verified user reviews

Pros
  • Users find Pentera's ease of use exceptional, thanks to its automation, customizable scenarios, and simple interface.
  • Users value the effective vulnerability scanning and remediation capabilities of Pentera, enhancing overall security posture.
  • Users value the automation capabilities of Pentera, enhancing their security testing and validation processes efficiently.
  • Users value the responsive customer support from Pentera, enhancing their experience and facilitating smooth operations.
  • Users value the realistic attack simulations offered by Pentera, enhancing their security posture through continuous validation.
Cons
  • Users find the reporting inadequate, suggesting it requires improvement for better enterprise-level insights.
  • Users express concern about the lack of a robust RBAC system, limiting proper access control and user rights management.
  • Users desire improvement in handling false positives, though overall satisfaction with Pentera remains high.
  • Users note the limited reporting capabilities of Pentera, especially for enterprise-level assessments and lacking Spanish translation.
  • Users are concerned about the missing features in Pentera, including updates on vulnerabilities and insufficient RBAC options.

What Are Recent G2 Reviews of Pentera?

DeCYFIR by CYFIRMA

DeCYFIR is an AI-powered preemptive External Threat Landscape Management platform engineered to help organizations predict and prevent cyberattacks before they occur. Adopting a hacker's perspective, it delivers early warnings, prioritized insights, and actionable intelligence across the full external threat landscape. Built on a proprietary 9-pillar architecture — spanning Attack Surface Discovery & Intelligence, Vulnerability Intelligence & Threat Prioritization, Brand & Online Exposure Management, Digital Risk & Identity Protection, Third Party Risk Management, Situational Awareness & Emerging Threats, Predictive Threat Intelligence, Threat Adaptive Awareness & Training, and Sector Tailored Deception Intelligence. DeCYFIR correlates signals across all pillars to cut through noise, surface what is truly critical, and empower security teams to stay decisively ahead of emerging threats.

Average Rating: 4.8/5.0

Total Reviews: 49

How Do G2 Users Rate DeCYFIR by CYFIRMA?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind DeCYFIR by CYFIRMA?

  • Seller: CYFIRMA
  • Year Founded: 2017
  • HQ Location: Singapore, SG
  • Twitter: @cyfirma
    1,002 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    135 employees on LinkedIn®
  • Phone: marketing@cyfirma.com

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 53% Medium, 24% Large

What Do G2 Reviewers Say About DeCYFIR by CYFIRMA?

AI-generated summary from verified user reviews

Pros
  • Users value the thorough threat detection capabilities of DeCYFIR, enhancing cybersecurity measures against potential attacks.
  • Users value the informative threat intelligence from DeCYFIR, aiding in proactive prevention of cyber incidents.
  • Users value DeCYFIR for its contextual and predictive intelligence, enhancing threat visibility and strategic risk management.
  • Users value DeCYFIR's comprehensive threat intelligence features, enhancing proactive defense against cyber threats effectively.
  • Users value the advanced security insights from DeCYFIR, enhancing their ability to prevent and respond to threats.
Cons
  • Users find DeCYFIR not user-friendly, citing a confusing UI and technical complexity for less experienced individuals.
  • Users find DeCYFIR's interface to be complex and overwhelming, particularly for those unfamiliar with threat intelligence workflows.
  • Users find DeCYFIR's learning curve daunting, as its complexity may overwhelm new users without proper training.
  • Users find the platform's limited customization options challenging, impacting their overall user experience.
  • Users find DeCYFIR's complex setup challenging, particularly for newcomers and those needing customized dashboards or API integration.

What Are Recent G2 Reviews of DeCYFIR by CYFIRMA?

Recorded Future

Recorded Future is the world’s largest threat intelligence company. Recorded Future’s Intelligence Cloud provides end-to-end intelligence across adversaries, infrastructure, and targets. Indexing the internet across the open web, dark web, and technical sources, Recorded Future provides real-time visibility into an expanding attack surface and threat landscape, empowering clients to act with speed and confidence to reduce risk and securely drive business forward. Headquartered in Boston with offices and employees around the world, Recorded Future works with over 1,900 businesses and government organizations across 80 countries to provide real-time, unbiased and actionable intelligence. Learn more at recordedfuture.com.

Average Rating: 4.5/5.0

Total Reviews: 234

How Do G2 Users Rate Recorded Future?

  • Vulnerability Intelligence: 8.6/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 7.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 7.6/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.5/10 (Category avg: 9.0/10)

Who Is the Company Behind Recorded Future?

  • Seller: Recorded Future
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Somerville, US
  • Twitter: @RecordedFuture
    107,965 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,150 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Cyber Threat Intelligence Analyst, Threat Intelligence Analyst
  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 64% Large, 21% Medium

What Do G2 Reviewers Say About Recorded Future?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Recorded Future, finding the interface intuitive and features beneficial for daily tasks.
  • Users enjoy the advanced customization features of Recorded Future, providing in-depth insights and alerts for cyber threats.
  • Users value the intelligent insights from Recorded Future, enhancing their understanding of critical data relationships effectively.
  • Users value the effective threat detection capabilities of Recorded Future, enabling prompt response to potential security risks.
  • Users value the actionable threat intelligence from Recorded Future, enhancing their vulnerability management and overall security posture.
Cons
  • Users find the navigation complex in Recorded Future, leading to difficulties in creating accurate queries and managing data.
  • Users often mention the high cost of Recorded Future, which can be challenging for teams with tight budgets.
  • Users find the learning curve steep, requiring significant time and effort to master the platform's features.
  • Users find difficult learning curves due to complexity and advanced settings, hindering team accessibility and efficiency.
  • Users express concern over inaccuracy issues in Recorded Future, affecting predictions and relevant alerts significantly.

What Are Recent G2 Reviews of Recorded Future?

What Are G2 Users Discussing About Recorded Future?

Scrut Automation

Scrut Automation is a leading compliance automation platform designed for fast-growing businesses looking to streamline security, risk, and compliance without disrupting operations. It centralizes compliance functions, automates evidence collection, and simplifies audits, helping security teams reduce compliance efforts. Scrut supports 70+ out-of-the-box frameworks, including SOC 2, ISO 27001, GDPR, HIPAA, and PCI-DSS, with the flexibility to add custom frameworks for unique regulatory needs. With 150+ integrations, Scrut seamlessly integrates into your security and IT ecosystem, automating compliance, eliminating manual work, and improving risk visibility. Join 2500+ industry leaders who trust Scrut for simplified compliance and risk management. Schedule a demo today.

Average Rating: 4.9/5.0

Total Reviews: 1,314

How Do G2 Users Rate Scrut Automation?

  • Vulnerability Intelligence: 9.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.5/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.5/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Scrut Automation?

  • Seller: Scrut Automation
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Palo Alto, US
  • Twitter: @scrutsocial
    120 Twitter followers
  • LinkedIn® Page: in.linkedin.com
    237 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO, CEO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 50% Small, 48% Medium

What Do G2 Reviewers Say About Scrut Automation?

AI-generated summary from verified user reviews

Pros
  • Users find Scrut Automation’s ease of use essential for tracking tasks and collaboration across teams effectively.
  • Users value the exceptional customer support from Scrut Automation, which enhances their experience and success in compliance.
  • Users highlight the exceptional support from Priyanshi and the Scrut team throughout their compliance journey.
  • Users highlight Scrut Automation's exceptional compliance management, simplifying SOC 2 processes with outstanding support and integrated services.
  • Users value the clarity in compliance documentation offered by Scrut Automation, aiding successful audits and implementation.
Cons
  • Users note the need for improvement in UI, documentation, and bug resolution, which complicates the overall experience.
  • Users face technical issues that can overwhelm non-technical team members and hinder platform usability.
  • Users note the missing features like auto-answerable security and limited customization options for reports in Scrut Automation.
  • Users express concerns over lack of clarity in test results and policy processes, complicating their experience with Scrut Automation.
  • Users find the learning curve steep, facing challenges in navigation and understanding the certification process in Scrut Automation.

What Are Recent G2 Reviews of Scrut Automation?

What Are G2 Users Discussing About Scrut Automation?

Microsoft Defender External Attack Surface Management

In this era of hybrid work, shadow IT creates an increasingly serious security risk. Defender EASM helps cloud security teams see unknown and unmanaged resources outside the firewall.

Average Rating: 4.3/5.0

Total Reviews: 17

How Do G2 Users Rate Microsoft Defender External Attack Surface Management?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Microsoft Defender External Attack Surface Management?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 35% Medium, 35% Small

What Are Recent G2 Reviews of Microsoft Defender External Attack Surface Management?

Sprocket Security

Sprocket Security — Technology-Powered. Human-Verified. Sprocket Security is a technology-powered continuous penetration testing platform that eliminates the blind spots left by annual testing. Traditional pentests give you a point-in-time snapshot and then leave you exposed for the other 345 days of the year — while your infrastructure keeps changing. Sprocket closes that gap by combining automation with US-based human pentesters who validate what actually matters, so your security posture is tested continuously, not once a quarter or once a year. Sprocket runs on the Continuous Lifecycle: Attack Surface Monitoring surfaces what you have exposed, Bleeding-Edge Testing puts expert pentesters against it using the latest attacker techniques, IT Change Detection automatically triggers new testing whenever your environment changes, and Notifications & Support push findings straight into the workflows your team already uses. When something changes, testing happens — no waiting for the next scheduled engagement. What makes Sprocket different -Continuous, not calendar-based. Testing is triggered by change, not by the calendar. No 345-day gaps between engagements. -Human-verified findings, not scanner noise. Automation does the heavy lifting; expert US-based pentesters validate real, exploitable risk so your team gets signal instead of a 200-page PDF to triage. -Continuous, not coin-operated. Unlimited retests are included. When you patch a finding, verify the fix at no additional cost — no per-retest fees, no surprise invoices for scope changes. -From finding to fixed, faster. Findings flow into your existing tools in real time, so remediation starts immediately instead of waiting on a report. -Compliance-ready, always. Generate on-demand reporting for SOC 2, ISO 27001, HIPAA, PCI-DSS, and more — built from live data, not a stale snapshot. Who it's for Sprocket is built for security and IT teams at growing organizations that need offensive security coverage without standing up a full internal red team. CISOs, Directors of Security, IT leaders, and compliance and risk owners rely on Sprocket to continuously validate their defenses, prove control effectiveness to auditors and the board, and stay ahead of an attack surface that never stops changing — with particularly strong fit for financial services, healthcare, SaaS, and other compliance-driven industries. Doing what Gartner now calls Continuous Offensive Security Testing since 2018, Sprocket gives you the coverage of a dedicated adversary and the visibility of an always-on platform — so you find your weaknesses before an attacker does.

Average Rating: 4.8/5.0

Total Reviews: 17

How Do G2 Users Rate Sprocket Security?

  • Vulnerability Intelligence: 9.6/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.2/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Sprocket Security?

Who Uses This Product?

  • Company Size: 71% Medium, 12% Large

What Do G2 Reviewers Say About Sprocket Security?

AI-generated summary from verified user reviews

Pros
  • Users commend Sprocket Security for their thorough pentesting efficiency, enhancing security and providing actionable remediation guidance.
  • Users praise the helpful customer support of Sprocket Security for being responsive and easy to communicate with.
  • Users find Sprocket Security's ease of use excellent, facilitated by a user-friendly interface and responsive support.
  • Users praise the expertise of Sprocket Security, noting their top-tier penetration testing and exceptional support for security goals.
  • Users value the effective remediation efficiency of Sprocket Security, enhancing their cybersecurity strategy through actionable insights.
Cons
  • Users experience false positives from Sprocket Security, complicating alert management and causing unnecessary notifications.
  • Users find Sprocket Security to be expensive, with steep renewal costs and inadequate support affecting timely resolutions.
  • Users experience limited support and communication, resulting in prolonged remediation and dissatisfaction with the contract process.
  • Users experience poor customer support with slow response times and inadequate communication following pentests and contract renewals.
  • Users struggle with poor integration, as Sprocket Security doesn't connect with existing security tools, causing alert confusion.

What Are Recent G2 Reviews of Sprocket Security?

ThreatMon

ThreatMon is an AI-powered end-to-end cyber risk intelligence platform designed to assist organizations in identifying, analyzing, prioritizing, and responding to external cyber risks within their digital ecosystems. This comprehensive solution caters to security operations, threat intelligence, risk management, and executive teams, offering continuous visibility into exposed assets, emerging threats, threat actors, compromised data, and third-party risks from a unified environment. As a robust cyber risk intelligence platform, ThreatMon combines various capabilities to provide organizations with a thorough understanding of their external exposure and the evolving threat landscape. By collecting and analyzing threat data, the platform supports proactive risk identification, enabling informed security decisions that are crucial in today’s complex digital environment. This proactive approach is essential for organizations aiming to stay ahead of potential cyber threats and vulnerabilities. Key features of ThreatMon include Attack Surface Intelligence, which allows users to discover and monitor internet-facing assets, exposures, and vulnerabilities. Additionally, the platform offers Cyber Threat Intelligence and Dark Web Intelligence, enabling organizations to track threat actors, emerging threats, leaked credentials, and compromised data. Fraud Intelligence capabilities help identify phishing attempts, brand impersonation, and other external fraud-related risks, while Supply Chain Risk Management focuses on monitoring cyber risks associated with vendors and third-party ecosystems. The AI-driven analysis, risk prioritization, dashboards, alerts, and reporting features empower teams to transform complex threat data into actionable intelligence. By integrating these capabilities, ThreatMon provides security teams with a consolidated view of external cyber risks, reducing reliance on fragmented tools and enhancing operational efficiency. Continuous monitoring and contextual intelligence facilitate the identification of relevant threats, the investigation of exposures, and the prioritization of risks based on their potential impact. Furthermore, ThreatMon aids technical security teams in effectively communicating risk information to decision-makers through structured insights, dashboards, and reporting. This comprehensive visibility across the digital environment supports risk-based decision-making and fosters a more proactive, intelligence-driven approach to cyber risk management.

Average Rating: 4.9/5.0

Total Reviews: 27

How Do G2 Users Rate ThreatMon?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.8/10 (Category avg: 9.0/10)

Who Is the Company Behind ThreatMon?

  • Seller: ThreatMon
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Sterling VA
  • Twitter: @MonThreat
    17,241 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    43 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 41% Large, 37% Medium

What Do G2 Reviewers Say About ThreatMon?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the real-time monitoring capabilities of ThreatMon, enabling proactive management of cybersecurity threats and vulnerabilities.
  • Users value the advanced threat detection capabilities of ThreatMon, offering actionable insights and early warnings.
  • Users find ThreatMon incredibly easy to use, streamlining configuration and management with user-friendly dashboards and reports.
  • Users commend the detailed analysis of ThreatMon, enabling proactive identification of vulnerabilities and informed threat prioritization.
  • Users value the reliable threat intelligence of ThreatMon, enhancing security through proactive threat detection and response.
Cons
  • Users find the excessive notifications from ThreatMon create unnecessary work and can be overwhelming initially.
  • Users find the threat data overwhelming, making it challenging to effectively manage and understand the Mobile Application Monitoring Module.
  • Users find the limited reporting features restrictive, desiring more customization and clarity for specific needs.
  • Users find the inefficient alerts from ThreatMon create unnecessary work and can be challenging to manage.
  • Users face challenges with the inefficient alert system, finding too many alerts create unnecessary work and confusion.

What Are Recent G2 Reviews of ThreatMon?

UpGuard Breach Risk

UpGuard Breach Risk is an AI-powered attack surface management solution that empowers lean security teams to see what attackers see and take control of their external risk. As part of the UpGuard Cyber Risk Posture Management (CRPM) platform, it integrates seamlessly with Vendor Risk and User Risk to provide a unified defense against modern cyber threats. As organizations scale, their digital footprint expands beyond the firewall, creating dangerous blind spots. Traditional tools often miss these external signals, leaving teams vulnerable to shadow IT, exposed credentials, and brand abuse. Breach Risk solves this by combining Attack Surface Management (ASM), Digital Risk Protection (DRP), and advanced Threat Monitoring into a single, automated platform. Key Capabilities: • Continuous Attack Surface Discovery: You can’t protect what you can’t see. Breach Risk continuously maps your internet-facing assets like domains, IPs, and cloud resources, to uncover shadow IT and misconfigurations. We automatically inventory your digital footprint to close the gaps that attackers exploit, ensuring no asset goes unmonitored. • AI-Powered Threat Monitoring: Move beyond static feeds. Our Threat Monitoring engine scans the open, deep, and dark web to detect leaked employee credentials, infostealer logs, and malware signals before they are weaponized. Unlike traditional threat intelligence that floods you with raw data, our AI Threat Analyst triages signals to filter out noise and prioritize high-fidelity threats for immediate action. • Brand Protection & Disinformation Defense: Safeguard your reputation against fraud. We proactively detect lookalike domains (typosquatting) and fraudulent social media profiles used to launch phishing attacks and disinformation campaigns. Our integrated workflows help you identify and neutralize these impersonation attempts before they erode customer trust. • Actionable Remediation: We don’t just find problems; we help you fix them. Breach Risk provides guided remediation plans and integrates with your security tech stack, allowing lean teams to accelerate response times without adding headcount. By translating complex technical risks into a quantifiable Cyber Risk Score, UpGuard enables security leaders to benchmark performance, justify budget, and prove risk reduction to the board.

Average Rating: 4.5/5.0

Total Reviews: 27

How Do G2 Users Rate UpGuard Breach Risk?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.7/10 (Category avg: 9.2/10)
  • Ease of Admin: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind UpGuard Breach Risk?

  • Seller: UpGuard
  • Company Website:
  • Year Founded: 2012
  • HQ Location: Mountain View, California
  • Twitter: @UpGuard
    8,705 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    402 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 59% Large, 37% Medium

What Are Recent G2 Reviews of UpGuard Breach Risk?

Saner CVEM

Prevention-first Vulnerability and Exposure Management for unified visibility, prioritization, compliance, and remediation Saner Continuous Vulnerability and Exposure Management unifies asset exposure, posture anomaly detection, vulnerability assessment, compliance management, risk prioritization, patching, and endpoint actions in one dashboard. Saner CVEM is built to help teams continuously detect, assess, prioritize, and remediate vulnerabilities and other security risks from a unified console Why Choose Saner CVEM? • Unified dashboard with interactive views across visibility, detection, prioritization, and remediation for a single source of truth • Complete asset visibility across endpoint and non-endpoint devices, operating system applications, third-party applications, and lifecycle changes • Continuous risk discovery with rapid scans, daily-updated risk intelligence, and posture anomaly detection that helps surface outliers and misconfigurations faster • Context-driven prioritization with SSVC categories such as Act, Attend, Track, and Track* so teams can focus on the risks that deserve action first. • Continuous compliance management with built-in templates, customizable profiles, daily checks, and deviation tracking across common frameworks. • Integrated patching and remediation with vulnerability-to-patch mapping, automated deployment workflows, and endpoint actions from the same ecosystem. • Machine-learning-assisted analysis to identify deeper risk patterns, detect unusual posture, and support smarter remediation decisions. • Customizable, audit-ready reporting for security, IT, and compliance teams that need clearer evidence and easier tracking. • Flexible deployment on cloud or on-premises, with remediation support across Windows, Linux, macOS, and AIX environments.

Average Rating: 4.5/5.0

Total Reviews: 72

How Do G2 Users Rate Saner CVEM?

  • Vulnerability Intelligence: 9.5/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.0/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Saner CVEM?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • Twitter: @secpod
    542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Small, 38% Medium

What Do G2 Reviewers Say About Saner CVEM?

AI-generated summary from verified user reviews

Pros
  • Users value the automatic security updates from Saner CVEM, ensuring timely compliance for remote workforce systems.
  • Users appreciate the advanced automation features of Saner CVEM, streamlining security patch management for remote systems.
  • Users value the seamless integrations of Saner CVEM, enhancing operational efficiency and strengthening digital security across IT processes.
  • Users value the automated compliance management of Saner CVEM, enhancing efficiency and reducing manual intervention significantly.
  • Users highlight the exceptional customer support from Saner CVEM, enhancing security and helping organizations stay protected.
Cons
  • Users often face integration issues with Saner CVEM, leading to frustrations during setup and ongoing maintenance.
  • Users note limited features in Saner CVEM, especially in multi-tenant support and integration capabilities, impacting efficiency.
  • Users experience slow performance when loading large data sets and during initial setup, affecting usability.
  • Users experience slow scanning, especially with initial dashboard load times and large data sets affecting daily checks.
  • Users find the limited cloud integration challenging, requiring workarounds and custom scripts for effective use.

What Are Recent G2 Reviews of Saner CVEM?

What Are G2 Users Discussing About Saner CVEM?

Armis

Armis is THE cyber exposure management and security solution designed to help organizations protect their entire attack surface and manage cyber risk exposure in real time. In an era where traditional perimeter defenses are becoming increasingly ineffective, Armis provides a comprehensive approach to cybersecurity that enables organizations to continuously monitor, secure, and manage all critical assets, whether on-premises or in the cloud. Armis' target audience includes a wide range of organizations, from Fortune 100, 200, and 500 companies to national governments and local entities. These organizations face unique challenges in safeguarding their critical infrastructure and sensitive data against evolving cyber threats. Armis is particularly beneficial for industries that rely heavily on connected devices and IoT (Internet of Things) technologies, as it offers visibility and protection across diverse environments. This capability is essential for organizations aiming to maintain operational continuity and protect their reputations in a landscape where cyber incidents can have far-reaching consequences. Key features of Armis include real-time visibility into all connected devices, automated risk assessment, and continuous monitoring of network activity. The platform uses advanced machine learning algorithms to detect anomalies and potential threats, allowing organizations to respond swiftly to emerging risks. Additionally, Armis seamlessly integrates with existing security tools, enhancing security posture without disrupting current workflows. This interoperability is crucial for organizations looking to strengthen their defenses without overhauling their entire security infrastructure. The benefits of using Armis extend beyond mere compliance; they encompass a proactive approach to cybersecurity that empowers organizations to anticipate and mitigate risks before they escalate into significant incidents. By providing a unified view of the attack surface, Armis enables security teams to prioritize their efforts and allocate resources effectively. This strategic focus not only enhances security measures, but also fosters a culture of cybersecurity awareness throughout the organization, ultimately contributing to a more resilient operational framework. In summary, Armis stands out in the cybersecurity landscape by offering a holistic solution that addresses the complexities of modern threats. Its ability to provide real-time insights and automate risk management processes makes it an invaluable tool for organizations striving to protect their critical assets and maintain a secure environment in an increasingly interconnected world.

Average Rating: 4.3/5.0

Total Reviews: 19

How Do G2 Users Rate Armis?

  • Vulnerability Intelligence: 8.1/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 7.3/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 3.7/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Armis?

  • Seller: ServiceNow
  • Company Website:
  • Year Founded: 2004
  • HQ Location: Santa Clara, CA
  • Twitter: @servicenow
    55,548 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    35,078 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Hospital & Health Care
  • Company Size: 53% Large, 26% Small

What Do G2 Reviewers Say About Armis?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the intuitive interface of Armis, which makes accessing insights and managing tasks effortless.
  • Users value Armis for its effective asset management, providing clear insights and risk assessments in real-time.
  • Users appreciate Armis for its intuitive and user-friendly interface, making it easy to manage system risks and insights.
  • Users value the deep visibility Armis offers, providing comprehensive insights and context into their network environments.
  • Users praise the responsive customer support of Armis, enhancing their overall experience and problem-solving capabilities.
Cons
  • Users report integration issues with Armis, making it challenging to configure for reliable information.
  • Users find the additional costs for add-on modules to be quite high, impacting overall satisfaction with Armis.
  • Users find the complex setup challenging, requiring effort to configure integrations and additional modules that are expensive.
  • Users find the difficult setup of Armis frustrating, though integrations work well once configured.
  • Users experience excessive notifications from Armis, finding the initial alert noise overwhelming and requiring further integration.

What Are Recent G2 Reviews of Armis?

What Are G2 Users Discussing About Armis?

Detectify

Detectify sets a new standard for advanced application security testing, challenging traditional DAST by providing evolving coverage of each and every exposed asset across the changing attack surface. AppSec teams trust Detectify to expose how attackers will exploit their Internet-facing applications. The Detectify platform automates continuous real-world, payload-based attacks fuelled by its global community of elite ethical hackers into its own expert-built engines, exposing critical weaknesses before it's too late. The Detectify solution includes: - Automated discovery of known and unknown digital assets via domain & cloud connectors - Continuous coverage (24/7) of every corner of the attack surface with dynamic testing. Not just predefined targets - 100% payload-based testing fuelled by elite ethical hackers for a high signal-to-noise ratio - Distributed coverage across an unmatched array of relevant technologies - Actionable remediation tips for software development teams - Team functionality to easily share reports - Powerful integrations platform to prioritize and triage vulnerability findings onward to development teams -Advanced API functionality -Capabilities to set custom attack surface security policies

Average Rating: 4.5/5.0

Total Reviews: 49

How Do G2 Users Rate Detectify?

  • Vulnerability Intelligence: 9.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.4/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Detectify?

  • Seller: Detectify
  • Year Founded: 2013
  • HQ Location: Stockholm, Sweden
  • Twitter: @detectify
    11,256 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    96 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Small, 35% Medium

What Do G2 Reviewers Say About Detectify?

AI-generated summary from verified user reviews

Pros
  • Users praise Detectify for its automation capabilities, making security testing seamless and adaptable to existing workflows.
  • Users appreciate Detectify's automation testing capabilities, making security assessments easier and more efficient to manage.
  • Users appreciate the customizability of Detectify, enjoying its easy integration and tailored security testing options.
  • Users praise Detectify for its easy integration and comprehensive dynamic application security testing, enhancing security without complex setups.
  • Users value Detectify for its effective dynamic application security testing and seamless integration into existing workflows.
Cons
  • Users find the initial setup complex, which can create challenges in getting started with Detectify.
  • Users struggle with the complex queries in Detectify, which hinder understanding of the spidering outcomes and assessments.
  • Users find the complex setup of Detectify challenging, making initial use more difficult than expected.
  • Users find Detectify expensive when testing multiple sites, affecting its accessibility for wider use.
  • Users face inaccuracies in Detectify's spidering results, leading to uncertainty in thorough application assessments.

What Are Recent G2 Reviews of Detectify?

What Are G2 Users Discussing About Detectify?

Heimdal

Accommodate all your cybersecurity needs under one convenient roof with the Heimdal® Unified Cybersecurity Platform. Our cybersecurity solutions can be used as standalone products or integrated into one another as part of a cohesive and unified XDR platform. Whether you’re a reseller, distributor, MSSP, or an organization committed to bolstering your online security, we provide an array of cutting-edge products to make your mission smoother. Heimdal® is a fast-growing cybersecurity company focused on continuous technological innovation. Since its establishment in 2014 in Copenhagen, based on the winning idea of CTF World Champions, Heimdal has experienced spectacular growth by proactively building products that anticipate threatscape trends. The company offers a multi-layeredand unified security suite that combines threat prevention, patch and asset management, endpoint rights management, antivirus and mail security which together secure customers against cyberattacks and keep critical information and intellectual property safe. Heimdal has been recognized as a thought leader in the industry and has won multiple international awards both for its solutions and for its educational content creation. The Heimdal line of products currently consists of 10 products and 2 services. The former category encompasses DNS Security for Endpoints & Network, Patch & Asset Management, Privileged Access Management, Application Control, Next-Gen Endpoint Antivirus, Ransomware Encryption Protection, Email Security, Email Fraud Prevention, and Remote Desktop. The latter is represented by Endpoint Detection & Response, as well as eXtended Detection & Response, or EDR and XDR for short. Currently, Heimdal’s cybersecurity solutions are deployed in more than 45 countries and supported regionally from offices in 15+ countries, by 175+ highly qualified specialists. Heimdal is ISAE 3000 certified and secures more than 2 million endpoints for over 10,000 companies. The company supports its partners without concessions on the basis of predictability and scalability. The common goal is to create a sustainable ecosystem and a strategic partnership.

Average Rating: 4.4/5.0

Total Reviews: 80

How Do G2 Users Rate Heimdal?

  • Ease of Admin: 8.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Heimdal?

  • Seller: Heimdal®
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • Twitter: @HeimdalSecurity
    5,086 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Construction
  • Company Size: 56% Medium, 30% Small

What Do G2 Reviewers Say About Heimdal?

AI-generated summary from verified user reviews

Pros
  • Users praise the easy setup of Heimdal, appreciating its straightforward installation and quick integration with their systems.
  • Users find that file transfer with Heimdal is seamless and reliable, enhancing overall productivity and ease of use.
  • Users commend Heimdal for its exceptional issue resolution support, providing quick and professional solutions exceeding expectations.
  • Users value the reliable patch management of Heimdal, delivering consistent performance without issues during monthly updates.
  • Users value the reliable security and user-friendly interface of Heimdal, enhancing overall satisfaction and support.
Cons
  • Users find the complex interface of Heimdal difficult to navigate, complicating their overall experience and functionality.
  • Users find the admin portal complex and illogical, making navigation frustrating and cumbersome for essential tasks.
  • Users find the customer support lacking during initial setup, which causes issues with product deployment and upgrades.
  • Users find the poor interface design of Heimdal difficult to navigate, complicating essential tasks and access.
  • Users experience restart issues with Heimdal, feeling unprotected after scans until the software is rebooted.

What Are Recent G2 Reviews of Heimdal?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

How Do G2 Users Rate Edgescan?

  • Vulnerability Intelligence: 9.4/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.3/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 6.7/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.8/10 (Category avg: 9.0/10)

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • Twitter: @edgescan
    2,256 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    90 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, highlighting its intuitive interface and straightforward navigation.
  • Users value the automated vulnerability detection features of Edgescan for efficient risk assessment and remediation support.
  • Users value the excellent customer support from Edgescan, noting their responsiveness and proactivity in addressing queries.
  • Users value the detailed vulnerability identification from Edgescan, enabling effective risk management and threat mitigation strategies.
  • Users value Edgescan for its intuitive interface and comprehensive functionality that streamlines security assessments and support.
Cons
  • Users find the complex UI of Edgescan challenging, often requiring guidance to navigate key functions effectively.
  • Users find limited customization options frustrating, particularly with filtering systems and administrative functionalities.
  • Users find the poor interface design of Edgescan challenging, causing navigation and task completion difficulties.
  • Users experience slow performance with Edgescan as manual reviews lead to longer scan completion times.
  • Users find the user interface challenging and unintuitive, leading to difficulties in navigation and task completion.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?

AI-Native Continuous Offensive Security Platform

RidgeBot by Ridge Security is a leading agentic AI-driven offensive security platform, supporting continuous threat management programs. It enables CISOs to minimize cyber risks by continuously validating the cybersecurity posture and controls protecting attack surfaces against increasingly sophisticated and frequent attacks. RidgeBot automatically tests an organization’s entire IP-based environment, including network infrastructure, applications, websites, IoT, and OT, using ethical hacking techniques to pinpoint the most critical vulnerabilities. It's dynamic AI-powered decision-making supports DevSecOps, compliance, incident response verification, and custom attack simulations. RidgeBot maintains a library of over 36,000 plugins to launch complex penetration tests and attack simulations, with detailed reporting of results and remediation recommendations.

Average Rating: 4.5/5.0

Total Reviews: 98

How Do G2 Users Rate AI-Native Continuous Offensive Security Platform?

  • Vulnerability Intelligence: 8.9/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.6/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.5/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.1/10 (Category avg: 9.0/10)

Who Is the Company Behind AI-Native Continuous Offensive Security Platform?

  • Seller: Ridge Security Technology
  • Company Website:
  • Year Founded: 2020
  • HQ Location: Santa Clara, California
  • Twitter: @RidgeSecurityAI
    1,291 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    49 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Small, 45% Medium

What Do G2 Reviewers Say About AI-Native Continuous Offensive Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users praise the automation capabilities of RidgeBot, streamlining penetration testing and providing accurate vulnerability assessments efficiently.
  • Users appreciate the ease of use of the AI-Native Continuous Offensive Security Platform for streamlined penetration testing.
  • Users commend the pentesting efficiency of RidgeBot, automating tests and validating vulnerabilities seamlessly to save time.
  • Users appreciate the automated vulnerability identification of RidgeBot, which effectively validates risks and streamlines security processes.
  • Users value the efficiency of RidgeBot, as it automates testing to save time and enhance security processes.
Cons
  • Users find RidgeBot's setup to be complex and challenging, particularly in customized or legacy system environments.
  • Users find the complex setup challenging, especially due to limited documentation and support for new admins.
  • Users find the missing features such as improved API testing and customizable reporting templates quite limiting.
  • Users find the poor customer support challenging, as documentation is often lacking for troubleshooting issues.
  • Users find the poor documentation challenging, making initial setup and onboarding confusing for new admins.

What Are Recent G2 Reviews of AI-Native Continuous Offensive Security Platform?

Rankiteo

Rankiteo's Monitoring product offers a comprehensive cybersecurity monitoring solution designed to enhance an organization's digital defense mechanisms. This service provides real-time insights into potential vulnerabilities and threats, enabling businesses to proactively manage and mitigate cyber risks. By leveraging advanced technologies, Rankiteo ensures that organizations can maintain a robust security posture without the need for additional agents or workloads. Key Features and Functionality: - Security Ratings: Evaluate security strengths across ten risk factors to identify and address potential weaknesses. - Cyber Risk Quantification: Translate cyber risks into financial terms, facilitating informed decision-making. - Exploit Prediction: Utilize data-driven models to estimate the likelihood of vulnerability exploitation. - Vulnerability Prioritizer: Determine which vulnerabilities require immediate attention to optimize mitigation efforts. - Threat and Risk Intelligence: Access data-driven insights for proactive cybersecurity risk management. - Attack Surface Intelligence: Obtain on-demand, contextualized global threat intelligence to understand and manage exposure. - Automatic Vendor Detection: Identify and manage third and fourth-party vendors to enhance risk control. - SBOM (Supply Chain): Improve supply chain transparency and security with detailed software inventories. - Cyber Insurance Prediction: Predict cyber risks and tailor coverage for robust cybersecurity protection. - Malware Simulation: Simulate malware scenarios to predict risks and strengthen cybersecurity defenses. Primary Value and Problem Solved: Rankiteo's Monitoring product addresses the critical need for continuous and proactive cybersecurity oversight. By offering real-time monitoring and comprehensive risk assessments, it empowers organizations to identify and mitigate potential threats before they escalate. This proactive approach not only enhances security but also supports compliance with industry standards and regulations. Additionally, the solution's affordability makes enterprise-grade cybersecurity intelligence accessible to small and mid-sized businesses, democratizing access to essential security tools. By focusing on sectors like healthcare and frontline services, Rankiteo ensures that organizations can protect sensitive data and maintain trust without incurring exorbitant costs.

Average Rating: 4.7/5.0

Total Reviews: 37

How Do G2 Users Rate Rankiteo?

  • Vulnerability Intelligence: 8.9/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.4/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind Rankiteo?

  • Seller: Rankiteo
  • Year Founded: 2022
  • HQ Location: London, GB
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Marketing and Advertising
  • Company Size: 68% Medium, 16% Large

What Do G2 Reviewers Say About Rankiteo?

AI-generated summary from verified user reviews

Pros
  • Users value the easy-to-use interface of Rankiteo, which enhances workflow and prioritizes critical security issues effortlessly.
  • Users value the clear risk assessments of Rankiteo, enabling effective prioritization and enhanced security visibility.
  • Users commend the excellent customer support of Rankiteo, enhancing their ability to secure and track server safety efficiently.
  • Users value the actionable intelligence of Rankiteo, simplifying security management and guiding improvement efforts effectively.
  • Users commend the user-friendly security testing of Rankiteo, enabling effective server protection without extensive resources.
Cons
  • Users find the pricing on the higher side, which may deter budget-conscious organizations from considering Rankiteo.
  • Users face integration issues with internal systems, requiring manual effort and experiencing sluggishness with large data sets.
  • Users find the limited features of Rankiteo challenging, especially as several are still in beta testing.
  • Users find the complex setup of Rankiteo challenging, especially for smaller organizations lacking dedicated support.
  • Users find the lack of integration limits functionality, requiring manual workarounds for niche tool connections.

What Are Recent G2 Reviews of Rankiteo?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026