Best Intrusion Detection and Prevention Systems (IDPS)

How Many Intrusion Detection and Prevention Systems (IDPS) Products Does G2 Track?

Total Products under this Category: 76

Category Stats (Oct 2026)

  • Average Rating: 4.4/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+0.43%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: October 11, 2026

How Does G2 Rank Intrusion Detection and Prevention Systems (IDPS) Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,700+ Authentic Reviews
  • 76+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

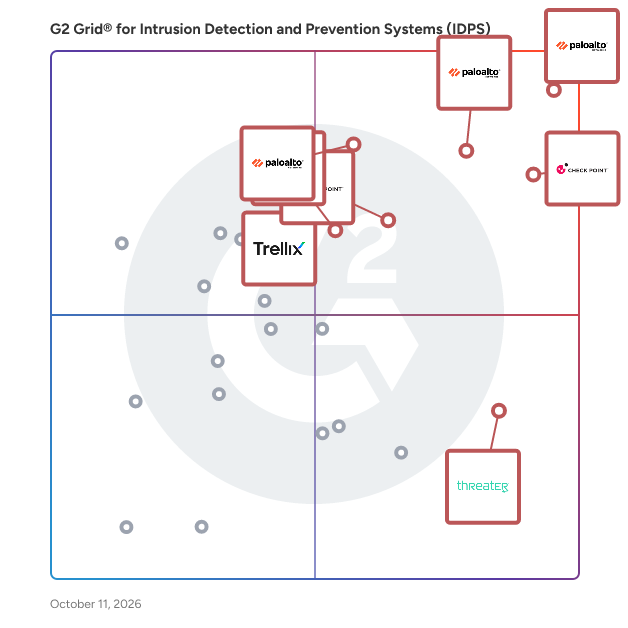
G2 Grid® for Intrusion Detection and Prevention Systems (IDPS)

G2 Grid® for Intrusion Detection and Prevention Systems (IDPS) plotting products by satisfaction and market presence

Highlighted products: Palo Alto Networks Next-Generation Firewalls, Check Point Quantum Intrusion Prevention System (IPS), Palo Alto Networks VM-Series Virtual Firewall, Cloud-Delivered Security Services, Check Point Infinity Platform, Trellix Network Detection and Response (NDR), FortiGate IPS, and threatER.

Underlying data: [Grid® JSON](https://www.g2.com/categories/intrusion-detection-and-prevention-systems-idps/grids.json?focus%5B%5D=palo-alto-networks-next-generation-firewalls&focus%5B%5D=check-point-quantum-intrusion-prevention-system-ips&focus%5B%5D=palo-alto-networks-vm-series-virtual-firewall&focus%5B%5D=cloud-delivered-security-services&focus%5B%5D=check-point-infinity-platform&focus%5B%5D=trellix-network-detection-and-response-ndr&focus%5B%5D=fortigate-ips&focus%5B%5D=threater)

Palo Alto Networks Next-Generation Firewalls

Our next-generation firewall classifies all traffic, including encrypted traffic, based on application, application function, user and content. You can create comprehensive, precise security policies, resulting in safe enablement of applications. This lets only authorized users run sanctioned applications, greatly reducing the surgace area of cyber attacks across the organization.

Average Rating: 4.5/5.0

Total Reviews: 167

How Do G2 Users Rate Palo Alto Networks Next-Generation Firewalls?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Security hardening: 9.0/10 (Category avg: 8.9/10)
  • Compliance: 8.8/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Palo Alto Networks Next-Generation Firewalls?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Who Uses This: Network Engineer, Network Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Medium, 38% Large

What Do G2 Reviewers Say About Palo Alto Networks Next-Generation Firewalls?

AI-generated summary from verified user reviews

Pros
  • Users commend the efficiency of Palo Alto firewalls, excelling in advanced threat detection and application-level traffic inspection.
  • Users appreciate the ease of use of Palo Alto Networks, benefiting from a smooth, intuitive interface and navigation.
  • Users value the advanced threat prevention of Palo Alto Networks Firewalls, enhancing visibility and control over security.
  • Users value the reliable performance and extensive features of Palo Alto Networks Next-Generation Firewalls, enhancing security management.
  • Users value the robust control and visibility provided by Palo Alto Networks Next-Generation Firewalls for enhanced security.
Cons
  • Users find the high cost of Palo Alto Networks Firewalls to be a significant barrier for small businesses.
  • Users find the difficult learning curve of Palo Alto Networks Next-Generation Firewalls challenging, especially for new administrators.
  • Users experience slow performance due to high security settings and complex configurations, impacting efficiency on lower-end systems.
  • Users face a complex configuration challenge, especially if unfamiliar with the Palo Alto ecosystem, complicating overall management.
  • Users find the poor interface design frustrating, as it's not intuitive and feels overwhelming for navigation.

What Are Recent G2 Reviews of Palo Alto Networks Next-Generation Firewalls?

What Are G2 Users Discussing About Palo Alto Networks Next-Generation Firewalls?

Check Point Quantum Intrusion Prevention System (IPS)

Check Point's Quantum Intrusion Prevention System (IPS) is a comprehensive security solution designed to detect and prevent attempts to exploit vulnerabilities in systems and applications. Integrated within Check Point's Next Generation Firewall, it offers automatic updates to safeguard organizations against both longstanding and emerging threats. By combining signature-based detection, protocol validation, anomaly detection, and behavioral analysis, Quantum IPS delivers robust protection against a wide array of cyber threats. Key Features and Functionality: - Comprehensive Threat Detection: Identifies and mitigates specific known exploits, vulnerabilities (both known and unknown), protocol misuse, tunneling attempts indicating data leakage, and outbound malware communications. - Real-Time Protection Updates: Continuously updated with new defenses against emerging threats, including preemptive protections that address vulnerabilities before they are exploited. - Virtual Patching: Provides a proactive approach to security by offering robust IPS functionality that complements traditional patching strategies, ensuring networks remain secure between updates. - Efficient Deployment: Features predefined recommended profiles for immediate use, customizable signature activation rules tailored to network assets, and an optional detect-only mode for evaluation purposes. - 360° Visibility and Reporting: Seamlessly integrates with SmartEvent, enabling Security Operations Center (SOC) staff to prioritize and respond to critical events efficiently. Primary Value and User Benefits: Quantum IPS addresses the critical need for proactive and comprehensive network security by offering real-time threat prevention and automatic updates. Its integration with Check Point's security gateways ensures a unified security approach, reducing the total cost of ownership. The system's low false positive rate and efficient deployment options save valuable time for IT staff, while its robust protection mechanisms safeguard organizations against a wide spectrum of cyber threats, ensuring business continuity and data integrity.

Average Rating: 4.4/5.0

Total Reviews: 59

How Do G2 Users Rate Check Point Quantum Intrusion Prevention System (IPS)?

  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.0/10)
  • Security hardening: 8.6/10 (Category avg: 8.9/10)
  • Compliance: 9.0/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Check Point Quantum Intrusion Prevention System (IPS)?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 46% Medium, 41% Large

What Are Recent G2 Reviews of Check Point Quantum Intrusion Prevention System (IPS)?

What Are G2 Users Discussing About Check Point Quantum Intrusion Prevention System (IPS)?

Palo Alto Networks VM-Series Virtual Firewall

Palo Alto Networks' VM-Series Virtual Firewall is the industry’s leading cloud security software, delivering the world’s most effective network security to any cloud or virtualized environment. It is a virtualized form factor of Palo Alto Networks' next-generation firewalls, built to protect your applications from zero-day threats, providing consistent security and easy deployment across all clouds and virtualized environments, including technologies from Amazon Web Services, Microsoft Azure, Google Cloud, VMware, Cisco, KVM, Nutanix, OpenStack, and more.

Average Rating: 4.3/5.0

Total Reviews: 92

How Do G2 Users Rate Palo Alto Networks VM-Series Virtual Firewall?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.0/10)
  • Security hardening: 9.1/10 (Category avg: 8.9/10)
  • Compliance: 9.0/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Palo Alto Networks VM-Series Virtual Firewall?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 43% Large, 30% Medium

What Do G2 Reviewers Say About Palo Alto Networks VM-Series Virtual Firewall?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the low false-positive rates and comprehensive features of Palo Alto Networks VM-Series, enhancing their security experience.
  • Users value the advanced threat protection of Palo Alto Networks VM-Series, ensuring security across hybrid and multi-cloud environments.
  • Users appreciate the strong security features of the VM-Series, enhancing protection against threats in diverse environments.
  • Users value the consistent security provided by Palo Alto's VM-Series, ensuring strong protection across on-premises and cloud environments.
  • Users value the deployment ease of Palo Alto Networks VM-Series, enjoying seamless integration and intuitive configuration processes.
Cons
  • Users find the high cost of Palo Alto VM-Series a barrier, limiting its adoption among budget-sensitive clients.
  • Users find the difficult learning curve of Palo Alto Networks VM-Series Virtual Firewall challenging, often needing extensive training to utilize effectively.
  • Users find the setup and configuration complex, particularly for newcomers, complicating management and increasing costs.
  • Users experience slow performance during heavy traffic, impacting efficiency and responsiveness of the Palo Alto Networks VM-Series Virtual Firewall.
  • Users find the setup and management process complex, particularly challenging for teams unfamiliar with the Palo Alto ecosystem.

What Are Recent G2 Reviews of Palo Alto Networks VM-Series Virtual Firewall?

What Are G2 Users Discussing About Palo Alto Networks VM-Series Virtual Firewall?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Cloud-Delivered Security Services

Overview Our Cloud-Delivered Security Services are natively integrated, offering consistent best-in-class protection everywhere. Backed by our world-renowned Unit 42® Threat Research team, this one-of-a-kind protection uses the network effect of 70,000+ global customers to share intelligence across all threat vectors to stop known, unknown and zero-day threats 180X faster than any other platform or point solution and prevent patient zero. What are Cloud-Delivered Security Services? A comprehensive suite of natively-integrated security services delivered from the cloud that provide protection for a customer’s entire network, securing all users, applications, devices, and data, regardless of the location. Our security services are powered by Precision AI™ and analyze real network traffic inline and stop threats in real time, including phishing, malware, command and control, ransomware, DNS-layered threats, and much more. These services include: Advanced Threat Prevention, the industry’s leading intrusion prevention system that addresses known and unknown command-and-control attacks from red team tools, as well as injection attacks and vulnerability exploits. Advanced WildFire, the industry’s largest malware analysis engine that stops the first instance of known, unknown and highly-evasive malware. Advanced URL Filtering, the industry’s first web security engine to stop unknown phishing attacks in real time. Advanced DNS Security, the industry’s most comprehensive DNS security solution that offers over 2x more threat coverage than the next leading security vendor and is also the industry’s first solution to stop network-based DNS hijacking attacks in real time. IoT/OT Security, the industry’s most comprehensive zero trust solution for IoT devices, helping you see and secure all connected devices in your network. NG-CASB, our SaaS application and data security solution that allows you to discover and control all of the SaaS consumption in your network. AI Access Security, our solution that ensures safe use of GenAI apps with access control, data protection and real-time visibility of over 600 applications, so that your employees can securely use AI to increase their productivity. With the power of AI and a robust global cloud infrastructure, Palo Alto Networks Cloud-Delivered Security Services can scale to stay ahead of today's threats and keep up with your organization's network security needs.

Average Rating: 4.4/5.0

Total Reviews: 101

How Do G2 Users Rate Cloud-Delivered Security Services?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Security hardening: 8.3/10 (Category avg: 8.9/10)
  • Compliance: 8.7/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind Cloud-Delivered Security Services?

  • Seller: Palo Alto Networks
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Who Uses This: Network Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Medium, 34% Large

What Are Recent G2 Reviews of Cloud-Delivered Security Services?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Security hardening: 9.1/10 (Category avg: 8.9/10)
  • Compliance: 8.7/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

Trellix Network Detection and Response (NDR)

Trellix Network Detection and Response (NDR) converts passive network monitoring into proactive defense. It inspects all hybrid cloud traffic—north-south and east-west—to eliminate blind spots, uncover unmanaged devices, and detect lateral threat movement. Central to its capability is Trellix Wise, a built-in generative AI engine that automates complex forensics, triage, and threat investigations. Wise leverages specialized AI agents to turn cryptic telemetry into plain-language narratives, draft automated remediation steps, and prioritize high-fidelity alerts. This reduces Mean Time to Detect and Respond (MTTD/MTTR) by 50%. Trellix NDR runs advanced machine learning and Trellix Wise workflows locally in air-gapped environments. It also delivers "Active NDR" via native Intrusion Prevention System (IPS) engines to actively block threats at line rate. Correlating endpoints and email data, it stops adversaries before damage is done.

Average Rating: 4.1/5.0

Total Reviews: 77

How Do G2 Users Rate Trellix Network Detection and Response (NDR)?

  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.0/10)
  • Security hardening: 8.4/10 (Category avg: 8.9/10)
  • Compliance: 8.2/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Trellix Network Detection and Response (NDR)?

  • Seller: Trellix
  • Company Website:
  • Year Founded: 2004
  • HQ Location: Plano, TX
  • Twitter: @Trellix
    241,168 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,811 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 41% Medium, 30% Small

What Are Recent G2 Reviews of Trellix Network Detection and Response (NDR)?

What Are G2 Users Discussing About Trellix Network Detection and Response (NDR)?

FortiGate IPS

Whether part of a firewall solution or a separate standalone appliance, Intrusion Prevention Systems (IPS) technology is becoming an increasingly ubiquitous part of network security defenses.

Average Rating: 4.7/5.0

Total Reviews: 13

How Do G2 Users Rate FortiGate IPS?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Security hardening: 9.7/10 (Category avg: 8.9/10)
  • Compliance: 9.3/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.4/10 (Category avg: 9.1/10)

Who Is the Company Behind FortiGate IPS?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • Twitter: @Fortinet
    151,422 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT

Who Uses This Product?

  • Company Size: 47% Medium, 40% Large

What Are Recent G2 Reviews of FortiGate IPS?

What Are G2 Users Discussing About FortiGate IPS?

threatER

threatER is the leading preemptive cybersecurity platform for building and maintaining trust at scale. Our SaaS solution continuously learns from all available data, allowing you to gain better insights and extract more value from your security stack. threatER transforms your security stack into a smart, adaptive and automated prevention engine. With threatER you reduce risk, get more value from your security investments and reinforce trust across every connection without slowing down your business. Learn more at www.threater.com.

Average Rating: 4.8/5.0

Total Reviews: 36

How Do G2 Users Rate threatER?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.0/10)
  • Security hardening: 9.4/10 (Category avg: 8.9/10)
  • Compliance: 9.2/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.7/10 (Category avg: 9.1/10)

Who Is the Company Behind threatER?

  • Seller: threatER
  • Company Website:
  • HQ Location: Tysons, Virginia
  • LinkedIn® Page: www.linkedin.com
    26 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About threatER?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of threatER, appreciating its straightforward setup and minimal administration requirements.
  • Users praise the performance efficiency of threatER, highlighting its seamless integration and effective threat management capabilities.
  • Users value the strong security measures of threatER, which effectively block malicious sites and reduce threats.
  • Users find the setup ease of threatER excellent, with straightforward installation and minimal administration required.
  • Users value the effective threat protection of threatER, significantly reducing malicious traffic with dynamic updates and geo blocking.
Cons
  • Users experience performance issues with slow report pulling and cumbersome log management processes that affect efficiency.
  • Users face compatibility issues as threatER is limited to specific platforms and lacks some essential features.
  • Users face issues with false positives, as legitimate sites are incorrectly blocked, needing manual resolution.
  • Users find the overzealous blocking of legitimate IPs frustrating, suggesting improvements for easier domain allow/block management.
  • Users face access issues as centralized searching of logs is not available through the SaaS portal.

What Are Recent G2 Reviews of threatER?

TrendAI Vision One - Cloud Security

In today's complex digital landscape, securing your cloud environment is paramount. The management and security of your hybrid and multi-cloud setup pose increasing challenges. TrendAI's Cloud Security provides essential visibility, allowing you and your teams to secure every aspect of your transformation and eliminate disruptive security silos. Automate security policies, deployments, monitoring, and compliance audits seamlessly from a single console, ensuring the automatic protection of all workloads from both known and unknown threats. With Cloud-Native Application Protection and robust platform capabilities, TrendAI empowers you to proactively address vulnerabilities and defend against threats. Gain centralized visibility, continuous asset discovery, and contextualized risk assessments, equipping your team with everything necessary to stay ahead of potential cloud security risks.

Average Rating: 4.5/5.0

Total Reviews: 181

How Do G2 Users Rate TrendAI Vision One - Cloud Security?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.0/10)
  • Security hardening: 8.8/10 (Category avg: 8.9/10)
  • Compliance: 8.6/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind TrendAI Vision One - Cloud Security?

  • Seller: TrendAI
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY
  • Total Revenue (USD mm): $1,515

Who Uses This Product?

  • Who Uses This: Cyber Security Associate, Cyber Security Engineer
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 43% Medium, 34% Large

What Do G2 Reviewers Say About TrendAI Vision One - Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized management of TrendAI Vision One, simplifying security configuration and threat monitoring from one platform.
  • Users value the robust security connectivity of TrendAI Vision One, ensuring comprehensive protection across various cloud platforms.
  • Users value the unified visibility in Hybrid Cloud Security, facilitating effective management of hybrid environments and compliance.
  • Users value the comprehensive coverage of both on-premise and cloud security offered by TrendAI Vision One.
  • Users appreciate the comprehensive security of TrendAI Vision One, enabling seamless threat monitoring across cloud and on-premises environments.
Cons
  • Users find the complexity of TrendAI Vision One challenging, requiring expert handling and increasing misconfiguration risks.
  • Users find the complex setup of TrendAI Vision One challenging, requiring significant time and expertise to configure properly.
  • Users find feature complexity frustrating, as it requires technical expertise and complicates initial setup and integration.
  • Users find the learning curve steep, making it challenging for beginners to navigate and configure TrendAI Vision One.
  • Users find TrendAI Vision One's learning curve difficult, often requiring expert knowledge for effective implementation and management.

What Are Recent G2 Reviews of TrendAI Vision One - Cloud Security?

What Are G2 Users Discussing About TrendAI Vision One - Cloud Security?

ExtraHop

ExtraHop is the cybersecurity partner enterprises trust to reveal cyber risk and build business resilience. The ExtraHop RevealX platform for network detection and response and network performance management uniquely delivers the instant visibility and unparalleled decryption capabilities organizations need to expose the cyber risks and performance issues that other tools can’t see. When organizations have full network transparency with ExtraHop, they can investigate smarter, stop threats faster, and keep operations running. RevealX deploys on premises or in the cloud. It addresses the following use cases: - Ransomware - Zero trust - Software supply chain attacks - Lateral movement and C2 communication - Security hygiene - Network and Application Performance Management - IDS - Forensics and more A few of our differentiators: Continuous and on-demand PCAP: Full packet processing is superior to NetFlow and yields higher quality detections. Strategic decryption across a variety of protocols, including SSL/TLS, MS-RPC, WinRM, and SMBv3, gives you better visibility into early-stage threats hiding in encrypted traffic as they attempt to move laterally across your network. Protocol coverage: RevealX decodes more than 70 network protocols. Cloud-scale machine learning: Rather than relying on limited "on-box" compute power for analysis and detections, RevealX uses sophisticated cloud-hosted and cloud-scale machine learning workloads to identify suspicious behavior in real time and create high-fidelity alerts. ExtraHop was named a Leader in The Forrester Wave™: Network Analysis and Visibility, Q2 2023. Key Technology Integration and Go-to-Market Partners: CrowdStrike: RevealX integrates with CrowdStrike Falcon® LogScale, Falcon Insight XDR, Falcon Threat Graph, and Falcon Intelligence. Splunk SOAR AWS Google Cloud Security Founded in 2007, ExtraHop is privately held and headquartered in Seattle, Wash. To learn more, visit www.extrahop.com.

Average Rating: 4.6/5.0

Total Reviews: 68

How Do G2 Users Rate ExtraHop?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Security hardening: 8.8/10 (Category avg: 8.9/10)
  • Compliance: 7.6/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind ExtraHop?

  • Seller: ExtraHop Networks
  • Year Founded: 2007
  • HQ Location: Seattle, Washington
  • Twitter: @ExtraHop
    10,695 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    774 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Hospital & Health Care, Transportation/Trucking/Railroad
  • Company Size: 69% Large, 26% Medium

What Do G2 Reviewers Say About ExtraHop?

AI-generated summary from verified user reviews

Pros
  • Users value the all-in-one monitoring solution of ExtraHop, appreciating its comprehensive visibility and insightful analysis of network traffic.
  • Users value the comprehensive monitoring capabilities of ExtraHop, enhancing network visibility and analysis effectively.
  • Users appreciate the easy deployment of ExtraHop, benefiting from seamless installation on both physical and virtual networks.
  • Users value the responsive support from ExtraHop's knowledgeable Customer Success teams, enhancing their overall experience and satisfaction.

What Are Recent G2 Reviews of ExtraHop?

What Are G2 Users Discussing About ExtraHop?

Cisco Secure Firewall Threat Defense Virtual (formerly NGFWv)

Cisco Secure Firewall Threat Defense Virtual (formerly FTDv/NGFWv) is a comprehensive security solution designed to protect virtualized environments across private and public clouds. It integrates Cisco's proven network firewall capabilities with advanced threat defense features, including Snort Intrusion Prevention System (IPS), URL filtering, and malware defense. This virtualized firewall ensures consistent security policies and deep visibility into network traffic, enabling organizations to detect and mitigate threats before they impact operations. Key Features and Functionality: - Advanced Threat Defense: Combines network firewall with Snort IPS, URL filtering, and malware defense to protect against known and emerging threats. - Consistent Security Policies: Maintains uniform security policies across physical, private, and public cloud environments, ensuring seamless protection as workloads move. - Deep Network Visibility: Provides comprehensive insights into network traffic, allowing for quick detection of threat origins and activities. - Automated Risk Ranking: Prioritizes threats with automated risk rankings and impact flags, enabling efficient resource allocation to critical events. - License Portability: Offers flexibility to move from on-premises private clouds to public clouds while maintaining consistent policies and unified management. - Centralized Management: Utilizes Cisco Smart Software Licensing for easy deployment, management, and tracking of virtual firewall instances. Primary Value and User Solutions: Cisco Secure Firewall Threat Defense Virtual addresses the need for robust security in dynamic, virtualized environments. By providing consistent security policies and deep visibility across various cloud platforms, it simplifies threat protection and management. Organizations benefit from automated threat prioritization, flexible deployment options, and centralized control, ensuring efficient and effective defense against a wide range of cyber threats. This solution is particularly valuable for businesses undergoing data center consolidation, office relocations, mergers, acquisitions, or experiencing fluctuating application demands, as it offers the agility and scalability required to adapt to changing security needs.

Average Rating: 4.2/5.0

Total Reviews: 89

How Do G2 Users Rate Cisco Secure Firewall Threat Defense Virtual (formerly NGFWv)?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Security hardening: 8.9/10 (Category avg: 8.9/10)
  • Compliance: 8.8/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.2/10 (Category avg: 9.1/10)

Who Is the Company Behind Cisco Secure Firewall Threat Defense Virtual (formerly NGFWv)?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • Twitter: @Cisco
    720,366 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO

Who Uses This Product?

  • Top Industries: Information Technology and Services, Telecommunications
  • Company Size: 45% Medium, 42% Large

What Do G2 Reviewers Say About Cisco Secure Firewall Threat Defense Virtual (formerly NGFWv)?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the simplified management that allows for easy policy and rule management from a single console.
  • Users value the simplified management offered by Cisco Secure Firewall, allowing centralized control of policies and rules.
  • Users appreciate the efficiency of Cisco Secure Firewall in managing hybrid infrastructure seamlessly.
  • Users appreciate the convenience of Cisco Firepower virtual firewalls for managing hybrid infrastructure effectively.
Cons
  • Users find the SNMP configuration too complex, leading to issues like broken HA after upgrades.
  • Users find the SNMP configuration overly complex, leading to challenges and issues during upgrades.
  • Users highlight the management complexity of Cisco Secure Firewall, requiring additional tools that may not justify the cost.
  • Users face dependency issues due to the need for dedicated management tools, increasing costs for fewer firewalls.
  • Users find the difficult management of Cisco Secure Firewall due to the need for dedicated central management, adding costs.

What Are Recent G2 Reviews of Cisco Secure Firewall Threat Defense Virtual (formerly NGFWv)?

What Are G2 Users Discussing About Cisco Secure Firewall Threat Defense Virtual (formerly NGFWv)?

Trend Micro TippingPoint

Trend Micro TippingPoint integrates with the Deep Discovery Advanced Threat Protection Solution to detect and block targeted attacks and malware through preemptive threat prevention, threat insight and prioritization, and real-time enforcement and remediation.

Average Rating: 4.1/5.0

Total Reviews: 25

How Do G2 Users Rate Trend Micro TippingPoint?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Security hardening: 9.7/10 (Category avg: 8.9/10)
  • Compliance: 8.8/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.3/10 (Category avg: 9.1/10)

Who Is the Company Behind Trend Micro TippingPoint?

  • Seller: TrendAI
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY
  • Total Revenue (USD mm): $1,515

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 38% Small, 31% Medium

What Are Recent G2 Reviews of Trend Micro TippingPoint?

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Security hardening: 9.0/10 (Category avg: 8.9/10)
  • Compliance: 8.9/10 (Category avg: 8.8/10)
  • Security Monitoring: 9.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • Twitter: @blumira
    1 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the easy setup of Blumira Automated Detection & Response, enabling quick integration and efficient use.
  • Users appreciate the responsive customer support of Blumira, finding it reliable and personal for their IT needs.
  • Users praise the setup ease of Blumira, appreciating its quick integration and automated alert features.
  • Users appreciate the reliable real-time alerting of Blumira, valuing its clarity and ease of use for all techs.
  • Users value the reliable real-time alerting of Blumira, appreciating its ease of use and helpful implementation.
Cons
  • Users find limited customization with detection filters, relying on support for creating necessary custom detections.
  • Users express concern over false positives that can disrupt business functions and lead to frustration with repeated alerts.
  • Users find Blumira's pricing expensive, citing inflexible models and insufficient features in lower tiers.
  • Users express frustration over false positives that waste time and complicate the overall experience with Blumira.
  • Users express concern over insufficient information, desiring better data accessibility and clearer deployment status.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

Trend Micro Deep Discovery

Deep Discovery Inspector is available as a physical or virtual network appliance. It's designed to quickly detect advanced malware that typically bypasses traditional security defenses and exfiltrates sensitive data. Specialized detection engines and custom sandbox analysis detect and prevent breaches.

Average Rating: 4.3/5.0

Total Reviews: 16

How Do G2 Users Rate Trend Micro Deep Discovery?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Security hardening: 8.5/10 (Category avg: 8.9/10)
  • Compliance: 9.0/10 (Category avg: 8.8/10)
  • Security Monitoring: 8.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Trend Micro Deep Discovery?

  • Seller: TrendAI
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY
  • Total Revenue (USD mm): $1,515

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 41% Medium, 35% Large

What Are Recent G2 Reviews of Trend Micro Deep Discovery?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 47

How Do G2 Users Rate Darktrace / HYBRID NETWORK?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.0/10)
  • Security hardening: 10.0/10 (Category avg: 8.9/10)
  • Compliance: 10.0/10 (Category avg: 8.8/10)
  • Security Monitoring: 10.0/10 (Category avg: 9.1/10)

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • Twitter: @Darktrace
    18,177 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 31% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the excellent monitoring capabilities of Darktrace, offering impressive visibility and efficient network analysis.
  • Users appreciate the self-learning AI technology of Darktrace/Network, effectively adapting to threats without extensive configuration.
  • Users commend Darktrace's rapid threat detection, ensuring robust security with minimal manual intervention for maximum efficiency.
  • Users commend the responsive customer support of Darktrace/Network, enhancing learning and facilitating efficient troubleshooting.
  • Users highlight the autonomous AI-driven cybersecurity of Darktrace, which effectively detects and responds to threats in real time.
Cons
  • Users report a significant learning curve with Darktrace as the AI generates numerous alerts during initial setup.
  • Users note that the product can be expensive, particularly for smaller organizations with constrained budgets and significant training costs.
  • Users experience alert issues with Darktrace, needing extensive manual tuning to manage false positives during the learning phase.
  • Users find the complex setup of Darktrace challenging, requiring skilled teams for effective management and configuration.
  • Users experience false positives occasionally, requiring IT support to resolve issues affecting network connectivity.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024