Best Enterprise Endpoint Detection & Response (EDR) Software - Page 2

How Many Endpoint Detection & Response (EDR) Software Products Does G2 Track?

Total Products under this Category: 130

Category Stats (Oct 2026)

  • Average Rating: 4.43/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CrowdStrike Falcon Endpoint Protection Platform (+0.82%) - Among all products in this category, CrowdStrike Falcon Endpoint Protection Platform recorded the largest rating increase compared to last month

Last updated: October 01, 2026

How Does G2 Rank Endpoint Detection & Response (EDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 12,900+ Authentic Reviews
  • 130+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

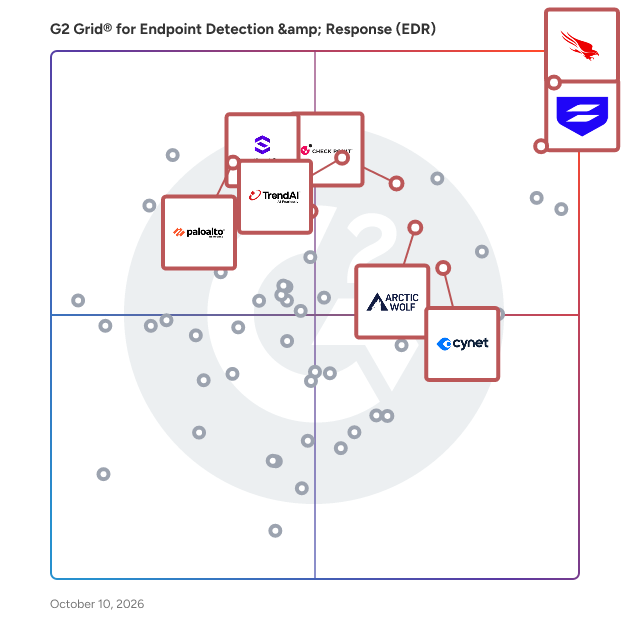
G2 Grid® for Endpoint Detection & Response (EDR) Software

G2 Grid® for Endpoint Detection & Response (EDR) Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, TrendAI Vision One, SentinelOne Singularity Endpoint, Arctic Wolf, Cynet, Cortex XDR, and Check Point Endpoint Security.

Underlying data: [Grid® JSON](https://www.g2.com/categories/endpoint-detection-response-edr/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=trendai-vision-one&focus%5B%5D=sentinelone-singularity-endpoint&focus%5B%5D=arctic-wolf&focus%5B%5D=cynet&focus%5B%5D=palo-alto-networks-cortex-xdr&focus%5B%5D=check-point-endpoint-security&segment=enterprise)

ESET PROTECT

ESET PROTECT is an AI-native cybersecurity platform that combines next-generation prevention, detection, and response capabilities with AI-powered security technologies and 24/7 managed detection and response (MDR) services delivered by ESET security experts. A single, unified management console provides centralized visibility across security operations, helping organizations automate repetitive tasks and enabling security teams to focus on higher-priority activities. With exceptional detection accuracy and fewer false positives, the platform helps reduce alert noise and identify real threats faster. Designed to help organizations stay ahead of known and emerging threats, ESET PROTECT strengthens cyber resilience, improves operational efficiency, and supports compliance initiatives. Why Organizations Choose ESET PROTECT Reduce Security Burden with Expert-Led Protection Fill cybersecurity skill gaps with 24/7 managed detection and response (MDR) backed by ESET experts. Gain faster incident response, actionable threat intelligence, and access to a team of experienced threat hunters. Secure AI Workflows Without Slowing Innovation Adopt AI confidently while protecting your organization from emerging AI-related threats. Secure AI conversations from malicious responses and risky prompts, protect against AI agent attacks, and detect suspicious AI agent behavior. Confidence in Cybersecurity with ESET AI Technologies Benefit from AI-powered technologies built specifically for cybersecurity. ESET helps security teams prevent threats earlier, prioritize and respond faster, improve threat detection, reduce noise, and protect people, devices, data, and businesses across multiple perimeters. Strengthen Compliance Readiness Navigate growing compliance demands with confidence. Our endpoint protection solutions help you assess risk, automate compliance processes, and demonstrate adherence to regulatory, customer, and industry requirements. Support compliance with NIS2, DORA, GDPR, ISO 27001, and more through continuous monitoring, automated evidence collection, and actionable recommendations to strengthen your security and compliance posture.

Average Rating: 4.6/5.0

Total Reviews: 961

How Do G2 Users Rate ESET PROTECT?

  • Ease of Admin: 8.5/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.0/10)
  • Quality of Support: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.7/10)

Who Is the Company Behind ESET PROTECT?

  • Seller: ESET
  • Company Website:
  • Year Founded: 1992
  • HQ Location: Bratislava, Slovak Republic
  • Twitter: @ESET
    275,702 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,014 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Network Administrator
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Medium, 45% Small

What Do G2 Reviewers Say About ESET PROTECT?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the straightforward installation of ESET PROTECT, making it easy for anyone to get started.
  • Users commend ESET PROTECT for its robust ransomware protection, ensuring comprehensive security across multiple endpoints.
  • Users commend the reliability of ESET PROTECT, especially its strong protection against ransomware across multiple platforms.
  • Users value the great security of ESET PROTECT, ensuring computer safety with minimal impact on performance.
  • Users value the centralized management of ESET PROTECT, enabling effortless device oversight and enhanced threat detection.
Cons
  • Users find a learning curve with ESET PROTECT, as some features are complex and require expensive licenses.
  • Users find the difficult configuration process of ESET PROTECT time-consuming and sometimes overly complex for setup and management.
  • Users find the dashboard not user-friendly, citing excessive clicks for accessing necessary data and managing settings.
  • Users report a lack of clarity in policy management and task handling, complicating effective security oversight.
  • Users find difficult navigation in ESET PROTECT, requiring advanced skills and patience during implementation and setup.

What Are Recent G2 Reviews of ESET PROTECT?

What Are G2 Users Discussing About ESET PROTECT?

Iru

Iru is an AI-powered IT and security platform designed to help organizations secure their users, applications, and devices in an increasingly complex digital landscape. Tailored for the AI era, Iru integrates identity and access management, endpoint security, and compliance automation into a single cohesive solution. This unification streamlines operations, allowing IT and security teams to regain control and allocate their time more effectively. Targeted at fast-growing companies, Iru addresses the challenges faced by IT and security professionals who often juggle multiple tools and systems. The platform is particularly beneficial for organizations that require robust security measures while maintaining agility and efficiency. Use cases include managing user access across various applications, ensuring device security, and automating compliance processes, all of which are critical in today’s fast-paced business environment. At the heart of Iru is the Iru Context Model, which provides a dynamic overview of the organization’s environment by continuously monitoring users, devices, and applications in real-time. Complementing this model is Iru AI, an intelligent layer that transforms live data signals into actionable insights, orchestrates necessary actions, and maintains a comprehensive audit trail. This integration enhances policy enforcement, automates response mechanisms, and simplifies compliance, making it easier for organizations to adhere to regulatory requirements. One of Iru's standout features is its single endpoint agent, which manages and secures every device within an organization’s fleet. By implementing passwordless access through device-bound passkeys linked to device posture, Iru creates a trust fabric that strengthens security between users and devices. Additionally, compliance is continuously monitored with customized controls and an Adaptive Evidence Map that updates automatically, reducing the burden on IT teams and minimizing the risk of oversight. Iru aims to bring clarity and control back to overwhelmed IT and security teams by consolidating disparate tools into one unified platform. This shift allows teams to transition from reactive firefighting to proactive strategic initiatives that drive business success. The result is a more robust security posture, simplified workflows, and outcomes that align with organizational goals, ultimately fostering a safer and more efficient operational environment.

Average Rating: 4.7/5.0

Total Reviews: 863

How Do G2 Users Rate Iru?

  • Ease of Admin: 9.4/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.0/10)
  • Quality of Support: 9.5/10 (Category avg: 8.7/10)
  • Ease of Use: 9.4/10 (Category avg: 8.7/10)

Who Is the Company Behind Iru?

  • Seller: Iru
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Miami, FL
  • Twitter: @officiallyiru
    2,021 Twitter followers
  • LinkedIn® Page: linkedin.com
    400 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, CTO
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 70% Medium, 25% Small

What Do G2 Reviewers Say About Iru?

AI-generated summary from verified user reviews

Pros
  • Users praise Iru for its ease of use, appreciating the user-friendly interface and helpful customer support.
  • Users praise the exceptional customer support of Iru, highlighting dedicated assistance that goes above and beyond.
  • Users praise the user-friendly device management of Iru, simplifying their experience and enhancing security for Apple devices.
  • Users praise the easy setup of Iru, highlighting effective blueprints and supportive customer assistance during onboarding.
  • Users value the reliable platform of Iru for easy and effective Apple device management, ensuring security and efficiency.
Cons
  • Users desire more advanced features like enhanced EDR capabilities and better reporting options for improved functionality.
  • Users note a lack of features in Iru that necessitates workarounds and limits overall functionality, especially in urgent situations.
  • Users face challenges with device management limitations, particularly for non-Apple devices, complicating the overall process.
  • Users are frustrated with the limited compatibility of Iru, restricting its use to Mac OS devices only.
  • Users find the pricing steep for smaller teams, making budget management a challenge with licensing requirements.

What Are Recent G2 Reviews of Iru?

What Are G2 Users Discussing About Iru?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 104

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Ease of Admin: 8.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.5/10 (Category avg: 9.0/10)
  • Quality of Support: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.7/10 (Category avg: 8.7/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • Twitter: @PaloAltoNtwks
    128,951 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 35% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users value the best-in-class log management of Palo Alto Cortex XSIAM, benefiting from its effective alerting and integration features.
  • Users find the user-friendly dashboard of Palo Alto Cortex XSIAM essential for monitoring and understanding alerts effectively.
  • Users value the real-time monitoring capabilities of Palo Alto Cortex XSIAM, enhancing threat detection and response efficiency.
  • Users value the simple and user-friendly interface of Palo Alto Cortex XSIAM, making monitoring effortless.
  • Users value the good dashboard creation tools in Palo Alto Cortex XSIAM, enhancing ease of use and implementation.
Cons
  • Users note that Palo Alto Cortex XSIAM requires significant resources, impacting implementation time and increasing infrastructure costs.
  • Users find the complexity of implementation for Palo Alto Cortex XSIAM to be time-consuming and resource-intensive.
  • Users find the cost of Palo Alto Cortex XSIAM to be high, especially for smaller businesses.
  • Users face dashboard issues with XSIAM, finding it difficult to monitor assets and navigate the interface.
  • Users face difficult setup issues with Palo Alto Cortex XSIAM, requiring expertise and extensive time for initial implementation.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Carbon Black EDR

Carbon Black EDR is a market-leading incident response and threat hunting solution designed to provide responders with the most information possible, accompanied by expert threat analysis and armed with real-time response capabilities to stop attacks, minimize damage and close security gaps. Carbon Black EDR makes these teams more efficient, reducing investigations from days to hours, and more effective, enabling them to discover threats before attacks can exploit them. Carbon Black EDR also allows teams to connect to and isolate infected machines to prevent lateral movement and remediate devices without costly IT involvement. Continuous and Centralized Recording Centralized access to continuously recorded endpoint data means that security professionals have the information they need to hunt threats in real time as well as conduct in-depth investigations after a breach has occurred. Live Response for Remote Remediation With Live Response, incident responders can create a secure connection to infected hosts to pull or push files, kill processes, perform memory dumps and quickly remediate from anywhere in the world. Attack Chain Visualization and Search Carbon Black EDR provides intuitive attack chain visualization to make identifying root cause fast and easy. Analysts can quickly jump through each stage of an attack to gain insight into the attacker’s behavior, close security gaps and learn from every new attack technique to avoid falling victim to the same attack twice. Automation via Integrations and Open APIs Carbon Black boasts a robust partner ecosystem and open platform that allows security teams to integrate products like Carbon Black EDR into their existing security stack.

Average Rating: 4.4/5.0

Total Reviews: 83

How Do G2 Users Rate Carbon Black EDR?

  • Ease of Admin: 7.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.0/10)
  • Quality of Support: 8.6/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 8.7/10)

Who Is the Company Behind Carbon Black EDR?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • Twitter: @broadcom
    63,909 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 63% Medium, 41% Large

What Do G2 Reviewers Say About Carbon Black EDR?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of Carbon Black EDR, enhancing security and incident response capabilities.
  • Users value the rapid incident response capabilities of Carbon Black EDR, enhancing their ability to detect and react to threats.
  • Users value the real-time threat detection of Carbon Black EDR, enhancing security through continuous monitoring and behavioral analysis.
  • Users rave about the next-gen antivirus protection that effectively analyzes behaviors to combat advanced threats.
  • Users rave about the AI-powered behavior analysis of Carbon Black EDR, ensuring robust protection against various cyber threats.
Cons
  • Users find the pricing steep, especially after the company's acquisition, impacting overall value perception.
  • Users report high resource usage of Carbon Black EDR, impacting performance and requiring powerful machines for optimal operation.
  • Users are frustrated by the overwhelming alerts that hinder efficient use and increase resource demands.
  • Users experience a high rate of false positives with Carbon Black EDR, necessitating careful tuning to avoid fatigue.
  • Users experience inefficient search functionality in Carbon Black EDR, making it challenging to quickly find necessary information.

What Are Recent G2 Reviews of Carbon Black EDR?

What Are G2 Users Discussing About Carbon Black EDR?

Carbon Black Cloud

The Carbon Black Cloud security platform helps you strengthen and unify security tools to see more and stop more. Carbon Black unifies visibility across your endpoints, networks, and containers to enable you to stop threats targeting your organization with speed and confidence. Carbon Black protects against the full spectrum of modern cyber-attacks, including emerging threats and ransomware. Top SOC teams, IR firms and MSSPs have adopted Carbon Black as a core component of their prevention, detection, and response capability stack. Carbon Black is available via MSSP or directly.

Average Rating: 4.1/5.0

Total Reviews: 38

How Do G2 Users Rate Carbon Black Cloud?

  • Ease of Admin: 8.1/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Quality of Support: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.7/10)

Who Is the Company Behind Carbon Black Cloud?

  • Seller: Broadcom
  • Year Founded: 1991
  • HQ Location: San Jose, CA
  • Twitter: @broadcom
    63,909 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    44,602 employees on LinkedIn®
  • Ownership: NASDAQ: CA

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 56% Medium, 33% Large

What Do G2 Reviewers Say About Carbon Black Cloud?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Carbon Black Cloud, highlighting its intuitive interface and manageable block/whitelist features.
  • Users appreciate the easy installation and robust protection offered by Carbon Black Cloud for their digital infrastructure.
  • Users value the robust security features of Carbon Black Cloud, ensuring comprehensive protection for their digital infrastructure.
  • Users value the advanced antivirus protection of Carbon Black Cloud, ensuring 24/7 security against various threats.
  • Users appreciate the advanced AI-powered security of Carbon Black Cloud, providing affordable 24/7 protection effortlessly.
Cons
  • Users report agent removal issues with VMware Carbon Black Cloud, causing disruptions during critical tasks like exams.
  • Users face significant compatibility issues as the tool needs extensive customization and lacks integration with Microsoft OS.
  • Users find complex implementation challenging, particularly in creating global blocks and whitelists without individual policy updates.
  • Users face complex installation issues with VMware Carbon Black Cloud, leading to interruptions during critical tasks like exams.
  • Users find it challenging to manage configuration issues, especially when needing global blocks or whitelists.

What Are Recent G2 Reviews of Carbon Black Cloud?

What Are G2 Users Discussing About Carbon Black Cloud?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 187

How Do G2 Users Rate Intezer?

  • Ease of Admin: 8.8/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.0/10)
  • Quality of Support: 8.6/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 8.7/10)

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Year Founded: 2015
  • HQ Location: New York
  • Twitter: @IntezerLabs
    10,170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 23% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the robust security features of Intezer, ensuring timely detection and blocking of malware.
  • Users value the effective malware detection and security features of Intezer that enhance system protection.
  • Users value Intezer for its effective malware detection and response capabilities, enhancing overall security and incident management.
  • Users value the high detection accuracy of Intezer, ensuring timely malware detection and enhanced system security.
  • Users appreciate the ease of use of Intezer, making malware detection and incident response straightforward and efficient.
Cons
  • Users feel the inability to control file visibility limits their privacy and management options in certain situations.
  • Users report complex interface issues with Intezer, making navigation challenging and less intuitive.
  • Users are concerned about limited file visibility control, which may impact their data privacy and access management.
  • Users find the difficult navigation of Intezer frustrating, with a less-than-ideal UI and small text affecting readability.
  • Users find the expensive pricing of Intezer problematic, especially with the limited free tier and some GUI issues.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated