Top Free Endpoint Detection & Response (EDR) Software

How Many Endpoint Detection & Response (EDR) Software Products Does G2 Track?

Total Products under this Category: 129

Category Stats (Sep 2026)

  • Average Rating: 4.43/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CrowdStrike Falcon Endpoint Protection Platform (+0.82%) - Among all products in this category, CrowdStrike Falcon Endpoint Protection Platform recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Endpoint Detection & Response (EDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 12,900+ Authentic Reviews
  • 129+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

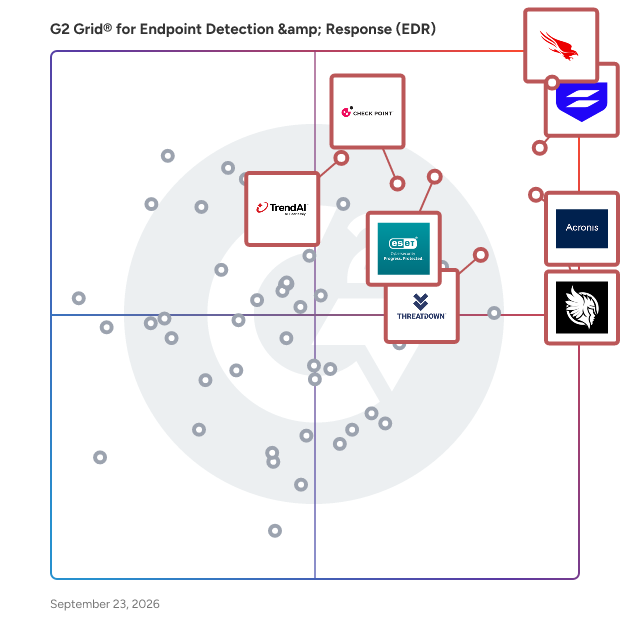
G2 Grid® for Endpoint Detection & Response (EDR) Software

G2 Grid® for Endpoint Detection & Response (EDR) Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, Acronis Cyber Protect Cloud, Huntress Managed EDR, ESET PROTECT, ThreatDown, Check Point Endpoint Security, and TrendAI Vision One.

Underlying data: [Grid® JSON](https://www.g2.com/categories/endpoint-detection-response-edr/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=acronis-cyber-protect-cloud&focus%5B%5D=huntress-managed-edr&focus%5B%5D=eset-protect&focus%5B%5D=threatdown&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=trendai-vision-one)

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 544

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Ease of Admin: 8.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Quality of Support: 9.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 8.7/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • Twitter: @CrowdStrike
    110,809 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Analyst, Security Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Large, 40% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the lightweight performance and powerful threat detection of CrowdStrike Falcon, enhancing security without slowing down systems.
  • Users commend the effective threat detection capabilities of CrowdStrike Falcon, ensuring robust security without system slowdowns.
  • Users appreciate the ease of use of CrowdStrike Falcon, benefiting from its lightweight impact and efficient incident management.
  • Users appreciate the advanced real-time threat protection of CrowdStrike Falcon, ensuring efficient security without system performance issues.
  • Users praise the exceptional threat detection of CrowdStrike Falcon, noting its effectiveness against both known and unknown threats.
Cons
  • Users find the cost prohibitive for smaller organizations, especially with additional modules increasing overall expenses.
  • Users find the complexity of the user interface and additional costs challenging, complicating their overall experience.
  • Users face a steep learning curve with CrowdStrike’s query language, making transitions from other platforms challenging.
  • Users find the limited features challenging, especially concerning cost and technical accessibility for smaller businesses.
  • Users find that pricing can be a barrier for smaller organizations, complicating access to advanced features.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Huntress Managed EDR

Huntress Managed EDR is a fully managed endpoint detection and response (EDR) solution that pairs continuous endpoint monitoring with a 24/7, human-staffed Security Operations Center (SOC). Built for managed service providers (MSPs) and small to mid-sized businesses (SMBs) with limited in-house security staff, it monitors Windows, macOS, and Linux endpoints for malicious behavior, including ransomware, persistent footholds, and lateral movement, and pairs automated detection with expert threat hunters who validate and respond to incidents in real time. Huntress Managed EDR reduces attacker dwell time through rapid threat containment and remediation, giving lean IT and security teams enterprise-grade endpoint protection without the overhead of building an internal SOC.

Average Rating: 4.8/5.0

Total Reviews: 897

How Do G2 Users Rate Huntress Managed EDR?

  • Ease of Admin: 9.6/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.0/10)
  • Quality of Support: 9.7/10 (Category avg: 8.7/10)
  • Ease of Use: 9.5/10 (Category avg: 8.7/10)

Who Is the Company Behind Huntress Managed EDR?

  • Seller: Huntress Labs
  • Company Website:
  • Year Founded: 2015
  • HQ Location: Ellicott City, US
  • Twitter: @HuntressLabs
    40,338 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    978 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 78% Small, 17% Medium

What Do G2 Reviewers Say About Huntress Managed EDR?

AI-generated summary from verified user reviews

Pros
  • Users praise the exceptional customer support from Huntress, ensuring smooth transitions and effective issue resolution for MSPs.
  • Users find Huntress Managed EDR incredibly easy to implement, ensuring a smooth transition and outstanding support throughout.
  • Users value the real-time threat detection of Huntress, enhancing security and minimizing false positives for effective response.
  • Users value the continuous monitoring of Huntress Managed EDR, ensuring swift threat identification and endpoint protection.
  • Users value the easy deployment of Huntress Managed EDR, simplifying setup and improving security coverage efficiently.
Cons
  • Users face alert issues with Huntress Managed EDR, including false positives and unclear notifications during updates.
  • Users suggest that improvements are needed for exception management and better visibility into AV scans and quarantined files.
  • Users are concerned about integration issues with various platforms, wishing for more compatibility beyond just Defender.
  • Users find the lack of customization in alerting and reporting limits the ability to tailor their experience effectively.
  • Users face limited Mac compatibility and deployment challenges, leading to frustration in mixed OS environments.

What Are Recent G2 Reviews of Huntress Managed EDR?

What Are G2 Users Discussing About Huntress Managed EDR?

ESET PROTECT

Stay one step ahead of known and emerging cyber threats with our AI-native, prevention-first approach. ESET combines the power of AI and human expertise to make protection easy and effective. Experience best-in-class protection thanks to our in-house global cyber threat intelligence, compiled and examined for over 30 years, which drives our extensive R&D network led by industry-acclaimed researchers. ESET PROTECT, our cloud-first XDR cybersecurity platform combines next-gen prevention, detection, and proactive threat hunting capabilities. ESET's highly customizable solutions include local support and have minimal impact on performance, identify and neutralize known and emerging threats before they can be executed, support business continuity, and reduce the cost of implementation and management. HOW YOUR ORGANIZATION WILL BENEFIT - Improved protection against ransomware and zero-day threats via cloud-based sandboxing technology. - Helps comply with data regulations thanks to full disk encryption capabilities on Windows and macOS. - Easily accessible ESET PROTECT console improves TCO of security management. - Single-pane-of-glass remote management for visibility of threats, users, and quarantined items. - Company endpoints and mobiles are protected via advanced multilayered technology, now with brute-force attack protection.

Average Rating: 4.6/5.0

Total Reviews: 961

How Do G2 Users Rate ESET PROTECT?

  • Ease of Admin: 8.5/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.0/10)
  • Quality of Support: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.7/10)

Who Is the Company Behind ESET PROTECT?

  • Seller: ESET
  • Company Website:
  • Year Founded: 1992
  • HQ Location: Bratislava, Slovak Republic
  • Twitter: @ESET
    275,702 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,014 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Network Administrator
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 47% Medium, 45% Small

What Do G2 Reviewers Say About ESET PROTECT?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the straightforward installation of ESET PROTECT, making it easy for anyone to get started.
  • Users commend ESET PROTECT for its robust ransomware protection, ensuring comprehensive security across multiple endpoints.
  • Users commend the reliability of ESET PROTECT, especially its strong protection against ransomware across multiple platforms.
  • Users value the great security of ESET PROTECT, ensuring computer safety with minimal impact on performance.
  • Users value the centralized management of ESET PROTECT, enabling effortless device oversight and enhanced threat detection.
Cons
  • Users find a learning curve with ESET PROTECT, as some features are complex and require expensive licenses.
  • Users find the difficult configuration process of ESET PROTECT time-consuming and sometimes overly complex for setup and management.
  • Users find the dashboard not user-friendly, citing excessive clicks for accessing necessary data and managing settings.
  • Users report a lack of clarity in policy management and task handling, complicating effective security oversight.
  • Users find difficult navigation in ESET PROTECT, requiring advanced skills and patience during implementation and setup.

What Are Recent G2 Reviews of ESET PROTECT?

What Are G2 Users Discussing About ESET PROTECT?

ThreatDown

AI has changed what businesses need to protect and how fast they need to respond. Ungoverned AI tools leak data through identities and API keys nobody's watching, while AI-driven attacks compress exploit windows from months to hours and generate the alert volume of dozens of attackers at once — a scale problem no team can staff its way out of. ThreatDown meets AI-scale risk with an AI-native platform built for more than the endpoint — one lightweight agent, one console, no tool sprawl. AI visibility flags every AI tool in use and blocks sensitive data before it reaches the model. ThreatDown ITDR monitors every identity, human and non-human, to catch compromise before attackers act. And Endpoint and email security stop attacks where they start - on the device and in the inbox. On top, ThreatDown MDR pairs AI-powered triage, with elite analysts who respond 24/7, detecting threats in a median of 5 minutes and containing them in 19. It's enterprise-grade protection at AI speed, without the headcount or complexity.

Average Rating: 4.6/5.0

Total Reviews: 1,047

How Do G2 Users Rate ThreatDown?

  • Ease of Admin: 9.1/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Quality of Support: 8.8/10 (Category avg: 8.7/10)
  • Ease of Use: 9.3/10 (Category avg: 8.7/10)

Who Is the Company Behind ThreatDown?

  • Seller: ThreatDown
  • Company Website:
  • HQ Location: Santa Clara, US
  • LinkedIn® Page: www.linkedin.com
    164 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Owner
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 48% Small, 41% Medium

What Do G2 Reviewers Say About ThreatDown?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use in deploying ThreatDown, making integration and implementation straightforward and efficient.
  • Users praise ThreatDown for its easy onboarding and integration, offering robust security with user-friendly tools and support.
  • Users value the enhanced security provided by ThreatDown, appreciating its effectiveness and minimal performance impact.
  • Users appreciate the effective threat detection of ThreatDown, making security straightforward and reliable over the years.
  • Users find the customer support of ThreatDown exceptional, noting prompt resolutions and helpful account management.
Cons
  • Users express concerns about poor customer support, citing difficulty in reaching help and needing more regular engagement.
  • Users find the lack of clarity in customization and integration processes frustrating, impacting overall user experience.
  • Users are frustrated by the significant lack of features in ThreatDown, diminishing its overall appeal and functionality.
  • Users experience false positives with ThreatDown, causing complications and confusion in managing software access effectively.
  • Users experience communication issues with ThreatDown, including sporadic device identification and slow support responses.

What Are Recent G2 Reviews of ThreatDown?

What Are G2 Users Discussing About ThreatDown?

TrendAI Vision One

TrendAI Vision One is a cloud-native security operations platform, serving cloud, hybrid, and on-premises environments. It combines ASM and XDR in a single console to effectively manage cyber risk across your organization. The platform provides powerful risk insights, earlier threat detection, and automated risk and threat response options. Utilize the platform’s predictive machine learning and advanced security analytics for a broader perspective and advanced context. TrendAI Vision One integrates with its own expansive protection platform portfolio and industry-leading global threat intelligence, in addition to a broad ecosystem of purpose-built and API-driven third-party integrations.

Average Rating: 4.7/5.0

Total Reviews: 246

How Do G2 Users Rate TrendAI Vision One?

  • Ease of Admin: 8.7/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.0/10)
  • Quality of Support: 8.7/10 (Category avg: 8.7/10)
  • Ease of Use: 8.6/10 (Category avg: 8.7/10)

Who Is the Company Behind TrendAI Vision One?

  • Seller: TrendAI
  • Company Website:
  • Year Founded: 1988
  • HQ Location: Tokyo
  • LinkedIn® Page: www.linkedin.com
    7,996 employees on LinkedIn®
  • Ownership: OTCMKTS:TMICY

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 52% Large, 34% Medium

What Do G2 Reviewers Say About TrendAI Vision One?

AI-generated summary from verified user reviews

Pros
  • Users benefit from centralized visibility across environments, enhancing risk management and simplifying security analysis and monitoring.
  • Users appreciate the intuitive and unified security dashboard of TrendAI Vision One for seamless monitoring and response.
  • Users appreciate the ease of use of TrendAI Vision One, simplifying security management with intuitive dashboards and automation.
  • Users value the centralized cloud management of TrendAI Vision One, highlighting its ease of setup and integration.
  • Users value the unified threat detection capabilities of TrendAI Vision One, enhancing cybersecurity and reducing alert fatigue.
Cons
  • Users find the interface complex and suggest improving third-party integrations for better usability and accessibility.
  • Users experience integration issues with third-party tools, making the platform less flexible and user-friendly.
  • Users face a steep learning curve with TrendAI Vision One, which complicates setup and effective usage of features.
  • Users note the high cost of TrendAI Vision One compared to competitors, impacting overall value perception.
  • Users feel the limited features of TrendAI Vision One hinder reporting capabilities and integration options.

What Are Recent G2 Reviews of TrendAI Vision One?

What Are G2 Users Discussing About TrendAI Vision One?

Cynet

Cynet is the unified, AI-powered cybersecurity platform that delivers robust and comprehensive protection for security teams while maximizing operational efficiency for managed service providers (MSPs). This platform consolidates a wide array of security capabilities into a single, user-friendly interface, ensuring that organizations can effectively safeguard their digital assets without the complexity often associated with multi-solution environments. Cynet’s platform simplifies security management by integrating various functionalities, such as endpoint protection, threat detection, and incident response, into one cohesive system. This integration not only streamlines operations but also allows organizations to allocate their resources more effectively, ultimately enhancing their overall security posture. One of the standout features of Cynet’s platform is its remarkable performance in the MITRE ATT&CK Evaluations. Cynet delivered 100% visibility and 100% analytic coverage without requiring any configuration changes three years in a row. This capability ensures that organizations can monitor their environments comprehensively and respond to threats with precision. The platform’s built-in analytics and reporting tools provide actionable insights, enabling users to make informed decisions about their cybersecurity strategies. Additionally, Cynet offers 24/7 expert support, which is crucial for organizations that may not have in-house cybersecurity expertise. This round-the-clock assistance ensures that users can quickly address any security incidents or concerns, minimizing potential downtime and damage. The combination of advanced technology and dedicated support positions Cynet as a valuable partner for SMEs and service providers looking to enhance their cybersecurity measures. In summary, Cynet’s unified, AI-powered cybersecurity platform stands out in the crowded cybersecurity market by offering a unified solution tailored to the needs of MSPs. Its comprehensive features, exceptional performance in industry evaluations, and continuous expert support make it a compelling choice for organizations seeking to bolster their cybersecurity defenses while maintaining operational efficiency.

Average Rating: 4.7/5.0

Total Reviews: 218

How Do G2 Users Rate Cynet?

  • Ease of Admin: 9.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.0/10)
  • Quality of Support: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 8.7/10)

Who Is the Company Behind Cynet?

  • Seller: Cynet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    335 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: SOC Analyst, Technical Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 58% Medium, 30% Small

What Do G2 Reviewers Say About Cynet?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Cynet, appreciating its straightforward yet comprehensive functionalities for effective protection.
  • Users value the unified platform of Cynet, which offers effective security through streamlined endpoint protection and detection.
  • Users praise Cynet for its effective threat detection and seamless monitoring, enhancing overall cybersecurity effortlessly.
  • Users commend Cynet for its exceptional customer support, ensuring a smooth and efficient deployment experience.
  • Users praise Cynet for its flawless threat monitoring and detection, enhancing overall cybersecurity effectiveness effortlessly.
Cons
  • Users find limited customization options in reporting and dashboards, affecting their ability to present necessary data.
  • Users note a lack of customization in reports, wishing for more options to tailor data presentation.
  • Users find the reporting features lacking, with requests for better customization and visualization tools.
  • Users find feature limitations in Cynet, with a desire for more customization options and broader integrations.
  • Users note limited features, such as basic reporting and few third-party integrations, impacting customization and deeper controls.

What Are Recent G2 Reviews of Cynet?

What Are G2 Users Discussing About Cynet?

SentinelOne Singularity Endpoint

SentinelOne® Singularity™ Endpoint is an autonomous endpoint security platform that stops threats in real-time. It unifies endpoint protection (EPP), endpoint detection and response (EDR), and autonomous remediation to stop ransomware, zero-day exploits, supply chain attacks, and fileless malware. Singularity Endpoint protects workstations, mobile devices, servers, and cloud workloads across SaaS, on-premises, hybrid, and air-gapped environments. Behavioral and static AI detection models stop known and unknown threats by identifying how threats behave, not just what they look like. SentinelOne catches what signatures miss, without waiting on updates. Storyline® automatically correlates telemetry into one visual attack story, and patented one-click rollback restores systems to a trusted state in seconds. The result is stronger protection with fewer incidents and less operational overhead: lower dwell time, fewer false positives, and faster response. With Purple AI™, teams accelerate triage, threat hunting, and investigation. From alert to verdict without manual investigation. Purple AI's Agentic Investigation runs the analysis, surfaces the evidence, and tells your team exactly what to do next. The same SentinelOne agent that protects endpoints also defends every identity behind them. Detect credential abuse, shrink your attack surface, and contain identity threats from one console. Seamless integration of endpoint, identity, cloud, and third-party telemetry eliminates blind spots. Built AI-native from day one, Singularity Endpoint delivers best-in-industry coverage across Windows, macOS, Linux, and mobile operating systems, including legacy OSes. Trusted by more than 11,500 customers, SentinelOne is a six-time Gartner® Magic Quadrant™ Leader for Endpoint Protection.

Average Rating: 4.7/5.0

Total Reviews: 205

How Do G2 Users Rate SentinelOne Singularity Endpoint?

  • Ease of Admin: 8.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Quality of Support: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.7/10)

Who Is the Company Behind SentinelOne Singularity Endpoint?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,571 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 45% Medium, 36% Large

What Do G2 Reviewers Say About SentinelOne Singularity Endpoint?

AI-generated summary from verified user reviews

Pros
  • Users value the tool efficiency of SentinelOne Singularity Endpoint, appreciating its user-friendly interface and effective threat detection.
  • Users find the ease of integration with Nable RMM and setup straightforward for daily operations.
  • Users praise the exceptional malware protection of SentinelOne, effectively stopping threats before they can cause harm.
  • Users find SentinelOne Singularity Endpoint to be a highly useful tool for incident notification and investigation.
  • Users appreciate the quick alerts and feature-rich capabilities of SentinelOne, enhancing security management and support.
Cons
  • Users face update issues with SentinelOne Singularity, leading to login problems and cumbersome agent management.
  • Users find the difficult learning curve of SentinelOne Singularity Endpoint challenging, especially for beginners navigating its features.
  • Users find the frequent updates challenging, as rapid changes lead to login issues and a steep learning curve.
  • Users report challenges with agent removal issues impacting application functionality and requiring improvement in uninstallation processes.
  • Users report ineffective alerts that hinder troubleshooting and prevent them from addressing application issues effectively.

What Are Recent G2 Reviews of SentinelOne Singularity Endpoint?

What Are G2 Users Discussing About SentinelOne Singularity Endpoint?

Coro Cybersecurity

Coro is the easy cybersecurity company. We designed an all-in-one platform that every lean IT team will master. While other solutions scare people into buying complicated, confusing products, we lead with elegant simplicity. Coro is fast to deploy, easy to use, and designed not to waste your time. Once you install Coro, you’ll hardly think about us. That’s the point. Coro automatically detects and fixes security problems, so IT teams don’t have to spend time investigating or troubleshooting. We’re also one of the fastest-growing tech companies in North America, just ask Deloitte. Designed primarily for lean IT teams, Coro’s platform is particularly beneficial for organizations that may lack extensive IT resources or dedicated cybersecurity teams. With the increasing complexity of cyber threats, these businesses often find it challenging to maintain adequate security measures. Coro addresses this gap by automating the detection and remediation of security threats, allowing businesses to focus on their core operations without the constant worry of potential breaches or security incidents. One of Coro's key benefits is its intuitive, user-friendly interface, which simplifies the management of cybersecurity protocols. This ease of use is particularly advantageous for organizations with limited IT expertise, as it minimizes the need for extensive training or technical knowledge. Additionally, Coro’s continuous monitoring and reporting features provide businesses with valuable insights into their security posture, enabling them to make informed decisions about their cybersecurity strategies. Another impressive features is how comprehensive, yet powerful, it's all-in-one platform is. Using advanced AI technology, it detects and remediates over 92% of threats automatically, ensuring potential vulnerabilities are identified and addressed in real-time, significantly reducing the risk of data breaches and other cyber incidents. Their impressive performance has been recognised by G2 with a 94% approval rating from users and SE Labs, who awarded them three AAA ratings for their EDR, Email and Cloud modules. Overall, Coro’s cybersecurity platform represents a significant advancement in the field of cybersecurity. By automating threat detection and remediation, offering customizable solutions, and providing a user-friendly experience, Coro empowers organizations to effectively defend against the evolving landscape of cyber threats. Its recognition as one of the fastest-growing cybersecurity companies in North America further underscores its commitment to delivering innovative and effective security solutions.

Average Rating: 4.7/5.0

Total Reviews: 232

How Do G2 Users Rate Coro Cybersecurity?

  • Ease of Admin: 9.5/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.0/10)
  • Quality of Support: 9.5/10 (Category avg: 8.7/10)
  • Ease of Use: 9.5/10 (Category avg: 8.7/10)

Who Is the Company Behind Coro Cybersecurity?

  • Seller: Coronet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Chicago, IL
  • Twitter: @coro_cyber
    1,876 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    275 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Non-Profit Organization Management, Financial Services
  • Company Size: 56% Medium, 36% Small

What Do G2 Reviewers Say About Coro Cybersecurity?

AI-generated summary from verified user reviews

Pros
  • Users find Coro Cybersecurity's ease of use outstanding, with quick setup and excellent support for seamless protection.
  • Users value the peace of mind provided by Coro Cybersecurity's easy installation and effective endpoint protection.
  • Users appreciate the fantastic customer support from Coro Cybersecurity, making implementation and maintenance seamless.
  • Users value Coro Cybersecurity for its affordability and robust protection, enhancing security for users and endpoints.
  • Users appreciate the easy setup of Coro Cybersecurity, enjoying a seamless experience with excellent customer support.
Cons
  • Users experience performance issues with Coro Cybersecurity, particularly regarding spam filtration and agent limitations.
  • Users indicate that improvements are needed in malware reporting, dashboard detail, and client update reliability.
  • Users report a higher than expected incidence of false positives, complicating email management and efficiency.
  • Users experience inaccuracy in spam training, with false positives and region-specific content hindering effectiveness for USA users.
  • Users express concerns about limited features in Coro, particularly regarding email reporting and basic module functionalities.

What Are Recent G2 Reviews of Coro Cybersecurity?

What Are G2 Users Discussing About Coro Cybersecurity?

Guardz

Guardz is a unified cybersecurity platform specifically designed for Managed Service Providers (MSPs). This innovative solution consolidates essential security controls, identity threat detection and response (ITDR), endpoint protection (EDR), email security, user awareness training and phishing simulations, and Managed Detection and Response (MDR) into a single AI-native framework. The platform aims to enhance operational efficiency by streamlining security processes and providing a comprehensive approach to cybersecurity. Targeting MSPs, Guardz addresses the unique challenges these providers face in managing multiple security tools that often operate in silos. By adopting an identity-centric approach, Guardz connects various security vectors, effectively reducing the gaps that can leave organizations vulnerable. This layered and holistic view enables MSPs to respond to user risks in real time, ensuring that security measures are not only reactive but also proactive in safeguarding client environments. Key features of Guardz include its 24/7 AI and human-led Managed Detection and Response (MDR) services. The platform employs agentic AI to triage threats at machine speed, allowing for rapid identification and prioritization of potential security incidents. This automated triage process is complemented by expert analysts who validate findings, mitigate risks, and guide response actions. As a result, MSPs can offer scalable protection to their clients without the need to expand their workforce, making it a cost-effective solution for growing cybersecurity demands. Guardz stands out in the cybersecurity landscape by providing a unified platform that integrates various security functions into one cohesive system. This integration not only simplifies the management of security tools but also enhances the overall effectiveness of security measures. By leveraging AI-driven insights and human expertise, Guardz empowers MSPs to deliver robust cybersecurity solutions that adapt to the evolving threat landscape, ensuring their clients remain protected against emerging risks.

Average Rating: 4.6/5.0

Total Reviews: 124

How Do G2 Users Rate Guardz?

  • Ease of Admin: 9.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Quality of Support: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.4/10 (Category avg: 8.7/10)

Who Is the Company Behind Guardz?

  • Seller: Guardz
  • Company Website:
  • Year Founded: 2022
  • HQ Location: Tel Aviv, IL
  • Twitter: @GuardzCyber
    114 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    160 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Owner, CEO
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 77% Small, 18% Medium

What Do G2 Reviewers Say About Guardz?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Guardz, highlighting its organized dashboard and straightforward integration.
  • Users value the robust security of Guardz, ensuring comprehensive protection for their systems and emails effortlessly.
  • Users value the efficient multi-tenant features of Guardz, enhancing operational workflow and client management.
  • Users appreciate the easy setup of Guardz, quickly deploying it for customers in about an hour.
  • Users value the effective threat detection capabilities of Guardz, enhancing overall cybersecurity for their clients.
Cons
  • Users find the limited features of Guardz restrict their workflow and hinder automation capabilities, needing more flexibility.
  • Users face integration issues with Guardz, finding alerts cumbersome and lacking essential API support for smoother operations.
  • Users note a significant lack of features in Guardz, limiting its effectiveness in mixed environments and advanced configurations.
  • Users find limited customization options in Guardz, impacting its adaptability for advanced configurations in mixed environments.
  • Users desire more transparency and clarity regarding the tools and methods used by Guardz for safety.

What Are Recent G2 Reviews of Guardz?

IBM MaaS360

IBM MaaS360 is an easy to use, unified endpoint management (UEM) solution that transforms the way that organizations support users, apps, content, and data across essentially every type of device. Its open, cloud-based platform integrates with preferred security and productivity tools. You can protect your workforce with evolved Threat Management, Mobile Security, Device management features and your analytics will be powered by watsonx AI capabilities, helping you to set up a good security posture. IBM MaaS360 is available for purchase on ibm.com and AWS Marketplace.

Average Rating: 4.2/5.0

Total Reviews: 193

G2 Deal: Buy today for 30% off

Manage and protect your mobile workforce with AI-driven unified endpoint management (UEM). Choose IBM Maas360 and get 30% off your first annual subscription. Offer ends 15 April 2026.

Price: ~~5.00 USD~~ → 3.50 USD

View this exclusive G2 deal

How Do G2 Users Rate IBM MaaS360?

  • Ease of Admin: 8.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.0/10 (Category avg: 9.0/10)
  • Quality of Support: 8.1/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.7/10)

Who Is the Company Behind IBM MaaS360?

  • Seller: IBM
  • Company Website:
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 44% Medium, 33% Large

What Do G2 Reviewers Say About IBM MaaS360?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the advanced threat management and user-friendly integration of IBM MaaS360 for enhanced security.
  • Users appreciate the security features of IBM MaaS360, effectively safeguarding their tools against various cyber threats.
  • Users value the unified device management of IBM MaaS360, effectively enhancing security across all devices.
  • Users value the ease of use in IBM MaaS360, highlighting its intuitive onboarding and management features.
  • Users value the robust protection offered by IBM MaaS360, ensuring security and management for enterprise tools.
Cons
  • Users find the learning curve steep, as advanced configurations and outdated interface complicate intuitive usage.
  • Users find the interface design poor, describing it as outdated and occasionally overwhelming for new users.
  • Users find the UI outdated and clunky, making navigation and usability less enjoyable on IBM MaaS360.
  • Users experience slow performance with IBM MaaS360 due to outdated interface and occasional sync delays.
  • Users find the interface outdated, making navigation and usage less intuitive compared to modern applications.

What Are Recent G2 Reviews of IBM MaaS360?

What Are G2 Users Discussing About IBM MaaS360?

WatchGuard Endpoint Security

The WatchGuard Endpoint Security portfolio delivers endpoint security for organizations of every size, from foundational protection to advanced EDR, zero-trust execution, and automated containment. Designed to scale with organizational maturity, the portfolio includes Endpoint Security Basic, Prime, 360, and Elite. All solutions are managed through a single, lightweight agent and WatchGuard Cloud, simplifying deployment and management while maintaining consistent security across environments.

Average Rating: 4.4/5.0

Total Reviews: 116

How Do G2 Users Rate WatchGuard Endpoint Security?

  • Ease of Admin: 8.7/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.0/10)
  • Quality of Support: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.7/10)

Who Is the Company Behind WatchGuard Endpoint Security?

  • Seller: WatchGuard
  • Company Website:
  • Year Founded: 1996
  • HQ Location: Seatle, WA
  • Twitter: @watchguard
    19,467 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,227 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Developer, IT Manager
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 55% Small, 33% Medium

What Do G2 Reviewers Say About WatchGuard Endpoint Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the user-friendly interface and robust threat detection of WatchGuard Endpoint Security for easy use and integration.
  • Users appreciate the real-time threat detection and protection of WatchGuard Endpoint Security, ensuring constant safety and user-friendly access.
  • Users appreciate the real-time threat detection of WatchGuard Endpoint Security, ensuring constant protection against malware and ransomware.
  • Users appreciate the robust cybersecurity protection of WatchGuard Endpoint Security, ensuring constant safety and integration with other products.
  • Users highlight the ease of installation and use of WatchGuard Endpoint Security, making it user-friendly and efficient.
Cons
  • Users find the setup process overly complex, making it challenging for newcomers to effectively utilize WatchGuard Endpoint Security.
  • Users find the setup process complex, posing challenges for those unfamiliar with the system.
  • Users find the difficult configuration of WatchGuard Endpoint Security challenging, especially for those less experienced with technology.
  • Users find WatchGuard Endpoint Security to be too expensive, impacting their overall satisfaction with the product.
  • Users find the setup process complex, which can be challenging, especially for those new to the system.

What Are Recent G2 Reviews of WatchGuard Endpoint Security?

What Are G2 Users Discussing About WatchGuard Endpoint Security?

N-able N-central

Join the thousands of MSPs and IT professionals who use N-able™ N-central® to remotely monitor and manage devices and complex networks. Built with security in mind, N-central provides the visibility and efficiency you need to monitor more, provide great customer service, and scale your business. Key features include: • Monitor almost any device, including support for Windows, Linux, and macOS • Gain complete insight across your network and cloud services without the need for extra network monitoring software • Create automated patch management policies to ensure devices are up to date • Streamline your workflow with drag-and-drop scripting in automation manager—no need to write a line of code • Provide remote support across devices and platforms with the integrated Take Control feature • Integrate your existing PSA software or use N-able MSP Manager to manage tickets and billing • Manage security with integrated backup, EDR, AV, and disk encryption • Available as an on-premises or hosted cloud solution to fit your business N-central is designed to help you run your managed services business or internal IT department more efficiently, so you can focus on scaling operations.

Average Rating: 4.4/5.0

Total Reviews: 543

How Do G2 Users Rate N-able N-central?

  • Ease of Admin: 7.9/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.0/10)
  • Quality of Support: 7.9/10 (Category avg: 8.7/10)
  • Ease of Use: 7.9/10 (Category avg: 8.7/10)

Who Is the Company Behind N-able N-central?

  • Seller: N-able
  • Company Website:
  • HQ Location: Morrisville, North Carolina
  • Twitter: @Nable
    15,859 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Who Uses This: Director, Operations Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 59% Small, 33% Medium

What Do G2 Reviewers Say About N-able N-central?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of N-able N-central, finding it intuitive for managing systems seamlessly.
  • Users value the customizable automation features of N-able N-central, enhancing control and efficiency in IT management.
  • Users value the customizable scripting options in N-able N-central, enhancing control and flexibility for IT management.
  • Users appreciate the solid remote access features of N-able N-central, enhancing system monitoring and management efficiency.
  • Users value the proactive monitoring capabilities of N-able N-central, enhancing efficiency without disrupting clients.
Cons
  • Users find the missing features, like chat and credential management, hinder efficiency and user experience.
  • Users often face feature issues that hinder efficiency, including bugs, connection problems, and inconsistent filtering.
  • Users express frustration over filter editing limitations and the cumbersome patching process in N-able N-central.
  • Users find the steep learning curve due to scattered documentation and lack of comprehensive guides challenging.
  • Users find the interface confusing, struggling with a steep learning curve and unwieldy settings management.

What Are Recent G2 Reviews of N-able N-central?

What Are G2 Users Discussing About N-able N-central?

N-able N-Sight RMM

N-able N-sight™ RMM combines remote monitoring and management, remote access, ticketing, and billing capabilities, into one powerful yet easy to use platform that streamlines day-to-operations, combats threats and drives operational efficiency. Key features include: • Manage all devices across Windows, Linux and Apple platforms • Get up in running rapidly with simple onboarding steps, built-in automation scripts and patching policies • Automated Microsoft patch management to help ensure compliance and security at all times • Integrated Endpoint Detection and Response for layered security • Drag and drop automation for efficient service delivery • Secure and instant remote access to desktop or mobile devices (Windows, macOS, iOS and Android) • Ticketing, including workflows, routing rules and automation to drive efficiency and collaboration across teams • Simple time tracking, including functionality for recurring tickets and appointments • Automated billing and invoicing that integrates with your existing accounting software • Best in class integrations, providing flexibility via APIs and open ecosystem N-sight RMM makes it easy for MSPs and IT Professionals to get started in minutes with a powerful all-in-one platform that delivers the perfect blend of capabilities and ease of use.

Average Rating: 4.3/5.0

Total Reviews: 349

How Do G2 Users Rate N-able N-Sight RMM?

  • Ease of Admin: 8.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.0/10)
  • Quality of Support: 8.2/10 (Category avg: 8.7/10)
  • Ease of Use: 8.3/10 (Category avg: 8.7/10)

Who Is the Company Behind N-able N-Sight RMM?

  • Seller: N-able
  • Company Website:
  • HQ Location: Morrisville, North Carolina
  • Twitter: @Nable
    15,859 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Who Uses This: Owner, President
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 73% Small, 20% Medium

What Do G2 Reviewers Say About N-able N-Sight RMM?

AI-generated summary from verified user reviews

Pros
  • Users enjoy the ease of use of N-able N-Sight RMM, finding it simple to navigate and set up.
  • Users value the fast remote access of N-able N-Sight RMM, enhancing control and productivity for customer support.
  • Users value the automation capability of N-able N-Sight RMM, as it significantly enhances efficiency and time management.
  • Users value the real-time monitoring capabilities of N-able N-Sight RMM, enhancing proactive management of systems.
  • Users appreciate the intuitive ease of use of N-able N-Sight RMM, enhancing their team's efficiency with straightforward functionality.
Cons
  • Users experience feature issues with N-able N-Sight RMM, leading to frustration and inefficiency in daily operations.
  • Users find the interface not user-friendly, making navigation and understanding features challenging and frustrating.
  • Users struggle with laggy performance on slow devices, making remote access challenging and frustrating at times.
  • Users find the missing features in N-able N-Sight RMM limit integration and functionality for device management.
  • Users experience significant patching issues, with unreliable agents and inconsistent management creating more work, not less.

What Are Recent G2 Reviews of N-able N-Sight RMM?

What Are G2 Users Discussing About N-able N-Sight RMM?

BlackFog

Data can’t be stolen if it never leaves. BlackFog prevents data exfiltration from endpoints, stopping sensitive information from flowing to ransomware groups, AI tools, cloud services, and other unauthorized destinations. While most cybersecurity solutions focus on detecting threats, BlackFog focuses on preventing the outcome attackers want most: access to your data. Our endpoint-native platform monitors and controls outbound communications in real time, preventing data loss through ransomware, insider threats, shadow AI, and other exfiltration channels. BlackFog pioneered anti data exfiltration (ADX), a category built around a simple principle: the endpoint is the last place data can be stopped before it’s gone. By operating directly on the device, BlackFog provides visibility and control across browsers, cloud applications, AI tools, encrypted connections, and emerging AI workflows that traditional network-based approaches often miss. Today, organizations use BlackFog to prevent ransomware data theft, govern AI usage, reduce data loss risk, and protect sensitive information wherever users work. Key Capabilities * Anti data exfiltration (ADX) * Ransomware Data Theft Prevention * Shadow AI Discovery and Governance * AI Data Loss Prevention * Insider Threat Protection * Real-Time Outbound Traffic Control * Endpoint Data Protection * Compliance and Privacy Enforcement

Average Rating: 4.9/5.0

Total Reviews: 34

How Do G2 Users Rate BlackFog?

  • Ease of Admin: 9.1/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.0/10)
  • Quality of Support: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 8.7/10)

Who Is the Company Behind BlackFog?

  • Seller: BlackFog
  • Company Website:
  • Year Founded: 2015
  • HQ Location: BlackFog Inc. Suite 1400 4 Embarcadero Ctr San Francisco CA 94111, United States
  • Twitter: @blackfogprivacy
    1,494 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 31% Medium

What Do G2 Reviewers Say About BlackFog?

AI-generated summary from verified user reviews

Pros
  • Users value the exceptional security features of BlackFog, ensuring robust protection for sensitive data against digital threats.
  • Users commend BlackFog for its exceptional protection against ransomware, ensuring peace of mind for clients and service providers.
  • Users praise the responsive customer support of BlackFog, enhancing their experience with friendly and effective assistance.
  • Users appreciate the ease of use of BlackFog, highlighting its user-friendly interface and seamless setup process.
  • Users appreciate the security protection of BlackFog, providing seamless monitoring and safeguarding against data breaches continuously.
Cons
  • Users desire missing features, such as automated reports and better integration with other security tools.
  • Users note the odd UI design with translucent windows, which affects their overall experience with BlackFog.
  • Users find BlackFog's features limited, particularly noting the lack of advanced device management tools for comprehensive security.
  • Users express frustration with false positives in alert management, leading to time-consuming processes and inefficiencies.
  • Users find the user interface complex, making it difficult for newcomers to navigate and fully utilize BlackFog.

What Are Recent G2 Reviews of BlackFog?

What Are G2 Users Discussing About BlackFog?

Field Effect MDR

Field Effect delivers intelligence-grade managed detection and response for the AI era. Built on Federated Smart Compute™ and nation-state tradecraft, our holistic MDR platform uncovers weaknesses early, blocks attacks in real time, and reduces risk across the entire threat surface—endpoint, network, cloud, and more. With an 18-second median time to detect, Field Effect helps MSPs and overwhelmed IT teams outpace agentic attacks and achieve premium protection with the team they have.

Average Rating: 4.8/5.0

Total Reviews: 43

How Do G2 Users Rate Field Effect MDR?

  • Ease of Admin: 9.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Quality of Support: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 8.7/10)

Who Is the Company Behind Field Effect MDR?

  • Seller: Field Effect
  • Company Website:
  • Year Founded: 2016
  • HQ Location: Ottawa
  • Twitter: @fieldeffectsoft
    1,304 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    149 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 52% Small, 27% Medium

What Do G2 Reviewers Say About Field Effect MDR?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use in Field Effect MDR, particularly enjoying simple setup and deployment processes.
  • Users value the responsive and helpful customer support of Field Effect MDR, ensuring effective implementation and issue resolution.
  • Users appreciate the comprehensive alert notifications of Field Effect MDR, enabling timely identification of vulnerabilities and issues.
  • Users commend the easy initial setup of Field Effect MDR, allowing for quick deployment and seamless integration.
  • Users value the 24/7 threat detection of Field Effect MDR, ensuring immediate identification and isolation of cybersecurity threats.
Cons
  • Users find alert issues with Field Effect MDR, often needing additional support due to unclear notifications and false alarms.
  • Users find the inefficient alert system difficult to manage due to overwhelming volume and lack of detail.
  • Users find the learning curve steep, necessitating additional time for onboarding and user adaptation to the Field Effect MDR.
  • Users find the communication issues frustrating, often needing to simplify technical info for clients, leading to extra support requests.
  • Users experience integration issues with Field Effect MDR, leading to reporting challenges and account disruptions during system interactions.

What Are Recent G2 Reviews of Field Effect MDR?

What Are G2 Users Discussing About Field Effect MDR?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated March 4, 2025