Best Attack Surface Management Software - Page 4

How Many Attack Surface Management Software Products Does G2 Track?

Total Products under this Category: 189

Category Stats (Sep 2026)

  • Average Rating: 4.6/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Hunto AI (+2.02%) - Among all products in this category, Hunto AI recorded the largest rating increase compared to last month

Last updated: September 26, 2026

How Does G2 Rank Attack Surface Management Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 5,900+ Authentic Reviews
  • 189+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

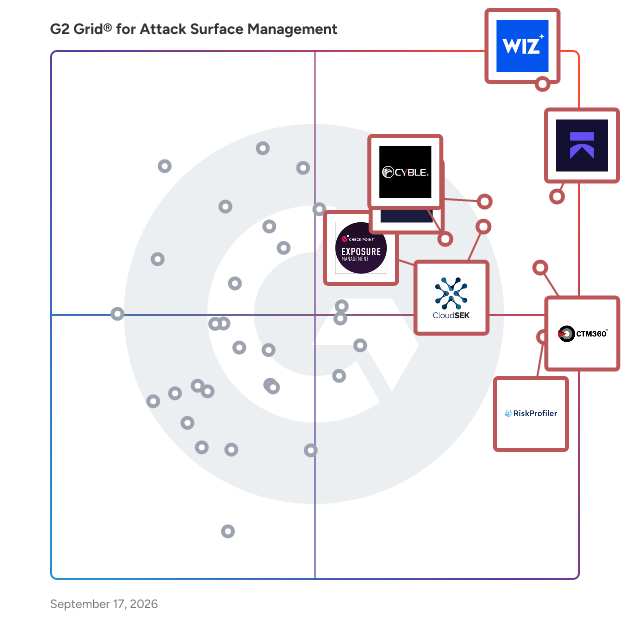
G2 Grid® for Attack Surface Management Software

G2 Grid® for  Attack Surface Management Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Aikido Security, SOCRadar Extended Threat Intelligence, CTM360, CloudSEK, Cyble, RiskProfiler - External Threat Exposure Management, and Check Point Exposure Management.

Underlying data: [Grid® JSON](https://www.g2.com/categories/attack-surface-management/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=aikido-security&focus%5B%5D=socradar-extended-threat-intelligence&focus%5B%5D=ctm360-ctm360&focus%5B%5D=cloudsek&focus%5B%5D=cyble&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=check-point-exposure-management)

HostedScan.com

HostedScan provides 24x7 alerts and detection for security vulnerabilities. Industry-standard, open-source, vulnerability scans. Automated alerts when something changes. Manage target list manually or import automatically from providers, such as AWS, DigitalOcean, and Linode, with read-only access. Manage and audit risks with dashboarding and reporting.

Average Rating: 4.3/5.0

Total Reviews: 13

How Do G2 Users Rate HostedScan.com?

  • Ease of Admin: 8.8/10 (Category avg: 9.0/10)

Who Is the Company Behind HostedScan.com?

  • Seller: HostedScan
  • Year Founded: 2019
  • HQ Location: Seattle, Washington
  • Twitter: @hostedscan
    59 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 85% Small, 15% Medium

What Are Recent G2 Reviews of HostedScan.com?

SentinelOne Singularity Network Discovery

Singularity Ranger is a real-time network attack surface control solution that finds and fingerprints all IP-enabled devices on your network, to deliver global visibility with zero additional agents, hardware, or network changes. Ranger discovers and recovers unsecured endpoints with configurable, automated peer-to-peer agent deployment, to quickly plug gaps in your attack surface.

Average Rating: 4.8/5.0

Total Reviews: 8

How Do G2 Users Rate SentinelOne Singularity Network Discovery?

  • Vulnerability Intelligence: 8.3/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.3/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.8/10 (Category avg: 8.7/10)
  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind SentinelOne Singularity Network Discovery?

  • Seller: SentinelOne
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • Twitter: @SentinelOne
    57,863 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    6,571 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Company Size: 56% Large, 33% Medium

What Do G2 Reviewers Say About SentinelOne Singularity Network Discovery?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the incredibly deep visibility of SentinelOne Singularity Network Discovery, enhancing understanding of their network environment.
  • Users value the easy integrations of SentinelOne Singularity, enhancing efficiency and simplifying network management.
  • Users value the enhanced efficiency of SentinelOne, benefiting from automated visibility and streamlined asset discovery.
  • Users value the real-time visibility provided by SentinelOne, enhancing security through automated device mapping and risk detection.
  • Users praise the deep visibility provided by SentinelOne Singularity, enhancing their understanding of network environments.
Cons
  • Users find the initial setup complex, as numerous configurations can be overwhelming and challenging to navigate.
  • Users find the product expensive with limited customization, making it less appealing for some organizations.
  • Users report that false positives can lead to unnecessary alerts, impacting their experience with SentinelOne Singularity.
  • Users find the filtering options overwhelming, especially with large datasets during the initial setup process.
  • Users find the limited customization options restrictive, impacting their ability to tailor the solution to their needs.

What Are Recent G2 Reviews of SentinelOne Singularity Network Discovery?

Criminal IP

Criminal IP is a cyber threat intelligence solution that provides decision-ready threat intelligence, and attack surface management solutions to security teams worldwide. By continuously scanning the global internet, Criminal IP aggregates and contextualizes threat signals across IPs, domains, URLs, and attack infrastructure, covering malicious indicators, known vulnerabilities, exposed assets, and attacker behavior. Criminal IP's mission is to give organizations real visibility into their cyber landscape and accelerate threat detection and response by delivering the intelligence needed to outsmart attackers.

Average Rating: 4.6/5.0

Total Reviews: 12

How Do G2 Users Rate Criminal IP?

  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Criminal IP?

  • Seller: Criminal IP
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Las Vegas, US
  • LinkedIn® Page: www.linkedin.com
    29 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 93% Small, 7% Medium

What Do G2 Reviewers Say About Criminal IP?

AI-generated summary from verified user reviews

Pros
  • Users value the automation capabilities of Criminal IP, enabling efficient visualization and management of security data.
  • Users appreciate the ease of use of Criminal IP, enjoying its intuitive navigation and quick setup for complex data.
  • Users appreciate the intuitive design and powerful toolkit of Criminal IP, making complex security data easy to manage.
  • Users commend the quick response time of Criminal IP, enabling efficient real-time visualization and action on threats.
  • Users appreciate the seamless setup of Criminal IP, enabling quick and effortless integration into their systems.
Cons
  • Users find the difficult learning curve frustrating, especially when mastering advanced search filters and navigating the interface.
  • Users experience a steep learning curve for advanced search filters, highlighting the need for improved onboarding resources.
  • Users experience slow loading issues with Criminal IP's web interface, causing minor delays in accessing live data.

What Are Recent G2 Reviews of Criminal IP?

IDARK360

IDARK360 is an advanced platform offering 360-degree protection against modern cyber risks, focusing on four key areas: Dark Web Discovery and Monitoring: Accurate identification of your stolen data trading (credentials, IP, customer data) for early threat neutralization. Brand Identity Protection: Immediate monitoring for impersonation and phishing, with rapid removal of fraudulent content to safeguard your reputation. Security Controls Governance: Continuous and precise assessment of compliance with global controls (NIST, NCA) and gap management via a unified dashboard. Cyber Awareness and Culture Building: Employee Training: Providing simulated and realistic training programs to enhance employee vigilance. Phishing Simulation: Periodically testing the effectiveness of the human defence layer and identifying individual and collective weaknesses. Transforming Employees into a Defence Line: Reducing human errors that cause a significant percentage of breaches.

Average Rating: 5.0/5.0

Total Reviews: 9

How Do G2 Users Rate IDARK360?

  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind IDARK360?

  • Seller: IDARK360
  • Year Founded: 2025
  • HQ Location: Riyadh , SA
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of IDARK360?

Qomplx

QOMPLX is a leading provider of identity-focused cybersecurity software solutions. Our technology continually monitors user activity across all points of access, including cloud and on-premise systems, to prevent harm to your network, detect suspicious behavior and anomalies, and provide contextualized recommendations to improve your overall cybersecurity. The QOMPLX data platform provides real-time alerts and visualizations for rapid response and to allow for a proactive stance against malicious actors. It also enables the capture and store of identity data for future analysis, allowing organizations to detect and respond to emerging threats in a timely and effective manner. Additionally, our platform provides comprehensive reporting, audit trails, and a secure environment for identity management. With QOMPLX solutions, organizations can protect their digital environment from identity-related threats and ensure business continuity by utilizing: • Threat Detection and Response (ITDR) Prevent, detect and respond to identity threats in real-time • Managed Solutions Cost effective managed cybersecurity including Managed ITDR, Managed Extended Detection and Response (XDR), and Managed Detection and Response (MDR) • Attack Surface Monitoring (ASM) Discover cyber vulnerabilities and the size of your attack surface

Average Rating: 4.5/5.0

Total Reviews: 11

How Do G2 Users Rate Qomplx?

  • Vulnerability Intelligence: 8.8/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.9/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Qomplx?

  • Seller: QOMPLX
  • Year Founded: 2015
  • HQ Location: Tysons, Virginia
  • Twitter: @QOMPLX
    575 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    22 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 55% Medium, 27% Large

What Are Recent G2 Reviews of Qomplx?

Tenable OT Security

Tenable OT Security disrupts attack paths and protects industrial and critical infrastructure from cyber threats. From inventory management and asset tracking to threat detection at the device and network level, vulnerability management and configuration control, Tenable’s OT security capabilities provide maximum visibility, security, and control across your entire operations.

Average Rating: 4.1/5.0

Total Reviews: 7

How Do G2 Users Rate Tenable OT Security?

  • Vulnerability Intelligence: 7.8/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.3/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 7.5/10 (Category avg: 8.7/10)
  • Ease of Admin: 6.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Tenable OT Security?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • Twitter: @TenableSecurity
    87,752 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Company Size: 57% Large, 29% Small

What Do G2 Reviewers Say About Tenable OT Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the true OT awareness and visibility provided by Tenable OT Security for complex environments.
  • Users appreciate the enhanced OT visibility of Tenable OT Security, facilitating security team efforts without operational disruption.
  • Users value the comprehensive visibility Tenable OT Security provides, enhancing understanding and actionability in complex OT environments.
  • Users value the full visibility into OT assets provided by Tenable OT Security, enabling quick risk remediation.
  • Users commend the detection efficiency of Tenable OT Security, facilitating swift risk remediation without disrupting operations.
Cons
  • Users find the limited features of Tenable OT Security restrictive, impacting advanced reporting and asset management tasks.
  • Users find the complexity of asset management in Tenable OT Security makes asset discovery tedious and reporting limited.
  • Users find the pricing higher than expected for smaller plants, complicating access to Tenable OT Security's features.
  • Users find the asset management process complicated, making the discovery of OT assets a tedious task.
  • Users find the inadequate reporting and customization limiting, alongside complexities in pricing and licensing.

What Are Recent G2 Reviews of Tenable OT Security?

Edgio

Edgio (NASDAQ: EGIO) helps companies deliver online experiences and content faster, safer, and with more control. Our developer-friendly, globally scaled edge network, combined with our fully integrated application and media solutions, provide a single platform for the delivery of high-performing, secure web properties, and streaming content. Through this fully integrated platform and end-to-end edge services, companies can deliver content quicker and more securely, boosting overall revenue and business value. All services run at the edge of our private, global network with 250 Tbps of bandwidth capacity. We process 5% of all web traffic and are rapidly growing. Edgio is trusted and relied on by TD Ameritrade, Plus500, Solvay Bank, Yahoo, Shoe Carnival, Canadian Hockey League, World Champion Fantasy, Mars Wrigley, Coach, and Kate Spade.

Average Rating: 4.1/5.0

Total Reviews: 19

How Do G2 Users Rate Edgio?

  • Ease of Admin: 7.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Edgio?

  • Seller: Edgio
  • Year Founded: 2001
  • HQ Location: Scottsdale, Arizona
  • LinkedIn® Page: www.linkedin.com
    428 employees on LinkedIn®
  • Ownership: NASDAQ:LLNW
  • Total Revenue (USD mm): $200

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 40% Large, 40% Medium

What Are Recent G2 Reviews of Edgio?

What Are G2 Users Discussing About Edgio?

FortifyData AI-Powered Cyber GRC Platform

FortifyData is an AI-powered Cyber GRC platform that unifies attack surface management, risk-based vulnerability management, third-party risk management, and compliance automation into a single, continuously updated system built for modern security and risk teams. Where traditional GRC tools generate static dashboards and reports for humans to interpret, FortifyData's AI layer transforms how organizations engage with their risk data, moving from passive consumption to active, continuous risk management. Underpinning the platform is a layer of AI capabilities that automate risk workflows, analyze security reports, and give teams a direct interface to interrogate their security posture and take action on what they find. Attack Surface Management & Risk-Based Vulnerability Management FortifyData continuously discovers, assesses, and prioritizes risk across your entire external attack surface, delivering the real-time exposure intelligence security teams need to act on what matters most. The platform combines external attack surface discovery, vulnerability identification, and risk-based prioritization into a unified, continuously updated workflow. Rather than generating point-in-time snapshots, FortifyData maintains a live inventory of assets, exposures, and risk context, enabling organizations to operationalize a Continuous Threat Exposure Management (CTEM) strategy without stitching together multiple point solutions. AI-powered analysis correlates asset exposure with threat intelligence and business context, so teams prioritize remediation based on actual risk impact rather than raw vulnerability volume. Configurable risk modeling ensures prioritization reflects your organization's unique environment and not a generic industry baseline. Third-Party Risk Management & Vendor Security Assessment FortifyData's TPRM solution goes beyond questionnaires and periodic assessments by continuously monitoring the external attack surface of your vendor ecosystem, giving organizations a live, evidence-based view of third-party risk rather than a self-reported one. Vendor findings from continuous external monitoring are used to automatically validate technology-related questions within assessments, questionnaires, and compliance frameworks, eliminating manual cross-referencing and reducing the time and subjectivity inherent in traditional vendor review processes. Combined with in-scope assessments that target the specific technologies and controls relevant to each vendor relationship, FortifyData ensures that third-party risk reviews reflect actual exposure and not just vendor attestation. AI capabilities extend across the entire vendor lifecycle. An AI Auditor automatically analyzes and scores vendor-submitted security reports. AI Lifecycle Management Agents autonomously manage vendor workflows from onboarding through continuous monitoring and renewal. An AI interrogation interface allows risk teams to actively query vendor risk data and trigger actions, replacing passive report consumption with dynamic risk engagement. Governance, Risk & Compliance FortifyData's compliance automation capabilities connect live risk and control data directly to framework requirements, eliminating the manual effort of mapping security posture to compliance obligations. The platform supports any standard compliance framework out of the box, with the flexibility to configure custom frameworks to meet organization-specific requirements. Unlike standalone GRC tools that rely on self-assessed control status, FortifyData continuously validates compliance posture against real-time asset, vulnerability, and vendor risk data, so compliance reporting reflects actual security state rather than a periodic attestation. This connection between live risk intelligence and compliance workflows enables organizations to reduce audit preparation time, identify control gaps proactively, and demonstrate a defensible, evidence-based compliance posture to auditors, boards, and regulators. A Unified Platform Advantage FortifyData eliminates the tool sprawl and data fragmentation that undermines effective cyber risk management. By unifying attack surface management, vulnerability prioritization, third-party risk, and compliance automation in a single platform, security and risk teams gain a connected view of exposure across internal assets, vendor relationships, and regulatory obligations, with AI accelerating every step from discovery to remediation. The result is faster risk decisions, reduced operational complexity, and a measurably stronger security posture.

Average Rating: 4.6/5.0

Total Reviews: 7

How Do G2 Users Rate FortifyData AI-Powered Cyber GRC Platform?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.3/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind FortifyData AI-Powered Cyber GRC Platform?

  • Seller: FortifyData
  • Year Founded: 2015
  • HQ Location: Acworth, US
  • Twitter: @fortifydata
    85 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    19 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 38% Small

What Do G2 Reviewers Say About FortifyData AI-Powered Cyber GRC Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the quick and efficient support of FortifyData, enhancing their overall experience with the platform.
  • Users appreciate the deployment ease of FortifyData, noting its simple setup and user-friendly interface.
  • Users appreciate the ease of use of FortifyData, highlighting its simplicity in navigation and setup.
  • Users value the easy integrations of FortifyData, enhancing their experience with seamless setup and navigation.
  • Users find the easy setup of FortifyData AI-Powered Cyber GRC Platform greatly enhances their experience and productivity.

What Are Recent G2 Reviews of FortifyData AI-Powered Cyber GRC Platform?

What Are G2 Users Discussing About FortifyData AI-Powered Cyber GRC Platform?

RedHunt Labs ASM Platform

RedHunt Labs is a 360º Attack Surface Management platform that stands out by offering an unparalleled and all-encompassing solution. Our platform goes beyond traditional host and subdomain discovery, extending its reach to encompass a vast array of assets, including third-party SaaS clouds, Docker images, GitHub repositories, Postman collections, and more. With RedHunt Labs ASM Platform, an organization can - continuously track their exposure on the internet - keep an eye on External Supply Chain risks - manage vendor and subsidiary risk - find security issues before threat actors do.

Average Rating: 4.8/5.0

Total Reviews: 6

How Do G2 Users Rate RedHunt Labs ASM Platform?

  • Vulnerability Intelligence: 9.4/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.4/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 8.1/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind RedHunt Labs ASM Platform?

  • Seller: RedHunt Labs
  • Year Founded: 2019
  • HQ Location: London, GB
  • Twitter: @RedHuntLabs
    3,628 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    30 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Small, 33% Large

What Do G2 Reviewers Say About RedHunt Labs ASM Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time risk insights provided by RedHunt Labs ASM, enhancing their security measures effectively.
  • Users value the real-time visibility provided by RedHunt Labs ASM, enhancing their security insights and risk management.
  • Users value the proactive vulnerability identification of RedHunt Labs ASM, enhancing their security posture effectively and efficiently.
  • Users value the actionable intelligence provided by RedHunt Labs ASM Platform, enhancing customization and relevance of data.
  • Users value the alert notifications feature for proactively identifying security risks and safeguarding online assets efficiently.
Cons
  • Users find the dashboard usability issues challenging, wishing for more detailed alerts to assess risks effectively.
  • Users find the inefficient alert system lacking detail, which hinders their understanding of potential risks.
  • Users find the lack of native integrations a limitation, with a desire for better API and Okta SSO support.
  • Users feel the lack of detail in alerts hinders their understanding of risks and affects dashboard usability.
  • Users find the poor usability of RedHunt Labs ASM Platform challenging, especially regarding the dashboard and alerts.

What Are Recent G2 Reviews of RedHunt Labs ASM Platform?

Axonius

Axonius is the cybersecurity asset management platform that lets IT and Security teams see devices for what they are in order to manage and secure all.

Average Rating: 4.2/5.0

Total Reviews: 7

How Do G2 Users Rate Axonius?

  • Vulnerability Intelligence: 9.2/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 6.7/10 (Category avg: 8.7/10)
  • Ease of Admin: 7.8/10 (Category avg: 9.0/10)

Who Is the Company Behind Axonius?

  • Seller: Axonius
  • Year Founded: 2017
  • HQ Location: New York, US
  • Twitter: @AxoniusInc
    1,856 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    713 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 57% Large, 43% Medium

What Do G2 Reviewers Say About Axonius?

AI-generated summary from verified user reviews

Pros
  • Users value the visibility and intelligence of Axonius, effortlessly managing and identifying assets across their environment.
  • Users appreciate the centralized management of Axonius, enhancing visibility and simplifying asset identification across their environment.
  • Users value the enhanced visibility from Axonius, streamlining data management and improving asset identification significantly.
  • Users enjoy the ease of use of Axonius, praising its powerful queries and comprehensive visibility across environments.
  • Users praise the easy management of Axonius, simplifying data visibility and enhancing understanding of their environment.
Cons
  • Users find Axonius to have a steep learning curve, making initial use feel complex and overwhelming.
  • Users find the UI complex, especially for beginners, making it challenging to navigate and understand.
  • Users find the difficult learning curve of Axonius challenging, especially with complex queries and data integrations.
  • Users find Axonius to be expensive, which can be a drawback for budget-conscious organizations.
  • Users find Axonius to have a complex feature set, leading to confusion due to its steep learning curve.

What Are Recent G2 Reviews of Axonius?

What Are G2 Users Discussing About Axonius?

Brinqa

Brinqa is the only company that orchestrates the entire cyber risk lifecycle — understanding the attack surface, prioritizing vulnerabilities, automating remediation, and continuously monitoring cyber hygiene — across all security tools and programs. The Brinqa Attack Surface Intelligence Platform enables your organization to automate the cyber risk lifecycle across infrastructure, application and cloud security.

Average Rating: 3.6/5.0

Total Reviews: 15

How Do G2 Users Rate Brinqa?

  • Vulnerability Intelligence: 1.7/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 5.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 2.5/10 (Category avg: 8.7/10)
  • Ease of Admin: 5.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Brinqa?

  • Seller: brinqa
  • Year Founded: 2009
  • HQ Location: Austin, TX
  • Twitter: @brinqa
    476 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    102 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 80% Large, 20% Medium

What Are Recent G2 Reviews of Brinqa?

What Are G2 Users Discussing About Brinqa?

ImmuniWeb AI Platform

The ImmuniWeb AI Platform helps over 1,000 enterprise customers from more than 50 countries to test, secure and protect their web and mobile applications, APIs and microservices, cloud and networks, to prevent data breaches and reduce third-party risk, and to comply with regulatory requirements. ImmuniWeb’s products available on the Platform include Continuous Threat Exposure Management (CTEM), External Attack Surface Management (EASM), Dark Web Monitoring and phishing websites takedown, as well as vulnerability scanning and penetration testing for web and mobile apps, cloud and network infrastructure, and LLM models. Headquartered in Geneva, Switzerland, ImmuniWeb has offices in Washington, London and Dubai to provide an uninterrupted service to all global customers and partners.

Average Rating: 4.7/5.0

Total Reviews: 12

How Do G2 Users Rate ImmuniWeb AI Platform?

  • Vulnerability Intelligence: 8.3/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 9.2/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.3/10 (Category avg: 9.0/10)

Who Is the Company Behind ImmuniWeb AI Platform?

  • Seller: ImmuniWeb
  • Year Founded: 2019
  • HQ Location: Geneva, CH
  • Twitter: @immuniweb
    8,473 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    32 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 92% Medium, 8% Small

What Do G2 Reviewers Say About ImmuniWeb AI Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the effective vulnerability detection of ImmuniWeb AI Platform, significantly improving security and compliance efforts.
  • Users commend the responsive customer support, which offers prompt assistance and enhances the overall scanning experience.
  • Users value the continuous monitoring of the attack surface, ensuring proactive awareness of critical security issues.
  • Users value the continuous monitoring efficiency of ImmuniWeb AI Platform, ensuring proactive security and reducing potential losses.
  • Users value the alert notifications for keeping them informed about critical security issues and protecting their assets.
Cons
  • Users find the complexity of target scans leads to uncertain scanning times, complicating the overall experience.
  • Users face integration issues as ImmuniWeb AI Platform lacks connections with tools like Slack and PagerDuty.
  • Users find the lack of integration with Slack and PagerDuty complicates on-call support and accessibility after hours.
  • Users find the Excel export limited, which affects their data handling capabilities compared to the full JSON export.
  • Users note the limited flexibility in the algorithm for cost calculation, though improvements have been made.

What Are Recent G2 Reviews of ImmuniWeb AI Platform?

What Are G2 Users Discussing About ImmuniWeb AI Platform?

ThreatAware

ThreatAware is an agentless cyber hygiene platform that helps CISOs, CIOs, and SecOps leaders at mid-market and enterprises with 1,000+ devices to uniquely identify every network device and validate that key security controls are deployed, functioning and correctly configured. The platform addresses the visibility gap caused by a fragmented corporate perimeter, remote work models, and bring-your-own-device (BYOD) access. While typical enterprise cyber hygiene hovers between 70% and 80% due to untracked asset growth and control deterioration, ThreatAware closes this gap. Instead of relying on network-layer scanning or fragile metadata matching which can misidentify devices, ThreatAware uses patented Timeline Matching. This approach aligns behavioural timelines from multiple sources to deliver a 99%+ trusted asset hygiene posture with empirical proof. ThreatAware provides an automated solution for asset validation, helping teams find unknown devices on corporate networks, reconcile CrowdStrike and Intune data, or move away from manual spreadsheet reconciliation. It offers a modern alternative to legacy CAASM solutions and security control validation tools by tracking endpoint vitals on a continuous 60-minute loop to expose silent agent failures and configuration policy drift without deploying additional software agents. This automated single source of truth allows organizations to meet the strict continuous compliance demands of modern frameworks like DORA, NIS 2, and Cyber Essentials Plus. CORE PRODUCT CAPABILITIES - Identity-Layer Stealth Detection: Uncovers hidden endpoint blind spots, unprovisioned assets, and personal BYOD devices by reading authentication logs directly at the single sign-on (SSO) and identity provider level. - Independent Cross-Stack Validation: Normalises separate telemetry streams from directories, MDMs, and EDRs to confirm whether mandated security tools are actually deployed and active. - Continuous Vitals Monitoring: Tracks asset health on a continuous 60-minute loop to instantly flag silent agent failures, local policy drift, and broken communication heartbeats. - Patented Timeline Matching: Replaces brittle metadata registries by aligning multi-source behavioural timelines to uniquely identify every device. - Audit Readiness: Automates evidence collection to trace every performance metric directly back to source tool data, providing unbroken provenance for regulatory audits. USE CASES & SOLVED PROBLEMS - Exposing the "Intune Illusion": Security teams often treat MDM platforms as an absolute source of truth, ignoring that these agents are vulnerable to misconfigurations, silent crashes or BYOD bypasses. ThreatAware cross-references MDM registries against cloud application authentication streams and core directories to expose active control coverage gaps without relying on siloed vendor dashboards. - Eliminating Manual Spreadsheet Reconciliation: Manually extracting and cross-referencing device registries across tool consoles consumes up to 80 hours per cycle, creating static asset data that is obsolete immediately upon completion. ThreatAware automates the entire asset discovery lifecycle to maintain a live single source of truth, condensing audit and compliance preparation timelines from weeks to days. - Stopping Silent Agent Failures: Centralized dashboards frequently show misleading compliance metrics based on historical logs. This masks crashed agents, broken management heartbeats or localized policy drift. ThreatAware prevents these tracking deficits through continuous loop validation that directly queries the live operational status of endpoint controls every 60 minutes. TECHNICAL SPECIFICATIONS & PROFILE ATTRIBUTES Software Category: Cyber Asset Attack Surface Management (CAASM) and Cyber Asset Management platforms Deployment Framework: Built entirely as an Agentless Deployment Framework operating via secure, read-only APIs. Deployment Velocity: Rapid corporate deployment, enabling the platform architecture to go fully live within 1 hour. Data Ingestion Loops: Automated health logging with critical asset vitals tracked on a continuous 60-minute loop. Target Company Size: Developed for mid-market and enterprise organizations with at least 1,000+ active devices. Architecture Scalability: Proven in large-scale enterprise production environments with live deployments exceeding 250,000 devices. Supported Fabric Layers: Natively ingests data across Central Directories (Entra ID, Active Directory), CMDB registers, MDM, EDR, and SSO platforms. Evaluation Framework: Delivered through a low-friction, read-only API-driven Free Proof of Value (POV) Trial and comprehensive gap analysis.

Average Rating: 4.3/5.0

Total Reviews: 7

How Do G2 Users Rate ThreatAware?

  • Continuous Monitoring: 10.0/10 (Category avg: 9.2/10)
  • Ease of Admin: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind ThreatAware?

  • Seller: ThreatAware
  • Company Website:
  • Year Founded: 2019
  • HQ Location: London, GB
  • Twitter: @Threat_Aware
    170 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    49 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 86% Large, 14% Medium

What Are Recent G2 Reviews of ThreatAware?

ThreatConnect Risk Quantifier

Risk Quantifier (RQ) translates cyber risk into clear financial terms, allowing security leaders to prioritize defenses and communicate impact in the language of business. By mapping MITRE ATT&CK techniques and vulnerabilities to financial loss scenarios, RQ enables cost-justified security decisions. Together with TI Ops and Polarity, RQ ensures that operational efforts align to risk-based priorities — bridging the gap between threat activity and executive decision-making.

Average Rating: 4.6/5.0

Total Reviews: 5

How Do G2 Users Rate ThreatConnect Risk Quantifier?

  • Vulnerability Intelligence: 9.4/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Ease of Admin: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind ThreatConnect Risk Quantifier?

  • Seller: ThreatConnect
  • Year Founded: 2011
  • HQ Location: Arlington, US
  • Twitter: @ThreatConnect
    14,141 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    77 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Medium, 40% Large

What Do G2 Reviewers Say About ThreatConnect Risk Quantifier?

AI-generated summary from verified user reviews

Pros
  • Users commend the excellent customer service provided with ThreatConnect Risk Quantifier, enhancing their overall user experience.
  • Users value the ease of use of ThreatConnect Risk Quantifier, simplifying risk assessment and mitigation processes effectively.
  • Users value the easy integrations of ThreatConnect Risk Quantifier, enhancing risk insights and mitigation strategies effortlessly.
  • Users value the user-friendly platform of ThreatConnect Risk Quantifier, appreciating its exceptional performance and support.

What Are Recent G2 Reviews of ThreatConnect Risk Quantifier?

Truzta

Truzta is an AI-powered Compliance Automation & Security Platform that simplifies regulatory compliance and strengthens cybersecurity with proactive risk management. It automates SOC 2, ISO 27001, HIPAA, GDPR,NCA, SAMA,DPTM, PCI DSS, and more, while providing continuous monitoring, risk assessments, and automated evidence collection. With 200+ integrations, Truzta streamlines workflows, reduces audit timelines, and enables real-time threat detection for enhanced security. By unifying compliance and security, Truzta minimizes costs and ensures end-to-end protection—making audit readiness faster and hassle-free!

Average Rating: 4.9/5.0

Total Reviews: 54

How Do G2 Users Rate Truzta?

  • Vulnerability Intelligence: 10.0/10 (Category avg: 9.0/10)
  • Continuous Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Compliance Monitoring: 10.0/10 (Category avg: 8.7/10)
  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Truzta?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 44% Medium, 37% Small

What Do G2 Reviewers Say About Truzta?

AI-generated summary from verified user reviews

Pros
  • Users value the strong focus on compliance with Truzta, enhancing productivity and ensuring top-notch regulatory adherence.
  • Users value the strong focus on compliance of Truzta, enhancing productivity and ensuring regulatory adherence.
  • Users praise the incredible customer support of Truzta for its expertise and guidance throughout the implementation process.
  • Users find Truzta's ease of use greatly enhances their GRC program and simplifies the audit process.
  • Users value Truzta's end-to-end automation, significantly reducing manual work and enhancing compliance processes.
Cons
  • Users experience integration issues with Truzta, particularly with on-Prem systems and AWS Cloud Formation.
  • Users note that improvement is needed in workflow and integration options, especially for on-prem systems.
  • Users find the limited scope of Truzta frustrating, as it only supports cloud-based HRMS integration.
  • Users face challenges with cloud dependency, as Truzta currently only supports cloud-based HRMS integration, limiting flexibility.
  • Users express concerns about the lack of integration with on-prem systems, limiting flexibility and compatibility.

What Are Recent G2 Reviews of Truzta?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 10, 2026