Best Application Security Posture Management (ASPM) Software - Page 2

How Many Application Security Posture Management (ASPM) Software Products Does G2 Track?

Total Products under this Category: 50

Category Stats (Nov 2026)

  • Average Rating: 4.53/5 (↓0.02 vs Oct 2026) The average rating of products in this category, based on all submitted ratings

Last updated: November 01, 2026

How Does G2 Rank Application Security Posture Management (ASPM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 1,300+ Authentic Reviews
  • 50+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

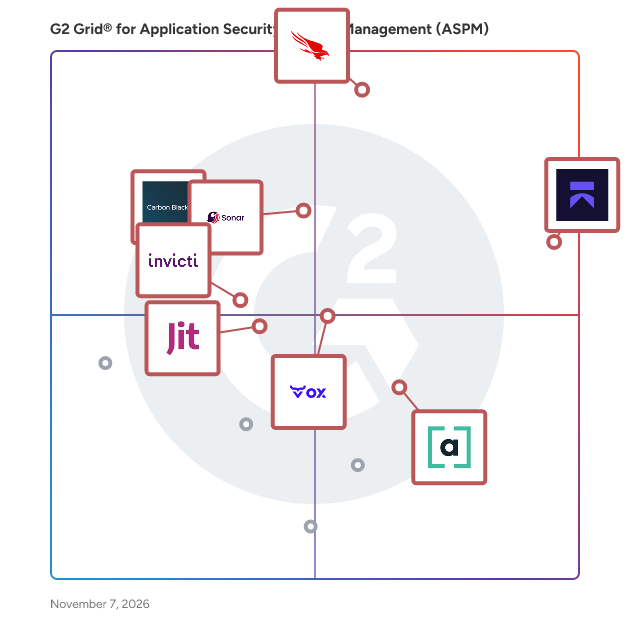
G2 Grid® for Application Security Posture Management (ASPM) Software

G2 Grid® for Application Security Posture Management (ASPM) Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, CrowdStrike Falcon Cloud Security, SonarQube, OX Security, Arnica, Invicti, Jit, and Carbon Black App Control.

Underlying data: [Grid® JSON](https://www.g2.com/categories/application-security-posture-management-aspm/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=sonarqube&focus%5B%5D=ox-security&focus%5B%5D=arnica&focus%5B%5D=invicti&focus%5B%5D=jit&focus%5B%5D=carbon-black-app-control)

Whitespots Security Portal

The ASPM (Application Security Posture Management) platform that runs on your infrastructure, not ours. Air-gapped if you need it. 🔌 Onboard an entire repo group with one webhook. No pipeline rewrites, no CI expertise, no repo left unscanned 🔎 30+ scanners out of the box across code, dependencies, secrets, IaC, domains, containers, hosts and cloud. Or plug in ANY tool you already pay for 🔥 Duplicates merged across tools, false positives stripped automatically. What survives is real 🧑‍💻 Findings land where developers already are: Jira, merge request comments, IDE ⏱️ Every finding gets an owning team and an SLA clock. Quality gate blocks the release when you say so 📈 One risk number for the board, WRT, tracked against a risk appetite you set 💶 Fixed price per organization. No per-developer maths, no per-seat surprises Your code never leaves your perimeter. The only outbound connection is license activation.

Average Rating: 5.0/5.0

Total Reviews: 10

Who Is the Company Behind Whitespots Security Portal?

Who Uses This Product?

  • Company Size: 60% Medium, 20% Small

What Do G2 Reviewers Say About Whitespots Security Portal?

AI-generated summary from verified user reviews

Pros
  • Users praise the effortless setup of Whitespots Security Portal, seamlessly integrating into their workflows without complications.
  • Users highlight the intuitive UI/UX and seamless integration of Whitespots Security Portal, enhancing workflow and efficiency.
  • Users value the speed and ease of integration of Whitespots Security Portal, enhancing their security workflow effortlessly.
  • Users appreciate the intuitive UI of Whitespots Security Portal, which enhances monitoring and response efficiency.
  • Users value the enhanced vulnerability detection of Whitespots, significantly improving overall security and monitoring efficiency.
Cons
  • Users note poor analytics in the Whitespots Security Portal, particularly for specialized management reports.
  • Users find the poor documentation challenging, particularly for advanced features and initial onboarding processes.
  • Users find the interface not always user-friendly, though support resolves issues upon request.

What Are Recent G2 Reviews of Whitespots Security Portal?

AccuKnox

AccuKnox Zero Trust CNAPP cloud security protects public and private clouds, Kubernetes and VMs. AccuKnox is a AI-powered Zero Trust Cloud Native Security Platform that helps organizations comply with various frameworks and over 33+ compliance controls, including MITRE, NIST, STIG, CIS, PCI-DSS, GDPR, and SOC2. AccuKnox enhances InfraSec and DevSecOps teams by enabling them to detect, prioritize, prevent and protect against advanced and sophisticated cloud attacks. Key Benefits 1. Code to Cloud Security 2. Easy Deployment 3. Extensive Coverage. 4. Preemptive Attack Mitigation 5. Open Source and Innovative Key Differentiators - Inline Preemptive Security (as opposed to Post-attack mitigation) - Secures modern workloads (Kubernetes) and traditional workloads (VMs) - Multi-Cloud, Private, Air-gapped, and Hybrid Cloud Security - IaC – Infrastructure As Code scanning - Secures AI/ML workloads like Jupyter Notebooks Features - Automated Zero Trust Cloud Security (Public, Private, Hybrid, Air-gapped) - Vulnerability Management & Prioritization - Run-time security, Micro-segmentation - Application Firewalling, Kernel Hardening - Drift Detection & Audit Trail - Continuous Diagnostics & Mitigation - GRC – CIS, HIPAA, GDPR, SOC2, STIG, MITRE, NIST - Securing Mission-Critical Workloads like Vault - Securing AI workbenches like Jupyter Notebooks - Cryptojacking and TNTBotinger Attacks With over 15+ patents, we're proud to offer an OpenSource, DevSecOps-led delivery model. To top it off, we have an ongoing R&D partnership with the esteemed SRI International. We deliver both Static and Runtime Security, anchored on innovations in Cloud Security and AI/ML-based Anomaly Detection. Static Code Analysis - Deeply analyze your code for vulnerabilities and weaknesses. CI/CD Pipelines Scanning - Continuously scan your pipelines for security flaws and risks. Container Security - Fortify your containers with robust security measures. Kubernetes Orchestration - Seamlessly manage and secure your Kubernetes environments. Secret Scanning - Detect and protect sensitive information from unauthorized access.

Average Rating: 4.4/5.0

Total Reviews: 12

Who Is the Company Behind AccuKnox?

  • Seller: Accuknox
  • Year Founded: 2020
  • HQ Location: California, USA
  • LinkedIn® Page: www.linkedin.com
    197 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 46% Large, 31% Medium

What Do G2 Reviewers Say About AccuKnox?

AI-generated summary from verified user reviews

Pros
  • Users praise the comprehensive security of AccuKnox, noting its robustness and customer-focused solutions for cloud management.
  • Users highlight the high security level of AccuKnox, ensuring comprehensive protection for cloud environments and applications.
  • Users value the easy cloud integration of AccuKnox, enhancing security for applications and maintaining compliance effortlessly.
  • Users value the continuous compliance capabilities of AccuKnox, ensuring robust security for cloud workloads and seamless integration.
  • Users praise the excellent customer support of AccuKnox for their quick responses and in-depth technical knowledge.
Cons
  • Users find the difficult learning curve of AccuKnox challenging, especially with its complex setup and Kubernetes requirements.
  • Users find the complex setup of AccuKnox challenging, particularly those with limited security expertise.
  • Users find AccuKnox to be cost prohibitive, which limits its accessibility for many potential users.
  • Users note the slow customer support, often requiring multiple follow-ups for assistance and troubleshooting.
  • Users find the complex setup and management of AccuKnox challenging, particularly for those lacking security expertise.

What Are Recent G2 Reviews of AccuKnox?

ArmorCode Unified Exposure Management

ArmorCode is redefining security governance in the AI era as the agentic control plane for Unified Exposure Management. Its Platform delivers software and infrastructure security governance that consolidates findings and prioritizes ones with real business impact, surfaces exploitability and attack paths, de-risks AI adoption, and accelerates compliance. ArmorCode's Agentic Control Plane helps enterprises manage security risk across today's heterogeneous environments. Powered by 
Anya Agents, an agentic workforce for enterprise security, it connects a Context Risk Graph to 400+ sources; unifying exposure management across infrastructure, software supply chains, applications, and AI systems; and delivering visibility, insight, and control without replacing existing tools. ArmorCode was founded in 2020 by Nikhil Gupta and is headquartered in Palo Alto, California. Trusted by dozens of Fortune 1000 enterprise customers, ArmorCode serves North America and EMEA with a team of 200+ employees.

Average Rating: 4.1/5.0

Total Reviews: 4

Who Is the Company Behind ArmorCode Unified Exposure Management?

  • Seller: ArmorCode
  • Year Founded: 2020
  • HQ Location: Palo Alto, California, United States
  • LinkedIn® Page: www.linkedin.com
    222 employees on LinkedIn®
  • Ownership: Dana Torgersen

Who Uses This Product?

  • Company Size: 50% Medium, 25% Large

What Do G2 Reviewers Say About ArmorCode Unified Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users value the enhanced security and streamlined vulnerability management provided by ArmorCode, boosting their overall efficiency.
  • Users value the enhanced security in ArmorCode, effectively managing vulnerabilities from development to deployment.
  • Users commend ArmorCode for its effective vulnerability identification, streamlining workflows and enhancing security throughout development and deployment.
  • Users value the automation features of ArmorCode for effortlessly enhancing security from development to deployment.
  • Users value the centralization of vulnerabilities in ArmorCode, enhancing workflows for security teams effectively.
Cons
  • Users find that ArmorCode requires improvement in scalability and customization for better data presentation and analysis.
  • Users find the reporting inadequate, noting accuracy issues and limited customization options in ArmorCode Unified Exposure Management.
  • Users find that the data presentation requires significant effort to clearly convey organizational risks effectively.
  • Users find the information overload from ArmorCode challenging, requiring significant effort to distill actionable insights.
  • Users note the limited customization options in reporting, leading to inaccuracies and less tailored insights.

What Are Recent G2 Reviews of ArmorCode Unified Exposure Management?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Apiiro

Apiiro is the leader in application security posture management (ASPM), unifying risk visibility, prioritization, and remediation with deep code analysis and runtime context. Get complete application and risk visibility: Apiiro takes a deep, code-based approach to ASPM. Its Cloud Application Security Platform analyzes source code and pulls in runtime context to build a continuous, graph-based inventory of application and software supply chain components. Prioritize with code-to-runtime context: With its proprietary Risk Graph™️, Apiiro contextualizes security alerts from third-party tools and native security solutions based on the likelihood and impact of risk to uniquely minimize alert backlogs and triage time by 95%. Fix faster and prevent risks that matter: By tying risks to code owners, providing LLM-enriched remediation guidance, and embedding risk-based guardrails directly into developer tools and workflows, Apiiro improves remediation times (MTTR) by up to 85%. Apiiro's native security solutions include API security testing in code, secrets detection and validation, software bill of materials (SBOM) generation, sensitive data exposure prevention, software composition analysis (SCA), and CI/CD and SCM security.

Average Rating: 4.8/5.0

Total Reviews: 2

Who Is the Company Behind Apiiro?

  • Seller: Apiiro
  • Year Founded: 2019
  • HQ Location: New York, New York, United States
  • LinkedIn® Page: www.linkedin.com
    135 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Apiiro?

What Are G2 Users Discussing About Apiiro?

Snyk Apprisk

Snyk AppRisk is a product offered by Snyk that enables Application Security teams to implement, manage, and scale a modern, high-performing, developer security program.

Average Rating: 4.3/5.0

Total Reviews: 2

Who Is the Company Behind Snyk Apprisk?

  • Seller: Snyk
  • HQ Location: Boston, Massachusetts
  • LinkedIn® Page: www.linkedin.com
    1,764 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Snyk Apprisk?

Cycode

Cycode’s AI-Native Application Security Platform unites security and development teams with actionable context from code to runtime to identify, prioritize, and fix the software risks that matter. Powered by proprietary scanners, third-party integrations, and the Context Intelligence Graph (CIG), Cycode delivers unified, correlated insight across the Software Factory. Its unique ability to sense, reason, and act with context in the AI-Era comes from its foundational convergence of AST, ASPM, and Software Supply Chain Security—purpose-built to secure both AI- and human-generated code.

Average Rating: 4.0/5.0

Total Reviews: 2

Who Is the Company Behind Cycode?

  • Seller: Cycode
  • Year Founded: 2019
  • HQ Location: New York, New York, United States
  • LinkedIn® Page: www.linkedin.com
    149 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Medium, 33% Large

What Are Recent G2 Reviews of Cycode?

Fluid Attacks

Implement Fluid Attacks' comprehensive, AI-powered solution into your SDLC and develop secure software without delays. As an all-in-one solution, Fluid Attacks accurately finds and helps you remediate vulnerabilities throughout the SDLC and ensures secure software development. The solution integrates its AI, automated tool, and team of pentesters to perform SAST, SCA, DAST, CSPM, SCR, PtaaS and RE to help you improve your security posture. This way, Fluid Attacks delivers accurate knowledge of the security status of your application. This means security goes alongside innovation without hindering your speed. Fluid Attacks provides you with expert knowledge about vulnerabilities and support options that enable you to remediate the security issues in your application.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Fluid Attacks?

  • Seller: Fluid Attacks
  • Year Founded: 2001
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    181 employees on LinkedIn®
  • Phone: +14154042154

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Fluid Attacks?

GuardBee

GuardBee scans websites, APIs, and AI applications for security issues (OWASP Top 10, SSL/TLS misconfigurations, exposed secrets, prompt-injection risk) and delivers modular, actionable reports. Built for teams shipping AI-powered products that need continuous security visibility without a dedicated pentest team.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind GuardBee?

  • Seller: GuardBee
  • Year Founded: 2026
  • HQ Location: İstanbul, TR
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of GuardBee?

Phoenix Security

Phoenix Security is a Contextual ASPM focused on product security. It combines risk-based Vulnerability Management, Application Security Posture Management, and Cloud into a risk and remediation-first platform. Phoenix was founded by the team running Application security and Cloud security posture for HSBC. What sets Phoenix apart is the risk-based quantitative view, the level of customization, and the scanning code to cloud vulnerabilities. Phoenix security utilizes threat intelligence, dependency analysis, and cloud analysis to detect which category of vulnerabilities needs to be addressed and minimize the false positives.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind Phoenix Security?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Phoenix Security?

Plexicus

Plexicus is the AI-native Application Security Posture Management (ASPM) platform with built-in Vibe Coding Security — purpose-built for the era of AI-assisted development. As developers ship more code, faster, with AI assistants like Cursor, Claude Code, Copilot, Windsurf, Devin, Replit, Zed, and VS Code, the volume of vulnerable code is outpacing every traditional AppSec tool. Plexicus closes that gap by replacing alert-only scanners with an autonomous remediation loop that detects, prioritizes, and fixes risks directly in the developer's Git workflow. Unlike fragmented point solutions that drown DevSecOps teams in findings, Plexicus unifies the full application risk surface — SAST, SCA, secrets, IaC, container, and AI-specific threats — and resolves them with proprietary GenAI agents that open the pull request to fix the code. The Plexicus Platform includes: 1. AI-Native ASPM — Correlates findings across SAST, SCA, secrets, IaC, and container scanners into a single prioritized risk view, then generates the PR that fixes the underlying issue. No more triage backlogs, no more swivel-chair between tools. 2. Vibe Coding Security — The industry's first security layer designed specifically for AI-generated code, with five capabilities: - IDE Guardrail — real-time security feedback inside Cursor, Claude Code, Copilot, Windsurf, and other AI coding tools. - MCP Security Scanner — protects Model Context Protocol integrations from prompt injection and tool abuse. - Hallucination & Slopsquatting Detector — catches non-existent or malicious packages invented by AI assistants. - Authz & Business-Logic Analyzer — surfaces the access-control and logic flaws that pattern-based scanners miss. - AI Provenance & AIBOM — tracks which code came from which AI tool, with full attestation for audits. 3. Compliance-grade evidence — SOC 2 Type II, NIS2, DORA Art. 28, CRA, and EU AI Act evidence packs out of the box. On the CPSTIC pathway. EU data residency by default. Key differentiator: automated remediation, not just visibility. While other AppSec tools focus on finding vulnerabilities, Plexicus focuses on resolving them. Proprietary GenAI remediation agents reduce Mean Time to Remediation (MTTR) by up to 90%, freeing DevSecOps teams from alert fatigue and letting AI-accelerated dev teams ship securely at the speed they actually code. Secure the vibe, patch the legacy. Visit https://www.plexicus.ai/ for more information.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Plexicus?

  • Seller: PLEXICUS
  • Year Founded: 2025
  • HQ Location: Bilbao, ES
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Plexicus?

Xygeni

Xygeni: AI-Native ASPM for the Software Supply Chain Xygeni is an AI-native ASPM (Application Security Posture Management) platform that unifies native and third-party security findings into one prioritized view. Its own detection engines cover SAST, SCA, DAST, Secrets, IaC, Container, CI/CD, and Build Security, and it also ingests results from tools like Snyk, Veracode, and Checkmarx so teams don't have to abandon what they've already invested in. Every finding, regardless of source, gets scored by exploitability, reachability, and business impact through Xygeni's Dynamic Funnels, which is what drives its reported 90% cut in alert noise. Two AI systems sit underneath the platform. CoreAI acts as a correlation and reporting layer for security leaders, turning scattered findings into a single risk narrative. DevAI works earlier, inside the developer's IDE and AI coding assistants, catching problems in both human-written and AI-generated code and proposing fixes before a pull request is even opened. On the supply chain side, Xygeni's MEW engine (Malware Early Warning) is built to catch malicious open-source packages the moment they hit a public registry, ahead of when a formal malware signature would normally exist. Shield takes that enforcement to the developer's own machine, blocking unauthorized package downloads at the OS level before they reach disk. Xygeni also runs a dedicated Code Quality engine across ten languages, ranking maintainability and complexity issues alongside security findings in the same console, so a team can see when the messiest file is also the riskiest one. The platform connects to GitHub, GitLab, Bitbucket, Jenkins, and Azure DevOps, and deploys as SaaS, on-premises, or fully air-gapped. Xygeni was named Hot Company in ASPM and in GenAI Application Security at the 2026 Global InfoSec Awards.

Average Rating: 4.6/5.0

Total Reviews: 4

Who Is the Company Behind Xygeni?

Who Uses This Product?

  • Company Size: 60% Small, 40% Medium

What Do G2 Reviewers Say About Xygeni?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive security of Xygeni, providing peace of mind and efficient vulnerability management in development.
  • Users value the contextual risk prioritization of Xygeni, enabling effective focus on critical security issues.
  • Users value the comprehensive risk management of Xygeni, enhancing security while maintaining efficient development cycles.
  • Users value the robust security features of Xygeni, which significantly enhance their development process and compliance.
  • Users highlight the seamless CI/CD integration of Xygeni, enhancing security without hindering development pace.
Cons
  • Users face difficult setup challenges with Xygeni, especially requiring manual adjustments for certain configurations.
  • Users note the steep learning curve for beginners, though support and documentation are helpful for navigation.

What Are Recent G2 Reviews of Xygeni?

Aegyn

Aegyn is a continuous security watchdog for applications built on Supabase. It connects to a project and runs daily scans for the misconfigurations that actually cause breaches: missing or permissive row level security policies, IDOR exposure through predictable identifiers, secrets left in reachable places, and tables that are writable when they should not be. Aegyn reports only new findings, so a daily mail is meaningful rather than noise, and each finding ships with ready-to-run SQL that closes the gap. A free instant scan is available without signing up: paste a project URL and see what an attacker would see from the outside.

Who Is the Company Behind Aegyn?

Amplify Security

Amplify Security created the agentic security harness, a new category of application security built for how software is actually written now, including the surge of AI-generated code. Rather than flagging problems after the fact, Amplify works autonomously inside the CI/CD pipeline to surface and remediate vulnerabilities before they ship. It deploys in the cloud or on-premises and fits existing developer workflows, giving security and engineering teams coverage that keeps pace with modern, high-velocity development.

Who Is the Company Behind Amplify Security?

Bionic

Bionic is an agentless Application Security Posture Management (ASPM) platform that provides unique visibility into the security, data privacy, and operational risk of applications running in production at scale. Bionic operates continuously and in real-time at the speed of CI/CD so that no application change, drift, or risk goes unnoticed by security, DevOps, and engineering teams. Bionic is the only solution that provides customers with a complete security posture of their applications, services, dependencies, APIs, and data flows within hybrid cloud production environments.

Who Is the Company Behind Bionic?

  • Seller: Bionic
  • Year Founded: 2011
  • HQ Location: Remote, Oregon, United States
  • LinkedIn® Page: www.linkedin.com
    10,347 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024