Best Malware Analysis Tools - Page 2

How Many Malware Analysis Tools Products Does G2 Track?

Total Products under this Category: 55

Category Stats (Sep 2026)

  • Average Rating: 4.51/5 The average rating of products in this category, based on all submitted ratings

Last updated: September 08, 2026

How Does G2 Rank Malware Analysis Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 2,200+ Authentic Reviews
  • 55+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

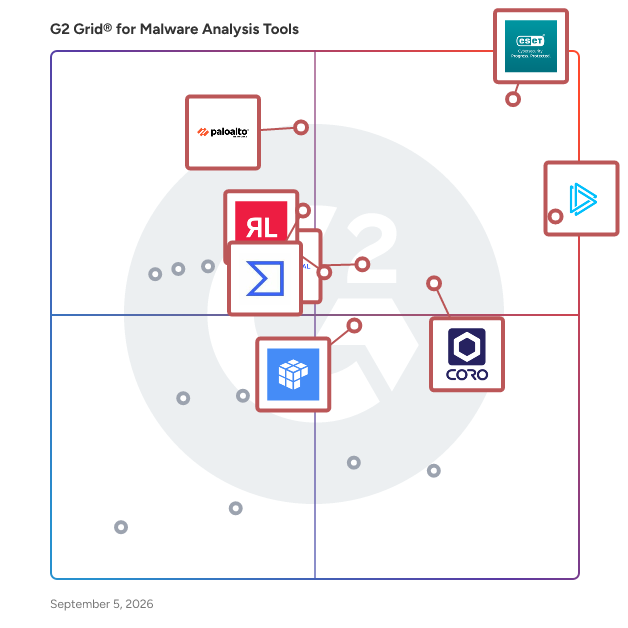
G2 Grid® for Malware Analysis Tools

G2 Grid® for Malware Analysis Tools plotting products by satisfaction and market presence

Highlighted products: ESET PROTECT, ANY.RUN Sandbox, Cloud-Delivered Security Services, Coro Cybersecurity, VirusTotal, Google VirusTotal, ReversingLabs, and Intezer.

Underlying data: [Grid® JSON](https://www.g2.com/categories/malware-analysis-tools/grids.json?focus%5B%5D=eset-protect&focus%5B%5D=any-run-sandbox&focus%5B%5D=cloud-delivered-security-services&focus%5B%5D=coro-cybersecurity&focus%5B%5D=virustotal&focus%5B%5D=google-virustotal&focus%5B%5D=reversinglabs&focus%5B%5D=intezer-intezer)

Hybrid Analysis

Hybrid Analysis provides free malware analysis service for the community that detects and analyzes unknown threats

Average Rating: 4.4/5.0

Total Reviews: 12

How Do G2 Users Rate Hybrid Analysis?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.3/10 (Category avg: 9.0/10)
  • Malware Detection: 9.3/10 (Category avg: 9.1/10)
  • File Analysis: 9.0/10 (Category avg: 9.0/10)

Who Is the Company Behind Hybrid Analysis?

Who Uses This Product?

  • Company Size: 50% Large, 33% Medium

What Are Recent G2 Reviews of Hybrid Analysis?

PolySwarm

PolySwarm is a more effective way to detect, analyze and respond to the latest malware threats, the ones more likely to go undetected. PolySwarm is a launchpad for new and innovative threat detection methods, where commercial solutions and specialized engines compete with each other to detect threats, and get compensated based on their performance.

Average Rating: 4.4/5.0

Total Reviews: 13

How Do G2 Users Rate PolySwarm?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.4/10 (Category avg: 9.0/10)
  • Malware Detection: 8.9/10 (Category avg: 9.1/10)
  • File Analysis: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind PolySwarm?

  • Seller: PolySwarm
  • Year Founded: 2017
  • HQ Location: San Diego, US
  • LinkedIn® Page: www.linkedin.com
    26 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 46% Small, 38% Medium

What Are Recent G2 Reviews of PolySwarm?

Cuckoo Sandbox

Cuckoo Sandbox is the leading open source automated malware analysis system.You can throw any suspicious file at it and in a matter of minutes Cuckoo will provide a detailed report outlining the behavior of the file when executed inside a realistic but isolated environment.

Average Rating: 4.3/5.0

Total Reviews: 14

How Do G2 Users Rate Cuckoo Sandbox?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 8.3/10 (Category avg: 9.0/10)
  • Malware Detection: 8.3/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Cuckoo Sandbox?

  • Seller: Cuckoo
  • Year Founded: 2010
  • HQ Location: N/A
  • Twitter: @cuckoosandbox
    13,677 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 57% Small, 36% Medium

What Are Recent G2 Reviews of Cuckoo Sandbox?

DeCYFIR by CYFIRMA

DeCYFIR is an AI-powered preemptive External Threat Landscape Management platform engineered to help organizations predict and prevent cyberattacks before they occur. Adopting a hacker's perspective, it delivers early warnings, prioritized insights, and actionable intelligence across the full external threat landscape. Built on a proprietary 9-pillar architecture — spanning Attack Surface Discovery & Intelligence, Vulnerability Intelligence & Threat Prioritization, Brand & Online Exposure Management, Digital Risk & Identity Protection, Third Party Risk Management, Situational Awareness & Emerging Threats, Predictive Threat Intelligence, Threat Adaptive Awareness & Training, and Sector Tailored Deception Intelligence. DeCYFIR correlates signals across all pillars to cut through noise, surface what is truly critical, and empower security teams to stay decisively ahead of emerging threats.

Average Rating: 4.8/5.0

Total Reviews: 49

How Do G2 Users Rate DeCYFIR by CYFIRMA?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind DeCYFIR by CYFIRMA?

  • Seller: CYFIRMA
  • Year Founded: 2017
  • HQ Location: Singapore, SG
  • Twitter: @cyfirma
    1,002 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    135 employees on LinkedIn®
  • Phone: marketing@cyfirma.com

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 53% Medium, 24% Large

What Do G2 Reviewers Say About DeCYFIR by CYFIRMA?

AI-generated summary from verified user reviews

Pros
  • Users value the thorough threat detection capabilities of DeCYFIR, enhancing cybersecurity measures against potential attacks.
  • Users value the informative threat intelligence from DeCYFIR, aiding in proactive prevention of cyber incidents.
  • Users value DeCYFIR for its contextual and predictive intelligence, enhancing threat visibility and strategic risk management.
  • Users value DeCYFIR's comprehensive threat intelligence features, enhancing proactive defense against cyber threats effectively.
  • Users value the advanced security insights from DeCYFIR, enhancing their ability to prevent and respond to threats.
Cons
  • Users find DeCYFIR not user-friendly, citing a confusing UI and technical complexity for less experienced individuals.
  • Users find DeCYFIR's interface to be complex and overwhelming, particularly for those unfamiliar with threat intelligence workflows.
  • Users find DeCYFIR's learning curve daunting, as its complexity may overwhelm new users without proper training.
  • Users find the platform's limited customization options challenging, impacting their overall user experience.
  • Users find DeCYFIR's complex setup challenging, particularly for newcomers and those needing customized dashboards or API integration.

What Are Recent G2 Reviews of DeCYFIR by CYFIRMA?

VIPRE Integrated Email Security

Todays zero-day threats, polymorphic malware and weaponized attachments demand a sophisticated multi-layered approach to keep businesses safe. VIPRE Email Security and suite of add-on solutions, delivered from the convenience of cloud-based architecture, is the secure choice for todays pervasive email threats. Processing over 1.2 billion emails a month. 50,000+ customers and 4,000+ partner. - Anti-spam & Antivirus - Outbound Email Scanning - Email Replay 90 Days - Large Message Handling - Advanced Policies - Custom Policies - DLP - Spoofing Protection - End-User Spam Reports - LDAP Integration - Always-On Continuity - Email Link Isolation - Email Analytics - Attachment Sandboxing - Email Encryption - Remote Browser Isolation

Average Rating: 4.4/5.0

Total Reviews: 34

How Do G2 Users Rate VIPRE Integrated Email Security?

  • Has the product been a good partner in doing business?: 7.6/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 8.3/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind VIPRE Integrated Email Security?

  • Seller: VIPRE Security
  • Company Website:
  • Year Founded: 1994
  • HQ Location: Clearwater, FL
  • Twitter: @VIPRESecurity
    8,293 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    238 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services
  • Company Size: 49% Medium, 44% Small

What Are Recent G2 Reviews of VIPRE Integrated Email Security?

What Are G2 Users Discussing About VIPRE Integrated Email Security?

MetaDefender Cloud

MetaDefender Cloud is a cloud-native file security and malware analysis platform that detects, analyzes, and prevents threats before they execute. Built for individuals, security professionals, developers, and organizations, it combines multi-layer inspection, threat intelligence, and active file prevention in one unified platform, available from free individual use to full enterprise deployment. Core Features: • Metascan™ Multiscanning with 20+ AV engines for maximum detection coverage across known and emerging threats • Deep CDR™ file sanitization, removing embedded malicious content from files while preserving full usability • Adaptive Sandbox for behavioral zero-day malware analysis in an isolated environment • Predictive ALIN AI for machine learning-based pre-execution threat detection • Proactive DLP™ for identifying and protecting sensitive data within files before sharing or processing • File, URL, IP, domain, and hash reputation analysis for multi-vector threat intelligence • REST API and native integrations enable secure file workflows across DevSecOps pipelines, SaaS applications, cloud storage, and platforms such as Salesforce, Microsoft 365, Google Drive, SharePoint, Box, and Amazon S3. Enterprise Features: • Custom workflows and policy-based controls for granular access and automation • Private scanning and zero file retention for full data sovereignty • Enterprise reporting, dashboards, and organization management for centralized visibility • End-to-end encryption, mTLS, and IP range restrictions • SLA-backed availability and dedicated enterprise support • Supports compliance with HIPAA, PCI DSS, GDPR, NIST, ISO 27001, and AICPA SOC 2 Why MetaDefender Cloud: • Eliminates threats rather than only detecting them, reducing breach risk at the point of ingestion • Protects the full file lifecycle: uploads, downloads, sharing in transit, and storage at rest • Improves detection coverage and reduces false positives through multi-engine scanning • Enables fast integration with no infrastructure to manage and continuous threat intelligence updates • Free to get started, with enterprise-grade capabilities available as your security needs grow

Average Rating: 5.0/5.0

Total Reviews: 7

How Do G2 Users Rate MetaDefender Cloud?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind MetaDefender Cloud?

  • Seller: OPSWAT
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Tampa, Florida
  • Twitter: @OPSWAT
    7,257 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,185 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 57% Small, 43% Medium

What Are Recent G2 Reviews of MetaDefender Cloud?

VMRay

Sandboxing reinvented against the threats of today - and tomorrow. At VMRay, our purpose is to liberate the world from undetectable digital threats. Led by reputable cyber security pioneers, we develop best-of-breed technologies to detect and analyze unknown, evasive, and sophisticated threats that others miss. We empower organizations to accelerate analysis and response, automate security tasks, and build their own threat intelligence by providing the world’s best detection and analysis platform for malware and phishing threats. ___ The target audience for VMRay encompasses a wide range of organizations, including enterprises such as top technology firms, banks and financial organizations, leading manufacturing companies, accounting and consulting firms, managed security service providers (MSSPs), and government entities. These users face the daunting challenge of safeguarding sensitive data against increasingly sophisticated cyber threats. VMRay's unique technologies, based on the world’s most advanced sandbox which employs a hypervisor-based approach, enables users to observe malicious samples in a completely invisible environment. This capability not only enhances the accuracy and depth of threat detection but also ensures that security teams can analyze threats without interference from evasive tactics employed by cyber threat actors. By meticulously sorting, filtering, and prioritizing results, VMRay delivers clear and actionable reports that eliminate the noise often associated with advanced threat analysis. This clarity is crucial for security teams, as it allows them to focus on the highest-priority insights without being overwhelmed by irrelevant data. Furthermore, VMRay's integration capabilities enable seamless integrations with existing security tools, such as Endpoint Detection and Response (EDR) systems, Security Orchestration, Automation, and Response (SOAR) platforms, and Threat Intelligence platforms enhancing overall operational efficiency of SOC and CTRI teams, incident responders and threat hunters. In addition to its technological prowess, VMRay places a strong emphasis on privacy and data control. Unlike many competitors, VMRay does not share customer analysis reports, indicators of compromise (IOCs), and any kind of data with third parties, ensuring that sensitive information remains confidential. Customers have the flexibility to choose their data hosting locations (in Germany and the USA) and durations, which is particularly beneficial for organizations that must comply with stringent privacy regulations. This commitment to privacy, combined with VMRay's innovative solutions, positions the company as a trusted partner for organizations seeking to bolster their cyber resilience and enhance SOC maturity. Ultimately, VMRay's dedication to continuous innovation, coupled with its focus on delivering reliable and clear threat analysis, makes it a formidable player in the malware analysis landscape. By addressing the complexities of modern cyber threats with precision and clarity, VMRay empowers organizations to navigate the challenges of cybersecurity with confidence, ensuring they are well-equipped to defend against both current and future threats.

Average Rating: 4.6/5.0

Total Reviews: 7

How Do G2 Users Rate VMRay?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 8.7/10 (Category avg: 9.0/10)
  • Malware Detection: 9.0/10 (Category avg: 9.1/10)
  • File Analysis: 8.7/10 (Category avg: 9.0/10)

Who Is the Company Behind VMRay?

  • Seller: VMRay
  • Year Founded: 2013
  • HQ Location: Bochum, DE
  • Twitter: @vmray
    4,092 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    126 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 86% Large, 14% Small

What Do G2 Reviewers Say About VMRay?

AI-generated summary from verified user reviews

Pros
  • Users value the automation integrations of VMRay, enhancing their threat analysis and incident response efficiency.
  • Users commend the stellar customer support of VMRay, highlighting the team's responsiveness and expertise.
  • Users highlight the deployment ease of VMRay, appreciating its robust architecture and effective threat detection capabilities.
  • Users value the detailed analysis features of VMRay, benefiting from enhanced interaction and automation integration.
  • Users value the ease of use of VMRay, appreciating its intuitive interface and seamless integration capabilities.
Cons
  • Users find the difficult learning curve of VMRay challenging due to its less intuitive interface.
  • Users find the difficult setup of VMRay frustrating, especially with unclear processing failures for samples.
  • Users find VMRay expensive, but many believe it is worth the cost for its value and effectiveness.
  • Users report experiencing poor detection performance, occasionally missing important findings during scans with VMRay.
  • Users feel the need for a more intuitive interface to enhance the learning curve for VMRay.

What Are Recent G2 Reviews of VMRay?

BitNinja

State-of-the-art server security with an all-in-one platform BitNinja offers an advanced server security solution with a proactive and unified system designed to effectively defend against a wide range of malicious attacks. Breaking new ground, BitNinja will be the first server security tool that protects Windows servers. Main solutions: - Reduce the server load as a result of the real-time IP reputation, with a database of 100M+ IP addresses thanks to BitNinja’s Defense Network - Stop zero-day exploits with the WAF module, and BitNinja’s self-written rules - Remove malware quickly and prevent reinfections with the industry-leader malware scanner - Enable the AI Malware Scanner to remove malware than ever before - Identify possible backdoors in your system with the Defense Robot - Protect your server from brute-force attacks with the Log Analysis module that runs silently in the background - Regularly examine and clean your database with the Database Cleaner - Discover and eliminate vulnerabilities in your website at no additional cost with the SiteProtection module - Block spam accounts, prevent server blocklisting, and gain insights into outgoing spam emails with the Outbound - Spam Detection module powered by ChatGPT - Trap suspicious connections with Honeypots and block access through backdoors with the Web Honeypot BitNinja Security stops the latest attack types, including: - All types of malware - with the best malware scanner in the market - Brute-force attacks at both network and HTTP levels; - Vulnerability exploitation – CMS (WP/Drupal/Joomla) - SQL injection - XSS - Remote code execution - Zero-day attacks; - DoS (denial of service) attacks BitNinja Security makes it easy to secure web servers: - 1-line code installation - Fully automated operation keeps servers safe and eliminates human error - AI-powered community-driven worldwide Defense Network - Unified, intuitive Dashboard for your whole infrastructure - Easy server management with Cloud Configuration - Premium support with a maximum 5-min response time - The convenience of a robust CLI - API available for automation and reporting - Seamless integrations with a wide range of platforms like Enhance control panel, 360 Monitoring, and JetBackup. BitNinja is supported on THE PLATFORM and up, installed on the following Linux distributions: CentOS 7 and up 64 bit CloudLinux 7 and up 64 bit Debian 8 and up 64 bit Ubuntu 16.04 and up 64 bit RedHat 7 and up 64 bit AlmaLinux 8 64 bit VzLinux 7 and up 64 bit Rocky Linux 8 64 bit Amazon Linux 2 64 bit Windows 2012 RE and newer

Average Rating: 4.6/5.0

Total Reviews: 20

How Do G2 Users Rate BitNinja?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 8.8/10)
  • Malware Evaluation: 6.7/10 (Category avg: 9.0/10)
  • Malware Detection: 8.3/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind BitNinja?

  • Seller: BitNinja Ltd.
  • Year Founded: 2014
  • HQ Location: Debrecen
  • Twitter: @bitninjaio
    1,079 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    24 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Internet
  • Company Size: 88% Small, 8% Medium

What Are Recent G2 Reviews of BitNinja?

What Are G2 Users Discussing About BitNinja?

Emsisoft Business Security

Emsisoft Business Security is a powerful Windows cybersecurity solution that protects small and medium sized businesses from online threats. Featuring a full suite of multi-layered real-time protection components - including behavioral analysis, machine learning and anti-ransomware technologies - Emsisoft Business Security provides complete protection from known and emerging threats.

Average Rating: 4.8/5.0

Total Reviews: 6

How Do G2 Users Rate Emsisoft Business Security?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.3/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 9.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Emsisoft Business Security?

  • Seller: Emsisoft
  • Year Founded: 2003
  • HQ Location: Nelson,New Zealand
  • Twitter: @emsisoft
    6,024 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    20 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Medium, 50% Small

What Are Recent G2 Reviews of Emsisoft Business Security?

Remnux

REMnux® is a Linux toolkit for reverse-engineering or otherwise examining malicious software. It provides a curated collection of free tools created by the community. Malware analysts can start using them without having to find, install, and configure them.

Average Rating: 3.7/5.0

Total Reviews: 6

How Do G2 Users Rate Remnux?

  • Has the product been a good partner in doing business?: 5.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 9.4/10 (Category avg: 9.0/10)
  • Malware Detection: 7.2/10 (Category avg: 9.1/10)
  • File Analysis: 8.9/10 (Category avg: 9.0/10)

Who Is the Company Behind Remnux?

  • Seller: Remnux
  • HQ Location: N/A
  • Twitter: @REMnux
    6,400 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small, 17% Medium

What Are Recent G2 Reviews of Remnux?

Joe Sandbox

Joe Security specializes in the development of malware analysis systems for malware detection and forensics. Based on the idea of deep malware analysis & multi-technology platform, Joe Security has developed unique technologies to analyze malware in a depth previously not possible. Joe Security provides malware analysis systems as a cloud service or as a standalone software package on premise.

Average Rating: 4.7/5.0

Total Reviews: 5

How Do G2 Users Rate Joe Sandbox?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 8.8/10)
  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 9.4/10 (Category avg: 9.1/10)
  • File Analysis: 9.4/10 (Category avg: 9.0/10)

Who Is the Company Behind Joe Sandbox?

  • Seller: Joe Security
  • Year Founded: 2011
  • HQ Location: Reinach, CH
  • Twitter: @joe4security
    7,830 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 20% Medium

What Are Recent G2 Reviews of Joe Sandbox?

What Are G2 Users Discussing About Joe Sandbox?

Comodo Valkyrie

Valkyrie is a file verdict system. Different from traditional signature based malware detection techniques Valkyrie conducts several analysis using run-time behavior and hundreds of features from a file and based on analysis results can warn users against malware undetected by classic Anti-Virus products.

Average Rating: 3.8/5.0

Total Reviews: 3

How Do G2 Users Rate Comodo Valkyrie?

  • Has the product been a good partner in doing business?: 7.5/10 (Category avg: 8.8/10)
  • Malware Evaluation: 8.3/10 (Category avg: 9.0/10)
  • Malware Detection: 8.3/10 (Category avg: 9.1/10)
  • File Analysis: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Comodo Valkyrie?

  • Seller: Xcitium
  • Year Founded: 2018
  • HQ Location: Clifton, NJ
  • LinkedIn® Page: www.linkedin.com
    681 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Are Recent G2 Reviews of Comodo Valkyrie?

Zemana AntiMalware

Scan your PC in fast and effective way for malware, spyware, virus detection and removal. Detects and removes annoying browser add-on's, adware, unwanted apps and toolbar and any type of malware on your PC.

Average Rating: 4.7/5.0

Total Reviews: 3

How Do G2 Users Rate Zemana AntiMalware?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 8.8/10)
  • Malware Evaluation: 8.3/10 (Category avg: 9.0/10)
  • Malware Detection: 9.2/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind Zemana AntiMalware?

  • Seller: Zemana
  • Year Founded: 2007
  • HQ Location: Ankara, TR
  • Twitter: @Zemana
    10,266 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Zemana AntiMalware?

IObit Cloud

IObit Cloud is an advanced automated threat analysis system. We use the latest Cloud Computing technology and Heuristic Analyzing mechanic to analyze the behavior of spyware, adware, trojans, keyloggers, bots, worms, hijackers and other security-related risks in a fully automated mode.

Average Rating: 4.3/5.0

Total Reviews: 2

How Do G2 Users Rate IObit Cloud?

  • Malware Evaluation: 9.2/10 (Category avg: 9.0/10)
  • Malware Detection: 10.0/10 (Category avg: 9.1/10)
  • File Analysis: 8.3/10 (Category avg: 9.0/10)

Who Is the Company Behind IObit Cloud?

  • Seller: IObit Undelete
  • Year Founded: 2004
  • HQ Location: N/A
  • Twitter: @IObitSoft
    8,077 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    130 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 50% Small

What Are Recent G2 Reviews of IObit Cloud?

Avira Cloud Sandbox

The Avira Cloud Sandbox API enables security vendors and service providers to submit files and receive detailed threat intelligence reports containing a complete threat assessment.

Average Rating: 3.5/5.0

Total Reviews: 1

How Do G2 Users Rate Avira Cloud Sandbox?

  • Malware Evaluation: 10.0/10 (Category avg: 9.0/10)
  • Malware Detection: 8.3/10 (Category avg: 9.1/10)
  • File Analysis: 6.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Avira Cloud Sandbox?

  • Seller: Gen Digital
  • Year Founded: 2022
  • HQ Location: Tempe, Arizona
  • Twitter: @GenDigitalInc
    4,481 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,497 employees on LinkedIn®
  • Ownership: NASDAQ: GEN

Who Uses This Product?

  • Company Size: 100% Small
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024