Best Zero Trust Networking Software - Page 9

How Many Zero Trust Networking Software Products Does G2 Track?

Total Products under this Category: 158

Category Stats (Oct 2026)

  • Average Rating: 4.49/5 (↑0.01 vs Sep 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Venn (+4.77%) - Among all products in this category, Venn recorded the largest rating increase compared to last month

Last updated: October 25, 2026

How Does G2 Rank Zero Trust Networking Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 8,300+ Authentic Reviews
  • 158+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

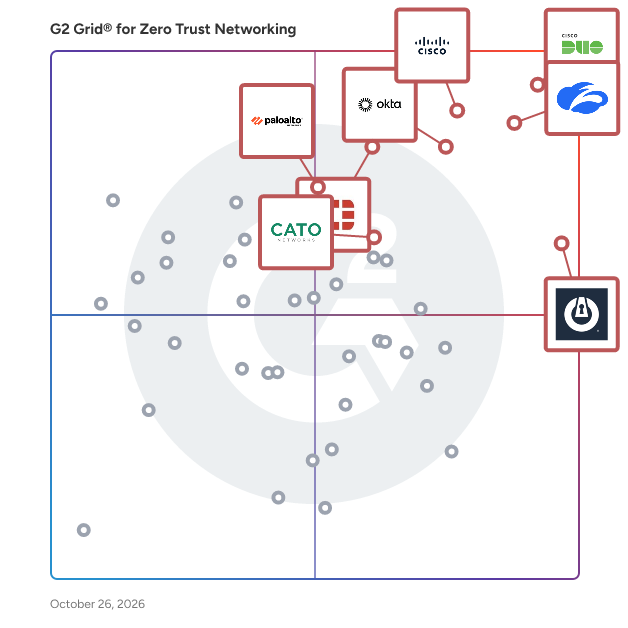
G2 Grid® for Zero Trust Networking Software

G2 Grid® for Zero Trust Networking Software plotting products by satisfaction and market presence

Highlighted products: Cisco Duo, Zscaler Private Access, Cisco Secure Access, ThreatLocker Zero Trust Platform, Okta, FortiClient, Cato SASE Cloud, and Palo Alto Networks IoT/OT Security.

Underlying data: [Grid® JSON](https://www.g2.com/categories/zero-trust-networking/grids.json?focus%5B%5D=cisco-duo&focus%5B%5D=zscaler-private-access&focus%5B%5D=cisco-secure-access&focus%5B%5D=threatlocker-zero-trust-platform&focus%5B%5D=okta&focus%5B%5D=forticlient&focus%5B%5D=cato-networks-cato-sase-cloud&focus%5B%5D=palo-alto-networks-iot-ot-security)

Mamori Server

Mamori Server is an all-in-one data security solution that integrates ZTNA, 2FA, DAM, PAM, SQL Firewall and data privacy solutions that helps businesses prevent cyber attacks and data theft, helps meet compliance and cyber insurance requirements, and simply DevOps & access to resources.

Who Is the Company Behind Mamori Server?

Mesh Security Zero Trust Posture Management Platform

Mesh Security is the industry's first ZTPM (Zero Trust Posture Management) solution, empowering modern enterprises with continuous, holistic hardening, detection, and auto-response across everything. Mesh seamlessly supercharges your existing stack and teams, enabling to easily drive a holistic Zero Trust posture. Mesh performs a holistic and deep assessment across identities, multi-cloud, SaaS, and data, correlating extended security signals to trace pre-breach and real-time critical infiltration vectors attackers use. It provides context and automation tools to bridge SecOps, IAM, DevOps, and SOC teams, fostering unified defense against evasive risks and threats invisible to other tools. With Mesh, you can drive a Zero-Trust posture and culture across your entire digital landscape, resulting in a resilient, efficient, and compliant organization.

Who Is the Company Behind Mesh Security Zero Trust Posture Management Platform?

MetaAccess

Zero-Trust Access (ZTA), an approach that considers all entities untrusted by default, is rapidly becoming the industry standard and being mandated by regulatory bodies including governments. Leveraging the latest ZTA technologies, OPSWAT’s MetaAccess Zero-Trust Access Platform is a unified platform cloud solution for providing deep endpoint compliance, advanced endpoint protection, identity authorization, and secure access without hindering workflows. MetaAccess delivers security compliance, visibility, and control to every device and user accessing enterprise resources. Based upon the Software Defined Perimeter Technology (SDP), it examines devices to make sure that they are secure, with the required security controls installed. It then goes much deeper by doing the most comprehensive device posture check in the industry. The MetaAccess Vulnerability Management Module enables the MetaAccess Platform to detect and report vulnerabilities in installed software on the device including 3rd party applications and critical OS security patches. MetaAccess detects more than 27,000 CVEs and displays the Known Exploited Vulnerabilities (KEV) as posted by CISA that are relevant to the specific endpoint. The MetaAccess Patch Management module enables the MetaAccess Platform to provide a remediation process for required vulnerability patches. MetaAccess detects vulnerabilities on more than 700 third party applications, auto-patching more than 150 of these. On the security side, MetaAccess provides removable media protection and executes a multi-scan of more than 20 Anti-Virus engines as well as protects against keyloggers, screen capture and copy and paste. Only once MetaAccess has ensured that the endpoint device is both compliant and secure, will the user be authorized through an integrated IAM (identity authorization management) solution and be given access to corporate resources based on a policy of least-privilege access, that is only to those resources to which the user is entitled.

Average Rating: 3.9/5.0

Total Reviews: 14

How Do G2 Users Rate MetaAccess?

  • Quality of Support: 5.7/10 (Category avg: 8.9/10)
  • Ease of Use: 7.7/10 (Category avg: 8.9/10)
  • Ease of Admin: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind MetaAccess?

  • Seller: OPSWAT
  • Year Founded: 2002
  • HQ Location: Tampa, Florida
  • Twitter: @OPSWAT
    7,257 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,185 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 43% Medium, 36% Large

What Are Recent G2 Reviews of MetaAccess?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Microsoft Entra Private Access

Microsoft Entra Private Access is an identity-centric Zero Trust Network Access (ZTNA solution designed to provide secure and seamless connectivity to private applications and resources, regardless of their location—on-premises or across any cloud. By eliminating the need for traditional VPNs, it enhances security by enforcing least-privilege access and preventing lateral movement within networks. This approach ensures that users can efficiently and securely access the applications they need from any device and any network, aligning with modern security principles. Key Features and Functionality: - Zero Trust Access: Enforces adaptive Conditional Access policies, including multifactor authentication (MFA, location-based security, and least-privilege access, without requiring changes to existing applications or resources. - Seamless User Experience: Provides fast and easy access to private apps through Microsoft's global private network, enhancing productivity for users working remotely or in hybrid environments. - Broad Protocol Support: Supports secure connectivity across various operating systems and accommodates any port and protocol, including RDP, SSH, SMB, FTP, and other TCP/UDP-based protocols. - Integration with Existing Security Services: Integrates with Microsoft Entra ID Governance and Privileged Identity Management (PIM to secure just-in-time access to sensitive resources for privileged users. - Simplified Deployment: Offers Quick Access policies to facilitate the transition from legacy VPNs, allowing for easy onboarding and network segmentation without extensive configuration. Primary Value and User Solutions: Microsoft Entra Private Access addresses the challenges associated with traditional VPNs by providing a modern, secure, and efficient method for accessing private applications. It reduces operational complexity and costs, enhances security by enforcing strict access controls, and improves user productivity through seamless and fast connectivity. By adopting this solution, organizations can effectively implement Zero Trust principles, ensuring that access to private resources is both secure and user-friendly.

Who Is the Company Behind Microsoft Entra Private Access?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • Twitter: @microsoft
    13,091,739 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT

NetLinkz

Netlinkz Limited is an Australian technology company specializing in secure, high-performance network solutions designed to meet the evolving needs of businesses worldwide. Their flagship product, VSN+ (Virtual Secure Network Plus, offers an end-to-end network security solution that ensures seamless and protected connectivity for enterprises of all sizes. By leveraging software-driven networking, VSN+ provides operational agility, rapid scalability, and uncompromised security, enabling businesses to adapt swiftly to changing demands without the need for specialized hardware. Additionally, Netlinkz has partnered with leading satellite providers to offer the Netlinkz Satellite Portal, a centralized management platform that allows resellers to efficiently oversee customer networks, equipment, and usage plans. Through these innovative solutions, Netlinkz empowers organizations to enhance their network performance, secure critical data, and achieve sustainable growth in today's digital landscape. Key Features and Functionality: - Blistering Speed and Connectivity: VSN+ is engineered to perform optimally across various network speeds, from small business Wi-Fi to data center fiber, ensuring that encryption does not degrade network performance. - Operational Agility: As a purely software-driven solution, VSN+ allows for easy configuration and rapid adaptation to evolving business challenges, growth, and scale. - Security Without Compromise: VSN+ provides end-to-end security solutions, including zero trust architecture, network segmentation, and 256-bit encryption, safeguarding business-critical data. - Rapid Scalability: Businesses can scale their networks to new locations locally or internationally without the need for bespoke hardware or specific service providers, using any ISP or connectivity method required. - Secure Access from Anywhere: VSN+ enables private connectivity to applications in the cloud or data centers from any location, with fully encrypted data in transit and intelligent network configuration capabilities to grant staff access only to necessary applications. Primary Value and Solutions Provided: Netlinkz's VSN+ addresses the critical need for secure, flexible, and high-performance network connectivity in the modern business environment. By offering a software-driven approach, it eliminates the reliance on specialized hardware, reducing costs and complexity. The solution ensures that businesses can maintain robust security measures without compromising on speed or scalability, enabling them to adapt to market changes and expand operations seamlessly. Furthermore, the Netlinkz Satellite Portal enhances the management of satellite-based networks, providing resellers with comprehensive oversight and control, thereby improving service delivery and customer satisfaction.

Who Is the Company Behind NetLinkz?

  • Seller: NetLinkz
  • Year Founded: 2004
  • HQ Location: Pyrmont, AU
  • LinkedIn® Page: www.linkedin.com
    14 employees on LinkedIn®
  • Ownership: ASX: NET

Netskope Private Access

Who Is the Company Behind Netskope Private Access?

  • Seller: Netskope
  • Year Founded: 2012
  • HQ Location: Santa Clara, CA
  • Twitter: @Netskope
    11,290 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3,402 employees on LinkedIn®

Netwrix Privilege Secure

Netwrix Privilege Secure is an advanced Privileged Access Management (PAM) solution designed to enhance organizational security by eliminating standing privileges and implementing just-in-time access controls. Rather than granting access for a set time window while the privileged account stays active, it dynamically creates temporary, task-specific accounts only when needed and removes them immediately after use, whether by disabling the account or deleting it entirely. This significantly reduces the attack surface and mitigates risks associated with persistent administrative accounts. Key Features and Functionality: - Zero Standing Privilege: Eliminates permanent administrative accounts by granting temporary, task-specific access, which is revoked upon task completion. - Agentless Discovery: Continuously scans the environment without agents to identify and remediate unmanaged privileged accounts, preventing privilege sprawl. - Granular Privilege Control: Provides precise control over user permissions, ensuring users have only the necessary rights for specific tasks, thereby preventing unauthorized actions. - Session Monitoring and Auditing: Records and monitors all privileged sessions with detailed logs and session playback, facilitating compliance reporting and forensic analysis. - Secure Remote Access: Enables secure, VPN-less, browser-based access to critical systems, verified with multi-factor authentication (MFA) and fully monitored to ensure security. - Endpoint Privilege Management: Removes standing local administrative rights from endpoints and grants elevated access only when needed, whether through just-in-time local admin access or task-specific application elevation, to prevent malware and ransomware attacks while maintaining user productivity. - Primary Value and Problem Solved: Netwrix Privilege Secure addresses the critical challenge of managing and securing privileged access within organizations. By implementing a zero standing privilege model, it minimizes the risk of unauthorized access and lateral movement by attackers. The solution ensures that privileged access is granted only when necessary, for the exact duration required, and with the least privilege necessary to perform the task. This approach not only enhances security but also simplifies compliance with regulatory requirements by providing comprehensive monitoring and auditing capabilities. Additionally, its agentless discovery and secure remote access features streamline administrative processes, reducing operational overhead and improving overall efficiency.

Who Is the Company Behind Netwrix Privilege Secure?

  • Seller: Netwrix
  • HQ Location: Irvine, CA
  • Twitter: @Netwrix
    2,912 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    757 employees on LinkedIn®

Oxidize

Oxidize is a zero trust security platform for company-issued employee devices, from Oxidize Labs Inc. at oxd.sh. 39 security modules run from one endpoint agent and one console, and enforcement is agentic: every control starts in observe mode, learns a baseline from your own traffic, promotes itself to enforcement once validated, and stands itself back down when live false positives rise. Administrators pin or override any control, and every action is policy-scoped, reversible, and audited. That enforcement covers AI agents, not just people. Oxidize discovers shadow MCP servers, controls what coding agents and AI tools send outbound through an authenticated egress path, governs the non-human identities they run as, and detects prompt injection in inspected traffic. Capabilities: - Zero trust access: per-application, evaluated against identity, device posture, and network conditions, with a kill switch that fails closed when the tunnel drops. - Secure web gateway and CASB, DNS filtering including DoH and DoT, and network-path DLP with OCR, exact data matching, and fingerprinting. - TLS inspection, applied only to destinations matching your policy and only on devices that trust your organization CA. - Email security: business email compromise, impersonation, and phishing detection for Microsoft 365 and Google Workspace. - Endpoint response: kill a process, isolate a host, quarantine a file. Remote browser isolation for risky sites. - Compliance evidence for SOC 2, ISO 27001, HIPAA, PCI DSS, NIST 800-53, GDPR, and CIS Controls, assessed from live telemetry. Oxidize produces evidence; it does not certify your organization. How it works. The agent builds an encrypted tunnel, OxTunnel, to a regional Oxidize relay, where policy, inspection, and detection run inline in a single pass rather than through a chain of third-party proxies. OxTunnel is not a WireGuard derivative: ChaCha20-Poly1305 with the header and connection ID authenticated, a hybrid post-quantum handshake combining X25519 with ML-KEM-768, and relay identity signed with both Ed25519 and ML-DSA-65. The datapath is first-party, the relay uses AF_XDP kernel bypass on supported network cards, and the detection models are trained and signed by Oxidize, so a model update that fails signature verification never loads. Inbox security sits in the same platform, where comparable secure service edge products sell email separately, as an add-on, or through a partner. Scope. Windows, macOS, and Linux. iOS and Android clients are built and pending release approval, so they are not yet installable. Trials stay observe-only. Best fit: 100 to 10,000+ employee organizations whose staff run AI tools, coding agents, and MCP servers on company devices, and security teams consolidating point products onto one agent and one console. Pricing: per active user per month. Bandwidth, relay capacity, and management API calls are not billed separately, and one user covers unlimited devices.

Who Is the Company Behind Oxidize?
Oyster VPN

OysterVPN protects your online activity with military-grade encryption, ensuring your browsing remains secure and untraceable across all networks. -Encrypt your traffic to hide your IP address and internet activity -Access global content without limitations by changing your virtual location -Prevent data leaks with a built-in kill switch that maintains your anonymity

Who Is the Company Behind Oyster VPN?

Pexip Secure collaboration

Who Is the Company Behind Pexip Secure collaboration?

  • Seller: Pexip
  • Year Founded: 2012
  • HQ Location: Oslo, Norway
  • Twitter: @pexip
    4,124 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    329 employees on LinkedIn®

ProID Workforce Identity

Over 180 Customers and 170.000 Employees trust ProID Workforce Identity platform that provides a secure, passwordless and biometric-based digital identity management. It covers: • Multi-Factor Authentication - Secure and user-friendly login to systems and applications. • E-Signing & digitization of documents • Physical access & device control • Management platform for all users / tools / certificates autommating all processes and minimizing requirement towards admins. ProID Workforce Identity tools: • P r o I D M o b i l e An ultimate Employee App that combines maximum security with the use of Biometrics allowing the users to seamlessly log into various system & applications, sign documents and even emulate a contactless chip for use cases related to physical security and interaction with devices. • P r o I D S m a r t C a r d s ProID Smart Cards provide Multifunctional solutions for Secure employee identity, including: MFA, E-signatures and Physical Access. These cards integrate seamlessly with existing systems and support various contactless technologies. • B i t t r o n U S B H W t o k e n w i t h a p p Bittron combines the highest level of Security with the convenience of Mobile Authentication. It supports Passwordless login and Biometric verification, ensuring robust Security for sensitive operations. Supported use cases: - login to OS - login to VPN - login to Remote Desktop - login to various 3rd party applications (includig custom) - login to admin apps - electronic Signature / Seal (Documents, e-Precriptions, etc.) - contactless authentication (Attendance, Door/Elevator access, Canteen, etc.) - device authentication (Secure Printing, Manufacturing machines, etc.) Request a demo: https://proid.cz/en/demo-for-free/

Average Rating: 4.7/5.0

Total Reviews: 29

How Do G2 Users Rate ProID Workforce Identity?

  • Quality of Support: 9.5/10 (Category avg: 8.9/10)
  • Ease of Use: 9.4/10 (Category avg: 8.9/10)
  • Ease of Admin: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind ProID Workforce Identity?

  • Seller: MONET+
  • Year Founded: 1996
  • HQ Location: Zlín, Zlínský kraj
  • LinkedIn® Page: www.linkedin.com
    267 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Medium, 41% Small

What Do G2 Reviewers Say About ProID Workforce Identity?

AI-generated summary from verified user reviews

Pros
  • Users value the security features of ProID, appreciating passwordless authentication and seamless integration for workforce needs.
  • Users appreciate the flexible authentication options of ProID Workforce Identity, enjoying seamless integration and enhanced security.
  • Users highlight the easy setup of ProID Workforce Identity, making authentication incredibly convenient and user-friendly.
  • Users value the flexibility and security of the ProID Mobile app, making daily logins easy and effective.
  • Users value the data security of ProID Workforce Identity, ensuring reliable and seamless access across various platforms.
Cons
  • Users experience occasional delay issues due to forgetting to allow notifications, impacting the approval process.
  • Users experience a difficult learning curve initially, requiring time to adjust to the ProID Workforce Identity app.
  • Users experienced a learning curve initially, but adjustments made the app easier to use over time.
  • Users experience notification issues as some occasionally forget to enable them, causing delays in approvals.
  • Users experience process delays when notifications are overlooked, impacting timely approvals in ProID Workforce Identity.

What Are Recent G2 Reviews of ProID Workforce Identity?

What Are G2 Users Discussing About ProID Workforce Identity?

Proofpoint Meta

Proofpoint Meta providez the most effective cybersecurity and compliance solutions to protect people on every channel including email, the web, the cloud, and social media.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Proofpoint Meta?

  • Seller: Proofpoint
  • Year Founded: 2002
  • HQ Location: Sunnyvale, CA
  • Twitter: @proofpoint
    31,157 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5,261 employees on LinkedIn®
  • Ownership: NASDAQ: PFPT

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Proofpoint Meta?

What Are G2 Users Discussing About Proofpoint Meta?

remote.it

Who Is the Company Behind remote.it?

  • Seller: Amnimo
  • Year Founded: 2018
  • HQ Location: Tokyo, JP
  • LinkedIn® Page: www.linkedin.com
    10 employees on LinkedIn®

Revbits Zero Trust Network

Identify, Isolate, and Monitor Remote Network Connections in Real-time Moving the network perimeter to the endpoint RevBits Zero Trust Network (ZTN) helps isolate and protect your internal assets. As the network perimeter moves to where the user is, RevBits Zero Trust Network (ZTN) helps isolate and protect internal network assets without the necessity of implementing complicated network segmentation. RevBits ZTN focuses on protecting resources like network assets, applications, services, and accounts by trusting no one by default, whether inside or outside the network. The ease of implementing a zero-trust architecture has never been so simple.

Who Is the Company Behind Revbits Zero Trust Network?

Safe-T Secure Data Access

Deploying Safe-T SDA (Secure Data Access) allows performing network level logical segmentation as well as connecting cloud elements to ground elements, without the need to open any ports within the perimeter firewall, close firewalls located between two network segments, while allowing secured access through the internal firewall on an outbound firewall rule.

Who Is the Company Behind Safe-T Secure Data Access?

  • Seller: Safe-T
  • Year Founded: 2005
  • HQ Location: Sydney, AU
  • LinkedIn® Page: au.linkedin.com
    2 employees on LinkedIn®
  • Ownership: NASDAQ: SFET
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated April 9, 2026