Best Threat Intelligence Software for Small Business - Page 2

How Many Threat Intelligence Software Products Does G2 Track?

Total Products under this Category: 295

Category Stats (Nov 2026)

  • Average Rating: 4.59/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+0.63%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Threat Intelligence Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 9,300+ Authentic Reviews
  • 295+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

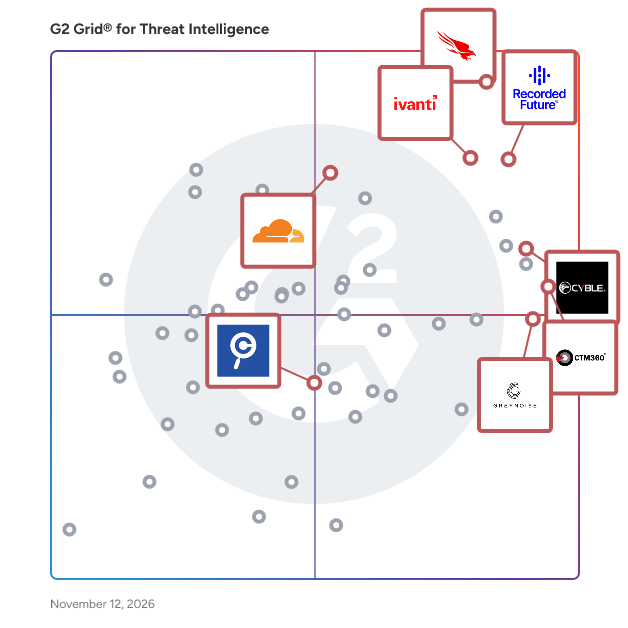
G2 Grid® for Threat Intelligence Software

G2 Grid® for Threat Intelligence Software plotting products by satisfaction and market presence

Highlighted products: Ivanti Autonomous Endpoint Management, CrowdStrike Falcon Endpoint Protection Platform, Recorded Future, Cloudflare Application Security and Performance, CTM360, GreyNoise, Cyble, and Criminal IP.

Underlying data: [Grid® JSON](https://www.g2.com/categories/threat-intelligence/grids.json?focus%5B%5D=ivanti-autonomous-endpoint-management&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=recorded-future&focus%5B%5D=cloudflare-application-security-and-performance&focus%5B%5D=ctm360-ctm360&focus%5B%5D=greynoise&focus%5B%5D=cyble&focus%5B%5D=criminal-ip-criminal-ip&segment=small-business)

DeCYFIR by CYFIRMA

DeCYFIR is an AI-powered preemptive External Threat Landscape Management platform engineered to help organizations predict and prevent cyberattacks before they occur. Adopting a hacker's perspective, it delivers early warnings, prioritized insights, and actionable intelligence across the full external threat landscape. Built on a proprietary 9-pillar architecture — spanning Attack Surface Discovery & Intelligence, Vulnerability Intelligence & Threat Prioritization, Brand & Online Exposure Management, Digital Risk & Identity Protection, Third Party Risk Management, Situational Awareness & Emerging Threats, Predictive Threat Intelligence, Threat Adaptive Awareness & Training, and Sector Tailored Deception Intelligence. DeCYFIR correlates signals across all pillars to cut through noise, surface what is truly critical, and empower security teams to stay decisively ahead of emerging threats.

Average Rating: 4.8/5.0

Total Reviews: 51

How Do G2 Users Rate DeCYFIR by CYFIRMA?

  • Security Validation: 9.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.1/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind DeCYFIR by CYFIRMA?

  • Seller: CYFIRMA
  • Year Founded: 2017
  • HQ Location: Singapore, SG
  • LinkedIn® Page: www.linkedin.com
    135 employees on LinkedIn®
  • Phone: marketing@cyfirma.com

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 50% Medium, 25% Large

What Do G2 Reviewers Say About DeCYFIR by CYFIRMA?

AI-generated summary from verified user reviews

Pros
  • Users value the clear outside-in view of threats provided by DeCYFIR, enhancing their understanding of vulnerabilities.
  • Users value the timely and actionable threat intelligence from DeCYFIR, enhancing their understanding and decision-making on risks.
  • Users appreciate DeCYFIR for its clear and proactive threat intelligence, enhancing their security strategies and decision-making.
  • Users value the outside-in view of threats DeCYFIR offers, enhancing understanding and proactive protection against cyber risks.
  • Users value DeCYFIR for its proactive threat insights, which significantly enhance organizational security and decision-making.
Cons
  • Users find the not user-friendly interface challenging, especially for first-time interactions and custom API creation.
  • Users find DeCYFIR's interface to have a complexity that overwhelms new users and lacks intuitive customization options.
  • Users find the platform complex and overwhelming, particularly without proper training in threat intelligence workflows.
  • Users find the limited customization of DeCYFIR's dashboards to be a barrier for effective usage and understanding.
  • Users find DeCYFIR to have a complex setup that can overwhelm new users unfamiliar with threat intelligence workflows.

What Are Recent G2 Reviews of DeCYFIR by CYFIRMA?

RiskProfiler - External Threat Exposure Management

RiskProfiler is an advanced cybersecurity platform purpose-built for Continuous Threat Exposure Management (CTEM). It unifies external, cloud, vendor, and brand risk intelligence into a single ecosystem—providing organizations with real-time visibility, contextual threat insights, and actionable remediation guidance. Through its integrated suite, External Attack Surface Managemnet, Third_party Risk Management, Cloud Attack Surface Management, and Brand Risk Protection; the platform continuously discovers, classifies, and evaluates external-facing assets and risks across the internet, multi-cloud environments, and third-party ecosystems. Powered by AI-enabled risk questionnaires, RiskProfiler automates the exchange, validation, and scoring of security assessments, dramatically accelerating third-party due diligence and compliance validation. The platform’s context-enriched graph engine correlates vulnerabilities, exposures, and configurations with real-world threat data, revealing how attackers might exploit an organization’s digital footprint. Its newly enhanced Cyber Threat Intelligence (CTI) module provides live insights into industry-specific attack trends, threat actor profiles, and evolving TTPs, directly embedded within the dashboard. By analyzing CVEs, IOCs, and exploit patterns, it maps these to relevant assets and potential attack paths, enabling focused, prioritized mitigation. From identifying exposed cloud resources across AWS, Azure, and Google Cloud to uncovering brand impersonation, phishing campaigns, or logo abuse, RiskProfiler delivers unified visibility and continuous monitoring that extends beyond the perimeter. It helps organizations anticipate, contextualize, and neutralize threats before they turn into breaches, transforming exposure management into a truly intelligent, predictive defense capability.

Average Rating: 5.0/5.0

Total Reviews: 135

How Do G2 Users Rate RiskProfiler - External Threat Exposure Management?

  • Security Validation: 10.0/10 (Category avg: 9.1/10)
  • Intelligence Reports: 10.0/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 10.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.9/10 (Category avg: 9.1/10)

Who Is the Company Behind RiskProfiler - External Threat Exposure Management?

  • Seller: Riskprofiler
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Rock Hill , US
  • LinkedIn® Page: www.linkedin.com
    35 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Security Consultant
  • Top Industries: Information Technology and Services, Design
  • Company Size: 65% Medium, 30% Small

What Do G2 Reviewers Say About RiskProfiler - External Threat Exposure Management?

AI-generated summary from verified user reviews

Pros
  • Users value the multi-dimensional threat intelligence of RiskProfiler, enabling efficient management of external threats and vendor risks.
  • Users value the seamless integration features of RiskProfiler, enhancing real-time monitoring and adaptability in their workflows.
  • Users praise the fast and efficient customer support of RiskProfiler, enhancing their overall experience and threat management.
  • Users value the ease of use of RiskProfiler, as it seamlessly integrates and enhances external threat management.
  • Users highlight the easy setup of RiskProfiler, facilitating quick implementation and seamless integration for effective threat management.
Cons
  • Users face a steep learning curve with RiskProfiler, needing sufficient time for training and customization.
  • Users find the complexity of RiskProfiler challenging, requiring time for training and adjustment to navigate effectively.
  • Users find the difficult learning curve challenging, requiring significant time and training for effective platform use.
  • Users find a steep learning curve with RiskProfiler, requiring time and training for effective use.
  • Users find the complex setup of RiskProfiler challenging, hindering smooth adoption and integration for non-specialist teams.

What Are Recent G2 Reviews of RiskProfiler - External Threat Exposure Management?

VulScan

Automated Vulnerability Scanning. Affordably Priced For Everyone! With almost 70 new hidden vulnerabilities identified every day, you would need to be a super hero with X-ray vision to find them all. Or, you can let VulScan do it for you. VulScan is purpose-built for MSPs and for IT Departments that handle their own IT security. It has all the features you need for both internal and external vulnerability management, but without all the complexity found in older solutions. Best of all, VulScan is priced so that cost is no longer a barrier to scanning as many assets as you need, as frequently as you want. That’s why our slogan is “Vulnerability Management For The Rest of Us! VulScan is an affordable cloud-based vulnerability management platform. It includes the software needed to spin up an unlimited number of virtual network scanner appliances using Hyper-V or VMWare, and a cloud-based portal to control the scanners and manage the discovered issues. For internal network scanning, the appliances can be installed on any existing computer that has excess capacity on the network, or installed on a dedicated box to be permanently installed. You can add multiple scanners and configure them each to scan separate parts of the network to get even faster results pushed into the same client site dashboard at no additional cost. For external scanning, the appliances are installed on the MSP’s data center or other remote location and “pointed” to the public facing IP addresses of the target network.

Average Rating: 4.1/5.0

Total Reviews: 121

How Do G2 Users Rate VulScan?

  • Security Validation: 8.1/10 (Category avg: 9.1/10)
  • Intelligence Reports: 7.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.1/10 (Category avg: 9.1/10)

Who Is the Company Behind VulScan?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 66% Small, 32% Medium

What Do G2 Reviewers Say About VulScan?

AI-generated summary from verified user reviews

Pros
  • Users love the ease of use of VulScan, praising its simple interface and intuitive scheduling for scanning and reporting.
  • Users value the thorough scanning and intuitive UI of VulScan, enhancing both ease of use and security insights.
  • Users value the detailed reporting features of VulScan, which provide actionable insights and facilitate client communication.
  • Users appreciate the in-depth reporting features of VulScan, enabling easy identification and justification of security vulnerabilities.
  • Users value the scanning efficiency of VulScan, appreciating its ease of use and comprehensive vulnerability reports.
Cons
  • Users criticize the inadequate reporting of VulScan, finding it overwhelming and lacking clear, actionable insights.
  • Users find the difficult UX of VulScan frustrating due to its outdated design and lack of organization features.
  • Users find the difficult setup of VulScan frustrating, with a confusing UI and cumbersome documentation requirements.
  • Users find the limited reporting options inadequate, complicating client communication and overall usability of VulScan.
  • Users are frustrated by the poor customer support from VulScan, experiencing delays and lack of resolution for issues.

What Are Recent G2 Reviews of VulScan?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

CrowdSec

CrowdSec is an open-source security stack that detects aggressive behaviors and prevents them from accessing your systems. Its user-friendly design and ease of integration into your current security infrastructure offer a low technical entry barrier and a high-security gain. Once an unwanted behavior is detected, it is automatically blocked. The aggressive IP, scenario triggered and the timestamp is sent for curation, to avoid poisoning & false positives. If verified, this IP is then redistributed to all CrowdSec users running the same scenario. By sharing the threat they faced, all users are protecting each other.

Average Rating: 4.7/5.0

Total Reviews: 84

How Do G2 Users Rate CrowdSec?

  • Security Validation: 8.8/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.8/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.7/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind CrowdSec?

  • Seller: CrowdSec
  • Year Founded: 2020
  • HQ Location: Paris, FR
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CTO
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 70% Small, 21% Medium

What Are Recent G2 Reviews of CrowdSec?

What Are G2 Users Discussing About CrowdSec?

CYREBRO

CYREBRO is an AI-native Managed Detection and Response solution, providing the core foundation and capabilities of a state-level Security Operations Center delivered through its cloud-based, interactive SOC Platform. CYREBRO rapidly detects, analyzes, investigates and responds to cyber threats, for businesses of all sizes.

Average Rating: 4.4/5.0

Total Reviews: 129

How Do G2 Users Rate CYREBRO?

  • Security Validation: 8.9/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind CYREBRO?

  • Seller: CYREBRO
  • Year Founded: 2013
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 64% Medium, 25% Small

What Do G2 Reviewers Say About CYREBRO?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of CYREBRO, enjoying straightforward navigation and quick access to critical investigations.
  • Users praise CYREBRO's highly responsive customer support, enhancing the overall experience and efficiency in issue resolution.
  • Users value the real-time alerts from CYREBRO, enhancing their ability to respond swiftly to cyber threats.
  • Users value the real-time alerts from CYREBRO, enhancing security and enabling quick, informed decision-making in threat management.
  • Users value the intuitive dashboard usability of CYREBRO for quick status visibility and efficient client monitoring.
Cons
  • Users report frequent update issues with CYREBRO, experiencing overwhelming alerts and integration difficulties during onboarding.
  • Users experience communication issues with CYREBRO, noting delays in support responses and vague initial ticket details.
  • Users experience poor customer support with delayed responses and vague details, impacting overall effectiveness and communication.
  • Users face dashboard issues with connectivity and limited features, complicating their overall experience with CYREBRO.
  • Users experience ineffective alerts due to overwhelming volume and vague details, impacting usability and clarity.

What Are Recent G2 Reviews of CYREBRO?

What Are G2 Users Discussing About CYREBRO?

Intezer

Intezer automates the entire alert triage process, like an extension of your team handling Tier 1 SOC tasks for every alert at machine-speed. Intezer monitors incoming incidents from endpoint, reported phishing pipelines, or SIEM tools, then autonomously collects evidence, investigates, makes triage decisions, and escalates only the serious threats to your team for human intervention. Power your SOC with artificial intelligence that makes sure every alert is deeply analyzed (including every single artifact like files, URLs, endpoint memory, etc.), detecting malicious code in memory and other evasive threats. Fast set up and integrations with your SOC team's workflows (EDR, SOAR, SIEM, etc.) means Intezer's AI can immediately start filtering out false positives, giving you detailed analysis about every threat, and speeding up your incident response time. With Intezer: • Reduce Tier 1 escalation, sending only 4% of alerts on average to your team for immediate action. • Identify up to 97% of false positive alerts without taking any time from your analysts. • Reduce average triage time to 5 minutes or less, while giving your analysts deep context about every alert to prioritize critical treats and respond faster.

Average Rating: 4.5/5.0

Total Reviews: 188

How Do G2 Users Rate Intezer?

  • Security Validation: 8.8/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.3/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Intezer?

  • Seller: Intezer
  • Company Website:
  • Year Founded: 2015
  • HQ Location: New York
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Student
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 54% Small, 24% Medium

What Do G2 Reviewers Say About Intezer?

AI-generated summary from verified user reviews

Pros
  • Users value the detection accuracy of Intezer, ensuring timely malware blocking and enhanced system security.
  • Users find Intezer to provide ease of use, enabling quick detection and proactive security measures for their systems.
  • Users appreciate the timely detection and blocking of malware by Intezer, enhancing their system security significantly.
  • Users value the effective malware detection of Intezer, ensuring timely security for their systems and peace of mind.
  • Users value the timely malware detection and blocking capabilities of Intezer, enhancing their overall system security.
Cons
  • Users report challenges due to the complex interface, which can hinder easy navigation and usability.
  • Users find the poor interface design of Intezer challenging, with small characters and various GUI issues.
  • Users find the UI challenging and difficult to read, noting small text and various GUI issues affecting usability.
  • Users find the lack of access control limits file visibility and can complicate collaborative efforts.
  • Users find it challenging to ensure data privacy, as file visibility control is limited in certain situations.

What Are Recent G2 Reviews of Intezer?

What Are G2 Users Discussing About Intezer?

Trellix Threat Intelligence Exchange

Trellix Threat Intelligence Exchange is a software that facilitates the real-time sharing, management, and integration of threat intelligence across an organization’s security infrastructure. The software enables automated detection and response to threats by correlating data from multiple security sources to identify malicious files, URLs, or other indicators of compromise. It centralizes threat intelligence, allowing security teams to enhance protection by leveraging collective data from endpoints, networks, and other systems. The software helps streamline workflows by reducing manual analysis and supports the investigation and containment of security incidents. Trellix Threat Intelligence Exchange is designed to address the challenge of timely threat identification and unified intelligence management in enterprise environments.

Average Rating: 4.0/5.0

Total Reviews: 52

How Do G2 Users Rate Trellix Threat Intelligence Exchange?

  • Security Validation: 8.8/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.1/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Trellix Threat Intelligence Exchange?

  • Seller: Trellix
  • Year Founded: 2004
  • HQ Location: Plano, TX
  • LinkedIn® Page: www.linkedin.com
    3,811 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Medium, 37% Small

What Are Recent G2 Reviews of Trellix Threat Intelligence Exchange?

What Are G2 Users Discussing About Trellix Threat Intelligence Exchange?

Maltego

Maltego is the world’s most widely used cyber investigation platform, offering an all-in-one solution for both quick OSINT investigations and complex link analysis of large datasets with seamless data integration in one analytical environment. It enables real-time social media monitoring and deep network analysis to uncover hidden patterns and connections. Maltego is trusted for threat intelligence, situational awareness, law enforcement investigations, and trust & safety applications.

Average Rating: 4.5/5.0

Total Reviews: 22

How Do G2 Users Rate Maltego?

  • Security Validation: 9.3/10 (Category avg: 9.1/10)
  • Intelligence Reports: 9.5/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 7.9/10 (Category avg: 9.1/10)

Who Is the Company Behind Maltego?

  • Seller: Maltego
  • Year Founded: 2017
  • HQ Location: Munich, DE
  • LinkedIn® Page: www.linkedin.com
    179 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 59% Small, 27% Medium

What Are Recent G2 Reviews of Maltego?

What Are G2 Users Discussing About Maltego?

Dataminr

Dataminr provides a revolutionary real-time AI platform for detecting events, risks and critical information from public data signals. Recognized as one of the world's leading AI companies, Dataminr enables faster real-time response and more effective risk management for public and private sector organizations, including multinational corporations, governments, NGOs, and newsrooms. Dataminr Pulse for Corporate Security With Dataminr Pulse for Corporate Security, you can detect, visualize, and respond to events and threats in real-time to: • Improve People Safety: Improve the safety of your employees, executives, customers, and contractors against external risks and threats wherever they are—in the office, working from home, or on a business trip. • Secure Facilities and Events: Protect all your global premises—including offices, manufacturing plants, warehouses, data centers, retail stores, stadiums, arenas, and temporary work locations—against external threats and hazards. • Increase Operational Resilience: Safeguard your revenue-generating activities against external threats and disruptive events that could directly or indirectly affect core business operations. Dataminr Pulse for Cyber Risk Enhance cyber resilience with Dataminr Pulse for Cyber Risk, a real-time, external cyber threat detection solution that empowers your team to: • Identify Digital Risk: Respond quickly to early warnings of threats to and exposures of your organization's digital assets. • Expose Third-Party Risk: Mitigate risk to your organization with increased visibility into threats to your subsidiaries, vendors, and service providers. • Receive Vulnerability Intelligence: Improve prioritization of patching with visibility into the full lifecycle of vulnerabilities. Get alerts about exploits, emerging and trending vulnerabilities, and more. • Respond to Cyber-Physical Risks: Respond to real-time alerts on cyber threats affecting physical assets and physical threats affecting digital assets.

Average Rating: 4.5/5.0

Total Reviews: 48

How Do G2 Users Rate Dataminr?

  • Security Validation: 7.6/10 (Category avg: 9.1/10)
  • Intelligence Reports: 7.6/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 8.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Dataminr?

  • Seller: Dataminr
  • Year Founded: 2009
  • HQ Location: New York, NY
  • LinkedIn® Page: www.linkedin.com
    880 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Security and Investigations
  • Company Size: 56% Large, 33% Small

What Do G2 Reviewers Say About Dataminr?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Dataminr, highlighting its straightforward setup and fast real-time alerts.
  • Users value the fast and reliable alerts from Dataminr, enhancing decision-making with timely and organized information.
  • Users value the real-time monitoring capabilities of Dataminr, enhancing awareness and decision-making during critical events.
  • Users value the fast and reliable alert notifications from Dataminr, enhancing awareness and timely decision-making.
  • Users value Dataminr for its rapid and reliable detection of emerging issues, enhancing awareness and decision-making.
Cons
  • Users experience inefficient alerts that can be overwhelming, often lacking relevance and requiring better prioritization.
  • Users find complexity and information overload in Dataminr, struggling with overwhelming alerts and customization challenges.
  • Users experience false positives from Dataminr, receiving excessive irrelevant alerts that complicate decision-making and require filtering.
  • Users experience information overload with Dataminr due to excessive notifications, making it hard to focus on relevant updates.
  • Users note the learning curve with Dataminr can be steep, affecting initial usability and accessibility.

What Are Recent G2 Reviews of Dataminr?

What Are G2 Users Discussing About Dataminr?

Defendify All-In-One Cybersecurity Solution

Founded in 2017, Defendify is pioneering All-In-One Cybersecurity® for organizations with growing security needs, backed by experts offering ongoing guidance and support. Delivering multiple layers of protection, Defendify provides an all-in-one, easy-to-use platform designed to strengthen cybersecurity across people, process, and technology, continuously. With Defendify, organizations streamline cybersecurity assessments, testing, policies, training, detection, response & containment in one consolidated and cost-effective cybersecurity solution. 3 layers, 13 solutions, 1 platform, including: • Managed Detection & Response • Cyber Incident Response Plan • Cybersecurity Threat Alerts • Phishing Simulations • Cybersecurity Awareness Training • Cybersecurity Awareness Videos • Cybersecurity Awareness Posters & Graphics • Technology Acceptable Use Policy • Cybersecurity Risk Assessments • Penetration Testing • Vulnerability Scanning • Compromised Password Scanning • Website Security Scanning See Defendify in action at www.defendify.com.

Average Rating: 4.7/5.0

Total Reviews: 57

How Do G2 Users Rate Defendify All-In-One Cybersecurity Solution?

  • Security Validation: 9.2/10 (Category avg: 9.1/10)
  • Intelligence Reports: 8.7/10 (Category avg: 9.1/10)
  • Endpoint Intelligence: 9.3/10 (Category avg: 8.7/10)
  • Ease of Use: 9.4/10 (Category avg: 9.1/10)

Who Is the Company Behind Defendify All-In-One Cybersecurity Solution?

  • Seller: Defendify
  • Year Founded: 2017
  • HQ Location: Portland, Maine
  • LinkedIn® Page: www.linkedin.com
    38 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 65% Small, 35% Medium

What Do G2 Reviewers Say About Defendify All-In-One Cybersecurity Solution?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Defendify, making cybersecurity management seamless and efficient for their teams.
  • Users appreciate the comprehensive and cost-effective cybersecurity features of Defendify, enhancing security management for organizations.
  • Users appreciate the easy setup of Defendify, allowing quick implementation and seamless integration into existing systems.
  • Users value the comprehensive and cost-effective features of Defendify, enhancing their cybersecurity management efficiently.
  • Users value the effective threat monitoring of Defendify, enhancing their cybersecurity posture with comprehensive protection.
Cons
  • Users express concerns about inadequate reporting, wishing for improvements like custom options and concise summaries.
  • Users find the reporting features inadequate, noting the need for concise summaries and customizable options for better insights.
  • Users desire a more concise format and detailed reporting for penetration tests in Defendify's solution.
  • Users find the lack of limited customization options disappointing, desiring co-branding and custom reporting features.
  • Users find the lack of custom reporting options a limitation, which could enhance personalized data monitoring.

What Are Recent G2 Reviews of Defendify All-In-One Cybersecurity Solution?

What Are G2 Users Discussing About Defendify All-In-One Cybersecurity Solution?

OnSecurity

OnSecurity is the CREST-accredited AI-augmented penetration testing platform that unifies expert-led manual testing, continuous vulnerability management, and remediation tracking in one connected programme. Built by penetration testers for security and engineering teams, OnSecurity's Platform moves organisations beyond one-off, point-in-time pentests to an always-on offensive security programme. The platform gives teams live visibility into findings as they're discovered, free retesting and remediation workflows, and a single source of truth for vulnerability status across the business, cutting manual admin and reporting effort by 30-50% and saving security teams significant time on every test cycle. OnSecurity helps secure over 500 organisations including Gousto, Lidl, Yonder, Retail in Motion, Incident.io, L&G Group and many more...

Average Rating: 4.9/5.0

Total Reviews: 37

How Do G2 Users Rate OnSecurity?

  • Ease of Use: 9.6/10 (Category avg: 9.1/10)

Who Is the Company Behind OnSecurity?

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 66% Small, 29% Medium

What Are Recent G2 Reviews of OnSecurity?

What Are G2 Users Discussing About OnSecurity?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated