Best Penetration Testing Tools - Page 3

How Many Penetration Testing Tools Products Does G2 Track?

Total Products under this Category: 200

Category Stats (Nov 2026)

  • Average Rating: 4.64/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Penetration Testing Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 200+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

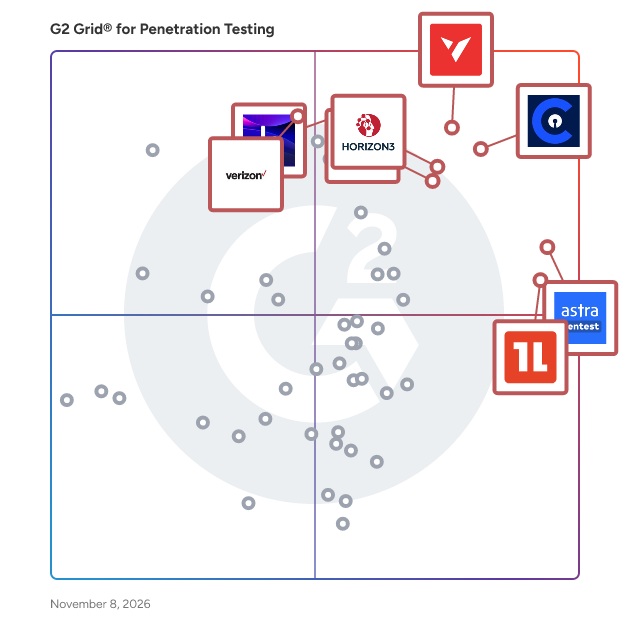
G2 Grid® for Penetration Testing Tools

G2 Grid® for Penetration Testing Tools plotting products by satisfaction and market presence

Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)

APPCHECK

Uncover your full attack surface, test it constantly, act with confidence. AppCheck helps organisations reduce cyber risk, meet compliance requirements and keep pace with evolving threats. Our platform delivers continuous security testing across your attack surface with the depth of a manual penetration test, uncovering vulnerabilities unique to your systems across web applications, APIs and infrastructure. Born from a UK-based penetration testing organisation, AppCheck combines over 20 years of testing expertise with a first-principles approach to security testing. Developed and supported by experienced penetration testers, the platform goes beyond known vulnerability signatures, analysing application behaviour to identify weaknesses that conventional scanning approaches can miss. Using multiple proprietary crawling engines, AppCheck tests modern and traditional technologies, including Single Page Applications (SPAs), APIs and complex authentication flows such as SSO, 2FA and TOTP. Discover: Gain visibility across your attack surface, including forgotten assets and third-party exposure. Assess: Find and validate vulnerabilities with the depth and rigour of a manual penetration test. Take action: Prioritise real-world risk and focus resources on what needs fixing first. Organisations can conduct unlimited security assessments across web applications, SPAs, APIs, cloud services and network infrastructure, covering both internal and external assets. With support for production and UAT environments, AppCheck also helps development teams shift security testing left through integrations with CI/CD pipelines and build tools, including Azure DevOps, GitHub, Jenkins, TeamCity, CircleCI, Bamboo and GitLab CI/CD. This enables automated security testing throughout development, helping teams identify vulnerabilities as changes are introduced. With unlimited scans and users per licence, teams can test continuously without additional charges for each scan, backed by direct UK-based support from security specialists. AppCheck is proud to be a CVE Numbering Authority (CNA), contributing to global vulnerability research.

Average Rating: 4.7/5.0

Total Reviews: 68

How Do G2 Users Rate APPCHECK?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.3/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.5/10 (Category avg: 9.2/10)
  • Extensibility: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind APPCHECK?

  • Seller: APPCHECK
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Leeds, GB
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 49% Medium, 31% Small

What Do G2 Reviewers Say About APPCHECK?

AI-generated summary from verified user reviews

Pros
  • Users commend the thorough and reliable vulnerability detection of AppCheck, enhancing security in their applications effectively.
  • Users find the ease of use of AppCheck remarkable, praising its user-friendly interface and responsive support.
  • Users value the excellent pricing and functionality of AppCheck, along with its reliable and intuitive vulnerability scanning.
  • Users find Pentest efficiency remarkable with AppCheck, leading to significant cost savings and streamlined vulnerability detection.
  • Users value the automated scanning feature of AppCheck, enhancing efficiency and streamlining vulnerability management across multiple apps.
Cons
  • Users find the poor customer support frustrating, needing to raise tickets for simple adjustments to the scan list.
  • Users suggest that UX improvements in scoring, customization, and integrations could enhance the AppCheck experience.
  • Users find the API issues frustrating, as endpoint changes require a service request and delays functionality.
  • Users find difficult customization in AppCheck's reporting features, needing more flexibility for contextual adjustments.
  • Users experience a notable difficult learning curve with Appcheck, which may hinder initial ease of use.

What Are Recent G2 Reviews of APPCHECK?

Black Duck Polaris Platform

Black Duck builds trust in software by enabling organizations to manage application security, quality, and compliance risks at the speed their business demands. Black Duck solutions help developers to secure code as fast as they write it, development and DevSecOps teams to automate testing within development pipelines without compromising velocity, and security teams to proactively manage risk and focus remediation efforts on what matters most. With Black Duck, organizations can transform the way they build and deliver software, aligning people, processes, and technology to intelligently address software risks across their portfolio and at all stages of the application lifecycle.

Average Rating: 4.2/5.0

Total Reviews: 103

How Do G2 Users Rate Black Duck Polaris Platform?

  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 6.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Black Duck Polaris Platform?

  • Seller: Black Duck
  • Year Founded: 2024
  • HQ Location: Burlington, US
  • LinkedIn® Page: www.linkedin.com
    1,317 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Large, 32% Medium

What Do G2 Reviewers Say About Black Duck Polaris Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the accuracy of findings in Black Duck Polaris, especially its powerful engine for identifying open source issues.
  • Users praise the powerful open source issue identification by Black Duck Polaris, benefiting from extensive Black Duck Knowledge.
Cons
  • Users note that the platform requires huge resource constraints for on-prem deployment, impacting its usability.

What Are Recent G2 Reviews of Black Duck Polaris Platform?

What Are G2 Users Discussing About Black Duck Polaris Platform?

OnSecurity

OnSecurity is the CREST-accredited AI-augmented penetration testing platform that unifies expert-led manual testing, continuous vulnerability management, and remediation tracking in one connected programme. Built by penetration testers for security and engineering teams, OnSecurity's Platform moves organisations beyond one-off, point-in-time pentests to an always-on offensive security programme. The platform gives teams live visibility into findings as they're discovered, free retesting and remediation workflows, and a single source of truth for vulnerability status across the business, cutting manual admin and reporting effort by 30-50% and saving security teams significant time on every test cycle. OnSecurity helps secure over 500 organisations including Gousto, Lidl, Yonder, Retail in Motion, Incident.io, L&G Group and many more...

Average Rating: 4.9/5.0

Total Reviews: 37

How Do G2 Users Rate OnSecurity?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 10.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.8/10 (Category avg: 9.2/10)
  • Extensibility: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind OnSecurity?

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 66% Small, 29% Medium

What Are Recent G2 Reviews of OnSecurity?

What Are G2 Users Discussing About OnSecurity?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Pynt - API Security Testing

Pynt is an innovative API Security Testing platform exposing verified API threats through simulated attacks. Hundreds of companies rely on Pynt to continuously monitor, classify and attack poorly secured APIs, before hackers do.

Average Rating: 4.8/5.0

Total Reviews: 44

How Do G2 Users Rate Pynt - API Security Testing?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.2/10 (Category avg: 9.2/10)
  • Extensibility: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Pynt - API Security Testing?

  • Seller: Pynt
  • Year Founded: 2022
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    13 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Computer & Network Security
  • Company Size: 57% Small, 23% Large

What Do G2 Reviewers Say About Pynt - API Security Testing?

AI-generated summary from verified user reviews

Pros
  • Users value Pynt for its efficient vulnerability detection, quickly uncovering critical security issues in APIs.
  • Users appreciate Pynt for its effective security engine, quickly identifying critical issues and boosting confidence in API security.
  • Users appreciate the seamless integration of Pynt with their SDLC, enhancing API discovery and security automation.
  • Users appreciate the simple integration of Pynt with their SDLC, enhancing their API security workflow effortlessly.
  • Users value the automation capabilities of Pynt, as it simplifies API security testing and enhances confidence in their systems.
Cons
  • Users find the complex setup challenging initially, requiring time and effort to fully integrate Pynt effectively.
  • Users find the setup complexity of Pynt challenging, often requiring support to navigate the initial process.
  • Users note the limited features of Pynt, particularly in reporting and onboarding, which can hinder functionality.
  • Users find the user interface challenging, making it difficult to navigate and set up the software effectively.
  • Users find the user interface challenging, suggesting significant improvements for a better overall experience.

What Are Recent G2 Reviews of Pynt - API Security Testing?

Beagle Security

Beagle Security helps you identify vulnerabilities in your web applications, APIs, GraphQL and remediate them with actionable insights before hackers harm you in any manner. With Beagle Security, you can integrate automated penetration testing into your CI/CD pipeline to identify security issues earlier in your development lifecycle and ship safer web applications. Major features: - Checks your web apps & APIs for 3000+ test cases to find security loopholes - OWASP & SANS standards - Recommendations to address security issues - Security test complex web apps with login - Compliance reports (GDPR, HIPAA & PCI DSS) - Test scheduling - DevSecOps integrations - API integration - Team access - Integrations with popular tools like Slack, Jira, Asana, Trello & 100+ other tools

Average Rating: 4.7/5.0

Total Reviews: 85

How Do G2 Users Rate Beagle Security?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.7/10 (Category avg: 9.2/10)
  • Extensibility: 6.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Beagle Security?

Who Uses This Product?

  • Who Uses This: CEO, Director
  • Top Industries: Marketing and Advertising, Information Technology and Services
  • Company Size: 91% Small, 7% Medium

What Do G2 Reviewers Say About Beagle Security?

AI-generated summary from verified user reviews

Pros
  • Users value the attractive and comprehensive reporting offered by Beagle Security, enhancing their overall experience.
  • Users appreciate the setup ease of Beagle Security, finding it simple to configure and enjoy the reports.

What Are Recent G2 Reviews of Beagle Security?

What Are G2 Users Discussing About Beagle Security?

Breachlock

BreachLock is the only offensive security provider combining continuous ASM, autonomous pentesting, CREST-certified penetration testing, and closed-loop remediation in a single workflow within the BreachLock Unified Platform. The platform brings together three core capabilities: • BreachLock PTaaS (Penetration Testing as a Service), which pairs certified human pentesters with AI acceleration for deep, expert-led testing. • Breach360, an autonomous penetration testing solution powered by agentic AI that discovers real attack paths, chains exploits, and proves what's exploitable with documented evidence so teams can continuously understand and remediate what matters most. • BreachLock ASM (Attack Surface Management), which discovers and prioritizes attack surface exposures in real time. Together, they offer continuous security validation for applications, networks, APIs, cloud, IoT, and LLMs. BreachLock is globally CREST-accredited with 100% in-house certified pentesters (CREST, OSCP, OSCE, CISSP) across the U.S., U.K., E.U., and Asia, and delivers audit-ready reports aligned to SOC 2, PCI DSS, ISO 27001, HIPAA, and GDPR

Average Rating: 4.6/5.0

Total Reviews: 38

How Do G2 Users Rate Breachlock?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.7/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.9/10 (Category avg: 9.2/10)
  • Extensibility: 7.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Breachlock?

  • Seller: Breachlock
  • Company Website:
  • Year Founded: 2019
  • HQ Location: New York, NY
  • LinkedIn® Page: www.linkedin.com
    137 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Small, 39% Medium

What Do G2 Reviewers Say About Breachlock?

AI-generated summary from verified user reviews

Pros
  • Users commend Breachlock for its great customer support, praising the team's quick response and helpfulness.
  • Users value the excellent communication from Breachlock, appreciating their responsiveness and clarity throughout the process.
  • Users find Breachlock easy to use, even for non-technical individuals, with excellent customer support enhancing their experience.
  • Users praise Breachlock for its thorough vulnerability detection and clear remediation suggestions, enhancing security management efficiency.
  • Users value the efficiency of Breachlock's pentesting, appreciating its thoroughness and clear communication throughout the process.
Cons
  • Users are frustrated by the high number of false positives, complicating their workflow and slowing down corrections.
  • Users criticize the poor interface design of Breachlock, finding it slow and difficult for tracking vulnerabilities effectively.
  • Users find Breachlock expensive, with high pricing persisting despite discounts and varying costs among different companies.
  • Users find the inadequate reporting lacking polish, affecting the credibility of reports shared with customers.
  • Users find a lack of detail in product descriptions and security findings, complicating their troubleshooting processes.

What Are Recent G2 Reviews of Breachlock?

StackHawk

StackHawk is reimagining AppSec for AI-driven development, where applications are built faster than traditional AppSec tools can keep up. Our AppSec Intelligence Platform combines scalable runtime testing with complete attack surface discovery from source code. We integrate directly into development workflows and provide context-aware remediations to developers, enabling teams to find and fix exploitable vulnerabilities before they reach production. With real-time visibility and centralized program intelligence, AppSec teams can prioritize testing and fixing what matters. Companies like British Airways, ITV, and Norstella trust StackHawk to evaluate application risk, prove program value, and scale testing coverage to match development velocity.

Average Rating: 4.6/5.0

Total Reviews: 67

How Do G2 Users Rate StackHawk?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.2/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.3/10 (Category avg: 9.2/10)
  • Extensibility: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind StackHawk?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 46% Small, 35% Medium

What Do G2 Reviewers Say About StackHawk?

AI-generated summary from verified user reviews

Pros
  • Users value the easy integrations of StackHawk, which streamline workflows and enhance collaboration across development teams.
  • Users commend the exceptional customer support from StackHawk, highlighting their friendly assistance and effective onboarding process.
  • Users find StackHawk to be easy to use, especially after the initial setup, enhancing their security testing experience.
  • Users value the seamless integrations with various tools, making automated security testing straightforward and efficient.
  • Users praise StackHawk for its scanning efficiency, boosting development speed while enhancing security integration seamlessly.
Cons
  • Users find the setup complexity of StackHawk challenging, requiring extensive trial and error for configuration.
  • Users find the complex setup of StackHawk frustrating due to unclear documentation and extensive configuration requirements.
  • Users find the high learning curve of StackHawk challenging, hindered by its complex setup and limited training resources.
  • Users point out the lack of features in StackHawk, especially regarding API management and vulnerability tracking.
  • Users note the limited scope of StackHawk, citing issues with on-prem use and insufficient reporting capabilities.

What Are Recent G2 Reviews of StackHawk?

What Are G2 Users Discussing About StackHawk?

Core Impact

Core Impact is an easy-to-use penetration testing tool with commercially developed and tested exploits that enables security teams to exploit security weaknesses, increase productivity, and improve efficiencies. With guided automation and certified exploits , this powerful penetration testing software enables you to safely test your environment using the same techniques as today's attackers. Core Impact gives you visibility into the effectiveness of your defenses and reveals where your most pressing risks exist in your environment. This enables you to assess your organization’s ability to detect, prevent, and respond to real-world, multi-staged threats against your infrastructure, applications, and people. Organizations can rely on Core Impact to measure their ability to identify attacks, track, and validate their effectiveness through a variety of approaches, including: - Demonstrating what vulnerabilities surfaced from scanners are truly exploitable, revealing how chains of exploitable vulnerabilities open paths to your organization’s mission-critical systems and assets. - Re-testing exploited systems to verify that remediation measures or compensating controls are effective and working. - Simplifying testing for new users by providing intuitive, step-by-step wizards and rapid penetration tests so they can automatically gather the information they need. - Deploying phishing campaigns for social engineering tests to discover which users are susceptible and what credentials can be harvested. Core Impact’s Key Features Include: · Guide Automation and Patented Agents · Certified Exploits · Reporting and Visibility · Programmable Self-Destruct & Error Prevention · Teaming, Automated Retesting, and Validation Core Impact is also interoperable with Vuln Scanners, like Fortra VM, and Red Team Tools such as Cobalt Strike and Outflank OST. View our product bundles https://www.coresecurity.com/products/bundles. Learn more at https://www.coresecurity.com/products/core-impact

Average Rating: 4.1/5.0

Total Reviews: 29

How Do G2 Users Rate Core Impact?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.1/10 (Category avg: 9.2/10)
  • Extensibility: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Core Impact?

  • Seller: Fortra
  • Company Website:
  • Year Founded: 1982
  • HQ Location: Eden Prairie, Minnesota
  • LinkedIn® Page: www.linkedin.com
    1,784 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 37% Small, 33% Large

What Are Recent G2 Reviews of Core Impact?

What Are G2 Users Discussing About Core Impact?

Qodex.ai

Qodex is a swarm of AI agents that attacks and tests your app 24/7, so your team ships AI-written code without a security or QA team. The problem: your team ships with coding agents, so the code doubles and the people who test and secure it do not. 45% of AI-written code fails OWASP Top 10 security tests (Veracode, 2025). Your pentest is once a year. What Qodex does: a swarm of agents runs against your live app. The largest group tries to break in the way a hacker would: injection, broken auth, one customer seeing another customer's data, the OWASP Top 10 and the OWASP API Top 10, with the exploit reproduced as evidence. The others click through every screen in a real browser and call every API, from an OpenAPI, Swagger or Postman import. How you drive it: describe what to attack or test in plain English and watch it work live. It remembers your app across sessions: auth, quirks, past bugs, your code if you link the repo. What you keep: every test is saved as plain Playwright or HTTP code you own. Saved tests re-run with no AI calls, every night, from CI on every deploy, or from Claude Code and Cursor. When a screen changes, a saved step finds its control again from the intent. What you get back: every failure labelled real bug, stale test or environment problem, with severity, steps and evidence. A security test passes only when the attack was blocked. Start: free plan, no card. Paid from $1,299 per project per month. Managed cloud, AWS Marketplace or self-host.

Average Rating: 4.9/5.0

Total Reviews: 60

How Do G2 Users Rate Qodex.ai?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)

Who Is the Company Behind Qodex.ai?

  • Seller: QodexAI
  • Year Founded: 2024
  • HQ Location: San Francisco, California
  • LinkedIn® Page: linkedin.com
    13 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 75% Small, 20% Medium

What Do G2 Reviewers Say About Qodex.ai?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Qodex.ai, allowing quick adoption and streamlined testing workflows effortlessly.
  • Users value the automation capabilities of Qodex.ai, which streamline AI testing while maintaining high quality and speed.
  • Users praise Qodex.ai for its ability to automate AI-driven testing workflows, significantly reducing manual efforts while ensuring quality.
  • Users appreciate the testing efficiency of Qodex.ai, enabling faster workflows while ensuring high-quality coverage in AI testing.
  • Users appreciate the ease of use and automation in Qodex.ai, simplifying testing processes and enhancing productivity.
Cons
  • Users note that the slow loading times for UI and reports can hinder their overall experience.
  • Users find the poor documentation of Qodex.ai limits their ability to fully utilize advanced features effectively.
  • Users notice slow performance in Qodex.ai, with delays in UI loading and chatbot response times affecting usability.
  • Users report bug issues with repeated test cases, suggesting improvements in tagging and reporting processes.
  • Users experience repeated test case issues and suggest improvements in bug reporting and prioritization.

What Are Recent G2 Reviews of Qodex.ai?

Detectify

Detectify sets a new standard for advanced application security testing, challenging traditional DAST by providing evolving coverage of each and every exposed asset across the changing attack surface. AppSec teams trust Detectify to expose how attackers will exploit their Internet-facing applications. The Detectify platform automates continuous real-world, payload-based attacks fuelled by its global community of elite ethical hackers into its own expert-built engines, exposing critical weaknesses before it's too late. The Detectify solution includes: - Automated discovery of known and unknown digital assets via domain & cloud connectors - Continuous coverage (24/7) of every corner of the attack surface with dynamic testing. Not just predefined targets - 100% payload-based testing fuelled by elite ethical hackers for a high signal-to-noise ratio - Distributed coverage across an unmatched array of relevant technologies - Actionable remediation tips for software development teams - Team functionality to easily share reports - Powerful integrations platform to prioritize and triage vulnerability findings onward to development teams -Advanced API functionality -Capabilities to set custom attack surface security policies

Average Rating: 4.5/5.0

Total Reviews: 50

How Do G2 Users Rate Detectify?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.5/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.3/10 (Category avg: 9.2/10)
  • Extensibility: 7.2/10 (Category avg: 8.8/10)

Who Is the Company Behind Detectify?

  • Seller: Detectify
  • Year Founded: 2013
  • HQ Location: Stockholm, Sweden
  • LinkedIn® Page: www.linkedin.com
    94 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 46% Small, 37% Medium

What Do G2 Reviewers Say About Detectify?

AI-generated summary from verified user reviews

Pros
  • Users appreciate Detectify's automation capabilities, enabling effective and customizable security testing with easy integrations.
  • Users appreciate the ease of automation in testing with Detectify, enhancing security efforts without complex setups.
  • Users appreciate the customizability of Detectify, allowing easy integration and tailored security testing for diverse needs.
  • Users appreciate the dynamic application security testing capabilities of Detectify, easily integrating it into existing workflows.
  • Users appreciate the dynamic application security testing capabilities of Detectify, making security integration seamless and effective.
Cons
  • Users find the complexity of initial setup a hurdle that complicates their experience with Detectify.
  • Users find the complex queries in Detectify lacking, especially in terms of GraphQL support and clarity on outcomes.
  • Users find the complex setup of Detectify challenging, leading to a cumbersome experience during initial configuration.
  • Users find Detectify expensive when testing multiple sites, which may limit its accessibility for some.
  • Users find the inaccuracy in spidering results problematic, hindering their ability to verify complete assessments of applications.

What Are Recent G2 Reviews of Detectify?

What Are G2 Users Discussing About Detectify?

Defendify All-In-One Cybersecurity Solution

Founded in 2017, Defendify is pioneering All-In-One Cybersecurity® for organizations with growing security needs, backed by experts offering ongoing guidance and support. Delivering multiple layers of protection, Defendify provides an all-in-one, easy-to-use platform designed to strengthen cybersecurity across people, process, and technology, continuously. With Defendify, organizations streamline cybersecurity assessments, testing, policies, training, detection, response & containment in one consolidated and cost-effective cybersecurity solution. 3 layers, 13 solutions, 1 platform, including: • Managed Detection & Response • Cyber Incident Response Plan • Cybersecurity Threat Alerts • Phishing Simulations • Cybersecurity Awareness Training • Cybersecurity Awareness Videos • Cybersecurity Awareness Posters & Graphics • Technology Acceptable Use Policy • Cybersecurity Risk Assessments • Penetration Testing • Vulnerability Scanning • Compromised Password Scanning • Website Security Scanning See Defendify in action at www.defendify.com.

Average Rating: 4.7/5.0

Total Reviews: 57

How Do G2 Users Rate Defendify All-In-One Cybersecurity Solution?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.8/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Defendify All-In-One Cybersecurity Solution?

  • Seller: Defendify
  • Year Founded: 2017
  • HQ Location: Portland, Maine
  • LinkedIn® Page: www.linkedin.com
    38 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 65% Small, 35% Medium

What Do G2 Reviewers Say About Defendify All-In-One Cybersecurity Solution?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Defendify, making cybersecurity management seamless and efficient for their teams.
  • Users appreciate the comprehensive and cost-effective cybersecurity features of Defendify, enhancing security management for organizations.
  • Users appreciate the easy setup of Defendify, allowing quick implementation and seamless integration into existing systems.
  • Users value the comprehensive and cost-effective features of Defendify, enhancing their cybersecurity management efficiently.
  • Users value the effective threat monitoring of Defendify, enhancing their cybersecurity posture with comprehensive protection.
Cons
  • Users express concerns about inadequate reporting, wishing for improvements like custom options and concise summaries.
  • Users find the reporting features inadequate, noting the need for concise summaries and customizable options for better insights.
  • Users desire a more concise format and detailed reporting for penetration tests in Defendify's solution.
  • Users find the lack of limited customization options disappointing, desiring co-branding and custom reporting features.
  • Users find the lack of custom reporting options a limitation, which could enhance personalized data monitoring.

What Are Recent G2 Reviews of Defendify All-In-One Cybersecurity Solution?

What Are G2 Users Discussing About Defendify All-In-One Cybersecurity Solution?

Appknox

Appknox is an on-demand mobile application security platform that helps businesses detect and fix security vulnerabilities using an Automated Security Testing suite. We have been successfully reducing delivery timelines, manpower costs & mitigating security threats for Global Banks and Enterprises in 10 + countries.

Average Rating: 4.4/5.0

Total Reviews: 41

How Do G2 Users Rate Appknox?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.7/10 (Category avg: 9.2/10)
  • Extensibility: 9.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Appknox?

  • Seller: Appknox
  • Year Founded: 2014
  • HQ Location: Singapore, Singapore
  • LinkedIn® Page: www.linkedin.com
    84 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 41% Small, 36% Medium

What Are Recent G2 Reviews of Appknox?

What Are G2 Users Discussing About Appknox?

Hackrate Ethical Hacking Platform

Hackrate Ethical Hacking Platform is a crowdsourced security testing solution designed to connect businesses with ethical hackers in order to identify and remediate security vulnerabilities. By leveraging the expertise of a diverse pool of ethical hackers, Hackrate enables organizations to enhance their cybersecurity posture efficiently and effectively. The platform is tailored for businesses of all sizes, from startups to large enterprises, seeking to bolster their security measures. With the increasing frequency of cyber threats, organizations are recognizing the importance of proactive security testing. Hackrate facilitates this by allowing companies to tap into a global network of skilled ethical hackers who can provide insights and solutions to potential vulnerabilities. This collaborative approach not only accelerates the testing process but also enriches the quality of security assessments through varied perspectives and methodologies. One of the key features of Hackrate is its user-friendly interface, which simplifies the onboarding process for both businesses and ethical hackers. Companies can initiate security testing within hours, streamlining the process of vulnerability identification. This rapid deployment is critical for organizations that need to address security concerns promptly, especially in a fast-paced digital landscape. Furthermore, Hackrate offers flexible pricing plans, making it accessible for businesses with varying budgets and security needs. Security and confidentiality are paramount in the realm of cybersecurity, and Hackrate prioritizes these aspects by implementing robust encryption and adhering to industry-standard security protocols. This commitment ensures that sensitive data remains protected throughout the testing process, fostering trust between businesses and ethical hackers. By utilizing Hackrate, organizations can confidently engage in security testing without compromising their data integrity. Overall, Hackrate Ethical Hacking Platform stands out as a comprehensive solution for businesses aiming to enhance their security frameworks. By combining the expertise of ethical hackers with an efficient, secure platform, Hackrate offers a practical approach to identifying and addressing security vulnerabilities, ultimately contributing to a safer digital environment.

Average Rating: 4.9/5.0

Total Reviews: 35

How Do G2 Users Rate Hackrate Ethical Hacking Platform?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.7/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.9/10 (Category avg: 9.2/10)
  • Extensibility: 9.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Hackrate Ethical Hacking Platform?

  • Seller: Hackrate
  • Year Founded: 2020
  • HQ Location: Budapest, HU
  • LinkedIn® Page: www.linkedin.com
    12 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 83% Small, 11% Large

What Do G2 Reviewers Say About Hackrate Ethical Hacking Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the supportive communication from the Hackrate team, enhancing the overall positive experience of collaboration.
  • Users commend the highly motivated and skilled customer support team at Hackrate, enhancing their experience in cybersecurity projects.
  • Users appreciate the ease of use of Hackrate, benefiting from its concise rules and responsive support.
  • Users value the expertise of Hackrate's founders, appreciating their real-world insights and supportive approach throughout the service.
  • Users commend the motivated and skilled team of Hackrate, contributing to successful cybersecurity project completions.
Cons
  • Users report poor customer support, especially during high activity periods, leading to occasional delays in assistance.
  • Users find the poor interface design of Hackrate challenging, often struggling to navigate and locate necessary information.

What Are Recent G2 Reviews of Hackrate Ethical Hacking Platform?

What Are G2 Users Discussing About Hackrate Ethical Hacking Platform?

BugBase

BugBase is a Continuous Vulnerability Assessment Platform that conducts comprehensive security operations such as bug bounty programs and next-gen pentesting (VAPT) to assist startups and enterprises in effectively identifying, managing and mitigating vulnerabilities.

Average Rating: 4.5/5.0

Total Reviews: 45

How Do G2 Users Rate BugBase?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.7/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.1/10 (Category avg: 9.2/10)
  • Extensibility: 8.2/10 (Category avg: 8.8/10)

Who Is the Company Behind BugBase?

  • Seller: BugBase
  • Year Founded: 2021
  • HQ Location: Singapore, US
  • LinkedIn® Page: www.linkedin.com
    43 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Computer Software
  • Company Size: 60% Small, 21% Medium

What Do G2 Reviewers Say About BugBase?

AI-generated summary from verified user reviews

Pros
  • Users find BugBase's ease of use impressive, making it ideal for both beginners and experienced bug bounty hunters.
  • Users praise the simple and user-friendly interface of BugBase, making it ideal for newcomers in bug bounties.
  • Users value the enhanced cybersecurity measures of BugBase, ensuring confidentiality and effective vulnerability detection for secure applications.
  • Users appreciate the user-friendly interface of BugBase, making integration and tracking security issues convenient and efficient.
  • Users appreciate the easy integrations of BugBase, making it simple to manage various tools and initiatives.
Cons
  • Users experience slow performance on BugBase, particularly when handling multiple reports or loading extensive dashboards.
  • Users find the pricing expensive compared to competitors, highlighting a need for more flexible options.
  • Users find the difficult setup of BugBase frustrating, especially for those lacking technical expertise or software familiarity.
  • Users face a steep learning curve with BugBase, making it challenging for newcomers to configure advanced features.
  • Users report poor customer support, noting slow response times and a need for better documentation and instruction.

What Are Recent G2 Reviews of BugBase?

ZAP by Checkmarx

ZAP by Checkmarx, formerly known as Zed Attack Proxy , is a leading open-source web application security scanner designed to help developers, testers, and security professionals identify vulnerabilities in web applications. Actively maintained by a global community, ZAP offers both automated and manual testing capabilities, making it suitable for users with varying levels of security expertise. Key Features and Functionality: - Automated Security Scanning: ZAP provides simple, single-click automated scanning, enabling users to identify security flaws with ease. - Active and Passive Scanning: Utilizes both passive and active scanning techniques to uncover a wide range of security vulnerabilities. - Advanced User Controls: Offers tools like manual interception, fuzzing, and forced browsing for thorough penetration testing. - CI/CD Integration: Seamlessly integrates with Continuous Integration/Continuous Deployment pipelines, automating security testing within development workflows. - Cross-Platform Support: Compatible with Linux, Windows, and macOS operating systems. Primary Value and Problem Solved: ZAP by Checkmarx addresses the critical need for accessible and effective web application security testing. By offering a free, open-source solution with both automated and manual testing capabilities, ZAP empowers organizations to identify and remediate vulnerabilities early in the development lifecycle. Its integration with CI/CD pipelines ensures that security becomes an integral part of the development process, reducing the risk of security breaches and enhancing overall application security.

Average Rating: 4.7/5.0

Total Reviews: 13

How Do G2 Users Rate ZAP by Checkmarx?

  • Performance and Reliability: 8.9/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.4/10 (Category avg: 9.2/10)
  • Extensibility: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind ZAP by Checkmarx?

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 71% Small, 14% Large

What Do G2 Reviewers Say About ZAP by Checkmarx?

AI-generated summary from verified user reviews

Pros
  • Users find ZAP easy to use, appreciating its automation and seamless integration for web application security scans.
  • Users value the automated scanning features of ZAP, making web application security easier and more efficient.
  • Users praise ZAP for its powerful automated testing features, enhancing efficiency in web application security assessments.
  • Users appreciate the easy integrations of ZAP by Checkmarx, enhancing their CI/CD processes with automation.
  • Users praise the pentesting efficiency of ZAP for its ease of use and comprehensive vulnerability testing capabilities.
Cons
  • Users face false positives with ZAP, requiring manual checks that can disrupt the scanning process.
  • Users find the poor documentation of ZAP frustrating, especially during troubleshooting and error resolution.
  • Users find the limited automated tasks of ZAP restrict its effectiveness compared to other web pen-testing applications.
  • Users often face navigation problems due to insufficient documentation and support, impacting usability and efficiency.
  • Users report facing poor customer support, with insufficient documentation leading to frustration and unresolved issues.

What Are Recent G2 Reviews of ZAP by Checkmarx?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated March 5, 2025