Best Vulnerability Scanner Software for Small Business - Page 2

How Many Vulnerability Scanner Software Products Does G2 Track?

Total Products under this Category: 287

Category Stats (Nov 2026)

  • Average Rating: 4.59/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Vulnerability Scanner Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 8,800+ Authentic Reviews
  • 287+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

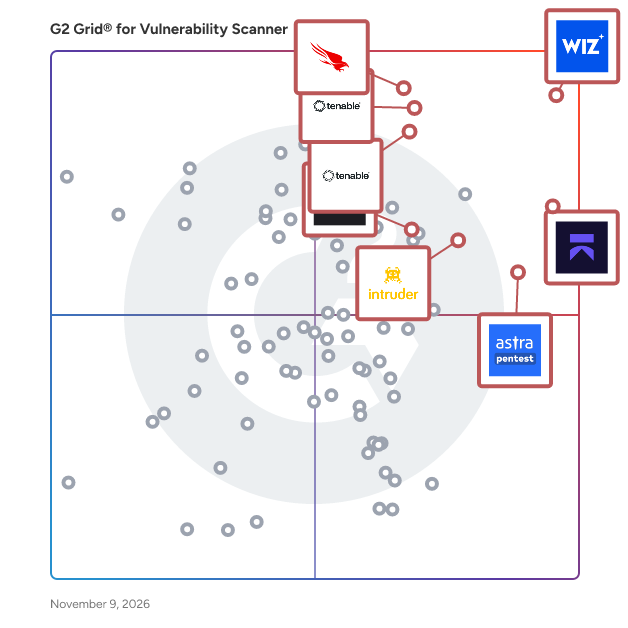
G2 Grid® for Vulnerability Scanner Software

G2 Grid® for Vulnerability Scanner Software plotting products by satisfaction and market presence

Highlighted products: Aikido Security, Wiz, Tenable Vulnerability Management, Astra Pentest, CrowdStrike Falcon Cloud Security, Intruder, Sysdig Secure, and Tenable Nessus.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vulnerability-scanner/grids.json?focus%5B%5D=aikido-security&focus%5B%5D=wiz-wiz&focus%5B%5D=tenable-vulnerability-management&focus%5B%5D=astra-pentest&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=intruder&focus%5B%5D=sysdig-sysdig-secure&focus%5B%5D=tenable-nessus&segment=small-business)

Beagle Security

Beagle Security helps you identify vulnerabilities in your web applications, APIs, GraphQL and remediate them with actionable insights before hackers harm you in any manner. With Beagle Security, you can integrate automated penetration testing into your CI/CD pipeline to identify security issues earlier in your development lifecycle and ship safer web applications. Major features: - Checks your web apps & APIs for 3000+ test cases to find security loopholes - OWASP & SANS standards - Recommendations to address security issues - Security test complex web apps with login - Compliance reports (GDPR, HIPAA & PCI DSS) - Test scheduling - DevSecOps integrations - API integration - Team access - Integrations with popular tools like Slack, Jira, Asana, Trello & 100+ other tools

Average Rating: 4.7/5.0

Total Reviews: 85

How Do G2 Users Rate Beagle Security?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Beagle Security?

Who Uses This Product?

  • Who Uses This: CEO, Director
  • Top Industries: Marketing and Advertising, Information Technology and Services
  • Company Size: 91% Small, 7% Medium

What Do G2 Reviewers Say About Beagle Security?

AI-generated summary from verified user reviews

Pros
  • Users value the attractive and comprehensive reporting offered by Beagle Security, enhancing their overall experience.
  • Users appreciate the setup ease of Beagle Security, finding it simple to configure and enjoy the reports.

What Are Recent G2 Reviews of Beagle Security?

What Are G2 Users Discussing About Beagle Security?

BugDazz API Scanner

BugDazz API Security Scanner by SecureLayer7 is a comprehensive tool designed to automatically detect vulnerabilities, misconfigurations, and security gaps in API endpoints, aiding security teams in protecting digital assets against increasing API-related threats and potential exploits. It offers real-time scanning capabilities, enabling the automatic detection of vulnerabilities as they arise. It supports authentication and access control management, allowing for the management of API controls within a single platform. BugDazz assists in achieving compliance by accelerating the generation of reports for standards such as PCI DSS and HIPAA. It integrates seamlessly with existing CI/CD pipelines, facilitating the acceleration of product rollouts. The scanner goes beyond standard OWASP Top 10 vulnerabilities, providing comprehensive protection against critical API security risks.

Average Rating: 4.9/5.0

Total Reviews: 11

How Do G2 Users Rate BugDazz API Scanner?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Detection Rate: 9.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.3/10 (Category avg: 8.5/10)

Who Is the Company Behind BugDazz API Scanner?

Who Uses This Product?

  • Company Size: 91% Small, 9% Medium

What Do G2 Reviewers Say About BugDazz API Scanner?

AI-generated summary from verified user reviews

Pros
  • Users value the accuracy of results from BugDazz API Scanner, enhancing collaboration and efficiency in release cycles.
  • Users value the seamless CD integration of BugDazz API Scanner, enhancing efficiency in workflows and collaboration between teams.
  • Users value the seamless integration into CI/CD workflows, enhancing efficiency and collaboration between security and engineering teams.
  • Users find the ease of use in BugDazz API Scanner crucial for seamless CI/CD integration and quick adoption.
  • Users appreciate the fast and clear scanning technology of BugDazz API Scanner, enhancing productivity in API management.
Cons
  • Users feel the poor documentation lacks clarity and could benefit from more detailed guidance on integrations.
  • Users find the difficult learning curve manageable, requiring time to effectively tune scans for various testing scenarios.
  • Users feel there's a lack of infrastructure-specific guidance in the documentation, limiting effective use of BugDazz API Scanner.
  • Users feel there is a lack of information in documentation, particularly regarding infrastructure-specific guidance.
  • Users face a learning curve with BugDazz API Scanner, but find it manageable for optimizing scan settings.

What Are Recent G2 Reviews of BugDazz API Scanner?

Amazon Inspector

Amazon Inspector is an automated vulnerability management service that continuously scans AWS workloads—including Amazon EC2 instances, container images in Amazon ECR, AWS Lambda functions, and code repositories—for software vulnerabilities and unintended network exposure. By integrating seamlessly with AWS environments, it provides real-time detection and prioritization of security issues, enabling organizations to enhance their security posture efficiently. Key Features and Functionality: - Automated Discovery and Continuous Scanning: Automatically identifies and assesses AWS resources for vulnerabilities and network exposures, ensuring comprehensive coverage without manual intervention. - Contextualized Risk Scoring: Generates risk scores by correlating vulnerability data with environmental factors such as network accessibility and exploitability, aiding in the prioritization of remediation efforts. - Integration with AWS Services: Seamlessly integrates with AWS Security Hub and Amazon EventBridge, facilitating automated workflows and centralized management of security findings. - Support for Multiple Resource Types: Extends vulnerability management to various AWS services, including EC2 instances, container images, Lambda functions, and code repositories, providing a unified security assessment across the cloud environment. - Agentless Scanning for EC2 Instances: Offers continuous monitoring of EC2 instances for software vulnerabilities without the need for installing additional agents, simplifying deployment and maintenance. Primary Value and Problem Solved: Amazon Inspector addresses the critical need for continuous and automated vulnerability management within AWS environments. By providing real-time detection and prioritization of security issues, it enables organizations to proactively identify and remediate vulnerabilities, reducing the risk of security breaches and ensuring compliance with industry standards. Its integration with existing AWS services and support for various resource types streamline security operations, allowing teams to focus on strategic initiatives while maintaining a robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 25

How Do G2 Users Rate Amazon Inspector?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Amazon Inspector?

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 41% Small, 33% Medium

What Do G2 Reviewers Say About Amazon Inspector?

AI-generated summary from verified user reviews

Pros
  • Users value the security protection provided by Amazon Inspector, ensuring vulnerability detection and compliance across AWS resources.
  • Users commend the excellent customer support provided by AWS, ensuring effective guidance and assistance throughout their experience.
  • Users value the centralized management of logs and security insights provided by Amazon Inspector for effective monitoring.
  • Users value the collaborative capabilities of Amazon Inspector, effectively facilitating security and compliance management.
  • Users appreciate the automatic security issue detection of Amazon Inspector, making setup and fixes effortless.
Cons
  • Users find the complexity of Amazon Inspector's setup challenging, requiring well-trained admins for effective use.
  • Users find the complexity issues of Amazon Inspector challenging, requiring trained admins for effective configuration and security.
  • Users note a significant learning curve for effective use of Amazon Inspector's advanced security features and configurations.
  • Users find the limited features of Amazon Inspector restricts its effectiveness in tackling complex security audits.
  • Users find Amazon Inspector not user-friendly, requiring advanced knowledge for effective configuration and security management.

What Are Recent G2 Reviews of Amazon Inspector?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Mend.io

Modern risk doesn't live in one layer, it lives between them. Mend.io is built for every risk, across AI and AppSec, securing the code layer, the AI layer, and the interactions between them. From discovery and red teaming to guardrails and runtime protection, Mend.io delivers continuous protection across the entire AI application lifecycle. Mend.io solutions include: 1. Mend AI secures the layer where modern risk actually lives—the interaction between code and AI. It continuously discovers AI components (agents, prompts, models), tests real behavioral risk through automated red teaming, and enforces in-app runtime guardrails for one continuous control system for the AI lifecycle. 2. Mend AppSec secures the modern code layer by continuously discovering and prioritizing risk across code, libraries, containers, and dependencies, giving teams the clarity they need to reduce exposure and ship secure software faster. 3. Mend Renovate secures the foundation of every codebase by automatically updating dependencies, rating the likelihood each update will succeed without breaking changes, and grouping them by confidence level so teams can resolve them faster.

Average Rating: 4.3/5.0

Total Reviews: 117

How Do G2 Users Rate Mend.io?

  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.2/10)
  • Detection Rate: 10.0/10 (Category avg: 9.0/10)
  • Automated Scans: 9.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 10.0/10 (Category avg: 8.5/10)

Who Is the Company Behind Mend.io?

  • Seller: Mend
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Boston, Massachusetts
  • LinkedIn® Page: www.linkedin.com
    259 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 36% Small, 33% Large

What Do G2 Reviewers Say About Mend.io?

AI-generated summary from verified user reviews

Pros
  • Users highlight the scanning efficiency of Mend.io, enabling seamless integration and effective source code analysis.
  • Users appreciate the ease of use of Mend.io, finding it helpful and easy to integrate into their workflow.
  • Users value the easy integrations with source code repositories, making security management efficient and straightforward.
  • Users praise Mend.io for its quick and accurate scanning capabilities, enhancing efficiency across various platforms.
  • Users value the automated vulnerability detection in Mend.io, enabling quick identification and resolution of critical issues.
Cons
  • Users face integration issues, finding it challenging to connect with on-premise tools and experiencing configuration problems.
  • Users find the limited features of Mend.io challenging, requiring workarounds for integration and specific use cases.
  • Users find missing features in Mend.io, struggling with integration and needing additional functionality for their workflows.
  • Users report complex implementation with numerous issues, including false positives and difficult integration processes.
  • Users find the interface confusing due to navigating between different portals for SAST and SCA products.

What Are Recent G2 Reviews of Mend.io?

What Are G2 Users Discussing About Mend.io?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

How Do G2 Users Rate Edgescan?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Detection Rate: 9.3/10 (Category avg: 9.0/10)
  • Automated Scans: 9.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, enjoying its user-friendly interface and convenient access to essential information.
  • Users value the near false positive free vulnerability scanning of Edgescan, making web application testing efficient and reliable.
  • Users highly value the fantastic customer support from Edgescan, enhancing their overall experience significantly.
  • Users value the validated, near false positive free vulnerability scanning of Edgescan, enhancing their testing experience significantly.
  • Users appreciate the user-friendly console of Edgescan, as it offers easy access and comprehensive functionality for managing vulnerabilities.
Cons
  • Users find the complex UI of Edgescan challenging, leading to inefficiencies and difficulties in task navigation.
  • Users find the limited customization for hosts and filtering frustrating, impacting their ability to adapt to changes.
  • Users find the poor interface design of Edgescan frustrating, hindering efficient navigation and task completion.
  • Users experience slow performance with Edgescan, as scans can take longer due to thorough validation processes.
  • Users find the user interface challenging to navigate, leading to delays and difficulty performing common tasks.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?

APPCHECK

Uncover your full attack surface, test it constantly, act with confidence. AppCheck helps organisations reduce cyber risk, meet compliance requirements and keep pace with evolving threats. Our platform delivers continuous security testing across your attack surface with the depth of a manual penetration test, uncovering vulnerabilities unique to your systems across web applications, APIs and infrastructure. Born from a UK-based penetration testing organisation, AppCheck combines over 20 years of testing expertise with a first-principles approach to security testing. Developed and supported by experienced penetration testers, the platform goes beyond known vulnerability signatures, analysing application behaviour to identify weaknesses that conventional scanning approaches can miss. Using multiple proprietary crawling engines, AppCheck tests modern and traditional technologies, including Single Page Applications (SPAs), APIs and complex authentication flows such as SSO, 2FA and TOTP. Discover: Gain visibility across your attack surface, including forgotten assets and third-party exposure. Assess: Find and validate vulnerabilities with the depth and rigour of a manual penetration test. Take action: Prioritise real-world risk and focus resources on what needs fixing first. Organisations can conduct unlimited security assessments across web applications, SPAs, APIs, cloud services and network infrastructure, covering both internal and external assets. With support for production and UAT environments, AppCheck also helps development teams shift security testing left through integrations with CI/CD pipelines and build tools, including Azure DevOps, GitHub, Jenkins, TeamCity, CircleCI, Bamboo and GitLab CI/CD. This enables automated security testing throughout development, helping teams identify vulnerabilities as changes are introduced. With unlimited scans and users per licence, teams can test continuously without additional charges for each scan, backed by direct UK-based support from security specialists. AppCheck is proud to be a CVE Numbering Authority (CNA), contributing to global vulnerability research.

Average Rating: 4.7/5.0

Total Reviews: 68

How Do G2 Users Rate APPCHECK?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.5/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind APPCHECK?

  • Seller: APPCHECK
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Leeds, GB
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 49% Medium, 31% Small

What Do G2 Reviewers Say About APPCHECK?

AI-generated summary from verified user reviews

Pros
  • Users commend the thorough and reliable vulnerability detection of AppCheck, enhancing security in their applications effectively.
  • Users find the ease of use of AppCheck remarkable, praising its user-friendly interface and responsive support.
  • Users value the excellent pricing and functionality of AppCheck, along with its reliable and intuitive vulnerability scanning.
  • Users find Pentest efficiency remarkable with AppCheck, leading to significant cost savings and streamlined vulnerability detection.
  • Users value the automated scanning feature of AppCheck, enhancing efficiency and streamlining vulnerability management across multiple apps.
Cons
  • Users find the poor customer support frustrating, needing to raise tickets for simple adjustments to the scan list.
  • Users suggest that UX improvements in scoring, customization, and integrations could enhance the AppCheck experience.
  • Users find the API issues frustrating, as endpoint changes require a service request and delays functionality.
  • Users find difficult customization in AppCheck's reporting features, needing more flexibility for contextual adjustments.
  • Users experience a notable difficult learning curve with Appcheck, which may hinder initial ease of use.

What Are Recent G2 Reviews of APPCHECK?

Invicti Web + API (formerly Acunetix)

Invicti Web + API (formerly Acunetix) is a dynamic application security testing (DAST) solution that helps security and development teams find and validate exploitable vulnerabilities across web applications and APIs. Built on the same Acunetix technology and expertise customers already know, Invicti Web + API combines fast, accurate scanning with proof-based validation, modern application coverage, and intelligent automation. With Invicti Web + API, teams can: - Discover and test vulnerabilities across websites, web applications, APIs, single-page applications, and modern JavaScript frameworks - Validate exploitable vulnerabilities with proof-based scanning to reduce false positives and manual verification - Test REST, SOAP, and GraphQL APIs, including complex and stateful application workflows - Integrate security testing into CI/CD, issue tracking, and development workflows so validated findings reach the teams responsible for remediation - Automate recurring application security testing across development and production environments Invicti Web + API serves as the foundation of Invicti’s solution portfolio, extending proven web and API security into the broader Invicti AppSec platform and its agentic pentesting capabilities.

Average Rating: 4.1/5.0

Total Reviews: 100

How Do G2 Users Rate Invicti Web + API (formerly Acunetix)?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.2/10)
  • Detection Rate: 8.5/10 (Category avg: 9.0/10)
  • Automated Scans: 8.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.9/10 (Category avg: 8.5/10)

Who Is the Company Behind Invicti Web + API (formerly Acunetix)?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 40% Large, 34% Medium

What Do G2 Reviewers Say About Invicti Web + API (formerly Acunetix)?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid and precise vulnerability detection in Invicti Web + API, enhancing security for their applications.
  • Users commend the ease of use of Invicti Web + API, appreciating its intuitive interface and seamless integration.
  • Users appreciate the robust security features of Invicti Web + API, ensuring thorough protection for web applications.
  • Users appreciate the effective vulnerability identification capabilities of Invicti, enhancing web application security significantly.
  • Users value the accuracy of results from Invicti Web + API, ensuring reliable vulnerability assessments for web applications.
Cons
  • Users find the pricing of Invicti Web + API to be expensive, limiting accessibility for smaller teams and projects.
  • Users find the complexity in setup and configurations of Invicti Web + API challenging, especially for new users.
  • Users find the complex setup of Invicti Web + API challenging, especially for first-time configurations and integrations.
  • Users experience slow scanning that can hinder normal workflows and complicate the use of the tool.
  • Users find that difficult customization can hinder the integration of Invicti Web + API, requiring extensive technical knowledge.

What Are Recent G2 Reviews of Invicti Web + API (formerly Acunetix)?

What Are G2 Users Discussing About Invicti Web + API (formerly Acunetix)?

Invicti

Invicti (formerly known as Netsparker) is an enterprise application and API security testing platform that helps organizations secure thousands of web applications and APIs at scale while dramatically reducing the risk of attack. Combining advanced DAST and IAST capabilities in a single platform, Invicti enables security teams to continuously identify, prioritize, and remediate vulnerabilities across complex modern environments with confidence and automation. With Invicti, security teams can: - Automate application security testing workflows and save hundreds of hours every month - Discover and secure all web applications and APIs, including forgotten, unmanaged, and shadow assets - Deliver actionable, developer-friendly feedback that helps teams remediate vulnerabilities faster and build more secure code over time - Reduce false positives with proof-based scanning technology that validates exploitable vulnerabilities - Scale application security programs across large enterprises without slowing development teams - Integrate security seamlessly into existing DevSecOps and CI/CD workflows Built for organizations with the most demanding security requirements, Invicti empowers teams to confidently secure their entire attack surface with accuracy, scalability, and automation.

Average Rating: 4.5/5.0

Total Reviews: 69

How Do G2 Users Rate Invicti?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Detection Rate: 9.0/10 (Category avg: 9.0/10)
  • Automated Scans: 9.1/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Invicti?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Large, 29% Medium

What Do G2 Reviewers Say About Invicti?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Invicti, highlighting its quick setup and straightforward report generation.
  • Users value the effective scanning technology of Invicti, enabling accurate identification of vulnerabilities and streamlined workflows.
  • Users value the accuracy and integration capabilities of Invicti, enhancing efficiency and simplifying reporting processes.
  • Users appreciate the well-formatted and easy-to-read reports from Invicti, simplifying certification processes significantly.
  • Users value the super accurate vulnerability detection of Invicti, enhancing their security workflows efficiently.
Cons
  • Users find the customer support inadequate, struggling with timely responses and effective solutions to issues.
  • Users experience slow performance during scans and setup, which affects their overall satisfaction with Invicti.
  • Users experience slow scanning issues with Invicti, affecting efficiency despite good support and solid performance once set up.
  • Users face API scanning issues with Invicti, limiting its effectiveness for their specific needs despite good support.
  • Users find the complex setup to be overwhelming initially, impacting the ease of using Invicti effectively.

What Are Recent G2 Reviews of Invicti?

What Are G2 Users Discussing About Invicti?

VulScan

Automated Vulnerability Scanning. Affordably Priced For Everyone! With almost 70 new hidden vulnerabilities identified every day, you would need to be a super hero with X-ray vision to find them all. Or, you can let VulScan do it for you. VulScan is purpose-built for MSPs and for IT Departments that handle their own IT security. It has all the features you need for both internal and external vulnerability management, but without all the complexity found in older solutions. Best of all, VulScan is priced so that cost is no longer a barrier to scanning as many assets as you need, as frequently as you want. That’s why our slogan is “Vulnerability Management For The Rest of Us! VulScan is an affordable cloud-based vulnerability management platform. It includes the software needed to spin up an unlimited number of virtual network scanner appliances using Hyper-V or VMWare, and a cloud-based portal to control the scanners and manage the discovered issues. For internal network scanning, the appliances can be installed on any existing computer that has excess capacity on the network, or installed on a dedicated box to be permanently installed. You can add multiple scanners and configure them each to scan separate parts of the network to get even faster results pushed into the same client site dashboard at no additional cost. For external scanning, the appliances are installed on the MSP’s data center or other remote location and “pointed” to the public facing IP addresses of the target network.

Average Rating: 4.1/5.0

Total Reviews: 121

How Do G2 Users Rate VulScan?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.2/10)
  • Detection Rate: 7.8/10 (Category avg: 9.0/10)
  • Automated Scans: 8.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 6.9/10 (Category avg: 8.5/10)

Who Is the Company Behind VulScan?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 66% Small, 32% Medium

What Do G2 Reviewers Say About VulScan?

AI-generated summary from verified user reviews

Pros
  • Users love the ease of use of VulScan, praising its simple interface and intuitive scheduling for scanning and reporting.
  • Users value the thorough scanning and intuitive UI of VulScan, enhancing both ease of use and security insights.
  • Users value the detailed reporting features of VulScan, which provide actionable insights and facilitate client communication.
  • Users appreciate the in-depth reporting features of VulScan, enabling easy identification and justification of security vulnerabilities.
  • Users value the scanning efficiency of VulScan, appreciating its ease of use and comprehensive vulnerability reports.
Cons
  • Users criticize the inadequate reporting of VulScan, finding it overwhelming and lacking clear, actionable insights.
  • Users find the difficult UX of VulScan frustrating due to its outdated design and lack of organization features.
  • Users find the difficult setup of VulScan frustrating, with a confusing UI and cumbersome documentation requirements.
  • Users find the limited reporting options inadequate, complicating client communication and overall usability of VulScan.
  • Users are frustrated by the poor customer support from VulScan, experiencing delays and lack of resolution for issues.

What Are Recent G2 Reviews of VulScan?

Saner CVEM

Prevention-first Vulnerability and Exposure Management for unified visibility, prioritization, compliance, and remediation Saner Continuous Vulnerability and Exposure Management unifies asset exposure, posture anomaly detection, vulnerability assessment, compliance management, risk prioritization, patching, and endpoint actions in one dashboard. Saner CVEM is built to help teams continuously detect, assess, prioritize, and remediate vulnerabilities and other security risks from a unified console Why Choose Saner CVEM? • Unified dashboard with interactive views across visibility, detection, prioritization, and remediation for a single source of truth • Complete asset visibility across endpoint and non-endpoint devices, operating system applications, third-party applications, and lifecycle changes • Continuous risk discovery with rapid scans, daily-updated risk intelligence, and posture anomaly detection that helps surface outliers and misconfigurations faster • Context-driven prioritization with SSVC categories such as Act, Attend, Track, and Track* so teams can focus on the risks that deserve action first. • Continuous compliance management with built-in templates, customizable profiles, daily checks, and deviation tracking across common frameworks. • Integrated patching and remediation with vulnerability-to-patch mapping, automated deployment workflows, and endpoint actions from the same ecosystem. • Machine-learning-assisted analysis to identify deeper risk patterns, detect unusual posture, and support smarter remediation decisions. • Customizable, audit-ready reporting for security, IT, and compliance teams that need clearer evidence and easier tracking. • Flexible deployment on cloud or on-premises, with remediation support across Windows, Linux, macOS, and AIX environments.

Average Rating: 4.5/5.0

Total Reviews: 72

How Do G2 Users Rate Saner CVEM?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Detection Rate: 8.9/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 9.1/10 (Category avg: 8.5/10)

Who Is the Company Behind Saner CVEM?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Small, 38% Medium

What Do G2 Reviewers Say About Saner CVEM?

AI-generated summary from verified user reviews

Pros
  • Users value the robust security features of Saner CVEM for effective endpoint management and vulnerability assessments.
  • Users appreciate the rich feature set of Saner CVEM, streamlining security management and enhancing vulnerability assessments efficiently.
  • Users commend the ease of use of Saner CVEM, allowing swift deployment and seamless management across diverse systems.
  • Users commend the exceptional customer support of Saner CVEM, providing assistance during critical deployments and compliance setups.
  • Users value the efficient compliance management of Saner CVEM, facilitating seamless audit preparation and vulnerability tracking.
Cons
  • Users note significant integration issues with Saner CVEM, requiring workarounds for smooth multi-tenant management and legacy software connections.
  • Users find the pricing structure expensive for small organizations, impacting their decision to choose Saner CVEM.
  • Users find the limited features of Saner CVEM restrict effective multi-tenant support and integration capabilities.
  • Users experience slow performance during initial loading and installation, impacting daily checks and onboarding efficiency.
  • Users experience slow scanning during initial dashboard loads and installation, affecting efficiency with large data sets.

What Are Recent G2 Reviews of Saner CVEM?

What Are G2 Users Discussing About Saner CVEM?

Orca Security

The Orca Cloud Security Platform identifies, prioritizes, and remediates risks and compliance issues in workloads, configurations, and identities across your cloud estate spanning AWS, Azure, Google Cloud, Kubernetes, Alibaba Cloud, and Oracle Cloud. Orca offers the industry’s most comprehensive cloud security solution in a single platform — eliminating the need to deploy and maintain multiple point solutions. Orca is agentless-first, and connects to your environment in minutes using Orca’s patented SideScanning™ technology that provides deep and wide visibility into your cloud environment, without requiring agents. In addition, Orca can integrate with third-party agents for runtime visibility and protection for critical workloads. Orca is at the forefront of leveraging Generative AI for simplified investigations and accelerated remediation – reducing required skill levels and saving cloud security, DevOps, and development teams time and effort, while significantly improving security outcomes. As a Cloud Native Application Protection Platform (CNAPP), Orca consolidates many point solutions in one platform, including: CSPM, CWPP, CIEM, Vulnerability Management, Container and Kubernetes Security, DSPM, API Security, CDR, Multi-cloud Compliance, Shift Left Security, and AI-SPM.

Average Rating: 4.7/5.0

Total Reviews: 314

How Do G2 Users Rate Orca Security?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Detection Rate: 8.8/10 (Category avg: 9.0/10)
  • Automated Scans: 9.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.8/10 (Category avg: 8.5/10)

Who Is the Company Behind Orca Security?

  • Seller: Orca Security
  • Company Website:
  • Year Founded: 2019
  • HQ Location: Portland, Oregon
  • LinkedIn® Page: www.linkedin.com
    523 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Security Engineer, Senior Security Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 54% Large, 36% Medium

What Do G2 Reviewers Say About Orca Security?

AI-generated summary from verified user reviews

Pros
  • Users find Orca Security to have a user-friendly interface, making navigation and onboarding exceptionally easy.
  • Users appreciate the rich features and integrations of Orca Security, enhancing visibility and responsiveness to needs.
  • Users value the comprehensive security features of Orca Security, enjoying full visibility and easy implementation.
  • Users appreciate the user-friendly interface of Orca Security, making navigation and integration seamless and straightforward.
  • Users appreciate the enhanced visibility of Orca Security, benefiting from better attack path insights and data posture updates.
Cons
  • Users note significant improvement needed in reporting capabilities and quality of vulnerability validations within Orca Security.
  • Users find feature limitations in Orca Security, citing issues with scheduled reporting and lack of customization options.
  • Users express frustration with the limited features of Orca Security, affecting usability and customization options.
  • Users express dissatisfaction with missing features, such as a cached dashboard and an endpoint agent for non-cloud devices.
  • Users experience ineffective alerts from Orca Security, leading to alert fatigue and missed vulnerabilities in dynamic environments.

What Are Recent G2 Reviews of Orca Security?

What Are G2 Users Discussing About Orca Security?

Microsoft Defender Vulnerability Management

Defender Vulnerability Management delivers asset visibility, intelligent assessments, and built-in remediation tools for Windows, macOS, Linux, Android, iOS, and network devices. Leveraging Microsoft threat intelligence, breach likelihood predictions, business contexts, and devices assessments, Defender Vulnerability Management rapidly and continuously prioritizes the biggest vulnerabilities on your most critical assets and provides security recommendations to mitigate risk. Reduce risk with continuous vulnerability assessment, risk-based prioritization, and remediation. Defender Vulnerability Management is available for cloud workloads and endpoints. Defender for Endpoint Plan 2 customers can access advanced vulnerability management capabilities with the Defender Vulnerability Management add-on, now generally available.

Average Rating: 4.4/5.0

Total Reviews: 34

How Do G2 Users Rate Microsoft Defender Vulnerability Management?

  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • Detection Rate: 8.3/10 (Category avg: 9.0/10)
  • Automated Scans: 7.2/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 7.2/10 (Category avg: 8.5/10)

Who Is the Company Behind Microsoft Defender Vulnerability Management?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 41% Small, 35% Large

What Are Recent G2 Reviews of Microsoft Defender Vulnerability Management?

Detectify

Detectify sets a new standard for advanced application security testing, challenging traditional DAST by providing evolving coverage of each and every exposed asset across the changing attack surface. AppSec teams trust Detectify to expose how attackers will exploit their Internet-facing applications. The Detectify platform automates continuous real-world, payload-based attacks fuelled by its global community of elite ethical hackers into its own expert-built engines, exposing critical weaknesses before it's too late. The Detectify solution includes: - Automated discovery of known and unknown digital assets via domain & cloud connectors - Continuous coverage (24/7) of every corner of the attack surface with dynamic testing. Not just predefined targets - 100% payload-based testing fuelled by elite ethical hackers for a high signal-to-noise ratio - Distributed coverage across an unmatched array of relevant technologies - Actionable remediation tips for software development teams - Team functionality to easily share reports - Powerful integrations platform to prioritize and triage vulnerability findings onward to development teams -Advanced API functionality -Capabilities to set custom attack surface security policies

Average Rating: 4.5/5.0

Total Reviews: 50

How Do G2 Users Rate Detectify?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.2/10)
  • Detection Rate: 8.5/10 (Category avg: 9.0/10)
  • Automated Scans: 9.0/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.3/10 (Category avg: 8.5/10)

Who Is the Company Behind Detectify?

  • Seller: Detectify
  • Year Founded: 2013
  • HQ Location: Stockholm, Sweden
  • LinkedIn® Page: www.linkedin.com
    94 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 46% Small, 37% Medium

What Do G2 Reviewers Say About Detectify?

AI-generated summary from verified user reviews

Pros
  • Users appreciate Detectify's automation capabilities, enabling effective and customizable security testing with easy integrations.
  • Users appreciate the ease of automation in testing with Detectify, enhancing security efforts without complex setups.
  • Users appreciate the customizability of Detectify, allowing easy integration and tailored security testing for diverse needs.
  • Users appreciate the dynamic application security testing capabilities of Detectify, easily integrating it into existing workflows.
  • Users appreciate the dynamic application security testing capabilities of Detectify, making security integration seamless and effective.
Cons
  • Users find the complexity of initial setup a hurdle that complicates their experience with Detectify.
  • Users find the complex queries in Detectify lacking, especially in terms of GraphQL support and clarity on outcomes.
  • Users find the complex setup of Detectify challenging, leading to a cumbersome experience during initial configuration.
  • Users find Detectify expensive when testing multiple sites, which may limit its accessibility for some.
  • Users find the inaccuracy in spidering results problematic, hindering their ability to verify complete assessments of applications.

What Are Recent G2 Reviews of Detectify?

What Are G2 Users Discussing About Detectify?

Jit

Jit is redefining application security by introducing the first Agentic AppSec Platform, seamlessly blending human expertise with AI-driven automation. Designed for modern development teams, Jit empowers organizations to proactively manage security risks across the entire software development lifecycle.​ AI-Powered Agents Jit's AI Agents, such as SERA (Security Evaluation and Remediation Agent) and COTA (Communication, Ops, and Ticketing Agent), collaborate with your teams to automate vulnerability triage, risk assessment, and remediation processes, significantly reducing manual workloads. ​ Comprehensive Security Scanning Achieve full-stack security coverage with integrated scanners for SAST, DAST, SCA, IaC, CSPM, and more. Jit's platform ensures continuous monitoring and immediate feedback on code changes, facilitating rapid identification and resolution of security issues. ​ Developer-Centric Experience With integrations into popular IDEs and CI/CD pipelines, Jit provides developers with contextual security insights directly within their workflows, promoting a shift-left approach without disrupting productivity. ​ Agentic AI for AppSec Teams Risk-Based Prioritization Utilizing the Model Context Protocol (MCP), Jit evaluates vulnerabilities in the context of runtime environments, business impact, and compliance requirements, enabling teams to focus on the most critical risks. ​ Seamless Integrations Jit integrates with a wide array of tools, including GitHub, GitLab, AWS, Azure, GCP, Jira, Slack, and more, ensuring that security processes are embedded within your existing technology stack. ​

Average Rating: 4.5/5.0

Total Reviews: 43

How Do G2 Users Rate Jit?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Detection Rate: 8.4/10 (Category avg: 9.0/10)
  • Automated Scans: 8.6/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.4/10 (Category avg: 8.5/10)

Who Is the Company Behind Jit?

  • Seller: jit
  • Year Founded: 2021
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    161 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 44% Medium, 42% Small

What Do G2 Reviewers Say About Jit?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automated and lightweight security controls of Jit, enhancing workflows without adding complexity.
  • Users praise the easy integrations of Jit, which streamline security management within existing development workflows effortlessly.
  • Users value the ease of use of Jit, enjoying seamless integration and simplified management within their workflows.
  • Users value the efficiency of Jit, streamlining workflows and reducing excess with lightweight, automated security controls.
  • Users appreciate the seamless integration support of Jit, enhancing their development workflow without added complexity.
Cons
  • Users face integration issues with Jit, as it lacks comprehensive support for all enterprise environments and tools.
  • Users find the limited features of Jit hinder integrations and onboarding, affecting complex environments and documentation quality.
  • Users experience limited integration capabilities with Jit, particularly for advanced configurations and third-party tools.
  • Users frequently find the documentation lacking, particularly for advanced configurations and integrations with third-party tools.
  • Users find the complexity of Jit overwhelming, particularly with advanced integrations and configuration for beginners.

What Are Recent G2 Reviews of Jit?

Defendify All-In-One Cybersecurity Solution

Founded in 2017, Defendify is pioneering All-In-One Cybersecurity® for organizations with growing security needs, backed by experts offering ongoing guidance and support. Delivering multiple layers of protection, Defendify provides an all-in-one, easy-to-use platform designed to strengthen cybersecurity across people, process, and technology, continuously. With Defendify, organizations streamline cybersecurity assessments, testing, policies, training, detection, response & containment in one consolidated and cost-effective cybersecurity solution. 3 layers, 13 solutions, 1 platform, including: • Managed Detection & Response • Cyber Incident Response Plan • Cybersecurity Threat Alerts • Phishing Simulations • Cybersecurity Awareness Training • Cybersecurity Awareness Videos • Cybersecurity Awareness Posters & Graphics • Technology Acceptable Use Policy • Cybersecurity Risk Assessments • Penetration Testing • Vulnerability Scanning • Compromised Password Scanning • Website Security Scanning See Defendify in action at www.defendify.com.

Average Rating: 4.7/5.0

Total Reviews: 57

How Do G2 Users Rate Defendify All-In-One Cybersecurity Solution?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.2/10)
  • Detection Rate: 9.2/10 (Category avg: 9.0/10)
  • Automated Scans: 9.4/10 (Category avg: 9.1/10)
  • Configuration Monitoring: 8.9/10 (Category avg: 8.5/10)

Who Is the Company Behind Defendify All-In-One Cybersecurity Solution?

  • Seller: Defendify
  • Year Founded: 2017
  • HQ Location: Portland, Maine
  • LinkedIn® Page: www.linkedin.com
    38 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 65% Small, 35% Medium

What Do G2 Reviewers Say About Defendify All-In-One Cybersecurity Solution?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Defendify, making cybersecurity management seamless and efficient for their teams.
  • Users appreciate the comprehensive and cost-effective cybersecurity features of Defendify, enhancing security management for organizations.
  • Users appreciate the easy setup of Defendify, allowing quick implementation and seamless integration into existing systems.
  • Users value the comprehensive and cost-effective features of Defendify, enhancing their cybersecurity management efficiently.
  • Users value the effective threat monitoring of Defendify, enhancing their cybersecurity posture with comprehensive protection.
Cons
  • Users express concerns about inadequate reporting, wishing for improvements like custom options and concise summaries.
  • Users find the reporting features inadequate, noting the need for concise summaries and customizable options for better insights.
  • Users desire a more concise format and detailed reporting for penetration tests in Defendify's solution.
  • Users find the lack of limited customization options disappointing, desiring co-branding and custom reporting features.
  • Users find the lack of custom reporting options a limitation, which could enhance personalized data monitoring.

What Are Recent G2 Reviews of Defendify All-In-One Cybersecurity Solution?

What Are G2 Users Discussing About Defendify All-In-One Cybersecurity Solution?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated