Best Vendor Security and Privacy Assessment Software - Page 8

How Many Vendor Security and Privacy Assessment Software Products Does G2 Track?

Total Products under this Category: 140

Category Stats (Sep 2026)

  • Average Rating: 4.56/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Skypher (+0.29%) - Among all products in this category, Skypher recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Vendor Security and Privacy Assessment Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 16,100+ Authentic Reviews
  • 140+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

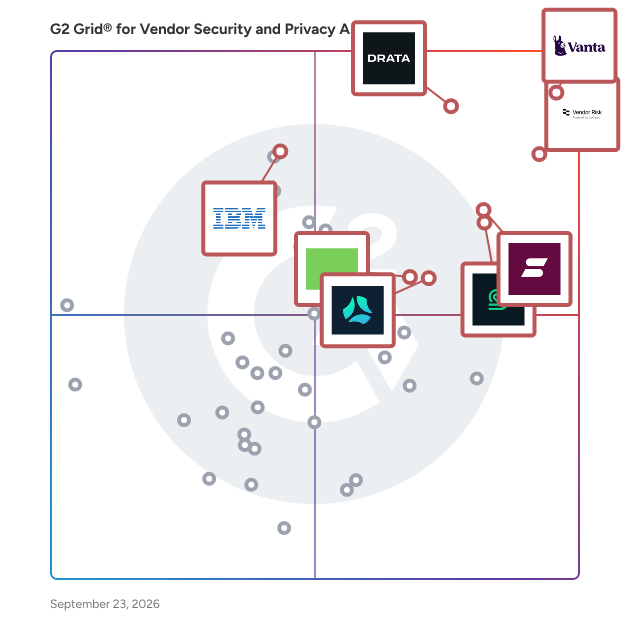
G2 Grid® for Vendor Security and Privacy Assessment Software

G2 Grid® for Vendor Security and Privacy Assessment Software plotting products by satisfaction and market presence

Highlighted products: Vanta, UpGuard Vendor Risk, Drata, Sprinto, Secureframe, Scrut Automation, IBM OpenPages, and Thoropass.

Underlying data: [Grid® JSON](https://www.g2.com/categories/vendor-security-and-privacy-assessment/grids.json?focus%5B%5D=vanta&focus%5B%5D=upguard-vendor-risk&focus%5B%5D=drata&focus%5B%5D=sprinto-inc&focus%5B%5D=secureframe&focus%5B%5D=scrut-automation&focus%5B%5D=ibm-openpages&focus%5B%5D=thoropass)

iTrust

iTrust is the cornerstone of your cyber defense, offering a cutting-edge platform for cybersecurity intelligence. It's designed not only to evaluate and enhance the of your but also to provide a detailed analysis of your organization s own and comprehensive risk assessment security posture third-party networks cybersecurity strengths vulnerabilities iTrust turns insights into action, empowering you to build fortified, trust-based, partners, and suppliers, while ensuring you against the evolving cyber threat landscape.

Who Is the Company Behind iTrust?

  • Seller: iTrust
  • Year Founded: 2016
  • HQ Location: Atlanta, US
  • Twitter: @iTrust_Inc
    11 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

Kertos

Kertos is an all-in-one compliance platform that combines powerful technology with the support of certified experts to allow companies to manage privacy and compliance requirements, certifications, audits, and processes for frameworks like GDPR, AI Act, ISO27001, NIS2, ISO42001, TISAX®, SOC2, and C5 fast and efficiently with full ownership and guarantee for success. By leveraging workflow automation, expert support, and AI, Kertos provides peace of mind, ensuring seamless and continuous compliance. Based in Germany and crafted for the European market, Kertos simplifies InfoSec and Data Privacy through automated tool and data discovery, vendor management, privacy documentation, automated data subject requests, incident management and risk mitigation, LMS for training courses, automated policy maker and manager, compliance checks, and a trust center.

Average Rating: 4.8/5.0

Total Reviews: 60

How Do G2 Users Rate Kertos?

  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Kertos?

  • Seller: Kertos
  • Year Founded: 2021
  • HQ Location: München, DE
  • LinkedIn® Page: www.linkedin.com
    81 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: CEO, Chief of Staff
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 82% Small, 18% Medium

What Do G2 Reviewers Say About Kertos?

AI-generated summary from verified user reviews

Pros
  • Users find Kertos makes GDPR compliance manageable with structured workflows and responsive support, enhancing their operations significantly.
  • Users value Kertos for its extensive automation of compliance processes, significantly streamlining operations in healthcare data management.
  • Users find Kertos easy to use, thanks to its intuitive interface and helpful features for ISO 27001 compliance.
  • Users value the step-by-step instructions of Kertos, enhancing their confidence and efficiency with ISO 27001 compliance.
  • Users value the seamless GDPR compliance automation of Kertos, significantly reducing manual tasks and enhancing efficiency.
Cons
  • Users note the limited customization options in Kertos, especially regarding the reporting section, which could be improved.
  • Users experience a short learning curve with Kertos, but support ensures they can unlock its full potential.
  • Users experience integration issues due to initial setup requirements, especially with niche or customized systems.
  • Users find the difficult setup of Kertos challenging initially, especially with niche or customized system integrations.
  • Users experience lack of clarity due to frequent system changes, causing confusion despite responsive customer support.

What Are Recent G2 Reviews of Kertos?

Knowally

Knowally automates security questionnaire responses for B2B software vendors. Upload your existing security documentation once — SOC 2 reports, policies, ISO 27001 controls — and Knowally's AI uses that knowledge to auto-fill incoming CAIQ, SIG, DDQ, VSA, and custom security questionnaires. The platform includes an Answer Library for storing and reusing approved responses, and exports to XLSX, CSV, or DOCX for delivery. Built for InfoSec and GRC teams that are drowning in repetitive compliance questionnaires during their sales or procurement cycles. GDPR-compliant, hosted in the EU.

Who Is the Company Behind Knowally?

Lema

Lema is an advanced Third-Party Risk Management platform designed to help organizations proactively manage and mitigate risks associated with their vendors, service providers, contractors, and partners. By continuously monitoring third-party interactions with critical business units and assets, Lema collects intelligence feeds on their activities and automatically detects gaps in their attestations. This enables automated vendor assessments, real-time risk mitigation, and minimizes the business impact of third-party incidents. Key Features and Functionality: - Continuous Third-Party Monitoring: Lema bridges the gap between Governance, Risk, and Compliance processes and operational activities by continuously monitoring discrepancies between agreed-upon terms and actual third-party interactions with critical assets and business units. - Automated Risk Assessments: The platform's Proactive TPRM module automatically detects changes in third-party risk by monitoring engagements and external intelligence feeds, alerting users to new risks and suggesting mitigating actions. - Real-Time Risk Mitigation: Lema enables organizations to proactively take risk-mitigating actions based on the actual context of third-party interactions, minimizing the business impact of potential incidents. - Always Up-to-Date Third-Party Inventory: The platform instantly creates and maintains an up-to-date third-party inventory, eliminating manual spreadsheet management and ensuring organizations are always aware of their vendor engagements. - Automatic Third-Party Artifact Gap Analysis: Lema's fine-tuned LLM module analyzes third-party artifacts, extracting critical risk information and detecting gaps based on compliance controls and risk appetite. - Integration of Intelligence Feeds: The platform continuously gathers real-time data from third-party websites, news, threat intelligence feeds, trust centers, and other public databases to build accurate third-party profiles and identify potential risks before they escalate. Primary Value and Problem Solved: Lema addresses the challenges organizations face in managing third-party risks by transforming traditional, static risk assessments into dynamic, real-time evaluations. By automating vendor assessments and continuously monitoring third-party interactions, Lema empowers organizations to proactively identify and mitigate risks, ensuring business continuity and resilience. This proactive approach minimizes the business impact of third-party incidents and enhances overall risk management efficiency.

Who Is the Company Behind Lema?

MetricStream Third-Party Management

The MetricStream Third-Party Management App enables a comprehensive process to identify, assess, mitigate, and monitor third-party risks, as well as to manage compliance. The app streamlines third-party information gathering, due diligence, onboarding, real-time monitoring, and risk and control assessments.

Who Is the Company Behind MetricStream Third-Party Management?

  • Seller: MetricStream
  • Year Founded: 1999
  • HQ Location: San Jose, CA
  • Twitter: @MetricStream
    4,383 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,205 employees on LinkedIn®

Noru

Noru is the AI-powered GRC platform that turns compliance from a cost center into a growth driver. We help modern businesses get — and stay — compliant with frameworks like SOC 2, ISO 27001, GDPR, NIS2, and more in days, not months. Noru's autonomous AI agents continuously gather evidence, map controls across multiple frameworks, and monitor your environment so you’re always audit-ready. Unlike checklist tools, Noru goes beyond passing audits — it transforms your compliance status into a live trust signal you can share with customers to shorten security reviews, win deals faster, and stand out from competitors. With Noru you can: Get compliant in a fraction of the time Reduce manual busywork with fully automated evidence collection Maintain readiness year-round with continuous monitoring Build trust and accelerate revenue with real-time compliance sharing

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind Noru?

  • Seller: Noru
  • Year Founded: 2025
  • HQ Location: Stockholm, SE
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About Noru?

AI-generated summary from verified user reviews

Pros
  • Users find the Compliance process enjoyable and straightforward, providing clear guidance at every step.
  • Users find that Noru makes compliance fun and easy, providing clear guidance every step of the way.
  • Users find compliance management easy and engaging with Noru, as it guides them clearly through every step.
  • Users love how Noru makes Compliance fun and easy, providing clear guidance through every step of the process.
  • Users find Noru's ease of use makes compliance enjoyable with clear guidance throughout every step.

What Are Recent G2 Reviews of Noru?

Openly

Openly is a technology-driven insurance provider specializing in premium homeowners insurance, designed to empower independent agents and simplify the insurance process for consumers. By leveraging advanced data analytics and modern technology, Openly offers comprehensive coverage options that are both transparent and easy to understand. Founded by industry veterans, the company focuses on delivering superior insurance products through a network of trusted independent agents, ensuring personalized service and expert advice for homeowners. Key Features and Functionality: - Rapid Quoting Process: Agents can generate fully underwritten policies in as little as 15 seconds, streamlining the traditionally time-consuming quoting process. - Comprehensive Coverage: Policies include features like guaranteed replacement cost coverage up to $5 million, endorsements for home-sharing, and optional coverage for losses arising from cyberbullying. - Agent Empowerment: Openly's platform is designed to support independent agents by providing state-of-the-art technology, improved products, and lead generation support, enabling them to better serve their clients. - Transparent Policies: The company emphasizes clear and straightforward policy terms, reducing the complexity often associated with homeowners insurance. Primary Value and User Solutions: Openly addresses the inefficiencies and opaqueness prevalent in the traditional insurance industry by offering a transparent, efficient, and comprehensive insurance solution. For independent agents, Openly's platform reduces administrative burdens, allowing them to focus on providing personalized advice and service. Homeowners benefit from more extensive coverage options, competitive pricing, and a simplified insurance experience. By combining technology with human expertise, Openly enhances trust and satisfaction among both agents and policyholders.

Who Is the Company Behind Openly?

Phinity Risk Solutions

The Phinity Risk Solutions integrate into your risk and compliance processes to help you decrease your risk and compliance exposure. Boost your risk management capability and manage your organisational risks, from identification through to remediation. Make informed decisions faster with our reporting. Our key solutions include: - Essential Risk Management - Third Party Risk Management (TPRM) - ISMS Management - Insurance Compliance Management - Vulnerability Management - Risk Remediation Management

Who Is the Company Behind Phinity Risk Solutions?

Prosikon Vendor Due Diligence

Prosikon Vendor Due Diligence is a secure, invite-only platform developed by Arrakis Consulting, Inc., designed to streamline the assessment and monitoring of third-party vendors' cybersecurity readiness. This enterprise-grade solution enables organizations to evaluate, score, and track the security posture of their suppliers through a structured and auditable process. The platform offers structured questionnaires tailored to various aspects of cybersecurity, including governance, access control, incident response, and data protection. Vendors respond to these assessments by providing detailed answers and uploading supporting evidence such as policies, certifications, and screenshots. Each response is scored against a weighted rubric, allowing organizations to quantify risk and compare vendors objectively. The system maintains a comprehensive audit trail, logging every response change with full version history to ensure audit readiness. Prosikon's assessment workflow is straightforward and efficient. Organizations can configure assessments by creating weighted categories and adding scored questions aligned with regulatory requirements. Vendors are invited securely through unique codes delivered via email, QR code, or shareable link, ensuring private access without public sign-ups. Vendors complete the assessments at their own pace, with progress saved automatically, and organizations can review scores, compare vendors, and generate detailed reports with full scoring details and regulatory references. Key features of Prosikon include weighted category scoring, auto-fail and regulatory flags for critical questions, secure evidence uploads, real-time dashboards, vendor comparison tools, re-assessment scheduling with reminders, role-based access control, and end-to-end encryption with AES-256. The platform is built on zero-trust principles, ensuring data security through invite-only access, isolated file storage per vendor, and full response version history for audit trails. By utilizing Prosikon, organizations can enhance their vendor risk management programs, make informed procurement decisions, and maintain compliance with various regulatory frameworks. The platform's comprehensive capabilities provide a structured, scored, and auditable approach to vendor cybersecurity assessments, reducing the effort and stress associated with traditional methods. For more information, visit the Prosikon website: https://prosikon.arrakisconsulting.com/

Who Is the Company Behind Prosikon Vendor Due Diligence?

Qubixor

Qubixor is a comprehensive platform designed to help organizations assess, benchmark, and enhance their post-quantum cryptographic maturity. As quantum computing advances, traditional encryption methods face increasing vulnerabilities. Qubixor addresses this challenge by offering tools and resources that enable businesses to evaluate their readiness for the post-quantum era, compare their status with industry standards, and develop strategic migration plans. Key Features and Functionality: - Post-Quantum Maturity Assessment: Utilizes the Qubixor Post-Quantum Maturity Model (QPQMM) to evaluate an organization's current cryptographic posture across five levels, from Unaware to Proactive. - Benchmarking: Allows organizations to compare their maturity scores with anonymized market and sector benchmarks, providing insights into their standing relative to peers. - E-Learning Modules: Offers self-paced courses on post-quantum cryptography, catering to different expertise levels, and provides certificates upon completion. - Ecosystem Collaboration: Enables organizations to invite partners and suppliers to assess their readiness, fostering a comprehensive security view of the entire ecosystem. - Awareness Quizzes: Facilitates the launch of multi-level quizzes to educate employees, track participation, and measure knowledge on post-quantum topics. Primary Value and Solutions Provided: Qubixor empowers organizations to proactively prepare for the impending quantum computing era by: - Identifying Vulnerabilities: Helps detect potential weaknesses in current cryptographic systems that could be exploited by quantum technologies. - Ensuring Regulatory Compliance: Aligns with standards such as NIST, ANSSI, ENISA, NIS2, DORA, and eIDAS, assisting organizations in meeting regulatory requirements for cryptographic risk management. - Facilitating Strategic Planning: Provides actionable insights and structured roadmaps for transitioning to post-quantum cryptographic solutions, ensuring data security against future threats. By leveraging Qubixor, organizations can safeguard sensitive information, maintain compliance with evolving regulations, and stay ahead in the rapidly changing cybersecurity landscape.

Who Is the Company Behind Qubixor?

Relixi - Compliance Automation

Automating Trust in Compliance Relixi is a B2B SaaS compliance automation platform focusing on Security and Privacy domain to perform Automated, Paperless Compliance & Assessments. The tool is powered by Riskpro and comes with a preloaded compliance framework library which includes SOC 2, ISO 27001, GDPR, AI Act, DPDPA, and many more! Unlimited Security and Privacy Possibilities Relixi is a compliance automation platform that bundles pre-loaded content specific to your industry and company size and tech stack. Answer a few questions and Click "Load" to immediately load 30-50% of content for your compliance journey. It is meant to be used as a DIY Tool so that with little support, you can maximize value. Our team provided expertise and hand holding as needed. Relixi is built as a modular platform where each area of compliance such as ISO 27001, SOC2, Vendor Risk Management etc can be enabled as a module and all related forms and formats are activated instantly. Single Platform with unlimited users for all your compliance needs. The best part is content is complimentary. Annual subscription plans starting at Rs. 10,000 pm*.

Who Is the Company Behind Relixi - Compliance Automation?

Rescana

Rescana is a cybersecurity company focused on Third-Party Risk Management (TPRM) and External Attack Surface Management (EASM). It was founded in 2016 and has evolved into a platform that uses AI-powered automation to streamline how organizations assess and manage the security risks posed by their vendors and external digital assets. What Rescana Does: Rescana automates the traditionally manual and time-consuming processes of TPRM by: 1. Vendor Discovery & Classification Automatically identifies and classifies vendors, even those without a web presence, using AI and OSINT (open-source intelligence). 2. Risk Assessment Runs autonomous, on-demand security assessments and generates detailed risk profiles for vendors, integrating questionnaires, external scans, and organizational policies. 3. Remediation Guidance Offers actionable remediation steps and guidance based on the specific risks found. 4. Interactive Chat-Based Interface Enables users to interact with the system like a chatbot (powered by LLMs), asking questions about vendors, risks, policies, and controls. 5. Support for ESG and Multiple Questionnaire Formats Handles diverse compliance needs, including environmental, social, and governance (ESG) questionnaires, and supports multiple formats per vendor. Key Differentiators: • Agentic AI: Not just automation — Rescana employs autonomous agents that reason through questionnaire filling, evidence matching, and more. • No ticketing system needed: Unlike competitors, it doesn’t require manual back-and-forth with vendors. • Live risk dashboards: With real-time scanning and risk scoring. • Low false positives: Thanks to contextual analysis and risk validation. • Vendor Simulator: For demos and internal testing of workflows using simulated vendor responses.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind Rescana?

  • Seller: Rescana
  • Year Founded: 2017
  • HQ Location: New York, US
  • LinkedIn® Page: www.linkedin.com
    19 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Rescana?

What Are G2 Users Discussing About Rescana?

ResponseHub

ResponseHub is a security questionnaire automation platform that uses AI to help organizations complete vendor security assessments and compliance questionnaires. The tool processes security questionnaires in various spreadsheet formats and automatically generates answers by referencing uploaded policy documents, SOPs, and other organizational documentation. The platform maintains an automated knowledge base that stores previously answered questions and suggests new entries based on completed questionnaires. Each generated answer includes citations to specific policies, sections, pages, and sentences to provide traceability and confidence in responses. The tool includes an AI-powered parser that handles complex spreadsheet structures with multiple sheets and ambiguous column headers. Users can upload Excel files containing questionnaires, and the system extracts questions across all sheets, then allows downloading of the completed file with answers in the correct locations. ResponseHub provides question explainers to help users understand what each question means, confidence ratings for generated answers, and an AI-assisted writer for questions without existing references. The platform supports question assignment and delegation to subject matter experts with change tracking and approval workflows. Users can import existing knowledge bases from CSV files or generate templates based on the NIST Cybersecurity Framework 2.0. The system monitors changes to source documents and prompts users to refresh knowledge base entries to maintain accuracy.

Who Is the Company Behind ResponseHub?

RiskAssessmentAI

Security Questionnaire Automation Meet RiskAssessmentAI – The platform that uses artificial intelligence to automate security questionnaire responses. How can I automate security questionnaires? 1. Upload your IT, HR, GRC policies and procedures, any previous risk assessments you’ve completed or security questionnaires to the RiskAssessmentAI platform. 2. The RiskAssessmentAI platform uses Artificial Intelligence (AI) to deep search and scan your documentation, and builds a highly-accurate knowledge base. 3. Upload (or email) risk assessments and cyber security questionnaires you receive from your customers or prospects. Within minutes, the platform completes it for you. 4. Mark the assessment or questionnaire as approved, and send it back! You can get back to focusing on what matters.

Who Is the Company Behind RiskAssessmentAI?

Risk Quantifier (RQ)

Nehemiah Security provides a simple SaaS solution, Risk Quantifier™ (RQ), that continuously measures financial loss related to cyber risk to enable businesses to make more informed decisions. RQ automates cyber risk quantification in hours, not months. By reducing the effort and costs associated with financial data risk assessment (FinDRA), businesses of all sizes can benefit from managing risk and the ROI of security investments. Our expert risk and financial models are based upon the most current market information. RQ layers this financial risk data into trusted cybersecurity frameworks such as the US NIST and MITRE ATT&CK™ to visualize the effects over time; thus, enabling organizations to report quantified the cyber risk to their Boards of Directors in terms of financial outcomes. RQ 3.0, incorporates vital feedback from our users and includes advanced features that quantify the magnitude of potential financial losses in real-time, providing details about attacks and losses, and delivering even more visibility into the attack landscape.

Who Is the Company Behind Risk Quantifier (RQ)?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated October 3, 2024