Best Penetration Testing Tools - Page 2

How Many Penetration Testing Tools Products Does G2 Track?

Total Products under this Category: 200

Category Stats (Nov 2026)

  • Average Rating: 4.64/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CybaOps (+4.75%) - Among all products in this category, CybaOps recorded the largest rating increase compared to last month

Last updated: November 01, 2026

How Does G2 Rank Penetration Testing Tools Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,900+ Authentic Reviews
  • 200+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

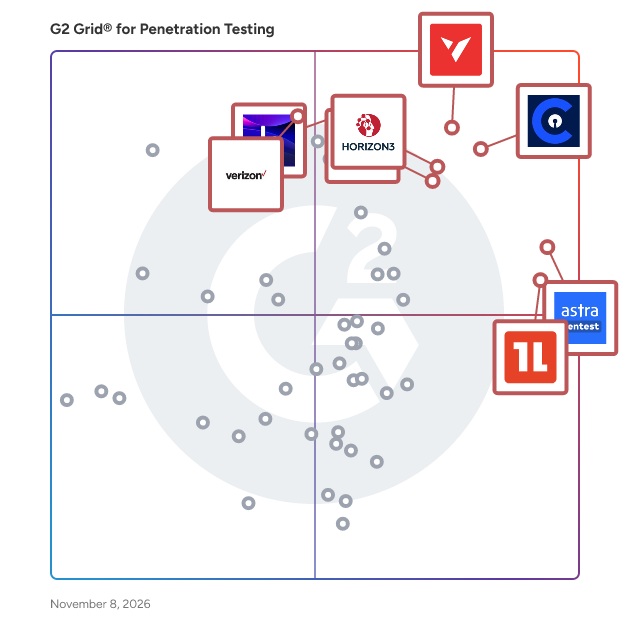
G2 Grid® for Penetration Testing Tools

G2 Grid® for Penetration Testing Tools plotting products by satisfaction and market presence

Highlighted products: Cobalt, vPenTest, Astra Pentest, NodeZero from Horizon3, Oneleet, Pentera, H1 Platform, and Verizon Penetration Testing.

Underlying data: [Grid® JSON](https://www.g2.com/categories/penetration-testing-tools/grids.json?focus%5B%5D=cobalt-io-cobalt&focus%5B%5D=vpentest&focus%5B%5D=astra-pentest&focus%5B%5D=nodezero-from-horizon3&focus%5B%5D=oneleet&focus%5B%5D=pentera&focus%5B%5D=h1-platform&focus%5B%5D=verizon-penetration-testing)

Metasploit

Metasploit is a comprehensive penetration testing platform developed by Rapid7, designed to help security professionals identify, exploit, and validate vulnerabilities within their networks. By simulating real-world attacks, Metasploit enables organizations to assess their security posture and enhance their defenses against potential threats. Key Features and Functionality: - Extensive Exploit Library: Access to a vast, regularly updated database of over 1,500 exploits and 3,300 modules, allowing users to simulate a wide range of attack scenarios. - Automated Exploitation: Features like Smart Exploitation and automated credential brute-forcing streamline the penetration testing process, increasing efficiency and accuracy. - Post-Exploitation Modules: Over 330 post-exploitation modules enable testers to assess the impact of a successful breach and gather critical information from compromised systems. - Credential Testing: Ability to run brute-force attacks against more than 20 account types, including databases, web servers, and remote administration tools, to uncover weak or reused passwords. - Integration Capabilities: Seamless integration with other Rapid7 products, such as InsightVM and Nexpose, facilitates closed-loop vulnerability validation and remediation prioritization. Primary Value and Problem Solving: Metasploit empowers organizations to proactively identify and address security weaknesses before malicious actors can exploit them. By simulating real-world attacks, it provides valuable insights into potential vulnerabilities, enabling security teams to prioritize remediation efforts effectively. This proactive approach enhances overall security awareness, reduces the risk of breaches, and ensures compliance with industry standards and regulations.

Average Rating: 4.6/5.0

Total Reviews: 53

How Do G2 Users Rate Metasploit?

  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.4/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Metasploit?

  • Seller: Rapid7
  • Year Founded: 2000
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    8,746 employees on LinkedIn®
  • Ownership: NASDAQ:RPD
  • Total Revenue (USD mm): $411

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 47% Small, 40% Medium

What Do G2 Reviewers Say About Metasploit?

AI-generated summary from verified user reviews

Pros
  • Users value the pentesting efficiency of Metasploit, appreciating its extensive toolkit and versatile payload creation.
  • Users commend Metasploit for its expertise in payload creation, making it a top choice for hackers.
Cons
  • Users find the complex setup of Metasploit challenging and suggest that automation would improve usability.

What Are Recent G2 Reviews of Metasploit?

What Are G2 Users Discussing About Metasploit?

BeEF

BeEF is short for The Browser Exploitation Framework. It is a penetration testing tool that focuses on the web browser.

Average Rating: 4.4/5.0

Total Reviews: 11

How Do G2 Users Rate BeEF?

  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 6.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind BeEF?

  • Seller: BeEF
  • Year Founded: 2008
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 58% Small, 33% Medium

What Are Recent G2 Reviews of BeEF?

What Are G2 Users Discussing About BeEF?

Pentest-Tools.com

Vulnerability detection | Autonomous pentesting | Human expertise Built by offensive security practitioners, Pentest-Tools.com gives security teams a unified place to test their defenses continuously, go deeper when needed, and prove what needs to be fixed. Pentest-Tools.com covers multiple classes of assets, from web applications to network and cloud infrastructures, with daily detection and exploitation updates. Experienced offensive security professionals, including our customers and our own services team, constantly battle-test it across numerous engagements. Their feedback helps us keep improving the product so it delivers: ✔️ a low false positive rate ✔️ rich evidence, including screenshots, attack replay, data snippets, and more ✔️ detailed, customizable reporting Behind all of this, our vulnerability research team proactively looks for new security issues in widely used software and explores attack techniques, using them to enrich our exploit database and vulnerability feed. Unlike vulnerability scanners that primarily stop at detection, or testing approaches built around a single level of depth, Pentest-Tools.com lets teams match testing depth to the situation. Security teams can: ✔️ control what gets tested, how & when with deterministic Scanning & Validation ✔️ investigate web apps on-demand with autonomous AI Pentests ✔️ bring in human-led Offensive Security Services when business context, independent attestation, or custom reporting matter. As the target or situation changes, internal security teams can move between these testing modes without changing vendors or breaking their workflow.

Average Rating: 4.8/5.0

Total Reviews: 110

How Do G2 Users Rate Pentest-Tools.com?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.9/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.2/10 (Category avg: 9.2/10)
  • Extensibility: 6.9/10 (Category avg: 8.8/10)

Who Is the Company Behind Pentest-Tools.com?

Who Uses This Product?

  • Who Uses This: CEO
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 67% Small, 19% Medium

What Do G2 Reviewers Say About Pentest-Tools.com?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Pentest-Tools.com, appreciating its straightforward setup and user-friendly features.
  • Users value the automation of scans on Pentest-Tools.com, enabling efficient and reliable vulnerability management with minimal manual effort.
  • Users commend the exceptional customer support from Pentest-Tools.com, highlighting their responsiveness and willingness to assist.
  • Users value the efficiency of Pentest-Tools.com, appreciating its comprehensive and user-friendly penetration testing capabilities.
  • Users appreciate the easy scheduling features of Pentest-Tools.com, significantly streamlining their vulnerability management process.
Cons
  • Users face difficult customization in Pentest-Tools.com due to limited report editing and template options, hindering flexibility.
  • Users feel the limited features of Pentest-Tools.com hinder report customization and timely scan test reports.
  • Users note that slow scanning can hinder efficiency, complicating the user experience with Pentest-Tools.com.
  • Users find the manual work required for complex findings somewhat annoying, especially when dealing with numerous assets.
  • Users find the interface confusing, wishing for more intuitive navigation and better integration capabilities.

What Are Recent G2 Reviews of Pentest-Tools.com?

What Are G2 Users Discussing About Pentest-Tools.com?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Indusface WAS

Indusface WAS (Web Application Scanner) provides comprehensive managed dynamic application security testing (DAST) solution. It is a zero-touch, non-intrusive cloud-based solution that provides daily monitoring for web applications, checking for systems and application vulnerabilities, and malware. Indusface WAS with its automated scans & manual pentesting done by certified security experts ensures none of the OWASP Top10, business logic vulnerabilities, and malware go unnoticed. With zero false-positive guarantee and comprehensive reporting with remediation guidance, Indusface web app scanning ensures developers to quickly fix vulnerabilities seamlessly.

Average Rating: 4.6/5.0

Total Reviews: 64

How Do G2 Users Rate Indusface WAS?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.2/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.7/10 (Category avg: 8.8/10)

Who Is the Company Behind Indusface WAS?

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Small, 37% Medium

What Do G2 Reviewers Say About Indusface WAS?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive vulnerability detection by Indusface WAS, benefiting from detailed insights and helpful remediation guidelines.
  • Users appreciate the comprehensive vulnerability identification offered by Indusface WAS, ensuring detailed insights and effective remediation.
  • Users commend the responsive customer support from Indusface, ensuring timely assistance during VAPT testing and queries.
  • Users value the scanning efficiency of Indusface WAS, benefiting from automated deep-dive security scans and detailed reports.
  • Users value the deep-dive security scans of Indusface WAS, which enhance security accreditation and vulnerability management.
Cons
  • Users note that Indusface WAS is expensive, particularly for development environment scans and SSL certificates.
  • Users find the interface confusing and suggest it needs to be more intuitive and up-to-date.
  • Users find the limited functionality in the free testing version restricts their ability to effectively scan development environments.
  • Users feel that limited pricing options for staging scans hinder effective testing before deployment in development environments.
  • Users find the interface design outdated and unintuitive, though improvements are reportedly in progress.

What Are Recent G2 Reviews of Indusface WAS?

What Are G2 Users Discussing About Indusface WAS?

Sprocket Security

Sprocket Security — Technology-Powered. Human-Verified. Sprocket Security is a technology-powered continuous penetration testing platform that eliminates the blind spots left by annual testing. Traditional pentests give you a point-in-time snapshot and then leave you exposed for the other 345 days of the year — while your infrastructure keeps changing. Sprocket closes that gap by combining automation with US-based human pentesters who validate what actually matters, so your security posture is tested continuously, not once a quarter or once a year. Sprocket runs on the Continuous Lifecycle: Attack Surface Monitoring surfaces what you have exposed, Bleeding-Edge Testing puts expert pentesters against it using the latest attacker techniques, IT Change Detection automatically triggers new testing whenever your environment changes, and Notifications & Support push findings straight into the workflows your team already uses. When something changes, testing happens — no waiting for the next scheduled engagement. What makes Sprocket different -Continuous, not calendar-based. Testing is triggered by change, not by the calendar. No 345-day gaps between engagements. -Human-verified findings, not scanner noise. Automation does the heavy lifting; expert US-based pentesters validate real, exploitable risk so your team gets signal instead of a 200-page PDF to triage. -Continuous, not coin-operated. Unlimited retests are included. When you patch a finding, verify the fix at no additional cost — no per-retest fees, no surprise invoices for scope changes. -From finding to fixed, faster. Findings flow into your existing tools in real time, so remediation starts immediately instead of waiting on a report. -Compliance-ready, always. Generate on-demand reporting for SOC 2, ISO 27001, HIPAA, PCI-DSS, and more — built from live data, not a stale snapshot. Who it's for Sprocket is built for security and IT teams at growing organizations that need offensive security coverage without standing up a full internal red team. CISOs, Directors of Security, IT leaders, and compliance and risk owners rely on Sprocket to continuously validate their defenses, prove control effectiveness to auditors and the board, and stay ahead of an attack surface that never stops changing — with particularly strong fit for financial services, healthcare, SaaS, and other compliance-driven industries. Doing what Gartner now calls Continuous Offensive Security Testing since 2018, Sprocket gives you the coverage of a dedicated adversary and the visibility of an always-on platform — so you find your weaknesses before an attacker does.

Average Rating: 4.8/5.0

Total Reviews: 17

How Do G2 Users Rate Sprocket Security?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.3/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Sprocket Security?

Who Uses This Product?

  • Company Size: 71% Medium, 12% Large

What Do G2 Reviewers Say About Sprocket Security?

AI-generated summary from verified user reviews

Pros
  • Users commend the thoroughness and effectiveness of pentesting by Sprocket Security, enhancing overall product security significantly.
  • Users commend the helpful customer support of Sprocket Security, facilitating quick resolutions and effective communication.
  • Users value the ease of use of Sprocket Security, appreciating the intuitive interface and straightforward setup process.
  • Users highlight the extensive expertise of Sprocket Security, praising their top-tier penetration testing and exceptional support.
  • Users value the remediation efficiency of Sprocket Security, appreciating actionable guidance and ongoing support for improved security.
Cons
  • Users experience false positives from alerting tools, complicating the integration of Sprocket Security into their systems.
  • Users find Sprocket Security expensive, citing significant price increases and a frustrating contract renewal process.
  • Users criticize the limited scope of Sprocket Security's support, resulting in slow remediation and contract issues.
  • Users express frustration with poor customer support, experiencing slow response times and unaddressed issues following pentests.
  • Users find the poor integration of Sprocket Security challenging, causing alerts and notifications that complicate usage.

What Are Recent G2 Reviews of Sprocket Security?

Edgescan

What Is Edgescan? Edgescan is a cybersecurity company that helps organizations proactively identify, validate, and prioritize vulnerabilities across their applications, API’s and digital landscape. The company specializes in continuous vulnerability assessment, automated penetration testing, Attack Surface Management and Penetration Testing as a Service (PTaaS). Edgescan also delivers Autonomous Penetration Testing via "Edgescan Atomic". Atomic is an AI powered autonomous penetration testing capability available exclusively to Edgescan customers. Each Atomic Attack Credit provides an autonomous penetration test, allowing organizations to perform an additional autonomous penetration test when required Atomic complements PTaaS by providing another way to assess security as environments evolve. (Supercharge your security with AI) Edgescan combines advanced automation with certified security experts, including professionals holding credentials such as CREST and OSCP, to deliver highly accurate and actionable security testing. This hybrid approach allows organizations to move beyond traditional point-in-time penetration tests and operate a continuous proactive cybersecurity program. The Edgescan platform is designed primarily for web application and API security, enabling organizations to continuously assess their attack surface and identify vulnerabilities throughout the development lifecycle but also delivers “full stack” coverage to detect host layer CVE’s. With a client retention rate of over 90%, Edgescan has built long-term partnerships by delivering measurable improvements in security efficiency, risk visibility, and vulnerability management. Key Features and Capabilities of Edgescan Automated Penetration Testing Edgescan uses intelligent automation to continuously assess applications, APIs, hosts, and cloud environments for vulnerabilities. This enables frequent, scalable security testing across modern and distributed architectures. Human‑Validated Testing Findings are reviewed and manually validated by certified security experts to eliminate false positives and provide deeper insight into real‑world exploitability. Each result is accurate, contextual, and actionable. Penetration Testing as a Service (PTaaS) Edgescan’s PTaaS model extends beyond automated testing by allowing expert testers to focus on vulnerabilities that require human analysis, including: • Business logic flaws • Authentication and authorization weaknesses • Context-dependent exposures • Complex attack chains and privilege escalation paths Cyber Analytics and AI‑Assisted Validation AI-driven analysis enhances detection, verifies exploitability, and increases accuracy. This reduces noise and gives security teams a clearer picture of genuine threats. Integrated Threat Intelligence Edgescan correlates vulnerabilities with real-world threat intelligence, including known exploits and ransomware activity to help organizations prioritize the most dangerous exposures first. Risk‑Based Prioritization Findings are prioritized based on exploitability, severity, threat context, and business impact, ensuring teams focus on the issues that matter most. Primary Value: What Edgescan Solves for Clients Edgescan enables organizations to shift from reactive vulnerability management to a continuous, proactive security model. Traditional scanners and periodic penetration tests frequently produce large volumes of unvalidated findings. This creates noise and forces security teams to spend hours determining which issues are real and critical. Edgescan solves this by combining: Automation for continuous testing Human expertise for validation and complex analysis Cyber analytics and AI for accuracy and prioritization Key Benefits Significant efficiency gains: reducing thousands of hours spent on manual validation. Higher accuracy, thanks to expert‑validated findings and reduced false positives. Clear prioritization, using threat intelligence and ransomware insights to highlight the highest‑risk exposures. Continuous security improvement, enabling rapid detection, faster remediation, and scalable vulnerability management. By unifying automation, human expertise, AI, and threat intelligence, Edgescan empowers organizations to maintain a continuous cybersecurity program that strengthens overall security posture while dramatically reducing operational burden.

Average Rating: 4.6/5.0

Total Reviews: 58

How Do G2 Users Rate Edgescan?

  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.5/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.5/10 (Category avg: 9.2/10)
  • Extensibility: 9.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Edgescan?

  • Seller: Edgescan
  • Company Website:
  • Year Founded: 2017
  • HQ Location: Dublin, Dublin
  • LinkedIn® Page: www.linkedin.com
    88 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 38% Large, 28% Medium

What Do G2 Reviewers Say About Edgescan?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Edgescan, enjoying its user-friendly interface and convenient access to essential information.
  • Users value the near false positive free vulnerability scanning of Edgescan, making web application testing efficient and reliable.
  • Users highly value the fantastic customer support from Edgescan, enhancing their overall experience significantly.
  • Users value the validated, near false positive free vulnerability scanning of Edgescan, enhancing their testing experience significantly.
  • Users appreciate the user-friendly console of Edgescan, as it offers easy access and comprehensive functionality for managing vulnerabilities.
Cons
  • Users find the complex UI of Edgescan challenging, leading to inefficiencies and difficulties in task navigation.
  • Users find the limited customization for hosts and filtering frustrating, impacting their ability to adapt to changes.
  • Users find the poor interface design of Edgescan frustrating, hindering efficient navigation and task completion.
  • Users experience slow performance with Edgescan, as scans can take longer due to thorough validation processes.
  • Users find the user interface challenging to navigate, leading to delays and difficulty performing common tasks.

What Are Recent G2 Reviews of Edgescan?

What Are G2 Users Discussing About Edgescan?
Intigriti

Intigriti is the trusted leader in crowdsourced security, empowering the world’s largest organizations to find and fix vulnerabilities before cybercriminals can exploit them. Since 2016, the company has helped its customers reduce risk with the expertise of 125,000+ global security researchers, enabling real-time vulnerability detection and preventing costly breaches. Intigriti's flexible platform offers a full suite of solutions, including Bug Bounty, PTaaS, Focused Sprints, and Live Hacking Events, tailored to your evolving digital needs and delivered through a pay-for-impact model, meaning you only pay for valid vulnerabilities submitted. Our solutions span: - Bug Bounty - Vulnerability Disclosure Programs (VDP) - Focused Sprints - PTaaS - Live Hacking Events - Reward Services With industry-leading triage, commitment to legal compliance, and exceptional customer service, Intigriti is the go-to choice for organizations like Coca-Cola, Microsoft, and Intel to secure their digital assets and stay ahead in a changing world.

Average Rating: 4.7/5.0

Total Reviews: 32

How Do G2 Users Rate Intigriti?

  • Has the product been a good partner in doing business?: 9.5/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 6.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Intigriti?

  • Seller: Intigriti
  • Year Founded: 2016
  • HQ Location: Antwerpen, BE
  • LinkedIn® Page: www.linkedin.com
    829 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Human Resources
  • Company Size: 59% Medium, 34% Large

What Are Recent G2 Reviews of Intigriti?

SQLmap

Automatic SQL injection and database takeover tool

Average Rating: 4.3/5.0

Total Reviews: 37

How Do G2 Users Rate SQLmap?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.4/10 (Category avg: 9.2/10)
  • Extensibility: 7.8/10 (Category avg: 8.8/10)

Who Is the Company Behind SQLmap?

  • Seller: SQLmap
  • Year Founded: 2008
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Computer & Network Security
  • Company Size: 53% Small, 42% Medium

What Are Recent G2 Reviews of SQLmap?

What Are G2 Users Discussing About SQLmap?

Strobes Security

Strobes is an AI-driven exposure management platform designed to help organizations streamline their security operations by unifying various security methodologies, including Attack Surface Management (ASM), Application Security Posture Management (ASPM), Risk-Based Vulnerability Management (RBVM), and Penetration Testing as a Service (PTaaS). This comprehensive solution provides users with a holistic view of their security posture, enabling them to identify, assess, and respond to potential risks and vulnerabilities effectively. Targeted primarily at security teams and IT professionals, Strobes caters to organizations of all sizes that require a robust approach to managing their security exposure. The platform is particularly beneficial for those who need to navigate the complexities of modern security environments, where multiple tools and processes can lead to fragmented insights. By consolidating various security functions into a single workflow, Strobes empowers users to make informed decisions based on a complete understanding of their risk landscape. One of the key features of Strobes is its extensive integration capabilities, boasting over 120 integrations with existing security tools and systems. This allows organizations to pull findings from disparate sources into a single view, enriching data with contextual information that enhances the relevance of insights. The platform's advanced correlation capabilities help identify relationships between different vulnerabilities and risks, enabling security teams to prioritize their remediation efforts effectively. The user-friendly dashboards in Strobes serve as a central hub for monitoring security activities, encompassing everything from asset discovery and vulnerability insights to Service Level Agreement (SLA) tracking and ticketing. This comprehensive visibility supports continuous prioritization and fix validation, allowing teams to address the most critical issues first. By automating triage processes, Strobes ensures that real risks and exposures are highlighted, facilitating a more efficient response to potential threats. Overall, Strobes stands out in the exposure management landscape by providing a cohesive and intelligent approach to security management. Its ability to unify various methodologies, coupled with powerful automation and integration features, positions it as a valuable tool for organizations seeking to enhance their security posture and effectively manage their exposure to risks.

Average Rating: 4.5/5.0

Total Reviews: 44

How Do G2 Users Rate Strobes Security?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.3/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Strobes Security?

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 42% Medium, 33% Large

What Do G2 Reviewers Say About Strobes Security?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid vulnerability assessments that enhance security fixes significantly, boosting efficiency and prioritization.
  • Users appreciate the rapid vulnerability assessments and prioritized remediation that enhance their security processes significantly.
  • Users value the thorough security measures of Strobes Security, impressed by its attention to detail in vulnerability management.
  • Users value the responsive customer support of Strobes Security, enhancing the experience with timely and effective assistance.
  • Users find Strobes Security exceptionally easy to use, enjoying quick setup and intuitive dashboards for efficient workflows.
Cons
  • Users express dissatisfaction with the inadequate reporting in Strobes Security, citing lack of transparency and customization options.
  • Users find the limited customization options in Strobes Security hinder initial workflow setup and usability improvements.
  • Users find Strobes Security's poor usability challenging initially, with a steep learning curve and complex dashboard navigation.
  • Users find the reporting issues in Strobes Security limit transparency and hinder customization for effective analysis.
  • Users find the user interface complex, making initial customization and workflow setup a challenging experience.

What Are Recent G2 Reviews of Strobes Security?

Evolve Security

Evolve Security's patent pending Darwin Attack® platform is a comprehensive collaboration and management tool designed to help organizations manage their cybersecurity services and reduce risks of successful cyberattacks. The platform serves as a repository for research, vulnerability and attack details, compliance requirements, remediation recommendations, and mitigating controls. It also functions as a security feed, collaboration tool, tracking tool, management platform, and reporting platform. The platform enables organizations to actively manage their security program by providing real-time updates on testing progress and findings, which allows for timely remediation. Darwin Attack® is constantly updated with new information and functionality to ensure that it remains effective and efficient in meeting the needs of Evolve Security's clients.

Average Rating: 4.8/5.0

Total Reviews: 53

How Do G2 Users Rate Evolve Security?

  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.4/10 (Category avg: 9.2/10)
  • Extensibility: 8.8/10 (Category avg: 8.8/10)

Who Is the Company Behind Evolve Security?

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 70% Medium, 21% Small

What Do G2 Reviewers Say About Evolve Security?

AI-generated summary from verified user reviews

Pros
  • Users value the actionable intelligence provided by Evolve Security, enhancing their cybersecurity with clear guidance and insights.
  • Users commend the effective communication from Evolve Security, enhancing collaboration and clarity during the pentesting process.
  • Users find the ease of use of Evolve Security's interface enhances their configuration and testing experience.
  • Users value the vulnerability detection expertise of Evolve Security, enhancing their understanding and response to security issues.
  • Users value the effective vulnerability identification by Evolve Security, enhancing their cybersecurity with clear corrective instructions.

What Are Recent G2 Reviews of Evolve Security?

Invicti Web + API (formerly Acunetix)

Invicti Web + API (formerly Acunetix) is a dynamic application security testing (DAST) solution that helps security and development teams find and validate exploitable vulnerabilities across web applications and APIs. Built on the same Acunetix technology and expertise customers already know, Invicti Web + API combines fast, accurate scanning with proof-based validation, modern application coverage, and intelligent automation. With Invicti Web + API, teams can: - Discover and test vulnerabilities across websites, web applications, APIs, single-page applications, and modern JavaScript frameworks - Validate exploitable vulnerabilities with proof-based scanning to reduce false positives and manual verification - Test REST, SOAP, and GraphQL APIs, including complex and stateful application workflows - Integrate security testing into CI/CD, issue tracking, and development workflows so validated findings reach the teams responsible for remediation - Automate recurring application security testing across development and production environments Invicti Web + API serves as the foundation of Invicti’s solution portfolio, extending proven web and API security into the broader Invicti AppSec platform and its agentic pentesting capabilities.

Average Rating: 4.1/5.0

Total Reviews: 100

How Do G2 Users Rate Invicti Web + API (formerly Acunetix)?

  • Has the product been a good partner in doing business?: 8.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 8.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.6/10 (Category avg: 9.2/10)
  • Extensibility: 7.4/10 (Category avg: 8.8/10)

Who Is the Company Behind Invicti Web + API (formerly Acunetix)?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 40% Large, 34% Medium

What Do G2 Reviewers Say About Invicti Web + API (formerly Acunetix)?

AI-generated summary from verified user reviews

Pros
  • Users value the rapid and precise vulnerability detection in Invicti Web + API, enhancing security for their applications.
  • Users commend the ease of use of Invicti Web + API, appreciating its intuitive interface and seamless integration.
  • Users appreciate the robust security features of Invicti Web + API, ensuring thorough protection for web applications.
  • Users appreciate the effective vulnerability identification capabilities of Invicti, enhancing web application security significantly.
  • Users value the accuracy of results from Invicti Web + API, ensuring reliable vulnerability assessments for web applications.
Cons
  • Users find the pricing of Invicti Web + API to be expensive, limiting accessibility for smaller teams and projects.
  • Users find the complexity in setup and configurations of Invicti Web + API challenging, especially for new users.
  • Users find the complex setup of Invicti Web + API challenging, especially for first-time configurations and integrations.
  • Users experience slow scanning that can hinder normal workflows and complicate the use of the tool.
  • Users find that difficult customization can hinder the integration of Invicti Web + API, requiring extensive technical knowledge.

What Are Recent G2 Reviews of Invicti Web + API (formerly Acunetix)?

What Are G2 Users Discussing About Invicti Web + API (formerly Acunetix)?

Invicti

Invicti (formerly known as Netsparker) is an enterprise application and API security testing platform that helps organizations secure thousands of web applications and APIs at scale while dramatically reducing the risk of attack. Combining advanced DAST and IAST capabilities in a single platform, Invicti enables security teams to continuously identify, prioritize, and remediate vulnerabilities across complex modern environments with confidence and automation. With Invicti, security teams can: - Automate application security testing workflows and save hundreds of hours every month - Discover and secure all web applications and APIs, including forgotten, unmanaged, and shadow assets - Deliver actionable, developer-friendly feedback that helps teams remediate vulnerabilities faster and build more secure code over time - Reduce false positives with proof-based scanning technology that validates exploitable vulnerabilities - Scale application security programs across large enterprises without slowing development teams - Integrate security seamlessly into existing DevSecOps and CI/CD workflows Built for organizations with the most demanding security requirements, Invicti empowers teams to confidently secure their entire attack surface with accuracy, scalability, and automation.

Average Rating: 4.5/5.0

Total Reviews: 69

How Do G2 Users Rate Invicti?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.1/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.7/10 (Category avg: 9.2/10)
  • Extensibility: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Invicti?

  • Seller: Invicti Security
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Austin, Texas
  • LinkedIn® Page: www.linkedin.com
    326 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 46% Large, 29% Medium

What Do G2 Reviewers Say About Invicti?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Invicti, highlighting its quick setup and straightforward report generation.
  • Users value the effective scanning technology of Invicti, enabling accurate identification of vulnerabilities and streamlined workflows.
  • Users value the accuracy and integration capabilities of Invicti, enhancing efficiency and simplifying reporting processes.
  • Users appreciate the well-formatted and easy-to-read reports from Invicti, simplifying certification processes significantly.
  • Users value the super accurate vulnerability detection of Invicti, enhancing their security workflows efficiently.
Cons
  • Users find the customer support inadequate, struggling with timely responses and effective solutions to issues.
  • Users experience slow performance during scans and setup, which affects their overall satisfaction with Invicti.
  • Users experience slow scanning issues with Invicti, affecting efficiency despite good support and solid performance once set up.
  • Users face API scanning issues with Invicti, limiting its effectiveness for their specific needs despite good support.
  • Users find the complex setup to be overwhelming initially, impacting the ease of using Invicti effectively.

What Are Recent G2 Reviews of Invicti?

What Are G2 Users Discussing About Invicti?

AI-Native Continuous Offensive Security Platform

RidgeBot by Ridge Security is an AI-powered platform for continuous security validation that enables CISOs to minimize cyber risks from increasingly sophisticated and frequent cyberattacks by validating the cybersecurity posture and controls that protect attack surfaces. RidgeBot delivers continuous threat exposure management by automatically testing an organization’s entire Internet Protocol (IP)-based attack surfaces, including network infrastructure, applications, websites, IoT, and OT. RidgeBot pinpoints the most critical vulnerabilities using ethical hacking techniques. RidgeBot’s dynamic AI-powered decision-making capability supports many use cases, including DevSecOps, compliance, incident response verification, and custom attack simulations. RidgeBot maintains a library of over 36,000 plugins to launch complex penetration tests and attack simulations, with detailed reporting of results and remediation recommendation.

Average Rating: 4.5/5.0

Total Reviews: 98

How Do G2 Users Rate AI-Native Continuous Offensive Security Platform?

  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.4/10)
  • Performance and Reliability: 9.2/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 9.0/10 (Category avg: 9.2/10)
  • Extensibility: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind AI-Native Continuous Offensive Security Platform?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Small, 45% Medium

What Do G2 Reviewers Say About AI-Native Continuous Offensive Security Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the automation features of RidgeBot, which efficiently streamline security validation and prioritization of threats.
  • Users find the ease of use exceptional, praising its intuitive interface and straightforward setup for security tasks.
  • Users appreciate the efficiency of automated pentesting with RidgeBot, significantly reducing manual validation and saving time.
  • Users value the autonomous vulnerability testing of RidgeBot, significantly enhancing efficiency and risk assessment in security processes.
  • Users appreciate the efficiency of RidgeBot in automating penetration testing and prioritizing critical vulnerabilities effectively.
Cons
  • Users find the platform's setup to be complex and challenging, especially in customized or legacy environments.
  • Users find the complex setup of the AI-Native platform challenging, particularly for newcomers and unique environments.
  • Users feel there are several missing features, like improved API testing and custom reporting templates for compliance.
  • Users find the customer support lacking, often leaving them to troubleshoot issues independently.
  • Users find the poor documentation challenging, making initial setup and troubleshooting difficult, especially for new admins.

What Are Recent G2 Reviews of AI-Native Continuous Offensive Security Platform?

Titania Nipper InfraSight

Award-winning Risk-Based Vulnerability Management. Nipper InfraSight analyzes network device configurations in the way Advances Persistent Threat (APT) groups do, to identify misconfigurations that could create attack paths. This analysis offers unparalleled, pen-tester accuracy, finding critical vulnerabilities in firewalls, routers, switches that other tools simply cannot see. Our solutions then prioritize the biggest risks to your business and provide device-specific remediation guidance, right down to specific command line prompts.  By analyzing device configurations against key compliance standards and security frameworks (including STIGs/CIS Benchmarks/PCI DSS/CMMC/CORA/NIST SP 800-53), Nipper solutions tell you precisely which devices are at risk of failing, how significant that risk is, and how you can solve it, with auditor-ready reports. Whether your focus is taking pragmatic, risk-based security measures to minimize known vulnerabilities or ensuring compliance with industry security standards, Nipper solutions provide the targeted insights you need. No other security provider looks at the network in the same way. That’s why Nipper can uniquely provide the network configuration coverage that organizations urgently require. 30+ U.S. federal agencies and 800+ organizations globally trust Nipper solutions to deliver vulnerability analysis and compliance automation while supporting air-gapped environments, sovereign cloud requirements, and complex regulated infrastructures.

Average Rating: 4.3/5.0

Total Reviews: 33

How Do G2 Users Rate Titania Nipper InfraSight?

  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.4/10)
  • Performance and Reliability: 10.0/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 10.0/10 (Category avg: 9.2/10)
  • Extensibility: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Titania Nipper InfraSight?

  • Seller: Titania
  • Company Website:
  • Year Founded: 2009
  • HQ Location: London, GB
  • LinkedIn® Page: www.linkedin.com
    104 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 39% Large, 24% Medium

What Do G2 Reviewers Say About Titania Nipper InfraSight?

AI-generated summary from verified user reviews

Pros
  • Users find the ease of use of Titania Nipper InfraSight exceptional, enabling straightforward assessments with clear documentation.
  • Users value the clear and actionable reporting of Titania Nipper InfraSight, enhancing their assessment accuracy and usability.
  • Users value the scanning efficiency of Titania Nipper InfraSight, enabling quick identification of vital system risks.
  • Users commend Titania Nipper for its effective vulnerability detection, providing actionable recommendations and enhancing network security.
  • Users value the clear and user-friendly interface of Titania Nipper InfraSight, making assessment straightforward and efficient.
Cons
  • Users find the licensing issues challenging, specifically with device limits and the model based on quantity.
  • Users often experience false positives, leading to confusion with inaccurate findings and device vulnerability reports.
  • Users find the lack of cloud support frustrating, especially with inaccuracies in scanning recommendations for specific devices.
  • Users face limited compatibility with devices, leading to the inconvenience of maintaining multiple software versions.
  • Users face a limited scope of device support, requiring maintenance of older versions and encountering auditing challenges.

What Are Recent G2 Reviews of Titania Nipper InfraSight?

What Are G2 Users Discussing About Titania Nipper InfraSight?

Cyver Core

Cyver Core is a pentest collaboration and management platform to digitize, automate, and optimize manual work for pentest firms, while enabling Pentest-as-a-Service delivery. Cyver Core offers pentest report automation, branded client portals, pentest management, team management, and more.

Average Rating: 4.7/5.0

Total Reviews: 20

How Do G2 Users Rate Cyver Core?

  • Has the product been a good partner in doing business?: 9.7/10 (Category avg: 9.4/10)
  • Performance and Reliability: 7.9/10 (Category avg: 9.2/10)
  • Vulnerability Scan: 8.3/10 (Category avg: 9.2/10)
  • Extensibility: 8.6/10 (Category avg: 8.8/10)

Who Is the Company Behind Cyver Core?

  • Seller: Cyver
  • Year Founded: 2020
  • HQ Location: Amsterdam, NL
  • LinkedIn® Page: www.linkedin.com
    10 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 75% Small, 20% Medium

What Do G2 Reviewers Say About Cyver Core?

AI-generated summary from verified user reviews

Pros
  • Users are impressed with the high efficiency and automation in managing pentesting workflows through Cyver Core.
  • Users value the streamlined reporting quality of Cyver Core, enhancing efficiency and client communication throughout the process.
  • Users appreciate the seamless communication of Cyver Core, enhancing collaboration and streamlining the workflow efficiently.
  • Users value the fast and helpful customer support of Cyver Core, enhancing their overall experience and engagement.
  • Users appreciate the robust cybersecurity features of Cyver Core, enhancing pentesting efficiency and customer experience.
Cons
  • Users find the limited customization of Cyver Core restricting, particularly with fixed roles and predefined options.
  • Users have reported technical issues such as stability problems and occasional slowness that affect usability.
  • Users experience poor documentation, leading to non-intuitive UI/UX and occasional bugs despite quick fixes.
  • Users find poor interface design in Cyver Core, with some UI/UX areas being non-intuitive and causing confusion.
  • Users report experiencing slow performance at times, which can hinder their overall experience with Cyver Core.

What Are Recent G2 Reviews of Cyver Core?

What Are G2 Users Discussing About Cyver Core?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated March 5, 2025