Best Extended Detection and Response (XDR) Platforms - Page 5

How Many Extended Detection and Response (XDR) Platforms Products Does G2 Track?

Total Products under this Category: 103

Category Stats (Sep 2026)

  • Average Rating: 4.55/5 (↑0.01 vs Aug 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Singularity AI SIEM (+3.53%) - Among all products in this category, Singularity AI SIEM recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Extended Detection and Response (XDR) Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,500+ Authentic Reviews
  • 103+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

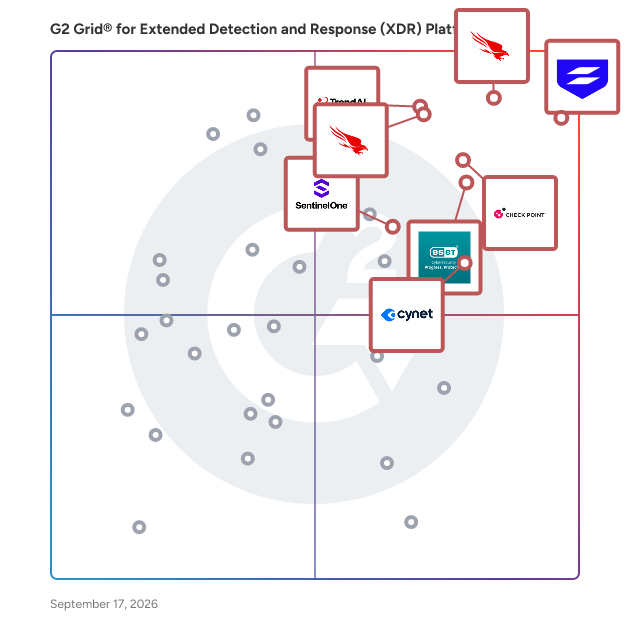
G2 Grid® for Extended Detection and Response (XDR) Platforms

G2 Grid® for Extended Detection and Response (XDR) Platforms plotting products by satisfaction and market presence

Highlighted products: Sophos Endpoint, CrowdStrike Falcon Endpoint Protection Platform, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Cynet, and SentinelOne Singularity Endpoint.

Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=cynet&focus%5B%5D=sentinelone-singularity-endpoint)

Anomali Security Analytics

Anomali is the ultra-modern SIEM, fusing the key capabilities of ETL, SIEM, Next-Gen SIEM, XDR, UEBA, SOAR, and TIP into a single, high-speed data lake — with 7+ years of always-hot storage for instant access to historical data. A system of action, Anomali weaves AI throughout every workflow, driving smarter ingestion, enrichment, detection, investigation, and response at massive scale. By connecting native threat intelligence with security data, Anomali delivers total visibility, real-time contextual insight, and the clarity to act fast.

Who Is the Company Behind Anomali Security Analytics?

  • Seller: ANOMALI
  • Year Founded: 2013
  • HQ Location: Redwood City, California, United States
  • Twitter: @Anomali
    8,773 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    314 employees on LinkedIn®
  • Phone: (844) 484-7328

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Anomali Security Analytics?

What Are G2 Users Discussing About Anomali Security Analytics?

Argus By Genix

Argus by Genix Cyber is a powerful Extended Detection and Response (XDR) platform designed to simplify cybersecurity across cloud, hybrid, and on-premise environments. It integrates advanced threat detection, identity access governance, and continuous compliance into one centralized system. With real-time insights, AI-enhanced analytics, and automated incident response, Argus helps reduce security risks while ensuring regulatory alignment. Ideal for enterprises and MSPs, it delivers flexible protection that scales with your infrastructure.

Who Is the Company Behind Argus By Genix?

ARIA ADR

Find and stop 99% of threats with 100x less manual effort for maximum ROI with ARIA ADR ARIA Advanced Detection and Response (ADR) is a purpose-built solution combining the functionality of six threat detection and response tools — consisting of SIEMs, UEBAs, SOARs, and other tools — into a single platform. No longer will organizations have to settle for limited threat surface coverage or struggle to integrate and maintain disparate tools at substantial cost and little return. ARIA ADR’s machine learning-powered threat models, guided by AI, can find and stop threats in just minutes—no humans required. This is a powerful advantage over most traditional approaches that surface more noise than threats and require highly-trained security operations staff.

Who Is the Company Behind ARIA ADR?

BitLyft AIR Platform

We believe you deserve to have your technology from cyber threats. We help keep organization safe by illuminating and eliminating cyber threats before they have time to harm you or your customers.

Who Is the Company Behind BitLyft AIR Platform?

BlackSOC Labs

Managed SOC – everything in one dashboard The intensity and frequency of cyberattacks is steadily increasing. Digitally networked SMEs in particular are increasingly being targeted by attackers. However, measures such as firewalls or virus scanners alone are not enough to effectively ward off hackers. With BLACKSOC, we take your existing security systems and create a customized solution with 24/7-monitoring – simple and clear.

Who Is the Company Behind BlackSOC Labs?

Command|Link

ONE platform to manage your SD-WAN, UCaaS, CaaS, firewalls, MPLS, network, switches, IP phones, installs, trouble tickets, bills, and network performance across the entire globe Complete control of your technology stack without interference or dependency on vendors Increase agent efficiency and speed up issue resolution using CommandLink's proprietary ITSM Streamline IT support with automated software-enabled support workflows Shape service experiences for employees anywhere with full transparency at the most granular level Make real-time moves, adds, changes without picking up the phone Analyze and control bandwidth traffic by application, port, IP, and or protocol. Enable real-time, dynamic, and pre-scheduled bandwidth modifications as often as you like. Direct communication with your tier 3 engineering POD, enabling you to scale your IT infrastructure without headcount and especially without headaches Deliver high-quality services proactively and at scale with real-time analytics and reports If you need access to third party apps like ServiceNow, the CommandLink API enables streaming push and pull functions with any API enabled app.

Average Rating: 4.8/5.0

Total Reviews: 22

How Do G2 Users Rate Command|Link?

  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)

Who Is the Company Behind Command|Link?

  • Seller: CommandLink
  • Year Founded: 2012
  • HQ Location: Bothell, Washington, United States
  • LinkedIn® Page: www.linkedin.com
    314 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 59% Medium, 32% Large

What Do G2 Reviewers Say About Command|Link?

AI-generated summary from verified user reviews

Pros
  • Users value the exceptional responsiveness of Command|Link's customer support, enhancing their experience with personalized and proactive assistance.
  • Users value the quick response time of Command|Link, appreciating their proactive and engaged support during network issues.
  • Users commend Command|Link for their exceptional reliability, quick responses, and proactive support in managing ISP accounts.
  • Users value the robust support from Command|Link, enjoying quick responses and a dedicated, engaged account team.
  • Users value the ease of use of Command|Link, highlighting its helpful support and efficient service management.
Cons
  • Users find the limited features of Command|Link hinder effective network management and troubleshooting options.
  • Users face communication issues with Command|Link, as direct carrier contact for support is not available.
  • Users find the insufficient information during issues frustrating, especially the lack of detailed ISP notes and direct contact options.
  • Users find the lack of detailed configuration options in Command|Link limits effective network management and control.
  • Users find the poor support services of Command|Link frustrating, especially lacking direct carrier contact for issues.

What Are Recent G2 Reviews of Command|Link?

CybrHawk XDR

CybrHawk is a leading provider of information security-driven risk intelligence solutions focused solely on providing clients from cyber-attacks. Our solutions enable organizations to define their cyber defences to prevent security breaches, detect real-time malicious activity, prioritize and respond quickly to security breaches, and predict emerging threats.We also pioneered an integrated approach that provides a wide range of cyber security solutions for organizations of varying size and complexity.

Who Is the Company Behind CybrHawk XDR?

  • Seller: CybrHawk
  • Year Founded: 2016
  • HQ Location: Fort Lauderdale Fort , US
  • LinkedIn® Page: www.linkedin.com
    18 employees on LinkedIn®

Cynco

Who Is the Company Behind Cynco?

  • Seller: Cynco
  • Year Founded: 2024
  • HQ Location: Kuala Lumpur, MY
  • LinkedIn® Page: www.linkedin.com
    3 employees on LinkedIn®

Defense.com

Defense.com is an XDR platform that contains everything your organisation needs to detect and respond to cyber threats across all areas of your network, without the enterprise price tag or complexity. Without a solution like Defense.com, you can spend a lot of time and resources manually correlating data from multiple, disparate security tools in order to identify and remediate cyber threats. Defense.com ingests and correlates native and third-party security data from all areas of your environment into a single detection and response platform, helping you to quickly identify threats and prevent breaches. In addition to threat detection and response, the Defense.com platform also helps your organisation strengthen its security posture with built-in vulnerability scanning, endpoint protection, external attack surface monitoring and security awareness training. Managed services Small and medium sized organisations often lack the time or resources to properly monitor their environment, forcing them to settle for just business hours coverage. Defense.com solves this challenge with a 24/7 Managed SIEM service, backed by our in-house SOC analysts and our advanced log monitoring technology. We can take the pressure off your team by monitoring your organisation's environment on your behalf, alerting you to genuine threats and providing detailed remediation advice to help fix issues fast. Why choose Defense.com? Unlike many other providers on the market that operate as MSSPs with third party technology, Defense.com has developed a proprietary SIEM platform that delivers advanced threat detection capabilities and can ingest logs from any system or vendor. This enables organisations to make the most out of their existing security investments, break free from vendor lock-in, and monitor everything in their environment for security threats. We also operate our own in-house SOC team, who provide 24/7 proactive threat detection and log monitoring. Our managed services alleviate the pressure on IT teams by proactively looking for malicious activity in their networks and raising security alerts to their attention, saving them time and ensuring that they only focus on genuine risks. Existing vendors on the market provide complex and expensive solutions that are usually tailored to enterprise organisations with in-house SecOps teams. Defense.com stands out as a more accessible alternative for SMEs in comparison to the current MDR and XDR category leaders.

Who Is the Company Behind Defense.com?

  • Seller: Defense.com
  • Year Founded: 2016
  • HQ Location: Stevenage, GB
  • Twitter: @defensedotcom
    178 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    40 employees on LinkedIn®

eScan Vision Core XDR

eScan Vision Core XDR delivers government-grade cybersecurity with Neural Intelligence AI/ML Defense through three deployment models: secure on-premises installations for classified environments, scalable cloud SaaS for rapid enterprise deployment, and SOC2-certified cloud solutions for government agencies requiring enhanced compliance. eScan Vision Core XDR is an advanced Extended Detection and Response (XDR) platform that provides real-time visibility, analysis, protection, and remediation across enterprise endpoints. The platform delivers comprehensive threat insights and automated alerts, enabling security teams to conduct faster investigations and implement rapid response measures that minimize attack impact.

Who Is the Company Behind eScan Vision Core XDR?

Google Threat Intelligence

Mandiant Advantage is a multi-vendor XDR platform that delivers Mandiant’s transformative expertise and frontline intelligence to security teams of all sizes.

Average Rating: 5.0/5.0

Total Reviews: 1

Who Is the Company Behind Google Threat Intelligence?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • Twitter: @google
    31,899,995 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Google Threat Intelligence?

What Are G2 Users Discussing About Google Threat Intelligence?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024