Top Free Endpoint Detection & Response (EDR) Software - Page 2

How Many Endpoint Detection & Response (EDR) Software Products Does G2 Track?

Total Products under this Category: 129

Category Stats (Sep 2026)

  • Average Rating: 4.43/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: CrowdStrike Falcon Endpoint Protection Platform (+0.82%) - Among all products in this category, CrowdStrike Falcon Endpoint Protection Platform recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Endpoint Detection & Response (EDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 12,900+ Authentic Reviews
  • 129+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

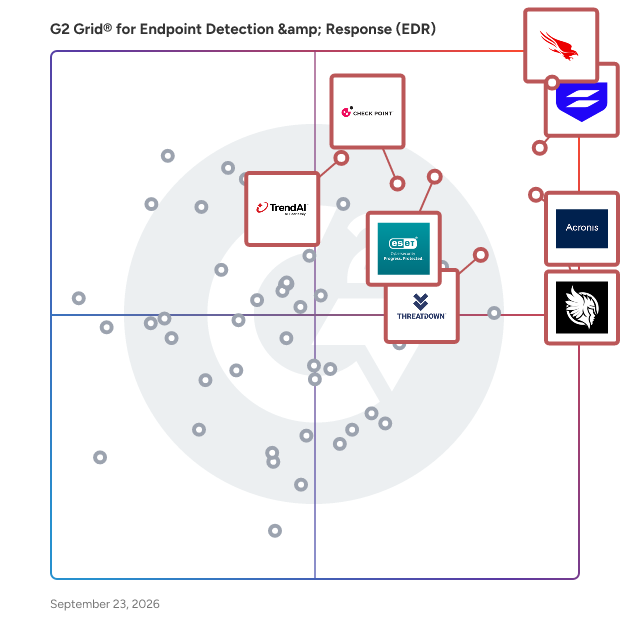
G2 Grid® for Endpoint Detection & Response (EDR) Software

G2 Grid® for Endpoint Detection & Response (EDR) Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, Acronis Cyber Protect Cloud, Huntress Managed EDR, ESET PROTECT, ThreatDown, Check Point Endpoint Security, and TrendAI Vision One.

Underlying data: [Grid® JSON](https://www.g2.com/categories/endpoint-detection-response-edr/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=acronis-cyber-protect-cloud&focus%5B%5D=huntress-managed-edr&focus%5B%5D=eset-protect&focus%5B%5D=threatdown&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=trendai-vision-one)

Bitdefender GravityZone XDR

Bitdefender Business Solutions Group is the business cybersecurity division of Bitdefender, delivering GravityZone — a unified platform that consolidates endpoint protection (EPP), endpoint detection and response (EDR), extended detection and response (XDR), and managed detection and response (MDR) into a single agent and console. Bitdefender GravityZone serves mid-market organizations with lean IT and security teams, protecting endpoints, identities, email, network, and cloud workloads. Effortless Security. Unmatched Protection For more information, visit https://www.bitdefender.com/en-us/business/.

Average Rating: 4.1/5.0

Total Reviews: 107

How Do G2 Users Rate Bitdefender GravityZone XDR?

  • Ease of Admin: 7.8/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.1/10 (Category avg: 9.0/10)
  • Quality of Support: 8.2/10 (Category avg: 8.7/10)
  • Ease of Use: 8.0/10 (Category avg: 8.7/10)

Who Is the Company Behind Bitdefender GravityZone XDR?

  • Seller: Bitdefender
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Bucuresti, Romania
  • Twitter: @Bitdefender
    114,121 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,344 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 56% Small, 35% Medium

What Do G2 Reviewers Say About Bitdefender GravityZone XDR?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of deployment and administration of Bitdefender GravityZone XDR, enhancing security management efficiency.
  • Users praise the responsive and helpful customer support of Bitdefender GravityZone XDR, enhancing their overall experience.
  • Users find Bitdefender GravityZone XDR to be extremely easy to use, facilitating seamless implementation and management.
  • Users value the efficiency of Bitdefender GravityZone XDR, enjoying streamlined deployment and seamless integration with existing systems.
  • Users value the robust security features of Bitdefender GravityZone XDR, effectively protecting against emerging threats and vulnerabilities.
Cons
  • Users find the setup and configuration complex, making it challenging for non-technical users to navigate.
  • Users face configuration issues that can complicate the setup process and lead to operational disruptions.
  • Users experience a difficult configuration process, particularly during the initial setup and policy adjustments.
  • Users find the user interface cumbersome, complicating navigation and management for those handling numerous devices.
  • Users express concerns about poor management control, requiring dedicated personnel and facing integration challenges and update issues.

What Are Recent G2 Reviews of Bitdefender GravityZone XDR?

What Are G2 Users Discussing About Bitdefender GravityZone XDR?

Heimdal

Accommodate all your cybersecurity needs under one convenient roof with the Heimdal® Unified Cybersecurity Platform. Our cybersecurity solutions can be used as standalone products or integrated into one another as part of a cohesive and unified XDR platform. Whether you’re a reseller, distributor, MSSP, or an organization committed to bolstering your online security, we provide an array of cutting-edge products to make your mission smoother. Heimdal® is a fast-growing cybersecurity company focused on continuous technological innovation. Since its establishment in 2014 in Copenhagen, based on the winning idea of CTF World Champions, Heimdal has experienced spectacular growth by proactively building products that anticipate threatscape trends. The company offers a multi-layeredand unified security suite that combines threat prevention, patch and asset management, endpoint rights management, antivirus and mail security which together secure customers against cyberattacks and keep critical information and intellectual property safe. Heimdal has been recognized as a thought leader in the industry and has won multiple international awards both for its solutions and for its educational content creation. The Heimdal line of products currently consists of 10 products and 2 services. The former category encompasses DNS Security for Endpoints & Network, Patch & Asset Management, Privileged Access Management, Application Control, Next-Gen Endpoint Antivirus, Ransomware Encryption Protection, Email Security, Email Fraud Prevention, and Remote Desktop. The latter is represented by Endpoint Detection & Response, as well as eXtended Detection & Response, or EDR and XDR for short. Currently, Heimdal’s cybersecurity solutions are deployed in more than 45 countries and supported regionally from offices in 15+ countries, by 175+ highly qualified specialists. Heimdal is ISAE 3000 certified and secures more than 2 million endpoints for over 10,000 companies. The company supports its partners without concessions on the basis of predictability and scalability. The common goal is to create a sustainable ecosystem and a strategic partnership.

Average Rating: 4.4/5.0

Total Reviews: 80

How Do G2 Users Rate Heimdal?

  • Ease of Admin: 8.2/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.0/10)
  • Quality of Support: 9.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.6/10 (Category avg: 8.7/10)

Who Is the Company Behind Heimdal?

  • Seller: Heimdal®
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Copenhagen, Denmark
  • Twitter: @HeimdalSecurity
    5,086 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    284 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Construction
  • Company Size: 56% Medium, 30% Small

What Do G2 Reviewers Say About Heimdal?

AI-generated summary from verified user reviews

Pros
  • Users praise the easy setup of Heimdal, appreciating its straightforward installation and quick integration with their systems.
  • Users find that file transfer with Heimdal is seamless and reliable, enhancing overall productivity and ease of use.
  • Users commend Heimdal for its exceptional issue resolution support, providing quick and professional solutions exceeding expectations.
  • Users value the reliable patch management of Heimdal, delivering consistent performance without issues during monthly updates.
  • Users value the reliable security and user-friendly interface of Heimdal, enhancing overall satisfaction and support.
Cons
  • Users find the complex interface of Heimdal difficult to navigate, complicating their overall experience and functionality.
  • Users find the admin portal complex and illogical, making navigation frustrating and cumbersome for essential tasks.
  • Users find the customer support lacking during initial setup, which causes issues with product deployment and upgrades.
  • Users find the poor interface design of Heimdal difficult to navigate, complicating essential tasks and access.
  • Users experience restart issues with Heimdal, feeling unprotected after scans until the software is rebooted.

What Are Recent G2 Reviews of Heimdal?

Saner CVEM

Prevention-first Vulnerability and Exposure Management for unified visibility, prioritization, compliance, and remediation Saner Continuous Vulnerability and Exposure Management unifies asset exposure, posture anomaly detection, vulnerability assessment, compliance management, risk prioritization, patching, and endpoint actions in one dashboard. Saner CVEM is built to help teams continuously detect, assess, prioritize, and remediate vulnerabilities and other security risks from a unified console Why Choose Saner CVEM? • Unified dashboard with interactive views across visibility, detection, prioritization, and remediation for a single source of truth • Complete asset visibility across endpoint and non-endpoint devices, operating system applications, third-party applications, and lifecycle changes • Continuous risk discovery with rapid scans, daily-updated risk intelligence, and posture anomaly detection that helps surface outliers and misconfigurations faster • Context-driven prioritization with SSVC categories such as Act, Attend, Track, and Track* so teams can focus on the risks that deserve action first. • Continuous compliance management with built-in templates, customizable profiles, daily checks, and deviation tracking across common frameworks. • Integrated patching and remediation with vulnerability-to-patch mapping, automated deployment workflows, and endpoint actions from the same ecosystem. • Machine-learning-assisted analysis to identify deeper risk patterns, detect unusual posture, and support smarter remediation decisions. • Customizable, audit-ready reporting for security, IT, and compliance teams that need clearer evidence and easier tracking. • Flexible deployment on cloud or on-premises, with remediation support across Windows, Linux, macOS, and AIX environments.

Average Rating: 4.5/5.0

Total Reviews: 72

How Do G2 Users Rate Saner CVEM?

  • Ease of Admin: 9.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.0/10)
  • Quality of Support: 9.2/10 (Category avg: 8.7/10)
  • Ease of Use: 8.6/10 (Category avg: 8.7/10)

Who Is the Company Behind Saner CVEM?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • Twitter: @secpod
    542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Small, 38% Medium

What Do G2 Reviewers Say About Saner CVEM?

AI-generated summary from verified user reviews

Pros
  • Users value the automatic security updates from Saner CVEM, ensuring timely compliance for remote workforce systems.
  • Users appreciate the advanced automation features of Saner CVEM, streamlining security patch management for remote systems.
  • Users value the seamless integrations of Saner CVEM, enhancing operational efficiency and strengthening digital security across IT processes.
  • Users value the automated compliance management of Saner CVEM, enhancing efficiency and reducing manual intervention significantly.
  • Users highlight the exceptional customer support from Saner CVEM, enhancing security and helping organizations stay protected.
Cons
  • Users often face integration issues with Saner CVEM, leading to frustrations during setup and ongoing maintenance.
  • Users note limited features in Saner CVEM, especially in multi-tenant support and integration capabilities, impacting efficiency.
  • Users experience slow performance when loading large data sets and during initial setup, affecting usability.
  • Users experience slow scanning, especially with initial dashboard load times and large data sets affecting daily checks.
  • Users find the limited cloud integration challenging, requiring workarounds and custom scripts for effective use.

What Are Recent G2 Reviews of Saner CVEM?

What Are G2 Users Discussing About Saner CVEM?

Datto Endpoint Detection and Response (EDR)

Datto EDR is a layered, integrated endpoint security solution that provides continuous monitoring and automated responses to threats that target Windows, Mac and Linux-based endpoints. Going beyond traditional antivirus, Datto EDR records and analyzes endpoint behaviors, proactively identifying and responding to activities that signal potential threats, including zero-day threats, multi-staged attacks, and advanced persistent threats (APTs). Datto EDR offers features tailored for Managed Service Providers (MSPs) and small to midsized enterprises, providing endpoint detection and response in an affordable, user-friendly package. Highlights include an advanced correlation engine to reduce alert fatigue, rapid threat response capabilities, fileless attack detection via behavioral analysis, ransomware detection, ransomware rollback, and integrations with Datto AV, Datto RMM, RocketCyber MDR, and the Kaseya IT Complete platform.

Average Rating: 4.3/5.0

Total Reviews: 31

How Do G2 Users Rate Datto Endpoint Detection and Response (EDR)?

  • Ease of Admin: 8.1/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.7/10 (Category avg: 9.0/10)
  • Quality of Support: 8.1/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 8.7/10)

Who Is the Company Behind Datto Endpoint Detection and Response (EDR)?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • Twitter: @KaseyaCorp
    17,411 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 84% Small, 16% Medium

What Do G2 Reviewers Say About Datto Endpoint Detection and Response (EDR)?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized management of Datto EDR, simplifying security while enhancing overall endpoint protection.
  • Users value the cost savings of Datto EDR, appreciating its all-in-one solution for effective endpoint security.
  • Users appreciate the strong protection offered by Datto EDR, noting its user-friendly design and effective threat management.
  • Users value the unified security approach of Datto EDR, providing comprehensive protection and enhanced peace of mind.
  • Users appreciate the app variety in Datto EDR, enhancing overall security management and effectiveness.
Cons
  • Users find integration issues with Datto EDR and AV, lacking functionality with other systems and limited tracking options.
  • Users report compatibility issues with certain applications like Dropbox, requiring additional exclusions for optimal performance.
  • Users often experience connectivity issues, occasionally losing connection to various endpoints during use.
  • Users find the learning curve steep, feeling overwhelmed by the platform's extensive features without adequate guidance.
  • Users express frustration over the limited customization in Datto EDR, impacting functionality and initial expectations significantly.

What Are Recent G2 Reviews of Datto Endpoint Detection and Response (EDR)?

Acronis Cyber Protect

Acronis Cyber Protect delivers robust protection against cyberthreats, unparalleled backup and recovery capabilities and simplified management and visibility through a single pane of glass, for the entire environment. Key features of Acronis Cyber Protect include: · Cyberthreat protection: Using artificial intelligence (AI) and machine learning (ML), proactively secures data, applications and systems, from advanced cyberattacks, including ransomware and other forms of malware. · Rapid Recovery: Reduced dependency on central IT support empowers users to initiate one-click recovery of distributed endpoints, including bare-metal recovery of physical workloads. · Reduced TCO: Broad, multigenerational OS support, enables vendor consolidation while ensuring comprehensive protection. · Simplified management: Centralized management includes local autonomy and seamless integration with existing third-party tools to provide a unified view of backup and recovery operations along with broad, multigenerational OS support. · Data sovereignty: With the use of Acronis’ extensive network of global data centers, users can ensure compliance and master regional data sovereignty laws, offering peace of mind and regulatory compliance. Acronis is majority-owned by EQT.

Average Rating: 4.3/5.0

Total Reviews: 658

How Do G2 Users Rate Acronis Cyber Protect?

  • Ease of Admin: 8.4/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.4/10 (Category avg: 9.0/10)
  • Quality of Support: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 8.6/10 (Category avg: 8.7/10)

Who Is the Company Behind Acronis Cyber Protect?

  • Seller: Acronis
  • Year Founded: 2003
  • HQ Location: Schaffhausen
  • Twitter: @acronis
    94,498 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,923 employees on LinkedIn®
  • Ownership: Acronis is majority-owned by EQT

Who Uses This Product?

  • Who Uses This: Software Developer, Support Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 45% Small, 40% Medium

What Do G2 Reviewers Say About Acronis Cyber Protect?

AI-generated summary from verified user reviews

Pros
  • Users value Acronis Cyber Protect for its integrated backup and cybersecurity, streamlining management and enhancing data safety.
  • Users appreciate the ease of use of Acronis Cyber Protect, thanks to its intuitive interface and streamlined features.
  • Users appreciate the all-in-one solution of Acronis Cyber Protect, combining backup and cybersecurity for efficient management.
  • Users appreciate the data recovery capabilities of Acronis Cyber Protect, allowing quick restoration and seamless management.
  • Users appreciate the all-in-one security solution of Acronis Cyber Protect, simplifying data protection and recovery management.
Cons
  • Users find Acronis Cyber Protect to be expensive, especially challenging for smaller businesses on a budget.
  • Users find the complexity of setup and configuration of Acronis Cyber Protect can be overwhelming, especially for non-IT users.
  • Users find Acronis Cyber Protect to have a difficult learning curve, which complicates initial setup and usage.
  • Users express frustration with poor customer support from Acronis, leading to delays and unresolved issues during setup.
  • Users experience slow performance with Acronis Cyber Protect, particularly during client setup and on older machines.

What Are Recent G2 Reviews of Acronis Cyber Protect?

What Are G2 Users Discussing About Acronis Cyber Protect?

IBM QRadar EDR

IBM Security QRadar EDR (formerly ReaQta) combines automation and dashboards to minimize analyst workloads, detect anomalous endpoint behavior and remediate threats in near real time. IBM Security QRadar EDR is available on AWS Marketplace. With visibility across endpoints, it combines expected features, like MITRE ATT&CK mapping and attack visualizations, with dual-engine AI and automation. For teams that need extended support, managed detection and response (MDR) services offers 24/7 monitoring and response to help keep users protected. IBM Security QRadar EDR (formerly ReaQta) can be deployed as SaaS, on-premises and in air-gapped environments. For more information, visit https://www.ibm.com/products/qradar-edr

Average Rating: 4.2/5.0

Total Reviews: 45

How Do G2 Users Rate IBM QRadar EDR?

  • Ease of Admin: 8.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Quality of Support: 8.2/10 (Category avg: 8.7/10)
  • Ease of Use: 8.5/10 (Category avg: 8.7/10)

Who Is the Company Behind IBM QRadar EDR?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • Twitter: @IBMSecurity
    74,660 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM

Who Uses This Product?

  • Top Industries: Computer & Network Security
  • Company Size: 45% Small, 40% Medium

What Do G2 Reviewers Say About IBM QRadar EDR?

AI-generated summary from verified user reviews

Pros
  • Users find the advanced threat detection of IBM QRadar EDR essential for maintaining system security and integrity.
  • Users appreciate the ease of use of IBM QRadar EDR, noting its simple installation and effective logging capabilities.
  • Users value the advanced threat detection and endpoint protection of IBM QRadar EDR, ensuring robust security and continuous updates.
  • Users praise the advanced threat detection capabilities of IBM QRadar EDR, enhancing security and responsiveness significantly.
  • Users value the robust threat detection of IBM QRadar EDR, enhancing security against cyber threats effectively.
Cons
  • Users find IBM QRadar EDR too expensive for small and mid-sized businesses, limiting accessibility and affordability.
  • Users find difficult learning due to initial setup challenges and a need for programming knowledge, complicating effective use.
  • Users find IBM QRadar EDR to be resource intensive, leading to increased costs and implementation challenges.
  • Users experience many false positives with QRadar EDR, requiring additional manual investigation and attention from the team.
  • Users experience high resource usage with IBM QRadar EDR, requiring powerful devices for optimal performance.

What Are Recent G2 Reviews of IBM QRadar EDR?

CrowdSec

CrowdSec is an open-source security stack that detects aggressive behaviors and prevents them from accessing your systems. Its user-friendly design and ease of integration into your current security infrastructure offer a low technical entry barrier and a high-security gain. Once an unwanted behavior is detected, it is automatically blocked. The aggressive IP, scenario triggered and the timestamp is sent for curation, to avoid poisoning & false positives. If verified, this IP is then redistributed to all CrowdSec users running the same scenario. By sharing the threat they faced, all users are protecting each other.

Average Rating: 4.7/5.0

Total Reviews: 85

How Do G2 Users Rate CrowdSec?

  • Ease of Admin: 8.8/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.0/10)
  • Quality of Support: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 8.7/10)

Who Is the Company Behind CrowdSec?

  • Seller: CrowdSec
  • Year Founded: 2020
  • HQ Location: Paris, FR
  • Twitter: @Crowd_Security
    19,491 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    31 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 69% Small, 20% Medium

What Are Recent G2 Reviews of CrowdSec?

What Are G2 Users Discussing About CrowdSec?

VIPRE Endpoint Security Cloud

VIPRE Endpoint Security Cloud is a next-generation antivirus (NGAV) platform, a.k.a. Endpoint Protection Platform (EPP), that detects and blocks malicious activity on your Microsoft Windows and Apple MacOS desktops, laptops, and servers. Consistently ranked at the top of independent testing agencies' lists, VIPRE combines excellent detection with low false positives, minimal system impact, and an easy to use mobile-ready administrative console. Packed with other goodies such as integrated vulnerability and patch management, web access control, and DNS protection, VIPRE will keep you safe against even the most sophisticated threats.

Average Rating: 4.3/5.0

Total Reviews: 56

How Do G2 Users Rate VIPRE Endpoint Security Cloud?

  • Ease of Admin: 8.5/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.0/10)
  • Quality of Support: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 8.7/10)

Who Is the Company Behind VIPRE Endpoint Security Cloud?

  • Seller: VIPRE Security
  • Year Founded: 1994
  • HQ Location: Clearwater, FL
  • Twitter: @VIPRESecurity
    8,293 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    238 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 48% Small, 43% Medium

What Do G2 Reviewers Say About VIPRE Endpoint Security Cloud?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of VIPRE Endpoint Security Cloud, particularly benefiting from its central management console.
  • Users value the alert notifications from VIPRE Endpoint Security Cloud, which enhance their overall security awareness.
  • Users value the easy installation of VIPRE Endpoint Security Cloud, allowing for hassle-free antivirus protection.
  • Users appreciate the central management console of VIPRE Endpoint Security Cloud, simplifying network management significantly.
  • Users value the centralized management of VIPRE Endpoint Security Cloud, simplifying network management significantly.
Cons
  • Users note that the backup issues in VIPRE Endpoint Security Cloud, especially restoring removed links, require enhancement.
  • Users point out a need for improved email link restoration in VIPRE Endpoint Security Cloud for better functionality.
  • Users note that the ability to restore removed links from email requires significant enhancement for better usability.

What Are Recent G2 Reviews of VIPRE Endpoint Security Cloud?

What Are G2 Users Discussing About VIPRE Endpoint Security Cloud?

Uptycs

Uptycs unified CNAPP and XDR platform is a comprehensive security solution designed to protect the full spectrum of modern attack surfaces in your cloud, data centers, user devices, build pipelines, and containers. With a strong focus on DevSecOps, Uptycs offers a powerful combination of CNAPP capabilities, including Cloud Workload Protection Platform (CWPP), Kubernetes Security Posture Management (KSPM), Cloud Security Posture Management (CSPM), Cloud Infrastructure Entitlement Management (CIEM), and Cloud Detection and Response (CDR). With Uptycs you also get industry-leading eXtended Detection and Response (XDR) across macOS, Windows, and Linux endpoints, ensuring comprehensive protection, detection, and investigation. Uptycs delivers real-time threat detection, context-rich alerts, and maps detections to the MITRE ATT&CK framework for improved security insights. Uptycs performs scanning of containers for vulnerabilities throughout the CI/CD pipeline, promoting agile DevOps workflows, and reducing risk in production environments. Uptycs seamlessly integrates with existing tools and processes, streamlining operations and improving overall efficiency. Customers also benefit from the flexibility to choose between agent-based and agentless scanning options tailored to their unique cloud workload needs. Discover how Uptycs can transform your security posture with a comprehensive, flexible, and powerful security solution designed to meet the needs of today's complex and rapidly evolving cloud environments. Shift up with Uptycs. KEY DIFFERENTIATORS: 1. Unified & Comprehensive Platform: Uptycs offers a holistic security solution with CNAPP capabilities (CWPP, KSPM, CSPM, CIEM, and CDR) across data centers, laptops, build pipelines, containers, and cloud environments, reducing tool sprawl. 2. Advanced XDR: Industry-leading eXtended Detection and Response for endpoint protection across macOS, Windows, and Linux systems. 3. DevSecOps Focus: Enhanced security for container-based workloads and Kubernetes, supporting agile DevOps workflows. 4. Real-Time Threat Detection: Context-rich alerts and threat detection mapped to the MITRE ATT&CK framework for improved insights. 5. CI/CD Integration: Efficiently scan containers for vulnerabilities throughout the CI/CD pipeline, reducing risk in production. 6. Both agent-based and agentless scanning. Deploy agentless scanning for rapid, friction-free coverage to keep your data secure, and gain continuous runtime security, real-time investigations, and remediation with agent-based telemetry. 7. Rich API & Compatibility: Seamless integration with existing security tools and platforms, powered by osquery for broad compatibility. 8. Expert Support & Flexibility: Dedicated support from security experts and the best of both worlds with agent-based and agentless scanning options tailored to your needs.

Average Rating: 4.4/5.0

Total Reviews: 13

How Do G2 Users Rate Uptycs?

  • Ease of Admin: 8.3/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.0/10)
  • Quality of Support: 9.0/10 (Category avg: 8.7/10)
  • Ease of Use: 7.9/10 (Category avg: 8.7/10)

Who Is the Company Behind Uptycs?

  • Seller: Uptycs
  • Year Founded: 2016
  • HQ Location: Waltham, US
  • Twitter: @uptycs
    1,483 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 54% Medium, 38% Large

What Do G2 Reviewers Say About Uptycs?

AI-generated summary from verified user reviews

Pros
  • Users value the comparative analysis features of Uptycs, aiding in selecting the best cloud security tools.
  • Users appreciate the comparative analysis features of Uptycs, aiding them in selecting the best cloud security tools.
  • Users value the comparative analysis features of Uptycs for making informed decisions in cloud security tools.
  • Users value Uptycs for its compliance with CIS and PCI DSS standards, enhancing security monitoring capabilities.
  • Users value the compliance management of Uptycs, appreciating its adherence to CIS and PCI DSS standards.
Cons
  • Users regret the high fees of Uptycs, which impact their willingness to continue using the tool.
  • Users express concerns about high pricing, which makes continued use of Uptycs challenging for some.

What Are Recent G2 Reviews of Uptycs?

Elastic Security

Modernize your SOC with AI Security is a data problem. Your team needs to detect, investigate, and respond to threats quickly. Elastic Security unifies next-gen SIEM and XDR with native automation, with AI built into every step. Built on Elasticsearch, the open-source search platform trusted by millions, Elastic provides complete visibility across your environment. Our data mesh architecture streamlines analysis to raise team productivity and reduce attacker dwell time. Bolster your defenses - Detect threats faster by analyzing data from across your attack surface - Stop attacks with the industry's best-rated XDR protection - Close the loop faster with Elastic Workflows, blending scripted automation with agentic AI reasoning - Get more accurate AI assistance, grounded in your data using Elasticsearch's leading relevance capabilities With Elastic Security, your SOC team can use generative AI to distill alerts, automate repetitive tasks, and get tailored guidance, all with your choice of LLM and full transparency into reasoning and sources. SOC leaders choose Elastic Security when they need a unified, open platform ready to run on any cloud, on-prem, or air-gapped.

Average Rating: 4.5/5.0

Total Reviews: 23

How Do G2 Users Rate Elastic Security?

  • Ease of Admin: 7.7/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.0/10)
  • Quality of Support: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 8.7/10)

Who Is the Company Behind Elastic Security?

  • Seller: Elastic
  • Company Website:
  • Year Founded: 2012
  • HQ Location: San Francisco, CA
  • Twitter: @elastic
    65,200 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    10,457 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 61% Medium, 52% Small

What Do G2 Reviewers Say About Elastic Security?

AI-generated summary from verified user reviews

Pros
  • Users value the flexible integrations of Elastic Security, enhancing deep visibility and streamlining threat detection workflows.
  • Users appreciate the ease of use in managing alerts and navigating workflows within Elastic Security.
  • Users appreciate the powerful detection capabilities and flexibility of Elastic Security for effective threat management.
  • Users appreciate the easy integrations with existing tools, enhancing the overall functionality of Elastic Security.
  • Users value the efficiency in investigations provided by Elastic Security, enhancing their threat detection and response capabilities.
Cons
  • Users struggle with the steep learning curve and operational overhead of Elastic Security, complicating effective usage and maintenance.
  • Users find the complex implementation of Elastic Security challenging, requiring significant expertise and ongoing administrative effort.
  • Users struggle with the complexity of Elastic Security, citing high administrative demands and a steep learning curve.
  • Users struggle with the complex setup of Elastic Security, facing a steep learning curve and heavy administrative overhead.
  • Users experience integration issues with Elastic Security, facing challenges in correlating log sources effectively.

What Are Recent G2 Reviews of Elastic Security?

LMNTRIX

LMNTRIX has reimagined cybersecurity, turning the tables in favor of the defenders once again. We have cut out the bloat of SIEM, log analysis and false positives resulting in alert fatigue, and we created new methods for confounding even the most advanced attackers. We believe that in a time of continuous compromise you need continuous response – not incident response. Our approach turns inward and assumes that you’re already breached and that you’re continually going to be breached, so we take a pro-active, offensive, hunting, and adversarial pursuit stance as opposed to a reactive, defensive, legacy stance with analysts staring at a SIEM console wishing they could detect an APT. LMNTRIX Active Defense is a best in class Managed Detection & Response (MDR) service that detects and responds to advanced threats that bypass perimeter controls. We combine deep expertise with cutting-edge technology, leading intelligence, and advanced analytics to detect and investigate threats with great speed, accuracy, and focus. The outcomes we deliver clients are validated breaches that are investigated, contained and remediated. All incidents are aligned to the kill chain and Mitre ATT&CK frameworks and contain detailed investigative actions and recommendations that your organisation follows to protect against the unknown, insider threat and malicious attacker. Active Defense is made up of 3 elements: LMNTRIX GRID (XDR) – This is our cyber defence SaaS platform that provides a new utility model for enterprise security, delivering pervasive visibility, automated threat detection & prevention, threat hunting, investigation, validation and unlimited forensic exploration on-demand and entirely from the cloud. It is a single investigative platform for insights into threats on enterprise, cloud, hybrid, and industrial control systems (ICS) networks. The LMNTRIX Grid delivers unique advantages over current network security solutions. It is a holistic and multi-vector platform with unlimited retention window of full-fidelity network traffic, innovative security visualizations, and the ease and cost-savings of an on-demand deployment model. LMNTRIX Technology Stack –This is our powerful proprietary threat detection stack that is deployed onsite, behind existing controls. It combines multiple threat detection systems, with deceptions everywhere, machine learning, threat intel, correlation, static file analysis, heuristics, and behavior and anomaly detection techniques to find threats in real-time. It decreases alarm fatigue by automatically determining which alerts should be elevated to security events, and reduces false positives by requiring consensus across detection. LMNTRIX Cyber Defense Centers - While these technologies are without peer, what sets us apart from the pack is our team of cybersecurity professionals who continually monitor our clients environments 24x7 while simultaneously hunting threats internally as well as monitoring developments on the deep and dark web. Our CDC's are a global network of cyber defense centers with highly trained and certified intrusion analysts who provide constant vigilance and on-demand analysis of your networks. Our intrusion analysts monitor your networks and endpoints 24x7, applying the latest intelligence and proprietary methodologies to look for signs of compromise. When a potential compromise is detected, the team performs an in- depth analysis on affected systems to confirm the breach. When data theft or lateral movement is imminent, our automated perimeter containment blocks attackers in their tracks while endpoint containment feature makes immediate reaction possible by quarantining affected hosts, whether they are on or off your corporate network, significantly reducing or eliminating the consequences of a breach.

Average Rating: 4.9/5.0

Total Reviews: 10

How Do G2 Users Rate LMNTRIX?

  • Ease of Admin: 10.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.0/10)
  • Quality of Support: 9.6/10 (Category avg: 8.7/10)
  • Ease of Use: 9.6/10 (Category avg: 8.7/10)

Who Is the Company Behind LMNTRIX?

  • Seller: LMNTRIX
  • Year Founded: 2015
  • HQ Location: Orange, California
  • Twitter: @lmntrixlabs
    75 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    76 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Medium, 20% Large

What Are Recent G2 Reviews of LMNTRIX?

What Are G2 Users Discussing About LMNTRIX?

MetaDefender

MetaDefender Platform is an advanced threat prevention solution that lets organizations embed multi-layer file security into existing applications and security architectures, especially to protect common attack vectors like malicious file uploads, untrusted file transfers, and file-based supply chain risk. It’s designed for environments that need stronger protection against highly evasive malware, zero-day attacks, and APTs, including IT and OT/critical infrastructure use cases. MetaDefender easily integrates into your existing IT solutions and can be deployed on-premises (including air-gapped), in cloud/IaaS, or as SaaS. We offer flexible implementation options for ICAP enabled devices, containerized applications, AWS, Azure, NAS/Storage workflows and Rest API. Overview: Multi-engine malware scanning: Quickly scan files with 30+ antivirus engines and detect over 99% of known malware. Deep CDR (Content Disarm & Reconstruction): Recursively sanitize and rebuild 200+ file types to neutralize embedded threats while maintaining file usability, with extensive reconstruction and file conversion options. Proactive DLP: Remove, redact, or watermark sensitive data in files before content enters or leaves the organization; also supports AI-powered document classification. File-based Vulnerability Assessment: Identify vulnerabilities in installers, binaries, and applications before they are installed/executed and reduce exposure to known software flaws. Threat intelligence-driven detection: Identify malicious domains and IPs embedded in documents and support near real-time blocking using curated threat intelligence. Adaptive threat analysis (sandboxing): Detonate and analyze suspicious files in a controlled environment and improve zero-day detection. SBOM & software supply chain visibility: Generate SBOMs and identify vulnerabilities in source code and containers. Reputation Engine: Use file hash reputation (known good/known bad/unknown) and advanced analysis to remediate false positives faster. Visibility, reporting, and policy control: Gain operational visibility, use automated reports for remediation, and configure workflow/analysis rules based on user, business priority, file source, and file type. Free Training - OPSWAT Academy: https://www.opswat.com/academy

Average Rating: 4.3/5.0

Total Reviews: 15

How Do G2 Users Rate MetaDefender?

  • Ease of Admin: 8.8/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.0/10)
  • Quality of Support: 8.8/10 (Category avg: 8.7/10)
  • Ease of Use: 9.0/10 (Category avg: 8.7/10)

Who Is the Company Behind MetaDefender?

  • Seller: OPSWAT
  • Company Website:
  • Year Founded: 2002
  • HQ Location: Tampa, Florida
  • Twitter: @OPSWAT
    7,257 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,185 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 40% Medium, 40% Small

What Do G2 Reviewers Say About MetaDefender?

AI-generated summary from verified user reviews

Pros
  • Users find MetaDefender to be reliable and simple to manage, enhancing their cybersecurity experience effortlessly.
  • Users appreciate the exceptional security of MetaDefender, highlighting its reliability and effectiveness in threat elimination.
  • Users value the reliable protection of MetaDefender, praising its effectiveness against malware and ease of management.
  • Users benefit from the scanning efficiency of MetaDefender, confidently eliminating threats swiftly and effectively.
  • Users value the effective scanning capabilities of MetaDefender, enhancing security and providing thorough threat detection.
Cons
  • Users find the complex configuration requirements challenging, necessitating significant upfront planning and policy tuning effort.
  • Users experience a difficult setup process during rollout due to extensive policy tuning and adjustment needs.
  • Users experience excessive blocking issues during initial policy tuning, leading to unnecessary restrictions on business files.
  • Users find that overblocking can be an issue, requiring careful policy adjustments to ensure safe files aren't hindered.
  • Users find that policy tuning requires significant effort initially, particularly with archives and mixed file types.

What Are Recent G2 Reviews of MetaDefender?

What Are G2 Users Discussing About MetaDefender?

CySight

CySight’s revolutionary Actionable Intelligence, trusted by Fortune 500 globally, enables organizations with the most cost-effective and secure way to tackle the increasing density, complexity, and expanse of modern physical and cloud networking. Deploying cyber network intelligence, CySight empowers network and security teams to substantially accelerate incident response by eliminating blindspots, analyzing network telemetry to discover anomalies, uncover cyber-threats, and quantifying asset usage and performance. CySight's Dropless Collection method enables unsurpassed visibility of network big-data which is retained in the smallest footprint, accelerating machine learning, artificial intelligence and automation to fully utilize all metadata no matter the amount, size, or type.

Average Rating: 4.3/5.0

Total Reviews: 2

How Do G2 Users Rate CySight?

  • Quality of Support: 6.7/10 (Category avg: 8.7/10)
  • Ease of Use: 10.0/10 (Category avg: 8.7/10)

Who Is the Company Behind CySight?

Who Uses This Product?

  • Company Size: 100% Medium

What Do G2 Reviewers Say About CySight?

AI-generated summary from verified user reviews

Pros
  • Users value the extensive database of CySight, allowing for detailed investigations and easy data tracking.
  • Users value the comprehensive monitoring of CySight, allowing for thorough data tracking and detailed investigations.
  • Users value the extensive data tracking capabilities of CySight, enabling detailed investigations with ease.
  • Users value the robust monitoring capabilities of CySight, enabling detailed investigations of network data effectively.
  • Users value the superior visibility provided by CySight's Dropless Assortment, effectively capturing all organizational information.
Cons
  • Users experience alerting issues with CySight, leading to alarm fatigue and potentially overlooking critical notifications.
  • Users report alert issues while customizing CySight, leading to alarm fatigue and essential notifications being overlooked.
  • Users find configuration issues cumbersome, leading to alarm fatigue and potentially missing critical alerts.
  • Users face connection issues with CySight, leading to alarm fatigue and the risk of overlooking critical alerts.
  • Users express frustration with the inadequate reporting of anomalies, lacking specific details like IPs and protocols.

What Are Recent G2 Reviews of CySight?

Gradient Cyber

​Gradient Cyber’s Managed Extended Detection and Response (MXDR) service offers mid-market organizations comprehensive, 24/7/365 protection across their entire IT environment, including networks, endpoints, cloud infrastructures, Software as a Service (SaaS) applications, and business process applications. By integrating advanced AI/ML-driven analytics with human expertise through our proprietary XDR platform, Quorum™, we ensure rapid detection and neutralization of threats before they can impact operations. ​ Key Features of Gradient Cyber's MXDR Service: - Comprehensive Coverage: Our MXDR solution provides unified detection and response across all critical components of your IT ecosystem, ensuring no blind spots for attackers to exploit. ​ - Proactive Threat Detection: Utilizing a combination of automated tools and human analysis, we identify and mitigate threats in near real-time, significantly reducing the risk of breaches. ​ - Expert-Led Response: With a 10:1 client-to-analyst ratio, our dedicated team of security professionals offers personalized service, acting as an extension of your in-house team to swiftly address and remediate threats. ​ - High Accuracy: Our approach achieves a 99% false positive elimination rate, allowing your IT staff to focus on genuine threats without the distraction of unnecessary alerts. ​ - Scalability Across Industries: Serving clients in over 35 verticals, our MXDR service is tailored to meet the unique security challenges of various industries, ensuring relevant and effective protection. ​ - Robust Infrastructure: Operating from four in-house Security Operations Centers (SOCs) worldwide, we provide continuous monitoring and rapid response capabilities, ensuring global coverage and resilience. ​ - Integrated Compliance Tracking: Our service includes compliance tracking and detailed Situation Reports (SitReps), offering transparency and aiding in regulatory adherence. ​ By choosing Gradient Cyber’s MXDR service, organizations benefit from a seamless blend of technology and human expertise, transforming their cybersecurity posture from reactive to proactive.

Average Rating: 4.8/5.0

Total Reviews: 4

How Do G2 Users Rate Gradient Cyber?

  • Ease of Admin: 10.0/10 (Category avg: 8.8/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.0/10)
  • Quality of Support: 10.0/10 (Category avg: 8.7/10)
  • Ease of Use: 9.2/10 (Category avg: 8.7/10)

Who Is the Company Behind Gradient Cyber?

  • Seller: Gradient Cyber
  • Year Founded: 2017
  • HQ Location: Southlake, US
  • Twitter: @GradientCyber
    126 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    52 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Small, 25% Medium

What Do G2 Reviewers Say About Gradient Cyber?

AI-generated summary from verified user reviews

Pros
  • Users highlight the automation capabilities of Gradient Cyber, streamlining security management and enhancing overall efficiency.
  • Users value the continuous monitoring by Gradient Cyber, allowing for effortless security management and proactive threat response.
  • Users praise the exceptional customer support at Gradient Cyber, highlighting their proactive assistance and collaborative approach.
  • Users value the customization options in Gradient Cyber, enhancing their security management experience through tailored features.
  • Users value the dashboard customization of Gradient Cyber, appreciating its intuitive layout and focused functionality for effective security management.

What Are Recent G2 Reviews of Gradient Cyber?

iVerify Enterprise Mobile EDR

iVerify: Mobile EDR for the modern threat landscape: iVerify is a pioneer in mobile EDR, providing security teams kernel-adjacent visibility into mobile devices, closing a gap that's persisted while laptops and servers have long had full EDR. iVerify detects, investigates, and responds to the threats mobile devices face today: fileless malware, spyware, smishing, malicious applications, and enterprise credential theft. iVerify's solutions make secure mobile productivity possible, letting employees work confidently from their phones without putting the business at risk. A Threat Landscape That Has Outpaced Mobile Defenses: The mobile device has become the primary identity surface of the modern enterprise. It holds authentication tokens, password manager access, MFA applications, corporate email, and direct access to cloud systems, often more than any laptop. Yet mobile still receives a fraction of the security investment applied to traditional endpoints, and there is no mobile equivalent of EDR in most security stacks. Enterprise Differentiators Built for This Threat Model: iVerify was built specifically to close that gap, and its differentiation starts with depth of access. iVerify collects log and artifact data directly from the mobile operating system, kernel-adjacent telemetry that enables continuous analysis of device integrity, process behavior, and system activity, rather than the indirect, app-layer signals that MDM platforms and legacy MTD vendors are limited to. No current competitor combines operating system-level telemetry, full attack-chain coverage, and mobile-specific threat intelligence the way iVerify does, and the gap is most pronounced on iOS, historically the hardest platform to instrument. That visibility extends across the entire mobile attack chain, not just the device itself. SmishGuard detects and blocks smishing using on-device inference, SIM-swap detection closes the MFA-bypass gap, and telecom and location intelligence flags exposure to malicious networks, IMSI catchers, and high-risk infrastructure for traveling employees, visibility no device-only tool provides. Through its integration with NowSecure, iVerify extends that same rigor to the application layer, giving security teams continuous risk scoring for third-party and AI apps on the fleet. Underpinning all of it is an active threat research team running the iVerify Spyware Observatory, with an established track record of surfacing nation-state spyware such as Pegasus, Predator, and Paragon Graphite, and independently uncovering novel exploit chains like the DarkSword browser-to-OS vulnerability affecting up to 270 million devices. Every capability is delivered as enterprise infrastructure. iVerify deploys via MDM, MAM, or standalone, fleet-wide in minutes, and integrates through an open API with SIEM, SOAR, XDR, and IAM platforms, including Okta, Azure, and Entra ID, with real-time alerting via webhooks. Deployment options span cloud, hybrid, and fully on-prem environments, giving security operations teams mobile telemetry that flows directly into the workflows they already run. Key Benefits: For enterprise security leaders, that architecture translates into four concrete advantages: 1. Unrivaled visibility, with system-level telemetry across iOS and Android 2. Advanced detection, with a proven record against Pegasus, Predator, DarkSword, and Coruna, and forensics built to catch the zero-click exploits legacy MTD misses 3. Privacy by design, with no PII collection by default, no MDM requirement, and transparent handling whenever device data access is genuinely needed, making it equally effective for BYOD and corporate-owned fleets 4. Enterprise readiness, with flexible zero-touch, cloud, or on-prem deployment that protects devices from day one and drops straight into existing SOC workflows. Built for High-Value Enterprise Verticals: iVerify serves enterprise and government organizations with complex mobile fleets and elevated threat exposure. In financial services, it replaces legacy MTD with zero-click detection across the entire workforce, not just VIPs, supporting requirements like DORA, FFIEC, and PCI DSS. In government and defense, it surfaces nation-state spyware such as Pegasus and Graphite even when no visible indicators exist, addressing gaps that leave SOC teams unable to confirm compromise. For aviation and airlines, iVerify fuses mobile operator telemetry with on-device detection to flag network threats affecting device behavior, helping teams assess geographic exposure, investigate suspected compromise, and prioritize risks to operational access and sensitive data Technology and software companies rely on iVerify to stop IP theft and nation-state targeting of executive and engineering devices without surveilling BYOD employees. Healthcare and life sciences organizations use it to protect patient data as iOS adoption accelerates across clinical and administrative staff, faster than security coverage typically keeps pace. Media and entertainment organizations depend on detection that never touches a journalist's or source's content, and iVerify.org extends that same protection to civil society groups and NGOs facing sophisticated surveillance. And across mission-critical mobile operations involving shared or unmanaged devices, iVerify provides a detection layer beneath MDM where traditional management tools stop short. Mobile is no longer a secondary concern in the enterprise security stack, it is a primary target with the access adversaries want most. iVerify is Mobile EDR: built to give security teams the same visibility, detection, and response capability on mobile that they already expect from every other endpoint in the environment.

Who Is the Company Behind iVerify Enterprise Mobile EDR?

  • Seller: iVerify
  • Company Website:
  • Year Founded: 2023
  • HQ Location: New York City, US
  • LinkedIn® Page: www.linkedin.com
    50 employees on LinkedIn®
Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated March 4, 2025