Best Cloud Security Monitoring and Analytics Software for Small Business

How Many Cloud Security Monitoring and Analytics Software Products Does G2 Track?

Total Products under this Category: 86

Category Stats (Nov 2026)

  • Average Rating: 4.51/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: AppOmni (+2.3%) - Among all products in this category, AppOmni recorded the largest rating increase compared to last month

Last updated: November 12, 2026

How Does G2 Rank Cloud Security Monitoring and Analytics Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,900+ Authentic Reviews
  • 86+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

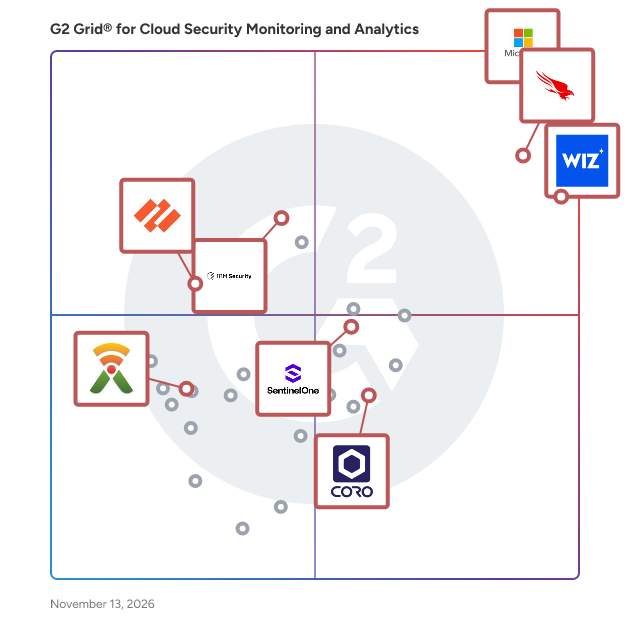
G2 Grid® for Cloud Security Monitoring and Analytics Software

G2 Grid® for Cloud Security Monitoring and Analytics Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, Wiz, CrowdStrike Falcon Cloud Security, IBM QRadar SIEM, Coro Cybersecurity, SentinelOne Singularity Cloud Security, SaaS Alerts, and Palo Alto Cortex XSIAM.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-security-monitoring-and-analytics/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=wiz-wiz&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=coro-cybersecurity&focus%5B%5D=sentinelone-singularity-cloud-security&focus%5B%5D=saas-alerts&focus%5B%5D=palo-alto-cortex-xsiam&segment=small-business)

Microsoft Defender for Cloud

Microsoft Defender for Cloud is a cloud native application protection platform for multicloud and hybrid environments with comprehensive security across the full lifecycle, from development to runtime.

Average Rating: 4.4/5.0

Total Reviews: 433

How Do G2 Users Rate Microsoft Defender for Cloud?

  • Security Integration: 8.3/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.8/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • Security Automation: 8.5/10 (Category avg: 8.6/10)

Who Is the Company Behind Microsoft Defender for Cloud?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Who Uses This: Saas Consultant, Software Engineer
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Medium, 35% Large

What Do G2 Reviewers Say About Microsoft Defender for Cloud?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the proactive security of Microsoft Defender for Cloud, ensuring peace of mind against potential threats and malware.
  • Users emphasize the comprehensive security of Microsoft Defender for Cloud, appreciating its proactive threat protection and ease of use.
  • Users appreciate the ease of use and real-time threat notifications of Microsoft Defender for Cloud, enhancing workflow efficiency.
  • Users appreciate the real-time vulnerability detection of Microsoft Defender for Cloud, enhancing their security and workflow efficiency.
  • Users value the real-time threat detection of Microsoft Defender for Cloud, ensuring robust security and peace of mind.
Cons
  • Users find the pricing complexity and overwhelming features of Microsoft Defender for Cloud challenging to navigate effectively.
  • Users note that the pricing can be expensive, especially for small to medium businesses, causing potential budgeting issues.
  • Users express frustration with delayed detection of threats, complicating their security management and response efforts.
  • Users experience false positive alerts with Microsoft Defender for Cloud, complicating the detection of real threats.
  • Users express frustration over the complex licensing structure of Microsoft Defender for Cloud, leading to confusion and unexpected costs.

What Are Recent G2 Reviews of Microsoft Defender for Cloud?

What Are G2 Users Discussing About Microsoft Defender for Cloud?

Wiz

Wiz transforms cloud security for customers – including more than 50% of the Fortune 100 – by enabling a new operating model. With Wiz, organizations can democratize security across the development lifecycle, empowering them to build fast and securely. Its Cloud Native Application Protection Platform (CNAPP) consolidates CSPM, KSPM, CWPP, Vulnerability management, IaC scanning, CIEM, DSPM into a single platform. Wiz drives visibility, risk prioritization, and business agility. Protecting Your Cloud Environments Requires a Unified, Cloud Native Platform. Wiz connects to every cloud environment, scans every layer, and covers every aspect of your cloud security - including elements that normally require installing agents. Its comprehensive approach has all of these cloud security solutions built in. Hundreds of organizations worldwide, including 50 percent of the Fortune 100, to rapidly identify and remove critical risks in cloud environments. Its customers include Salesforce, Slack, Mars, BMW, Avery Dennison, Priceline, Cushman & Wakefield, DocuSign, Plaid, and Agoda, among others. Wiz is backed by Sequoia, Index Ventures, Insight Partners, Salesforce, Blackstone, Advent, Greenoaks, Lightspeed and Aglaé. Visit https://www.wiz.io for more information.

Average Rating: 4.7/5.0

Total Reviews: 929

How Do G2 Users Rate Wiz?

  • Security Integration: 8.7/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.0/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Security Automation: 8.4/10 (Category avg: 8.6/10)

Who Is the Company Behind Wiz?

  • Seller: Google
  • Company Website:
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG

Who Uses This Product?

  • Who Uses This: Security Engineer, CISO
  • Top Industries: Financial Services, Computer Software
  • Company Size: 54% Large, 37% Medium

What Do G2 Reviewers Say About Wiz?

AI-generated summary from verified user reviews

Pros
  • Users praise the user-friendly capabilities of Wiz, highlighting excellent service and reporting improvements.
  • Users value the enhanced security features of Wiz, benefiting from improved visibility and innovation in cloud security.
  • Users find Wiz to be incredibly easy to use, with a friendly interface and great support enhancing the experience.
  • Users value the enhanced visibility from Wiz, enabling efficient data security management and quick access to essential resources.
  • Users find the setup of Wiz to be easy and fast, enhancing their overall experience with its intuitive interface.
Cons
  • Users indicate that improvement is needed in reporting, alert tuning, and AI-related features for Wiz.
  • Users desire more features and consistency in Wiz to improve experience and enhance AI-related security capabilities.
  • Users find the learning curve steep, struggling with navigation and overwhelming popups in Wiz's interface.
  • Users highlight the need for improvements in reporting and additional capabilities in AI security and alert tuning.
  • Users find the complexity of the platform can be overwhelming, requiring significant effort to navigate and manage effectively.

What Are Recent G2 Reviews of Wiz?

CrowdStrike Falcon Cloud Security

Crowdstrike Falcon Cloud Security is the only CNAPP to stop breaches in the cloud Built for today’s hybrid and multi-cloud environments, Falcon Cloud Security protects the entire cloud attack surface - from code to runtime - by combining continuous agentless visibility with real-time detection and response. At runtime, Falcon Cloud Security delivers best-in-class cloud workload protection and real-time cloud detection and response (CDR) to stop active threats across hybrid environments. Integrated with the CrowdStrike Falcon platform, it correlates signals across endpoint, identity, and cloud to detect sophisticated cross-domain attacks that point solutions miss—enabling teams to respond faster and stop breaches in progress. To reduce risk before attacks occur, Falcon Cloud Security also delivers agentless-driven posture management that proactively shrinks the cloud attack surface. Unlike typical solutions, Crowdstrike enriches cloud risk detections with adversary intelligence and graph-based context, enabling security teams to prioritize exploitable exposures and prevent breaches before they happen. Customers using Falcon Cloud Security consistently see measurable results: 89% faster cloud detection and response 100x reduction in false positives by prioritizing exploitable, business-critical risk 83% reduction in cloud security licenses due to elimination of redundant tools

Average Rating: 4.5/5.0

Total Reviews: 249

How Do G2 Users Rate CrowdStrike Falcon Cloud Security?

  • Security Integration: 8.7/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.7/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.1/10 (Category avg: 9.2/10)
  • Security Automation: 8.6/10 (Category avg: 8.6/10)

Who Is the Company Behind CrowdStrike Falcon Cloud Security?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 52% Large, 31% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their protection in cloud environments.
  • Users value the real-time threat detection of CrowdStrike Falcon Cloud Security, enhancing their cloud security management significantly.
  • Users value the real-time detection efficiency of CrowdStrike Falcon Cloud Security for enhanced cloud threat management.
  • Users value the real-time vulnerability detection of CrowdStrike Falcon Cloud Security, enhancing proactive risk management and security.
  • Users appreciate the ease of use of CrowdStrike Falcon Cloud Security, making it a top choice for cloud cybersecurity.
Cons
  • Users find CrowdStrike Falcon Cloud Security to be expensive, particularly challenging for small businesses with budget constraints.
  • Users face issues with alert fatigue and response lag, calling for improved prioritization and better support resources.
  • Users experience alert fatigue and desire improved response times and better training resources for CrowdStrike Falcon.
  • Users find the feature complexity of CrowdStrike Falcon Cloud Security can overwhelm new users and necessitate a learning curve.
  • Users report a challenging learning curve with CrowdStrike Falcon, especially for those unfamiliar with similar tools.

What Are Recent G2 Reviews of CrowdStrike Falcon Cloud Security?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

IBM QRadar SIEM

Outsmart threats with an end-to-end award-winning security suite; proven to prevent, endure and recover from both known & unknown IT hazards faced by SoCs in the modern-day.

Average Rating: 4.4/5.0

Total Reviews: 286

How Do G2 Users Rate IBM QRadar SIEM?

  • Security Integration: 8.4/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.5/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • Security Automation: 8.3/10 (Category avg: 8.6/10)

Who Is the Company Behind IBM QRadar SIEM?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM
  • Phone: 1-866-277-7488

Who Uses This Product?

  • Who Uses This: SOC Analyst, Security Engineer
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 52% Large, 29% Medium

What Do G2 Reviewers Say About IBM QRadar SIEM?

AI-generated summary from verified user reviews

Pros
  • Users value the intuitive user interface of IBM QRadar SIEM, enhancing ease of use for all experience levels.
  • Users appreciate the seamless integration capabilities of IBM QRadar SIEM, enhancing data management and reporting efficiency.
  • Users appreciate the user-friendly dashboard of IBM QRadar SIEM, enhancing ease of use and customization.
  • Users value the easy integrations of IBM QRadar SIEM, enhancing functionality with seamless API and SaaS connections.
  • Users appreciate the intuitive user interface of IBM QRadar SIEM, which simplifies navigation for less experienced users.
Cons
  • Users find the UI improvements unsatisfactory, noting limitations in features, search capabilities, and report building.
  • Users find the product expensive, especially when increasing EPS and managing costs for maintenance and features.
  • Users find the cost of implementing QRadar SIEM to be high, particularly for smaller organizations, affecting accessibility.
  • Users struggle with dashboard issues in QRadar, experiencing inefficiencies and limited functionality in the user interface.
  • Users find the initial setup time-consuming, requiring significant expertise and effort to customize for their needs.

What Are Recent G2 Reviews of IBM QRadar SIEM?

Coro Cybersecurity

Coro is the easy cybersecurity company. We designed an all-in-one platform that every lean IT team will master. While other solutions scare people into buying complicated, confusing products, we lead with elegant simplicity. Coro is fast to deploy, easy to use, and designed not to waste your time. Once you install Coro, you’ll hardly think about us. That’s the point. Coro automatically detects and fixes security problems, so IT teams don’t have to spend time investigating or troubleshooting. We’re also one of the fastest-growing tech companies in North America, just ask Deloitte. Designed primarily for lean IT teams, Coro’s platform is particularly beneficial for organizations that may lack extensive IT resources or dedicated cybersecurity teams. With the increasing complexity of cyber threats, these businesses often find it challenging to maintain adequate security measures. Coro addresses this gap by automating the detection and remediation of security threats, allowing businesses to focus on their core operations without the constant worry of potential breaches or security incidents. One of Coro's key benefits is its intuitive, user-friendly interface, which simplifies the management of cybersecurity protocols. This ease of use is particularly advantageous for organizations with limited IT expertise, as it minimizes the need for extensive training or technical knowledge. Additionally, Coro’s continuous monitoring and reporting features provide businesses with valuable insights into their security posture, enabling them to make informed decisions about their cybersecurity strategies. Another impressive features is how comprehensive, yet powerful, it's all-in-one platform is. Using advanced AI technology, it detects and remediates over 92% of threats automatically, ensuring potential vulnerabilities are identified and addressed in real-time, significantly reducing the risk of data breaches and other cyber incidents. Their impressive performance has been recognised by G2 with a 94% approval rating from users and SE Labs, who awarded them three AAA ratings for their EDR, Email and Cloud modules. Overall, Coro’s cybersecurity platform represents a significant advancement in the field of cybersecurity. By automating threat detection and remediation, offering customizable solutions, and providing a user-friendly experience, Coro empowers organizations to effectively defend against the evolving landscape of cyber threats. Its recognition as one of the fastest-growing cybersecurity companies in North America further underscores its commitment to delivering innovative and effective security solutions.

Average Rating: 4.7/5.0

Total Reviews: 236

How Do G2 Users Rate Coro Cybersecurity?

  • Security Integration: 8.9/10 (Category avg: 8.6/10)
  • Activity Monitoring: 9.1/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.2/10)
  • Security Automation: 8.9/10 (Category avg: 8.6/10)

Who Is the Company Behind Coro Cybersecurity?

  • Seller: Coronet
  • Company Website:
  • Year Founded: 2014
  • HQ Location: Chicago, IL
  • LinkedIn® Page: www.linkedin.com
    275 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager, IT Director
  • Top Industries: Non-Profit Organization Management, Financial Services
  • Company Size: 56% Medium, 37% Small

What Do G2 Reviewers Say About Coro Cybersecurity?

AI-generated summary from verified user reviews

Pros
  • Users highlight the super simplicity of Coro Cybersecurity, allowing easy setup and proactive support for compliance needs.
  • Users value the proactive security alerts and dedicated support from Coro Cybersecurity, ensuring peace of mind.
  • Users value the exceptional Customer Support from Coro Cybersecurity, highlighting proactive assistance and dedicated representatives.
  • Users value the comprehensive protection provided by Coro Cybersecurity, ensuring robust security across multiple layers and tools.
  • Users value the easy setup of Coro Cybersecurity, enabling quick deployment and efficient management of cybersecurity measures.
Cons
  • Users experience performance issues with Coro Cybersecurity, including delays and limitations on device management and functionality.
  • Users frequently note the need for improvements in support and feature functionality within Coro Cybersecurity.
  • Users find the false positives in Coro Cybersecurity can be cumbersome, affecting email differentiation and usability.
  • Users experience inaccuracy in spam detection with Coro Cybersecurity, leading to frustrating false positives at times.
  • Users are concerned about the limited features of Coro, especially regarding filter customization and email reporting capabilities.

What Are Recent G2 Reviews of Coro Cybersecurity?

What Are G2 Users Discussing About Coro Cybersecurity?

SentinelOne Singularity Cloud Security

Singularity Cloud Security is SentinelOne’s comprehensive, cloud-native application protection platform (CNAPP). It combines the best of agentless insights with AI-powered threat protection, to secure and protect your multi-cloud infrastructure, services, and containers from build time to runtime. SentinelOne’s CNAPP applies an attacker’s mindset to help security practitioners better prioritize their remediation tasks with evidence-backed Verified Exploit Paths™. The efficient and scalable runtime protection, proven over 5 years and trusted by many of the world’s leading cloud enterprises, harnesses local, autonomous AI engines to detect and thwart runtime threats in real-time. CNAPP data and workload telemetry is recorded to SentinelOne’s unified security lake, for easy access and investigation.

Average Rating: 4.9/5.0

Total Reviews: 122

How Do G2 Users Rate SentinelOne Singularity Cloud Security?

  • Security Integration: 9.8/10 (Category avg: 8.6/10)
  • Activity Monitoring: 9.7/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.8/10 (Category avg: 9.2/10)
  • Security Automation: 9.7/10 (Category avg: 8.6/10)

Who Is the Company Behind SentinelOne Singularity Cloud Security?

  • Seller: SentinelOne
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 59% Medium, 30% Large

What Do G2 Reviewers Say About SentinelOne Singularity Cloud Security?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the strong AI-driven threat detection of SentinelOne Singularity, enhancing security while reducing manual efforts.
  • Users appreciate the ease of use of SentinelOne Singularity Cloud Security, praising its intuitive implementation and management.
  • Users appreciate the effective vulnerability detection of SentinelOne, enabling faster responses and enhanced security posture.
  • Users value the real-time protection of SentinelOne for securing cloud servers and data, enhancing overall security posture.
  • Users value the strong AI-driven threat detection in SentinelOne Singularity Cloud Security, enhancing efficiency and response times.
Cons
  • Users find the complexity of setup and configuration in SentinelOne Singularity Cloud Security challenging and time-consuming.
  • Users find that ineffective alerts necessitate careful tuning, which can complicate their experience with SentinelOne Singularity Cloud Security.
  • Users find the initial setup complex and time-consuming, which can challenge teams lacking cloud security expertise.
  • Users find the difficult configuration of SentinelOne Singularity Cloud Security can be complex and time-consuming initially.
  • Users find the poor UI of SentinelOne Singularity Cloud Security to be clunky, complicating navigation and usability.

What Are Recent G2 Reviews of SentinelOne Singularity Cloud Security?

SaaS Alerts

​​SaaS Alerts is a automated cybersecurity platform to detect and automate the remediation of SaaS security threats. The platform provides unified, continuous monitoring of core business SaaS applications to protect against data theft and malicious actors, including Microsoft 365, Google Workspace, Salesforce, Slack, Dropbox, Okta, Duo and more. SaaS Alerts uses machine learning pattern detection to identify breaches, create instant alerts, and lock affected accounts, providing you with valuable time to respond before further damage can occur. It also enables you to terminate dangerous end-user file sharing activities and automate essential security tasks, enhancing efficiency and overall security.

Average Rating: 4.4/5.0

Total Reviews: 36

How Do G2 Users Rate SaaS Alerts?

  • Security Integration: 8.3/10 (Category avg: 8.6/10)
  • Activity Monitoring: 9.2/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Security Automation: 8.7/10 (Category avg: 8.6/10)

Who Is the Company Behind SaaS Alerts?

  • Seller: Kaseya
  • Company Website:
  • Year Founded: 2000
  • HQ Location: Miami, FL
  • LinkedIn® Page: www.linkedin.com
    5,483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 86% Small, 14% Medium

What Do G2 Reviewers Say About SaaS Alerts?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time alerts from SaaS Alerts, ensuring rapid response to unusual user activity and security threats.
  • Users appreciate the ease of use of SaaS Alerts, enjoying its straightforward navigation and clear alerts for user activity.
  • Users value the real-time alert notifications from SaaS Alerts, providing confidence in monitoring user activity across tools.
  • Users appreciate the easy setup and regular innovative features that enhance the overall SaaS Alerts experience.
  • Users find the reporting capabilities of SaaS Alerts invaluable for identifying security vulnerabilities effortlessly.
Cons
  • Users find the ineffective alerts lead to wasted time on non-urgent issues, highlighting a need for better filtering.
  • Users find the inefficient alert system requires extra time for investigating notifications, disrupting workflow and productivity.
  • Users note false positives initially, but the system improves as it learns to filter them effectively.
  • Users find the inadequate filtering capabilities of SaaS Alerts lead to unnecessary time spent on non-urgent issues.
  • Users find the inefficient filtering of SaaS Alerts often leads to unnecessary time spent on non-actionable alerts.

What Are Recent G2 Reviews of SaaS Alerts?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 111

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Security Integration: 8.5/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.5/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 8.6/10 (Category avg: 9.2/10)
  • Security Automation: 8.3/10 (Category avg: 8.6/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Palo Alto Cortex XSIAM, benefiting from its intuitive interface and seamless integration.
  • Users value the advanced threat detection capabilities of Palo Alto Cortex XSIAM, ensuring both known and unknown threats are managed effectively.
  • Users value the seamless integrations of Palo Alto Cortex XSIAM, enhancing overall functionality across various platforms.
  • Users value the unified console of Palo Alto Cortex XSIAM for simplifying security management across endpoints, network, and cloud.
  • Users value the single console integration, highlighting its ease of use and reliability for threat detection.
Cons
  • Users find the Cortex XSIAM to be very expensive compared to other solutions, impacting overall satisfaction.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM a challenge due to its complexity and setup.
  • Users find the complexity of the console overwhelming, requiring significant time and expertise to navigate effectively.
  • Users report integration issues with Palo Alto Cortex XSIAM, facing challenges with non-native equipment and log maintenance.
  • Users find the UX improvement of Palo Alto Cortex XSIAM lacking in customization and intuitive design for features.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

Amazon GuardDuty

Amazon GuardDuty is a managed threat detection service that continuously monitors for malicious or unauthorized behavior to help you protect your AWS accounts and workloads.GuardDuty also detects potentially compromised instances or reconnaissance by attackers.

Average Rating: 4.1/5.0

Total Reviews: 54

How Do G2 Users Rate Amazon GuardDuty?

  • Security Integration: 10.0/10 (Category avg: 8.6/10)
  • Activity Monitoring: 6.7/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • Security Automation: 10.0/10 (Category avg: 8.6/10)

Who Is the Company Behind Amazon GuardDuty?

Who Uses This Product?

  • Who Uses This: Software Developer
  • Top Industries: Computer Software, Accounting
  • Company Size: 39% Large, 33% Small

What Are Recent G2 Reviews of Amazon GuardDuty?

What Are G2 Users Discussing About Amazon GuardDuty?

Sumo Logic

Sumo Logic, Inc. unifies and analyzes enterprise data, translating it into actionable insights through one AI-powered cloud-native log analytics platform. This single source of truth enables Dev, Sec and Ops teams to simplify complexity, collaborate efficiently and accelerate data-driven decisions that drive business value. Customers around the world rely on the Sumo Logic SaaS Log Analytics Platform for trusted insights to ensure application reliability, secure and protect against modern security threats, and gain insights into their cloud infrastructures. For more information, visit: SUMOLOGIC.COM

Average Rating: 4.4/5.0

Total Reviews: 413

How Do G2 Users Rate Sumo Logic?

  • Security Integration: 8.7/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.8/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 8.8/10 (Category avg: 9.2/10)
  • Security Automation: 8.7/10 (Category avg: 8.6/10)

Who Is the Company Behind Sumo Logic?

  • Seller: Sumo Logic
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Redwood City, CA
  • LinkedIn® Page: www.linkedin.com
    824 employees on LinkedIn®
  • Ownership: NASDAQ: SUMO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 38% Large

What Do G2 Reviewers Say About Sumo Logic?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use in Sumo Logic, enabling quick insights from data without complexity.
  • Users commend the powerful and accessible log management features of Sumo Logic, enhancing efficiency and visualization capabilities.
  • Users value the flexible analytics and powerful real-time features of Sumo Logic, enhancing collaboration and operational visibility.
  • Users value the real-time monitoring capabilities of Sumo Logic, enabling quick insights and effective data visualization.
  • Users value the powerful and accessible analytics of Sumo Logic, enhancing their data visualization and decision-making capabilities.
Cons
  • Users find the difficult learning curve of Sumo Logic challenging, especially transitioning from simpler tools.
  • Users face a steeper learning curve with Sumo Logic, especially when transitioning from tools like Splunk or Elastic.
  • Users note a steep learning curve with Sumo Logic that may challenge teams transitioning from other tools.
  • Users find Sumo Logic expensive, especially if data tiers are misconfigured, leading to unexpected high bills.
  • Users experience slow performance with Sumo Logic, facing delays and lag during queries, especially with large datasets.

What Are Recent G2 Reviews of Sumo Logic?

What Are G2 Users Discussing About Sumo Logic?

Coralogix

Coralogix is a modern, full-stack observability platform transforming how businesses process and understand their data. Our unique architecture powers in-stream analytics without reliance on indexing or hot storage. We specialize in comprehensive monitoring of logs, metrics, trace and security events, enhancing operational efficiency and reducing total cost of ownership by up to 70%. Coralogix stands out for its simple pricing model, based solely on data volume ingested and retained, and offers free, fast customer support with less than 30 second response time and 1 hour resolution time. Our platform covers the entire range of observability with features such as APM, RUM, SIEM, Kubernetes monitoring and more, all streamlined for quick integration and immediate value. Components within the stream store the system state to provide stateful insights and real-time alerting without ever needing to index the data — so there are never any trade-offs to achieve observability. Once ingested, parsed, and enriched, data is written remotely to an archive bucket controlled by the client. The archive can be queried directly at any time, from the platform UI or via CLI, giving users infinite retention with full control over, and access to, their data. View and query your data from any dashboard using any syntax. Coralogix has successfully completed relevant security and privacy compliances by BDO including GDPR, SOC 2, PCI, HIPAA, and ISO 27001/27701.

Average Rating: 4.5/5.0

Total Reviews: 461

How Do G2 Users Rate Coralogix?

  • Security Integration: 8.9/10 (Category avg: 8.6/10)
  • Activity Monitoring: 9.0/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Security Automation: 8.4/10 (Category avg: 8.6/10)

Who Is the Company Behind Coralogix?

  • Seller: Coralogix
  • Company Website:
  • Year Founded: 2014
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    609 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 57% Medium, 32% Large

What Do G2 Reviewers Say About Coralogix?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Coralogix, highlighting its simple setup and efficient integrations.
  • Users value the integration of logs, metrics, and alerts, enhancing efficiency in root-cause analysis and monitoring.
  • Users commend the exceptional customer support of Coralogix, ensuring quick resolutions and a smooth experience.
  • Users value the real-time monitoring of Coralogix, enhancing their understanding of user behavior and improving incident response.
  • Users value the intuitive user interface of Coralogix, appreciating its ease of log searching and export functionality.
Cons
  • Users find that the learning curve is steep for beginners, making navigation and understanding features challenging.
  • Users find the missing feature for downloading log results a significant limitation in Coralogix's functionality.
  • Users find the difficult learning curve of Coralogix challenging, especially for beginners navigating complex options.
  • Users experience slow performance with Coralogix, leading to frustration due to delayed log fetching and UI loading.
  • Users find the learning difficulty of Coralogix challenging, especially when navigating advanced features and the overwhelming UI.

What Are Recent G2 Reviews of Coralogix?

Blumira Automated Detection & Response

Blumira is an integrated security operations platform built for growing teams and the partners supporting them to gain complete visibility into their environment, identify and address risk faster, and deliver advanced security and compliance. The platform includes: - Managed Detections for automated threat hunting to identify attacks early - AI Investigation with 98.5% accurate, human-in-the-loop triage validated against real cases - Rapid Response with automation and 1-click actions to contain and block threats immediately - One Year of Data Retention with unlimited log ingestion to satisfy compliance requirements - Advanced Reporting and dashboards for forensics and easy investigation - Endpoint & Identity Protection (EDR/ITDR) for real-time remediation across devices and users - 24/7 Security Operations support for critical priority issues

Average Rating: 4.6/5.0

Total Reviews: 122

How Do G2 Users Rate Blumira Automated Detection & Response?

  • Security Integration: 8.9/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.8/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.2/10)
  • Security Automation: 8.8/10 (Category avg: 8.6/10)

Who Is the Company Behind Blumira Automated Detection & Response?

  • Seller: Blumira
  • Company Website:
  • Year Founded: 2018
  • HQ Location: Ann Arbor, Michigan
  • LinkedIn® Page: www.linkedin.com
    55 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: IT Manager
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 51% Medium, 36% Small

What Do G2 Reviewers Say About Blumira Automated Detection & Response?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Blumira, facilitating quick detection and monitoring of security incidents.
  • Users value the outstanding customer support of Blumira, highlighting swift assistance and a seamless onboarding experience.
  • Users appreciate the easy implementation of Blumira Automated Detection & Response, enabling quick and efficient setup processes.
  • Users value the real-time alerting feature of Blumira, enhancing their security awareness and incident management.
  • Users value the real-time alerting of Blumira, as it effectively tracks security events in their MS 365 environment.
Cons
  • Users feel that the limited customization options hinder the product's potential and integration capabilities with other tools.
  • Users find the alert system's customization lacking, highlighting a need for improved log source comparisons and SIEM functionality.
  • Users find the pricing model expensive and inflexible, not meeting their budget or needs effectively.
  • Users find the faulty detection limitations frustrating, especially around custom rules and log visibility.
  • Users find the inefficient alert system lacking essential user details, complicating response strategies and false positive management.

What Are Recent G2 Reviews of Blumira Automated Detection & Response?

What Are G2 Users Discussing About Blumira Automated Detection & Response?

FortiCNAPP

FortiCNAPP (formerly Lacework) is an AI-powered Cloud-Native Application Protection Platform that delivers unified security across your multi-cloud and hybrid environments. Built to protect the entire application lifecycle—from development to runtime—it combines posture management, workload protection, identity security, and threat detection into one integrated platform. By leveraging machine learning and behavioral analytics, FortiCNAPP helps security teams detect unknown threats, reduce noise, and accelerate response. Integrated with the Fortinet Security Fabric, it provides full-stack visibility across cloud, network, and endpoint environments—empowering teams to operate with confidence, reduce complexity, and scale securely.

Average Rating: 4.4/5.0

Total Reviews: 383

How Do G2 Users Rate FortiCNAPP?

  • Security Integration: 8.4/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.9/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Security Automation: 8.0/10 (Category avg: 8.6/10)

Who Is the Company Behind FortiCNAPP?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT
  • Total Revenue (USD mm): $2,594

Who Uses This Product?

  • Who Uses This: Security Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 62% Medium, 26% Large

What Do G2 Reviewers Say About FortiCNAPP?

AI-generated summary from verified user reviews

Pros
  • Users value the unified visibility of FortiCNAPP, streamlining cloud security and making monitoring efficient and effective.
  • Users value the effective vulnerability detection of FortiCNAPP, enhancing security and reducing false positives significantly.
  • Users value the effective alert management in FortiCNAPP, which significantly reduces false positives and enhances security monitoring.
  • Users appreciate the good visibility across cloud resources provided by FortiCNAPP, enhancing security and compliance management.
  • Users commend the ease of use of FortiCNAPP, appreciating its simple interface and smooth setup for efficient monitoring.
Cons
  • Users find the difficult setup of FortiCNAPP challenging, particularly without sufficient documentation and seasoned expertise.
  • Users find the poor documentation challenging, making onboarding and understanding the product's features quite difficult.
  • Users find the complex setup of FortiCNAPP challenging, particularly during initial configuration and onboarding processes.
  • Users find the setup difficulty of FortiCNAPP to be overwhelming and time-consuming, especially for newcomers.
  • Users find the complex configuration process daunting, especially without adequate documentation or cloud security expertise.

What Are Recent G2 Reviews of FortiCNAPP?

What Are G2 Users Discussing About FortiCNAPP?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated