Cloud Directory Services Resources
Articles, Discussions, and Reports to expand your knowledge on Cloud Directory Services
Resource pages are designed to give you a cross-section of information we have on specific categories. You'll find articles from our experts, discussions from users like you, and reports from industry data.
Cloud Directory Services Articles
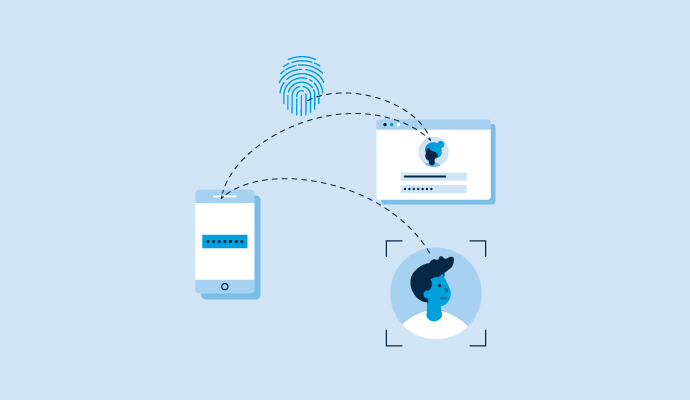
What Is Cloud Identity Management and Why It Is Important

Cloud Directory Services Discussions
To work out which cloud directory provider has the best security and compliance features for a healthcare organization that has strict access control requirements, I went past the marketing pages and filtered cloud directory services reviews down to reviewers in hospital and health care organizations. Interesting finding first: even healthcare reviewers rarely name HIPAA in their reviews. What they praise instead is the plumbing that makes strict access control livable day to day, which is probably the more useful signal anyway. What the healthcare-filtered set shows:
- Okta: One theme from healthcare reviewers is securely signing into shared workstations across offices with phone-based verification as the only way in, which is exactly the shared-terminal reality of clinical environments. Adaptive access that evaluates location and device per login shows up in reviews as well.
- Rippling IT: The deepest healthcare review base in this category's top products over the past year. Healthcare admins describe onboarding going from complicated and disorganized to nearly effortless, which matters for access control because rushed manual provisioning is where over-permissioning starts.
- JumpCloud: Healthcare reviewers echo the wider base: one point of control for MDM, SSO, and the user directory, reducing the tool sprawl of a hybrid workforce. Reviewers also note audit logs feeding compliance evidence collection, which auditors will ask for.
- AWS Directory Service: Amazon states SOC, PCI, HIPAA, and FedRAMP compliance for the service, a vendor claim worth validating in procurement. Its G2 review base is tiny at 17 reviews, so this one is here for architecture fit if your clinical workloads already run in AWS, not review depth.
- ManageEngine ADManager Plus: The vendor positions automated audit trails and access reviews supporting GDPR and HIPAA frameworks, and its reviewer base skews toward regulated industries like banking and government. Vendor claim on the frameworks, review-backed on the reporting strength.
For anyone running one of these in a healthcare setting, what did your last access audit actually flag? And is anyone enforcing different MFA rules for clinical versus back-office staff?
The HIPAA-in-reviews finding is surprising but makes sense, what healthcare IT actually needs day-to-day is "can I lock this shared workstation quickly," not a compliance certification on a slide.
Access audits tend to expose stale or overly broad permissions, so I’d want provisioning and offboarding to be tightly controlled. I’d also enforce different MFA policies for clinical and back-office staff since their devices and access patterns can be very different. Okta’s adaptive access approach sounds particularly useful for making those distinctions.
We run different MFA rules for clinical versus back-office staff, phone-based verification for shared clinical workstations and a stricter adaptive policy for admin accounts. Okta's adaptive access evaluating location and device per login made it straightforward to keep those two policies separate without maintaining two different systems.
The shared-workstation comments point to another healthcare-specific test: how quickly access disappears when someone changes roles, locations, or employment status. Strong authentication protects the login, but stale privileges can survive behind it. I’d want to test whether role changes propagate cleanly across connected clinical systems or whether access reviews still uncover accounts that should have been removed weeks earlier.
To work out which cloud directory provider has the best security and compliance features for a healthcare organization that has strict access control requirements, I went past the marketing pages and filtered cloud directory services reviews down to reviewers in hospital and health care organizations. Interesting finding first: even healthcare reviewers rarely name HIPAA in their reviews. What they praise instead is the plumbing that makes strict access control livable day to day, which is probably the more useful signal anyway. What the healthcare-filtered set shows:
- Okta: One theme from healthcare reviewers is securely signing into shared workstations across offices with phone-based verification as the only way in, which is exactly the shared-terminal reality of clinical environments. Adaptive access that evaluates location and device per login shows up in reviews as well.
- Rippling IT: The deepest healthcare review base in this category's top products over the past year. Healthcare admins describe onboarding going from complicated and disorganized to nearly effortless, which matters for access control because rushed manual provisioning is where over-permissioning starts.
- JumpCloud: Healthcare reviewers echo the wider base: one point of control for MDM, SSO, and the user directory, reducing the tool sprawl of a hybrid workforce. Reviewers also note audit logs feeding compliance evidence collection, which auditors will ask for.
- AWS Directory Service: Amazon states SOC, PCI, HIPAA, and FedRAMP compliance for the service, a vendor claim worth validating in procurement. Its G2 review base is tiny at 17 reviews, so this one is here for architecture fit if your clinical workloads already run in AWS, not review depth.
- ManageEngine ADManager Plus: The vendor positions automated audit trails and access reviews supporting GDPR and HIPAA frameworks, and its reviewer base skews toward regulated industries like banking and government. Vendor claim on the frameworks, review-backed on the reporting strength.
For anyone running one of these in a healthcare setting, what did your last access audit actually flag? And is anyone enforcing different MFA rules for clinical versus back-office staff?
The HIPAA-in-reviews finding is surprising but makes sense, what healthcare IT actually needs day-to-day is "can I lock this shared workstation quickly," not a compliance certification on a slide.
Access audits tend to expose stale or overly broad permissions, so I’d want provisioning and offboarding to be tightly controlled. I’d also enforce different MFA policies for clinical and back-office staff since their devices and access patterns can be very different. Okta’s adaptive access approach sounds particularly useful for making those distinctions.
We run different MFA rules for clinical versus back-office staff, phone-based verification for shared clinical workstations and a stricter adaptive policy for admin accounts. Okta's adaptive access evaluating location and device per login made it straightforward to keep those two policies separate without maintaining two different systems.
The shared-workstation comments point to another healthcare-specific test: how quickly access disappears when someone changes roles, locations, or employment status. Strong authentication protects the login, but stale privileges can survive behind it. I’d want to test whether role changes propagate cleanly across connected clinical systems or whether access reviews still uncover accounts that should have been removed weeks earlier.
Hey G2 community, what cloud directory services work best for replacing Active Directory and LDAP in a hybrid environment where some workloads are still on-premise? I have been collecting notes on this because it comes up constantly in cloud directory services research, and hybrid is where generic advice falls apart: the honest answer depends on whether you want to extend AD, replace it, or keep real AD but stop hosting it. Recent reviews split cleanly along those three paths:
- JumpCloud (4.5/5.0, 4,017 reviews): The replace path. The sentiment across reviews from smaller companies is that it delivers the best parts of AD without the downsides of an on-prem setup, and it ships cloud LDAP and RADIUS for the legacy pieces. The recurring warning in reviews is that the actual migration from traditional AD takes planning, with setup complexity the most cited pain.
- Microsoft Entra ID (4.5/5.0, 911 reviews): The extend path. Reviewers praise how it simplifies identity across cloud and hybrid environments, though some flag real friction migrating shared mailboxes and other AD objects, so the hybrid sync layer is where the work lives.
- Okta (4.5/5.0, 1,304 reviews): The unify-on-top path. Its on-premise identity repository support scores 9.4 against a category average of 8.7 on G2, and admins describe managing lifecycle across both cloud and on-prem applications with minimal end user friction.
- Managed Microsoft AD (4.4/5.0, 29 reviews): The keep-real-AD path, hosted by Google Cloud. Worth knowing about if applications genuinely require domain-joined AD, though the review base is small, so treat it as a shortlist candidate to validate rather than a review-backed verdict.
Which path did your team pick, and if you fully retired your domain controllers, how long did the last on-prem dependency actually take to die?
The three-path framing (extend, replace, or cloud-host real AD) is genuinely clarifying, most conversations about hybrid directory get stuck because the two people are describing different paths without realising it.
The three-paths framing is the most useful thing in this post, and I'd add that what decides the timeline is almost never the users, it's one stubborn dependency. Usually a file server whose permissions were built on nested groups nobody documented, a printer fleet doing Kerberos, or a single line-of-business app that only knows how to LDAP bind. Any one of those keeps a domain controller alive by itself, which is why the honest planning question is "which single thing can't move" rather than "how long is the migration." JumpCloud shipping cloud LDAP and RADIUS points straight at the app and network half of that list, which is often the difference between retiring the DC and keeping one running for one service.
JumpCloud is built for exactly this, unifying identity and device management to replace or bridge AD and LDAP in hybrid environments where some workloads are still on-prem.
For the unify-on-top path specifically, Okta's on-premise identity repository support scoring well above the category average is the detail I'd lean on. Managing lifecycle across cloud and on-prem apps with minimal friction is what you want if full replacement isn't realistic yet.