Best Cloud Detection and Response (CDR) Software - Page 2

How Many Cloud Detection and Response (CDR) Software Products Does G2 Track?

Total Products under this Category: 44

Category Stats (Nov 2026)

  • Average Rating: 4.58/5 (↓0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: UnderDefense MAXI (+0.43%) - Among all products in this category, UnderDefense MAXI recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Cloud Detection and Response (CDR) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 3,600+ Authentic Reviews
  • 44+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

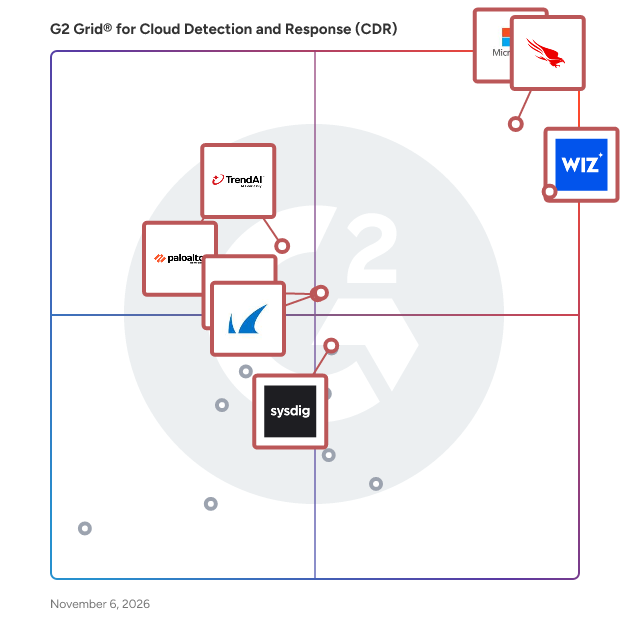
G2 Grid® for Cloud Detection and Response (CDR) Software

G2 Grid® for Cloud Detection and Response (CDR) Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security, Wiz, Cortex Cloud, TrendAI Vision One, Barracuda Managed XDR, Arctic Wolf, and Sysdig Secure.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-detection-and-response-cdr/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=wiz-wiz&focus%5B%5D=cortex-cloud&focus%5B%5D=trendai-vision-one&focus%5B%5D=barracuda-managed-xdr&focus%5B%5D=arctic-wolf&focus%5B%5D=sysdig-sysdig-secure)

Plerion

Plerion is a cloud security platform designed to assist organizations in managing and mitigating risks within their cloud environments. Unlike traditional security tools that inundate users with alerts, Plerion focuses on actionable insights, enabling teams to address vulnerabilities effectively. By streamlining the risk management process, Plerion transforms the way organizations approach cloud security, ensuring that the most critical threats are prioritized and resolved. The platform is tailored for IT security teams and cloud administrators across various industries that utilize cloud services such as AWS, Azure, and Google Cloud Platform (GCP). Plerion’s unique approach allows users to visualize their cloud infrastructure, identities, workloads, and code as a cohesive graph. This visualization helps users identify the approximately 1% of risks that are genuinely exploitable, eliminating the noise typically associated with security alerts. By presenting a concise, ranked list of vulnerabilities, Plerion empowers teams to focus their efforts where they matter most. At the heart of the Plerion platform is Pleri, an AI-driven cloud security engineer that mimics the investigative capabilities of a human security expert. Pleri assesses findings, verifies their exploitability in context, and traces risks back to the underlying code responsible for them. This automated process culminates in the creation of pull requests or Jira tickets for remediation, ensuring that every proposed change awaits human approval. This feature not only enhances accountability through full audit trails but also allows for easy rollbacks if necessary. Plerion’s comprehensive coverage includes cloud configuration, workloads, identity and permissions, data, code, and AI workloads, making it a versatile solution for diverse cloud environments. The platform also offers compliance mapping against a wide range of frameworks, linking each identified failure to specific corrective actions rather than merely generating reports. This capability significantly reduces the time and effort required for compliance management. Organizations using Plerion have reported substantial improvements in their security operations. For instance, Deputy achieved an 80% reduction in alerts and decreased their time-to-remediation from 30 days to just 4 hours. Similarly, Basis eliminated 40 hours of manual review each week, illustrating the platform's efficiency. With ISO 27001 certification, SOC 2 attestation, and the AWS Security Software Competency, Plerion ensures a high standard of security and reliability. By deploying in minutes rather than months, Plerion allows organizations to put their cloud security on autopilot while maintaining a human touch in the decision-making process.

Average Rating: 4.7/5.0

Total Reviews: 32

How Do G2 Users Rate Plerion?

  • Ease of Admin: 9.0/10 (Category avg: 8.9/10)
  • Ease of Use: 8.9/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.6/10 (Category avg: 9.3/10)
  • Quality of Support: 9.7/10 (Category avg: 9.2/10)

Who Is the Company Behind Plerion?

  • Seller: Plerion
  • Company Website:
  • Year Founded: 2021
  • HQ Location: Sydney, AU
  • LinkedIn® Page: www.linkedin.com
    30 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Financial Services
  • Company Size: 52% Medium, 36% Small

What Do G2 Reviewers Say About Plerion?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the centralized security data in Plerion, which enhances visibility and effective risk management.
  • Users appreciate the ease of use of Pleri, enhancing collaboration and simplifying cloud security management seamlessly.
  • Users commend Plerion's stellar customer support, highlighting responsiveness and commitment to customer success in security management.
  • Users appreciate the centralized security data of Plerion, benefiting from immediate visibility and actionable advice.
  • Users appreciate how Plerion's effective prioritization simplifies cloud security, focusing on critical issues without overwhelming alerts.
Cons
  • Users feel that improvements are needed in trend reporting and Jira ticket creation for better long-term value visibility.
  • Users note that while Plerion shows improvement needed in trend reporting and ongoing value visibility over time.
  • Users find the missing features of Plerion frustrating, particularly regarding customization and cloud support limitations.
  • Users note the limited support for Google Cloud, wishing for better feature parity with other providers.
  • Users experience integration issues due to manual updates and limited coverage, creating deployment challenges with Plerion.

What Are Recent G2 Reviews of Plerion?

ExtraHop

ExtraHop is the cybersecurity partner enterprises trust to reveal cyber risk and build business resilience. The ExtraHop RevealX platform for network detection and response and network performance management uniquely delivers the instant visibility and unparalleled decryption capabilities organizations need to expose the cyber risks and performance issues that other tools can’t see. When organizations have full network transparency with ExtraHop, they can investigate smarter, stop threats faster, and keep operations running. RevealX deploys on premises or in the cloud. It addresses the following use cases: - Ransomware - Zero trust - Software supply chain attacks - Lateral movement and C2 communication - Security hygiene - Network and Application Performance Management - IDS - Forensics and more A few of our differentiators: Continuous and on-demand PCAP: Full packet processing is superior to NetFlow and yields higher quality detections. Strategic decryption across a variety of protocols, including SSL/TLS, MS-RPC, WinRM, and SMBv3, gives you better visibility into early-stage threats hiding in encrypted traffic as they attempt to move laterally across your network. Protocol coverage: RevealX decodes more than 70 network protocols. Cloud-scale machine learning: Rather than relying on limited "on-box" compute power for analysis and detections, RevealX uses sophisticated cloud-hosted and cloud-scale machine learning workloads to identify suspicious behavior in real time and create high-fidelity alerts. ExtraHop was named a Leader in The Forrester Wave™: Network Analysis and Visibility, Q2 2023. Key Technology Integration and Go-to-Market Partners: CrowdStrike: RevealX integrates with CrowdStrike Falcon® LogScale, Falcon Insight XDR, Falcon Threat Graph, and Falcon Intelligence. Splunk SOAR AWS Google Cloud Security Founded in 2007, ExtraHop is privately held and headquartered in Seattle, Wash. To learn more, visit www.extrahop.com.

Average Rating: 4.6/5.0

Total Reviews: 68

How Do G2 Users Rate ExtraHop?

  • Ease of Admin: 9.0/10 (Category avg: 8.9/10)
  • Ease of Use: 8.6/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Quality of Support: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind ExtraHop?

Who Uses This Product?

  • Top Industries: Hospital & Health Care, Transportation/Trucking/Railroad
  • Company Size: 69% Large, 26% Medium

What Do G2 Reviewers Say About ExtraHop?

AI-generated summary from verified user reviews

Pros
  • Users value the all-in-one solution of ExtraHop, ensuring complete network visibility and excellent customer support.
  • Users value comprehensive monitoring with ExtraHop, enjoying complete visibility and anomaly detection across their network traffic.
  • Users value the easy deployment of ExtraHop, simplifying setup on both physical and virtual networks.
  • Users appreciate the responsive support from ExtraHop's knowledgeable Customer Success teams, enhancing overall satisfaction and experience.

What Are Recent G2 Reviews of ExtraHop?

What Are G2 Users Discussing About ExtraHop?

ARMO Platform

ARMO Platform is the only runtime-driven, open-source first, cloud security platform. It is the only security platform that continuously minimizes cloud attack surface based on runtime insights, while actively detecting and responding to cyberattacks with real risk context. Using an eBPF-based runtime sensor to record application behavior and related activities, ARMO Platform enables DevOps, security, and platform teams to eliminate the security noise and go from thousands of irrelevant alerts to focus on the most important and exploitable threats. This allows those teams to shift from managing hypothetical security issues to mitigating actual risks and providing them with the means to remediate them. ARMO is an open-source-driven company and the creator of Kubescape, a leading open-source Kubernetes security project, now an official CNCF project. To learn more about ARMO Platform please visit: https://www.armosec.io/

Average Rating: 4.5/5.0

Total Reviews: 44

How Do G2 Users Rate ARMO Platform?

  • Ease of Admin: 8.9/10 (Category avg: 8.9/10)
  • Ease of Use: 8.8/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.3/10)
  • Quality of Support: 9.3/10 (Category avg: 9.2/10)

Who Is the Company Behind ARMO Platform?

  • Seller: ARMO
  • Year Founded: 2019
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    103 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 59% Small, 36% Medium

What Do G2 Reviewers Say About ARMO Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of ARMO Platform, as it simplifies security operations and streamlines workflows.
  • Users commend ARMO Platform for its superior security capabilities, enhancing the protection of Kubernetes application clusters significantly.
  • Users value the robust automation and integration capabilities of ARMO Platform, enhancing security and efficiency in Kubernetes environments.
  • Users commend ARMO Platform for its superior vulnerability detection, simplifying compliance and enhancing Kubernetes security effortlessly.
  • Users commend the comprehensive security features of ARMO Platform, enhancing Kubernetes application safety and compliance effortlessly.
Cons
  • Users highlight the steep learning curve of the ARMO Platform, particularly for those less familiar with Kubernetes.
  • Users report integration issues with ARMO Platform that lead to disruptions and confusion during project workflows.
  • Users find the difficult learning curve of ARMO Platform challenging, especially those less experienced with Kubernetes.
  • Users note the limited third-party integrations of ARMO Platform, impacting its overall functionality and incident response efficiency.
  • Users often experience missing features like upload issues and outdated updates, impacting workflow and causing confusion.

What Are Recent G2 Reviews of ARMO Platform?

What Are G2 Users Discussing About ARMO Platform?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Tracebit

Tracebit automatically deploys security canaries across your cloud accounts, endpoints, SaaS applications, and CI/CD pipelines at scale. When attackers touch them, you know immediately. Security canaries are decoy resources and credentials that blend into your environment. They reveal attackers as they move laterally, escalate privileges, or access credentials. Tracebit supports AWS, Azure, Google Cloud, Kubernetes, identity systems, workstations, and developer pipelines. Security teams deploy in 30 minutes using infrastructure-as-code. Tracebit analyzes your environment and recommends canaries that match your naming conventions and resource types, then manages them as your environment evolves. No agents to maintain. No servers to patch. When canaries trigger, you get high-fidelity alerts with forensic context: which principal accessed what resource, from which IP address, using what user agent, and at what time. Alerts integrate with your existing security workflows so your team can investigate and respond. Canaries detect attackers; they do not prevent every breach. Tracebit makes deception technology practical to deploy and maintain, giving security teams detection that works from day one.

Average Rating: 4.6/5.0

Total Reviews: 17

How Do G2 Users Rate Tracebit?

  • Ease of Admin: 9.4/10 (Category avg: 8.9/10)
  • Ease of Use: 8.8/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 9.4/10 (Category avg: 9.2/10)

Who Is the Company Behind Tracebit?

  • Seller: Tracebit
  • Year Founded: 2022
  • HQ Location: London, GB
  • LinkedIn® Page: www.linkedin.com
    44 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 65% Medium, 24% Small

What Do G2 Reviewers Say About Tracebit?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the continuous monitoring of Tracebit, ensuring resource safety and rapid response to unusual activities.
  • Users commend the quick issue resolution and feature-rich capabilities of Tracebit, ensuring resource safety and seamless integration.
  • Users praise Tracebit for its seamless integrations and quick feature implementation, enhancing security and efficiency.
  • Users value the enhanced security features of Tracebit, ensuring real-time monitoring and protection against unusual activities.
  • Users value the real-time alerts from Tracebit, ensuring quick responses to potential security threats across multiple accounts.
Cons
  • Users find the confusing interface of Tracebit challenging, hindering smooth navigation essential for a security tool.
  • Users find the difficult navigation of Tracebit's layout cluttered, impacting their experience, especially for a security tool.
  • Users face false positives in alerts that require manual review, adding to their workload and complicating the experience.
  • Users feel that Tracebit's limited feature set may not meet the needs of larger enterprise customers.
  • Users find the high learning curve for initial setup of Tracebit challenging, especially for new users.

What Are Recent G2 Reviews of Tracebit?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 48

How Do G2 Users Rate Darktrace / HYBRID NETWORK?

  • Ease of Admin: 7.7/10 (Category avg: 8.9/10)
  • Ease of Use: 7.9/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.3/10)
  • Quality of Support: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®
  • Ownership: LON: DARK

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 61% Medium, 29% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users value the robust monitoring capabilities of Darktrace, which ensures thorough visibility and confidence in security coverage.
  • Users appreciate the self-learning AI technology of Darktrace, providing real-time monitoring and exceptional threat detection capabilities.
  • Users value the rapid and accurate threat detection of Darktrace, allowing for seamless integration and robust security.
  • Users appreciate the responsive customer support of Darktrace, enhancing their learning experience and overall platform usability.
  • Users appreciate the autonomous AI capabilities of Darktrace, effectively detecting and responding to evolving cyber threats in real-time.
Cons
  • Users experience a significant initial learning curve with Darktrace, requiring time to adjust to complex features and alerts.
  • Users find the product expensive, particularly affecting smaller organizations and their security budgets significantly.
  • Users experience alert issues with Darktrace, facing numerous notifications during initial setup, requiring extensive manual tuning.
  • Users find the complex setup of Darktrace challenging, requiring extensive engineering skills for effective management.
  • Some users experience false positives, necessitating IT intervention to restore services and improve detection capabilities.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

AccuKnox

AccuKnox Zero Trust CNAPP cloud security protects public and private clouds, Kubernetes and VMs. AccuKnox is a AI-powered Zero Trust Cloud Native Security Platform that helps organizations comply with various frameworks and over 33+ compliance controls, including MITRE, NIST, STIG, CIS, PCI-DSS, GDPR, and SOC2. AccuKnox enhances InfraSec and DevSecOps teams by enabling them to detect, prioritize, prevent and protect against advanced and sophisticated cloud attacks. Key Benefits 1. Code to Cloud Security 2. Easy Deployment 3. Extensive Coverage. 4. Preemptive Attack Mitigation 5. Open Source and Innovative Key Differentiators - Inline Preemptive Security (as opposed to Post-attack mitigation) - Secures modern workloads (Kubernetes) and traditional workloads (VMs) - Multi-Cloud, Private, Air-gapped, and Hybrid Cloud Security - IaC – Infrastructure As Code scanning - Secures AI/ML workloads like Jupyter Notebooks Features - Automated Zero Trust Cloud Security (Public, Private, Hybrid, Air-gapped) - Vulnerability Management & Prioritization - Run-time security, Micro-segmentation - Application Firewalling, Kernel Hardening - Drift Detection & Audit Trail - Continuous Diagnostics & Mitigation - GRC – CIS, HIPAA, GDPR, SOC2, STIG, MITRE, NIST - Securing Mission-Critical Workloads like Vault - Securing AI workbenches like Jupyter Notebooks - Cryptojacking and TNTBotinger Attacks With over 15+ patents, we're proud to offer an OpenSource, DevSecOps-led delivery model. To top it off, we have an ongoing R&D partnership with the esteemed SRI International. We deliver both Static and Runtime Security, anchored on innovations in Cloud Security and AI/ML-based Anomaly Detection. Static Code Analysis - Deeply analyze your code for vulnerabilities and weaknesses. CI/CD Pipelines Scanning - Continuously scan your pipelines for security flaws and risks. Container Security - Fortify your containers with robust security measures. Kubernetes Orchestration - Seamlessly manage and secure your Kubernetes environments. Secret Scanning - Detect and protect sensitive information from unauthorized access.

Average Rating: 4.4/5.0

Total Reviews: 12

How Do G2 Users Rate AccuKnox?

  • Ease of Admin: 8.3/10 (Category avg: 8.9/10)
  • Ease of Use: 7.6/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 8.9/10 (Category avg: 9.3/10)
  • Quality of Support: 8.1/10 (Category avg: 9.2/10)

Who Is the Company Behind AccuKnox?

  • Seller: Accuknox
  • Year Founded: 2020
  • HQ Location: California, USA
  • LinkedIn® Page: www.linkedin.com
    197 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 46% Large, 31% Medium

What Do G2 Reviewers Say About AccuKnox?

AI-generated summary from verified user reviews

Pros
  • Users praise the comprehensive security of AccuKnox, noting its robustness and customer-focused solutions for cloud management.
  • Users highlight the high security level of AccuKnox, ensuring comprehensive protection for cloud environments and applications.
  • Users value the easy cloud integration of AccuKnox, enhancing security for applications and maintaining compliance effortlessly.
  • Users value the continuous compliance capabilities of AccuKnox, ensuring robust security for cloud workloads and seamless integration.
  • Users praise the excellent customer support of AccuKnox for their quick responses and in-depth technical knowledge.
Cons
  • Users find the difficult learning curve of AccuKnox challenging, especially with its complex setup and Kubernetes requirements.
  • Users find the complex setup of AccuKnox challenging, particularly those with limited security expertise.
  • Users find AccuKnox to be cost prohibitive, which limits its accessibility for many potential users.
  • Users note the slow customer support, often requiring multiple follow-ups for assistance and troubleshooting.
  • Users find the complex setup and management of AccuKnox challenging, particularly for those lacking security expertise.

What Are Recent G2 Reviews of AccuKnox?

Sonrai Security

Sonrai Security is a leading cloud privileged access management solutions provider. With a mission to empower enterprises of all sizes to innovate securely and confidently, Sonrai Security delivers identity, access, and privilege security for companies running on AWS, Azure, and Google Cloud platforms. The company is renowned for pioneering the Cloud Permissions Firewall, enabling one-click least privilege while supporting developer access needs without disruption. Trusted by Cloud Operations, Development, and Security Teams at leading companies across various industries, Sonrai Security is committed to driving innovation and excellence in cloud security. Sonrai’s Cloud Permissions Firewall, the leading cloud PAM solution, gets cloud access under control, slashes the privileged attack surface, and automates least privilege all without impeding DevOps. The Cloud Permissions Firewall uses privileged permission intelligence and usage monitoring to determine who needs what permissions in your cloud. Then, with one-click, it eliminates all unused sensitive privileges across your entire multi-cloud estate. Just-in-time access and exceptions are granted to roles on the fly as new needs come up so development goes uninterrupted. SecOps teams spend 97% less time achieving least privilege and slash the attack surface by 92%.

Average Rating: 4.5/5.0

Total Reviews: 26

How Do G2 Users Rate Sonrai Security?

  • Ease of Admin: 8.3/10 (Category avg: 8.9/10)
  • Ease of Use: 8.6/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Quality of Support: 9.1/10 (Category avg: 9.2/10)

Who Is the Company Behind Sonrai Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 42% Medium, 38% Large

What Do G2 Reviewers Say About Sonrai Security?

AI-generated summary from verified user reviews

Pros
  • Users value the speed and simplicity of Sonrai Security's Cloud Permissions Firewall in enhancing cloud IAM effectiveness.
  • Users are impressed with Sonrai Security’s effective enforcement of permission controls that enhance cloud security management.
  • Users value the speed and simplicity of Sonrai Security's Cloud Management, achieving immediate results with minimal effort.
  • Users commend the ease of use of Sonrai Security, appreciating its quick setup and intuitive interface.
  • Users highlight the effective cloud security of Sonrai Security, enhancing identity and data governance effortlessly.
Cons
  • Users note a complexity in setup with Sonrai Security, requiring significant tuning and configuration for optimal results.
  • Users find the pricing of Sonrai Security to be high, particularly challenging for smaller businesses and teams.
  • Users express concerns about feature limitations, including complexity and manual intervention, hindering their overall experience.
  • Users find the software's complexity and limited features hinder usability and require significant tuning for effectiveness.
  • Users express frustration with the limited options for dashboard customization, hindering their overall experience with Sonrai Security.

What Are Recent G2 Reviews of Sonrai Security?

Darktrace / EMAIL

Darktrace / EMAIL secures email and collaboration by training exclusively on each organization’s own communication patterns, not shared threat intelligence. It builds a Unique Behavioral Profile for every user – spanning email, identity, DLP, and human risk – to catch novel phishing, business email compromise, and account takeover that signature-based tools miss by design. It’s recognized as a Leader in Gartner’s Magic Quadrant and in the 2025 Voice of the Customer for Email Security Platforms. Traditional secure email gateways and native protections rely on known threat intelligence, so they need a first victim before they can catch a new attack – and generative AI has only widened that gap. Darktrace / EMAIL takes a different approach: it uses Adaptive AI to build a Unique Behavioral Profile for every user, then detects deviations across inbound, outbound, and lateral mail and responds with precise, autonomous action. Key capabilities include: - Adaptive Email Security: Builds a Unique Behavioral Profile for every user across the full mail flow – inbound, outbound, and lateral protection, DMARC management, account takeover detection, data loss detection, and AI attack/GenAI visibility. Darktrace catches on average 17% of threats that leading SEGs miss on arrival. - Identity Detect & Respond: Adds autonomous response to account takeover – session termination and forced re-authentication – plus recovery and audit across email, SaaS, and cloud. - Email DLP & Collaboration Security: Suspicious emails are automatically quarantined, links are rewritten, and attachments are removed, extending detection with hold, redirect, and strip-sensitive-content response actions plus dedicated behavioral coverage across Microsoft Teams, Zoom, and Slack, all without interrupting legitimate business communication. - Adaptive Security Awareness Training: Personalizes training, phishing simulations, and just-in-time coaching to each employee’s actual behavior, with outcomes feeding back into the detection model to close the loop. For security teams, Darktrace / EMAIL reduces operational overhead by automating triage and response. Its Cyber AI Analyst provides contextual insights, while end-users benefit from clear, in-app narratives that explain why a message is suspicious – helping to reduce false phishing reports and improve awareness. Benefits for organizations include: - Coverage across email, collaboration, and SaaS platforms in one behavioral model. - Up to 90% less time spent triaging alerts, so security teams spend more time on higher-value work. - Native integration with Microsoft 365, Exchange, and Google Workspace that doesn’t disrupt mail flow. Darktrace / EMAIL is a Gartner Leader in both the Magic Quadrant and the 2025 Voice of the Customer for Email Security Platforms – recognition that tracks with what it actually catches: threats built for a specific business, not just known attack patterns.

Average Rating: 4.2/5.0

Total Reviews: 42

How Do G2 Users Rate Darktrace / EMAIL?

  • Ease of Admin: 8.1/10 (Category avg: 8.9/10)
  • Ease of Use: 8.2/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.3/10 (Category avg: 9.3/10)
  • Quality of Support: 8.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Darktrace / EMAIL?

  • Seller: Darktrace
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®
  • Ownership: LON: DARK

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 58% Medium, 33% Large

What Do G2 Reviewers Say About Darktrace / EMAIL?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the adaptive AI detection of Darktrace, making security management seamless and effective.
  • Users appreciate the excellent customer support provided by Darktrace, enhancing their experience and ensuring quick assistance.
  • Users appreciate the high detection efficiency of Darktrace EMAIL, ensuring minimal malicious emails slip through.
  • Users commend the superior product quality of Darktrace, benefiting from reliable security and excellent support services.
  • Users highlight the reliability of Darktrace EMAIL, offering confidence in email account protection and malicious detection.
Cons
  • Users note that Darktrace / EMAIL is expensive, though they acknowledge its value justifies the cost.
  • Users experience poor integration with Darktrace, particularly with Outlook on Windows and Mac, affecting usability.
  • Users find the complexity of the wording and descriptions challenging, requiring specialized IT knowledge for effective use.
  • Users experience false positives as emails are often blocked, but they can easily release and whitelist them.
  • Users find the regular software updates to be tedious and detracting from the overall experience of Darktrace / EMAIL.

What Are Recent G2 Reviews of Darktrace / EMAIL?

Uptycs

Uptycs unified CNAPP and XDR platform is a comprehensive security solution designed to protect the full spectrum of modern attack surfaces in your cloud, data centers, user devices, build pipelines, and containers. With a strong focus on DevSecOps, Uptycs offers a powerful combination of CNAPP capabilities, including Cloud Workload Protection Platform (CWPP), Kubernetes Security Posture Management (KSPM), Cloud Security Posture Management (CSPM), Cloud Infrastructure Entitlement Management (CIEM), and Cloud Detection and Response (CDR). With Uptycs you also get industry-leading eXtended Detection and Response (XDR) across macOS, Windows, and Linux endpoints, ensuring comprehensive protection, detection, and investigation. Uptycs delivers real-time threat detection, context-rich alerts, and maps detections to the MITRE ATT&CK framework for improved security insights. Uptycs performs scanning of containers for vulnerabilities throughout the CI/CD pipeline, promoting agile DevOps workflows, and reducing risk in production environments. Uptycs seamlessly integrates with existing tools and processes, streamlining operations and improving overall efficiency. Customers also benefit from the flexibility to choose between agent-based and agentless scanning options tailored to their unique cloud workload needs. Discover how Uptycs can transform your security posture with a comprehensive, flexible, and powerful security solution designed to meet the needs of today's complex and rapidly evolving cloud environments. Shift up with Uptycs. KEY DIFFERENTIATORS: 1. Unified & Comprehensive Platform: Uptycs offers a holistic security solution with CNAPP capabilities (CWPP, KSPM, CSPM, CIEM, and CDR) across data centers, laptops, build pipelines, containers, and cloud environments, reducing tool sprawl. 2. Advanced XDR: Industry-leading eXtended Detection and Response for endpoint protection across macOS, Windows, and Linux systems. 3. DevSecOps Focus: Enhanced security for container-based workloads and Kubernetes, supporting agile DevOps workflows. 4. Real-Time Threat Detection: Context-rich alerts and threat detection mapped to the MITRE ATT&CK framework for improved insights. 5. CI/CD Integration: Efficiently scan containers for vulnerabilities throughout the CI/CD pipeline, reducing risk in production. 6. Both agent-based and agentless scanning. Deploy agentless scanning for rapid, friction-free coverage to keep your data secure, and gain continuous runtime security, real-time investigations, and remediation with agent-based telemetry. 7. Rich API & Compatibility: Seamless integration with existing security tools and platforms, powered by osquery for broad compatibility. 8. Expert Support & Flexibility: Dedicated support from security experts and the best of both worlds with agent-based and agentless scanning options tailored to your needs.

Average Rating: 4.4/5.0

Total Reviews: 13

How Do G2 Users Rate Uptycs?

  • Ease of Admin: 8.3/10 (Category avg: 8.9/10)
  • Ease of Use: 7.9/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Uptycs?

  • Seller: Uptycs
  • Year Founded: 2016
  • HQ Location: Waltham, US
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 54% Medium, 38% Large

What Do G2 Reviewers Say About Uptycs?

AI-generated summary from verified user reviews

Pros
  • Users value the comparative analysis feature of Uptycs, aiding in selecting the best cloud security tools.
  • Users value the comparative analysis feature of Uptycs, aiding in selecting the best cloud security tools.
  • Users value the comparative analysis feature of Uptycs, which aids in choosing the best cloud security tools.
  • Users value Uptycs for its excellent compliance with CIS and PCI DSS standards, enhancing security monitoring capabilities.
  • Users value the strong compliance with standards like CIS and PCI DSS, enhancing security monitoring capabilities.
Cons
  • Users find the high fees regrettable, as it limits their willingness to continue using Uptycs.
  • Users express concern over the high pricing of Uptycs, which deters continued use of the tool.

What Are Recent G2 Reviews of Uptycs?

CloudFence

CloudFence monitors your cloud network like an invisible overhead drone. It studies the normal patterns of how workloads and non-human identities behave, who they talk to, where they send data, what access they actually use, and immediately alerts the moment one starts behaving in an unfamiliar way, blocking suspicious activity before it escalates into an attack. CloudFence then uses the learned behavior to help you scope down wide-open and unused IAM and Security Group access to what's actually needed — without the risk of blocking legitimate access.

Average Rating: 5.0/5.0

Total Reviews: 3

How Do G2 Users Rate CloudFence?

  • Ease of Admin: 9.2/10 (Category avg: 8.9/10)
  • Ease of Use: 8.3/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind CloudFence?

Who Uses This Product?

  • Company Size: 67% Medium, 33% Small

What Are Recent G2 Reviews of CloudFence?

Open XDR Security Operations Platform

The Stellar Cyber Open XDR platform delivers comprehensive, unified security without complexity, empowering lean security teams of any skill to successfully secure their environments. With Stellar Cyber, organizations reduce risk with early and precise identification and remediation of threats while slashing costs, retaining investments in existing tools, and improving analyst productivity, delivering an 8x improvement in MTTD and a 20x improvement in MTTR. The company is based in Silicon Valley. For more information, visit stellarcyber.ai.

Average Rating: 4.9/5.0

Total Reviews: 8

How Do G2 Users Rate Open XDR Security Operations Platform?

  • Ease of Admin: 9.7/10 (Category avg: 8.9/10)
  • Ease of Use: 9.7/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.3/10)
  • Quality of Support: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Open XDR Security Operations Platform?

  • Seller: STELLAR CYBER
  • Year Founded: 2017
  • HQ Location: San Jose, California, United States
  • LinkedIn® Page: www.linkedin.com
    150 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 25% Large

What Do G2 Reviewers Say About Open XDR Security Operations Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the seamless integrations of Open XDR, enhancing efficiency by unifying different security vendors' tools in one platform.
  • Users appreciate the easy integrations of Open XDR, enhancing threat detection without overhauling existing security systems.
  • Users value the comprehensive visibility provided by Open XDR, enabling a unified view of all security data sources.
  • Users value the effective threat detection capabilities of Open XDR, enhancing accuracy and reducing alert fatigue significantly.
  • Users appreciate the AI automation in Open XDR, enhancing threat detection speed and reducing alert fatigue significantly.
Cons
  • Users find the integration issues time-consuming, especially when connecting multiple tools or newly emerging solutions.
  • Users experience alerting issues that complicate operations, creating challenges with notifications and bulk assignments.
  • Users encounter troublesome alert management issues in Open XDR, leading to inefficiencies and increased workload during assignments.
  • Users face false positives that complicate alert management, creating unnecessary noise and impacting analyst efficiency.
  • Users face an inefficient alert system plagued by bugs, causing troubles with alerts during bulk assignments.

What Are Recent G2 Reviews of Open XDR Security Operations Platform?

Araali Network Security Pro

Araali Networks allows lean security teams to discover their exposure - data, services, and backdoors and prioritize the top 1% of risks that really matter. The security team can use cloud-native controls or Araali's ebpf firewall to create compensating controls to neutralize these risks. In addition, Araali is introducing a new feature that allows teams to patch their CVEs, automatically using Araali - this is a game changer as it allows team to knock off 90% of critical CVEs with little effort. Coverage: VMs, Containers, and Kubernetes across the public and private clouds. How: Araali automatically discovers your apps, their networking, access privileges, and security risks. It also creates and maintains the least privilege policies for all the apps. Your teams can enforce explicit policies for “who can do what” in your virtual private cloud, blocking malicious code from establishing a backdoor or accessing your services. Araali's customers include cloud-native startups, mid-market enterprises, and government agencies. To learn more visit www.araalinetworks.com or create a free trial account by signing up on console.araalinetworks.com Use Cases: 1) SOC-2 compliance: IDS/IPS, vulnerability management, asset management, vulnerability compensation controls, app access control for 2) Egress Filtering: Monitor and control egress to third-party sites, backdoors, supply chain attacks, and ransomware 3) Risk Prioritization: Visibility into the runtime - apps and associated risks 4) Vulnerability Management and Vulnerability Shielding: prevent vuln from getting exploited - especially useful for zero-day or cases where patches are not available as seen in Log4j 5) Enforcement: Proactively or Reactively Neutralize Threats to stop them from moving laterally and exfiltrating your data.

Average Rating: 4.3/5.0

Total Reviews: 3

How Do G2 Users Rate Araali Network Security Pro?

  • Ease of Use: 7.5/10 (Category avg: 8.6/10)
  • Quality of Support: 9.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Araali Network Security Pro?

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Do G2 Reviewers Say About Araali Network Security Pro?

AI-generated summary from verified user reviews

Pros
  • Users value the precision on threats in Araali Network Security Pro, enhancing their ability to address zero-day vulnerabilities effectively.
  • Users value the seamless API integration that enhances threat precision and mitigates zero-day vulnerabilities effectively.
  • Users value the detection efficiency of Araali Network Security Pro, effectively identifying and mitigating emerging zero-day vulnerabilities.
  • Users value the seamless integrations of Araali Network Security Pro, enhancing threat detection and mitigation efforts.
  • Users value the seamless integration and precise threat identification of Araali Network Security Pro, enhancing overall security posture.
Cons
  • Users find that complex coding complicates network integration and delays security alerts, hindering timely incident response.
  • Users find delayed detection of security alerts challenging, particularly with complex network setups, hampering incident response times.
  • Users experience ineffective alerts, leading to delays in incident response due to complex network infrastructure.
  • Users experience inefficient alert system, leading to delays in incident response due to complex network setups.
  • Users face network issues with Araali Network Security Pro, experiencing delays in security alerts and incident response.

What Are Recent G2 Reviews of Araali Network Security Pro?

Foresite Catalyst

Foresite Catalyst is MXDR for Google Cloud: managed detection and response (MDR) built on Google SecOps and Gemini Enterprise. Foresite is the 2026 Google Cloud Security Partner of the Year for North America. We deliver the Agentic SOC as a fully managed outcome. Autonomous agents triage and investigate at machine speed, and a named Foresite practitioner authorizes every high-impact action before it executes. Agentic never means uncontrolled. Catalyst monitors your networks, endpoints, cloud workloads, and identities 24/7, detecting, investigating, and resolving threats on your behalf. Every decision is logged in a fully auditable reasoning chain. We call this the Glass Box, not the black box: full visibility into every action we take in your environment, with shared channels and joint investigation alongside your team. Catalyst delivers: - 24/7 managed detection and response on Google SecOps - Agentic triage, investigation, and evidence-backed response with named-practitioner authorization - Threat intelligence and hunting powered by Google and Mandiant - Cloud security, managed compliance, continuous compliance monitoring, and vCISO - AI workload protection Foresite’s professional services practice accelerates Google SecOps deployments and migrations from legacy SIEM platforms including Splunk, Microsoft Sentinel, and QRadar. A complementary Wiz practice extends coverage to cloud-native application protection. Catalyst serves enterprise and public sector organizations across technology, financial services, healthcare, government, retail, and manufacturing.

Average Rating: 4.3/5.0

Total Reviews: 2

How Do G2 Users Rate Foresite Catalyst?

  • Ease of Admin: 10.0/10 (Category avg: 8.9/10)
  • Ease of Use: 8.3/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.3/10)
  • Quality of Support: 8.3/10 (Category avg: 9.2/10)

Who Is the Company Behind Foresite Catalyst?

  • Seller: Foresite
  • Year Founded: 2013
  • HQ Location: Overland Park, US
  • LinkedIn® Page: www.linkedin.com
    120 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of Foresite Catalyst?

ReliaQuest GreyMatter

ReliaQuest’s agentic AI security operations platform, GreyMatter, allows security teams to detect threats at the source, contain them in under 5 minutes, and eliminate Tier 1 and Tier 2 work for faster investigation and response. GreyMatter orchestrates 6 agentic AI personas with 200+ agent skills and 400+ AI tools to exponentially scale security operations and help organizations predict what's next.

Average Rating: 4.7/5.0

Total Reviews: 20

How Do G2 Users Rate ReliaQuest GreyMatter?

  • Ease of Admin: 8.8/10 (Category avg: 8.9/10)
  • Ease of Use: 8.9/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.3/10)
  • Quality of Support: 9.1/10 (Category avg: 9.2/10)

Who Is the Company Behind ReliaQuest GreyMatter?

  • Seller: ReliaQuest
  • Company Website:
  • Year Founded: 2007
  • HQ Location: Tampa, Florida, United States
  • LinkedIn® Page: www.linkedin.com
    1,106 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Consumer Services
  • Company Size: 40% Medium, 25% Small

What Do G2 Reviewers Say About ReliaQuest GreyMatter?

AI-generated summary from verified user reviews

Pros
  • Users value the exceptional visibility provided by ReliaQuest GreyMatter, enhancing security management across multiple environments effortlessly.
  • Users value the centralized management of ReliaQuest GreyMatter, enhancing security operations and streamlining incident response.
  • Users praise the exceptional customer support of ReliaQuest GreyMatter, noting responsiveness and helpful guidance in security management.
  • Users value the ease of use of ReliaQuest GreyMatter, enhancing efficiency through seamless integration and streamlined operations.
  • Users appreciate the easy integrations of ReliaQuest GreyMatter, significantly streamlining investigations and enhancing overall security visibility.
Cons
  • Users experience alert delays, clunky interfaces, and slow report loading, suggesting the need for improved UX design.
  • Users find the complexity of configurations and features requires significant time to fine-tune for desired outcomes.
  • Users experience inefficient alert systems due to delays, duplicates, and slow report loading, requiring additional fine-tuning.
  • Users experience a learning curve with advanced automation workflows, though support resources help ease the process.
  • Users experience login issues with ReliaQuest GreyMatter's Android app, citing a clunky sign-in process as frustrating.

What Are Recent G2 Reviews of ReliaQuest GreyMatter?

Cado Response

Cado is a Cloud Detection & Response platform that empowers security teams to get to the bottom of security incidents in the cloud faster. With Cado, what used to take analysts days, now takes minutes. Automate data collection. Process data at cloud speed. Analyze with purpose. No confusion, no complexity.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate Cado Response?

  • Ease of Use: 6.7/10 (Category avg: 8.6/10)
  • Quality of Support: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Cado Response?

Who Uses This Product?

  • Company Size: 50% Large, 50% Small

What Do G2 Reviewers Say About Cado Response?

AI-generated summary from verified user reviews

Pros
  • Users value the analytics capabilities of Cado Response, significantly reducing the time to address security threats.
  • Users highlight the efficiency of cloud security in Cado Response, significantly reducing time to resolve threats.
  • Users value the efficiency of Cado Response, significantly reducing the time needed to address security threats.
Cons
  • Users face integration issues with Cado Response, leading to data silos and complicating the security management process.

What Are Recent G2 Reviews of Cado Response?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024