Fortiv
Who Is the Company Behind Fortiv?
- Seller: Fortiv
- Year Founded: 2025
- HQ Location: Copenhagen, DK
-
LinkedIn® Page: www.linkedin.com
20 employees on LinkedIn®
Total Products under this Category: 90
Last updated: September 15, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
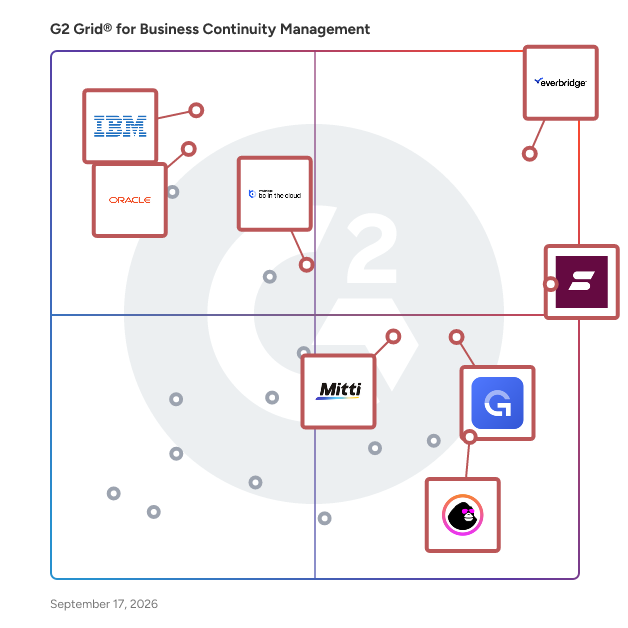
Highlighted products: Everbridge 360 (Critical Event Management), Sprinto, GlobalSuite, IBM OpenPages, Mitti (by SafetyCulture), BC in the Cloud, Oracle Risk Management Cloud, and Copla.
Underlying data: [Grid® JSON](https://www.g2.com/categories/business-continuity-management-software/grids.json?focus%5B%5D=everbridge-360-critical-event-management&focus%5B%5D=sprinto-inc&focus%5B%5D=globalsuite&focus%5B%5D=ibm-openpages&focus%5B%5D=safetyculturehq&focus%5B%5D=bc-in-the-cloud&focus%5B%5D=oracle-risk-management-cloud&focus%5B%5D=copla)
GRC360.ai is a unified Governance, Risk, and Compliance platform that enables organizations to structure, maintain, and continuously monitor their entire GRC ecosystem across policies, risks, controls, and regulatory frameworks. It supports global and regional standards such as ISO 27001, NCA ECC, SAMA regulations, NIST and custom enterprise frameworks. Designed for SMBs and large organizations, GRC360.ai provides a single operational environment for compliance, cybersecurity, audit, and risk teams who need predictability and structure across their governance processes. Most companies approach GRC reactively. Policies are stored in scattered folders, risks sit in spreadsheets, controls are checked only during audits, and compliance is treated as an annual documentation exercise. This leads to an inconsistent governance posture where teams rely on manual updates, disconnected workflows, and fragmented reporting. GRC360.ai eliminates this fragmentation by aligning all governance components into a deeply interconnected model where every policy, risk, control, and compliance obligation communicates with the others. As soon as something changes, whether it is a new risk assessment, a policy update, or a control adjustment, the entire system reflects it. Traditional GRC tools often handle components in isolation, requiring teams to jump between separate modules or external systems to maintain alignment. GRC360.ai takes a different approach: it treats governance as a living structure. Policies link to controls, controls map to risks, risks connect to frameworks, and evidence ties everything together. Nothing lives in a silo. This integrated design reduces manual coordination, prevents inconsistencies, and creates a perpetual audit readiness state, GRC360.ai consolidates what organizations typically handle through multiple spreadsheets, shared drives, policy management tools, and risk tracking systems. Instead of relying on external vendors or manual cross-checks, the platform provides built-in workflows, versioning, approval sequences, control libraries, and framework mappings. Whether a team is running an ISO 27001 cycle, preparing for a SAMA audit, or tracking internal cybersecurity controls, GRC360.ai provides the underlying structure needed to maintain clarity and continuity. Because the platform is built around interconnected data relationships, organizations avoid the blind spots that arise from traditional checklist-based compliance. GRC360.ai ensures that every governance element has traceability, context, and lineage. Dashboards offer a real-time view of governance posture showing how risks affect compliance, how controls mitigate gaps, and where attention is needed. Integrations with Active Directory, email systems, and custom APIs allow the platform to operate within existing enterprise ecosystems. As a result, organizations achieve predictable governance outcomes with reduced manual effort. Instead of managing documents and tasks across disconnected systems, teams operate within a single source of truth that keeps everything aligned. GRC360.ai is designed for compliance leaders, cybersecurity teams, and risk professionals who need a structured and reliable way to maintain governance in complex environments. Built by a company that has worked closely with regulated industries, the platform reflects a deep understanding of how frameworks, controls, and organizational processes intersect. GRC360.ai supports English and Arabic. It can be adapted to additional languages based on deployment requirements. Its goal is not just to digitize GRC, but to create a connected governance foundation that organizations can depend on as they scale.
Unified governance, risk, and compliance software suite that helps organizations manage enterprise risk, third party and vendor risk, policy management, compliance training, ethics and hotline reporting, business continuity, and cyber and IT risk, all in one connected system instead of disconnected point tools. 8,300+ organizations trust Mitratech to run their GRC programs, including the AI running inside them. AI governance isn't a feature we added. It's how the platform was designed. The platform is built around ARIES, an AI governance engine purpose built for regulatory compliance, risk assessment, and AI auditability in regulated environments. In a category full of black box AI, ARIES is one of the only solutions that validates its own outputs: 80%+ precision and recall on document analysis, full reasoning traces, and source linked results your team can verify before acting.
Opsbook is an AI-powered Resilience Operating System built for mid-market and enterprise organizations in regulated industries. It helps security, BC/DR, and risk teams move beyond static plans and one-off tabletop exercises, connecting plans, exercises, incidents, actions, and evidence into one continuous readiness loop, so response capability holds up under real disruption, not just on paper. The platform spans the full readiness cycle: AI-generated scenario creation, live multi-channel scenario injects, role-based response workspaces, voice-to-text hotwash debrief capture, automated after-action reports, and resiliency scoring that tracks teams across four maturity bands (Fragile, Functional, Mature, Optimized) over seven cross-functional domains. Tracked actions feed directly into updated plans and playbooks, closing the loop between exercise and institutional learning. Every exercise produces audit-ready documentation mapped to the regulatory frameworks our customers are actually examined against, including DORA, NIS2, SEC cyber disclosure rules, NIST 800-53, CMMC, NERC CIP-008-6, and HIPAA 405(d). Opsbook is also built for MSSPs, MSPs, and vCISOs who deliver resilience services to enterprise clients. All license tiers allow service providers to run exercises on behalf of their clients, no additional licensing required. Key capabilities: AI-generated, customizable tabletop scenarios for any industry or threat type Live, multi-channel scenario injects (email, SOC alert, SMS, executive directive, regulator letter) that adapt in real time Role-based response workspace with 50+ role-specific action templates (CISO, CFO, CRO, Legal Counsel, Incident Commander, Compliance Officer, Clinical Operations, and more) Voice-to-text hotwash capture for post-exercise debriefs, with logged actions and evidence folding directly into the AAR Automated after-action reports with resiliency scoring across seven cross-functional domains and four maturity bands Automated playbook generation and dynamic incident response libraries Regulator-aligned evidence mapping (DORA, NIS2, SEC, NIST 800-53, CMMC, NERC CIP-008-6, HIPAA 405(d)) with audit-ready GRC export 15+ integrations including Splunk, CrowdStrike, ServiceNow, Archer, Fusion, Palo Alto Cortex, OneTrust, LogicGate, Workday, and more Industries served: Financial Services, Healthcare, Manufacturing, Energy, Defense, Public Sector, Education.
The Operational Resilience Xcelerator (ORX) is an innovative tool designed to streamline and simplify the key processes that drive your organization’s operational resilience. From Business Impact Analysis (BIA) to Business Continuity Planning (BCP), ORX helps you manage critical data, automate workflows, and ensure your business remains resilient—directly within your MS Teams environment.
ReadiNow enables highly regulated organizations to rapidly build digital solutions to ever-changing business problems. The ReadiNow GRC platform allows businesses to swiftly automate risk management processes and improve productivity across the organization. This no-code platform democratizes solution development by allowing business experts to build their own solutions, to manage the ever-changing risk and compliance landscape.
riskcloud.NET is a cloud-based enterprise risk management software conforming to ISO31000 enabling to better manage risk.
Average Rating: 4.0/5.0
Total Reviews: 1
AI-generated summary from verified user reviews
"Good Compilation of Tools for Information Security and Compliance"
Rating: 4.0/5.0 stars
— Jose Luis M.
Sentinel is purpose-built crisis management software for Health, Safety, Environment (HSE) and Risk professionals. Where most crisis tooling focuses on real-time response, Sentinel codifies the work that happens before and after an event: drafting and maintaining the Crisis Management Manual, designing and running exercises, and tracking program maturity over time. The platform has four core modules: 1. CMR Manual Builder — A guided 10-section wizard tailored to the user's industry that drafts an editable DOCX aligned to ISO 22361, ISO 22301 and AS/NZS 5050. Sector profiles cover mining, energy, government, healthcare, transport, financial services, professional services and more. 2. Standards Alignment Review — Upload an existing manual (PDF or DOCX) and Sentinel scores it against ISO 22361, ISO 22301, AS/NZS 5050 and AIIMS, returning a board-ready 6-page maturity report in under two minutes. Each subsequent review tracks progress so users can show their program's evolution over time. 3. Scenario Builder & Exercise Pack — Generate full exercise packs (role cards, master inject log, briefing pack, after-action template) from either a manual upload or a starting-point scenario library. Most exercises generate in 1-3 minutes. All content uses Australian English, AIIMS principles, and a realistic mass-decisions cadence. 4. Program Maturity Diagnostic — A re-runnable 12-question capability assessment that scores the program against ISO 22361, ISO 22301, AS/NZS 5050 and AIIMS. Users run it quarterly and Sentinel tracks the trajectory. Sentinel is built with security and compliance in mind: - Microsoft Entra ID (Azure AD) single sign-on for enterprise customers - Audit logging on all sensitive actions - Australian English content throughout, with AU regulatory hooks (WHS Act, Privacy Act NDB, ASX 3.1, EPBC, SOCI, state EPA) - Transparent pricing in USD with AU GST applied at checkout The platform is used by Founders, HSE Managers, Risk Managers, and Crisis Management Consultants across Australia, New Zealand, the UK, North America and Asia. Learn more at https://sentinelcmt.com
SmartSuite is an AI-powered Work Operating System (Work OS) — one platform for GRC & Resilience, IT Service Delivery, Project & Portfolio Management, and Business Operations. Trusted by over 2,000 businesses worldwide, SmartSuite unites data, teams, and systems in a single governed environment, eliminating tool sprawl, reducing manual handoffs, and giving every stakeholder real-time visibility into the work that matters most. Where traditional GRC and ITSM platforms require lengthy build cycles, custom development, and months of professional services before a single team goes live, SmartSuite is built to launch in weeks, not quarters. Purpose-built Solution Suites — spanning Enterprise Risk Management, Compliance, Internal Audit, Cyber & IT Risk, ITSM, IT Asset Management, Portfolio & Financial Management, and more — are ready to deploy from day one, configured without code, and designed to expand as adoption grows across the organization. Underpinned by 8 interconnected platform frameworks — Data Architecture, Workflow Orchestration, Automation, Artificial Intelligence, Secure Collaboration, Enterprise Reporting, Integrations, and Security & Governance — SmartSuite delivers the structural rigor enterprise organizations demand without the total cost of ownership that traditional point solutions carry. SOC 2, ISO 27001, GDPR, and HIPAA compliant out of the box.
Average Rating: 4.9/5.0
Total Reviews: 46
AI-generated summary from verified user reviews
"SmartSuite impresses with enormous flexibility and powerful automations"
Rating: 5.0/5.0 stars
— martin l.
"Powerful and Flexible, Requires Commitment"
Rating: 5.0/5.0 stars
— Paolo B.
The SYNERGi Governance, Risk and Compliance Platform has been developed in-house by Information Risk Management (cybersecurity specialists) since 2013. Since then, it has won several awards with SC Magazine and global organisations are using SYNERGi to monitor their governance, risk and compliance obligations and requirements. SYNERGi is a dedicated Cyber GRC Platform that helps organisations manage their compliance and information security risk programs efficiently and inexpensively. Some of the key features include: - Seven modules (Governance, Risk Management, Compliance Management, Audit Management, Vendor Management, IT Security and Business Continuity. - Offered as a cloud SaaS, on premise SaaS or Perpetual licence - Dedicated in-house training/support team and maintenance - Supports organisation’s of all levels of cyber maturity - Developed in-house and delivered by IRM’s expert cyber consultants - User-friendly and scalable cloud offering - Helps clients with their GRC, Audit, Vendor and IT Security initiatives - Suitable for sharing with 3rd parties for compliance & reporting SYNERGi was developed as a result of IRM’s 20 year experience in Consultancy and Technical know-how; we can support client engagement with Managed Service arrangements. IRM do our utmost to ensure that SYNERGi works in a way to align with your risk management goals.
Average Rating: 4.0/5.0
Total Reviews: 1
"Helps us to achieve risk management goals"
Rating: 4.0/5.0 stars
— Verified User in Computer & Network Security
Whether reducing risks, ensuring business continuity, or managing complex transformation projects – the integrated approach and 360° management cockpit allow you to keep track even in a complex corporate structure while ensuring regulatory compliance. Corporate governance with TopEase® is: - Preventive and proactive: TopEase® supports you in identifying risks early and minimising them through targeted measures, optimising processes, increasing security, and improving quality. All of this allows for proactive preparation for the next challenge. - Comprehensive: Oftentimes, a variety of tools are used to manage processes, controls, risks, systems, and legal requirements, resulting in a fragmented view that obscures important relationships and dependencies. The integrated approach of TopEase® allows for a redundancy-free overall view of the company. - Intelligent: Take advantage of the benefits of intelligent automation and save time, effort, and costs. TopEase® offers automated self-assessments as well as intelligent resilience monitoring and helps you create graphics and documents effortlessly.
Average Rating: 4.5/5.0
Total Reviews: 1
AI-generated summary from verified user reviews
"A Quick Look at TopEase Software"
Rating: 4.5/5.0 stars
— Abhijith R.
