Best Security Information and Event Management (SIEM) Software for Small Business - Page 2

How Many Security Information and Event Management (SIEM) Software Products Does G2 Track?

Total Products under this Category: 145

Category Stats (Oct 2026)

  • Average Rating: 4.46/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: EventSentry (+0.55%) - Among all products in this category, EventSentry recorded the largest rating increase compared to last month

Last updated: October 07, 2026

How Does G2 Rank Security Information and Event Management (SIEM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,300+ Authentic Reviews
  • 145+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

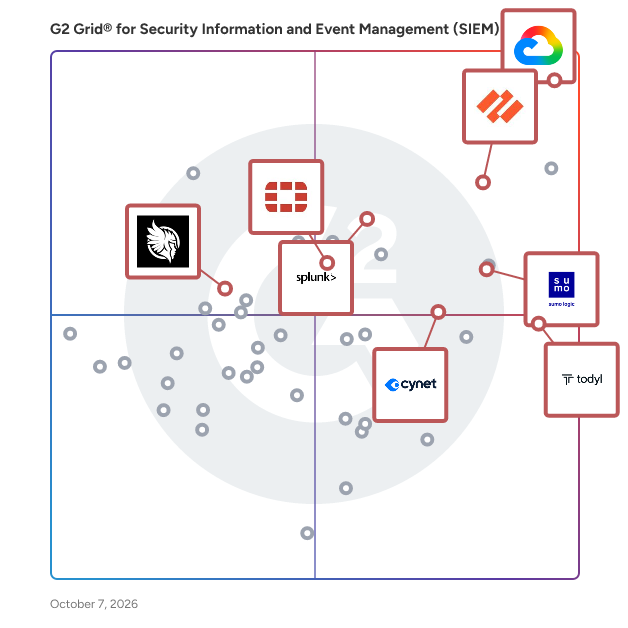
G2 Grid® for Security Information and Event Management (SIEM) Software

G2 Grid® for Security Information and Event Management (SIEM) Software plotting products by satisfaction and market presence

Highlighted products: Google Security Operations, Todyl Security Platform, Palo Alto Cortex XSIAM, Huntress Managed SIEM, Splunk Enterprise, Sumo Logic, FortiSIEM, and Cynet.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-information-and-event-management-siem/grids.json?focus%5B%5D=google-security-operations&focus%5B%5D=todyl-security-platform&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=huntress-managed-siem&focus%5B%5D=splunk-enterprise&focus%5B%5D=sumo-logic&focus%5B%5D=fortisiem&focus%5B%5D=cynet&segment=small-business)

Pandora FMS

Pandora FMS is a unified monitoring and observability platform designed to consolidate visibility, alerting, reporting, and automation across heterogeneous IT environments. Instead of combining multiple point tools for networks, servers, applications, and cloud services, Pandora FMS centralizes data collection and operational workflows in a single console, reducing integration effort and operational complexity in on-premise, hybrid, and multi-cloud architectures. The platform collects telemetry using multiple methods, including agents, remote checks, standard protocols (e.g., SNMP/WMI), APIs, and log/event ingestion. This enables teams to monitor infrastructure and services end-to-end, correlate signals, and maintain consistent alerting policies and dashboards across distributed estates. Pandora FMS also supports capacity and trend analysis to anticipate resource constraints and identify recurring patterns, and includes AI-assisted capabilities for anomaly detection and automated thresholds to surface hard-to-spot operational signals. Pandora FMS is extensible through a large plugin ecosystem (500+ plugins and integrations), covering a wide range of enterprise and infrastructure technologies such as SAP, Oracle, Citrix, JBoss, VMware, AWS, SQL Server, Red Hat, and WebSphere. This extensibility helps organizations standardize monitoring across legacy and modern stacks without redesigning their monitoring approach per technology. Core capabilities: -Unified monitoring for networks, servers, applications, cloud services, endpoints, and logs -Centralized alerting, event correlation, dashboards, and scheduled reporting -Flexible data collection via agents, remote checks, APIs, and plugins -Scalability for distributed environments and large numbers of monitored elements -Analytics for trend/capacity planning plus AI-assisted anomaly detection and dynamic thresholds -A key differentiator is direct vendor support, which simplifies escalation and ensures continuity of expertise for deployment, tuning, and ongoing operations.

Average Rating: 4.6/5.0

Total Reviews: 212

How Do G2 Users Rate Pandora FMS?

  • Activity Monitoring: 10.0/10 (Category avg: 9.1/10)
  • Data Examination: 8.3/10 (Category avg: 8.6/10)
  • Ease of Use: 9.1/10 (Category avg: 8.8/10)
  • Log Management: 10.0/10 (Category avg: 9.1/10)

Who Is the Company Behind Pandora FMS?

  • Seller: Pandora FMS
  • Company Website:
  • Year Founded: 2004
  • HQ Location: Madrid, Spain
  • Twitter: @pandorafms
    5,458 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    56 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Data Analyst
  • Top Industries: Information Technology and Services, Telecommunications
  • Company Size: 50% Medium, 37% Small

What Do G2 Reviewers Say About Pandora FMS?

AI-generated summary from verified user reviews

Pros
  • Users value the reliable remote monitoring capabilities of Pandora FMS, ensuring seamless oversight of their systems.
  • Users enjoy the ease of use of Pandora FMS, appreciating its intuitive interface and reliable support.
  • Users value the real-time monitoring capabilities of Pandora FMS, enhancing visibility of all network devices effortlessly.
  • Users value the flexibility and adaptability of Pandora FMS, making it suitable for diverse IT monitoring needs.
  • Users value the versatility of network monitoring in Pandora FMS, effectively managing diverse devices and environments.
Cons
  • Users find the learning curve steep, particularly with initial setup and complex functionalities of Pandora FMS.
  • Users find the complex setup of Pandora FMS challenging, particularly due to compatibility issues and steep learning curves.
  • Users note the learning difficulty with Pandora FMS, especially for those lacking technical expertise for setup and configuration.
  • Users find the complex configuration of Pandora FMS challenging, especially without extensive technical expertise.
  • Users face a difficult learning curve with Pandora FMS, which can hinder effective usage for beginners.

What Are Recent G2 Reviews of Pandora FMS?

What Are G2 Users Discussing About Pandora FMS?

Logsign Unified SO Platform

Logsign Unified SO Platform integrates next-gen SIEM, threat intelligence, UEBA, and SOAR and empowers organizations to optimize and streamline their cybersecurity operations. In addition to that, the platform offers seamless integration capabilities, allowing them to effortlessly integrate their existing security software and leverage our vast integration library, expanding the Logsign USO Platform's functionality and providing a comprehensive security management experience. With these extensive capabilities, it allows organizations to improve their security posture and ensure compliance with relevant regulations and standards. - Easy-to-deploy, easy-to-use Unified SO Platform for all sizes of enterprises. - Enterprise-grade scalability, high availability - Cluster SIEM, big data infrastructure.  - On-premise solution. - 500+ predefined integrations and free plugin service. - Collects & stores high volumes of data. - Threat hunting, fast search & investigation, advanced behaviour analysis, IOC detection. - Threat Intelligence and UEBA embedded. - Real-time detection & prevention, wide correlation library based on Mitre Att&ck framework.  - Real-time monitoring, predefined dashboards & reports, meeting Compliance Requirements (PCI DSS, ISO 27001, HIPAA, SOX, and more). - Automated notifications, automated Incident response - Incident Cycle Management - Incident Response - Multiple pricing options without capacity or log source limit, feature-based pricing.

Average Rating: 4.7/5.0

Total Reviews: 53

How Do G2 Users Rate Logsign Unified SO Platform?

  • Activity Monitoring: 9.1/10 (Category avg: 9.1/10)
  • Data Examination: 8.7/10 (Category avg: 8.6/10)
  • Ease of Use: 9.6/10 (Category avg: 8.8/10)
  • Log Management: 9.6/10 (Category avg: 9.1/10)

Who Is the Company Behind Logsign Unified SO Platform?

  • Seller: Logsign
  • Year Founded: 2010
  • HQ Location: Hague, Netherlands, NL
  • Twitter: @logsign
    368 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    41 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 50% Medium, 31% Small

What Are Recent G2 Reviews of Logsign Unified SO Platform?

What Are G2 Users Discussing About Logsign Unified SO Platform?

Guardsix

Guardsix is the sovereign security platform for lean European teams, bringing log management and audit-ready compliance to regulated industries, critical national infrastructure operators, and the Managed Security Service Providers (MSSPs) that serve them throughout Europe and beyond. Headquartered in Copenhagen, Denmark, Guardsix delivers sovereign-by-design security for organisations that carry real operational responsibility. The company employs several hundred cyber security specialists and keeps every organisation it serves in full control of their data, deployment, and operations. Guardsix provides a unified Command Centre platform combining: • Security Information and Event Management (SIEM) • Network Detection and Response (NDR) • Security Orchestration, Automation and Response (SOAR) • Fleet for enabling multi-tenant management • Governance for Healthcare internal risk compliance monitoring The platform is built to support European data sovereignty, regulatory compliance and operational control, with predictable node-based pricing and deployment options spanning on-premises, air-gapped, hybrid and cloud environments. Guardsix solutions help organisations: • Simplify audit readiness for regulations such as NIS2, DORA, and GDPR. • Support lean security teams with efficient log management and simplified workflows. • Scale security operations without increased complexity or ingestion-led pricing surprises. • Keep security data under European jurisdiction and control — where it lives, who operates it, and under whose laws. • Deploy on their own terms, on-prem and in infrastructure they control, keeping migration a real option at every renewal. • See clearly across their whole environment, with SIEM, NDR, SOAR, Fleet, and Governance in one sovereign platform rather than a stack of point tools. Guardsix maintains SOC 2 Type II attestation and designs its solutions in accordance with European data protection requirements. With a strong partner-first model, Guardsix works closely with regional MSSPs and service providers, combining sovereign-by-design security technology with European integrity and deployment flexibility.

Average Rating: 4.3/5.0

Total Reviews: 105

How Do G2 Users Rate Guardsix?

  • Activity Monitoring: 8.2/10 (Category avg: 9.1/10)
  • Data Examination: 8.0/10 (Category avg: 8.6/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 8.6/10 (Category avg: 9.1/10)

Who Is the Company Behind Guardsix?

  • Seller: guardsix
  • Company Website:
  • Year Founded: 2001
  • HQ Location: Copenhagen, Capital Region
  • LinkedIn® Page: linkedin.com
    180 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 44% Medium, 31% Small

What Do G2 Reviewers Say About Guardsix?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of Guardsix, simplifying administration and enhancing overall user experience.
  • Users appreciate the ease of use of Guardsix Log Management, making it simple and efficient for managing logs.
  • Users commend the excellent customer support of Logpoint, enhancing the overall experience and satisfaction with the product.
  • Users value the easy integrations of Logpoint, seamlessly unifying various telemetry types within their existing tech ecosystem.
  • Users value the efficiency of Logpoint, simplifying incident management and enhancing overall effectiveness in daily operations.
Cons
  • Users find the poor interface design challenging, making it difficult to navigate and utilize effectively.
  • Users find the UX improvement necessary as logs are poorly presented and the interface is slow and confusing.
  • Users find the interface complexity challenging, though improvements are expected in the near future.
  • Users find the confusing interface of Guardsix challenging and slow to navigate, impacting their overall experience.
  • Users feel there is an information deficiency about resource needs, leading to potential overuse and uncertainty in design.

What Are Recent G2 Reviews of Guardsix?

What Are G2 Users Discussing About Guardsix?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Graylog

SIEM and log management in one platform Graylog helps security and IT teams detect, investigate, and respond to threats faster, using explainable AI and real-time data correlation to turn large volumes of log data into decisions they can act on. More than 60,000 organizations worldwide use Graylog for visibility and control over their IT environments. The problem Security analysts and IT professionals spend their days sifting through vast amounts of log data to find the anomalies that matter, track incidents, and prove compliance with regulatory standards. Most of that data is noise. -Too many alerts that do not matter, and the one that does is buried. -Forensic evidence scattered across tools, so investigations stall. -Audit documentation assembled by hand the week before the deadline. Catch the patterns rules miss Anomaly detection flags unusual patterns in your data so your team sees behavior that signature-based rules leave in the blind spot. Real-time correlation connects related events as they arrive. Investigations that build themselves Guided investigations walk analysts through complex incidents. Automated workflows handle the repetitive tasks, and AI-driven summaries surface the affected assets, the incident timeline, and the high-priority findings. Analysts focus on what matters instead of excessive data. Work the alerts that matter first Risk scores rank each alert by the severity of what fired and the importance of the assets involved, so a port scan against a database of client PII outranks the same scan against a user laptop. With centralized log management, every log stays a single log, giving your team the historic evidence to complete forensic investigations in one place. One platform, three products Graylog fits the team you have: -Graylog Open for log management on an open foundation. -Graylog Enterprise for IT operations and log management at scale. -Graylog Security for detection, investigation, and response.

Average Rating: 4.4/5.0

Total Reviews: 108

How Do G2 Users Rate Graylog?

  • Activity Monitoring: 8.7/10 (Category avg: 9.1/10)
  • Data Examination: 8.3/10 (Category avg: 8.6/10)
  • Ease of Use: 8.5/10 (Category avg: 8.8/10)
  • Log Management: 9.1/10 (Category avg: 9.1/10)

Who Is the Company Behind Graylog?

  • Seller: Graylog
  • Company Website:
  • Year Founded: 2009
  • HQ Location: Houston, US
  • Twitter: @graylog2
    9,115 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    124 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 43% Medium, 31% Small

What Do G2 Reviewers Say About Graylog?

AI-generated summary from verified user reviews

Pros
  • Users value the cost optimization of Graylog, finding it reliable and compliant with industry standards.
  • Users find the detailed API information essential for effective debugging, enhancing their daily workflow significantly.
  • Users find the detailed API information invaluable for effective debugging, preventing potential dead ends in troubleshooting.
  • Users find the detailed API information provided by Graylog extremely helpful for effective debugging processes.
  • Users praise Graylog for its reliable and cost-effective pricing, aligning well with industry standards and needs.
Cons
  • Users find Graylog's complexity frustrating, as it often leads to wasted time during debugging and review processes.
  • Users face debugging difficulties with Graylog, often leading to wasted time and frustration during troubleshooting.
  • Users experience difficulties with integration issues, limiting the compatibility of Graylog with other platforms.
  • Users find the learning curve to be challenging, leading to time wasted instead of efficient debugging and reviews.
  • Users experience time consumption with Graylog, finding that it complicates workflows and wastes valuable debugging time.

What Are Recent G2 Reviews of Graylog?

What Are G2 Users Discussing About Graylog?

Adlumin

Adlumin, an N-able Company, provides enterprise-grade cybersecurity for organizations of all sizes through its innovative Security Operations as a Service platform. With an agnostic approach, the Adlumin platform seamlessly integrates with existing tech stacks, and its flexible management options enable it to be self-managed by an internal team, or fully managed by Adlumin experts. The Adlumin platform stops cyber threats early with deep learning models tailored to each environment. It maximizes resource efficiency by optimizing existing technology and streamlining workflows across teams. Adlumin transforms risk into resilience by identifying and addressing vulnerabilities, while cybersecurity experts proactively uncover and neutralize threats before they can do damage. Adlumin empowers organizations to take control of their digital security making advanced protection accessible to all.

Average Rating: 4.7/5.0

Total Reviews: 64

How Do G2 Users Rate Adlumin?

  • Activity Monitoring: 9.7/10 (Category avg: 9.1/10)
  • Data Examination: 9.2/10 (Category avg: 8.6/10)
  • Ease of Use: 9.0/10 (Category avg: 8.8/10)
  • Log Management: 9.5/10 (Category avg: 9.1/10)

Who Is the Company Behind Adlumin?

  • Seller: N-able
  • Company Website:
  • HQ Location: Morrisville, North Carolina
  • Twitter: @Nable
    15,859 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 55% Medium, 23% Small

What Do G2 Reviewers Say About Adlumin?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the detailed analytic reports of Adlumin, highlighting its reliability and user-friendly interface.
  • Users value the detailed analytic reports of Adlumin for their reliability and user-friendly interface.
  • Users appreciate the detailed analytic reports from Adlumin, enhancing reliability and ease of use.
  • Users praise the ease of management with Adlumin, appreciating its reliable and user-friendly interface.
  • Users praise the ease of use of Adlumin, highlighting its reliability and detail in analytic reports.
Cons
  • Users feel that the customer support for Adlumin is adequate but has room for improvement.

What Are Recent G2 Reviews of Adlumin?

Logz.io

Logz.io is an AI-powered observability platform designed to help teams solve critical log management, monitoring, and troubleshooting challenges. Built for modern environments, Logz.io unifies log management, infrastructure monitoring, and distributed tracing in a single platform to provide deep, actionable insights into system performance and health. At its core, Logz.io’s AI Agent technology automates root cause analysis (RCA) and surfaces insights that accelerate investigations, reduce MTTR, and eliminate the need for time-consuming manual analysis or navigating multiple dashboards. Whether managing microservices or troubleshooting production issues, Logz.io empowers teams to quickly pinpoint issues, de-risk deployments, and focus on innovation. Unlike traditional observability tools that require ever-increasing data volumes and expertise, Logz.io offers a smarter, cost-optimized solution. With the ability to customize data ingestion and optimize telemetry costs, Logz.io ensures you get the insights you need without breaking the budget.

Average Rating: 4.5/5.0

Total Reviews: 163

How Do G2 Users Rate Logz.io?

  • Activity Monitoring: 9.0/10 (Category avg: 9.1/10)
  • Data Examination: 8.5/10 (Category avg: 8.6/10)
  • Ease of Use: 8.8/10 (Category avg: 8.8/10)
  • Log Management: 8.8/10 (Category avg: 9.1/10)

Who Is the Company Behind Logz.io?

  • Seller: Logz.io
  • Year Founded: 2014
  • HQ Location: Boston, MA
  • Twitter: @logzio
    3,156 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    102 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, Software Developer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Medium, 30% Small

What Do G2 Reviewers Say About Logz.io?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized log management of Logz.io, enabling efficient issue tracking and automated reporting.
  • Users highlight the excellent customer support of Logz.io, noting quick responses and knowledgeable assistance from the team.
  • Users value the ease of implementation of Logz.io, praising its smooth integration and user-friendly dashboards.
  • Users praise the implementation ease of Logz.io, enjoying a smooth integration and user-friendly dashboard.
  • Users value the centralized log collection of Logz.io, enhancing productivity with user-friendly tools and insights.
Cons
  • Users find the dashboard issues in Logz.io cumbersome, with needs for improved chart creation and UI updates.
  • Users face integration issues with Logz.io, citing lag in indexing and complexity in advanced configurations.
  • Users find the limited customization options in Logz.io restrictive, affecting their overall satisfaction with the product.
  • Users find the complex configuration challenging, particularly with alerts and custom parsing rules setup.
  • Users find complex debugging challenging, often needing to deeply analyze data to set up alerts and reports effectively.

What Are Recent G2 Reviews of Logz.io?

What Are G2 Users Discussing About Logz.io?

Coralogix

Coralogix is a modern, full-stack observability platform transforming how businesses process and understand their data. Our unique architecture powers in-stream analytics without reliance on indexing or hot storage. We specialize in comprehensive monitoring of logs, metrics, trace and security events, enhancing operational efficiency and reducing total cost of ownership by up to 70%. Coralogix stands out for its simple pricing model, based solely on data volume ingested and retained, and offers free, fast customer support with less than 30 second response time and 1 hour resolution time. Our platform covers the entire range of observability with features such as APM, RUM, SIEM, Kubernetes monitoring and more, all streamlined for quick integration and immediate value. Components within the stream store the system state to provide stateful insights and real-time alerting without ever needing to index the data — so there are never any trade-offs to achieve observability. Once ingested, parsed, and enriched, data is written remotely to an archive bucket controlled by the client. The archive can be queried directly at any time, from the platform UI or via CLI, giving users infinite retention with full control over, and access to, their data. View and query your data from any dashboard using any syntax. Coralogix has successfully completed relevant security and privacy compliances by BDO including GDPR, SOC 2, PCI, HIPAA, and ISO 27001/27701.

Average Rating: 4.5/5.0

Total Reviews: 372

How Do G2 Users Rate Coralogix?

  • Activity Monitoring: 8.7/10 (Category avg: 9.1/10)
  • Data Examination: 8.7/10 (Category avg: 8.6/10)
  • Ease of Use: 8.8/10 (Category avg: 8.8/10)
  • Log Management: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind Coralogix?

  • Seller: Coralogix
  • Company Website:
  • Year Founded: 2014
  • HQ Location: San Francisco, CA
  • Twitter: @Coralogix
    4,102 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    609 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Medium, 33% Large

What Do G2 Reviewers Say About Coralogix?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Coralogix, highlighting its simple setup and efficient integrations.
  • Users value the ease of log monitoring and seamless integration, enhancing overall observability and support responsiveness.
  • Users value the integration of logs, metrics, and alerts, enhancing efficiency in root-cause analysis and monitoring.
  • Users commend the exceptional customer support of Coralogix, ensuring quick resolutions and a smooth experience.
  • Users value the real-time monitoring of Coralogix, enhancing their understanding of user behavior and improving incident response.
Cons
  • Users find that the learning curve is steep for beginners, making navigation and understanding features challenging.
  • Users experience slow performance with Coralogix, leading to frustration due to delayed log fetching and UI loading.
  • Users find the difficult learning curve of Coralogix challenging, especially for beginners navigating complex options.
  • Users find the missing feature for downloading log results a significant limitation in Coralogix's functionality.
  • Users find the learning difficulty of Coralogix challenging, especially when navigating advanced features and the overwhelming UI.

What Are Recent G2 Reviews of Coralogix?

LogRhythm SIEM

Rapidly deploy LogRhythm SIEM, the leading self-hosted SIEM, to secure your organization with powerful detections, synchronized threat intelligence, automated workflows, and achieve faster, more accurate threat detection, investigation, and response (TDIR).

Average Rating: 4.2/5.0

Total Reviews: 137

How Do G2 Users Rate LogRhythm SIEM?

  • Activity Monitoring: 8.9/10 (Category avg: 9.1/10)
  • Data Examination: 8.4/10 (Category avg: 8.6/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 9.0/10 (Category avg: 9.1/10)

Who Is the Company Behind LogRhythm SIEM?

  • Seller: Exabeam
  • Year Founded: 2013
  • HQ Location: Broomfield, CO
  • Twitter: @exabeam
    5,374 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    785 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Information Security Analyst, Cyber Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 40% Medium, 40% Large

What Are Recent G2 Reviews of LogRhythm SIEM?

What Are G2 Users Discussing About LogRhythm SIEM?

LevelBlue USM Anywhere

LevelBlue USM Anywhere is a cloud-based security management solution that accelerates and centralizes threat detection, incident response, and compliance management for your cloud, hybrid cloud, and on-premises environments. USM Anywhere includes purpose-built cloud sensors that natively monitor your Amazon Web Services (AWS) and Microsoft Azure cloud environments. On premises, lightweight virtual sensors run on Microsoft Hyper-V and VMware ESXi to monitor your virtual private cloud and physical IT infrastructure. With USM Anywhere, you can rapidly deploy sensors into your cloud and on-premises environments while centrally managing data collection, security analysis, and threat detection from the AlienVault Secure Cloud. Five Essential Security Capabilities in a Single SaaS Platform AlienVault USM Anywhere provides five essential security capabilities in a single SaaS solution, giving you everything you need for threat detection, incident response, and compliance management—all in a single pane of glass. With USM Anywhere, you can focus on finding and responding to threats, not managing software. An elastic, cloud-based security solution, USM Anywhere can readily scale to meet your threat detection needs as your hybrid cloud environment changes and grows. 1. Asset Discovery 2. Vulnerability Assessment 3. Intrusion Detection 4. Behavioral Monitoring 5. SIEM

Average Rating: 4.4/5.0

Total Reviews: 102

How Do G2 Users Rate LevelBlue USM Anywhere?

  • Activity Monitoring: 8.9/10 (Category avg: 9.1/10)
  • Data Examination: 8.4/10 (Category avg: 8.6/10)
  • Ease of Use: 8.3/10 (Category avg: 8.8/10)
  • Log Management: 8.9/10 (Category avg: 9.1/10)

Who Is the Company Behind LevelBlue USM Anywhere?

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 62% Medium, 20% Small

What Are Recent G2 Reviews of LevelBlue USM Anywhere?

What Are G2 Users Discussing About LevelBlue USM Anywhere?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated