VALIDA
Who Is the Company Behind VALIDA?
- Seller: Normadat
- Year Founded: 1992
- HQ Location: San Sebastián de los Reyes, ES
-
LinkedIn® Page: www.linkedin.com
165 employees on LinkedIn®
Total Products under this Category: 179
Last updated: September 01, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
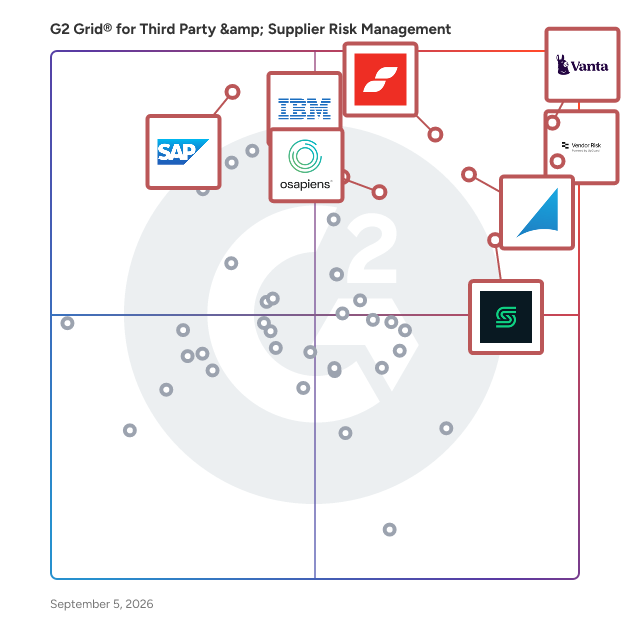
Highlighted products: Vanta, UpGuard Vendor Risk, Creditsafe, Descartes Denied Party Screening, Secureframe, osapiens, IBM OpenPages, and SAP Ariba.
Underlying data: [Grid® JSON](https://www.g2.com/categories/third-party-supplier-risk-management/grids.json?focus%5B%5D=vanta&focus%5B%5D=upguard-vendor-risk&focus%5B%5D=creditsafe&focus%5B%5D=descartes-denied-party-screening&focus%5B%5D=secureframe&focus%5B%5D=osapiens&focus%5B%5D=ibm-openpages&focus%5B%5D=sap-ariba)
VendorAuditly is vendor risk management software built for SMBs that don't have a compliance team. Replace spreadsheets with automated vendor assessments, questionnaires, AI contract risk analysis, insurance certificate tracking, breach monitoring, and one-click compliance evidence packs for DORA, NIS2, SOC2, ISO 27001, and HIPAA — all in 10 minutes setup at $49/month. Unlike ServiceNow, OneTrust, or Vanta — which cost $10,000–$100,000/year and require a dedicated GRC team — VendorAuditly is built for the operations manager or COO who needs to prove vendor oversight to enterprise customers and regulators without hiring a compliance department. Key capabilities: live vendor risk scoring with explainable breakdowns, AI-powered vendor questionnaires that adapt to how you use each vendor, automated 3-email follow-up sequences for questionnaire responses, breach watchlist monitoring (HIBP + CISA KEV), continuous vendor website monitoring, AI contract clause analysis, and regulator-ready evidence packs your auditor can use the same day. Used by fintech, SaaS, healthtech, and professional services companies across the UK, EU, and US who are subject to DORA, NIS2, GDPR, SOC2, or HIPAA third-party risk requirements.
With VendorXpert, third-party provider details can easily be monitored and tracked in a user-friendly Web-based environment that allows for rapid deployment and management of these crucial relationships. VendorXpert is a vendor management and compliance with integrated workflow reminders.
VERA is a vendor risk intelligence platform that helps organizations assess and continuously monitor third-party risk using externally observable, independently verifiable evidence. Traditional third-party risk management programs often rely heavily on questionnaires, self-attestations, and point-in-time assessments. VERA adds an independent layer of intelligence by collecting and validating external signals across a vendor’s security, operational, compliance, and reputational posture. This allows organizations to evaluate vendor risk without relying solely on what the vendor reports about itself. VERA evaluates a broad range of risk signals, including internet-facing attack surface, exposed services, DNS and email security, known vulnerabilities and CISA Known Exploited Vulnerabilities, credential and breach exposure, public code and secret exposure, compliance certifications, security maturity indicators, and financial and reputational signals. Evidence is evaluated for source credibility, vendor attribution, relevance, recency, and supporting context before it contributes to an assessment. Low-confidence, duplicate, or unverifiable findings can be excluded, helping reduce false positives and making findings easier for analysts to validate and defend. VERA is designed to complement existing third-party risk management processes rather than replace them. Security questionnaires, certifications, and vendor-provided documentation remain valuable, but external intelligence provides an additional perspective that can identify changes between formal assessments, validate vendor claims, and help teams focus limited analyst resources on the vendors and findings that deserve attention. By combining automated discovery and continuous monitoring with evidence verification and analyst judgment, VERA helps security, compliance, procurement, and third-party risk teams move from periodic vendor assessments toward a more continuous and evidence-based view of vendor risk.
VISO TRUST is a third-party risk management company built by a CISO who experienced firsthand how broken traditional vendor risk processes can be. Designed for senior security and compliance leaders, VISO TRUST partners with high-growth companies and enterprises operating in complex, regulated environments. The company brings a practitioner-led perspective to solving real-world third-party risk challenges faced by modern security teams. From that foundation, VISO TRUST delivers an automated third-party risk management platform purpose-built to eliminate manual, spreadsheet-driven workflows. The platform combines intelligent security questionnaires, automated evidence collection, continuous risk monitoring, and centralized reporting into a single system of record. Designed to integrate seamlessly into existing security programs, VISO TRUST helps teams scale vendor risk assessments without adding operational overhead. For security leaders, the value is immediate and measurable. VISO TRUST reduces the time required to assess vendors, accelerates vendor onboarding, and improves visibility into third-party risk across the organization. By focusing on real risk instead of administrative work, security teams can operate more strategically, demonstrate compliance with confidence, and make faster, better-informed risk decisions.
Average Rating: 4.7/5.0
Total Reviews: 3
AI-generated summary from verified user reviews
Rating: 5.0/5.0 stars
— Daniel D.
"Automated in the right direction"
Rating: 5.0/5.0 stars
— Verified User in Financial Services
Xapien is setting a new standard in enterprise due diligence in today’s evolving risk landscape. With unparalleled accuracy and unprecedented performance anchored by tech innovation, Xapien's AI-powered platform provides complete visibility of third-party risk across any business’s ecosystem without sacrificing commercial speed. Xapien was created by deep technology experts with decades of experience in intelligence and financial crime. It offers large organisations complete visibility of potential reputational or regulatory red flags in their third party relationships via comprehensive risk assessments delivered at the speed of enterprise. We're trusted by the world’s biggest corporations, consultancies, legal powerhouses and highly-regarded philanthropic & non-profit organisations.
What is this product? Zelthy Third-Party Due Diligence is an application for pharmaceutical compliance teams managing anti-corruption and anti-bribery obligations. It handles third-party risk profiling, sanctions and watchlist screening, due diligence questionnaire management, and ongoing monitoring of third-party relationships — supporting FCPA, UK Bribery Act, and other anti-corruption framework requirements. Key Features & Functionalities - Third-party risk profiling and scoring - Sanctions and watchlist screening with automated updates - Due diligence questionnaire management and tracking - Ongoing monitoring with periodic reassessment triggers - Investigation workflows for flagged relationships Primary Solution & Value Pharmaceutical companies maintain thousands of third-party relationships — distributors, consultants, CROs, investigators — each carrying potential anti-corruption risk. Regulatory expectations require risk-based due diligence and ongoing monitoring. This application structures the due diligence process from initial screening through ongoing monitoring, ensuring third-party relationships are assessed consistently and documented for regulatory review.
ZeroRisk is a Done-for-You vendor risk and compliance platform for mid-market regulated firms in the EU, UK and US. Most compliance tools give you a dashboard and leave the work to you. ZeroRisk runs the work itself: an agent assesses each vendor clause by clause against the frameworks you're held to, gathers the evidence, and produces a verdict your team reviews and signs. Vendors are re-checked continuously, so the record stays current between audits rather than going stale the day after you finish. The same evidence base powers internal certification readiness, so you're not maintaining two separate programs. Scope your ISMS, upload what you already have, and the platform tells you what's missing and what still needs an owner. Covers ISO 27001:2022, SOC 2, GDPR, NIS2, DORA and the Cyber Resilience Act. Includes a vendor library of 10,000+ pre-monitored suppliers, an asset register, access reviews, a risk register, and audit-ready evidence packs you can hand straight to an assessor. Pricing is published, from $149/month. No sales call required to find out what it costs.
