Best Enterprise Security Information and Event Management (SIEM) Software

How Many Security Information and Event Management (SIEM) Software Products Does G2 Track?

Total Products under this Category: 153

Category Stats (Nov 2026)

  • Average Rating: 4.47/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Singularity AI SIEM (+2.27%) - Among all products in this category, Singularity AI SIEM recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Security Information and Event Management (SIEM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,600+ Authentic Reviews
  • 153+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

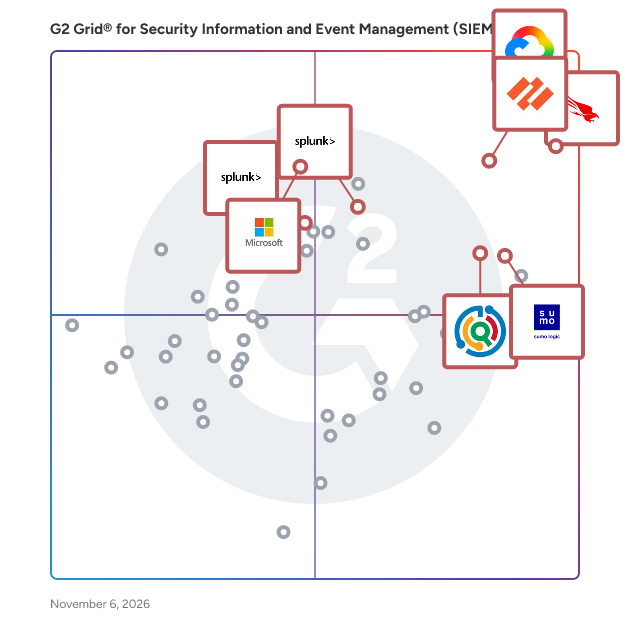
G2 Grid® for Security Information and Event Management (SIEM) Software

G2 Grid® for Security Information and Event Management (SIEM) Software plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Google Security Operations, Palo Alto Cortex XSIAM, Sumo Logic, Splunk Enterprise Security, Microsoft Sentinel, ManageEngine ADAudit Plus, and Splunk Enterprise.

Underlying data: [Grid® JSON](https://www.g2.com/categories/security-information-and-event-management-siem/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=google-security-operations&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=sumo-logic&focus%5B%5D=splunk-enterprise-security&focus%5B%5D=microsoft-sentinel&focus%5B%5D=manageengine-adaudit-plus&focus%5B%5D=splunk-enterprise&segment=enterprise)

CrowdStrike Falcon Endpoint Protection Platform

Organizations today face a serious challenge: managing numerous security vendors and tools while confronting an ever-evolving threat landscape. Sophisticated adversaries are becoming smarter, faster, and more evasive, launching complex attacks that can strike in minutes or even seconds. Traditional security approaches struggle to keep pace, leaving businesses vulnerable. The CrowdStrike Falcon Platform addresses this by offering a unified, cloud-native solution. It consolidates previously siloed security solutions and incorporates third-party data into a single platform with one efficient and resource-conscious agent, leveraging advanced AI and real-time threat intelligence. This approach simplifies security operations, speeds analyst decision making, and enhances protection to stop the breach, allowing organizations to reduce risk with less complexity and lower costs. CrowdStrike's Falcon Platform includes: - Endpoint Security: Secure the endpoint, stop the breach - Identify Protection: Identity is the front line, defend it - Next-Gen SIEM: The future of SIEM, today - Data Protection: Real-time data protection from endpoint to cloud - Exposure Management: Understand risk to stop breaches - Charlotte AI: Powering the next evolution of the SOC

Average Rating: 4.7/5.0

Total Reviews: 633

How Do G2 Users Rate CrowdStrike Falcon Endpoint Protection Platform?

  • Activity Monitoring: 9.5/10 (Category avg: 9.2/10)
  • Data Examination: 8.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.8/10)
  • Log Management: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind CrowdStrike Falcon Endpoint Protection Platform?

  • Seller: CrowdStrike
  • Company Website:
  • Year Founded: 2011
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    21,058 employees on LinkedIn®
  • Ownership: NASDAQ: CRWD

Who Uses This Product?

  • Who Uses This: Security Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 49% Large, 37% Medium

What Do G2 Reviewers Say About CrowdStrike Falcon Endpoint Protection Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the cloud-native architecture and effective features like workflow automation and asset management in CrowdStrike Falcon.
  • Users value the advanced threat detection capabilities of CrowdStrike Falcon, enhancing security and streamlining response efforts.
  • Users value the ease of use of CrowdStrike Falcon, benefiting from its lightweight agent and intuitive interface.
  • Users appreciate the robust security features of CrowdStrike Falcon, enhancing endpoint protection and system performance.
  • Users praise the superior detection capabilities of CrowdStrike Falcon, consistently delivering reliable and swift responses.
Cons
  • Users find that CrowdStrike Falcon's high licensing cost can be burdensome, particularly for smaller teams and organizations.
  • Users express frustration over the complexity of CrowdStrike Falcon's management console and its steep learning curve.
  • Users find the steep learning curve of CrowdStrike Falcon challenging due to its complex management console.
  • Users face limited functionality in adding hash values to CrowdStrike Falcon, which restricts monitoring capabilities.
  • Users express concern over the high pricing of CrowdStrike Falcon, especially for smaller organizations.

What Are Recent G2 Reviews of CrowdStrike Falcon Endpoint Protection Platform?

What Are G2 Users Discussing About CrowdStrike Falcon Endpoint Protection Platform?

Google Security Operations

Google Security Operations offers a unified experience across SIEM, SOAR, and threat intelligence to drive better detection, investigation, and response. Collect security telemetry data, apply threat intel to identify high priority threats, drive response with playbook automation, case management, and collaboration. It also provides Gemini-native agentic defense to help autonomously handle workflows like alert triage, threat hunting, and detection engineering. Google Security Operations also supports AI Threat Defense to monitor, detect, and respond to threats from code you do not own or cannot patch.

Average Rating: 4.4/5.0

Total Reviews: 125

How Do G2 Users Rate Google Security Operations?

  • Activity Monitoring: 9.8/10 (Category avg: 9.2/10)
  • Data Examination: 9.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.5/10 (Category avg: 8.8/10)
  • Log Management: 9.3/10 (Category avg: 9.2/10)

Who Is the Company Behind Google Security Operations?

  • Seller: Google
  • Year Founded: 1998
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    301,144 employees on LinkedIn®
  • Ownership: NASDAQ:GOOG
  • Phone: +1 (650) 253-0000

Who Uses This Product?

  • Who Uses This: Developer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 37% Medium, 35% Small

What Do G2 Reviewers Say About Google Security Operations?

AI-generated summary from verified user reviews

Pros
  • Users value the centralized detection and investigation capabilities of Google Security Operations for efficient threat management.
  • Users appreciate the scalability and efficiency of Google Security Operations for effective threat detection and response.
  • Users find Google Security Operations to have a user-friendly interface, enabling quick analysis and effective threat responses.
  • Users value the comprehensive security capabilities of Google Security Operations for effective threat detection and response.
  • Users appreciate the seamless integrations of Google Security Operations, enhancing threat detection and data analysis across the ecosystem.
Cons
  • Users feel that the high cost of Google Security Operations is a significant drawback affecting overall satisfaction.
  • Users find a steep learning curve when trying to utilize Google Security Operations effectively, especially for the inexperienced.
  • Users find the implementation complexity of Google Security Operations challenging, requiring significant time and resources to manage.
  • Users find the learning difficulty of Google Security Operations challenging, requiring substantial time to master its features.
  • Users find limited customization in Google Security Operations hinders adaptability to specific security requirements and user-friendliness.

What Are Recent G2 Reviews of Google Security Operations?

Palo Alto Cortex XSIAM

Product Description: Palo Alto Networks' Cortex XSIAM is an AI-driven security operations platform designed to transform traditional Security Operations Centers by integrating and automating key functions such as data centralization, threat detection, and incident response. By leveraging machine learning and automation, it enables organizations to detect and respond to threats more efficiently, reducing manual workloads and improving overall security posture. Key Features and Functionality: - Data Centralization: Aggregates data from various sources into a unified platform, providing comprehensive visibility across the enterprise. - AI-Powered Threat Detection: Utilizes machine learning algorithms to identify anomalies and potential threats in real-time. - Automated Incident Response: Streamlines response processes through automation, enabling rapid mitigation of security incidents. - Integrated SOC Capabilities: Combines functions such as Extended Detection and Response , Security Orchestration, Automation, and Response , Attack Surface Management , and Security Information and Event Management into a cohesive platform, eliminating the need for multiple disparate tools. - Scalability: Designed to handle large volumes of data and adapt to the evolving needs of modern enterprises. Primary Value and Problem Solved: Cortex XSIAM addresses the challenges of disjointed data, weak threat defense, and heavy reliance on manual work in traditional SOCs. By centralizing data and automating security operations, it simplifies processes, enhances threat detection accuracy, and accelerates incident response times. This transformation enables organizations to proactively outpace threats, reduce operational costs, and achieve a more robust security posture.

Average Rating: 4.4/5.0

Total Reviews: 108

How Do G2 Users Rate Palo Alto Cortex XSIAM?

  • Activity Monitoring: 9.5/10 (Category avg: 9.2/10)
  • Data Examination: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.7/10 (Category avg: 8.8/10)
  • Log Management: 9.5/10 (Category avg: 9.2/10)

Who Is the Company Behind Palo Alto Cortex XSIAM?

  • Seller: Palo Alto Networks
  • Company Website:
  • Year Founded: 2005
  • HQ Location: Santa Clara, CA
  • LinkedIn® Page: www.linkedin.com
    23,492 employees on LinkedIn®
  • Ownership: NYSE: PANW

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 38% Large, 36% Medium

What Do G2 Reviewers Say About Palo Alto Cortex XSIAM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Palo Alto Cortex XSIAM, benefiting from its intuitive interface and seamless integration.
  • Users value the advanced threat detection capabilities of Palo Alto Cortex XSIAM, ensuring both known and unknown threats are managed effectively.
  • Users value the seamless integrations of Palo Alto Cortex XSIAM, enhancing overall functionality across various platforms.
  • Users value the unified console of Palo Alto Cortex XSIAM for simplifying security management across endpoints, network, and cloud.
  • Users value the single console integration, highlighting its ease of use and reliability for threat detection.
Cons
  • Users find the Cortex XSIAM to be very expensive compared to other solutions, impacting overall satisfaction.
  • Users find the difficult learning curve of Palo Alto Cortex XSIAM a challenge due to its complexity and setup.
  • Users find the complexity of the console overwhelming, requiring significant time and expertise to navigate effectively.
  • Users report integration issues with Palo Alto Cortex XSIAM, facing challenges with non-native equipment and log maintenance.
  • Users find the UX improvement of Palo Alto Cortex XSIAM lacking in customization and intuitive design for features.

What Are Recent G2 Reviews of Palo Alto Cortex XSIAM?

What Are G2 Users Discussing About Palo Alto Cortex XSIAM?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Sumo Logic

Sumo Logic, Inc. unifies and analyzes enterprise data, translating it into actionable insights through one AI-powered cloud-native log analytics platform. This single source of truth enables Dev, Sec and Ops teams to simplify complexity, collaborate efficiently and accelerate data-driven decisions that drive business value. Customers around the world rely on the Sumo Logic SaaS Log Analytics Platform for trusted insights to ensure application reliability, secure and protect against modern security threats, and gain insights into their cloud infrastructures. For more information, visit: SUMOLOGIC.COM

Average Rating: 4.4/5.0

Total Reviews: 411

How Do G2 Users Rate Sumo Logic?

  • Activity Monitoring: 9.2/10 (Category avg: 9.2/10)
  • Data Examination: 9.0/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.4/10 (Category avg: 9.2/10)

Who Is the Company Behind Sumo Logic?

  • Seller: Sumo Logic
  • Company Website:
  • Year Founded: 2010
  • HQ Location: Redwood City, CA
  • LinkedIn® Page: www.linkedin.com
    824 employees on LinkedIn®
  • Ownership: NASDAQ: SUMO

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 48% Medium, 38% Large

What Do G2 Reviewers Say About Sumo Logic?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use in Sumo Logic, enabling quick insights from data without complexity.
  • Users commend the powerful and accessible log management features of Sumo Logic, enhancing efficiency and visualization capabilities.
  • Users value the flexible analytics and powerful real-time features of Sumo Logic, enhancing collaboration and operational visibility.
  • Users value the real-time monitoring capabilities of Sumo Logic, enabling quick insights and effective data visualization.
  • Users value the powerful and accessible analytics of Sumo Logic, enhancing their data visualization and decision-making capabilities.
Cons
  • Users find the difficult learning curve of Sumo Logic challenging, especially transitioning from simpler tools.
  • Users face a steeper learning curve with Sumo Logic, especially when transitioning from tools like Splunk or Elastic.
  • Users note a steep learning curve with Sumo Logic that may challenge teams transitioning from other tools.
  • Users find Sumo Logic expensive, especially if data tiers are misconfigured, leading to unexpected high bills.
  • Users experience slow performance with Sumo Logic, facing delays and lag during queries, especially with large datasets.

What Are Recent G2 Reviews of Sumo Logic?

What Are G2 Users Discussing About Sumo Logic?

Splunk Enterprise Security

Splunk Enterprise Security (ES) is a data-centric, modern security information and event management (SIEM) solution that delivers data-driven insights for full breadth visibility into your security posture so you can protect your business and mitigate risk at scale. With unparalleled search and reporting, advanced analytics, integrated intelligence, and prepackaged security content, Splunk ES accelerates threat detection and investigation, letting you determine the scope of high-priority threats to your environment so you can quickly take action. Built on an open and scalable data platform, you can stay agile in the face of evolving threats and business needs. Our extensive ecosystem of Splunk, partner, and community-built integrations as well as flexible deployment options ensure your technology investments are working in tandem with Splunk ES whilst meeting you wherever you are on your cloud, multi-cloud, or hybrid journey.

Average Rating: 4.3/5.0

Total Reviews: 226

How Do G2 Users Rate Splunk Enterprise Security?

  • Activity Monitoring: 8.8/10 (Category avg: 9.2/10)
  • Data Examination: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.3/10 (Category avg: 9.2/10)

Who Is the Company Behind Splunk Enterprise Security?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 60% Large, 30% Medium

What Do G2 Reviewers Say About Splunk Enterprise Security?

AI-generated summary from verified user reviews

Pros
  • Users value the powerful log analytics of Splunk Enterprise Security, enhancing their ability to analyze and correlate logs effectively.
  • Users benefit from the smart threat detection of Splunk Enterprise Security, enabling early identification of security issues.
  • Users value the extensive integration options of Splunk Enterprise Security, enhancing their existing Splunk investments and workflows.
  • Users value the versatility in data handling of Splunk Enterprise Security, enhancing insights and decision-making across domains.
  • Users appreciate the real-time monitoring capabilities of Splunk Enterprise Security, enhancing their cybersecurity responsiveness and decision-making.
Cons
  • Users find the complex setup of Splunk Enterprise Security time-consuming and challenging, impacting initial deployment effectiveness.
  • Users find the difficult learning curve of Splunk Enterprise Security challenging, especially for those new to data analysis.
  • Users often cite high costs at scale as a significant drawback, especially with growing data ingestion needs.
  • Users express concerns about poor customer support, highlighting the need for more responsive assistance and resources.
  • Users often face setup difficulties with Splunk Enterprise Security, requiring significant time and resources for configuration.

What Are Recent G2 Reviews of Splunk Enterprise Security?

What Are G2 Users Discussing About Splunk Enterprise Security?

Microsoft Sentinel

Microsoft Sentinel lets you see and stop threats before they cause harm, with SIEM reinvented for a modern world. Microsoft Sentinel is your birds-eye view across the enterprise. Put the cloud and large-scale intelligence from decades of Microsoft security experience to work. Make your threat detection and response smarter and faster with artificial intelligence (AI). Eliminate security infrastructure setup and maintenance, and elastically scale to meet your security needs—while reducing IT costs. With Microsoft Sentinel, you can: - Collect data at cloud scale—across all users, devices, applications, and infrastructure, both on-premises and in multiple clouds - Detect previously uncovered threats and minimize false positives using analytics and unparalleled threat intelligence from Microsoft - Investigate threats with AI and hunt suspicious activities at scale, tapping into decades of cybersecurity work at Microsoft -Respond to incidents rapidly with built-in orchestration and automation of common tasks

Average Rating: 4.4/5.0

Total Reviews: 275

How Do G2 Users Rate Microsoft Sentinel?

  • Activity Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Data Examination: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.5/10 (Category avg: 8.8/10)
  • Log Management: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Microsoft Sentinel?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Who Uses This: Senior Software Engineer, Security Analyst
  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 42% Large, 31% Medium

What Do G2 Reviewers Say About Microsoft Sentinel?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time monitoring of Microsoft Sentinel, gaining enhanced visibility and streamlined incident handling across their systems.
  • Users appreciate the effective alerting of Microsoft Sentinel, enhancing security through automated responses to unusual activities.
  • Users value the seamless dashboard usability of Microsoft Sentinel, enhancing their security management and threat response efficiency.
  • Users value the fast and secure threat response of Microsoft Sentinel, enhancing their security and alert management.
  • Users value the centralized data collection feature of Microsoft Sentinel, enhancing security analytics and threat visibility.
Cons
  • Users find the cloud dependency of Microsoft Sentinel challenging, making custom reporting and integration cumbersome.
  • Users find the complex configuration of Microsoft Sentinel challenging, often requiring extensive documentation and exploration.
  • Users find configuration issues in Microsoft Sentinel challenging, requiring time, effort, and technical expertise to navigate.
  • Users find the difficult setup of Microsoft Sentinel frustrating, often requiring extensive documentation exploration for configuration.
  • Users find the poor interface design of Microsoft Sentinel challenging, making navigation and understanding features difficult.

What Are Recent G2 Reviews of Microsoft Sentinel?

What Are G2 Users Discussing About Microsoft Sentinel?

ManageEngine ADAudit Plus

ADAudit Plus is a UBA-driven auditor that helps keep your AD, Azure AD, file systems (including Windows, NetApp, EMC, Synology, Hitachi, and Huawei), Windows servers, and workstations secure and compliant. ADAudit Plus transforms raw and noisy event log data into real-time reports and alerts, enabling you to get full visibility into activities happening across your Windows Server ecosystem in just a few clicks. More than 10,000 organizations across the world trust ADAudit Plus to: 1. Instantly notify them about changes in their Windows Server environments. 2. Continuously track Windows user logon activity. 3. Monitor the active and idle time spent by employees at their workstations. 4. Detect and troubleshoot AD account lockouts. 5. Provide a consolidated audit trail of privileged user activities across their domains. 6. Track changes and sign-ins in Azure AD. 7. Audit file accesses across Windows, NetApp, EMC, Synology, Hitachi, and Huawei file systems. 8. Monitor file integrity across local files residing on Windows systems. 9. Mitigate insider threats by leveraging UBA and response automation. 10. Generate audit-ready compliance reports for SOX, the GDPR, and other IT mandates.

Average Rating: 4.6/5.0

Total Reviews: 63

How Do G2 Users Rate ManageEngine ADAudit Plus?

  • Activity Monitoring: 9.4/10 (Category avg: 9.2/10)
  • Data Examination: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.8/10 (Category avg: 8.8/10)
  • Log Management: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind ManageEngine ADAudit Plus?

  • Seller: Zoho
  • Year Founded: 1996
  • HQ Location: Austin, TX
  • LinkedIn® Page: www.linkedin.com
    30,913 employees on LinkedIn®
  • Phone: +1 (888) 900-9646

Who Uses This Product?

  • Top Industries: Hospital & Health Care, Information Technology and Services
  • Company Size: 59% Medium, 32% Large

What Do G2 Reviewers Say About ManageEngine ADAudit Plus?

AI-generated summary from verified user reviews

Pros
  • Users value the depth of visibility and comprehensive reporting offered by ManageEngine ADAudit Plus for AD auditing.
  • Users appreciate the intuitive dashboard usability of ManageEngine ADAudit Plus, facilitating easy navigation and comprehensive insights.
  • Users appreciate the ease of setup and comprehensive reporting features of ManageEngine ADAudit Plus for effective monitoring.
  • Users appreciate the intuitive dashboard design of ADAudit Plus, providing a comprehensive overview of their Active Directory environment.
  • Users find the intuitive dashboard and extensive reporting options of ADAudit Plus highly beneficial for Active Directory management.
Cons
  • Users find the limited alert levels in ADAudit Plus restrictive, wishing for more options to fine-tune notifications.
  • Users find the data overload daunting, making it difficult to locate specific reports without prior knowledge.
  • Users feel the product is expensive considering the trade-off with support and language clarity.
  • Users experience false positives in alerts, which can lead to confusion and the need for better severity options.
  • Users are frustrated by the high resource usage of ManageEngine ADAudit Plus, impacting system performance significantly.

What Are Recent G2 Reviews of ManageEngine ADAudit Plus?

What Are G2 Users Discussing About ManageEngine ADAudit Plus?

Splunk Enterprise

Find out what is happening in your business and take meaningful action quickly with Splunk Enterprise. Automate the collection, indexing and alerting of machine data that's critical to your operations. Uncover the actionable insights from all your data — no matter the source or format. Leverage artificial intelligence and machine learning for predictive and proactive business decisions.

Average Rating: 4.3/5.0

Total Reviews: 415

How Do G2 Users Rate Splunk Enterprise?

  • Activity Monitoring: 9.1/10 (Category avg: 9.2/10)
  • Data Examination: 8.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.3/10 (Category avg: 9.2/10)

Who Is the Company Behind Splunk Enterprise?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Who Uses This: Software Engineer, Senior Software Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 64% Large, 28% Medium

What Do G2 Reviewers Say About Splunk Enterprise?

AI-generated summary from verified user reviews

Pros
  • Users value the innovation in data handling that Splunk Enterprise offers, enhancing insights and integration capabilities.
  • Users value the highly customizable dashboards in Splunk Enterprise, enhancing data visualization and insights significantly.
  • Users find Splunk Enterprise to be easy to use, with intuitive dashboards and simple setup for configurations.
  • Users find Splunk Enterprise's end-to-end log management essential for effective observability and IT infrastructure management.
  • Users appreciate the robust reporting features of Splunk Enterprise, allowing for customizable log insights and dynamic dashboards.
Cons
  • Users find Splunk Enterprise expensive, especially with growing data volumes and high renewal costs affecting affordability.
  • Users find the learning curve steep for Splunk Enterprise, requiring formal training to navigate its complexities effectively.
  • Users find the licensing costs and model of Splunk Enterprise challenging and complicated, impacting sales and usability.
  • Users find integration issues with Splunk Enterprise, noting limitations and delays in data display and onboarding options.
  • Users find the limited integration capabilities of Splunk Enterprise frustrating, especially after the recent version update.

What Are Recent G2 Reviews of Splunk Enterprise?

What Are G2 Users Discussing About Splunk Enterprise?

Datadog

Datadog is the monitoring, security and analytics platform for developers, IT operations teams, security engineers and business users in the cloud age. The SaaS platform integrates and automates infrastructure monitoring, application performance monitoring and log management to provide unified, real-time observability of our customers' entire technology stack. Datadog is used by organizations of all sizes and across a wide range of industries to enable digital transformation and cloud migration, drive collaboration among development, operations, security and business teams, accelerate time to market for applications, reduce time to problem resolution, secure applications and infrastructure, understand user behavior and track key business metrics.

Average Rating: 4.4/5.0

Total Reviews: 738

How Do G2 Users Rate Datadog?

  • Activity Monitoring: 8.9/10 (Category avg: 9.2/10)
  • Data Examination: 8.6/10 (Category avg: 8.7/10)
  • Ease of Use: 8.2/10 (Category avg: 8.8/10)
  • Log Management: 9.5/10 (Category avg: 9.2/10)

Who Is the Company Behind Datadog?

  • Seller: Datadog
  • Company Website:
  • Year Founded: 2010
  • HQ Location: New York
  • LinkedIn® Page: www.linkedin.com
    10,780 employees on LinkedIn®
  • Ownership: NASDAQ: DDOG

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 46% Medium, 33% Large

What Do G2 Reviewers Say About Datadog?

AI-generated summary from verified user reviews

Pros
  • Users value a unified observability view that brings logs, metrics, and traces together for easier monitoring and insights.
  • Users value clear, customizable dashboards that make relevant data easy to visualize and understand.
  • Users value unified visibility across applications, infrastructure, and services, helping them understand overall system health.
  • Users find the interface intuitive and easy to use, helping them navigate monitoring and streamline everyday operations.
  • Users value its broad integrations across cloud services and existing systems, with straightforward setup that connects their tools.
Cons
  • Users say costs are high and can rise quickly as infrastructure, data volume, and monitored services scale.
  • Users find the learning curve steep, with advanced features, queries, and dashboards taking time to master.
  • Users find the interface crowded with information and controls, making it feel overwhelming, especially at first.
  • Users find costs difficult to predict, track, and control, especially as usage and monitored environments scale.
  • Users find navigation confusing, with features and information difficult to locate across screens and dashboards.

What Are Recent G2 Reviews of Datadog?

What Are G2 Users Discussing About Datadog?

Check Point Infinity Platform

Check Point Infinity is the only fully consolidated cyber security architecture that provides unprecedented protection against Gen V mega-cyber attacks as well as future cyber threats across all networks, endpoint, cloud and mobile. The architecture is designed to resolve the complexities of growing connectivity and inefficient security.

Average Rating: 4.6/5.0

Total Reviews: 109

How Do G2 Users Rate Check Point Infinity Platform?

  • Ease of Use: 9.1/10 (Category avg: 8.8/10)

Who Is the Company Behind Check Point Infinity Platform?

Who Uses This Product?

  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 44% Large, 37% Medium

What Do G2 Reviewers Say About Check Point Infinity Platform?

AI-generated summary from verified user reviews

Pros
  • Users commend the advanced security features of Check Point Infinity Platform, effectively preventing future attacks on cloud infrastructures.
  • Users value the cloud security features of Check Point Infinity Platform for efficient audits and infrastructure evaluations.
  • Users commend the proactive threat detection of Check Point Infinity Platform, enhancing security for cloud applications.
  • Users highlight the comprehensive security features of Check Point Infinity Platform, effectively shielding against future attacks.
  • Users value the advanced security features of Check Point Infinity for effectively safeguarding their cloud infrastructure.
Cons
  • Users find the steep learning curve of Check Point Infinity Platform challenging due to its complexity and extensive features.
  • Users find the complex setup process for Check Point Infinity Platform can be time-consuming and confusing at times.
  • Users feel that improvement is needed in real-time support and custom ruleset creation for better functionality.
  • Users express concerns about poor support services, indicating a need for improvement in customer assistance and log visibility.
  • Users find the limited customization options challenging, affecting their ability to tailor the platform to their needs.

What Are Recent G2 Reviews of Check Point Infinity Platform?

What Are G2 Users Discussing About Check Point Infinity Platform?

Panther

Panther is the AI SOC Platform that scales security expertise by embedding AI agents across your security operations with native access to your data lake, detection logic, and organizational knowledge. Unlike bolt-on tools, Panther's closed-loop architecture turns every alert into compounding intelligence that makes the system smarter over time. Request a demo today at: https://panther.com/product/request-a-demo/

Average Rating: 4.7/5.0

Total Reviews: 49

How Do G2 Users Rate Panther?

  • Activity Monitoring: 9.3/10 (Category avg: 9.2/10)
  • Data Examination: 9.4/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.8/10)
  • Log Management: 9.7/10 (Category avg: 9.2/10)

Who Is the Company Behind Panther?

Who Uses This Product?

  • Who Uses This: Senior Security Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 53% Medium, 29% Large

What Do G2 Reviewers Say About Panther?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the responsive customer support of Panther, providing detailed guidance and efficient issue resolution.
  • Users commend Panther for its excellent detection efficiency, making SecOps seamless and effective with purposeful features.
  • Users praise Panther for its ease of use, allowing even small teams to operate efficiently with intuitive features.
  • Users love Panther's purposeful features, seamless log onboarding, and top-notch AI capabilities for effective SecOps.
  • Users value the easy integrations with various log sources, enhancing their operational efficiency and effectiveness.
Cons
  • Users find the alert management limited due to lack of customization and the need for extensive configuration.
  • Users find the complex configuration of Panther challenging, requiring extensive setup for effective integration and usability.
  • Users report dashboard issues with Panther, citing limitations in customization and maturity of features for security analysis.
  • Users find Panther's limited access cumbersome, with challenges in integration, dashboards, and customizable alert features.
  • Users note a difficult learning curve for Panther, especially for those not familiar with programming languages.

What Are Recent G2 Reviews of Panther?

What Are G2 Users Discussing About Panther?

Rapid7 Next-Gen SIEM

Rapid7 InsightIDR is a SaaS SIEM for modern threat detection and response. InsightIDR enables security analysts to work more efficiently and effectively, by unifying diverse data sources, providing early and reliable out of the box detections, and delivering rich visual investigations and automation to expedite response. With a lightweight cloud deployment and intuitive UI and onboarding experience, InsightIDR customers recognize an accelerated return on their investment and start seeing valuable insights from Day 1. With InsightIDR, teams can advance their threat detection and response program without adding headcount.

Average Rating: 4.4/5.0

Total Reviews: 69

How Do G2 Users Rate Rapid7 Next-Gen SIEM?

  • Activity Monitoring: 9.3/10 (Category avg: 9.2/10)
  • Data Examination: 8.6/10 (Category avg: 8.7/10)
  • Ease of Use: 8.9/10 (Category avg: 8.8/10)
  • Log Management: 9.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Rapid7 Next-Gen SIEM?

  • Seller: Rapid7
  • Year Founded: 2000
  • HQ Location: Boston, MA
  • LinkedIn® Page: www.linkedin.com
    8,746 employees on LinkedIn®
  • Ownership: NASDAQ:RPD
  • Total Revenue (USD mm): $411

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer Software
  • Company Size: 67% Medium, 30% Large

What Do G2 Reviewers Say About Rapid7 Next-Gen SIEM?

AI-generated summary from verified user reviews

Pros
  • Users commend the ease of use of Rapid7 Next-Gen SIEM for its intuitive implementation and clear alerts.
  • Users appreciate the easy integrations with third-party tools, enhancing the overall usability of Rapid7 Next-Gen SIEM.
  • Users appreciate the pre-built integrations of Rapid7 Next-Gen SIEM, facilitating easy connections with various third-party tools.
  • Users value the seamless integration of UEBA and deception tools, enhancing threat detection and speeding up investigations.
  • Users appreciate the visibility provided by Rapid7 Next-Gen SIEM, enabling easy log searching and clear alerting.
Cons
  • Users find the limited features of Rapid7 Next-Gen SIEM restrictive, hindering efficient alert creation and setup.
  • Users face challenges with limited alerting capabilities, making it hard to create effective and timely alerts.
  • Users find the limited alert management functionality challenging, particularly in creating and setting up pattern-based alerts.
  • Users find the difficult customization of Rapid7 Next-Gen SIEM hinders their ability to set effective alerts.
  • Users find the difficult setup of Rapid7 Next-Gen SIEM frustrating, especially with creating alerts effectively.

What Are Recent G2 Reviews of Rapid7 Next-Gen SIEM?

What Are G2 Users Discussing About Rapid7 Next-Gen SIEM?

Coralogix

Coralogix is a modern, full-stack observability platform transforming how businesses process and understand their data. Our unique architecture powers in-stream analytics without reliance on indexing or hot storage. We specialize in comprehensive monitoring of logs, metrics, trace and security events, enhancing operational efficiency and reducing total cost of ownership by up to 70%. Coralogix stands out for its simple pricing model, based solely on data volume ingested and retained, and offers free, fast customer support with less than 30 second response time and 1 hour resolution time. Our platform covers the entire range of observability with features such as APM, RUM, SIEM, Kubernetes monitoring and more, all streamlined for quick integration and immediate value. Components within the stream store the system state to provide stateful insights and real-time alerting without ever needing to index the data — so there are never any trade-offs to achieve observability. Once ingested, parsed, and enriched, data is written remotely to an archive bucket controlled by the client. The archive can be queried directly at any time, from the platform UI or via CLI, giving users infinite retention with full control over, and access to, their data. View and query your data from any dashboard using any syntax. Coralogix has successfully completed relevant security and privacy compliances by BDO including GDPR, SOC 2, PCI, HIPAA, and ISO 27001/27701.

Average Rating: 4.5/5.0

Total Reviews: 452

How Do G2 Users Rate Coralogix?

  • Activity Monitoring: 8.7/10 (Category avg: 9.2/10)
  • Data Examination: 8.5/10 (Category avg: 8.7/10)
  • Ease of Use: 8.7/10 (Category avg: 8.8/10)
  • Log Management: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Coralogix?

  • Seller: Coralogix
  • Company Website:
  • Year Founded: 2014
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    609 employees on LinkedIn®

Who Uses This Product?

  • Who Uses This: Software Engineer, DevOps Engineer
  • Top Industries: Computer Software, Information Technology and Services
  • Company Size: 56% Medium, 33% Large

What Do G2 Reviewers Say About Coralogix?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the ease of use of Coralogix, highlighting its simple setup and efficient integrations.
  • Users value the integration of logs, metrics, and alerts, enhancing efficiency in root-cause analysis and monitoring.
  • Users commend the exceptional customer support of Coralogix, ensuring quick resolutions and a smooth experience.
  • Users value the real-time monitoring of Coralogix, enhancing their understanding of user behavior and improving incident response.
  • Users value the intuitive user interface of Coralogix, appreciating its ease of log searching and export functionality.
Cons
  • Users find that the learning curve is steep for beginners, making navigation and understanding features challenging.
  • Users find the missing feature for downloading log results a significant limitation in Coralogix's functionality.
  • Users find the difficult learning curve of Coralogix challenging, especially for beginners navigating complex options.
  • Users experience slow performance with Coralogix, leading to frustration due to delayed log fetching and UI loading.
  • Users find the learning difficulty of Coralogix challenging, especially when navigating advanced features and the overwhelming UI.

What Are Recent G2 Reviews of Coralogix?

IBM QRadar SIEM

Outsmart threats with an end-to-end award-winning security suite; proven to prevent, endure and recover from both known & unknown IT hazards faced by SoCs in the modern-day.

Average Rating: 4.4/5.0

Total Reviews: 285

How Do G2 Users Rate IBM QRadar SIEM?

  • Activity Monitoring: 8.7/10 (Category avg: 9.2/10)
  • Data Examination: 8.3/10 (Category avg: 8.7/10)
  • Ease of Use: 8.4/10 (Category avg: 8.8/10)
  • Log Management: 8.8/10 (Category avg: 9.2/10)

Who Is the Company Behind IBM QRadar SIEM?

  • Seller: IBM
  • Year Founded: 1911
  • HQ Location: Armonk, New York, United States
  • LinkedIn® Page: www.linkedin.com
    344,328 employees on LinkedIn®
  • Ownership: SWX:IBM
  • Phone: 1-866-277-7488

Who Uses This Product?

  • Who Uses This: Security Engineer, SOC Analyst
  • Top Industries: Computer & Network Security, Information Technology and Services
  • Company Size: 52% Large, 29% Medium

What Do G2 Reviewers Say About IBM QRadar SIEM?

AI-generated summary from verified user reviews

Pros
  • Users value the intuitive user interface of IBM QRadar SIEM, enhancing ease of use for all experience levels.
  • Users appreciate the seamless integration capabilities of IBM QRadar SIEM, enhancing data management and reporting efficiency.
  • Users appreciate the user-friendly dashboard of IBM QRadar SIEM, enhancing ease of use and customization.
  • Users value the easy integrations of IBM QRadar SIEM, enhancing functionality with seamless API and SaaS connections.
  • Users appreciate the intuitive user interface of IBM QRadar SIEM, which simplifies navigation for less experienced users.
Cons
  • Users find the UI improvements unsatisfactory, noting limitations in features, search capabilities, and report building.
  • Users find the product expensive, especially when increasing EPS and managing costs for maintenance and features.
  • Users find the cost of implementing QRadar SIEM to be high, particularly for smaller organizations, affecting accessibility.
  • Users struggle with dashboard issues in QRadar, experiencing inefficiencies and limited functionality in the user interface.
  • Users find the initial setup time-consuming, requiring significant expertise and effort to customize for their needs.

What Are Recent G2 Reviews of IBM QRadar SIEM?

FortiSIEM

The complexity of managing network and security operations is resulting in increases in breaches worldwide. Discovery, isolation, and remediation of these incidents are measured in hundreds of days. And with a dwindling pool of skilled cyber security personnel able to manage the wide array of devices and data sources to protect their network assets, success requires a new approach. FortiSIEM provides organizations of all sizes with a comprehensive, holistic, and scalable solution for security, performance, and compliance management, from IoT to the cloud. FortiSIEM expands network visibility through the Fortinet Security Fabric's integrations with the leading security products present in most networks today.

Average Rating: 4.3/5.0

Total Reviews: 40

How Do G2 Users Rate FortiSIEM?

  • Activity Monitoring: 8.7/10 (Category avg: 9.2/10)
  • Data Examination: 7.9/10 (Category avg: 8.7/10)
  • Ease of Use: 8.6/10 (Category avg: 8.8/10)
  • Log Management: 8.7/10 (Category avg: 9.2/10)

Who Is the Company Behind FortiSIEM?

  • Seller: Fortinet
  • Year Founded: 2000
  • HQ Location: Sunnyvale, CA
  • LinkedIn® Page: www.linkedin.com
    16,564 employees on LinkedIn®
  • Ownership: NASDAQ: FTNT
  • Total Revenue (USD mm): $2,594

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 46% Medium, 29% Large

What Do G2 Reviewers Say About FortiSIEM?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the real-time visibility of FortiSIEM, enhancing threat detection and troubleshooting across their infrastructure.
  • Users value the single-pane-of-glass visibility of FortiSIEM, enhancing real-time threat detection and troubleshooting efficiency.
  • Users value the real-time threat detection capabilities of FortiSIEM, enhancing their ability to troubleshoot effectively.
  • Users value the real-time visibility of FortiSIEM for efficient troubleshooting and faster threat detection across their infrastructure.
  • Users value the real-time visibility of FortiSIEM, enhancing threat detection and troubleshooting across their infrastructure.
Cons
  • Users find the initial setup and configuration complex, creating challenges in effectively using FortiSIEM.
  • Users find the complex setup of FortiSIEM challenging, often needing time to master the interface and reporting features.
  • Users find the difficult customization of FortiSIEM challenging, requiring a steep learning curve for effective use.
  • Users find the learning curve for setup and customization of FortiSIEM to be complex and challenging, especially for advanced features.
  • Users find the poor interface design of FortiSIEM challenging, making initial setup and customization more complex.

What Are Recent G2 Reviews of FortiSIEM?

What Are G2 Users Discussing About FortiSIEM?

Brandon Summers-Miller
BS
Researched and written by Brandon Summers-Miller
Updated