Best Extended Detection and Response (XDR) Platforms - Page 4

How Many Extended Detection and Response (XDR) Platforms Products Does G2 Track?

Total Products under this Category: 113

Category Stats (Nov 2026)

  • Average Rating: 4.55/5 (↑0.01 vs Oct 2026) The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Eye Security (+8.95%) - Among all products in this category, Eye Security recorded the largest rating increase compared to last month

Last updated: November 02, 2026

How Does G2 Rank Extended Detection and Response (XDR) Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 6,900+ Authentic Reviews
  • 113+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

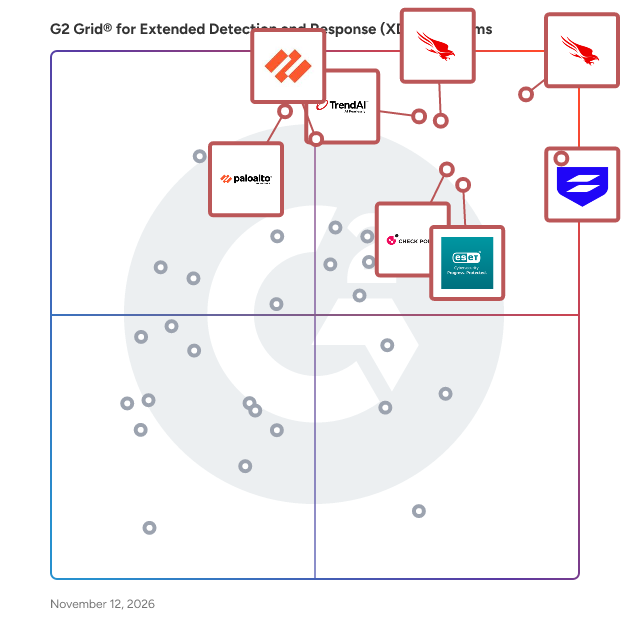
G2 Grid® for Extended Detection and Response (XDR) Platforms

G2 Grid® for Extended Detection and Response (XDR) Platforms plotting products by satisfaction and market presence

Highlighted products: CrowdStrike Falcon Endpoint Protection Platform, Sophos Endpoint, CrowdStrike Falcon Cloud Security, TrendAI Vision One, Check Point Endpoint Security, ESET PROTECT, Palo Alto Cortex XSIAM, and Cortex XDR.

Underlying data: [Grid® JSON](https://www.g2.com/categories/extended-detection-and-response-xdr-platforms/grids.json?focus%5B%5D=crowdstrike-falcon-endpoint-protection-platform&focus%5B%5D=sophos-endpoint&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=trendai-vision-one&focus%5B%5D=check-point-endpoint-security&focus%5B%5D=eset-protect&focus%5B%5D=palo-alto-cortex-xsiam&focus%5B%5D=palo-alto-networks-cortex-xdr)

TXHunter

TXHunter is one of the most advanced XDR/EDR solution for endpoint security protection and threat forensic investigation. It has built-in sandbox for behavior analysis, patent pending ransomware detection and data restoring technology, compliances auditing automation, APT blocking, network traffic analysis and isolation, fast incidence responding, SOC automation, AV integration, IOC query and IOD analysis, proactive threat hunting, vulnerability scanning, and remote threat mitigation. It supports Windows, Linux, and Mac.

Average Rating: 4.6/5.0

Total Reviews: 4

How Do G2 Users Rate TXHunter?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind TXHunter?

Who Uses This Product?

  • Company Size: 40% Small, 20% Medium

What Are Recent G2 Reviews of TXHunter?

N-able Threat Hunting

N-able Threat Hunting is a cloud based tool that is designed to provide threat detection, threat analysis and response, and integrated compliance tools so Managed Service Providers (MSPs) and Managed Security Service Providers (MSSPs) can detect, respond, and report cyber-threats to their managed networks.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate N-able Threat Hunting?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 8.3/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 9.2/10 (Category avg: 8.8/10)

Who Is the Company Behind N-able Threat Hunting?

  • Seller: N-able
  • HQ Location: Morrisville, North Carolina
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of N-able Threat Hunting?

nPro AI

nPro AI is a sovereign security operations platform that unifies four engines (XDR, SIEM, DLP and NRTG enterprise network monitoring) in one agent and one console. It deploys on your own servers, including fully air-gapped environments, so security data never leaves infrastructure you control. XDR: Endpoint detection and response for Windows, Linux and macOS, with threat detection mapped to MITRE ATT&CK, threat hunting, ransomware and anti-malware protection, file integrity monitoring, vulnerability and patch management, and an automated Active Response engine that stops malicious processes and blocks connections in real time. SIEM: Collect logs from endpoints, servers, firewalls, network devices and cloud workloads (AWS, Azure, Docker, Kubernetes). Write custom rules or import Sigma, correlate events, enrich alerts with threat intelligence, and manage incidents with analyst notes and a full audit trail. DLP: Block sensitive data leaving via USB, cloud uploads and clipboard, control screen capture, monitor printing, and govern what staff share with generative AI tools. NRTG: Enterprise network and device monitoring with asset discovery and remote probes, in the same console as your security data. Built-in AI analyses threats and assists analysts with investigation and response. Compliance reports cover ISO 27001, PCI-DSS, GDPR and PDPA. The interface is available in English, Bahasa Malaysia and Bahasa Indonesia. Pricing is per agent, not per GB of logs ingested. The free Community edition covers up to 30 agents with XDR, SIEM and NRTG; Pro adds DLP at $4.50 per agent per month. Built in Malaysia for regulated organisations, government agencies and MSSPs across Asia.

Average Rating: 5.0/5.0

Total Reviews: 3

How Do G2 Users Rate nPro AI?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind nPro AI?

  • Seller: NPRO TECH
  • Year Founded: 2021
  • HQ Location: Kuala Lumpur, Malaysia
  • LinkedIn® Page: www.linkedin.com
    4 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of nPro AI?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Qualys Multi-Vector EDR

Bringing the scale, accuracy and unifying power of the Qualys Cloud Platform to EDR

Average Rating: 4.5/5.0

Total Reviews: 2

How Do G2 Users Rate Qualys Multi-Vector EDR?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Qualys Multi-Vector EDR?

  • Seller: Qualys
  • Year Founded: 1999
  • HQ Location: Foster City, CA
  • LinkedIn® Page: www.linkedin.com
    3,637 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Qualys Multi-Vector EDR?

SentinelOne Purple AI

SentinelOne Purple AI is an advanced AI cybersecurity analyst designed to enhance security operations by automating and accelerating threat detection, investigation, and response. By integrating generative AI, Purple AI empowers security teams to manage complex threats more efficiently, reducing response times and improving overall security posture. Key Features and Functionality: - Automated Threat Detection: Utilizes AI-driven analysis to identify and assess potential security threats in real-time. - Accelerated Incident Investigation: Streamlines the investigation process by providing comprehensive insights and context for detected threats. - Enhanced Response Capabilities: Facilitates rapid and informed decision-making to mitigate risks effectively. - Integration with SentinelOne Platform: Seamlessly works within the SentinelOne ecosystem, ensuring cohesive security management. Primary Value and User Benefits: Purple AI addresses the challenges of modern cybersecurity by automating routine tasks, allowing security teams to focus on strategic initiatives. It reduces the time and effort required for threat detection and response, thereby minimizing potential damage from cyber incidents. By leveraging generative AI, Purple AI enhances the efficiency and effectiveness of security operations, providing organizations with a robust defense against evolving cyber threats.

Average Rating: 4.8/5.0

Total Reviews: 2

Who Is the Company Behind SentinelOne Purple AI?

  • Seller: SentinelOne
  • Year Founded: 2013
  • HQ Location: Mountain View, CA
  • LinkedIn® Page: www.linkedin.com
    3,529 employees on LinkedIn®
  • Ownership: NASDAQ: S

Who Uses This Product?

  • Company Size: 50% Large, 50% Small

What Are Recent G2 Reviews of SentinelOne Purple AI?

Uptycs

Uptycs unified CNAPP and XDR platform is a comprehensive security solution designed to protect the full spectrum of modern attack surfaces in your cloud, data centers, user devices, build pipelines, and containers. With a strong focus on DevSecOps, Uptycs offers a powerful combination of CNAPP capabilities, including Cloud Workload Protection Platform (CWPP), Kubernetes Security Posture Management (KSPM), Cloud Security Posture Management (CSPM), Cloud Infrastructure Entitlement Management (CIEM), and Cloud Detection and Response (CDR). With Uptycs you also get industry-leading eXtended Detection and Response (XDR) across macOS, Windows, and Linux endpoints, ensuring comprehensive protection, detection, and investigation. Uptycs delivers real-time threat detection, context-rich alerts, and maps detections to the MITRE ATT&CK framework for improved security insights. Uptycs performs scanning of containers for vulnerabilities throughout the CI/CD pipeline, promoting agile DevOps workflows, and reducing risk in production environments. Uptycs seamlessly integrates with existing tools and processes, streamlining operations and improving overall efficiency. Customers also benefit from the flexibility to choose between agent-based and agentless scanning options tailored to their unique cloud workload needs. Discover how Uptycs can transform your security posture with a comprehensive, flexible, and powerful security solution designed to meet the needs of today's complex and rapidly evolving cloud environments. Shift up with Uptycs. KEY DIFFERENTIATORS: 1. Unified & Comprehensive Platform: Uptycs offers a holistic security solution with CNAPP capabilities (CWPP, KSPM, CSPM, CIEM, and CDR) across data centers, laptops, build pipelines, containers, and cloud environments, reducing tool sprawl. 2. Advanced XDR: Industry-leading eXtended Detection and Response for endpoint protection across macOS, Windows, and Linux systems. 3. DevSecOps Focus: Enhanced security for container-based workloads and Kubernetes, supporting agile DevOps workflows. 4. Real-Time Threat Detection: Context-rich alerts and threat detection mapped to the MITRE ATT&CK framework for improved insights. 5. CI/CD Integration: Efficiently scan containers for vulnerabilities throughout the CI/CD pipeline, reducing risk in production. 6. Both agent-based and agentless scanning. Deploy agentless scanning for rapid, friction-free coverage to keep your data secure, and gain continuous runtime security, real-time investigations, and remediation with agent-based telemetry. 7. Rich API & Compatibility: Seamless integration with existing security tools and platforms, powered by osquery for broad compatibility. 8. Expert Support & Flexibility: Dedicated support from security experts and the best of both worlds with agent-based and agentless scanning options tailored to your needs.

Average Rating: 4.4/5.0

Total Reviews: 13

How Do G2 Users Rate Uptycs?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Uptycs?

  • Seller: Uptycs
  • Year Founded: 2016
  • HQ Location: Waltham, US
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 54% Medium, 38% Large

What Do G2 Reviewers Say About Uptycs?

AI-generated summary from verified user reviews

Pros
  • Users value the comparative analysis feature of Uptycs, aiding in selecting the best cloud security tools.
  • Users value the comparative analysis feature of Uptycs, aiding in selecting the best cloud security tools.
  • Users value the comparative analysis feature of Uptycs, which aids in choosing the best cloud security tools.
  • Users value Uptycs for its excellent compliance with CIS and PCI DSS standards, enhancing security monitoring capabilities.
  • Users value the strong compliance with standards like CIS and PCI DSS, enhancing security monitoring capabilities.
Cons
  • Users find the high fees regrettable, as it limits their willingness to continue using Uptycs.
  • Users express concern over the high pricing of Uptycs, which deters continued use of the tool.

What Are Recent G2 Reviews of Uptycs?

Araali Network Security Pro

Araali Networks allows lean security teams to discover their exposure - data, services, and backdoors and prioritize the top 1% of risks that really matter. The security team can use cloud-native controls or Araali's ebpf firewall to create compensating controls to neutralize these risks. In addition, Araali is introducing a new feature that allows teams to patch their CVEs, automatically using Araali - this is a game changer as it allows team to knock off 90% of critical CVEs with little effort. Coverage: VMs, Containers, and Kubernetes across the public and private clouds. How: Araali automatically discovers your apps, their networking, access privileges, and security risks. It also creates and maintains the least privilege policies for all the apps. Your teams can enforce explicit policies for “who can do what” in your virtual private cloud, blocking malicious code from establishing a backdoor or accessing your services. Araali's customers include cloud-native startups, mid-market enterprises, and government agencies. To learn more visit www.araalinetworks.com or create a free trial account by signing up on console.araalinetworks.com Use Cases: 1) SOC-2 compliance: IDS/IPS, vulnerability management, asset management, vulnerability compensation controls, app access control for 2) Egress Filtering: Monitor and control egress to third-party sites, backdoors, supply chain attacks, and ransomware 3) Risk Prioritization: Visibility into the runtime - apps and associated risks 4) Vulnerability Management and Vulnerability Shielding: prevent vuln from getting exploited - especially useful for zero-day or cases where patches are not available as seen in Log4j 5) Enforcement: Proactively or Reactively Neutralize Threats to stop them from moving laterally and exfiltrating your data.

Average Rating: 4.3/5.0

Total Reviews: 3

How Do G2 Users Rate Araali Network Security Pro?

  • Unified Visibility: 8.3/10 (Category avg: 9.1/10)
  • Threat Hunting: 8.3/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 8.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Araali Network Security Pro?

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Do G2 Reviewers Say About Araali Network Security Pro?

AI-generated summary from verified user reviews

Pros
  • Users value the precision on threats in Araali Network Security Pro, enhancing their ability to address zero-day vulnerabilities effectively.
  • Users value the seamless API integration that enhances threat precision and mitigates zero-day vulnerabilities effectively.
  • Users value the detection efficiency of Araali Network Security Pro, effectively identifying and mitigating emerging zero-day vulnerabilities.
  • Users value the seamless integrations of Araali Network Security Pro, enhancing threat detection and mitigation efforts.
  • Users value the seamless integration and precise threat identification of Araali Network Security Pro, enhancing overall security posture.
Cons
  • Users find that complex coding complicates network integration and delays security alerts, hindering timely incident response.
  • Users find delayed detection of security alerts challenging, particularly with complex network setups, hampering incident response times.
  • Users experience ineffective alerts, leading to delays in incident response due to complex network infrastructure.
  • Users experience inefficient alert system, leading to delays in incident response due to complex network setups.
  • Users face network issues with Araali Network Security Pro, experiencing delays in security alerts and incident response.

What Are Recent G2 Reviews of Araali Network Security Pro?

Confluera

Confluera's Cloud eXtended Detection and Response platform is a cloud-native security solution designed to detect and respond to cyber threats in real-time. By leveraging patented Continuous Attack Graph technology, Confluera provides comprehensive visibility into attack progressions, enabling organizations to intercept threats before they escalate into breaches. This proactive approach reduces the time to detect and respond to threats from months to days, enhancing overall security posture. Key Features and Functionality: - Real-time Threat Detection: Utilizes behavioral analysis and machine learning to identify suspicious workload behaviors as they occur, minimizing false positives and ensuring timely responses. - Continuous Attack Graphs: Automatically stitches together live events based on cause and effect, providing a clear, real-time narrative of attack sequences without relying on post-breach correlation. - Multi-Cloud Visibility and Observability: Offers continuous discovery and monitoring of workloads across various cloud environments, including AWS, Azure, and Google Cloud Platform, ensuring comprehensive coverage. - Run-time Container Security: Delivers real-time threat detection and observability for containerized environments, enabling rapid interception of threats navigating across containers. - Multi-Source Threat Integration: Integrates signals from diverse security tools, providing a holistic view of potential threats and enhancing detection accuracy. - Incident Response Automation: Offers auto-generated recommendations and precise remediation steps, facilitating swift and effective responses to identified threats. - Proactive Threat Hunting: Combines real-time analytics with Continuous Attack Graphs to enable proactive searches for indicators of compromise, reducing investigation time and improving threat detection. Primary Value and Problem Solved: Confluera's CxDR platform addresses the challenges of detecting and responding to sophisticated cyber threats in complex, multi-cloud environments. Traditional security solutions often struggle with delayed detection and fragmented visibility, leading to prolonged exposure and potential breaches. By providing real-time attack interception and comprehensive threat storyboarding, Confluera empowers organizations to proactively manage security risks, reduce alert fatigue, and enhance the efficiency of security operations. This approach ensures that threats are identified and mitigated promptly, safeguarding critical assets and maintaining business continuity.

Average Rating: 4.5/5.0

Total Reviews: 1

How Do G2 Users Rate Confluera?

  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 5.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 3.3/10 (Category avg: 8.8/10)

Who Is the Company Behind Confluera?

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About Confluera?

AI-generated summary from verified user reviews

Pros
  • Users admire Confluera for its real-time threat visibility, effectively reducing noise and improving focus on genuine threats.
  • Users commend Confluera for its real-time visibility into cyber threats, enhancing focus on genuine security risks.
Cons
  • Users find the complex implementation of Confluera challenging, particularly for teams lacking cloud security experience.
  • Users find the integration issues with legacy systems challenging, complicating the initial setup and overall experience.
  • Users find the poor customer support of Confluera leads to slower resolutions during critical situations, impacting effectiveness.
  • Users find the initial setup complex and the user interface overwhelming, especially for those with less experience.

What Are Recent G2 Reviews of Confluera?

Fidelis Elevate

Fidelis Elevate, an active XDR platform, is a proactive cybersecurity platform which automates defense operations across diverse network architectures. It seamlessly extends security controls from traditional networks to the cloud and endpoints, making it the powerhouse of a cyber-resilient environment. As the only purpose-built XDR platform, Fidelis Elevate offers contextual visibility and integrated deception for swift threat detection, hunting, and response. Fidelis Elevate is the only XDR platform that offers: Comprehensive Active Directory Defense, 300+ Field Contextual Traffic analysis, Integrated Deception Technology, Intelligent Active Threat Detection with MITRE ATT&CK Mapping, AI-driven Sandbox Analysis, In-band Traffic Decryption Network DLP, Risk-Aware Terrain Mapping and more...

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Fidelis Elevate?

  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Fidelis Elevate?

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Fidelis Elevate?

Gradient Cyber

​Gradient Cyber’s Managed Extended Detection and Response (MXDR) service offers mid-market organizations comprehensive, 24/7/365 protection across their entire IT environment, including networks, endpoints, cloud infrastructures, Software as a Service (SaaS) applications, and business process applications. By integrating advanced AI/ML-driven analytics with human expertise through our proprietary XDR platform, Quorum™, we ensure rapid detection and neutralization of threats before they can impact operations. ​ Key Features of Gradient Cyber's MXDR Service: - Comprehensive Coverage: Our MXDR solution provides unified detection and response across all critical components of your IT ecosystem, ensuring no blind spots for attackers to exploit. ​ - Proactive Threat Detection: Utilizing a combination of automated tools and human analysis, we identify and mitigate threats in near real-time, significantly reducing the risk of breaches. ​ - Expert-Led Response: With a 10:1 client-to-analyst ratio, our dedicated team of security professionals offers personalized service, acting as an extension of your in-house team to swiftly address and remediate threats. ​ - High Accuracy: Our approach achieves a 99% false positive elimination rate, allowing your IT staff to focus on genuine threats without the distraction of unnecessary alerts. ​ - Scalability Across Industries: Serving clients in over 35 verticals, our MXDR service is tailored to meet the unique security challenges of various industries, ensuring relevant and effective protection. ​ - Robust Infrastructure: Operating from four in-house Security Operations Centers (SOCs) worldwide, we provide continuous monitoring and rapid response capabilities, ensuring global coverage and resilience. ​ - Integrated Compliance Tracking: Our service includes compliance tracking and detailed Situation Reports (SitReps), offering transparency and aiding in regulatory adherence. ​ By choosing Gradient Cyber’s MXDR service, organizations benefit from a seamless blend of technology and human expertise, transforming their cybersecurity posture from reactive to proactive.

Average Rating: 4.8/5.0

Total Reviews: 4

How Do G2 Users Rate Gradient Cyber?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Gradient Cyber?

Who Uses This Product?

  • Company Size: 50% Small, 25% Large

What Do G2 Reviewers Say About Gradient Cyber?

AI-generated summary from verified user reviews

Pros
  • Users value the automation capabilities of Gradient Cyber, enhancing security management with proactive detection and intuitive features.
  • Users value the continuous monitoring by Gradient Cyber, which enhances security and reduces the need for daily logins.
  • Users praise the exceptional customer support from Gradient Cyber, feeling like a true partner in security management.
  • Users value the customization options of Gradient Cyber, enabling tailored features that perfectly fit their security needs.
  • Users value the intuitive dashboard customization of Gradient Cyber, enhancing usability and effectiveness across various environments.

What Are Recent G2 Reviews of Gradient Cyber?

Mave Security

Mave reinvents security operations for the modern enterprise. Security teams are buried in alerts and forced to reconstruct incidents across disconnected tools while attacks unfold in minutes. The SIEM holds only part of the picture. Critical context such as identity state, configuration, ownership, and live activity remains scattered across the security stack. Mave turns the tools you already use into one defense system. Its governed AI agents query each source directly in its native language, then reason across the evidence as each task unfolds. The underlying telemetry stays in place. No migration, duplicate data lake, central index, or prebuilt correlation pipeline is required. Mave investigates every alert, filters false positives, applies threat intelligence to your environment, hunts for related activity, creates and improves detections, and replaces brittle SOAR playbooks with automation that adapts to the evidence. Every action follows the permissions, policies, and approval rules set by your security team. The result is complete SecOps coverage, finally.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Mave Security?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind Mave Security?

  • Seller: Mave
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    20 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Mave Security?

SecBI XDR

SecBI is a leading provider of Universal XDR (Extended Detection and Response) solutions that allow organizations to transform traditionally siloed security functions into a unified, automated, and highly successful detection and response operations system. By creating a vendor-agnostic XDR overlay, SecBI's Universal XDR Platform provides seamless and simple vendor agnostic product integration of already-deployed network, endpoint, and cloud security tools, enabling enterprises to extract greater value from existing security resources and to make their security operations more efficient and effective in protecting against sophisticated and stealthy cyber attacks. SecBI Universal XDR is used by finance, telecom, retail, and manufacturing enterprises worldwide. For more information, visit: http://www.secbi.com

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate SecBI XDR?

  • Unified Visibility: 10.0/10 (Category avg: 9.1/10)
  • Threat Hunting: 10.0/10 (Category avg: 9.2/10)
  • Rule-Based Detection: 10.0/10 (Category avg: 8.8/10)

Who Is the Company Behind SecBI XDR?

  • Seller: SecBI
  • Year Founded: 2001
  • HQ Location: Copenhagen, Capital Region of Denmark, Denmark
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About SecBI XDR?

AI-generated summary from verified user reviews

Pros
  • Users value the automation capabilities of SecBI XDR for quickly detecting and prioritizing real threats efficiently.
  • Users value the responsive customer support of SecBI XDR, enhancing their overall experience and satisfaction.
  • Users value the automatic correlation of security data by SecBI XDR, enabling quick detection of real threats.
  • Users find the ease of use of SecBI XDR enhances their security management experience significantly.
  • Users commend the easy implementation of SecBI XDR, allowing for quick and seamless deployment in their environments.
Cons
  • Users find the complex implementation of SecBI XDR challenging, needing in-depth knowledge for effective configuration.
  • Users find the complexity of configuration in SecBI XDR challenging, necessitating a deep understanding of their environment.
  • Users find the complex configuration of SecBI XDR challenging, needing significant expertise to optimize its performance.
  • Users find it challenging to configure and fine-tune SecBI XDR, needing a solid understanding of their environment for optimization.
  • Users find the learning curve steep for SecBI XDR, needing time to optimize configurations and workflows effectively.

What Are Recent G2 Reviews of SecBI XDR?

Adlumin MDR

Who Is the Company Behind Adlumin MDR?

  • Seller: N-able
  • HQ Location: Morrisville, North Carolina
  • LinkedIn® Page: www.linkedin.com
    2,307 employees on LinkedIn®
  • Ownership: NYSE: NABL

AhnLab XDR

AhnLab XDR is an AI-powered, SaaS-delivered platform that provides granular threat detection, precise risk identification, contextual analysis, and optimal response to help customers prioritize and manage cyber risks. Why AhnLab XDR • Precise Risk Identification AhnLab XDR performs around-the-clock monitoring of enterprise users and their assets. Continuous monitoring is followed by correlation analysis into the entity and user/device behaviors, leading to precise risk identification with a clear understanding of its impact and context. • Orchestrated Response Enabled by Seamless Integration AhnLab XDR ingests logs from native and third-party products and conducts a full-historical analysis to enrich and contextualize the data. This allows customers to perform orchestrated incident response by leveraging the security features of seamlessly integrated products. • Advanced Security with Better Efficiency Our SaaS-delivered XDR guarantees better operational efficiency and minimal performance impact with our agentless log collection. Furthermore, the smooth integration with our best-in-class threat intelligence platform empowers customers with actionable insights into the latest cyber threats. Key Features • Risk Scoring AhnLab XDR normalizes the ingested data and performs a contextual analysis thanks to our AI and machine learning technologies. The outcome of AI-assisted analysis is presented as the intuitive company-wide risk score that allows users to prioritize risks and build a robust threat response strategy. • Up-to-date Scenario Rules AhnLab XDR is armed with up-to-date scenario rules that predefine well-known and latest risk scenarios. The platform ensures real-time rule updates to help users always stay response-ready. • Optimized Log Collection & Threat Response Interoperating with our EPP and EDR, AhnLab XDR aggregates a large volume of user/asset data and enriches it for an optimal response. The data acquisition from “AhnLab Data Hub” where all ingested data from security tools reside, makes the data ingestion process completely agentless. • Threat Intelligence based Monitoring Integration with AhnLab TIP empowers AhnLab XDR to perform threat intelligence-based monitoring that enables users to take an immediate response action by better understanding the latest IOCs and their potential impact. Users can also enjoy the rich content from AhnLab TIP, such as news clipping and security advisory.

Who Is the Company Behind AhnLab XDR?

  • Seller: AhnLab
  • Year Founded: 1995
  • HQ Location: Seongnam-si, KR
  • LinkedIn® Page: www.linkedin.com
    691 employees on LinkedIn®

AirCISO

AirCISO is Airiam’s extended detection and response (XDR) software that gives CISOs, IT Managers, CIOs, and other leaders the insights they need to improve their organization’s cybersecurity. Use AirCISO for free and get useful data on your cybersecurity threats and vulnerabilities in your environment immediately. Get all the data a CISO needs to know where they stand.

Who Is the Company Behind AirCISO?

  • Seller: Airiam
  • Year Founded: 2021
  • HQ Location: Lewisburg, US
  • LinkedIn® Page: www.linkedin.com
    49 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024