cysmo
Who Is the Company Behind cysmo?
- Seller: cysmo Cyber Risk GmbH
- Year Founded: 2017
- HQ Location: Hamburg, DE
-
LinkedIn® Page: www.linkedin.com
9 employees on LinkedIn®
Last updated: November 18, 2026
Total Products under this Category: 81
Last updated: November 17, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
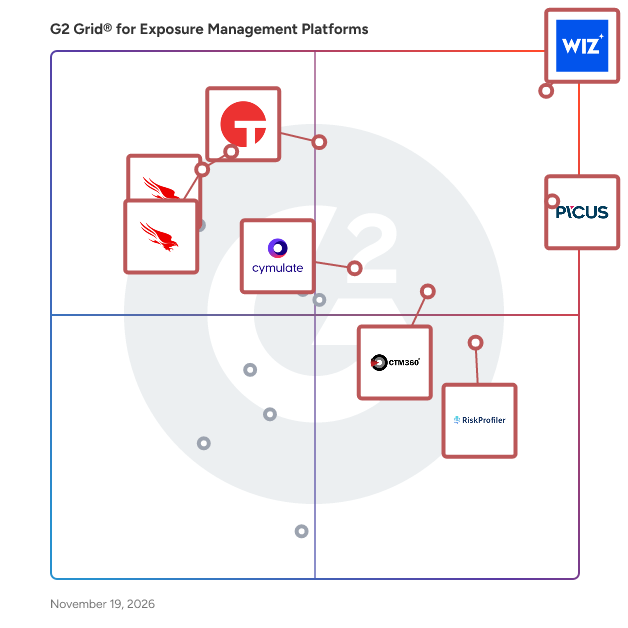
Highlighted products: Wiz, Picus Security, Tanium, CTM360, RiskProfiler - External Threat Exposure Management, Cymulate, CrowdStrike Falcon Cloud Security, and CrowdStrike Falcon Exposure Management.
Underlying data: [Grid® JSON](https://www.g2.com/categories/exposure-management-platforms/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=picus-security&focus%5B%5D=tanium&focus%5B%5D=ctm360-ctm360&focus%5B%5D=riskprofiler-external-threat-exposure-management&focus%5B%5D=cymulate&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=crowdstrike-falcon-exposure-management)
Detectify sets a new standard for advanced application security testing, challenging traditional DAST by providing evolving coverage of each and every exposed asset across the changing attack surface. AppSec teams trust Detectify to expose how attackers will exploit their Internet-facing applications. The Detectify platform automates continuous real-world, payload-based attacks fuelled by its global community of elite ethical hackers into its own expert-built engines, exposing critical weaknesses before it's too late. The Detectify solution includes: - Automated discovery of known and unknown digital assets via domain & cloud connectors - Continuous coverage (24/7) of every corner of the attack surface with dynamic testing. Not just predefined targets - 100% payload-based testing fuelled by elite ethical hackers for a high signal-to-noise ratio - Distributed coverage across an unmatched array of relevant technologies - Actionable remediation tips for software development teams - Team functionality to easily share reports - Powerful integrations platform to prioritize and triage vulnerability findings onward to development teams -Advanced API functionality -Capabilities to set custom attack surface security policies
Average Rating: 4.5/5.0
Total Reviews: 50
AI-generated summary from verified user reviews
"Vulnerability scans made easy"
Rating: 5.0/5.0 stars
— Arkadiusz K.
"Very happy from an admin/IT security manager view"
Rating: 5.0/5.0 stars
— Björn L.
Reveald's Epiphany Intelligence Platform offers advanced attack graph analysis of a client's digital estate, identifying the most likely path of exploitation and prioritizing vulnerabilities and misconfigurations that pose the most risk. By correlating information from the client's existing cybersecurity tools, EIP helps reduce time spent remediating unexploitable vulnerabilities or those that do not expose critical systems.
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
GridLock by InfinityGrid is a cybersecurity exposure management and endpoint intelligence platform designed to help organizations discover, investigate, prioritize, and reduce security risks across their IT environments. Built for IT administrators, security engineers, and cybersecurity teams, GridLock brings together asset intelligence, software vulnerability analysis, endpoint telemetry, security findings, and operational visibility within a unified investigation platform. GridLock helps organizations move beyond traditional asset inventories and disconnected security dashboards by connecting endpoint information with actionable security intelligence. Its capabilities include asset discovery, software stack analysis, vulnerability correlation, patch gap visibility, lifecycle intelligence, telemetry health monitoring, and security risk prioritization. Through its hybrid architecture, GridLock combines agent-collected endpoint intelligence with centralized analysis to help security teams identify exposed systems, investigate vulnerable software, uncover monitoring blind spots, and understand how security findings affect their environments. Key capabilities include: - Asset Intelligence: Centralized endpoint inventory, operating system visibility, agent health, telemetry freshness, security findings, and device risk assessments. - Software Stack Intelligence: Software inventory analysis, vulnerability correlation, patch gap assessment, lifecycle tracking, and potential blast radius visibility. - Telemetry Blind Spot Detection: Identification of disabled, stale, missing, or unhealthy security collectors that may create monitoring gaps. - Security Risk Investigation: Detailed endpoint findings and contextual intelligence to support vulnerability investigation and remediation prioritization. - Operational Security Visibility: Connected security intelligence that helps administrators evaluate endpoint coverage and identify areas requiring attention. GridLock is designed to help organizations transform endpoint data into meaningful security decisions, reduce manual investigation effort, improve visibility into their attack surface, and strengthen their overall cybersecurity posture. Developed by InfinityGrid, GridLock delivers a security-focused workspace for organizations seeking deeper endpoint intelligence, more effective exposure management, and greater control over their security operations.
Helios by Isaphia is a unified exposure-management platform combining External Attack Surface Management (EASM), Internal ASM, Cyber Threat Intelligence (CTI), and Cloud Security Posture Management (CSPM) in a single dashboard. External ASM continuously discovers and prioritizes every internet-facing asset you own — including the ones you forgot. Internal ASM uses lightweight collectors to map what's reachable behind the firewall, surfacing the legacy systems attackers pivot to once inside. CTI is asset-aware: every indicator is matched against your real inventory instead of flooding you with thousands of generic IOCs. CSPM catches misconfigurations, identity risk, and compliance drift across AWS, Azure, and GCP. Helios was built by Isaphia Security's penetration testers and red teamers around one question: what do we reach for first on a real engagement? Run it yourself as SaaS, or have Isaphia's practitioners operate it for you as a managed service.
Noetic’s full-stack visibility and effective controls monitoring empowers enterprises to see the full picture and truly understand significance of relationships between entities, so you can identify gaps and continuously improve efficacy. Find out what you can do with Noetic.
Nucleus Security is a vulnerability and asset management solution that automates processes and workflows, enabling organizations to mitigate vulnerabilities 10 times faster, using a fraction of the resources that it takes to perform these tasks today. Nucleus aggregates, cleans, correlates, and analyzes data from all sources of asset and vulnerability data and organizes it into a logical hierarchy. Once the data is organized, Nucleus streamlines operational processes with efficient workflows and time-saving automation that accelerate vulnerability management and response.
Average Rating: 4.5/5.0
Total Reviews: 31
AI-generated summary from verified user reviews
"Streamlined Reporting with Nucleus, Easy Setup!"
Rating: 4.0/5.0 stars
— Manish G.
"Comprehensive Vulnerability Management with Stellar Support"
Rating: 5.0/5.0 stars
— Husain A.
Offensity is an automated vulnerability scanner helping professional IT teams identify and fix vulnerabilities. Offensity is an easy to use External Attack Surface Management solution and minimizes human effort in your team. You will be set up in minutes: IT admins enter and verify their domain (e.g. company-demo.com). Additional subdomains will be suggested automatically. Scanning starts. That’s it.
Average Rating: 4.4/5.0
Total Reviews: 10
"Awesome Budget-Wise Vulnerability Tool"
Rating: 5.0/5.0 stars
— Raymond C.
"A Budget-Friendly Scanning Service!"
Rating: 4.5/5.0 stars
— Verified User in Computer & Network Security
Offensive Security Manager (OSM) is an Agentic AI-powered cybersecurity platform that transforms reactive defense into proactive risk management. Designed as a Virtual AI Security Team, OSM works 24/7 to detect, predict, and prevent cyber threats long before they strike—bringing the analytical power of a hundred top-tier security experts into a single intelligent system. At its core, OSM is built around Continuous Threat Exposure Management (CTEM), Gartner’s strategic framework for modern cybersecurity. The platform unifies risk data from every layer of the IT environment—network, web, containers, and source code—to create a single Mission Control Center for security. Through advanced machine learning, real-time asset composition analysis, and business-contextual risk scoring, OSM identifies which vulnerabilities truly matter and delivers precise, step-by-step remediation guidance. Unlike traditional tools that simply list vulnerabilities, OSM delivers an “OSM Issue” — an AI-generated intelligence briefing that translates complex technical findings into clear business directives. Each issue includes summarized impact, attacker scenarios, immediate prevention guidance, and a complete remediation plan. This approach enables organizations to fix what matters most, faster and with measurable impact. Engineered for both enterprises and SMBs, OSM can act as an organization’s entire cybersecurity team or as a powerful force multiplier for existing operations. Its on-premise, cloud, or hybrid deployments support even air-gapped and high-security environments, while native integrations with over 20 tool categories (including Tenable, Rapid7, Jira, and ServiceNow) make it a seamless addition to any ecosystem. OSM delivers quantifiable results: Reduces breach likelihood by up to 90% Automates 80% of repetitive analyst work Cuts mean time to remediate (MTTR) by over 70% Lowers security spend through tool consolidation and unlimited scanning With built-in compliance support for NIS2, PCI DSS, ISO 27001, GDPR, HIPAA, and more, OSM simplifies audit readiness and continuous governance. In a world drowning in security noise, OSM stands out as the AI brain that turns chaos into clarity—predicting attacks, prioritizing real risk, and empowering businesses to move from reaction to prevention. Offensive Security Manager (OSM) redefines cybersecurity as a strategic business enabler — the collision sensor that keeps organizations one step ahead of tomorrow’s threats.
Onit Security is an AI-native exposure management platform that turns millions of security findings into a short set of decisions your team can act on. Onit connects by API to the scanners, cloud, EDR, CMDB and ticketing tools you already run, with no new agent to deploy. It deduplicates findings, then works through each exposure in order: whether an attacker can actually reach it, whether it is exploitable in your environment, what it means to the business, and who owns it. What remains is grouped into decisions, meaning groups of exposures that share the same resolution path. That path can be a patch, a compensating control, or a risk acceptance that is explicit, owned and recorded. You approve the decision once. Every later action runs under that rule, logged and reversible. Onit’s agents then route the work to the right owner in ServiceNow, Jira, Slack or Teams and follow it through to closure. Humans define judgment. Agents execute. Keep the scanner. Fix what happens after the finding. Decide once. Resolve forever. Onit created the Decision-Based Exposure Management category and works with large enterprises, including Fortune 500 companies. The platform is SOC 2 Type II, ISO 27001 and ISO 42001 certified and offers 100+ integrations, including Tenable, Qualys, Rapid7, Wiz, CrowdStrike and Microsoft Defender. Visit https://onit.security/ for more information.
Onyxia is a Dynamic Cybersecurity Management platform that empowers Chief Information Security Officers and cybersecurity leaders with a centralized view of their cybersecurity environment and provides actionable insights for high-performing cyber defense strategies that align with business objectives. With Onyxia, security leaders can easily measure, manage and convey the business value of their cybersecurity program, enabling their organizations to stay safe from emerging threats, focus on what matters, and make smarter and more efficient decisions. The Onyxia platform identifies gaps in cybersecurity management and prioritizes recommendations for proactive cybersecurity strategy. Transform your team from being reactive to proactive, solving daily management, strategic planning and operational problems. Our mission is to empower CISOs with a holistic view and customized insights based upon real-time data.
Panop is a Exposure Management Platform It continuously discovers and validates signals across cloud, third-party and multi-entity ecosystems — reducing noise and increasing confidence. It connects technical exposure with business and operational context, enriched by external threat intelligence, to enable risk-based prioritization. All exposure is consolidated into a unified and continuously updated model, delivering decision-ready outputs for security and SOC teams. Panop is agentless Cloud Based Solution providing seamless automation, integrations, and advanced reporting capabilities.
Average Rating: 5.0/5.0
Total Reviews: 2
AI-generated summary from verified user reviews
"Very powerful solution to accelerate the discovery of cyber-infrastructure assets"
Rating: 5.0/5.0 stars
— Jean-Loup R.
"Great Attack Surface Management"
Rating: 5.0/5.0 stars
— Nuria U.
Panopsys is a cybersecurity platform that helps organizations identify, assess, and remediate security risks across their digital infrastructure. Combining attack surface management, vulnerability monitoring, and security misconfiguration tracking, Panopsys provides continuous visibility into IT assets and their exposure to threats. By connecting technical findings with business context, Panopsys enables security and IT teams to prioritize remediation, reduce their attack surface, and strengthen their security posture.
