Top Free Cloud Workload Protection Platforms - Page 2

How Many Cloud Workload Protection Platforms Products Does G2 Track?

Total Products under this Category: 89

Category Stats (Sep 2026)

  • Average Rating: 4.42/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: Darktrace / EMAIL (+3.53%) - Among all products in this category, Darktrace / EMAIL recorded the largest rating increase compared to last month

Last updated: September 15, 2026

How Does G2 Rank Cloud Workload Protection Platforms Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,900+ Authentic Reviews
  • 89+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

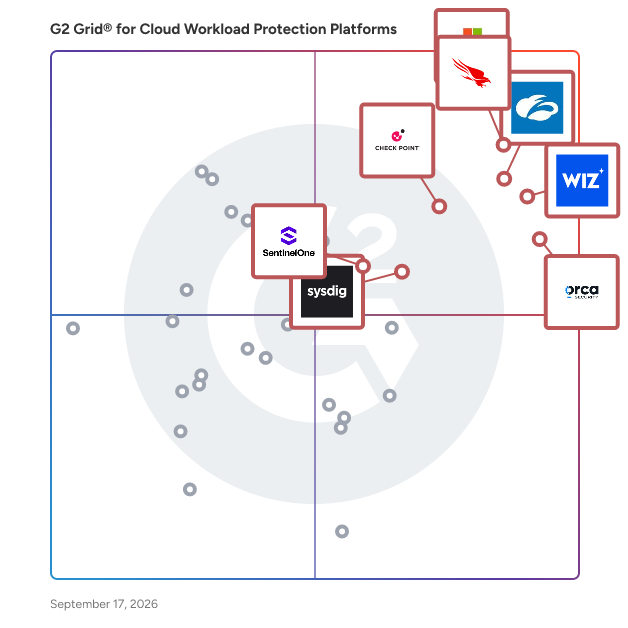
G2 Grid® for Cloud Workload Protection Platforms

G2 Grid® for Cloud Workload Protection Platforms plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security, Wiz, Zscaler Zero Trust Cloud, Orca Security, Check Point Cloud Firewall (formerly CloudGuard Network Security), Sysdig Secure, and SentinelOne Singularity Cloud Security.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-workload-protection-platforms/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=wiz-wiz&focus%5B%5D=zscaler-zero-trust-cloud&focus%5B%5D=orca-security&focus%5B%5D=check-point-cloud-firewall-formerly-cloudguard-network-security&focus%5B%5D=sysdig-sysdig-secure&focus%5B%5D=sentinelone-singularity-cloud-security)

AccuKnox

AccuKnox Zero Trust CNAPP cloud security protects public and private clouds, Kubernetes and VMs. AccuKnox is a AI-powered Zero Trust Cloud Native Security Platform that helps organizations comply with various frameworks and over 33+ compliance controls, including MITRE, NIST, STIG, CIS, PCI-DSS, GDPR, and SOC2. AccuKnox enhances InfraSec and DevSecOps teams by enabling them to detect, prioritize, prevent and protect against advanced and sophisticated cloud attacks. Key Benefits 1. Code to Cloud Security 2. Easy Deployment 3. Extensive Coverage. 4. Preemptive Attack Mitigation 5. Open Source and Innovative Key Differentiators - Inline Preemptive Security (as opposed to Post-attack mitigation) - Secures modern workloads (Kubernetes) and traditional workloads (VMs) - Multi-Cloud, Private, Air-gapped, and Hybrid Cloud Security - IaC – Infrastructure As Code scanning - Secures AI/ML workloads like Jupyter Notebooks Features - Automated Zero Trust Cloud Security (Public, Private, Hybrid, Air-gapped) - Vulnerability Management & Prioritization - Run-time security, Micro-segmentation - Application Firewalling, Kernel Hardening - Drift Detection & Audit Trail - Continuous Diagnostics & Mitigation - GRC – CIS, HIPAA, GDPR, SOC2, STIG, MITRE, NIST - Securing Mission-Critical Workloads like Vault - Securing AI workbenches like Jupyter Notebooks - Cryptojacking and TNTBotinger Attacks With over 15+ patents, we're proud to offer an OpenSource, DevSecOps-led delivery model. To top it off, we have an ongoing R&D partnership with the esteemed SRI International. We deliver both Static and Runtime Security, anchored on innovations in Cloud Security and AI/ML-based Anomaly Detection. Static Code Analysis - Deeply analyze your code for vulnerabilities and weaknesses. CI/CD Pipelines Scanning - Continuously scan your pipelines for security flaws and risks. Container Security - Fortify your containers with robust security measures. Kubernetes Orchestration - Seamlessly manage and secure your Kubernetes environments. Secret Scanning - Detect and protect sensitive information from unauthorized access.

Average Rating: 4.4/5.0

Total Reviews: 12

How Do G2 Users Rate AccuKnox?

  • Governance: 8.1/10 (Category avg: 8.8/10)
  • Ease of Admin: 8.3/10 (Category avg: 9.0/10)
  • API / Integrations: 8.0/10 (Category avg: 8.6/10)
  • Security Auditing: 8.5/10 (Category avg: 8.9/10)

Who Is the Company Behind AccuKnox?

  • Seller: Accuknox
  • Year Founded: 2020
  • HQ Location: California, USA
  • Twitter: @AccuKnox
    341 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    197 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 46% Large, 31% Medium

What Do G2 Reviewers Say About AccuKnox?

AI-generated summary from verified user reviews

Pros
  • Users highly value AccuKnox for its comprehensive security features that enhance cloud and Kubernetes environments.
  • Users highlight the high security level of AccuKnox, ensuring robust protection for cloud workloads and integrations.
  • Users appreciate the seamless cloud integration of AccuKnox, enhancing security and simplifying compliance with major providers.
  • Users value AccuKnox for its continuous compliance features, enhancing security and adaptability in their cloud environments.
  • Users praise the exceptional customer support from AccuKnox, highlighting their quick response and detailed understanding of needs.
Cons
  • Users find the difficult learning curve challenging, requiring prior knowledge of Kubernetes to manage AccuKnox effectively.
  • Users find the complex setup of AccuKnox challenging, particularly for those lacking security management experience.
  • Users find AccuKnox to be cost prohibitive, which may deter some from considering the solution.
  • Users often experience poor customer support, citing slow responses and the need for frequent follow-ups.
  • Users find the setup and management complexity of AccuKnox challenging, particularly for those with limited security knowledge.

What Are Recent G2 Reviews of AccuKnox?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 47

How Do G2 Users Rate Darktrace / HYBRID NETWORK?

  • Ease of Admin: 7.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • Twitter: @Darktrace
    18,177 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 31% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the excellent monitoring capabilities of Darktrace, offering impressive visibility and efficient network analysis.
  • Users appreciate the self-learning AI technology of Darktrace/Network, effectively adapting to threats without extensive configuration.
  • Users commend Darktrace's rapid threat detection, ensuring robust security with minimal manual intervention for maximum efficiency.
  • Users commend the responsive customer support of Darktrace/Network, enhancing learning and facilitating efficient troubleshooting.
  • Users highlight the autonomous AI-driven cybersecurity of Darktrace, which effectively detects and responds to threats in real time.
Cons
  • Users report a significant learning curve with Darktrace as the AI generates numerous alerts during initial setup.
  • Users note that the product can be expensive, particularly for smaller organizations with constrained budgets and significant training costs.
  • Users experience alert issues with Darktrace, needing extensive manual tuning to manage false positives during the learning phase.
  • Users find the complex setup of Darktrace challenging, requiring skilled teams for effective management and configuration.
  • Users experience false positives occasionally, requiring IT support to resolve issues affecting network connectivity.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

CloudWize

CloudWize is a no-code Cloud Security Center of Excellence that gives you maximum cloud compliance & security. Get 360° Protection from Architecture Design to Runtime. CludWize enforces cloud regulations with over 1K rules running continuously, scans your cloud vulnerabilities, and remediates them automatically. With our unique investigation graph engine, you can detect and fix cloud issues in minutes instead of days and weeks. This holistic solution offers a blackbox web app penetration test, evolved IAM (identity access management), IaC (infrastructure as code) risk scanning, Data Security Posture Management, and more. Why deal with many tools when you can have everything in one place? CNAPP + WAAP + KSPM – CSPM + CWPP + CIEM + CASB + DSPM + CNSP = CloudWize (CSCoE)

Average Rating: 4.7/5.0

Total Reviews: 11

How Do G2 Users Rate CloudWize?

  • Ease of Admin: 9.6/10 (Category avg: 9.0/10)

Who Is the Company Behind CloudWize?

  • Seller: CloudWize
  • Year Founded: 2019
  • HQ Location: Netanya, IL
  • Twitter: @cloud_wize
    94 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    3 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Small, 33% Medium

What Do G2 Reviewers Say About CloudWize?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the superior security features of CloudWize, enhancing control and vulnerability management for their systems.
  • Users appreciate the ease of use of CloudWize, enabling effortless security management and proactive monitoring.
  • Users value the robust cloud security and assistance from CloudWize, enhancing threat detection and response capabilities.
  • Users commend CloudWize's robust security features and exceptional customer support for optimizing cloud management effectively.
  • Users value the robust security features of CloudWize, providing control and confidence for cloud management.
Cons
  • Users find the complex implementation process cumbersome without templates to assist new users effectively.
  • Users find the complex setup of CloudWize challenging, needing templates to assist with the implementation process.
  • Users find customization challenging, wishing for more options to better suit individual preferences and requirements.
  • Users find the difficult navigation of CloudWize could be further simplified for an improved experience.
  • Users find the excessive customization options of CloudWize can be overwhelming, hindering a smooth user experience.

What Are Recent G2 Reviews of CloudWize?

NetApp Cloud Volumes ONTAP

NetApp® Cloud Volumes ONTAP® offers a self-managed, unified storage management solution built on NetApp’s industry-leading ONTAP® software—empowering organizations with unmatched control and flexibility across block and file workloads in hybrid and multicloud environments. Seamlessly integrated with all major cloud providers, it runs natively on each cloud platform (Microsoft Azure, Google Cloud, AWS), allowing you to deploy and manage storage for mission-critical applications, databases, containers, and user files without requiring extra tooling or complex configuration. With support for iSCSI, NVMe/TCP, NFS, SMB/CIFS, and S3, Cloud Volumes ONTAP brings enterprise-class data services to your cloud environment.  

Average Rating: 4.5/5.0

Total Reviews: 26

How Do G2 Users Rate NetApp Cloud Volumes ONTAP?

  • Governance: 8.3/10 (Category avg: 8.8/10)
  • Ease of Admin: 8.5/10 (Category avg: 9.0/10)
  • API / Integrations: 8.3/10 (Category avg: 8.6/10)
  • Security Auditing: 8.3/10 (Category avg: 8.9/10)

Who Is the Company Behind NetApp Cloud Volumes ONTAP?

  • Seller: NetApp
  • Year Founded: 1992
  • HQ Location: Sunnyvale, California
  • Twitter: @NetApp
    118,015 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    12,706 employees on LinkedIn®
  • Ownership: NASDAQ

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 41% Large, 32% Small

What Do G2 Reviewers Say About NetApp Cloud Volumes ONTAP?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive solutions provided by NetApp Cloud Volumes ONTAP, enhancing performance and reliability in storage.
  • Users value the reliable and powerful data storage provided by NetApp Cloud Volumes ONTAP for their needs.
  • Users find the ease of use in NetApp Cloud Volumes ONTAP beneficial for efficient management and operations.
  • Users value the user-friendly interface and powerful CLI of NetApp Cloud Volumes ONTAP, enhancing performance and availability.
  • Users value the high availability of NetApp Cloud Volumes ONTAP, ensuring reliable performance for their storage needs.
Cons
  • Users find the command line interface challenging, as frequent GUI changes complicate the navigation experience.
  • Users find the frequently changing GUI of NetApp Cloud Volumes ONTAP frustrating, often preferring the stability of CLI.
  • Users find the poor interface design frustrating, ultimately preferring the CLI over the frequently changing GUI.
  • Users find the poor UI of NetApp Cloud Volumes ONTAP frustrating, often preferring CLI for ease of use.
  • Users find the poor usability due to frequent GUI changes, often opting for CLI instead for simplicity.

What Are Recent G2 Reviews of NetApp Cloud Volumes ONTAP?

What Are G2 Users Discussing About NetApp Cloud Volumes ONTAP?

Sonrai Security

Sonrai Security is a leading cloud privileged access management solutions provider. With a mission to empower enterprises of all sizes to innovate securely and confidently, Sonrai Security delivers identity, access, and privilege security for companies running on AWS, Azure, and Google Cloud platforms. The company is renowned for pioneering the Cloud Permissions Firewall, enabling one-click least privilege while supporting developer access needs without disruption. Trusted by Cloud Operations, Development, and Security Teams at leading companies across various industries, Sonrai Security is committed to driving innovation and excellence in cloud security. Sonrai’s Cloud Permissions Firewall, the leading cloud PAM solution, gets cloud access under control, slashes the privileged attack surface, and automates least privilege all without impeding DevOps. The Cloud Permissions Firewall uses privileged permission intelligence and usage monitoring to determine who needs what permissions in your cloud. Then, with one-click, it eliminates all unused sensitive privileges across your entire multi-cloud estate. Just-in-time access and exceptions are granted to roles on the fly as new needs come up so development goes uninterrupted. SecOps teams spend 97% less time achieving least privilege and slash the attack surface by 92%.

Average Rating: 4.5/5.0

Total Reviews: 26

How Do G2 Users Rate Sonrai Security?

  • Governance: 10.0/10 (Category avg: 8.8/10)
  • Ease of Admin: 8.3/10 (Category avg: 9.0/10)
  • API / Integrations: 6.7/10 (Category avg: 8.6/10)
  • Security Auditing: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Sonrai Security?

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 42% Medium, 38% Large

What Do G2 Reviewers Say About Sonrai Security?

AI-generated summary from verified user reviews

Pros
  • Users value the enhanced visibility and control Sonrai Security offers for effective cloud security management.
  • Users value the strong security features of Sonrai Security, enabling effective control over permissions and risk management.
  • Users commend Sonrai Security for its effective cloud management, streamlining permission controls and enhancing security effortlessly.
  • Users highlight the ease of use of Sonrai Security, appreciating its straightforward deployment and seamless integration.
  • Users value the cloud security solution of Sonrai Security for simplifying access management and minimizing permissions.
Cons
  • Users find Sonrai Security to have a complexity that requires significant tuning and deep learning for effective use.
  • Users find the pricing to be high, especially impacting smaller teams and businesses seeking security solutions.
  • Users find feature limitations of Sonrai Security frustrating, citing complexity and the need for manual intervention.
  • Users feel that improvement is needed in Sonrai Security's complexity, feature limitations, and dashboard customization options.
  • Users feel the limited customization options hinder their experience and functionality in Sonrai Security.

What Are Recent G2 Reviews of Sonrai Security?

Saviynt

Saviynt helps organizations transform their organization with identity security, enabling them to build and run AI with confidence. Saviynt enables enterprises to secure every identity — human, non-human, and AI — in any application and environment, strengthen their identity security posture, streamline operations, and ensure every user and agent has the right access at the right time. With Saviynt Zuma, enterprises can discover, protect, and manage AI identities from a single control plane, delivering the necessary tools to flag and fix shadow AI, control access at runtime, establish accountability, and empower secure agentic development across the entire organization. In turn, organizations enjoy lower risk, complete visibility and governance, reduced total cost of ownership, and much more throughout their entire identity security program.

Average Rating: 4.3/5.0

Total Reviews: 91

How Do G2 Users Rate Saviynt?

  • Ease of Admin: 8.2/10 (Category avg: 9.0/10)

Who Is the Company Behind Saviynt?

  • Seller: Saviynt
  • Company Website:
  • Year Founded: 2010
  • HQ Location: El Segundo, US
  • Twitter: @saviynt
    1,242 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    1,662 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Financial Services
  • Company Size: 79% Large, 5% Medium

What Do G2 Reviewers Say About Saviynt?

AI-generated summary from verified user reviews

Pros
  • Users commend Saviynt for its exceptional ease of use, enabling efficient task performance with minimal training required.
  • Users value the exceptional functionality of Saviynt, appreciating its ease of use and regular updates.
  • Users commend the easy setup of Saviynt, enabling quick configuration and enhancing overall workflow efficiency.
  • Users value the 24/7 customer support from Saviynt, ensuring prompt assistance for product-related issues.
  • Users value the seamless integration with various tools, enhancing collaboration and efficiency across platforms.
Cons
  • Users find the difficult learning curve with Saviynt due to its complicated UX and confusing forms.
  • Users find a lack of features in Saviynt, particularly regarding customization and support for specific functionalities.
  • Users find limited features in Saviynt, including inflexible SavRoles and challenges with upgrades affecting functionality.
  • Users are frustrated by the poor interface design, making setup and navigation unnecessarily complicated and confusing.
  • Users find the complex setup of Saviynt challenging, impacting ease of use and flexibility in adoption.

What Are Recent G2 Reviews of Saviynt?

ADEPT Egress Control

ADEPT Egress Control blocks breaches and protects your cloud workloads. Our product essentially zero-trusts your software, protecting against supply chain threats, command and control, and data leaks. Concerned about compliance and certification? See how ADEPT protects data access and privacy, detects intrusions and anomalies, and tracks activity at the server level. Dart Frog Cyber fills cybersecurity gaps for customers using smart software that's easy to manage and very affordable. Contact us today to discuss your particular needs and pain points--we're here to help!

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate ADEPT Egress Control?

  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)

Who Is the Company Behind ADEPT Egress Control?

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of ADEPT Egress Control?

CimTrak Integrity Suite

Cimcor is the leading provider of System Integrity Assurance with our award-winning CimTrak Integrity Suite that protects a wide range of physical, network, cloud, and virtual IT assets in real time. CimTrak provides detailed analysis, evidence, and automated workflows that enforce an unprecedented security posture, ensures operational availability, stops zero-day attacks, detects unexpected changes, and achieves and maintains continuous compliance in a simple and cost-effective manner.

Average Rating: 4.8/5.0

Total Reviews: 23

How Do G2 Users Rate CimTrak Integrity Suite?

  • Ease of Admin: 9.2/10 (Category avg: 9.0/10)

Who Is the Company Behind CimTrak Integrity Suite?

  • Seller: Cimcor
  • Company Website:
  • Year Founded: 1997
  • HQ Location: Merrillville, Indiana, United States
  • Twitter: @cimtrak
    2,203 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    28 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 33% Medium

What Do G2 Reviewers Say About CimTrak Integrity Suite?

AI-generated summary from verified user reviews

Pros
  • Users find the compliance checking feature of CimTrak Integrity Suite to be very useful and easy to navigate.
  • Users appreciate the useful compliance checking feature of CimTrak Integrity Suite, enhancing PCI Compliance management effectively.
  • Users highlight the unbeatable ease of use of CimTrak Integrity Suite, making compliance tasks straightforward and efficient.
  • Users rave about the outstanding customer support from CimTrak, noting the team's knowledge and availability.
  • Users value the real-time monitoring of CimTrak, allowing immediate detection of file modifications and potential threats.
Cons
  • Users find the dashboard issues and outdated report scheduler detract from the overall user experience of CimTrak.
  • Users find the upgrade process cumbersome, wishing for a more integrated solution to simplify updates.
  • Users note compliance issues due to outdated UI and a lack of effective dashboards in the CimTrak Integrity Suite.
  • Users feel a strong need for better guidance during upgrades, preferring an integrated upgrade process for efficiency.
  • Users find the poor customer support of CimTrak Integrity Suite frustrating, impacting their overall experience and effectiveness.

What Are Recent G2 Reviews of CimTrak Integrity Suite?

Defensia

Defensia is a real-time server security platform for Linux. It detects and blocks brute-force attacks, port scans, web exploits, and malicious bots automatically — without complex configuration. It works through a lightweight open-source agent that installs in a single command (\~30 seconds). The agent monitors SSH authentication, web server logs, and network activity, then takes immediate action: banning malicious IPs, detecting vulnerability scanners, and blocking known attack patterns through its built-in Web Application Firewall (WAF). Everything is managed from a centralized cloud dashboard where teams can monitor all their servers in one place, review security events, configure protection policies per server, and receive real-time alerts via email. Key capabilities: * SSH brute-force protection — Detects failed login attempts and automatically bans repeat offenders with escalating durations (24h → 7 days → 30 days → permanent) * Web Application Firewall (WAF) — Blocks SQL injection, XSS, path traversal, shell injection, and 10+ other web attack categories directly at the log level * Bot management — Identifies 60+ known bots (search engines, AI crawlers, security scanners) with per-server allow/log/block policies * Threat intelligence network — Shares anonymized attack data across all Defensia-protected servers, so a threat detected on one server is blocked everywhere * Monitor mode — New servers start in observation-only mode so teams can review detections before enabling active blocking * Security scanning — On-demand hardening audits (SSH config, file permissions, web server settings) with one-click remediation for common issues * Real-time alerts — Instant email notifications for bans, critical events, server disconnections, and WAF attacks Who uses Defensia? Developers, sysadmins, and small DevOps teams running 1–50 Linux servers on any cloud provider (DigitalOcean, Hetzner, OVH, AWS, Linode) or bare metal. It's built for people who need production-grade server security without dedicating time to configure and maintain complex firewall rules. Deployment: One command installs the agent on any Ubuntu, Debian, CentOS, AlmaLinux, Rocky Linux, or CloudLinux server. No dependencies, no kernel modules, no Docker required on the server side. Available as a DigitalOcean 1-Click Droplet for instant deployment. Pricing: Free plan (1 server) with a Pro plan at 7 EUR/server/month for unlimited servers, advanced analytics, auto-remediation, and the full threat intelligence network.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Defensia?

  • Ease of Admin: 10.0/10 (Category avg: 9.0/10)
  • API / Integrations: 5.0/10 (Category avg: 8.6/10)
  • Security Auditing: 10.0/10 (Category avg: 8.9/10)

Who Is the Company Behind Defensia?

  • Seller: Defensia
  • Year Founded: 2026
  • HQ Location: Barcelona, ES
  • LinkedIn® Page: www.linkedin.com
    1 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Defensia?

Styra

Styra are the creators and maintainers of Open Policy Agent and leaders in cloud-native authorization. Our mission at Styra is to provide unified authorization and policy across the cloud-native stack. Styra enables enterprises to define, enforce and monitor policy across their cloud-native environments. With a combination of open source (Open Policy Agent) and commercial products (Styra Declarative Authorization Service and Styra Run), Styra provides security, operations and compliance guardrails to protect applications, as well as the infrastructure they run on. Styra policy-as-code approach lets developers, DevOps, and security teams mitigate risks, reduce human error and accelerate application development. Styra is rethinking authorization policy by providing enterprises with context-based policy guardrails to mitigate risk, reduce errors and accelerate development

Average Rating: 4.5/5.0

Total Reviews: 3

How Do G2 Users Rate Styra?

  • Ease of Admin: 6.7/10 (Category avg: 9.0/10)

Who Is the Company Behind Styra?

  • Seller: Styra
  • Year Founded: 2016
  • HQ Location: Redwood City, US
  • Twitter: @styrainc
    3,357 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    19 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Large, 33% Small

What Are Recent G2 Reviews of Styra?

Uptycs

Uptycs unified CNAPP and XDR platform is a comprehensive security solution designed to protect the full spectrum of modern attack surfaces in your cloud, data centers, user devices, build pipelines, and containers. With a strong focus on DevSecOps, Uptycs offers a powerful combination of CNAPP capabilities, including Cloud Workload Protection Platform (CWPP), Kubernetes Security Posture Management (KSPM), Cloud Security Posture Management (CSPM), Cloud Infrastructure Entitlement Management (CIEM), and Cloud Detection and Response (CDR). With Uptycs you also get industry-leading eXtended Detection and Response (XDR) across macOS, Windows, and Linux endpoints, ensuring comprehensive protection, detection, and investigation. Uptycs delivers real-time threat detection, context-rich alerts, and maps detections to the MITRE ATT&CK framework for improved security insights. Uptycs performs scanning of containers for vulnerabilities throughout the CI/CD pipeline, promoting agile DevOps workflows, and reducing risk in production environments. Uptycs seamlessly integrates with existing tools and processes, streamlining operations and improving overall efficiency. Customers also benefit from the flexibility to choose between agent-based and agentless scanning options tailored to their unique cloud workload needs. Discover how Uptycs can transform your security posture with a comprehensive, flexible, and powerful security solution designed to meet the needs of today's complex and rapidly evolving cloud environments. Shift up with Uptycs. KEY DIFFERENTIATORS: 1. Unified & Comprehensive Platform: Uptycs offers a holistic security solution with CNAPP capabilities (CWPP, KSPM, CSPM, CIEM, and CDR) across data centers, laptops, build pipelines, containers, and cloud environments, reducing tool sprawl. 2. Advanced XDR: Industry-leading eXtended Detection and Response for endpoint protection across macOS, Windows, and Linux systems. 3. DevSecOps Focus: Enhanced security for container-based workloads and Kubernetes, supporting agile DevOps workflows. 4. Real-Time Threat Detection: Context-rich alerts and threat detection mapped to the MITRE ATT&CK framework for improved insights. 5. CI/CD Integration: Efficiently scan containers for vulnerabilities throughout the CI/CD pipeline, reducing risk in production. 6. Both agent-based and agentless scanning. Deploy agentless scanning for rapid, friction-free coverage to keep your data secure, and gain continuous runtime security, real-time investigations, and remediation with agent-based telemetry. 7. Rich API & Compatibility: Seamless integration with existing security tools and platforms, powered by osquery for broad compatibility. 8. Expert Support & Flexibility: Dedicated support from security experts and the best of both worlds with agent-based and agentless scanning options tailored to your needs.

Average Rating: 4.4/5.0

Total Reviews: 13

How Do G2 Users Rate Uptycs?

  • Governance: 5.0/10 (Category avg: 8.8/10)
  • Ease of Admin: 8.3/10 (Category avg: 9.0/10)
  • API / Integrations: 3.3/10 (Category avg: 8.6/10)
  • Security Auditing: 6.7/10 (Category avg: 8.9/10)

Who Is the Company Behind Uptycs?

  • Seller: Uptycs
  • Year Founded: 2016
  • HQ Location: Waltham, US
  • Twitter: @uptycs
    1,483 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 54% Medium, 38% Large

What Do G2 Reviewers Say About Uptycs?

AI-generated summary from verified user reviews

Pros
  • Users value the comparative analysis features of Uptycs, aiding in selecting the best cloud security tools.
  • Users appreciate the comparative analysis features of Uptycs, aiding them in selecting the best cloud security tools.
  • Users value the comparative analysis features of Uptycs for making informed decisions in cloud security tools.
  • Users value Uptycs for its compliance with CIS and PCI DSS standards, enhancing security monitoring capabilities.
  • Users value the compliance management of Uptycs, appreciating its adherence to CIS and PCI DSS standards.
Cons
  • Users regret the high fees of Uptycs, which impact their willingness to continue using the tool.
  • Users express concerns about high pricing, which makes continued use of Uptycs challenging for some.

What Are Recent G2 Reviews of Uptycs?

Araali Network Security Pro

Araali Networks allows lean security teams to discover their exposure - data, services, and backdoors and prioritize the top 1% of risks that really matter. The security team can use cloud-native controls or Araali's ebpf firewall to create compensating controls to neutralize these risks. In addition, Araali is introducing a new feature that allows teams to patch their CVEs, automatically using Araali - this is a game changer as it allows team to knock off 90% of critical CVEs with little effort. Coverage: VMs, Containers, and Kubernetes across the public and private clouds. How: Araali automatically discovers your apps, their networking, access privileges, and security risks. It also creates and maintains the least privilege policies for all the apps. Your teams can enforce explicit policies for “who can do what” in your virtual private cloud, blocking malicious code from establishing a backdoor or accessing your services. Araali's customers include cloud-native startups, mid-market enterprises, and government agencies. To learn more visit www.araalinetworks.com or create a free trial account by signing up on console.araalinetworks.com Use Cases: 1) SOC-2 compliance: IDS/IPS, vulnerability management, asset management, vulnerability compensation controls, app access control for 2) Egress Filtering: Monitor and control egress to third-party sites, backdoors, supply chain attacks, and ransomware 3) Risk Prioritization: Visibility into the runtime - apps and associated risks 4) Vulnerability Management and Vulnerability Shielding: prevent vuln from getting exploited - especially useful for zero-day or cases where patches are not available as seen in Log4j 5) Enforcement: Proactively or Reactively Neutralize Threats to stop them from moving laterally and exfiltrating your data.

Average Rating: 4.3/5.0

Total Reviews: 3

Who Is the Company Behind Araali Network Security Pro?

Who Uses This Product?

  • Company Size: 67% Small, 33% Medium

What Do G2 Reviewers Say About Araali Network Security Pro?

AI-generated summary from verified user reviews

Pros
  • Users value the precision in threat alerting that aids in identifying and mitigating zero-day vulnerabilities effectively.
  • Users value the seamless API integration of Araali Network Security Pro, enhancing threat detection and mitigation capabilities.
  • Users value the detection efficiency of Araali Network Security Pro, effectively identifying and addressing zero-day vulnerabilities.
  • Users commend the seamless integrations of Araali Network Security Pro, enhancing their security tool ecosystem effectively.
  • Users value the seamless integration and precision in threat detection of Araali Network Security Pro.
Cons
  • Users find the complex coding challenging, as it delays security alerts and hinders timely incident response.
  • Users find that delayed detection hampers incident response, especially with complex network setups.
  • Users find the ineffective alerts from Araali Network Security Pro hinder timely incident responses, especially in complex networks.
  • Users experience delays in receiving security alerts, complicating incident response for complex network infrastructures.
  • Users experience challenges with network issues, facing delays in security alerts that hinder timely incident response.

What Are Recent G2 Reviews of Araali Network Security Pro?

kaimon

kaimon is a file integrity monitoring (FIM) platform built for Linux infrastructure. It uses an eBPF kernel agent to capture every file lifecycle event - create, modify, move, delete, attribute change and write - with full process, user and device context, across bare-metal servers, virtual machines and containerized workloads. Traditional file integrity monitoring tools push raw filesystem events into a SIEM and expect a security engineer to spend weeks writing suppression rules before the output means anything to an auditor. Most evaluations end before that point, because a tool that reports thousands of routine deployment writes as findings is worse than no tool at all. kaimon replaces that work with AI-powered automatic baselining. On deployment the agent begins learning immediately. Over seven days it runs progressive, time-staggered analysis to capture every layer of operational noise - container startup artifacts, log rotation, package updates, nightly cron and weekly maintenance - and generates narrowly scoped suppression rules for legitimate activity. On day seven the baseline locks and the system becomes deterministic: anything that does not match established patterns is a genuine anomaly worth investigating. The baseliner is security-aware by design. It refuses to suppress changes to credential stores, privilege configuration, service unit definitions, SSH key files or system logs, so an attacker cannot teach it to ignore malicious behavior during the learning window. Built-in detection categories classify anomalies by severity out of the box: unauthorized changes to credential and privilege files, persistence mechanisms including SSH key injection, service backdoors and dynamic linker hijacking, log tampering, kernel module and driver changes, data exfiltration to removable media or via archive creation, permission and ownership manipulation, cron modifications, and package installs outside declared maintenance windows. Container coverage is native. A single kernel agent resolves overlay filesystem paths for Docker, Kubernetes, containerd, Podman, CRI-O and LXC, with no sidecars, no image modifications and no per-container agents. Reports are generated daily and map directly to the controls auditors ask about: SOC 2 CC6 and CC7, HIPAA 164.312(c)(1), PCI DSS 10.5.5 and 11.5, and NIST SP 800-53 SI-7. Each carries an AI-written, framework-specific verdict covering workload profile, anomaly assessment and compliance status. Evidence exports as PDF, HTML or JSON, and delivers by webhook to any SIEM, Slack, Discord or email. An interactive dashboard provides forensic deep search across the entire fleet, filtering by host, user, process and file path, for engineers who need more than an executive summary. Deployment is a single command. The agent detects the distribution and architecture, verifies checksums, installs, and configures itself. Deploy, baseline, report - with no regex, no rule authoring and no security engineer in the loop.

Who Is the Company Behind kaimon?

Oasis Defender

Oasis Defender provides comprehensive protection across *multiple* cloud environments. **Multi-dimensional visualization** - **Cloud Map** visualizes the entire network infrastructure across multiple clouds - **Policy Map** visualizes cloud security policies - **Security Map** highlights and helps to remediate security issues **Automated security analysis** - **Network security analysis:** Oasis Defender performs network security analysis based on industry best practices and provides actionable recommendations for remediation - **Data storage security analysis:** Oasis Defender analyzes the security of data stores in cloud environments, checking access controls and permissions **Agentless architecture** - **Instant** onboarding - **Seamless** integration - **Preserves** your existing topology - **Reduces** potential weak points for attackers Designed for organizations of all sizes, it helps protect their cloud environments from potential security breaches with *minimal effort*.
Seamlessly integrating with DigitalOcean's existing infrastructure, Oasis Defender provides a hassle-free way to *increase security* and *ensure compliance*, providing *peace of mind* so customers can focus on growing their business.

Who Is the Company Behind Oasis Defender?

Saner Cloud

Saner Cloud is an AI-fortified Cloud-Native Application Protection Platform (CNAPP) that moves beyond detection. It empowers organizations with intelligent, real-time, and automated attack prevention. Unlike traditional cloud security solutions that overwhelm security teams with alerts but fail to act, Saner Cloud automatically fixes vulnerabilities, misconfigurations, identity risks, and compliance violations across multicloud environments. Why choose Saner Cloud? - Unified dashboard with real-time updates and interactive visuals for a single source of truth - Complete asset visibility with watchlists, exposure detection, region-based categorization, deprecated services, and cost analysis - AI-driven anomaly detection with confidence levels, severity distribution, whitelisting options, and one-click remediation - Continuous posture management with built-in benchmarks, quick misconfiguration checks, trend tracking, and drift detection - Risk prioritization with scoring, top-risk lists, and context across assets, posture, and anomalies to focus on which risk to remediate first - Identity and entitlement governance with policy maps, RBAC, resource groups, excessive permission detection, and activity logging - Enhanced Remediation with scheduling and approval workflows, Top 10 patches, patch aging, most-impactful-patches charts, and grouped remediation - Multi-cloud coverage across AWS, GCP and Azure with a prevention-first workflow - Smart tagging for fast filtering across thousands of resources and audit logs with tool-specific job codes for full traceability

Who Is the Company Behind Saner Cloud?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • Twitter: @secpod
    542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®
Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024