Best Cloud Security Monitoring and Analytics Software - Page 4

Last updated: October 3, 2024

How Many Cloud Security Monitoring and Analytics Software Products Does G2 Track?

Total Products under this Category: 86

Category Stats (Nov 2026)

  • Average Rating: 4.51/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: AppOmni (+2.3%) - Among all products in this category, AppOmni recorded the largest rating increase compared to last month

Last updated: November 18, 2026

How Does G2 Rank Cloud Security Monitoring and Analytics Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,900+ Authentic Reviews
  • 86+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

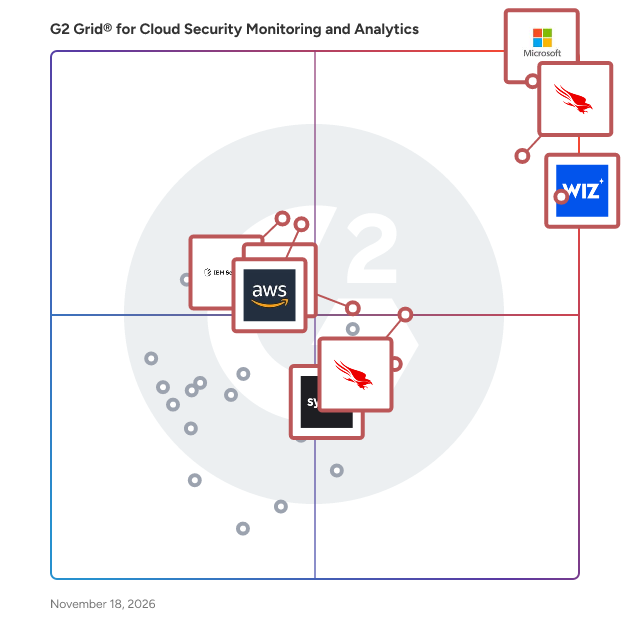
G2 Grid® for Cloud Security Monitoring and Analytics Software

G2 Grid® for Cloud Security Monitoring and Analytics Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security, Wiz, CrowdStrike Falcon Shield, Amazon GuardDuty, IBM QRadar SIEM, Falcon Next-Gen SIEM, and Sysdig Secure.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-security-monitoring-and-analytics/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=wiz-wiz&focus%5B%5D=crowdstrike-falcon-shield&focus%5B%5D=amazon-guardduty&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=falcon-next-gen-siem&focus%5B%5D=sysdig-sysdig-secure)

Darktrace / EMAIL

Darktrace / EMAIL secures email and collaboration by training exclusively on each organization’s own communication patterns, not shared threat intelligence. It builds a Unique Behavioral Profile for every user – spanning email, identity, DLP, and human risk – to catch novel phishing, business email compromise, and account takeover that signature-based tools miss by design. It’s recognized as a Leader in Gartner’s Magic Quadrant and in the 2025 Voice of the Customer for Email Security Platforms. Traditional secure email gateways and native protections rely on known threat intelligence, so they need a first victim before they can catch a new attack – and generative AI has only widened that gap. Darktrace / EMAIL takes a different approach: it uses Adaptive AI to build a Unique Behavioral Profile for every user, then detects deviations across inbound, outbound, and lateral mail and responds with precise, autonomous action. Key capabilities include: - Adaptive Email Security: Builds a Unique Behavioral Profile for every user across the full mail flow – inbound, outbound, and lateral protection, DMARC management, account takeover detection, data loss detection, and AI attack/GenAI visibility. Darktrace catches on average 17% of threats that leading SEGs miss on arrival. - Identity Detect & Respond: Adds autonomous response to account takeover – session termination and forced re-authentication – plus recovery and audit across email, SaaS, and cloud. - Email DLP & Collaboration Security: Suspicious emails are automatically quarantined, links are rewritten, and attachments are removed, extending detection with hold, redirect, and strip-sensitive-content response actions plus dedicated behavioral coverage across Microsoft Teams, Zoom, and Slack, all without interrupting legitimate business communication. - Adaptive Security Awareness Training: Personalizes training, phishing simulations, and just-in-time coaching to each employee’s actual behavior, with outcomes feeding back into the detection model to close the loop. For security teams, Darktrace / EMAIL reduces operational overhead by automating triage and response. Its Cyber AI Analyst provides contextual insights, while end-users benefit from clear, in-app narratives that explain why a message is suspicious – helping to reduce false phishing reports and improve awareness. Benefits for organizations include: - Coverage across email, collaboration, and SaaS platforms in one behavioral model. - Up to 90% less time spent triaging alerts, so security teams spend more time on higher-value work. - Native integration with Microsoft 365, Exchange, and Google Workspace that doesn’t disrupt mail flow. Darktrace / EMAIL is a Gartner Leader in both the Magic Quadrant and the 2025 Voice of the Customer for Email Security Platforms – recognition that tracks with what it actually catches: threats built for a specific business, not just known attack patterns.

Average Rating: 4.2/5.0

Total Reviews: 43

How Do G2 Users Rate Darktrace / EMAIL?

  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)

Who Is the Company Behind Darktrace / EMAIL?

  • Seller: Darktrace
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®
  • Ownership: LON: DARK

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 58% Medium, 33% Large

What Do G2 Reviewers Say About Darktrace / EMAIL?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the adaptive AI detection of Darktrace, making security management seamless and effective.
  • Users appreciate the excellent customer support provided by Darktrace, enhancing their experience and ensuring quick assistance.
  • Users appreciate the high detection efficiency of Darktrace EMAIL, ensuring minimal malicious emails slip through.
  • Users commend the superior product quality of Darktrace, benefiting from reliable security and excellent support services.
  • Users highlight the reliability of Darktrace EMAIL, offering confidence in email account protection and malicious detection.
Cons
  • Users note that Darktrace / EMAIL is expensive, though they acknowledge its value justifies the cost.
  • Users experience poor integration with Darktrace, particularly with Outlook on Windows and Mac, affecting usability.
  • Users find the complexity of the wording and descriptions challenging, requiring specialized IT knowledge for effective use.
  • Users experience false positives as emails are often blocked, but they can easily release and whitelist them.
  • Users find the regular software updates to be tedious and detracting from the overall experience of Darktrace / EMAIL.

What Are Recent G2 Reviews of Darktrace / EMAIL?

Data Theorem Cloud Secure

Data Theorem's Cloud Secure is an automated, continuous security service that integrates Cloud-Native Application Protection Platform (CNAPP) and Application Security (AppSec) capabilities across multi-cloud environments, encompassing both public and private assets. It offers a comprehensive, application-centric approach to cloud security, ensuring robust protection for cloud-native applications and infrastructure. Key Features and Functionality: - Monitoring: Implements Cloud Security Posture Management (CSPM) for continuous asset discovery, vulnerability assessments—including Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Software Composition Analysis (SCA), and Infrastructure as Code (IaC) analysis—and Cloud Identity and Entitlement Management (CIEM). - Hacking: Utilizes innovative Hacker Toolkits that provide daily updates on security vulnerabilities and exploits, identifying potential external attack vectors and data breach risks within cloud environments. - Protection: Offers runtime protections designed to prevent data breaches across cloud-native APIs and applications, leveraging Data Theorem's Software Development Kit (SDK) libraries for real-time telemetry collection and policy-based blocking. Primary Value and Problem Solved: Cloud Secure addresses the critical need for comprehensive security in cloud-native applications by providing continuous monitoring, proactive vulnerability identification, and real-time protection mechanisms. By integrating CNAPP and AppSec functionalities, it enables organizations to effectively manage and secure their multi-cloud assets, thereby reducing the risk of data breaches and ensuring compliance with security standards. This holistic approach empowers businesses to maintain a strong security posture in the dynamic landscape of cloud computing.

Average Rating: 4.5/5.0

Total Reviews: 3

How Do G2 Users Rate Data Theorem Cloud Secure?

  • Security Integration: 7.5/10 (Category avg: 8.6/10)
  • Activity Monitoring: 6.7/10 (Category avg: 8.5/10)
  • Security Automation: 6.7/10 (Category avg: 8.6/10)

Who Is the Company Behind Data Theorem Cloud Secure?

Who Uses This Product?

  • Company Size: 67% Medium, 33% Small

What Are Recent G2 Reviews of Data Theorem Cloud Secure?

FireMon Cloud Defense

FireMon Cloud Defense is the only distributed cloud security operations platform with real-time cloud security posture management, threat detection and response, and enhanced identity protection.

Average Rating: 4.3/5.0

Total Reviews: 3

How Do G2 Users Rate FireMon Cloud Defense?

  • Security Integration: 7.5/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.3/10 (Category avg: 8.5/10)
  • Security Automation: 7.8/10 (Category avg: 8.6/10)

Who Is the Company Behind FireMon Cloud Defense?

  • Seller: FireMon
  • Year Founded: 2004
  • HQ Location: Overland Park, KS
  • LinkedIn® Page: www.linkedin.com
    269 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Small, 33% Large

What Are Recent G2 Reviews of FireMon Cloud Defense?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

Cisco BroadWorks

Cisco BroadWorks is an enterprise-grade calling and collaboration platform delivering unmatched performance, security and scale. Hosted by Cisco service provider partners, it integrates with Cisco Webex to meet the full range of enterprise communications and collaboration needs.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate Cisco BroadWorks?

  • Security Integration: 8.3/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.3/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 8.3/10 (Category avg: 8.6/10)

Who Is the Company Behind Cisco BroadWorks?

  • Seller: Cisco
  • Year Founded: 1984
  • HQ Location: San Jose, CA
  • LinkedIn® Page: www.linkedin.com
    95,294 employees on LinkedIn®
  • Ownership: NASDAQ:CSCO
  • Phone: 847-678-6600

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Are Recent G2 Reviews of Cisco BroadWorks?

Hillstone CloudView

Hillstone CloudView is a cloud-based security management and analytics platform which provides SaaS security services across the Hillstone E-Series Next-Generation Firewalls (NGFW), T-Series Intelligent Next-Generation Firewalls (iNGFW), I-Series Network Intrusion Prevention System (NIPS) and Hillstone Virtual NGFW CloudEdge. The Hillstone CloudView service empowers security administrators to take swift action with real-time centralized monitoring of multiple devices, traffic and threat analytics, real-time alarms, as well as comprehensive reporting and log retention. With the 24/7 mobile and web access from anywhere on any devices, it delivers optimal customer experience along with optimized security management and operational efficiencies.

Average Rating: 4.8/5.0

Total Reviews: 2

Who Is the Company Behind Hillstone CloudView?

Who Uses This Product?

  • Company Size: 50% Large, 50% Small

What Are Recent G2 Reviews of Hillstone CloudView?

Skyhigh Cloud-Native Application Protection Platform

Skyhigh Cloud Native Application Protection Platform CNAPP is the industry’s first platform to extend Cloud Access Security Broker CASB, bringing application and data context to converge Cloud Security Posture Management CSPM with IaaS Data Loss Prevention DLP for IaaS public clouds. Skyhigh CNAPP provides consistent data protection, threat prevention, governance, and compliance throughout the cloud-native application development lifecycle. Skyhigh CNAPP is consolidated into a fully converged platform and managed from the same single console as the rest of the Skyhigh SSE services.

Average Rating: 4.8/5.0

Total Reviews: 2

How Do G2 Users Rate Skyhigh Cloud-Native Application Protection Platform?

  • Security Integration: 9.2/10 (Category avg: 8.6/10)
  • Activity Monitoring: 7.5/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 9.2/10 (Category avg: 8.6/10)

Who Is the Company Behind Skyhigh Cloud-Native Application Protection Platform?

Who Uses This Product?

  • Company Size: 100% Medium

What Are Recent G2 Reviews of Skyhigh Cloud-Native Application Protection Platform?

Atmosec

Atmosec takes a holistic approach to securing your ever evolving SaaS ecosystem. Focusing not only on individual services or specific users, Atmosec also understands how different services communicate with each other, how users interact with the ecosystem as well as what data might be passing between different services. Our unique platform monitors the behavior of an unlimited number of SaaS services, as they interact with users and each other and automates the mitigation of actual and potential risks, proactively flagging any anomalies or misconfigurations so that CIOs and CISOs can address them with better visibility and confidence. With advanced Machine Learning capabilities Atmosec alerts on abnormal activity of credentials, over-privileged accounts and API usage as well as stopping SaaS Supply Chain attacks.

Average Rating: 4.0/5.0

Total Reviews: 2

Who Is the Company Behind Atmosec?

  • Seller: Atmosec
  • Year Founded: 2021
  • HQ Location: Tel Aviv, IL
  • LinkedIn® Page: www.linkedin.com
    3 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 50% Medium

What Are Recent G2 Reviews of Atmosec?

Gauntlet

Gauntlet mitigates risks like security breaches, data theft, and compliance violations with Generative AI (GenAI), enhancing efficiency by accelerating time-to-fix by 60%. Its core pillars include Cloud Security Posture Management (CSPM) for proactive vulnerability remediation, Software Supply Chain Security (SBOM) for component transparency, Secrets Scanning to safeguard sensitive credentials, and AI Security Posture Management (AISPM) to secure cloud-based AI services. Gauntlet ensures seamless compliance with over 20 global standards, including HIPAA, FDA, and GDPR, making regulatory adherence effortless for organizations. This powerful platform reduces human error and optimizes operational security at every level. Visit https://www.gauntlet.security for more information.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Gauntlet?

  • Security Integration: 8.3/10 (Category avg: 8.6/10)
  • Activity Monitoring: 5.0/10 (Category avg: 8.5/10)
  • Security Automation: 8.3/10 (Category avg: 8.6/10)

Who Is the Company Behind Gauntlet?

Who Uses This Product?

  • Company Size: 100% Small

What Do G2 Reviewers Say About Gauntlet?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the clear guidance and precise recommendations provided by Gauntlet, enhancing their overall experience.
  • Users value the clear information and guidance from Gauntlet, benefiting from easy-to-read summaries and precise remediation recommendations.
  • Users value Gauntlet's clear reporting and guidance, highlighting easy summaries and precise remediation recommendations.
Cons
  • Users find the inefficient alert system frustrating, as it lacks proactive solutions for urgent issues.

What Are Recent G2 Reviews of Gauntlet?

Gurucul

Gurucul is the only cost-optimized security analytics company founded in data science that delivers radical clarity about cyber risk. Our REVEAL security analytics platform analyzes enterprise data at scale using machine learning and artificial intelligence. Instead of useless alerts, you get real-time, actionable information about true threats and their associated risk. The platform is open, flexible and cloud native. It conforms to your business requirements so you don't have to compromise. Our technology has earned us recognition from leading industry analysts as the most Visionary platform and an Overall leader in product, market and innovation. Our solutions are used by Global 1000 enterprises and government agencies to minimize their cybersecurity risk. To learn more, visit Gurucul.com

Average Rating: 3.0/5.0

Total Reviews: 2

How Do G2 Users Rate Gurucul?

  • Security Integration: 5.0/10 (Category avg: 8.6/10)
  • Activity Monitoring: 6.7/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 6.7/10 (Category avg: 8.6/10)

Who Is the Company Behind Gurucul?

  • Seller: Gurucul
  • Year Founded: 2010
  • HQ Location: El Segundo, US
  • LinkedIn® Page: www.linkedin.com
    288 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Large, 50% Medium

What Do G2 Reviewers Say About Gurucul?

AI-generated summary from verified user reviews

Pros
  • Users find that Gurucul's effective alerting reduces alert fatigue by prioritizing high-risk threats for security analysis.
  • Users value the alert reduction from Gurucul, as it mitigates fatigue by highlighting high-risk threats effectively.
  • Users find the self-explanatory dashboard of Gurucul comprehensive and reliable for security posture management.
  • Users value the self-explanatory dashboard of Gurucul, praising its reliability and comprehensive coverage of security posture.
  • Users value the data protection features of Gurucul, ensuring reliable log ingestion and security posture management.
Cons
  • Users experience delayed alert population from threat intel feeds, impacting timely response and usability in Gurucul.
  • Users find the cloud dependency tedious, hindering efficient utilization of security analytics in Gurucul's REVEAL.
  • Users report that the complex parsing of threat intel feeds delays alert population on the Gurucul console.
  • Users find the tedious cloud migration process hampers the effective utilization of Gurucul's security analytics capabilities.
  • Users experience ineffective alerts due to delays in populating threat intel integration feeds on the console.

What Are Recent G2 Reviews of Gurucul?

ImmuniWeb AI Platform

The ImmuniWeb AI Platform helps over 1,000 enterprise customers from more than 50 countries to test, secure and protect their web and mobile applications, APIs and microservices, cloud and networks, to prevent data breaches and reduce third-party risk, and to comply with regulatory requirements. ImmuniWeb’s products available on the Platform include Continuous Threat Exposure Management (CTEM), External Attack Surface Management (EASM), Dark Web Monitoring and phishing websites takedown, as well as vulnerability scanning and penetration testing for web and mobile apps, cloud and network infrastructure, and LLM models. Headquartered in Geneva, Switzerland, ImmuniWeb has offices in Washington, London and Dubai to provide an uninterrupted service to all global customers and partners.

Average Rating: 4.7/5.0

Total Reviews: 12

How Do G2 Users Rate ImmuniWeb AI Platform?

  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind ImmuniWeb AI Platform?

Who Uses This Product?

  • Company Size: 92% Medium, 8% Small

What Do G2 Reviewers Say About ImmuniWeb AI Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the continuous monitoring of the attack surface that prevents potential financial and reputational losses.
  • Users value the continuous monitoring efficiency of ImmuniWeb AI Platform, enhancing security and reducing operational overhead.
  • Users value the alert notifications from ImmuniWeb AI, keeping them informed about critical issues to prevent potential losses.
  • Users value the detailed remediation steps and responsive support offered by ImmuniWeb AI Platform for efficient testing.
  • Users commend the effective communication from ImmuniWeb AI Platform's account managers, enhancing client satisfaction and support.
Cons
  • Users find the varying complexity of targets makes it hard to estimate scanning times accurately.
  • Users find the lack of integration with Slack or PagerDuty challenging, especially for on-call engineers outside regular hours.
  • Users find the lack of integration with Slack or PagerDuty challenging, especially for on-call engineers after hours.
  • Users find the limited Excel export feature restrictive compared to the comprehensive JSON format available.
  • Users report a limited flexibility in the past with the algorithm for cost calculation, though improvements have been noted.

What Are Recent G2 Reviews of ImmuniWeb AI Platform?

What Are G2 Users Discussing About ImmuniWeb AI Platform?

Obsidian Security

Obsidian Security is the first truly comprehensive threat and posture management solution built for SaaS. Our platform consolidates data across core applications to help your team optimize configurations, reduce over-privilege, and mitigate account compromises and insider threats. Getting started with Obsidian takes just a few minutes—with no agents to deploy or rules to write.

Average Rating: 4.0/5.0

Total Reviews: 3

How Do G2 Users Rate Obsidian Security?

  • Has the product been a good partner in doing business?: 5.8/10 (Category avg: 9.2/10)

Who Is the Company Behind Obsidian Security?

Who Uses This Product?

  • Company Size: 67% Large, 67% Medium

What Do G2 Reviewers Say About Obsidian Security?

AI-generated summary from verified user reviews

Pros
  • Users praise the exceptional customer support from Obsidian, ensuring smooth implementation and successful outcomes.
  • Users highlight the ease of implementation with Obsidian Security, facilitated by excellent customer support and service.
  • Users commend the smooth onboarding process with Obsidian, benefiting from exceptional customer support during implementation.
  • Users praise Obsidian for its comprehensive solution, delivering valuable outcomes and excellent customer support in SaaS security.
Cons
  • Users find that the dashboard issues hinder functionality and overall user experience with Obsidian Security.
  • Users note inadequate threat analysis with Obsidian Security, citing limited reports and unhelpful dashboards impacting effectiveness.
  • Users find the limited reporting capabilities of Obsidian Security lacking compared to other SSPM solutions.
  • Users feel that the reporting issues in Obsidian Security hinder its effectiveness compared to other offerings.
  • Users find that the platform has limited functionality in dashboards, affecting the overall user experience.

What Are Recent G2 Reviews of Obsidian Security?

Saasment SaaS Security

Fully automated security marketplace to help digital businesses protect against cyber threats and data loss. Companies are now highly dependent on their digital environment for critical business functions like file sharing, collaboration, code management, and customer relationship. An emerging challenge for these companies is how to stay secure while continue and grow their digital business as they: 1) Have no understanding of how to protect against attacks. 2) Don’t have the personnel to address IT security. 3) Have failed to act following a cybersecurity incident. In our SaaS Security portfolio, you can find the following features 1) Proactive Threats Protection - Based on cloud-native security controls, proactively take action to mitigate risks before they evolve to breach. Revoke permissions, limit sharing & manage incident response. 2) Ongoing Backups - Prevent from losing mission-critical data and metadata with automated backups and rapid recovery. 3) Prevent Human Erros - Empowers employees with the knowledge and skills to stay cyber secure at work and home by automating communications and simulate cyberthreats. 4) Stay Compliant - Simplifying the complex, time-consuming, and tedious process of becoming SOC2, PCI, or ISO 27001 compliant. Saasment easily integrates with all your cloud applications seamlessly.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Saasment SaaS Security?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)

Who Is the Company Behind Saasment SaaS Security?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Saasment SaaS Security?

What Are G2 Users Discussing About Saasment SaaS Security?

Tenant Strike

Tenant Strike shows small and mid-sized businesses what an attacker would see in their Microsoft 365 and Azure environment - and exactly how to fix it. Connect in about five minutes with read-only access. Tenant Strike runs 130+ checks across identity, email, sharing, apps, devices, Azure infrastructure, audit logging, and your internet-facing attack surface. You get an A-F posture grade, per-category subscores, and a prioritized fix plan written in plain English, with the portal steps for each change and a warning about what it might break before you make it. Attacker's View is the part customers keep. A list of findings is not a list of breaches, so Tenant Strike correlates findings into the multi-step attack paths a real intruder would use - password spray to mailbox rule to invoice fraud, illicit app consent to silent mailbox exfiltration, an exposed server to credential reuse to tenant takeover - ranked by exploit likelihood and impact, each with the one change that breaks the chain. Read-only by design, and provable. Tenant Strike never requests write permissions. Every API endpoint it reads is published on a public trust page, generated automatically from the source on every release, and the build fails if anything capable of making a change is ever introduced. When a control cannot be verified with read-only access, the report says "unverified" and gives you a one-command way to confirm it yourself - it never guesses, and never reports green on something it could not read.

Average Rating: 5.0/5.0

Total Reviews: 1

How Do G2 Users Rate Tenant Strike?

  • Security Integration: 10.0/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Tenant Strike?

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Tenant Strike?

AIceberg

AIceberg is an enterprise-grade AI security platform that provides real-time, automated validation of all AI application traffic, including speech, text, and source code. By implementing robust safety measures, AIceberg ensures that only use case-relevant AI interactions are permitted, preventing unsanctioned, unsuitable, or illegal content. The platform automatically redacts personal or sensitive information, maintaining user privacy. AIceberg's security features detect common AI cybersecurity threats such as prompt injection and jailbreaking, ensuring that security postures are always up to date. Additionally, the platform offers comprehensive compliance, transparency, and auditability through explainable, non-generative AI models, providing maximum accuracy and end-to-end auditability. Enterprise observability across all AI interactions allows organizations to understand common prompts, objectives, and intentions, enhancing user experience and providing valuable business intelligence.

Who Is the Company Behind AIceberg?

  • Seller: AIceberg
  • Year Founded: 2022
  • HQ Location: New York, US
  • LinkedIn® Page: www.linkedin.com
    34 employees on LinkedIn®

Anomali Security Analytics

Anomali is the ultra-modern SIEM, fusing the key capabilities of ETL, SIEM, Next-Gen SIEM, XDR, UEBA, SOAR, and TIP into a single, high-speed data lake — with 7+ years of always-hot storage for instant access to historical data. A system of action, Anomali weaves AI throughout every workflow, driving smarter ingestion, enrichment, detection, investigation, and response at massive scale. By connecting native threat intelligence with security data, Anomali delivers total visibility, real-time contextual insight, and the clarity to act fast.

Who Is the Company Behind Anomali Security Analytics?

  • Seller: ANOMALI
  • Year Founded: 2013
  • HQ Location: Redwood City, US
  • LinkedIn® Page: www.linkedin.com
    306 employees on LinkedIn®
  • Phone: (844) 484-7328

Who Uses This Product?

  • Company Size: 100% Small

What Are Recent G2 Reviews of Anomali Security Analytics?

What Are G2 Users Discussing About Anomali Security Analytics?

Lauren Worth
LW
Researched and written by Lauren Worth