Best Cloud Security Monitoring and Analytics Software - Page 3

Last updated: October 3, 2024

How Many Cloud Security Monitoring and Analytics Software Products Does G2 Track?

Total Products under this Category: 86

Category Stats (Nov 2026)

  • Average Rating: 4.51/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: AppOmni (+2.3%) - Among all products in this category, AppOmni recorded the largest rating increase compared to last month

Last updated: November 18, 2026

How Does G2 Rank Cloud Security Monitoring and Analytics Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 4,900+ Authentic Reviews
  • 86+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

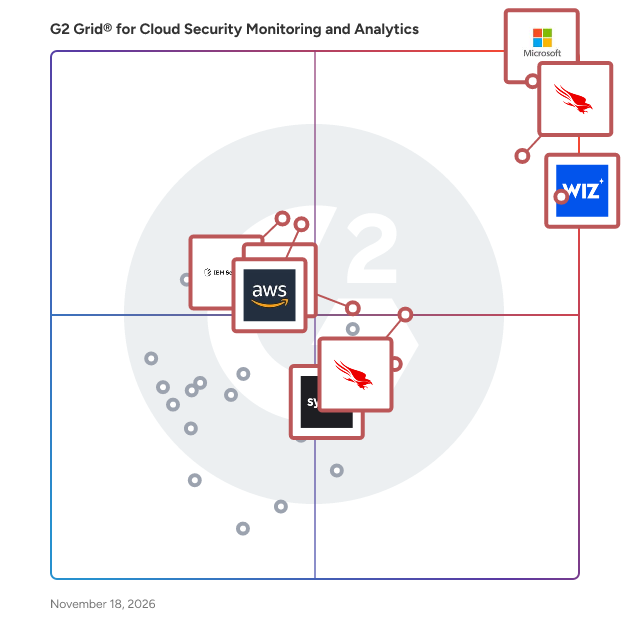
G2 Grid® for Cloud Security Monitoring and Analytics Software

G2 Grid® for Cloud Security Monitoring and Analytics Software plotting products by satisfaction and market presence

Highlighted products: Microsoft Defender for Cloud, CrowdStrike Falcon Cloud Security, Wiz, CrowdStrike Falcon Shield, Amazon GuardDuty, IBM QRadar SIEM, Falcon Next-Gen SIEM, and Sysdig Secure.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-security-monitoring-and-analytics/grids.json?focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=wiz-wiz&focus%5B%5D=crowdstrike-falcon-shield&focus%5B%5D=amazon-guardduty&focus%5B%5D=ibm-ibm-qradar-siem&focus%5B%5D=falcon-next-gen-siem&focus%5B%5D=sysdig-sysdig-secure)

Resmo

All in one platform for SaaS app and access management for modern IT teams. Streamline app discovery, user offboarding, access reviews, and cost tracking.

Average Rating: 5.0/5.0

Total Reviews: 9

How Do G2 Users Rate Resmo?

  • Security Integration: 9.6/10 (Category avg: 8.6/10)
  • Activity Monitoring: 10.0/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 10.0/10 (Category avg: 8.6/10)

Who Is the Company Behind Resmo?

  • Seller: Resmo
  • Year Founded: 2022
  • HQ Location: Dover, US
  • LinkedIn® Page: www.linkedin.com
    2 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 60% Small, 30% Medium

What Are Recent G2 Reviews of Resmo?

What Are G2 Users Discussing About Resmo?

Bindplane Enterprise

Bindplane Enterprise is a production-grade telemetry pipeline platform that helps organizations collect, process, and route observability and security data, at scale, using OpenTelemetry. Built for enterprise DevOps and security teams, Bindplane centralizes telemetry pipelines across logs, metrics, and traces. It enables teams to standardize on OpenTelemetry, reduce vendor lock-in, and control data flow across complex environments. With Bindplane, teams can ingest data from any source, transform and enrich it in real time, and route it to any destination, including platforms like Splunk, Datadog, and Google Cloud, without rebuilding pipelines or duplicating effort. Designed for large-scale production environments, Bindplane provides the flexibility, control, and automation required to manage modern telemetry pipelines efficiently and cost-effectively.

Average Rating: 4.6/5.0

Total Reviews: 14

How Do G2 Users Rate Bindplane Enterprise?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Bindplane Enterprise?

  • Seller: observIQ
  • Year Founded: 2020
  • HQ Location: Grand Rapids, US
  • LinkedIn® Page: www.linkedin.com
    17 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 40% Large, 40% Small

What Are Recent G2 Reviews of Bindplane Enterprise?

What Are G2 Users Discussing About Bindplane Enterprise?

Securonix Security Operations and Analytics Platform

Securonix is working to radically transform all areas of data security with actionable security intelligence.

Average Rating: 4.0/5.0

Total Reviews: 15

How Do G2 Users Rate Securonix Security Operations and Analytics Platform?

  • Security Integration: 7.9/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.3/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 7.7/10 (Category avg: 9.2/10)
  • Security Automation: 8.3/10 (Category avg: 8.6/10)

Who Is the Company Behind Securonix Security Operations and Analytics Platform?

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 53% Large, 33% Small

What Do G2 Reviewers Say About Securonix Security Operations and Analytics Platform?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the automatically correlated alerts in Securonix, making analysis simpler and reducing false positives.
  • Users value the automatically correlated alerts from Securonix, simplifying analysis and reducing false positives effectively.
  • Users value the automated alert correlation in Securonix, making analysis easier and reducing false positives.
  • Users value the easy analysis of alerts in Securonix, which reduces false positives and simplifies alert management.
  • Users value the automated alert correlation of Securonix, simplifying analysis and reducing false positives effectively.
Cons
  • Users find the complex setup of Securonix challenging, often struggling with integration and error troubleshooting.
  • Users experience information deficiency with Securonix, struggling with limited analysis and difficult integration troubleshooting.
  • Users find the insufficient detail in Securonix limits their analysis and complicates troubleshooting integration errors.
  • Users struggle with integration issues in Securonix, making analysis and troubleshooting errors quite difficult.
  • Users find limited features in Securonix hinder analysis, and troubleshooting integration errors poses challenges.

What Are Recent G2 Reviews of Securonix Security Operations and Analytics Platform?

What Are G2 Users Discussing About Securonix Security Operations and Analytics Platform?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

AppOmni

AppOmni is the leader in SaaS Security, enabling organizations to secure their SaaS applications and protect sensitive data from both external and insider threats. Its patented technology scans APIs, security controls, and configurations to ensure SaaS deployments align with best practices and business objectives. With deep visibility, comprehensive coverage, and SaaS expertise, AppOmni simplifies security for IT and security teams by providing actionable insights and automating protection across the entire SaaS environment.

Average Rating: 4.8/5.0

Total Reviews: 6

How Do G2 Users Rate AppOmni?

  • Security Integration: 9.2/10 (Category avg: 8.6/10)
  • Activity Monitoring: 10.0/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 10.0/10 (Category avg: 8.6/10)

Who Is the Company Behind AppOmni?

  • Seller: AppOmni
  • Year Founded: 2018
  • HQ Location: Bay Area, US
  • LinkedIn® Page: linkedin.com
    141 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 57% Large, 29% Medium

What Are Recent G2 Reviews of AppOmni?

Aviatrix

Aviatrix® is the cloud network security company trusted by more than 500 of the world’s leading enterprises. As cloud infrastructures become more complex and costly, the Aviatrix Cloud Network Security platform gives companies back the power, control, security, and simplicity they need to modernize their cloud strategies. Aviatrix is the only secure networking solution built specifically for the cloud, that ensures companies are ready for AI and what’s next. Combined with the Aviatrix Certified Engineer (ACE) Program, the industry’s leading secure multicloud networking certification, Aviatrix unifies cloud, networking, and security teams and unlocks greater potential across any cloud.

Average Rating: 4.3/5.0

Total Reviews: 11

How Do G2 Users Rate Aviatrix?

  • Security Integration: 9.2/10 (Category avg: 8.6/10)
  • Activity Monitoring: 7.8/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 8.0/10 (Category avg: 9.2/10)
  • Security Automation: 9.2/10 (Category avg: 8.6/10)

Who Is the Company Behind Aviatrix?

  • Seller: Aviatrix
  • Year Founded: 2014
  • HQ Location: Santa Clara, California
  • LinkedIn® Page: www.linkedin.com
    411 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 55% Medium, 36% Large

What Are Recent G2 Reviews of Aviatrix?

What Are G2 Users Discussing About Aviatrix?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 48

How Do G2 Users Rate Darktrace / HYBRID NETWORK?

  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®
  • Ownership: LON: DARK

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 61% Medium, 29% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users value the robust monitoring capabilities of Darktrace, enhancing visibility and confidence in network security.
  • Users appreciate the self-learning AI technology of Darktrace, enhancing security with real-time monitoring and automated responses.
  • Users commend the rapid and accurate threat detection of Darktrace, ensuring confidence and effective protection from cyber threats.
  • Users appreciate the responsive customer support of Darktrace, enhancing their learning and experience with the platform.
  • Users commend the autonomous AI capabilities of Darktrace for its proactive and effective threat detection and response.
Cons
  • Users face a significant initial learning curve with Darktrace, requiring extensive time investment for proper tuning and validation.
  • Users find Darktrace / HYBRID NETWORK to be expensive, especially for smaller organizations with limited security budgets.
  • Users often face alert issues during the learning phase, needing significant time and effort to manage false positives.
  • Users report that the complex setup of Darktrace requires significant engineering skills and ongoing management efforts.
  • Some users experience false positives, necessitating IT intervention to restore services and improve detection capabilities.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

RunReveal

RunReveal is a modern security data platform built for AI-forward security teams. RunReveal unifies logs, data pipelines, detections, AI-investigations, and analytics into one platform, so security teams are no longer stitching together tools to manage and use their security data. The platform ingests from 70+ sources, supports built-in and custom detections, and includes an AI agent for faster and automated investigations. RunReveal also support unlimited ingest, and prices based off of predictable data storage. If you're evaluating your first SIEM, escaping renewal sticker shock, or tired of paying enterprise prices for a SIEM that still require additional tooling, RunReveal gives you a unified platform for log management without the complexity or cost.

Average Rating: 4.9/5.0

Total Reviews: 10

How Do G2 Users Rate RunReveal?

  • Security Integration: 10.0/10 (Category avg: 8.6/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)

Who Is the Company Behind RunReveal?

  • Seller: RunReveal
  • Company Website:
  • Year Founded: 2023
  • HQ Location: Austin, US
  • LinkedIn® Page: www.linkedin.com
    23 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 50% Medium, 30% Small

What Do G2 Reviewers Say About RunReveal?

AI-generated summary from verified user reviews

Pros
  • Users commend RunReveal for its fast detection speed, enabling efficient threat hunting and significant improvements in security response.
  • Users commend the exceptional security features of RunReveal, significantly enhancing their threat detection and response capabilities.
  • Users praise RunReveal for its powerful threat detection capabilities that significantly enhance security operations and investigations.
  • Users value the powerful AI integration in RunReveal, enhancing threat investigations and simplifying security management significantly.
  • Users praise RunReveal for its powerful MCP and robust API, empowering efficient security investigations and detection development.
Cons
  • Users feel that the expensive paywall limits their ability to fully utilize RunReveal's features in their homelab.
  • Users are frustrated by feature limitations due to paywalls in the free version, hindering their full usage.
  • Users feel frustrated by the lack of features in the free version, limiting their usability in homelab setups.
  • Users find the limited features of RunReveal frustrating, especially those seeking full functionality without a paywall.

What Are Recent G2 Reviews of RunReveal?

Corelight Open NDR

Corelight's Open Network Detection and Response (NDR) Platform improves network detection coverage, accelerates incident response, and reduces operational costs by consolidating NDR, intrusion detection (IDS), and PCAP functionality in a single solution and by providing security analysts with machine learning-assisted investigations and one-click-pivots from prioritized alerts to the evidence needed to investigate and remediate them. Network Detection and Response platforms monitor and analyze network traffic, delivering telemetry into existing SIEM, XDR, or SaaS-based solutions. Corelight’s platform is unique because our detections and visibility engineering are community driven—with continuous content creation from Zeek®, Suricata IDS, and other Intel communities. And our integration with CrowdStrike XDR enables cross platform (EDR+NDR) analytics. This provides you with the most complete network visibility, powerful analytics, and threat hunting capabilities, and accelerates investigation across your entire kill chain. Corelight also delivers a comprehensive suite of network security analytics that help organizations identify more than 75 adversarial TTPs across the MITRE ATT&CK® spectrum including Exfiltration, Command and Control (C2), and Lateral Movement. These detections reveal known and unknown threats via hundreds of unique insights and alerts across machine learning, behavioral analysis, and signature-based approaches. CORELIGHT PRODUCTS + SERVICES Open NDR Platform Appliance, Cloud, Software, Virtual and SaaS Sensors IDS Fleet Manager Investigator Threat Hunting Platform Smart PCAP Corelight Training CERTIFICATIONS FIPS 140-2

Average Rating: 4.6/5.0

Total Reviews: 20

How Do G2 Users Rate Corelight Open NDR?

  • Security Integration: 7.9/10 (Category avg: 8.6/10)
  • Activity Monitoring: 7.9/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.4/10 (Category avg: 9.2/10)
  • Security Automation: 8.3/10 (Category avg: 8.6/10)

Who Is the Company Behind Corelight Open NDR?

  • Seller: Corelight
  • Year Founded: 2013
  • HQ Location: San Francisco, CA
  • LinkedIn® Page: www.linkedin.com
    483 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Information Technology and Services, Computer & Network Security
  • Company Size: 50% Medium, 50% Large

What Do G2 Reviewers Say About Corelight Open NDR?

AI-generated summary from verified user reviews

Pros
  • Users value the comprehensive security features of Corelight, enabling effective detection of network threats and easier event analysis.
  • Users value Corelight for its excellent network telemetry, making security events easy to understand and manage.
  • Users appreciate the great network telemetry of Corelight, effectively presenting and correlating security network events.
  • Users value the effective security features of Corelight, which enhance the detection of network threats efficiently.
  • Users praise Corelight's exceptional security features for effectively detecting threats and presenting network events clearly.
Cons
  • Users find Corelight's setup to be complex and difficult, often requiring specialized training to use effectively.
  • Users find Corelight's setup and management complex and challenging, requiring specialized knowledge beyond beginner analysts.
  • Users find Corelight's complexity challenging, especially for novice analysts requiring costly personalized training.
  • Users find the complex setup of Corelight challenging, especially for those without specialized knowledge or training.
  • Users find Corelight has a steep learning curve, making it challenging for novice security analysts to effectively use.

What Are Recent G2 Reviews of Corelight Open NDR?

Fastly's Web Application and API Security

Fastly’s AppSec solutions empower teams to mitigate threats and control bots while helping the business move faster, confidently. Protect Your Apps and APIs While Accelerating Growth with Fastly’s Next-Gen WAF, DDoS Protection, Bot Management, API Security, and more. Our solutions are designed to help you stop cyber threats from derailing your biggest moments, accelerate innovation while minimizing new risk, and govern bots without increasing user friction.

Average Rating: 4.2/5.0

Total Reviews: 29

How Do G2 Users Rate Fastly's Web Application and API Security?

  • Security Integration: 6.7/10 (Category avg: 8.6/10)
  • Activity Monitoring: 6.7/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.2/10 (Category avg: 9.2/10)
  • Security Automation: 6.7/10 (Category avg: 8.6/10)

Who Is the Company Behind Fastly's Web Application and API Security?

  • Seller: Fastly
  • Year Founded: 2011
  • HQ Location: San Francisco, California, United States
  • LinkedIn® Page: www.linkedin.com
    1,456 employees on LinkedIn®
  • Ownership: NYSE: FSLY

Who Uses This Product?

  • Top Industries: Computer Software
  • Company Size: 50% Medium, 37% Large

What Do G2 Reviewers Say About Fastly's Web Application and API Security?

AI-generated summary from verified user reviews

Pros
  • Users commend the excellent customer support provided by Fastly, enhancing their experience and implementation process.
  • Users value the effective DDoS protection of Fastly, ensuring robust security against various web application threats.
  • Users value the high detection efficiency of Fastly's security, ensuring robust protection against diverse attacks.
  • Users value the seamless HTTPS integration of Fastly's Web Application and API Security, ensuring a secure experience effortlessly.
  • Users find the setup process easy with Fastly's Web Application and API Security, backed by excellent support.
Cons
  • Users report poor customer support, highlighting issues with responsiveness and difficulty in obtaining assistance for configurations.
  • Users find the complex configuration of Fastly's WAF overwhelming and time-consuming, especially for rule management.
  • Users find the complex setup of Fastly's WAF cumbersome, making rule management and configurations time-consuming.
  • Users find the management complex, as the cumbersome interface and poor support hinder effective rule setup.
  • Users report data inconsistency issues that lead to vulnerabilities in monitoring traffic effectively, affecting overall security.

What Are Recent G2 Reviews of Fastly's Web Application and API Security?

JupiterOne

JupiterOne is the AI Risk Management Platform that helps security teams in highly regulated industries understand and prioritize risk across complex, AI-driven environments. Built on a true graph-native data model, JupiterOne brings together assets, identities, security posture, and controls, showing the intuitive relationships that connect everything across the enterprise. Unlike list-based approaches, it enables querying of those relationships to understand how risk flows, the blast radius, and what to prioritize in seconds, at enterprise scale. With deep integrations and automated discovery across hundreds of tools, JupiterOne provides a continually updated view of asset relationships and context to cut through tool sprawl and prioritize fixes quickly.

Average Rating: 4.9/5.0

Total Reviews: 5

How Do G2 Users Rate JupiterOne?

  • Security Integration: 10.0/10 (Category avg: 8.6/10)
  • Activity Monitoring: 10.0/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 10.0/10 (Category avg: 8.6/10)

Who Is the Company Behind JupiterOne?

Who Uses This Product?

  • Company Size: 67% Medium, 17% Large

What Do G2 Reviewers Say About JupiterOne?

AI-generated summary from verified user reviews

Pros
  • Users value the cloud-native security configuration of JupiterOne, enhancing asset management and cyber resilience.
  • Users appreciate the cloud-native security configurations of JupiterOne, enhancing their asset security management effectively.

What Are Recent G2 Reviews of JupiterOne?

Microsoft Security Copilot

Empower your defenders to detect hidden patterns, harden defenses, and respond to incidents faster with generative AI

Average Rating: 4.4/5.0

Total Reviews: 15

How Do G2 Users Rate Microsoft Security Copilot?

  • Has the product been a good partner in doing business?: 7.2/10 (Category avg: 9.2/10)

Who Is the Company Behind Microsoft Security Copilot?

  • Seller: Microsoft
  • Year Founded: 1975
  • HQ Location: Redmond, Washington
  • LinkedIn® Page: www.linkedin.com
    232,750 employees on LinkedIn®
  • Ownership: MSFT
  • Phone: +1 (877) 276-2464

Who Uses This Product?

  • Top Industries: Information Technology and Services
  • Company Size: 67% Large, 20% Medium

What Do G2 Reviewers Say About Microsoft Security Copilot?

AI-generated summary from verified user reviews

Pros
  • Users value the ease of use of Microsoft Security Copilot, enhancing security management effortlessly with AI-driven support.
  • Users value the AI integration of Microsoft Security Copilot for quickly identifying and managing security threats effectively.
  • Users value the AI integration for threat detection in Microsoft Security Copilot, enhancing their security operations effectively.
  • Users appreciate the AI-driven threat detection of Microsoft Security Copilot, simplifying security operations and enhancing response times.
  • Users appreciate the automation features of Microsoft Security Copilot, significantly speeding up threat identification and response.
Cons
  • Users find the tool's complexity challenging, especially for inexperienced team members and varied user needs.
  • Users find the product expensive, suggesting a need for more cost-effective options for wider accessibility.
  • Users find the difficult learning curve of Microsoft Security Copilot challenging, especially for inexperienced team members.
  • Users face false positives that waste time, complicating workflows and necessitating double-checking of results.
  • Users express concern over the limited access to Microsoft Security Copilot, restricting usability for everyone.

What Are Recent G2 Reviews of Microsoft Security Copilot?

Tenable Identity Exposure

Get real-time, unified visibility into Active Directory and Entra ID identities to help organizations proactively reduce identity-based cyber risks. By mapping pre-configured Indicators of Exposure to identities, it highlights the severity of associated risks, including misconfigurations, privilege escalation risks and structural security gaps. It continuously monitors identity attack paths and presents vulnerabilities through graphical views. Misconfigurations, exposures, and attack paths are identified and remediated in real time to reduce the AD and Entra ID attack surface. With risk-based prioritization and guided remediation, security teams can strengthen identity posture and prevent breaches without requiring agents or elevated privileges. As part of Tenable’s AI-powered exposure management platform, it brings identity context to your broader risk picture—delivering the visibility and control needed to reduce organizational risk.

Average Rating: 4.4/5.0

Total Reviews: 7

How Do G2 Users Rate Tenable Identity Exposure?

  • Security Integration: 9.2/10 (Category avg: 8.6/10)
  • Activity Monitoring: 8.3/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 9.0/10 (Category avg: 9.2/10)
  • Security Automation: 7.8/10 (Category avg: 8.6/10)

Who Is the Company Behind Tenable Identity Exposure?

  • Seller: Tenable
  • Company Website:
  • HQ Location: Columbia, MD
  • LinkedIn® Page: www.linkedin.com
    2,361 employees on LinkedIn®
  • Ownership: NASDAQ: TENB

Who Uses This Product?

  • Company Size: 43% Large, 29% Medium

What Do G2 Reviewers Say About Tenable Identity Exposure?

AI-generated summary from verified user reviews

Pros
  • Users value the real-time monitoring of Tenable Identity Exposure, enabling swift detection of unauthorized modifications in complex environments.
  • Users value the clear and actionable visibility Tenable Identity Exposure offers, enhancing proactive identity security and risk management.
  • Users appreciate the clear and actionable visibility of Tenable Identity Exposure, enhancing proactive identity security management.
  • Users appreciate the clear and actionable visibility provided by Tenable Identity Exposure for identity risk management.
  • Users value the real-time visibility and monitoring of Tenable Identity Exposure, enhancing security in complex AD environments.
Cons
  • Users find the difficult learning curve of Tenable Identity Exposure challenging, requiring technical expertise for effective use.
  • Users find the excessive notifications from Tenable Identity Exposure overwhelming, especially with low priority issues cluttering their workflow.
  • Users find the excessive false positives from Tenable Identity Exposure can overwhelm teams without proper tuning.
  • Users experience information overload due to excessive findings, including low priority issues that overwhelm teams without proper tuning.
  • Users note the steep learning curve for Tenable Identity Exposure, requiring technical skills for effective utilization.

What Are Recent G2 Reviews of Tenable Identity Exposure?

What Are G2 Users Discussing About Tenable Identity Exposure?

Scanner

Scanner is a radically different way to detect threats in security data. Most security teams run a SIEM at the center of their stack. But SIEMs price on ingestion volume and cap retention at around 30 days, which forces a painful tradeoff: teams end up diverting 95% of their log data to object storage like S3 just to keep costs manageable. The result is a SIEM that covers a thin slice of your environment and a data lake full of logs no one can practically search or run detections against. Scanner works differently at every layer. Storage: We index semi-structured and unstructured log data directly in your S3 buckets. No ingestion pipelines, no re-ingestion, no schema work. Your data stays where it is. Detection: Logs stream into a numerically efficient cache where detections run continuously. There's no batch job, no scheduled query scanning your entire dataset. Detections operate on the stream itself. Investigation: When an analyst or agent runs a query, Scanner spins up short-lived compute that exists only for the duration of that query and then disappears. The indexes narrow the search space by orders of magnitude before any data is read, so even petabyte-scale queries resolve in seconds. Query compute is active less than 1% of the day. The rest of the time, it doesn't exist. The result is a system where petabytes of security data are searchable in seconds, detections run continuously, and costs scale with actual usage rather than data volume. Today, AI agents are Scanner's most prolific users, investigating alerts and hunting threats around the clock. Teams at Notion, Ramp, and Benchling use Scanner as their core security data layer.

Average Rating: 4.6/5.0

Total Reviews: 7

How Do G2 Users Rate Scanner?

  • Has the product been a good partner in doing business?: 8.3/10 (Category avg: 9.2/10)

Who Is the Company Behind Scanner?

  • Seller: Scanner
  • Company Website:
  • Year Founded: 2022
  • HQ Location: San Francisco, US
  • LinkedIn® Page: www.linkedin.com
    11 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 29% Small, 14% Medium

What Do G2 Reviewers Say About Scanner?

AI-generated summary from verified user reviews

Pros
  • Users highlight the ease of use of Scanner, enabling quick queries and efficient log management effortlessly.
  • Users rave about the search efficiency of Scanner, with queries returning results in seconds across vast datasets.
  • Users highlight the fast querying speed of Scanner, allowing efficient log management and quick data exploration.
  • Users value the exceptional customer support from Scanner.dev, highlighting their responsiveness and commitment to user feedback.
  • Users commend the impressive detection efficiency of Scanner, enabling rapid querying and indexing of vast datasets.
Cons
  • Users face challenges with logging issues, lacking documentation and reliable monitoring, complicating data ingestion and management.
  • Users find the complex querying limitations frustrating, hindering seamless adoption as a direct tool replacement.
  • Users struggle with inadequate documentation and lack of multiple source detection, complicating data management and ingestion.
  • Users note the immaturity of Scanner, with limited features and complexities, making it harder for immediate replacement.
  • Users note the lack of features in Scanner due to its early stage, impacting teams seeking comprehensive solutions.

What Are Recent G2 Reviews of Scanner?

Uptycs

Uptycs unified CNAPP and XDR platform is a comprehensive security solution designed to protect the full spectrum of modern attack surfaces in your cloud, data centers, user devices, build pipelines, and containers. With a strong focus on DevSecOps, Uptycs offers a powerful combination of CNAPP capabilities, including Cloud Workload Protection Platform (CWPP), Kubernetes Security Posture Management (KSPM), Cloud Security Posture Management (CSPM), Cloud Infrastructure Entitlement Management (CIEM), and Cloud Detection and Response (CDR). With Uptycs you also get industry-leading eXtended Detection and Response (XDR) across macOS, Windows, and Linux endpoints, ensuring comprehensive protection, detection, and investigation. Uptycs delivers real-time threat detection, context-rich alerts, and maps detections to the MITRE ATT&CK framework for improved security insights. Uptycs performs scanning of containers for vulnerabilities throughout the CI/CD pipeline, promoting agile DevOps workflows, and reducing risk in production environments. Uptycs seamlessly integrates with existing tools and processes, streamlining operations and improving overall efficiency. Customers also benefit from the flexibility to choose between agent-based and agentless scanning options tailored to their unique cloud workload needs. Discover how Uptycs can transform your security posture with a comprehensive, flexible, and powerful security solution designed to meet the needs of today's complex and rapidly evolving cloud environments. Shift up with Uptycs. KEY DIFFERENTIATORS: 1. Unified & Comprehensive Platform: Uptycs offers a holistic security solution with CNAPP capabilities (CWPP, KSPM, CSPM, CIEM, and CDR) across data centers, laptops, build pipelines, containers, and cloud environments, reducing tool sprawl. 2. Advanced XDR: Industry-leading eXtended Detection and Response for endpoint protection across macOS, Windows, and Linux systems. 3. DevSecOps Focus: Enhanced security for container-based workloads and Kubernetes, supporting agile DevOps workflows. 4. Real-Time Threat Detection: Context-rich alerts and threat detection mapped to the MITRE ATT&CK framework for improved insights. 5. CI/CD Integration: Efficiently scan containers for vulnerabilities throughout the CI/CD pipeline, reducing risk in production. 6. Both agent-based and agentless scanning. Deploy agentless scanning for rapid, friction-free coverage to keep your data secure, and gain continuous runtime security, real-time investigations, and remediation with agent-based telemetry. 7. Rich API & Compatibility: Seamless integration with existing security tools and platforms, powered by osquery for broad compatibility. 8. Expert Support & Flexibility: Dedicated support from security experts and the best of both worlds with agent-based and agentless scanning options tailored to your needs.

Average Rating: 4.4/5.0

Total Reviews: 13

How Do G2 Users Rate Uptycs?

  • Security Integration: 7.5/10 (Category avg: 8.6/10)
  • Activity Monitoring: 5.8/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 7.8/10 (Category avg: 8.6/10)

Who Is the Company Behind Uptycs?

  • Seller: Uptycs
  • Year Founded: 2016
  • HQ Location: Waltham, US
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 54% Medium, 38% Large

What Do G2 Reviewers Say About Uptycs?

AI-generated summary from verified user reviews

Pros
  • Users value the comparative analysis feature of Uptycs, aiding in selecting the best cloud security tools.
  • Users value the comparative analysis feature of Uptycs, aiding in selecting the best cloud security tools.
  • Users value the comparative analysis feature of Uptycs, which aids in choosing the best cloud security tools.
  • Users value Uptycs for its excellent compliance with CIS and PCI DSS standards, enhancing security monitoring capabilities.
  • Users value the strong compliance with standards like CIS and PCI DSS, enhancing security monitoring capabilities.
Cons
  • Users find the high fees regrettable, as it limits their willingness to continue using Uptycs.
  • Users express concern over the high pricing of Uptycs, which deters continued use of the tool.

What Are Recent G2 Reviews of Uptycs?

Cyscale Cloud Platform

Cyscale offers a unified cloud security platform (CNAPP) that constantly monitors your cloud for risks and compliance issues. It includes CSPM, KSPM, CWPP, vulnerability management, CIEM, DSPM, and Container security. Designed to prioritize remediations, it is a valuable tool for Security Teams, CISOs, and CTOs looking to strengthen their security posture. Customers rely on Cyscale to bring products to market faster and more securely, consolidating 4 or 5 point security solutions into a single platform. Headquartered in London, Cyscale was founded by a team of visionary security experts and researchers. The founders have worked to protect companies like Rolls Royce, ABB, and Lloyd’s Register. Visit https://cyscale.com to learn more.

Average Rating: 4.8/5.0

Total Reviews: 6

How Do G2 Users Rate Cyscale Cloud Platform?

  • Security Integration: 10.0/10 (Category avg: 8.6/10)
  • Activity Monitoring: 10.0/10 (Category avg: 8.5/10)
  • Has the product been a good partner in doing business?: 10.0/10 (Category avg: 9.2/10)
  • Security Automation: 10.0/10 (Category avg: 8.6/10)

Who Is the Company Behind Cyscale Cloud Platform?

  • Seller: Cyscale
  • Year Founded: 2019
  • HQ Location: London, GB
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 50% Medium, 50% Small

What Do G2 Reviewers Say About Cyscale Cloud Platform?

AI-generated summary from verified user reviews

Pros
  • Users value the effortless cloud integration of Cyscale, enabling streamlined monitoring and management of multiple environments.
  • Users praise the exceptional customer support from Cyscale's team, providing guidance and quick issue resolution effectively.
  • Users find Cyscale Cloud Platform remarkably easy to use, simplifying complex monitoring with its intuitive interface and support.
  • Users highlight the efficacy of cloud security monitoring with Cyscale, streamlining compliance and risk management effortlessly.
  • Users value the ease of monitoring and compliance provided by Cyscale Cloud Platform, saving time and enhancing security.
Cons
  • Users note the limited features in managing CVEs and the absence of agent-based deployment options.
  • Users find the missing agent-based deployment feature limits the platform's flexibility and usability for their needs.
  • Users find the compliance issues can complicate initial setup, but improvements are being made with updates.
  • Users find the initial complexity of Cyscale Cloud Platform's default settings challenging, yet it improves with updates.
  • Users find the immaturity of the Cyscale Cloud Platform frustrating, particularly due to lack of agent-based deployment.

What Are Recent G2 Reviews of Cyscale Cloud Platform?

Lauren Worth
LW
Researched and written by Lauren Worth