Best Cloud Infrastructure Entitlement Management (CIEM) Software - Page 2

How Many Cloud Infrastructure Entitlement Management (CIEM) Software Products Does G2 Track?

Total Products under this Category: 24

Category Stats (Sep 2026)

  • Average Rating: 4.54/5 The average rating of products in this category, based on all submitted ratings
  • Top Trending Product: SailPoint (+1.11%) - Among all products in this category, SailPoint recorded the largest rating increase compared to last month

Last updated: September 30, 2026

How Does G2 Rank Cloud Infrastructure Entitlement Management (CIEM) Software Products?

Why You Can Trust G2's Software Rankings:

  • 30 Analysts and Data Experts
  • 2,500+ Authentic Reviews
  • 24+ Products
  • Unbiased Rankings

G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.

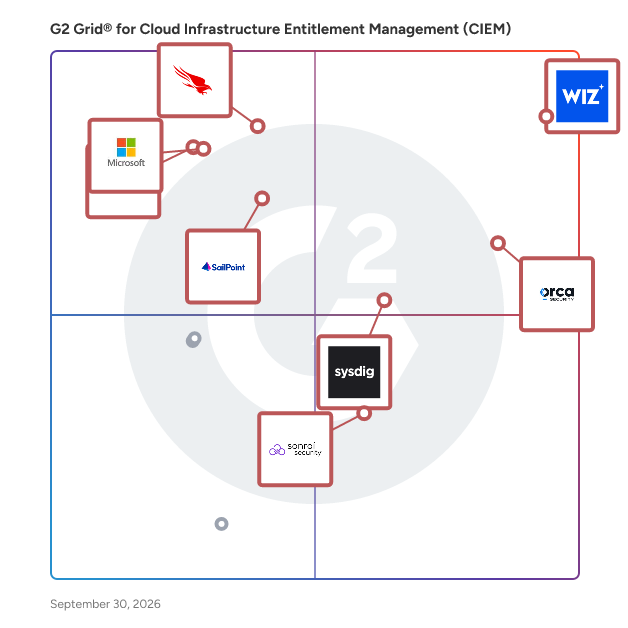
G2 Grid® for Cloud Infrastructure Entitlement Management (CIEM) Software

G2 Grid® for Cloud Infrastructure Entitlement Management (CIEM) Software plotting products by satisfaction and market presence

Highlighted products: Wiz, Orca Security, CrowdStrike Falcon Cloud Security, Sysdig Secure, SailPoint, Microsoft Entra Permissions Management, Cortex Cloud, and Sonrai Security.

Underlying data: [Grid® JSON](https://www.g2.com/categories/cloud-infrastructure-entitlement-management-ciem/grids.json?focus%5B%5D=wiz-wiz&focus%5B%5D=orca-security&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=sysdig-sysdig-secure&focus%5B%5D=sailpoint&focus%5B%5D=microsoft-entra-permissions-management&focus%5B%5D=cortex-cloud&focus%5B%5D=sonrai-security)

Trustle

Trustle goes beyond Cloud Infrastructure Entitlement Management (CIEM) to prioritize the most over-privileged users, and easily transition your entire organization to Just-In-Time Access to everything from AWS production environments processing customer transactions to GitHub repos with valuable source code and HR platforms housing your employees' personal information. Trustle takes you from questioning whether a contractor still has access to being confident that the Operations team's access was revoked immediately after the maintenance window. Your team will thank you when they see how easy it is to request and approve access through the Chat tools (Slack, Microsoft Teams) they use every day.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Trustle?

  • Seller: Trustle
  • Year Founded: 2019
  • HQ Location: Boston, MA, USA
  • LinkedIn® Page: www.linkedin.com
    15 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Medium

What Do G2 Reviewers Say About Trustle?

AI-generated summary from verified user reviews

Pros
  • Users value Trustle's cloud-based identity security and access management for its automation and risk identification capabilities.
  • Users value Trustle for its automated identity security and risk identification across cloud environments, enhancing access management.
  • Users appreciate the secure access provided by Trustle, enhancing their identity security in cloud environments.

What Are Recent G2 Reviews of Trustle?

Authomize

Authomize protects organizations from identity-based cyberattacks with the first Identity Threat Detection and Response (ITDR) Platform. Authomize collects and normalizes data of identities, access privileges, assets, and activities from cloud services, applications, and IAM solutions in order to detect, investigate and respond to identity risks and threats. Customers use Authomize to gain visibility of actual access, achieve least privilege across cloud services and applications, secure their IAM infrastructure, and automate compliance and audit preparations.

Average Rating: 4.5/5.0

Total Reviews: 1

Who Is the Company Behind Authomize?

  • Seller: Authomize
  • Year Founded: 2020
  • HQ Location: Alpharetta, US
  • LinkedIn® Page: www.linkedin.com
    5 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 100% Large

What Are Recent G2 Reviews of Authomize?

Darktrace / HYBRID NETWORK

Darktrace / HYBRID NETWORK uses Adaptive AI to continuously learn behavior across your infrastructure, combining NDR, CDR, OT security, ITDR, exposure management, attack path modelling and forensic investigations into a single solution. - Unify visibility - Detect and contain known, novel and insider threats - AI-led triage and investigations - Increase resilience Named a Leader in the 2025 and 2026 Gartner® Magic Quadrant™ for NDR and the only Visionary in the 2025 Gartner® Magic Quadrant™ for CPS.

Average Rating: 4.4/5.0

Total Reviews: 47

Who Is the Company Behind Darktrace / HYBRID NETWORK?

  • Seller: Darktrace
  • Company Website:
  • Year Founded: 2013
  • HQ Location: Cambridgeshire, England
  • Twitter: @Darktrace
    18,177 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    2,597 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services, Information Technology and Services
  • Company Size: 63% Medium, 31% Large

What Do G2 Reviewers Say About Darktrace / HYBRID NETWORK?

AI-generated summary from verified user reviews

Pros
  • Users appreciate the excellent monitoring capabilities of Darktrace, offering impressive visibility and efficient network analysis.
  • Users appreciate the self-learning AI technology of Darktrace/Network, effectively adapting to threats without extensive configuration.
  • Users commend Darktrace's rapid threat detection, ensuring robust security with minimal manual intervention for maximum efficiency.
  • Users commend the responsive customer support of Darktrace/Network, enhancing learning and facilitating efficient troubleshooting.
  • Users highlight the autonomous AI-driven cybersecurity of Darktrace, which effectively detects and responds to threats in real time.
Cons
  • Users report a significant learning curve with Darktrace as the AI generates numerous alerts during initial setup.
  • Users note that the product can be expensive, particularly for smaller organizations with constrained budgets and significant training costs.
  • Users experience alert issues with Darktrace, needing extensive manual tuning to manage false positives during the learning phase.
  • Users find the complex setup of Darktrace challenging, requiring skilled teams for effective management and configuration.
  • Users experience false positives occasionally, requiring IT support to resolve issues affecting network connectivity.

What Are Recent G2 Reviews of Darktrace / HYBRID NETWORK?

What Are G2 Users Discussing About Darktrace / HYBRID NETWORK?

AI can help you find the answers. G2 helps you trust them.

Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.

How it works

IP Fabric

IP Fabric is the leading automated network assurance platform, offering a continuously validated view of cloud, network and security systems to improve stability, security and spend. Within minutes, the platform creates a unified view of devices, state, configurations and interdependencies, normalizing multi-vendor data and revealing operational truth through automated intent checks. By uncovering risks and providing actionable insights, IP Fabric empowers enterprises to accelerate IT and business transformation while reducing costs. Trusted by industry leaders like Red Hat, Major League Baseball and Air France, IP Fabric delivers the foundation for end-to-end network governance. Learn more at www.ipfabric.io and follow the company on LinkedIn https://www.linkedin.com/company/ip-fabric

Who Is the Company Behind IP Fabric?

  • Seller: IP Fabric
  • Year Founded: 2015
  • HQ Location: Boston, Massachusetts, United States
  • Twitter: @IPFabric
    921 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    127 employees on LinkedIn®

NextLabs Application Enforcers

NextLabs' Application Enforcer is a suite of enforcers that integrate seamlessly with leading enterprise applications, enhancing their native security frameworks without the need for custom coding. By leveraging built-in awareness of application data models and business workflows, Application Enforcer provides an additional layer of control, ensuring that organizations meet stringent security and compliance requirements. It enforces Policy-Based Access Control in real-time, utilizing attributes related to users, data, and environmental factors. This approach externalizes authorization through a zero trust policy engine, strengthening application security and eliminating authorization silos. Key Features and Functionality: - Externalized Authorization: Allows modification of authorization policies without altering the application's code. - Enforce Least Privilege Access: Utilizes Attribute-Based Access Control to ensure that applications and data are accessible only to authorized entities. - Data Classification: Automatically identifies and categorizes sensitive data based on the application's underlying data model. - Access Activity Monitoring: Collects and analyzes access activities across applications to detect and respond to anomalous behavior. - Native Application Integration: Understands the identity systems, object models, and security frameworks of applications for easy deployment and a seamless user experience. Primary Value and Problem Solved: Application Enforcer addresses the challenge of securing critical data across a diverse and evolving application landscape. By externalizing security controls and enforcing zero trust access policies, it automates data security and compliance procedures, enhancing business agility and competitiveness. The solution eliminates the need for costly customizations, reduces time-to-market, and streamlines compliance by automating the auditing of authorization and data access. This ensures that sensitive data is protected, access is granted based on the principle of least privilege, and organizations can adapt swiftly to changing security and compliance demands.

Who Is the Company Behind NextLabs Application Enforcers?

  • Seller: NextLabs
  • Year Founded: 2004
  • HQ Location: San Mateo, California, United States
  • Twitter: @nextlabs
    402 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    213 employees on LinkedIn®

Saner Cloud

Saner Cloud is an AI-fortified Cloud-Native Application Protection Platform (CNAPP) that moves beyond detection. It empowers organizations with intelligent, real-time, and automated attack prevention. Unlike traditional cloud security solutions that overwhelm security teams with alerts but fail to act, Saner Cloud automatically fixes vulnerabilities, misconfigurations, identity risks, and compliance violations across multicloud environments. Why choose Saner Cloud? - Unified dashboard with real-time updates and interactive visuals for a single source of truth - Complete asset visibility with watchlists, exposure detection, region-based categorization, deprecated services, and cost analysis - AI-driven anomaly detection with confidence levels, severity distribution, whitelisting options, and one-click remediation - Continuous posture management with built-in benchmarks, quick misconfiguration checks, trend tracking, and drift detection - Risk prioritization with scoring, top-risk lists, and context across assets, posture, and anomalies to focus on which risk to remediate first - Identity and entitlement governance with policy maps, RBAC, resource groups, excessive permission detection, and activity logging - Enhanced Remediation with scheduling and approval workflows, Top 10 patches, patch aging, most-impactful-patches charts, and grouped remediation - Multi-cloud coverage across AWS, GCP and Azure with a prevention-first workflow - Smart tagging for fast filtering across thousands of resources and audit logs with tool-specific job codes for full traceability

Who Is the Company Behind Saner Cloud?

  • Seller: SecPod
  • Company Website:
  • Year Founded: 2008
  • HQ Location: Redwood City, California
  • Twitter: @secpod
    542 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    182 employees on LinkedIn®

TENET

TENET is a risk intelligence platform purpose-built for the Microsoft ecosystem to deliver unified visibility and proactive risk assessment across Azure and M365. It serves as a single source of truth for identifying, prioritizing, and mitigating cloud risk at scale—enabling organizations to shift from reactive firefighting to continuous, intelligence-driven security operations. Key Features: - Attack surface management: Identify risky entry points, misconfigurations, and third-party exposures. Visualize attack paths, map findings to MITRE ATT&CK, prioritize remediation, and manage incidents from a unified cloud risk view. - Anomaly detection: Detect issues early with real-time analysis of cloud workloads, identities, and applications, helping teams identify abnormal behaviour and mitigate risks before they become incidents. - Compliance readiness: Simplify audits with continuous compliance monitoring, guided remediation, and risk-prioritized insights. Reduce costs and manual effort while shrinking audit preparation from weeks to hours. - Microsoft 365: Gain visibility into external sharing, device risk, license utilization, and Copilot agents. Understand how identities, configurations, and data exposures combine to create risk across your cloud environment. - Access governance: Monitor human and non-human identities, analyze effective permissions across Entra ID and RBAC, and maintain clear visibility into who can access resources across your cloud estate. - AI monitoring: Discover and inventory AI models, agents, and cognitive services. Continuously monitor performance, reliability, and security posture while identifying AI-specific risks and prioritizing remediation. - Intelligent insights: Investigate and resolve issues faster with BriteAI. Transform live data into actionable insights, identify root causes through natural language queries, and receive precise remediation guidance. Core Value: TENET eliminates blind spots and reduces mean time to remediation (MTTR) through end-to-end Microsoft cloud visibility and guided remediation. It lowers compliance and audit overhead, enables teams to proactively identify and mitigate risks before they escalate, and scales security operations efficiently with AI-powered insights and autonomous remediation with full context via the TENET MCP server. For more information, visit www.aesonsolutions.com.

Who Is the Company Behind TENET?

Uptycs

Uptycs unified CNAPP and XDR platform is a comprehensive security solution designed to protect the full spectrum of modern attack surfaces in your cloud, data centers, user devices, build pipelines, and containers. With a strong focus on DevSecOps, Uptycs offers a powerful combination of CNAPP capabilities, including Cloud Workload Protection Platform (CWPP), Kubernetes Security Posture Management (KSPM), Cloud Security Posture Management (CSPM), Cloud Infrastructure Entitlement Management (CIEM), and Cloud Detection and Response (CDR). With Uptycs you also get industry-leading eXtended Detection and Response (XDR) across macOS, Windows, and Linux endpoints, ensuring comprehensive protection, detection, and investigation. Uptycs delivers real-time threat detection, context-rich alerts, and maps detections to the MITRE ATT&CK framework for improved security insights. Uptycs performs scanning of containers for vulnerabilities throughout the CI/CD pipeline, promoting agile DevOps workflows, and reducing risk in production environments. Uptycs seamlessly integrates with existing tools and processes, streamlining operations and improving overall efficiency. Customers also benefit from the flexibility to choose between agent-based and agentless scanning options tailored to their unique cloud workload needs. Discover how Uptycs can transform your security posture with a comprehensive, flexible, and powerful security solution designed to meet the needs of today's complex and rapidly evolving cloud environments. Shift up with Uptycs. KEY DIFFERENTIATORS: 1. Unified & Comprehensive Platform: Uptycs offers a holistic security solution with CNAPP capabilities (CWPP, KSPM, CSPM, CIEM, and CDR) across data centers, laptops, build pipelines, containers, and cloud environments, reducing tool sprawl. 2. Advanced XDR: Industry-leading eXtended Detection and Response for endpoint protection across macOS, Windows, and Linux systems. 3. DevSecOps Focus: Enhanced security for container-based workloads and Kubernetes, supporting agile DevOps workflows. 4. Real-Time Threat Detection: Context-rich alerts and threat detection mapped to the MITRE ATT&CK framework for improved insights. 5. CI/CD Integration: Efficiently scan containers for vulnerabilities throughout the CI/CD pipeline, reducing risk in production. 6. Both agent-based and agentless scanning. Deploy agentless scanning for rapid, friction-free coverage to keep your data secure, and gain continuous runtime security, real-time investigations, and remediation with agent-based telemetry. 7. Rich API & Compatibility: Seamless integration with existing security tools and platforms, powered by osquery for broad compatibility. 8. Expert Support & Flexibility: Dedicated support from security experts and the best of both worlds with agent-based and agentless scanning options tailored to your needs.

Average Rating: 4.4/5.0

Total Reviews: 13

Who Is the Company Behind Uptycs?

  • Seller: Uptycs
  • Year Founded: 2016
  • HQ Location: Waltham, US
  • Twitter: @uptycs
    1,483 Twitter followers
  • LinkedIn® Page: www.linkedin.com
    132 employees on LinkedIn®

Who Uses This Product?

  • Top Industries: Financial Services
  • Company Size: 54% Medium, 38% Large

What Do G2 Reviewers Say About Uptycs?

AI-generated summary from verified user reviews

Pros
  • Users value the comparative analysis features of Uptycs, aiding in selecting the best cloud security tools.
  • Users appreciate the comparative analysis features of Uptycs, aiding them in selecting the best cloud security tools.
  • Users value the comparative analysis features of Uptycs for making informed decisions in cloud security tools.
  • Users value Uptycs for its compliance with CIS and PCI DSS standards, enhancing security monitoring capabilities.
  • Users value the compliance management of Uptycs, appreciating its adherence to CIS and PCI DSS standards.
Cons
  • Users regret the high fees of Uptycs, which impact their willingness to continue using the tool.
  • Users express concerns about high pricing, which makes continued use of Uptycs challenging for some.

What Are Recent G2 Reviews of Uptycs?

Upwind

Upwind is the runtime-first cloud security platform that secures your deployments, configurations, and applications by providing real-time visibility from the inside out. We’ve built a unified fabric that maps your environment as it runs - revealing what’s truly at risk, what’s actively happening, and how to respond quickly and effectively. With Upwind, security, dev, and ops teams move faster, stay focused, and fix risks that matter most.

Average Rating: 4.9/5.0

Total Reviews: 9

Who Is the Company Behind Upwind?

  • Seller: Upwind
  • Company Website:
  • Year Founded: 2022
  • HQ Location: San Francisco, California, United States
  • LinkedIn® Page: www.linkedin.com
    537 employees on LinkedIn®

Who Uses This Product?

  • Company Size: 67% Medium, 33% Large

What Do G2 Reviewers Say About Upwind?

AI-generated summary from verified user reviews

Pros
  • Users find Upwind to be easy to use, appreciating its real-time functionality and responsive support team.
  • Users value the excellent visibility provided by Upwind, enhancing their ability to manage risks and identify threats.
  • Users appreciate the quick and responsive customer support of Upwind, enhancing their overall satisfaction with the product.
  • Users value the fast near real-time detection of Upwind, enabling immediate threat resolution with minimal noise.
  • Users find the implementation ease of Upwind impressive, enjoying seamless integration into their AWS environment.
Cons
  • Users report feeling overwhelmed by the large number of vulnerability findings due to excessive alert visibility in Upwind.
  • Users note the need for improvements regarding compliance issues related to NIST and GDPR reporting in Upwind.
  • Users express concerns over the inability to bulk resolve or suppress alerts, creating management challenges in Upwind.
  • Users find that the large number of vulnerability findings can quickly become overwhelming and hard to manage.
  • Users face challenges with false positives, as bulk resolution and suppression of alerts is not possible.

What Are Recent G2 Reviews of Upwind?

Lauren Worth
LW
Researched and written by Lauren Worth
Updated October 3, 2024