GuardionAI
Who Is the Company Behind GuardionAI?
- Seller: GuardionAI
- Year Founded: 2025
- HQ Location: United States, US
-
LinkedIn® Page: www.linkedin.com
2 employees on LinkedIn®
Total Products under this Category: 118
Last updated: October 09, 2026
Why You Can Trust G2's Software Rankings:
G2's software rankings are built on verified user reviews, rigorous moderation, and a consistent research methodology maintained by a team of analysts and data experts. Each product is measured using the same transparent criteria, with no paid placement or vendor influence. While reviews reflect real user experiences, which can be subjective, they offer valuable insight into how software performs in the hands of professionals. Together, these inputs power the G2 Score, a standardized way to compare tools within every category.
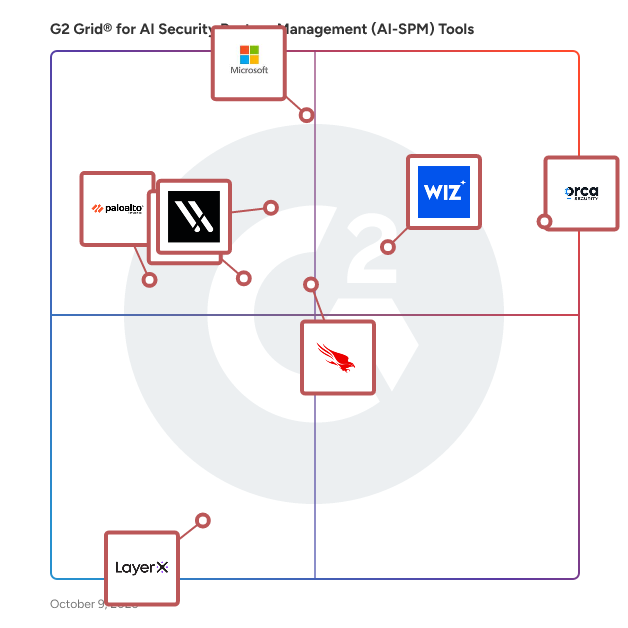
Highlighted products: Orca Security, Microsoft Defender for Cloud, Wiz, Varonis Data Security Platform, CrowdStrike Falcon Cloud Security, Saviynt, Cortex Cloud, and LayerX Browser Security Platform.
Underlying data: [Grid® JSON](https://www.g2.com/categories/ai-security-posture-management-ai-spm-tools/grids.json?focus%5B%5D=orca-security&focus%5B%5D=microsoft-defender-for-cloud&focus%5B%5D=wiz-wiz&focus%5B%5D=varonis-data-security-platform&focus%5B%5D=crowdstrike-falcon-cloud-security&focus%5B%5D=saviynt-saviynt&focus%5B%5D=cortex-cloud&focus%5B%5D=layerx-browser-security-platform)
Connect G2 to Claude or ChatGPT for answers grounded in G2's trusted reviews, comparisons, and pricing from real user insights.
Hush replaces static secrets with dynamic access policies and correlates posture findings with runtime insights to stop credential-based attacks at the source.
Kanopy Security gives enterprises visibility and control over the decisions their AI workforce makes. That workforce is every agent acting on your behalf: business-built agents in Copilot Studio, Power Automate and Salesforce Agentforce, and custom agents built on Claude, GPT and Gemini APIs. Kanopy maps every agent, skill and MCP server across your enterprise AI tools, then shows what each can reach and what it actually touches. It surfaces overprivileged agents, hard-coded secrets, unscoped access to sensitive data and data exposure, and stops destructive or malicious activity at execution. Static review reads what an agent was configured to do. Runtime analysis watches what it does, so findings show up as behavior, not guesses. It is agentless, with nothing to install, and it covers build time through runtime, fixing risk at the source before it ships. Native depth on Copilot Studio, Salesforce, ServiceNow, UiPath, Retool and Power Platform. One set of rules for every builder.
MandateMind AI is an advanced compliance intelligence platform designed to help small and medium-sized businesses (SMBs), virtual Chief Information Security Officers (vCISOs), and auditors maintain continuous compliance across multiple frameworks, including SOC 2, NIST 800‑53, HIPAA, PCI DSS, and ISO 27001. By leveraging artificial intelligence, MandateMind AI automates evidence analysis, detects security drift, and provides real-time readiness scoring, ensuring organizations remain audit-ready without the need for extensive manual effort. Key Features and Functionality: - Continuous Compliance Monitoring: Automatically aligns and monitors compliance across various mandates, reducing the risk of non-compliance. - AI-Powered Evidence Intelligence: Analyzes and interprets evidence, identifying gaps and providing actionable insights to strengthen security posture. - Real-Time Readiness Scoring: Offers instant assessments of compliance status, enabling proactive management and swift remediation of issues. - Unified Compliance Cockpit: Consolidates mandates, controls, evidence, and AI insights into a single interface for streamlined management. - Audit-Ready Snapshots and Exports: Generates structured, auditor-friendly reports to facilitate efficient audit processes. Primary Value and Problem Solved: MandateMind AI addresses the common challenge of maintaining continuous compliance in dynamic environments where security configurations can drift silently between audits. By automating the detection of such drifts and mapping evidence to relevant mandates, it ensures organizations stay consistently audit-ready. This reduces the reliance on manual processes, minimizes the risk of compliance gaps, and provides clarity and control over the compliance landscape, ultimately saving time and resources while enhancing security and compliance posture.
Neon Cyber is an AI-native, browser security solution that gives security teams real-time visibility into, and control over, how employees interact with AI tools, SaaS applications, and web-based resources — including activity that occurs outside of single sign-on (SSO) and identity provider (IDP) controls. The platform deploys as a lightweight browser extension across all major Chromium-based browsers (Chrome, Edge, Brave, Opera, and others) and requires no changes to existing network infrastructure. It can be pushed to end users in minutes via MDM, GPO or, Google Workspace. As employees adopt AI tools faster than security controls can keep pace, traditional solutions like DLP, EDR, and email security see only fragments of what's happening. Neon closes that gap. Deployed as a lightweight browser extension across all major Chromium-based browsers (Chrome, Edge, Brave, Opera, and others), it requires no infrastructure changes and can be rolled out in minutes via group policy, Google Workspace, or browser store enrollment. Core capabilities include: * AI & SaaS Visibility — Discovers every AI tool and SaaS application accessed by employees, including accounts created outside SSO and IDP controls, with vendor compliance metadata (SOC 2, HIPAA, etc.), data-sharing practices, and authentication methods. * AI Data Leakage Prevention — Monitors every prompt, input, upload, and download into generative AI tools in real time, enforcing context-aware guardrails to stop sensitive data from leaving the browser. * In-Browser Phishing Detection — A locally-run Small Language Model (SLM) analyzes form behavior and DOM interactions at the point of click to detect and block phishing attempts before credentials are entered — no external URL feeds required. * Identity & Credential Governance — Detects credential reuse, weak authentication, and identity anomalies across sanctioned and unsanctioned applications. * Forensic Timelines & SIEM Integration — Captures full session-level evidence per user and exports structured telemetry to SIEM/SOAR platforms via API. Neon Cyber complements existing EDR and IAM investments without replacing them — and without forcing employees into restrictive isolated browsers. Security teams get full visibility and control at the point of intent.
